Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: my75ex

Home > Cisco > CCNP Security > 350-701

350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Question and Answers

Question # 4

An organization has a Cisco ESA set up with policies and would like to customize the action assigned for

violations. The organization wants a copy of the message to be delivered with a message added to flag it as a

DLP violation. Which actions must be performed in order to provide this capability?

A.

deliver and send copies to other recipients

B.

quarantine and send a DLP violation notification

C.

quarantine and alter the subject header with a DLP violation

D.

deliver and add disclaimer text

Full Access
Question # 5

An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and

operate as a cloud-native CASB. Which solution must be used for this implementation?

A.

Cisco Cloudlock

B.

Cisco Cloud Email Security

C.

Cisco Firepower Next-Generation Firewall

D.

Cisco Umbrella

Full Access
Question # 6

Which two fields are defined in the NetFlow flow? (Choose two)

A.

type of service byte

B.

class of service bits

C.

Layer 4 protocol type

D.

destination port

E.

output logical interface

Full Access
Question # 7

A security engineer requires social-media websites to be blocked through Cisco Secure Firewall Threat Defense. Which configuration action must the engineer apply to meet the requirement?

A.

Enable global settings with default URL filtering.

B.

Configure a file policy in an access control policy.

C.

Apply web filtering in an access control policy.

D.

Block the social-media URL category in the destination-network condition of an access control rule.

Full Access
Question # 8

A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)

A.

POST /dna/intent/api/v1/image/distribution

B.

POST /dna/intent/api/v1/onboarding/pnp-device/import

C.

POST /dna/intent/api/v1/image/activation/device

D.

POST /dna/intent/api/v1/network/{site_id}

E.

POST /dna/intent/api/v1/template-programmer/project/{project_id}/template

Full Access
Question # 9

An engineer configured a new network identity in Cisco Umbrella but must verify that traffic is being routed

through the Cisco Umbrella network. Which action tests the routing?

A.

Ensure that the client computers are pointing to the on-premises DNS servers.

B.

Enable the Intelligent Proxy to validate that traffic is being routed correctly.

C.

Add the public IP address that the client computers are behind to a Core Identity.

D.

Browse to http://welcome.umbrella.com/ to validate that the new identity is working.

Full Access
Question # 10

A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?

A.

DHCP snooping has not been enabled on all VLANs.

B.

The ip arp inspection limit command is applied on all interfaces and is blocking the traffic of all users.

C.

Dynamic ARP Inspection has not been enabled on all VLANs

D.

The no ip arp inspection trust command is applied on all user host interfaces

Full Access
Question # 11

Which benefit is provided by ensuring that an endpoint is compliant with a posture policy configured in Cisco ISE?

A.

It allows the endpoint to authenticate with 802.1x or MAB.

B.

It verifies that the endpoint has the latest Microsoft security patches installed.

C.

It adds endpoints to identity groups dynamically.

D.

It allows CoA to be applied if the endpoint status is compliant.

Full Access
Question # 12

What is a difference between DMVPN and sVTI?

A.

DMVPN supports tunnel encryption, whereas sVTI does not.

B.

DMVPN supports dynamic tunnel establishment, whereas sVTI does not.

C.

DMVPN supports static tunnel establishment, whereas sVTI does not.

D.

DMVPN provides interoperability with other vendors, whereas sVTI does not.

Full Access
Question # 13

Which Cisco DNA Center Intent API action is used to retrieve the number of devices known to a DNA Center?

A.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/network-device/count

B.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/network-device

C.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v1/networkdevice?parameter1=value & parameter2=value & ....

D.

GET https://fqdnOrlPofDnaCenterPlatform/dna/intent/api/v 1/networkdevice/startIndex/recordsToReturn

Full Access
Question # 14

What are two advantages of using Cisco Any connect over DMVPN? (Choose two)

A.

It provides spoke-to-spoke communications without traversing the hub

B.

It allows different routing protocols to work over the tunnel

C.

It allows customization of access policies based on user identity

D.

It allows multiple sites to connect to the data center

E.

It enables VPN access for individual users from their machines

Full Access
Question # 15

What is the result of the ACME-Router(config)#login block-for 100 attempts 4 within 60 command on a Cisco IOS router?

A.

lf four log in attempts fail in 100 seconds, wait for 60 seconds to next log in prompt.

B.

After four unsuccessful log in attempts, the line is blocked for 100 seconds and only permit IP addresses are permitted in ACL

C.

After four unsuccessful log in attempts, the line is blocked for 60 seconds and only permit IP addresses are permitted in ACL1

D.

If four failures occur in 60 seconds, the router goes to quiet mode for 100 seconds.

Full Access
Question # 16

An engineer is adding a Cisco router to an existing environment. NTP authentication is configured on all devices in the environment with the command ntp authentication-key 1 md5 Clsc427128380. There are two routers on the network that are configured as NTP servers for redundancy, 192.168.1.110 and 192.168.1.111. 192.168.1.110 is configured as the authoritative time source. What command must be configured on the new router to use 192.168.1.110 as its primary time source without the new router attempting to offer time to existing devices?

A.

ntp server 192.168.1.110 primary key 1

B.

ntp peer 192.168.1.110 prefer key 1

C.

ntp server 192.168.1.110 key 1 prefer

D.

ntp peer 192.168.1.110 key 1 primary

Full Access
Question # 17

What must be configured in Cisco ISE to enforce reauthentication of an endpoint session when an endpoint is

deleted from an identity group?

A.

posture assessment

B.

CoA

C.

external identity source

D.

SNMP probe

Full Access
Question # 18

How does the Cisco WSA enforce bandwidth restrictions for web applications?

A.

It implements a policy route to redirect application traffic to a lower-bandwidth link.

B.

It dynamically creates a scavenger class QoS policy and applies it to each client that connects through the WSA.

C.

It sends commands to the uplink router to apply traffic policing to the application traffic.

D.

It simulates a slower link by introducing latency into application traffic.

Full Access
Question # 19

An engineer is implementing NAC for LAN users on a segmented network. The engineer confirms that the device of each user is supported and the Cisco switch configuration is correct.

Which configuration should be made next to ensure there are no authentication issues?

A.

Disable the host firewall.

B.

Enable TACACS+ on the switch.

C.

Open TCP port 49.

D.

Permit UDP port 1812.

Full Access
Question # 20

An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:

• Governance with role-based access control based on the principle of least privilege

• TLS 1.3 with signed certificates

• AES-256 with MD5

What must be configured to complete the secure implementation?

A.

3DES instead of AES

B.

DES instead of TLS 1.3

C.

SHA-512 instead of MD5

D.

SSLv3 instead of MD5

Full Access
Question # 21

Which two types of policies are used by ZTNA to provide access to an application? (Choose two.)

A.

Context

B.

Access

C.

Site-to-site

D.

Identity

E.

Remote access

Full Access
Question # 22

Which feature of a secure CI/CD pipeline defends container workloads against detected exploits, application flaws, configuration errors, and policy violations?

A.

Control groups

B.

Separation of duties

C.

Runtime protection

D.

Cloud-native firewalling

Full Access
Question # 23

A security engineer is tasked with configuring TACACS on a Cisco ASA firewall. The engineer must be able to access the firewall command line interface remotely. The authentication must fall back to the local user database of the Cisco ASA firewall. AAA server group named TACACS-GROUP is already configured with TACACS server IP address 192.168.10.10 and key C1sc0512222832!. Which configuration must be done next to meet the requirement?

A.

aaa authentication ssh console LOCAL TACACS-GROUP

B.

aaa authentication ssh console TACACS-GROUP LOCAL

C.

aaa authentication serial console LOCAL TACACS-GROUP

D.

aaa authentication http console TACACS-GROUP LOCAL

Full Access
Question # 24

An administrator configures new authorization policies within Cisco ISE and has difficulty profiling the devices. Attributes for the new Cisco IP phones that are profiled based on the RADIUS authentication are seen however the attributes for CDP or DHCP are not. What should the administrator do to address this issue?

A.

Configure the ip dhcp snooping trust command on the DHCP interfaces to get the information to Cisco ISE

B.

Configure the authentication port-control auto feature within Cisco ISE to identify the devices that are trying to connect

C.

Configure a service template within the switch to standardize the port configurations so that the correct information is sent to Cisco ISE

D.

Configure the device sensor feature within the switch to send the appropriate protocol information

Full Access
Question # 25

Which two parameters are used to prevent a data breach in the cloud? (Choose two.)

A.

DLP solutions

B.

strong user authentication

C.

encryption

D.

complex cloud-based web proxies

E.

antispoofing programs

Full Access
Question # 26

A network engineer has configured a NTP server on a Cisco ASA. The Cisco ASA has IP reachability to the

NTP server and is not filtering any traffic. The show ntp association detail command indicates that the

configured NTP server is unsynchronized and has a stratum of 16. What is the cause of this issue?

A.

Resynchronization of NTP is not forced

B.

NTP is not configured to use a working server.

C.

An access list entry for UDP port 123 on the inside interface is missing.

D.

An access list entry for UDP port 123 on the outside interface is missing.

Full Access
Question # 27

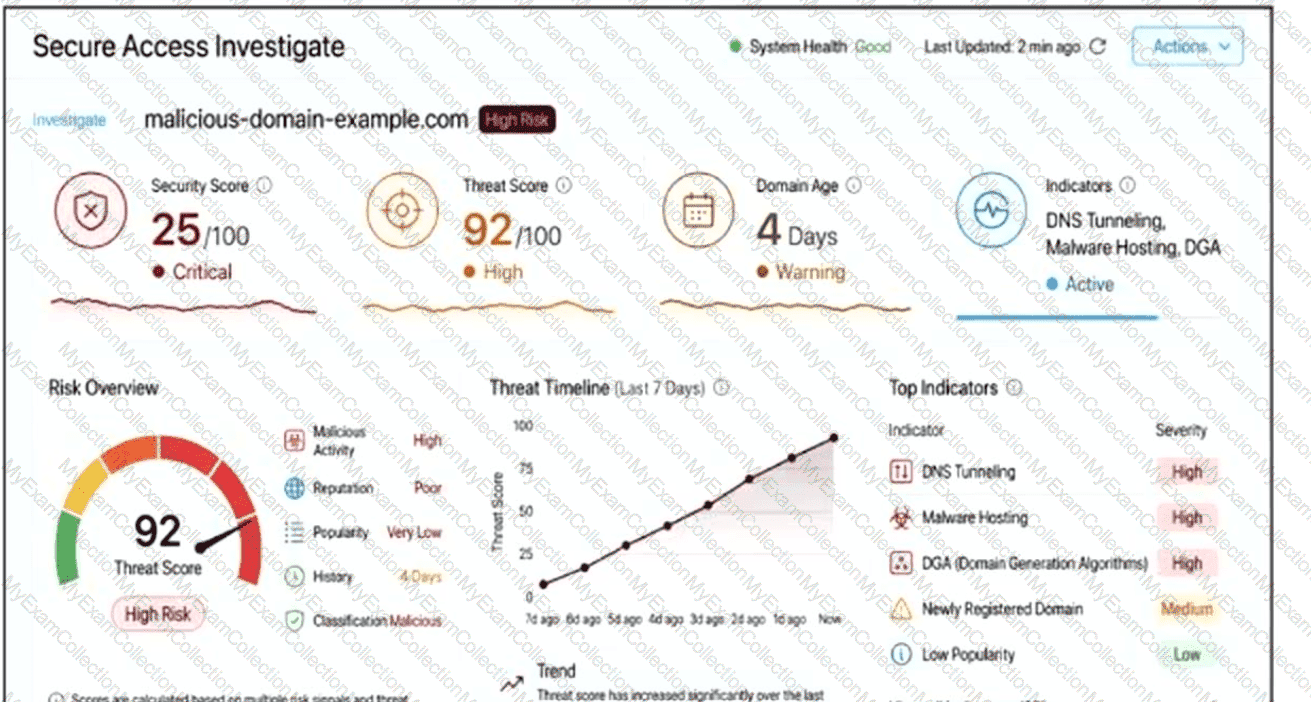
Which Cisco solution provides a comprehensive view of Internet domains. IP addresses, and autonomous systems to help pinpoint attackers and malicious infrastructures?

A.

Cisco Threat Indication Database

B.

Cisco Advanced Malware Investigate

C.

Cisco Umbrella Investigate

D.

Cisco Secure Workload Cloud

Full Access
Question # 28

Which Cisco network security device supports contextual awareness?

A.

Firepower

B.

CISCO ASA

C.

Cisco IOS

D.

ISE

Full Access
Question # 29

A mall provides security services to customers with a shared appliance. The mall wants separation of

management on the shared appliance. Which ASA deployment mode meets these needs?

A.

routed mode

B.

transparent mode

C.

multiple context mode

D.

multiple zone mode

Full Access
Question # 30

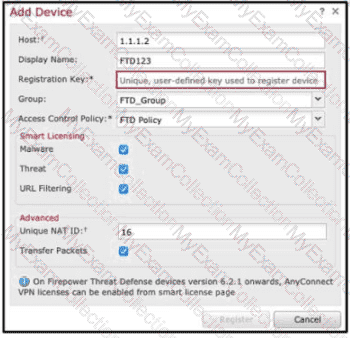
Refer to the exhibit.

An administrator is adding a new Cisco FTD device to their network and wants to manage it with Cisco FMC.

The Cisco FTD is not behind a NAT device. Which command is needed to enable this on the Cisco FTD?

A.

configure manager add DONTRESOLVE kregistration key >

B.

configure manager add < FMC IP address > < registration key > 16

C.

configure manager add DONTRESOLVE < registration key > FTD123

D.

configure manager add < FMC IP address > < registration key >

Full Access
Question # 31

Which process is used to obtain a certificate from a CA?

A.

Registration

B.

Enrollment

C.

Signing

D.

Approval

Full Access
Question # 32

An engineer needs to configure an access control policy rule to always send traffic for inspection without

using the default action. Which action should be configured for this rule?

A.

monitor

B.

allow

C.

block

D.

trust

Full Access
Question # 33

A network administrator is configuring a role in an access control policy to block certain URLs and selects the " Chat and instant Messaging " category. which reputation score should be selected to accomplish

this goal?

A.

3

B.

5

C.

10

D.

1

Full Access
Question # 34

An administrator wants to ensure that all endpoints are compliant before users are allowed access on the

corporate network. The endpoints must have the corporate antivirus application installed and be running the

latest build of Windows 10.

What must the administrator implement to ensure that all devices are compliant before they are allowed on the

network?

A.

Cisco Identity Services Engine and AnyConnect Posture module

B.

Cisco Stealthwatch and Cisco Identity Services Engine integration

C.

Cisco ASA firewall with Dynamic Access Policies configured

D.

Cisco Identity Services Engine with PxGrid services enabled

Full Access
Question # 35

An engineer must implement an external application that authenticates against the Cisco Secure Email Threat Defense API to perform automated message searches. The application already presents a user bearer token, but the API requires an additional authentication header with each request. The engineer must configure the external application to include the required header alongside the bearer token so that the API calls are accepted. Which header must be configured?

A.

x-api-key

B.

token-id

C.

client_secret

D.

x-auth-token

Full Access
Question # 36

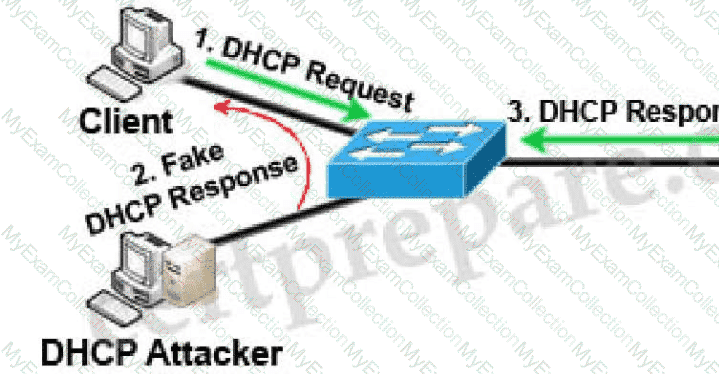
An administrator is configuring a DHCP server to better secure their environment. They need to be able to ratelimit the traffic and ensure that legitimate requests are not dropped. How would this be accomplished?
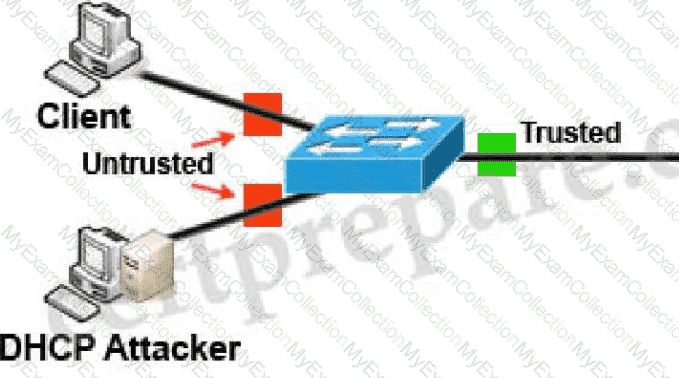
A.

Set a trusted interface for the DHCP server

B.

Set the DHCP snooping bit to 1

C.

Add entries in the DHCP snooping database

D.

Enable ARP inspection for the required VLAN

Full Access
Question # 37

A network administrator has configured TACACS on a network device using the key Cisc0467380030 tor authentication purposes. However, users are unable to authenticate. TACACS server is reachable, but authentication is tailing. Which configuration step must the administrator complete?

A.

Implement synchronized system clock on TACACS server that matches the network device.

B.

Install a compatible operating system version on the TACACS server.

C.

Configure the TACACS key on the server to match with the network device.

D.

Apply an access control list on TACACS server to allow communication with the network device.

Full Access
Question # 38

Which Cisco Secure Endpoint feature tracks the propagation and execution path of a malicious file across the environment?

A.

Exclusion Lists

B.

Device Flow Correlation

C.

Incident Manager

D.

File Trajectory

Full Access
Question # 39

What is the difference between a vulnerability and an exploit?

A.

A vulnerability is a hypothetical event for an attacker to exploit

B.

A vulnerability is a weakness that can be exploited by an attacker

C.

An exploit is a weakness that can cause a vulnerability in the network

D.

An exploit is a hypothetical event that causes a vulnerability in the network

Full Access
Question # 40

Which technology must be used to implement secure VPN connectivity among company branches over a

private IP cloud with any-to-any scalable connectivity?

A.

DMVPN

B.

FlexVPN

C.

IPsec DVTI

D.

GET VPN

Full Access
Question # 41

Which Cisco WSA feature supports access control using URL categories?

A.

transparent user identification

B.

SOCKS proxy services

C.

web usage controls

D.

user session restrictions

Full Access
Question # 42

An organization has a Cisco Stealthwatch Cloud deployment in their environment. Cloud logging is working as expected, but logs are not being received from the on-premise network, what action will resolve this issue?

A.

Configure security appliances to send syslogs to Cisco Stealthwatch Cloud

B.

Configure security appliances to send NetFlow to Cisco Stealthwatch Cloud

C.

Deploy a Cisco FTD sensor to send events to Cisco Stealthwatch Cloud

D.

Deploy a Cisco Stealthwatch Cloud sensor on the network to send data to Cisco Stealthwatch Cloud

Full Access
Question # 43

Which type of API is being used when a controller within a software-defined network architecture dynamically

makes configuration changes on switches within the network?
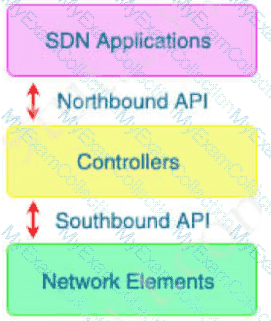
A.

westbound AP

B.

southbound API

C.

northbound API

D.

eastbound API

Full Access
Question # 44

For Cisco IOS PKI, which two types of Servers are used as a distribution point for CRLs? (Choose two)
A.

SDP

B.

LDAP

C.

subordinate CA

D.

SCP

E.

HTTP

Full Access
Question # 45

Which two key and block sizes are valid for AES? (Choose two)

A.

64-bit block size, 112-bit key length

B.

64-bit block size, 168-bit key length

C.

128-bit block size, 192-bit key length

D.

128-bit block size, 256-bit key length

E.

192-bit block size, 256-bit key length

Full Access
Question # 46

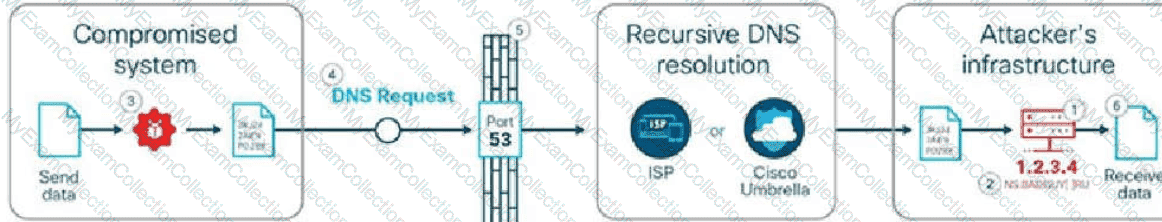
How is DNS tunneling used to exfiltrate data out of a corporate network?

A.

It corrupts DNS servers by replacing the actual IP address with a rogue address to collect information or start other attacks.

B.

It encodes the payload with random characters that are broken into short strings and the DNS serverrebuilds the exfiltrated data.

C.

It redirects DNS requests to a malicious server used to steal user credentials, which allows further damageand theft on the network.

D.

It leverages the DNS server by permitting recursive lookups to spread the attack to other DNS servers.

Full Access
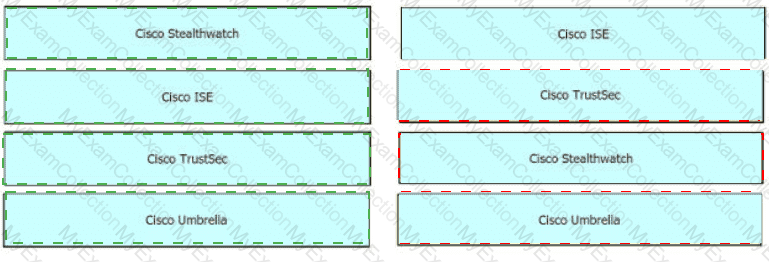
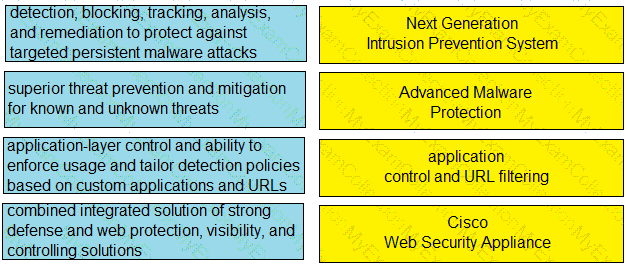
Question # 47

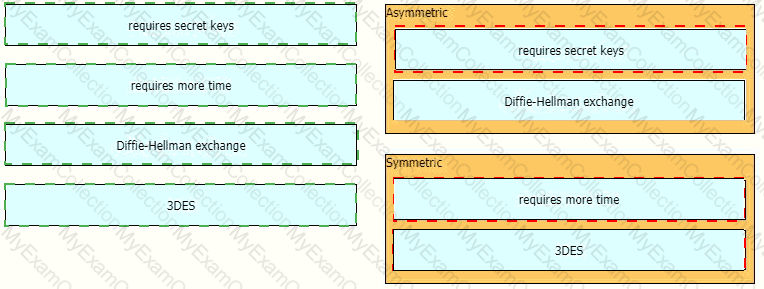
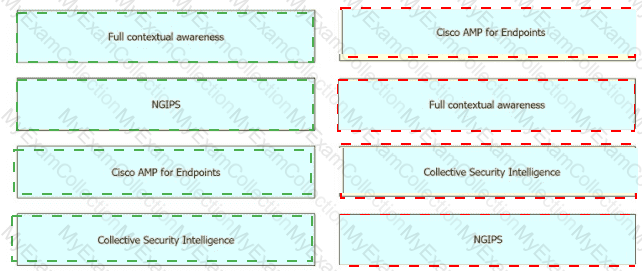
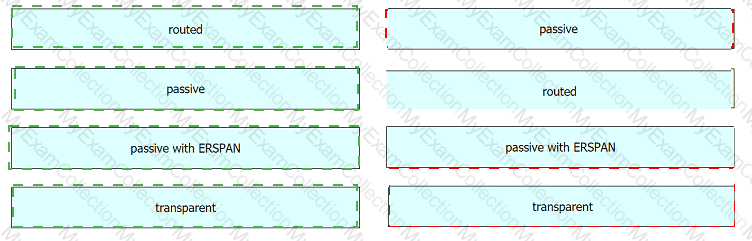
Drag and drop the capabilities from the left onto the correct technologies on the right.
Full Access
Question # 48

What is the function of the crypto is a kmp key cisc406397954 address 0.0.0.0 0.0.0.0 command when establishing an IPsec VPN tunnel?

A.

It defines what data is going to be encrypted via the VPN

B.

lt configures the pre-shared authentication key

C.

It prevents all IP addresses from connecting to the VPN server.

D.

It configures the local address for the VPN server.

Full Access
Question # 49

How does Cisco Umbrella protect clients when they operate outside of the corporate network?

A.

by modifying the registry for DNS lookups

B.

by using Active Directory group policies to enforce Cisco Umbrella DNS servers

C.

by using the Cisco Umbrella roaming client

D.

by forcing DNS queries to the corporate name servers

Full Access
Question # 50

An administrator is implementing management plane protection and must configure an interface on a Cisco router to only terminate management packets that are destined for the router. Which set of IOS commands must be used to complete the implementation?

A.

B.

C.

D.

Full Access
Question # 51

Which type of information does threat intelligence gather to identify potential threats using common adversary techniques?

A.

User browsing history and personal data

B.

Aggregated firewall syslogs and routing tables

C.

Network traffic statistics and performance metrics

D.

Data on known malware signatures and IP addresses

Full Access
Question # 52

In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)

A.

Customer needs to support roaming users.

B.

Customer does not own Cisco hardware and needs Transparent Redirection (WCCP).

C.

Customer owns ASA Appliance and Virtual Form Factor is required.

D.

Customer does not own Cisco hardware and needs Explicit Proxy.

E.

Customer owns ASA Appliance and SSL Tunneling is required.

Full Access
Question # 53

What are two characteristics of the RESTful architecture used within Cisco DNA Center? (Choose two.)

A.

REST uses methods such as GET, PUT, POST, and DELETE.

B.

REST codes can be compiled with any programming language.

C.

REST is a Linux platform-based architecture.

D.

The POST action replaces existing data at the URL path.

E.

REST uses HTTP to send a request to a web service.

Full Access
Question # 54

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

Full Access
Question # 55

Which Cisco platform provides an agentless solution to provide visibility across the network including encrypted traffic analytics to detect malware in encrypted traffic without the need for decryption?

A.

Cisco Advanced Malware Protection

B.

Cisco Stealthwatch

C.

Cisco Identity Services Engine

D.

Cisco AnyConnect

Full Access
Question # 56

What is a benefit of using Cisco AVC (Application Visibility and Control) for application control?

A.

management of application sessions

B.

retrospective application analysis

C.

zero-trust approach

D.

dynamic application scanning

Full Access
Question # 57

Which security solution uses NetFlow to provide visibility across the network, data center, branch offices, and cloud?

A.

Cisco CTA

B.

Cisco Encrypted Traffic Analytics

C.

Cisco Umbrella

D.

Cisco Secure Network Analytics

Full Access
Question # 58

Which technology provides a combination of endpoint protection endpoint detection, and response?

A.

Cisco AMP

B.

Cisco Talos

C.

Cisco Threat Grid

D.

Cisco Umbrella

Full Access
Question # 59

Which group within Cisco writes and publishes a weekly newsletter to help cybersecurity professionals remain

aware of the ongoing and most prevalent threats?

A.

PSIRT

B.

Talos

C.

CSIRT

D.

DEVNET

Full Access
Question # 60

Which ESA implementation method segregates inbound and outbound email?

A.

one listener on a single physical Interface

B.

pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address

C.

pair of logical IPv4 listeners and a pair Of IPv6 listeners on two physically separate interfaces

D.

one listener on one logical IPv4 address on a single logical interface

Full Access
Question # 61

Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?

A.

user input validation in a web page or web application

B.

Linux and Windows operating systems

C.

database

D.

web page images

Full Access
Question # 62

A network administrator is setting up Cisco FMC to send logs to Cisco Security Analytics and Logging (SaaS). The network administrator is anticipating a high volume of logging events from the firewalls and wants lo limit the strain on firewall resources. Which method must the administrator use to send these logs to Cisco Security Analytics and Logging?

A.

SFTP using the FMCCLI

B.

syslog using the Secure Event Connector

C.

direct connection using SNMP traps

D.

HTTP POST using the Security Analytics FMC plugin

Full Access
Question # 63

Which network monitoring solution uses streams and pushes operational data to provide a near real-time view

of activity?

A.

SNMP

B.

SMTP

C.

syslog

D.

model-driven telemetry

Full Access
Question # 64

What is the purpose of the Trusted Automated exchange cyber threat intelligence industry standard?

A.

public collection of threat intelligence feeds

B.

threat intelligence sharing organization

C.

language used to represent security information

D.

service used to exchange security information

Full Access
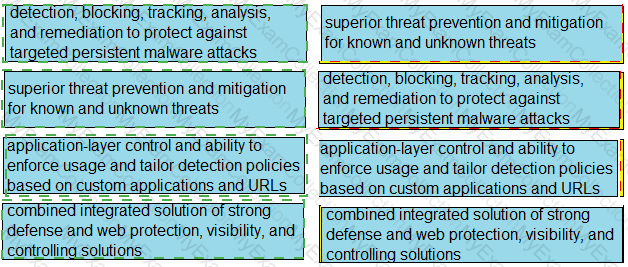
Question # 65

Drag and drop the solutions from the left onto the solution ' s benefits on the right.
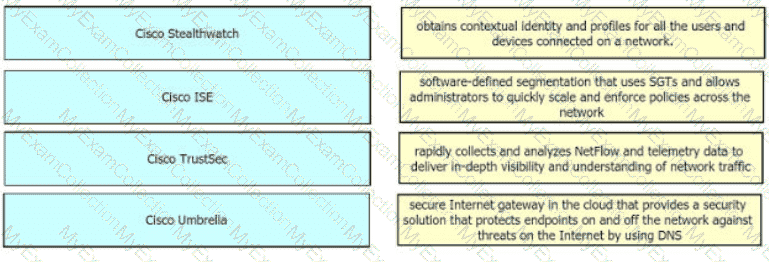
Full Access
Question # 66

Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?

A.

filters

B.

group key

C.

company key

D.

connector

Full Access
Question # 67

In which two ways does the Cisco Advanced Phishing Protection solution protect users? (Choose two.)

A.

It prevents use of compromised accounts and social engineering.

B.

It prevents all zero-day attacks coming from the Internet.

C.

It automatically removes malicious emails from users ' inbox.

D.

It prevents trojan horse malware using sensors.

E.

It secures all passwords that are shared in video conferences.

Full Access
Question # 68

What are two ways that Cisco Container Platform provides value to customers who utilize cloud service providers? (Choose two.)

A.

Allows developers to create code once and deploy to multiple clouds

B.

helps maintain source code for cloud deployments

C.

manages Docker containers

D.

manages Kubernetes clusters

E.

Creates complex tasks for managing code

Full Access
Question # 69

Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?

A.

Encrypted Traffic Analytics

B.

Threat Intelligence Director

C.

Cognitive Threat Analytics

D.

Cisco Talos Intelligence

Full Access
Question # 70

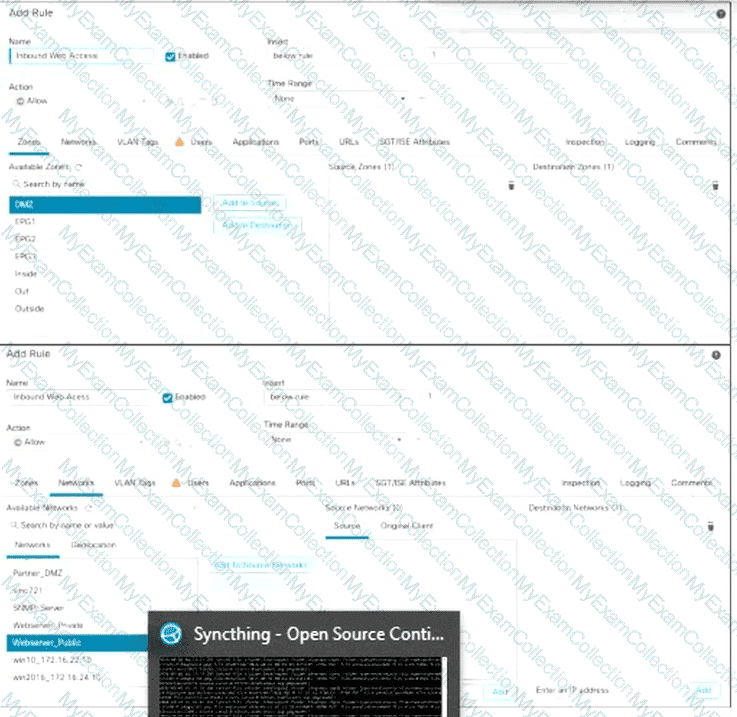
Refer to the exhibit.

A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)

A.

Add DMZ as the Source Zone and Outside as the Destination Zone.

B.

Add Webserver_Private as the Source Network and Webserver_Public as the Destination Network.

C.

Add Any as the Source Network and Webserver_Private as the Destination Network.

D.

Add Any as the Source Network and Webserver_Public as the Destination Network.

E.

Add Outside as the Source Zone and DMZ as the Destination Zone.

Full Access
Question # 71

Which two authentication protocols are supported by the Cisco WSA? (Choose two.)

A.

WCCP

B.

NTLM

C.

TLS

D.

SSL

E.

LDAP

Full Access
Question # 72

What is the purpose of CA in a PKI?

A.

To issue and revoke digital certificates

B.

To validate the authenticity of a digital certificate

C.

To create the private key for a digital certificate

D.

To certify the ownership of a public key by the named subject

Full Access
Question # 73

What is a language format designed to exchange threat intelligence that can be transported over the TAXII

protocol?

A.

STIX

B.

XMPP

C.

pxGrid

D.

SMTP

Full Access
Question # 74

What are two benefits of using an MDM solution? (Choose two.)

A.

grants administrators a way to remotely wipe a lost or stolen device

B.

provides simple and streamlined login experience for multiple applications and users

C.

native integration that helps secure applications across multiple cloud platforms or on-premises environments

D.

encrypts data that is stored on endpoints

E.

allows for centralized management of endpoint device applications and configurations

Full Access
Question # 75

What is the function of the Internet Key Exchange (IKE) protocol in an IPsec VPN?

A.

Handle packet filtering

B.

Negotiate tunnel parameters

C.

Manage data transfers

D.

Encrypt data packets

Full Access
Question # 76

An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the

organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which

mechanism should the engineer configure to accomplish this goal?

A.

mirror port

B.

Flow

C.

NetFlow

D.

VPC flow logs

Full Access
Question # 77

What are two DDoS attack categories? (Choose two)

A.

sequential

B.

protocol

C.

database

D.

volume-based

E.

screen-based

Full Access
Question # 78

In which two ways does a system administrator send web traffic transparently to the Web Security Appliance?

(Choose two)

A.

configure Active Directory Group Policies to push proxy settings

B.

configure policy-based routing on the network infrastructure

C.

reference a Proxy Auto Config file

D.

configure the proxy IP address in the web-browser settings

E.

use Web Cache Communication Protocol

Full Access
Question # 79

What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?

A.

It allows the administrator to quarantine malicious files so that the application can function, just notmaliciously.

B.

It discovers and controls cloud apps that are connected to a company’s corporate environment.

C.

It deletes any application that does not belong in the network.

D.

It sends the application information to an administrator to act on.

Full Access
Question # 80

A company wants to migrate to the cloud to reduce operational costs. The company requires full control to modify and patch its applications. The cloud provider must be responsible for managing everything else, and all data must be secured at rest. Which cloud service model must be used to meet these requirements?

A.

IaaS

B.

Hybrid cloud

C.

PaaS

D.

SaaS

Full Access
Question # 81

An administrator has been tasked with configuring the Cisco Secure Email Gateway to ensure there are no viruses before quarantined emails are delivered. In addition, delivery of mail from known bad mail servers must be prevented. Which two actions must be taken in order to meet these requirements? (Choose two.)

A.

Deploy the Secure Email Gateway in the DMZ.

B.

Use outbreak filters from Cisco Talos.

C.

Configure a recipient access table.

D.

Enable a message tracking service.

E.

Scan quarantined emails using AntiVirus signatures.

Full Access
Question # 82

What causes alert fatigue in Cisco XDR?

A.

Alerts lacking sufficient context to be accurate

B.

Reauthentication of an active endpoint during a vulnerability incident

C.

Notifications from too few devices in a data-breach event

D.

Automatic policy enforcement during a suspicious event

Full Access
Question # 83

What provides the ability to program and monitor networks from somewhere other than the DNAC GUI?

A.

NetFlow

B.

desktop client

C.

ASDM

D.

API

Full Access
Question # 84

An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices. The default management

port conflicts with other communications on the network and must be changed. What must be done to ensure

that all devices can communicate together?

A.

Manually change the management port on Cisco FMC and all managed Cisco FTD devices

B.

Set the tunnel to go through the Cisco FTD

C.

Change the management port on Cisco FMC so that it pushes the change to all managed Cisco FTDdevices

D.

Set the tunnel port to 8305

Full Access
Question # 85

In which form of attack is alternate encoding, such as hexadecimal representation, most often observed?

A.

Smurf

B.

distributed denial of service

C.

cross-site scripting

D.

rootkit exploit

Full Access
Question # 86

Which capability is provided by application visibility and control?

A.

reputation filtering

B.

data obfuscation

C.

data encryption

D.

deep packet inspection

Full Access
Question # 87

What is an attribute of the DevSecOps process?

A.

mandated security controls and check lists

B.

security scanning and theoretical vulnerabilities

C.

development security

D.

isolated security team

Full Access
Question # 88

Which two services must remain as on-premises equipment when a hybrid email solution is deployed? (Choose two)

A.

DDoS

B.

antispam

C.

antivirus

D.

encryption

E.

DLP

Full Access
Question # 89

Drag and drop the features of Cisco ASA with Firepower from the left onto the benefits on the right.
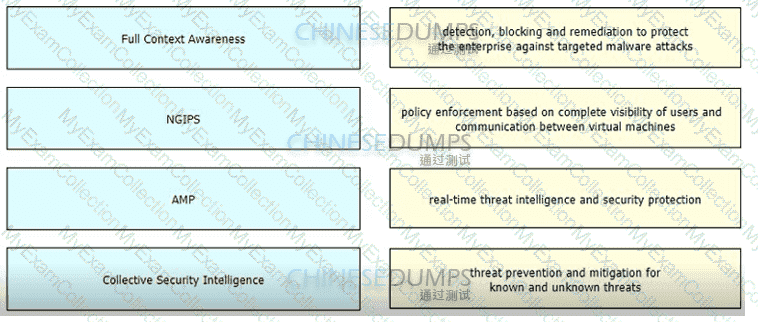
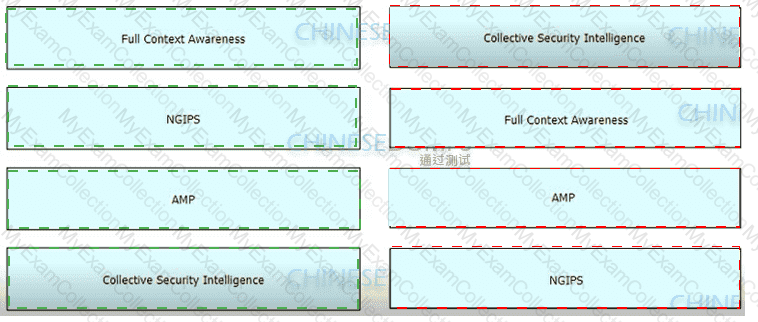
Full Access
Question # 90

Due to a traffic storm on the network, two interfaces were error-disabled, and both interfaces sent SNMP traps.

Which two actions must be taken to ensure that interfaces are put back into service? (Choose two)

A.

Have Cisco Prime Infrastructure issue an SNMP set command to re-enable the ports after the preconfigured interval.

B.

Use EEM to have the ports return to service automatically in less than 300 seconds.

C.

Enter the shutdown and no shutdown commands on the interfaces.

D.

Enable the snmp-server enable traps command and wait 300 seconds

E.

Ensure that interfaces are configured with the error-disable detection and recovery feature

Full Access
Question # 91

What is a benefit of using GET VPN over FlexVPN within a VPN deployment?

A.

GET VPN supports Remote Access VPNs

B.

GET VPN natively supports MPLS and private IP networks

C.

GET VPN uses multiple security associations for connections

D.

GET VPN interoperates with non-Cisco devices

Full Access
Question # 92

Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)

A.

blocks malicious websites and adds them to a block list

B.

does a real-time user web browsing behavior analysis

C.

provides a defense for on-premises email deployments

D.

uses a static algorithm to determine malicious

E.

determines if the email messages are malicious

Full Access
Question # 93

Why is it important to patch endpoints consistently?

A.

Patching reduces the attack surface of the infrastructure.

B.

Patching helps to mitigate vulnerabilities.

C.

Patching is required per the vendor contract.

D.

Patching allows for creating a honeypot.

Full Access
Question # 94

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

A.

Create an LDAP authentication realm and disable transparent user identification.

B.

Create NTLM or Kerberos authentication realm and enable transparent user identification.

C.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

D.

The eDirectory client must be installed on each client workstation.

E.

Deploy a separate eDirectory server; the dent IP address is recorded in this server.

Full Access
Question # 95

Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?

A.

Performing static routing configuration checks

B.

Conducting software composition analysis during builds

C.

Using dynamic routing between Kubernetes clusters

D.

Setting up round-robin DNS resolution for service discovery

Full Access
Question # 96

A university policy must allow open access to resources on the Internet for research, but internal workstations are exposed to malware. Which Cisco AMP feature allows the engineering team to determine whether a file is installed on a selected few workstations?

A.

file prevalence

B.

file discovery

C.

file conviction

D.

file manager

Full Access
Question # 97

What is a description of microsegmentation?

A.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate

B.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery

C.

Environments implement private VLAN segmentation to group servers with similar applications.

D.

Environments deploy centrally managed host-based firewall rules on each server or container

Full Access
Question # 98

Which two methods are available in Cisco Secure Web Appliance to process client requests when configured in Transparent mode? (Choose two.)

A.

WCCP

B.

Browser settings

C.

WPAD

D.

PAC files

E.

PBR

Full Access
Question # 99

What is the role of an endpoint in protecting a user from a phishing attack?

A.

Use Cisco Stealthwatch and Cisco ISE Integration.

B.

Utilize 802.1X network security to ensure unauthorized access to resources.

C.

Use machine learning models to help identify anomalies and determine expected sending behavior.

D.

Ensure that antivirus and anti malware software is up to date

Full Access
Question # 100

Which CLI command is used to enable URL filtering support for shortened URLs on the Cisco ESA?

A.

webadvancedconfig

B.

websecurity advancedconfig

C.

outbreakconfig

D.

websecurity config

Full Access
Question # 101

Which deployment model is the most secure when considering risks to cloud adoption?

A.

Public Cloud

B.

Hybrid Cloud

C.

Community Cloud

D.

Private Cloud

Full Access
Question # 102

A security engineer must add destinations into a destination list in Cisco Umbrella. What describes the application of these changes?

A.

The changes are applied immediately it the destination list is part or a policy.

B.

The destination list must be removed from the policy before changes are made to It.

C.

The changes are applied only after the configuration is saved in Cisco Umbrella.

D.

The user role of Block Page Bypass or higher is needed to perform these changes.

Full Access
Question # 103

Which security principle advocates rapid cryptographic algorithm replacement to defend against quantum-computing threats?

A.

Crypto agility

B.

Zero trust

C.

Network slicing

D.

Key escrow

Full Access
Question # 104

What are two differences between a Cisco Secure Web Appliance that is running in transparent mode and one running in explicit mode? (Choose two.)

A.

The Cisco Secure Web Appliance responds with its own IP address only if it is running in transparent mode.

B.

When the Cisco Secure Web Appliance is running in transparent mode, it uses the Secure Web Appliance ' s own IP address as the HTTP request destination.

C.

The Cisco Secure Web Appliance responds with its own IP address only if it is running in explicit mode.

D.

The Cisco Secure Web Appliance is configured in a web browser only if it is running in transparent mode.

E.

The Cisco Secure Web Appliance uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

Full Access
Question # 105

Refer to the exhibit.

=== Cisco Secure Endpoint - Detection Event ===

Endpoint : LAB-WKSTN-047 User: user1

Policy Group : Lab-Workstations Mode: Audit

Engine : ETHOS (fuzzy fingerprint)

Disposition : Malicious

File : C:\Users\user1\AppData\Local\Temp\svchost32.exe

SHA256 : 3a9f2c1d...e881b4a7

Parent Process: winword.exe

Threat Name : W32.Trojan.GenericKD.Agent

Retrospective : Previously UNKNOWN

Disposition changed to MALICIOUS at 09:31:55 UTC

File Activity : Created, Executed

Network : TCP outbound - > 91.205.188.47:4444

DNS query: c2-update.pharmadomain.ru

Quarantine : NOT quarantined (Audit mode active)

A security analyst at a pharmaceutical company is reviewing a Cisco Secure Endpoint malware-detection alert triggered on a laboratory workstation. The analyst observes the event data above. Which two things are occurring? (Choose two.)

A.

The antivirus engine update interval on workstation LAB-WKSTN-047 is too infrequent.

B.

The endpoint is running in Audit mode; the file was detected but not quarantined.

C.

The endpoint is running in Audit mode; the file was detected and quarantined.

D.

The file executed, was spawned by winword.exe, and opened an outbound connection to external command-and-control infrastructure.

E.

The parent file winword.exe is on a custom application allow list, permitting the malicious file to execute.

Full Access
Question # 106

DoS attacks are categorized as what?

A.

phishing attacks

B.

flood attacks

C.

virus attacks

D.

trojan attacks

Full Access
Question # 107

An administrator is establishing a new site-to-site VPN connection on a Cisco IOS router. The organization

needs to ensure that the ISAKMP key on the hub is used only for terminating traffic from the IP address of

172.19.20.24. Which command on the hub will allow the administrator to accomplish this?

A.

crypto ca identity 172.19.20.24

B.

crypto isakmp key Cisco0123456789 172.19.20.24

C.

crypto enrollment peer address 172.19.20.24

D.

crypto isakmp identity address 172.19.20.24

Full Access
Question # 108

What is the benefit of integrating Cisco ISE with a MDM solution?

A.

It provides compliance checks for access to the network

B.

It provides the ability to update other applications on the mobile device

C.

It provides the ability to add applications to the mobile device through Cisco ISE

D.

It provides network device administration access

Full Access
Question # 109

Which standard is used to automate exchanging cyber threat information?

A.

TAXII

B.

MITRE

C.

IoC

D.

STIX

Full Access
Question # 110

What is a benefit of an endpoint patch management strategy?

A.

Patches are deployed without a testing phase.

B.

Fewer staff is needed to manage the endpoints.

C.

Endpoints are resistant to vulnerabilities.

D.

Ensures adherence to regulatory and compliance standards.

Full Access
Question # 111

Which benefit does DMVPN provide over GETVPN?

A.

DMVPN supports QoS, multicast, and routing, and GETVPN supports only QoS.

B.

DMVPN is a tunnel-less VPN, and GETVPN is tunnel-based.

C.

DMVPN supports non-IP protocols, and GETVPN supports only IP protocols.

D.

DMVPN can be used over the public Internet, and GETVPN requires a private network.

Full Access
Question # 112

Which service allows a user export application usage and performance statistics with Cisco Application Visibility

and control?

A.

SNORT

B.

NetFlow

C.

SNMP

D.

802.1X

Full Access
Question # 113

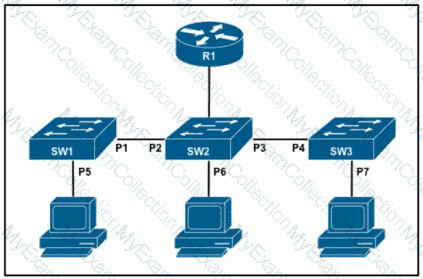
Refer to the exhibit.

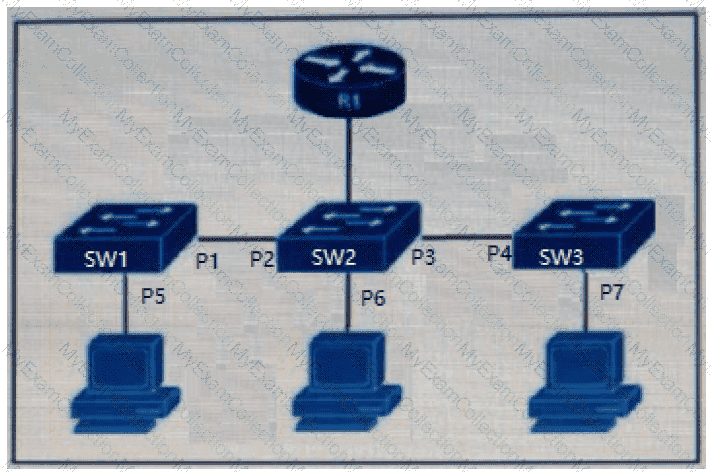
The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

A.

P2 and P3 only

B.

P5, P6, and P7 only

C.

P1, P2, P3, and P4 only

D.

P2, P3, and P6 only

Full Access
Question # 114

A security engineer is deploying an IPsec site-to-site VPN between headquarters and a remote plant, protected by Cisco Secure Firewall Threat Defense managed by Cisco Secure Firewall Management Center. The following configurations have already been completed:

    Matching IKEv2 proposals, preshared keys, and IPsec transform sets

    Access control rules permitting the traffic

    Crypto maps applied to the outside interfaces

    VPN traffic exempted from inspection

During a packet capture on the firewall, the engineer observes that the traffic is translated to the public IP address, preventing tunnel establishment. Which configuration action must be performed next?

A.

Configure NAT exemption for traffic between the interesting subnet pairs.

B.

Create a tunnel group with preshared-key authentication under connection profiles.

C.

Enable IKEv2 fragmentation on both peers to reduce packet size.

D.

Attach the new VPN policy to the global prefilter default action.

Full Access
Question # 115

Which type of API is being used when a security application notifies a controller within a software-defined network architecture about a specific security threat?

A.

westbound AP

B.

southbound API

C.

northbound API

D.

eastbound API

Full Access
Question # 116

An engineer recently completed the system setup on a Cisco WSA Which URL information does the system send to SensorBase Network servers?

A.

Summarized server-name information and MD5-hashed path information

B.

complete URL,without obfuscating the path segments

C.

URL information collected from clients that connect to the Cisco WSA using Cisco AnyConnect

D.

none because SensorBase Network Participation is disabled by default

Full Access
Question # 117

An engineer must implement a file transfer solution between a company ' s data center and branches. The company has numerous servers hosted in a hybrid cloud implementation. The file transfer protocol must support authentication, protect the data against unauthorized access, and ensure that users cannot list directories or remove files remotely. Which protocol must be used?

A.

SCP

B.

SSH

C.

FTPS

D.

SFTP

Full Access
Question # 118

An engineer needs to configure a Cisco Secure Email Gateway (SEG) to prompt users to enter multiple forms of identification before gaining access to the SEG. The SEG must also join a cluster using the preshared key of cisc421555367. What steps must be taken to support this?

A.

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG GUI.

B.

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG CLI.

C.

Enable two-factor authentication through a RADIUS server, and then join the cluster via the SEG CLI

D.

Enable two-factor authentication through a TACACS+ server, and then join the cluster via the SEG GUI.

Full Access
Question # 119

Which two mechanisms are used to control phishing attacks? (Choose two)

A.

Enable browser alerts for fraudulent websites.

B.

Define security group memberships.

C.

Revoke expired CRL of the websites.

D.

Use antispyware software.

E.

Implement email filtering techniques.

Full Access
Question # 120

Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data

within a network perimeter?

A.

cloud web services

B.

network AMP

C.

private cloud

D.

public cloud

Full Access
Question # 121

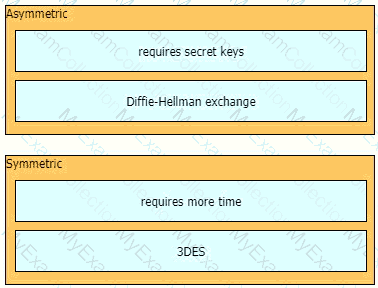
Drag and drop the descriptions from the left onto the encryption algorithms on the right.
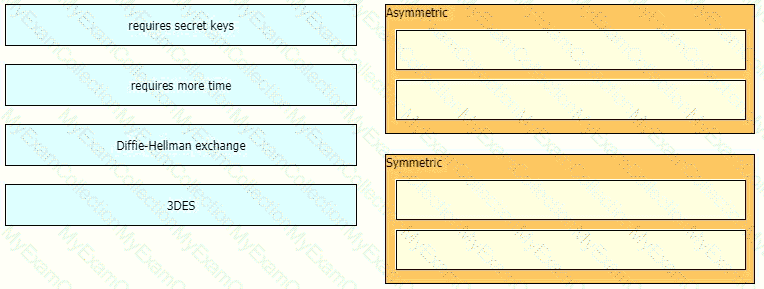
Full Access
Question # 122

Refer to the exhibit.
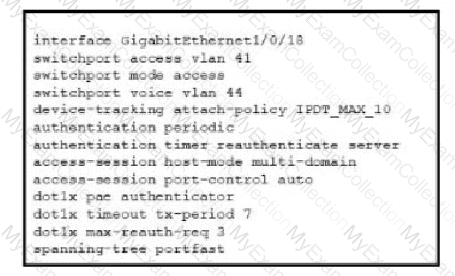
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.

Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?

A.

Change the default policy in Cisco ISE to allow all devices not using machine authentication .

B.

Enable insecure protocols within Cisco ISE in the allowed protocols configuration.

C.

Configure authentication event fail retry 2 action authorize vlan 41 on the interface

D.

Add mab to the interface configuration.

Full Access
Question # 123

Which suspicious pattern enables the Cisco Tetration platform to learn the normal behavior of users?

A.

file access from a different user

B.

interesting file access

C.

user login suspicious behavior

D.

privilege escalation

Full Access
Question # 124

Which Cisco Secure Client module is integrated with Splunk Enterprise to provide monitoring capabilities to administrators to allow them to view endpoint application usage?

A.

Umbrella Roaming Security

B.

Network Visibility

C.

AMP Enabler

D.

ISE Posture

Full Access
Question # 125

Which endpoint protection and detection feature performs correlation of telemetry, files, and intrusion

events that are flagged as possible active breaches?

A.

retrospective detection

B.

indication of compromise

C.

file trajectory

D.

elastic search

Full Access
Question # 126

An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?

A.

Sophos scanning engine

B.

Webroot scanning engine

C.

McAfee scanning engine

D.

Adaptive Scanning

Full Access
Question # 127

Which technology reduces data loss by identifying sensitive information stored in public computing

environments?

A.

Cisco SDA

B.

Cisco Firepower

C.

Cisco HyperFlex

D.

Cisco Cloudlock

Full Access
Question # 128

Based on the NIST 800-145 guide, which cloud architecture may be owned, managed, and operated by one or more of the organizations in the community, a third party, or some combination of them, and it may exist on or off premises?

A.

hybrid cloud

B.

private cloud

C.

public cloud

D.

community cloud

Full Access
Question # 129

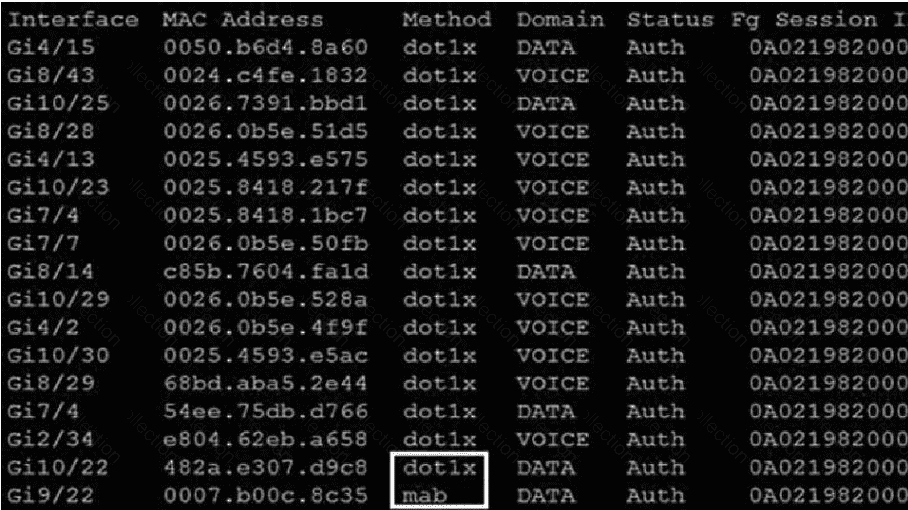
Refer to the exhibit.

Which command was used to generate this output and to show which ports are

authenticating with dot1x or mab?

A.

show authentication registrations

B.

show authentication method

C.

show dot1x all

D.

show authentication sessions

Full Access
Question # 130

Refer to the exhibit. Consider that any feature of DNS requests, such as the length of the domain name and the number of subdomains, can be used to construct models of expected behavior to which observed values can be compared. Which type of malicious attack are these values associated with?

A.

W32/AutoRun worm

B.

HeartBleed SSL Bug

C.

Spectre Worm

D.

Eternal Blue Windows

Full Access
Question # 131

A financial services firm is concerned about employees inadvertently pasting sensitive customer account information into public generative AI websites. The security team needs to implement a solution that inspects outbound traffic and prevents the transmission of sensitive data to AI platforms. Which two configuration actions must the administrator perform on Cisco Secure Access to achieve the requirement? (Choose two.)

A.

Apply an AI Guardrail rule to block uploads to unauthorized AI domains.

B.

Implement a strict firewall rule to block all outbound traffic on port 443 for the entire organization.

C.

Disable all web-browser access for employees to prevent them from navigating to any external websites.

D.

Configure a DLP policy to inspect outbound traffic for sensitive data patterns.

E.

Enable the local endpoint firewall to block all traffic to known AI-service IP addresses.

Full Access
Question # 132

Which Cisco security solution determines if an endpoint has the latest OS updates and patches installed on the system?

A.

Cisco Endpoint Security Analytics

B.

Cisco AMP for Endpoints

C.

Endpoint Compliance Scanner

D.

Security Posture Assessment Service

Full Access
Question # 133

What is the purpose of the Cisco Endpoint loC feature?

A.

It provides stealth threat prevention.

B.

lt is a signature-based engine.

C.

lt is an incident response tool

D.

It provides precompromise detection.

Full Access
Question # 134

Refer to the exhibit.

Consider that any feature of DNS requests, such as the length off the domain name

and the number of subdomains, can be used to construct models of expected behavior to which

observed values can be compared. Which type of malicious attack are these values associated with?

A.

Spectre Worm

B.

Eternal Blue Windows

C.

Heartbleed SSL Bug

D.

W32/AutoRun worm

Full Access
Question # 135

Which protocol provides the strongest throughput performance when using Cisco AnyConnect VPN?

A.

TLSv1.2

B.

TLSv1.1

C.

BJTLSv1

D.

DTLSv1

Full Access
Question # 136

An engineer enabled SSL decryption for Cisco Umbrella intelligent proxy and needs to ensure that traffic is inspected without alerting end-users. Which action accomplishes this goal?

A.

Restrict access to only websites with trusted third-party signed certificates.

B.

Modify the user’s browser settings to suppress errors from Cisco Umbrella.

C.

Upload the organization root CA to Cisco Umbrella.

D.

Install the Cisco Umbrella root CA onto the user’s device.

Full Access
Question # 137

What are two differences between a Cisco WSA that is running in transparent mode and one running in explicit mode? (Choose two)

A.

The Cisco WSA responds with its own IP address only if it is running in explicit mode.

B.

The Cisco WSA is configured in a web browser only if it is running in transparent mode.

C.

The Cisco WSA responds with its own IP address only if it is running in transparent mode.

D.

The Cisco WSA uses a Layer 3 device to redirect traffic only if it is running in transparent mode.

E.

When the Cisco WSA is running in transparent mode, it uses the WSA ' s own IP address as the HTTP request destination.

Full Access
Question # 138

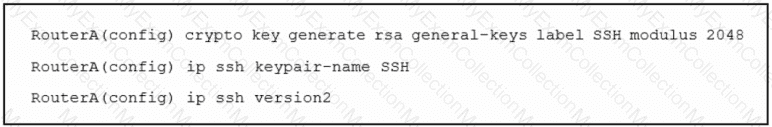
Refer to the exhibit. An engineer must enable secure SSH protocols and enters this configuration. What are two results of running this set of commands on a Cisco router? (Choose two.)

A.

Labels the key pair to be used for SSH

B.

Uses the FQDN with the label command

C.

Generates AES key pairs on the router

D.

Generates RSA key pair on the router

E.

Enables SSHv1 on the router

Full Access
Question # 139

Which two capabilities does an MDM provide? (Choose two.)

A.

delivery of network malware reports to an inbox in a schedule

B.

unified management of mobile devices, Macs, and PCs from a centralized dashboard

C.

enforcement of device security policies from a centralized dashboard

D.

manual identification and classification of client devices

E.

unified management of Android and Apple devices from a centralized dashboard

Full Access
Question # 140

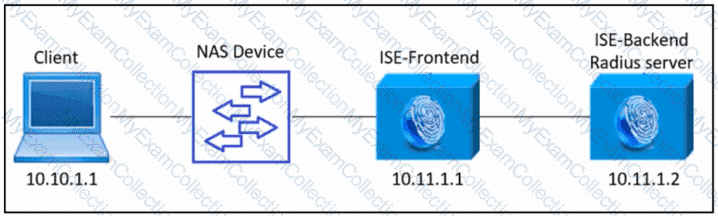
Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?

A.

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Full Access
Question # 141

Which type of dashboard does Cisco DNA Center provide for complete control of the network?

A.

service management

B.

centralized management

C.

application management

D.

distributed management

Full Access
Question # 142

Which IETF attribute is supported for the RADIUS CoA feature?

A.

24 State

B.

30 Calling-Station-ID

C.

42 Acct-Session-ID

D.

81 Message-Authenticator

Full Access
Question # 143

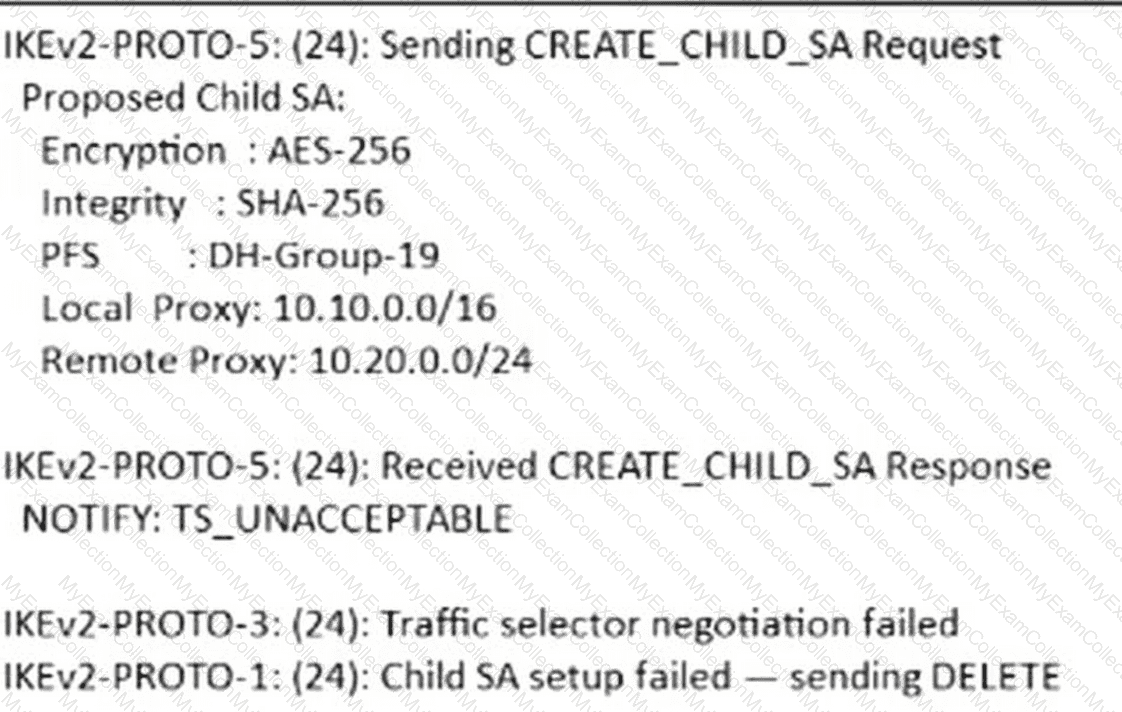
Refer to the exhibit.

A site-to-site IKEv2 VPN between two Cisco Secure Firewall Threat Defense devices at a healthcare organization completes IKE Phase 1 successfully but fails during CREATE_CHILD_SA. The engineer captures the debug output from the initiating Cisco Secure Firewall. Which action must be performed to resolve the issue?

A.

Align the protected network definitions on both firewalls so that the local and remote traffic selectors proposed during CREATE_CHILD_SA match on both peers.

B.

Change the IPsec encryption algorithm from AES-256 to AES-128 on the initiating firewall and redeploy the VPN policy.

C.

Extend the IKE SA lifetime on both firewalls to give CREATE_CHILD_SA sufficient time to complete the negotiation before the Phase 1 SA expires.

D.

Remove DH Group 19 from the IPsec proposal on the initiating FTD because the TS_UNACCEPTABLE notification indicates that the responder does not support the proposed PFS group.

Full Access
Question # 144

The Cisco ASA must support TLS proxy for encrypted Cisco Unified Communications traffic. Where must the

ASA be added on the Cisco UC Manager platform?

A.

Certificate Trust List

B.

Endpoint Trust List

C.

Enterprise Proxy Service

D.

Secured Collaboration Proxy

Full Access
Question # 145

Which attribute has the ability to change during the RADIUS CoA?

A.

NTP

B.

Authorization

C.

Accessibility

D.

Membership

Full Access
Question # 146

Why should organizations migrate to a multifactor authentication strategy?

A.

Multifactor authentication methods of authentication are never compromised

B.

Biometrics authentication leads to the need for multifactor authentication due to its ability to be hacked easily

C.

Multifactor authentication does not require any piece of evidence for an authentication mechanism

D.

Single methods of authentication can be compromised more easily than multifactor authentication

Full Access
Question # 147

Which Cisco product provides proactive endpoint protection and allows administrators to centrally manage the

deployment?

A.

NGFW

B.

AMP

C.

WSA

D.

ESA

Full Access
Question # 148

Cisco SensorBase gaihers threat information from a variety of Cisco products and services and performs analytics to find patterns on threats Which term describes this process?

A.

deployment

B.

consumption

C.

authoring

D.

sharing

Full Access
Question # 149

What must be used to share data between multiple security products?

A.

Cisco Rapid Threat Containment

B.

Cisco Platform Exchange Grid

C.

Cisco Advanced Malware Protection

D.

Cisco Stealthwatch Cloud

Full Access
Question # 150

An organization plans to upgrade its current email security solutions, and an engineer must deploy Cisco Secure Email. The requirements for the upgrade are:

Implement Data Loss Prevention

Implement mail encryption

Integrate with an existing Cisco IronPort Secure Email Gateway solution

Which Cisco Secure Email license is needed to accomplish this task?

A.

Cisco Secure Email Outbound Essentials

B.

Cisco Secure Email Phishing Defense

C.

Cisco Secure Email Domain Protection

D.

Cisco Secure Email Inbound Essentials

Full Access
Question # 151

What does Cisco AMP for Endpoints use to help an organization detect different families of malware?

A.

Ethos Engine to perform fuzzy fingerprinting

B.

Tetra Engine to detect malware when me endpoint is connected to the cloud

C.

Clam AV Engine to perform email scanning

D.

Spero Engine with machine learning to perform dynamic analysis

Full Access
Question # 152

A security engineer must configure a Splunk Universal Forwarder to send network traffic logs from Cisco Catalyst switches to a Splunk indexer cluster. Strict compliance requirements require all network traffic logs to be ingested into Splunk as an audit trail. The environment includes thousands of forwarders, and the data must be distributed across all indexers. Which two configuration actions must be performed? (Choose two.)

A.

Configure outputs.conf with the DNS names and indexing ports of all indexers within the cluster.

B.

Implement a large output queue in outputs.conf and disable automatic load balancing.

C.

Configure the forwarder to write logs to a local file share and schedule a batch job to copy the data into the indexers.

D.

Use a deployment server to push an application containing outputs.conf to all Universal Forwarders.

E.

Configure a single primary indexer in outputs.conf and enable a forced connection.

Full Access
Question # 153

Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?

(Choose two)

A.

Outgoing traffic is allowed so users can communicate with outside organizations.

B.

Malware infects the messenger application on the user endpoint to send company data.

C.

Traffic is encrypted, which prevents visibility on firewalls and IPS systems.

D.

An exposed API for the messaging platform is used to send large amounts of data.

E.

Messenger applications cannot be segmented with standard network controls

Full Access
Question # 154

A network engineer is deploying multiple Cisco Secure Firewall Threat Defense devices across two data centers. The solution has the following requirements:

    Management must have no Internet dependency.

    Management must remain accessible during major outages.

    Policy management must be centralized.

Which solution must be implemented to meet the requirements?

A.

Deploy an on-premises Cisco Secure Firewall Management Center high-availability pair with a dedicated out-of-band network.

B.

Deploy one Cisco Secure Firewall Management Center per data center with in-band network management.

C.

Use Cisco Security Cloud Control over the Internet with no on-premises managers.

D.

Manage each firewall locally with Cisco Secure Firewall Device Manager over the production network.

Full Access
Question # 155

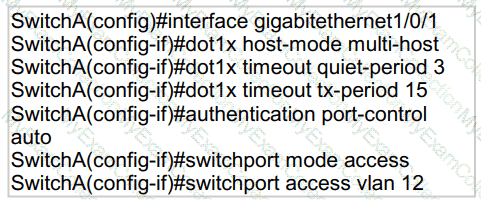
Refer to the exhibit.

An engineer configured wired 802.1x on the network and is unable to get a laptop to authenticate. Which port configuration is missing?

A.

authentication open

B.

dotlx reauthentication

C.

cisp enable

D.

dot1x pae authenticator

Full Access
Question # 156

Refer to the exhibit. The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

A.

P2 and P3 only

B.

P2, P3, and P6 only

C.

P5, P6, and P7 only

D.

P1, P2, P3, and P4 only

Full Access
Question # 157

An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?

A.

It is included m the license cost for the multi-org console of Cisco Umbrella

B.

It can grant third-party SIEM integrations write access to the S3 bucket

C.

No other applications except Cisco Umbrella can write to the S3 bucket

D.

Data can be stored offline for 30 days.

Full Access
Question # 158

An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to

prevent the session during the initial TCP communication?

A.

Configure the Cisco ESA to drop the malicious emails

B.

Configure policies to quarantine malicious emails

C.

Configure policies to stop and reject communication

D.

Configure the Cisco ESA to reset the TCP connection

Full Access
Question # 159

An engineer must force an endpoint to re-authenticate an already authenticated session without disrupting the

endpoint to apply a new or updated policy from ISE. Which CoA type achieves this goal?

A.

Port Bounce

B.

CoA Terminate

C.

CoA Reauth

D.

CoA Session Query

Full Access
Question # 160

An MDM provides which two advantages to an organization with regards to device management? (Choose two)

A.

asset inventory management

B.

allowed application management

C.

Active Directory group policy management

D.

network device management

E.

critical device management

Full Access
Question # 161

An engineer is configuring IPsec VPN and needs an authentication protocol that is reliable and supports ACK

and sequence. Which protocol accomplishes this goal?

A.

AES-192

B.

IKEv1

C.

AES-256

D.

ESP

Full Access
Question # 162

The main function of northbound APIs in the SDN architecture is to enable communication between which two areas of a network?

A.

SDN controller and the cloud

B.

management console and the SDN controller

C.

management console and the cloud

D.

SDN controller and the management solution

Full Access
Question # 163

Email security has become a high priority task for a security engineer at a large multi-national organization due to ongoing phishing campaigns. To help control this, the engineer has deployed an Incoming Content Filter with a URL reputation of (-10 00 to -6 00) on the Cisco ESA Which action will the system perform to disable any links in messages that match the filter?

A.

Defang

B.

Quarantine

C.

FilterAction

D.

ScreenAction

Full Access
Question # 164

In a PaaS model, which layer is the tenant responsible for maintaining and patching?

A.

hypervisor

B.

virtual machine

C.

network

D.

application

Full Access
Question # 165

What is a characteristic of Dynamic ARP Inspection?

A.

DAI determines the validity of an ARP packet based on valid IP to MAC address bindings from the DHCPsnooping binding database.

B.

In a typical network, make all ports as trusted except for the ports connecting to switches, which areuntrusted

C.

DAI associates a trust state with each switch.

D.

DAI intercepts all ARP requests and responses on trusted ports only.

Full Access
Question # 166

Which cloud service model offers an environment for cloud consumers to develop and deploy applications

without needing to manage or maintain the underlying cloud infrastructure?

A.

PaaS

B.

XaaS

C.

IaaS

D.

SaaS

Full Access
Question # 167

Which Cisco security solution gives the most complete view of the relationships and evolution of Internet domains IPs, and flies, and helps to pinpoint attackers ' infrastructures and predict future threat?

A.

Cisco Secure Network Analytics

B.

Cisco Secure Cloud Analytics

C.

Cisco Umbrella Investigate

D.

Cisco pxGrid

Full Access
Question # 168

A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?

A.

Configure the Calling-Station-ID attribute for CoA session identification.

B.

Apply the Message-Authenticator attribute for endpoint session lookup.

C.

Implement the Acct-Session-ID attribute for matching the active session.

D.

Use the NAS-Port-ID attribute for the CoA disconnect request.

Full Access
Question # 169

An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.

The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of

certificate should be presented to the end-user to accomplish this goal?

A.

third-party

B.

self-signed

C.

organization owned root

D.

SubCA

Full Access
Question # 170

An engineer is configuring device-hardening on a router in order to prevent credentials from being seen

if the router configuration was compromised. Which command should be used?

A.

service password-encryption

B.

username < username > privilege 15 password < password >

C.

service password-recovery

D.

username < username > password < password >

Full Access
Question # 171

What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?
A.

mobile device management

B.

mobile content management

C.

mobile application management

D.

mobile access management

Full Access
Question # 172

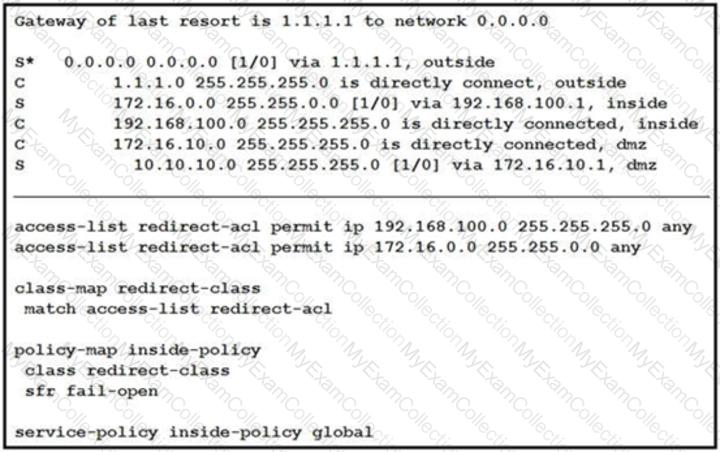
Refer to the exhibit.

What is a result of the configuration?

A.

Traffic from the DMZ network is redirected

B.

Traffic from the inside network is redirected

C.

All TCP traffic is redirected

D.

Traffic from the inside and DMZ networks is redirected

Full Access
Question # 173

Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?

A.

Configure an advanced custom detection list.

B.

Configure an IP Block & Allow custom detection list

C.

Configure an application custom detection list

D.

Configure a simple custom detection list

Full Access
Question # 174

Elliptic curve cryptography is a stronger more efficient cryptography method meant to replace which current

encryption technology?

A.

3DES

B.

RSA

C.

DES

D.

AES

Full Access
Question # 175

Why is it important to have logical security controls on endpoints even though the users are trained to spot security threats and the network devices already help prevent them?

A.

to prevent theft of the endpoints

B.

because defense-in-depth stops at the network

C.

to expose the endpoint to more threats

D.

because human error or insider threats will still exist

Full Access
Question # 176

A network engineer is trying to figure out whether FlexVPN or DMVPN would fit better in their environment.

They have a requirement for more stringent security multiple security associations for the connections, more efficient VPN establishment as well consuming less bandwidth. Which solution would be best for this and why?

A.

DMVPN because it supports IKEv2 and FlexVPN does not

B.

FlexVPN because it supports IKEv2 and DMVPN does not

C.

FlexVPN because it uses multiple SAs and DMVPN does not

D.

DMVPN because it uses multiple SAs and FlexVPN does not

Full Access
Question # 177

What is a benefit of conducting device compliance checks?

A.

It indicates what type of operating system is connecting to the network.

B.

It validates if anti-virus software is installed.

C.

It scans endpoints to determine if malicious activity is taking place.

D.

It detects email phishing attacks.

Full Access
Question # 178

Drag and drop the security solutions from the left onto the benefits they provide on the right.
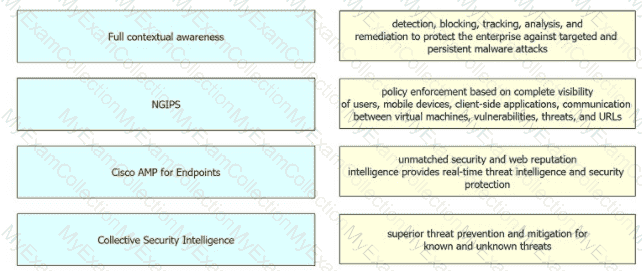
Full Access
Question # 179

What is a required prerequisite to enable malware file scanning for the Secure Internet Gateway?

A.

Enable IP Layer enforcement.

B.

Activate the Advanced Malware Protection license

C.

Activate SSL decryption.

D.

Enable Intelligent Proxy.

Full Access
Question # 180

Which solution stops unauthorized access to the system if a user ' s password is compromised?

A.

VPN

B.

MFA

C.

AMP

D.

SSL

Full Access
Question # 181

Refer to the exhibit.

What will happen when the Python script is executed?

A.

The hostname will be translated to an IP address and printed.

B.

The hostname will be printed for the client in the client ID field.

C.

The script will pull all computer hostnames and print them.

D.

The script will translate the IP address to FODN and print it

Full Access
Question # 182

Which type of attack is MFA an effective deterrent for?

A.

ping of death

B.

phishing

C.

teardrop

D.

syn flood

Full Access
Question # 183

What is a function of 3DES in reference to cryptography?

A.

It hashes files.

B.

It creates one-time use passwords.

C.

It encrypts traffic.

D.

It generates private keys.

Full Access
Question # 184

What is the purpose of the Decrypt for Application Detection feature within the WSA Decryption options?

A.

It decrypts HTTPS application traffic for unauthenticated users.

B.

It alerts users when the WSA decrypts their traffic.

C.

It decrypts HTTPS application traffic for authenticated users.

D.

It provides enhanced HTTPS application detection for AsyncOS.

Full Access
Question # 185

An administrator needs to configure the Cisco ASA via ASDM such that the network management system

can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?

(Choose two.)

A.

Specify the SNMP manager and UDP port.

B.

Specify an SNMP user group

C.

Specify a community string.

D.

Add an SNMP USM entry

E.

Add an SNMP host access entry

Full Access
Question # 186

Refer to the exhibit.

What does the API do when connected to a Cisco security appliance?

A.

get the process and PID information from the computers in the network

B.

create an SNMP pull mechanism for managing AMP

C.

gather network telemetry information from AMP for endpoints

D.

gather the network interface information about the computers AMP sees

Full Access
Question # 187

An organization is using DNS services for their network and want to help improve the security of the DNS infrastructure. Which action accomplishes this task?

A.

Use DNSSEC between the endpoints and Cisco Umbrella DNS servers.

B.

Modify the Cisco Umbrella configuration to pass queries only to non-DNSSEC capable zones.

C.

Integrate Cisco Umbrella with Cisco CloudLock to ensure that DNSSEC is functional.

D.

Configure Cisco Umbrella and use DNSSEC for domain authentication to authoritative servers.

Full Access
Question # 188

What is the concept of Cl/CD pipelining?

A.

The project is split into several phases where one phase cannot start before the previous phase finishes successfully.

B.

The project code is centrally maintained and each code change should trigger an automated build and test sequence

C.

The project is split into time-limited cycles and focuses on pair programming for continuous code review

D.

Each project phase is independent from other phases to maintain adaptiveness and continual improvement

Full Access
Question # 189

An engineer is configuring 802.1X authentication on Cisco switches in the network and is using CoA as a mechanism. Which port on the firewall must be opened to allow the CoA traffic to traverse the network?

A.

TCP 6514

B.

UDP 1700

C.

TCP 49

D.

UDP 1812

Full Access
Question # 190

Which API technology with SDN architecture is used to communicate with a controller and network devices such as routers and switches?

A.

REST APIs

B.

Northbound APIs

C.

Unprotected APIs

D.

Southbound APIs

Full Access
Question # 191

Which type of encryption uses a public key and private key?

A.

Asymmetric

B.

Symmetric

C.

Linear

D.

Nonlinear

Full Access
Question # 192

How does Cisco Advanced Phishing Protection protect users?

A.

It validates the sender by using DKIM.

B.

It determines which identities are perceived by the sender

C.

It utilizes sensors that send messages securely.

D.

It uses machine learning and real-time behavior analytics.

Full Access
Question # 193

An engineer is configuring AMP for endpoints and wants to block certain files from executing. Which outbreak

control method is used to accomplish this task?

A.

device flow correlation

B.

simple detections

C.

application blocking list

D.

advanced custom detections

Full Access
Question # 194

Which information is required when adding a device to Firepower Management Center?

A.

username and password

B.

encryption method

C.

device serial number

D.

registration key

Full Access
Question # 195

With which components does a southbound API within a software-defined network architecture communicate?
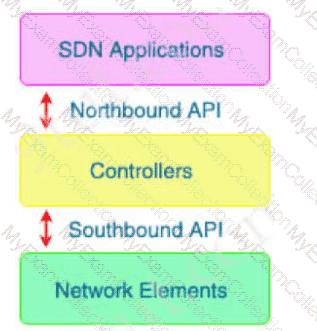
A.

controllers within the network

B.

applications

C.

appliances

D.

devices such as routers and switches

Full Access
Question # 196

Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?

A.

SIG Advantage

B.

DNS Security Essentials

C.

SIG Essentials

D.

DNS Security Advantage

Full Access
Question # 197

A Cisco FTD engineer is creating a new IKEv2 policy called s2s00123456789 for their organization to allow for additional protocols to terminate network devices with. They currently only have one policy established and need the new policy to be a backup in case some devices cannot support the stronger algorithms listed in the primary policy. What should be done in order to support this?

A.

Change the integrity algorithms to SHA* to support all SHA algorithms in the primary policy

B.

Make the priority for the new policy 5 and the primary policy 1

C.

Change the encryption to AES* to support all AES algorithms in the primary policy

D.

Make the priority for the primary policy 10 and the new policy 1

Full Access
Question # 198

What is a benefit of flexible NetFlow records?

A.

They are used for security

B.

They are used for accounting

C.

They monitor a packet from Layer 2 to Layer 5

D.

They have customized traffic identification

Full Access
Question # 199

Which CLI command is used to register a Cisco FirePower sensor to Firepower Management Center?

A.

configure system add < host > < key >

B.

configure manager < key > add host

C.

configure manager delete

D.

configure manager add < host > < key

Full Access
Question # 200

Which Cisco AMP feature allows an engineer to look back to trace past activities, such as file and process

activity on an endpoint?

A.

endpoint isolation

B.

advanced search

C.

advanced investigation

D.

retrospective security

Full Access
Question # 201

An engineer notices traffic interruption on the network. Upon further investigation, it is learned that broadcast

packets have been flooding the network. What must be configured, based on a predefined threshold, to

address this issue?

A.

Bridge Protocol Data Unit guard

B.

embedded event monitoring

C.

storm control

D.

access control lists

Full Access
Question # 202

Refer to the exhibit.

What conclusion should an administrator draw about the URL malicious-domain-example.com?

A.

The domain is blocked solely because it is newly registered, regardless of the Threat Score.

B.

The domain is a legacy site that has been compromised, as indicated by its domain age.

C.

The domain is safe because its Security Score is 25/100.

D.

The high Threat Score together with DNS tunneling, malware hosting, and DGA indicators shows active malicious behavior.

Full Access
Question # 203

Which license is required for Cisco Security Intelligence to work on the Cisco Next Generation Intrusion

Prevention System?

A.

control

B.

malware

C.

URL filtering

D.

protect

Full Access
Question # 204

Drag and drop the deployment models from the left onto the explanations on the right.
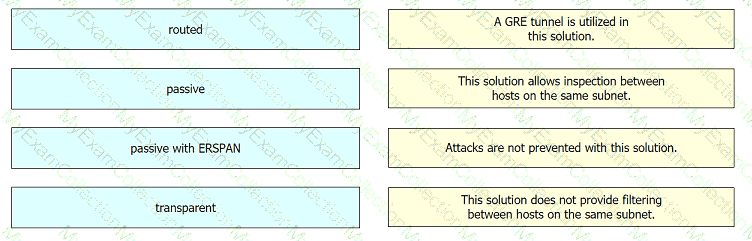
Full Access
Question # 205

What is a characteristic of traffic storm control behavior?

A.

Traffic storm control drops all broadcast and multicast traffic if the combined traffic exceeds the level withinthe interval.

B.

Traffic storm control cannot determine if the packet is unicast or broadcast.

C.

Traffic storm control monitors incoming traffic levels over a 10-second traffic storm control interval.

D.

Traffic storm control uses the Individual/Group bit in the packet source address to determine if the packet isunicast or broadcast.

Full Access
Question # 206

A network engineer is configuring NetFlow top talkers on a Cisco router Drag and drop the steps in the process from the left into the sequence on the right
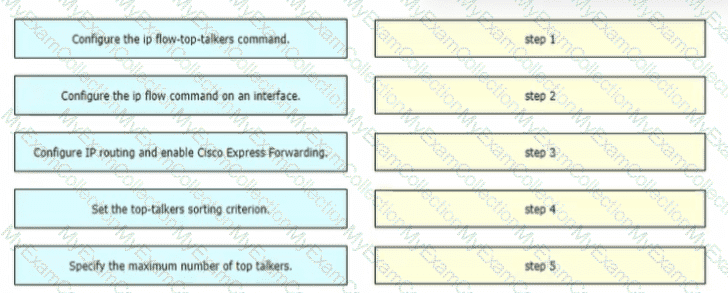
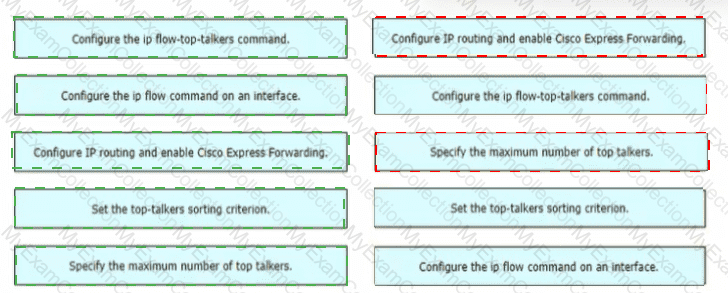
Full Access
Question # 207

Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?

A.

Policy Name: Default Policy  Sender: usera1@example.com  Recipient: @cisco.com

B.

Policy Name: usera1 policy  Sender: usera1@example.com  Recipient: @cisco.com

C.

Policy Name: Anti-Malware policy  Sender: usera1@example.com  Recipient: @cisco.com

D.

Policy Name: cisco.com policy  Sender: usera1@example.com  Recipient: @cisco.com

Full Access
Question # 208

Drag and drop the Firepower Next Generation Intrusion Prevention System detectors from the left onto the correct definitions on the right.
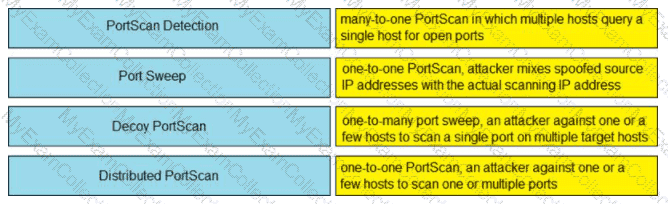
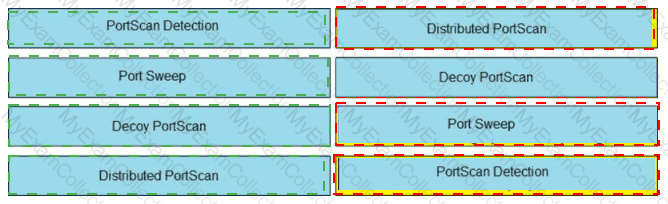
Full Access
Question # 209

An engineer wants to generate NetFlow records on traffic traversing the Cisco ASA. Which Cisco ASA

command must be used?

A.

flow-export destination inside 1.1.1.1 2055

B.

ip flow monitor input

C.

ip flow-export destination 1.1.1.1 2055

D.

flow exporter

Full Access
Question # 210

A hacker initiated a social engineering attack and stole username and passwords of some users within a company. Which product should be used as a solution to this problem?

A.

Cisco NGFW

B.

Cisco AnyConnect

C.

Cisco AMP for Endpoints

D.

Cisco Duo

Full Access
Question # 211

Drag and drop the steps from the left into the correct order on the right to enable AppDynamics to monitor an EC2 instance in Amazon Web Services.
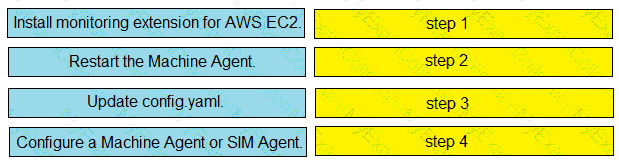
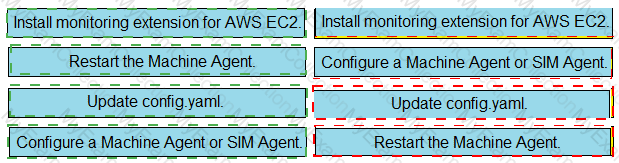
Full Access
Question # 212

Which technology is used to improve web traffic performance by proxy caching?

A.

WSA

B.

Firepower

C.

FireSIGHT

D.

ASA

Full Access
Question # 213

An organization wants to provide visibility and to identify active threats in its network using a VM. The

organization wants to extract metadata from network packet flow while ensuring that payloads are not retained

or transferred outside the network. Which solution meets these requirements?

A.

Cisco Umbrella Cloud

B.

Cisco Stealthwatch Cloud PNM

C.

Cisco Stealthwatch Cloud PCM

D.

Cisco Umbrella On-Premises

Full Access
Question # 214

What is the function of SDN southbound API protocols?

A.

to allow for the dynamic configuration of control plane applications

B.

to enable the controller to make changes

C.

to enable the controller to use REST

D.

to allow for the static configuration of control plane applications

Full Access
Question # 215

Which functions of an SDN architecture require southbound APIs to enable communication?

A.

SDN controller and the network elements

B.

management console and the SDN controller

C.

management console and the cloud

D.

SDN controller and the cloud

Full Access
Question # 216

Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?

A.

CMP

B.

SCEP

C.

SFTP

D.

OCSP

Full Access
Question # 217

Which statement describes a serverless application?

A.

The application delivery controller in front of the server farm designates on which server the application runs each time.

B.

The application runs from an ephemeral, event-triggered, and stateless container that is fully managed by a cloud provider.

C.

The application is installed on network equipment and not on physical servers.

D.

The application runs from a containerized environment that is managed by Kubernetes or Docker Swarm.

Full Access
Question # 218

An engineer is configuring Cisco WSA and needs to deploy it in transparent mode. Which configuration component must be used to accomplish this goal?

A.

MDA on the router

B.

PBR on Cisco WSA

C.

WCCP on switch

D.

DNS resolution on Cisco WSA

Full Access
Question # 219

Which feature must be configured before implementing NetFlow on a router?

A.

SNMPv3

B.

syslog

C.

VRF

D.

IP routing

Full Access
Question # 220

What is an advantage of network telemetry over SNMP pulls?

A.

accuracy

B.

encapsulation

C.

security

D.

scalability

Full Access
Question # 221

What is a benefit of a Cisco Secure Email Gateway Virtual as compared to a physical Secure Email Gateway?

A.

simplifies the distribution of software updates

B.

provides faster performance

C.

provides an automated setup process

D.

enables the allocation of additional resources

Full Access
Question # 222

An organization wants to secure data in a cloud environment. Its security model requires that all users be

authenticated and authorized. Security configuration and posture must be continuously validated before access is granted or maintained to applications and data. There is also a need to allow certain application traffic and deny all other traffic by default. Which technology must be used to implement these requirements?

A.

Virtual routing and forwarding

B.

Microsegmentation

C.

Access control policy

D.

Virtual LAN

Full Access
Question # 223

Refer to the exhibit.

A threat analyst is investigating the domain federatedplantmesh.garden after it appeared in DNS logs from several roaming users. In the Cisco Secure Access Investigate dashboard, the analyst notes that several individual indicators, including Lexical, TLD, and Geo Popularity, are not strongly elevated, yet the overall Risk Score is 100. What is occurring?

A.

The overall score of 100 is inconsistent and likely a dashboard-rendering error; the domain must be queried again before the classification is trusted.

B.

The infrastructure fields are blank, but the Umbrella Block Status of 100/100 and the malware security category identify the non-resolving domain as high risk.

C.

The Keyword Score of 83 is the only elevated indicator driving the overall score, and the classification is invalid unless confirmed through the Dispute Categorization link.

D.

The Dispute Categorization link means that the malware classification is contested, and the blank IP and ASN fields confirm that the domain has no active threat infrastructure.

Full Access
Question # 224

Which form of attack is launched using botnets?

A.

EIDDOS

B.

virus

C.

DDOS

D.

TCP flood

Full Access
Question # 225

Which solution combines Cisco IOS and IOS XE components to enable administrators to recognize

applications, collect and send network metrics to Cisco Prime and other third-party management tools, and prioritize application traffic?

A.

Cisco Security Intelligence

B.

Cisco Application Visibility and Control

C.

Cisco Model Driven Telemetry

D.

Cisco DNA Center

Full Access
Question # 226

A company deploys an application that contains confidential data and has a hybrid hub-and-spoke topology. The hub resides in a public cloud environment, and the spoke resides on-premises. An engineer must secure the application to ensure that confidential data in transit between the hub-and-spoke servers is accessible only to authorized users. The engineer performs these configurations:

Segregation of duties

Role-based access control

Privileged access management

What must be implemented to protect the data in transit?

A.

MD5

B.

AES-256

C.

SHA-512

D.

TLS 1.3

Full Access
Question # 227

What is a benefit of using Cisco CWS compared to an on-premises Cisco WSA?

A.

Cisco CWS eliminates the need to backhaul traffic through headquarters for remote workers whereas Cisco WSA does not

B.

Cisco CWS minimizes the load on the internal network and security infrastructure as compared to Cisco WSA.

C.

URL categories are updated more frequently on Cisco CWS than they are on Cisco WSA

D.

Content scanning for SAAS cloud applications is available through Cisco CWS and not available through Cisco WSA

Full Access
Question # 228

Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)

A.

Cisco Umbrella

B.

Cisco ISE

C.

Cisco DNA Center

D.

Cisco TrustSec

E.

Cisco Duo Security

Full Access
Question # 229

Drag and drop the cryptographic algorithms for IPsec from the left onto the cryptographic processes on the right.
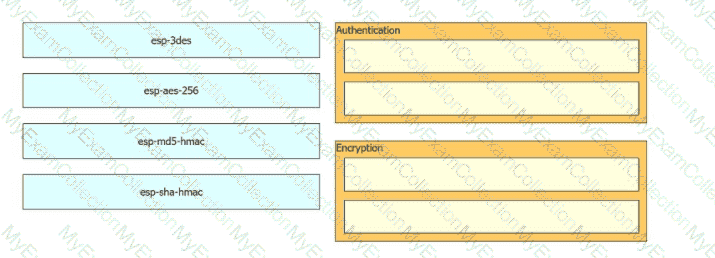
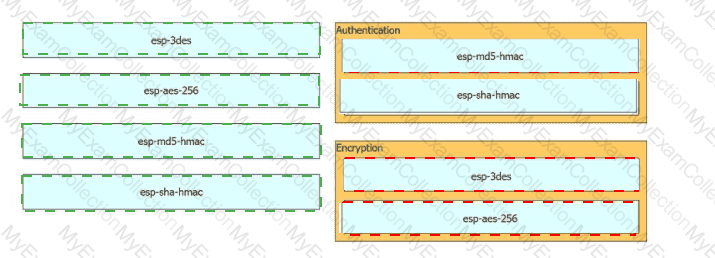
Full Access
Question # 230

An engineer is adding a Cisco DUO solution to the current TACACS+ deployment using Cisco ISE. The engineer wants to authenticate users using their account when they log into network devices. Which action accomplishes this task?

A.

Configure Cisco DUO with the external Active Directory connector and tie it to the policy set within Cisco ISE.

B.

Install and configure the Cisco DUO Authentication Proxy and configure the identity source sequence within Cisco ISE

C.

Create an identity policy within Cisco ISE to send all authentication requests to Cisco DUO.

D.

Modify the current policy with the condition MFASourceSequence DUO=true in the authorization conditions within Cisco ISE

Full Access
Question # 231

What is a feature of NetFlow Secure Event Logging?

A.

It exports only records that indicate significant events in a flow.

B.

It filters NSEL events based on the traffic and event type through RSVP.

C.

It delivers data records to NSEL collectors through NetFlow over TCP only.

D.

It supports v5 and v8 templates.

Full Access
Question # 232

Which type of attack is social engineering?

A.

trojan

B.

phishing

C.

malware

D.

MITM

Full Access
Question # 233

Which statement about the configuration of Cisco ASA NetFlow v9 Secure Event Logging is true?

A.

To view bandwidth usage for NetFlow records, the QoS feature must be enabled.

B.

A sysopt command can be used to enable NSEL on a specific interface.

C.

NSEL can be used without a collector configured.

D.

A flow-export event type must be defined under a policy

Full Access
Question # 234

Which feature within Cisco ISE verifies the compliance of an endpoint before providing access to the

network?

A.

Posture

B.

Profiling

C.

pxGrid

D.

MAB

Full Access
Question # 235

What are the two most commonly used authentication factors in multifactor authentication? (Choose two)

A.

biometric factor

B.

time factor

C.

confidentiality factor

D.

knowledge factor

E.

encryption factor

Full Access
Question # 236

Which Splunk SOAR component automates multi-step security actions into a repeatable workflow?

A.

Alert

B.

Action

C.

Data model

D.

Playbook

Full Access
Question # 237

Which security product enables administrators to deploy Kubernetes clusters in air-gapped sites without needing Internet access?

A.

Cisco Content Platform

B.

Cisco Container Controller

C.

Cisco Container Platform

D.

Cisco Cloud Platform

Full Access
Question # 238

What is a feature of an endpoint detection and response solution?

A.

Preventing attacks by identifying harmful events with machine learning and conduct-based defense

B.

Rapidly and consistently observing and examining data to mitigate threats

C.

Capturing and clarifying data on email, endpoints, and servers to mitigate threats

D.

Ensuring the security of network devices by choosing which devices are allowed to reach the network

Full Access
Question # 239

An administrator is adding a new Cisco ISE node to an existing deployment. What must be done to ensure that the addition of the node will be successful when inputting the FQDN?

A.

Change the IP address of the new Cisco ISE node to the same network as the others.

B.

Make the new Cisco ISE node a secondary PAN before registering it with the primary.

C.

Open port 8905 on the firewall between the Cisco ISE nodes

D.

Add the DNS entry for the new Cisco ISE node into the DNS server

Full Access
Question # 240

What Cisco command shows you the status of an 802.1X connection on interface gi0/1?
A.

show authorization status

B.

show authen sess int gi0/1

C.

show connection status gi0/1

D.

show ver gi0/1

Full Access