

Question # 6
You need to filter the websites that employees can access on the company network.
Which type of device should you deploy?
Question # 7
A restaurant installs a second wireless router that only employees can use.
Which statement describes how to securely configure the new router?
Question # 10
An employee accidentally sends an email containing sensitive corporate information to an external email address.
Which type of threat does this scenario describe?
Question # 11
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
Question # 12
A client cannot connect to the corporate web server. You discover a large number of half-open TCP connections to the server.
What should you do?
Question # 13
Several employees complain that the company intranet site is no longer accepting their login information. You attempt to connect using the URL and notice some misspellings on the site. When you connect using the IP address, the site functions normally.
What should you do?
Question # 14
Several employees report that the company intranet website is no longer accepting their login credentials.
You attempt to access the site using its URL and notice several misspellings on the webpage. However, when you access the site directly using its IP address, it functions normally.
What should you do?
Question # 15
Which two private IPv4 addresses should be blocked from being routed across the public Internet to prevent security and performance issues? (Choose two.)
Note: You will receive partial credit for each correct selection.
Question # 16
A security assessment showed that a system administrator accessed files outside of normal working hours. The assessment listed the commands the administrator executed and indicated how long the administrator was connected to the system.
Which AAA component does this represent?
Question # 17
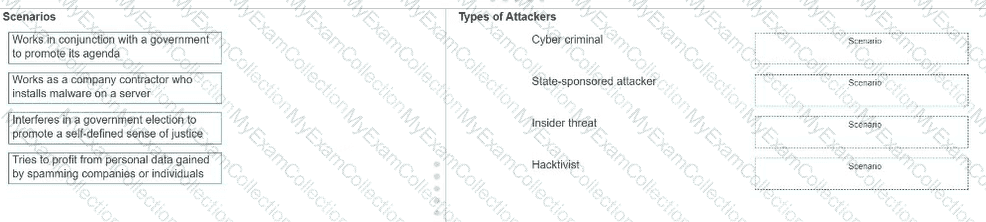
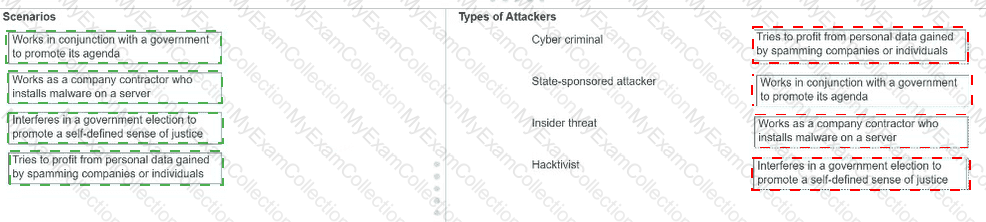
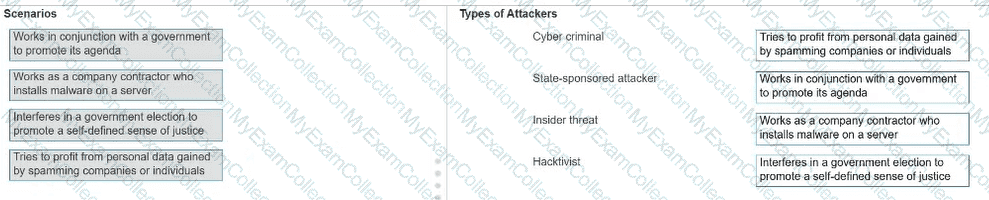
Move each scenario from the list on the left to the correct type of attacker on the right.
Note: You will receive partial credit for each correct answer.
Question # 18
Which security measure can prevent unauthorized devices from automatically connecting to a corporate network through unused switch ports?
Question # 19
An administrator wants to ensure that any files downloaded from the internet are automatically scanned for malicious code before execution. Which security control should be implemented?
Question # 20
A SOC analyst notices repeated failed login attempts from a foreign IP address followed by a successful login to a privileged account. What is the most appropriate next step?

