Question # 5
Exhibit:
module " network " {
source = " terraform-google-modules/network/google "
version = " ~ > 11.0 "
}
What version of the source module does Terraform allow with the module block shown in the exhibit?
Question # 7
Which are advantages of IaC (Infrastructure as Code) patterns instead of manual infrastructure management?
Pick the 2 correct responses below.
Question # 8
You can define multiple backend blocks in your Terraform configuration to store your state in multiple locations.
Question # 9
Before you can use a remote backend, you must first execute terra-form init.
Question # 11
Which provider authentication method prevents credentials from being stored in the state file?
Question # 12
You have a list of numbers that represents the number of free CPU cores on each virtual cluster:
numcpus = [ 18, 3, 7, 11, 2 ]
What Terraform function could you use to select the largest number from the list?
Question # 14
You use a cloud provider account that is shared with other team members. You previously used Terraform to create a load balancer that listens on port 80. After application changes, you updated the Terraform code to change the port to 443.
You run terraform plan and see that the execution plan shows the port changing from 80 to 443 like you intended and step away to grab some coffee.
In the meantime, another team member manually changes the load balancer port to 443 through the cloud provider console before you get back to your desk.
What will happen when you run terraform apply upon returning to your desk?
Question # 16
Your risk management organization requires that new AWS S3 buckets must be private and encrypted at rest. How can Terraform Cloud automatically and proactively enforce this security control?
Question # 17
You have set the TF_LOG_PATH environment variable for Terraform, and you would like to ensure the logs contain all debug-level messages and verbose process logs.
Which action should you take?
Question # 18
You ate making changes to existing Terraform code to add some new infrastructure. When is the best time to run terraform validate?
Question # 20
Which of the following locations can Terraform use as aprivate sourcefor modules?(Pick 2 correct responses)
Question # 21
You have provisioned some virtual machines (VMs) on Google Cloud Platform (GCP) using the gcloud command line tool. However, you are standardizing with Terraform and want to manage these VMs using Terraform instead. What are the two things you must do to achieve this? Choose two correct answers.
Question # 22
terraform validate uses provider APIs to verify your infrastructure settings.
Question # 24
Which of these ate secure options for storing secrets for connecting to a Terraform remote backend? Choose two correct answers.
Question # 25
After creating a new Terraform configuration, your configuration passes terraform validate but returns an “Access Denied†error from the cloud provider when running terraform plan.
Why did terraform validate not catch this issue?
Question # 26
A provider configuration block is required in every Terraform configuration.
Example:
Question # 27
You ' ve used Terraform to deploy a virtual machine and a database. You want to replace this virtual machine instance with an identical one without affecting the database. What is the best way to achieve this using Terraform?
Question # 28
The exhibit below shows part of a Terraform configuration you have been asked to update. The name of the Azure Virtual Network should be set to the name of the resource group followed by a dash and the word vnet.
Exhibit:
data " azurerm_resource_group " " example " {
name = var.resource_group_name
}
resource " azurerm_virtual_network " " example " {
name = ______________________
}
Which expression fulfills this requirement?
Question # 30
You want to know from which paths Terraform is loading providers referenced in your Terraform configuration (* files). You need to enable additional logging messages to find this out. Which of the following would achieve this?
Question # 31
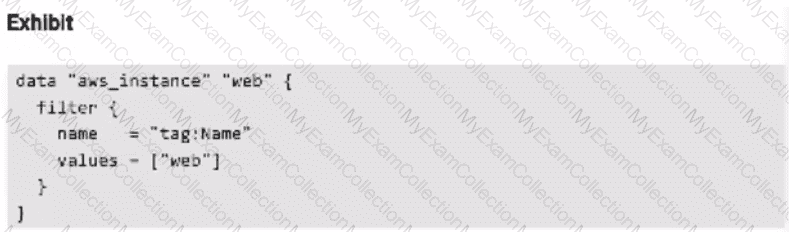
The Terraform configuration shown in the Exhibit space on this page v/ill create a new AWS instance.
Question # 34
Which is the best way to specify a tag of v1.0.0 when referencing a module stored in Git (for example.
Git::https://example.com/vpc.git)?
Question # 35
You have a simple Terraform configuration containing one virtual machine (VM) in a cloud provider. You run terraform apply and the VM is created successfully.
What will happen if you delete the VM using the cloud provider console, then run terraform apply again without changing any Terraform code?
Question # 36
A resource block is shown in the Exhibit space of this page. What is the Terraform resource name of that resource block?
Question # 37
Which type of information does the Terraform Registry provide about the modules it hosts?
Question # 38
When using multiple configurations of the same Terraform provider, what meta-argument must you include in any non-default provider configurations?
Question # 39
You can configure Terraform to log to a file using the TF_LOG environment variable.
Question # 40
You are tasked with making a change to an infrastructure stack running in a public cloud using HCP Terraform/Terraform Cloud. Which pattern follows IaC best practices?
Question # 41
Which of the following module source paths does not specify a remote module?
Question # 42
You want to create a string that combines a generated random_id and a variable and reuse that string several times in your configuration. What is the simplest correct way to implement this without repeating the random_id and variable?
Question # 44
The HCP Terraform private registry keeps the module configurations confidential within your organization.
Question # 46
When a check block’s assertion fails, Terraform blocks the current operation from executing.
Question # 47
Which option cannot be used to keep secrets out of Terraform configuration files?
Question # 48
You corrected a typo in a resource name, changing it from aws_s3_bucket.photoes to aws_s3_bucket.photos. You want to update the Terraform state so that the existing resource is recognized under the new name, without destroying and recreating it. Which configuration should you use?
Question # 49
You have a simple Terraform configuration containing one virtual machine (VM) in a cloud provider. You run terraform apply and the VM is created successfully. What will happen if you terraform apply again immediately afterward without changing any Terraform code?
Question # 50
How does the use of Infrastructure as Code (IaC) enhance the reliability of your infrastructure?
Pick the two correct responses below.
Question # 51
What does Terraform not reference when running a terraform apply -refresh-only ?
Question # 53
Exhibit:
data " aws_ami " " web " {
most_recent = true
owners = [ " self " ]
tags = {
Name = " web-server "
}
}
A data source is shown in the exhibit. How do you reference the id attribute of this data source?
Question # 55
A Terraform configuration returns errors when you run terraform plan. How would you enable debug logging to investigate further?
Question # 57
You can reference a resource created with for_each using a Splat ( *) expression.
Question # 58
terraform apply is failing with the following error. What next step should you take to determine the root cause of the problem?
Error:
yaml
CopyEdit
Error loading state: AccessDenied: Access Denied
status code: 403, request id: 288766CE5CCA24A0, host id: web.example.com
Question # 59
Which of the following does HCP Terraform perform during a health assessment for a workspace?
Pick the 2 correct responses below:
Question # 60
Which parameters does terraform import require? Choose two correct answers.
Question # 61
When using multiple configuration of the same Terraform provider, what meta-argument must you include in any non-default provider configurations?
Question # 62
One cloud block always maps to a single HCP Terraform/Terraform Cloud workspace.
Question # 63
You just upgraded the version of a provider in an existing Terraform project. What do you need to do to install the new provider?
Question # 64
What kind of configuration block will manage an infrastructure object with settings specified within the block?
Question # 65
If you update the version constraint in your Terraform configuration, Terraform will update your lock file the next time you run terraform Init.
Question # 66
When using Terraform to deploy resources into Azure, which scenarios are true regarding state files? (Choose two.)
Question # 69
Which argument can you set on a module block to prevent Terraform from updating the module’s configuration during an init or get operation?
Question # 71
Terraform stores the value of an output in its state file, even if the sensitive argument is set to true.
Question # 72
You have created a main.tf Terraform configuration consisting of an application server, a database and a load balanced. You ran terraform apply and Terraform created all of the resources successfully.
Now you realize that you do not actually need the load balancer, so you run terraform destroy without any flags. What will happen?
Question # 74
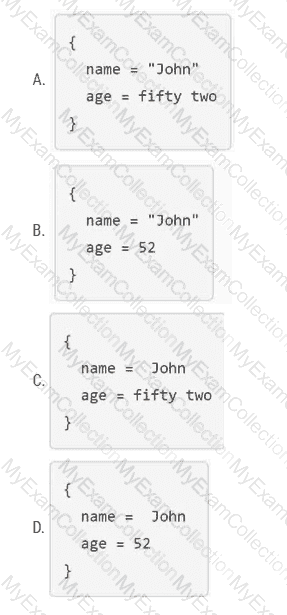
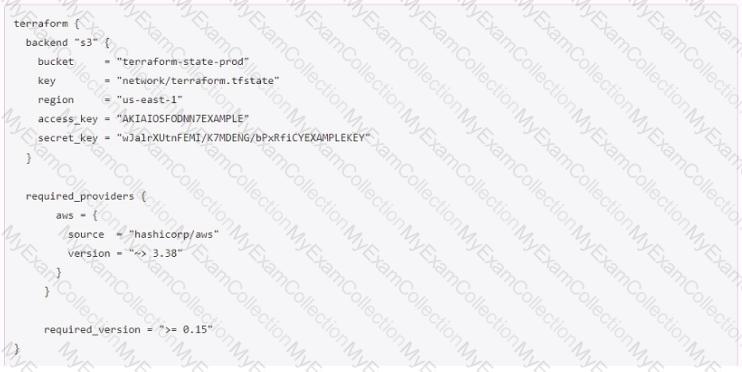
In Terraform HCL, an object type of object({name=string, age-number}) would match this value.
Question # 80
You want to bring an existing database under Terraform management. What information is required to create a new import block for the database?
Pick the two correct responses below.
Question # 82
Running terraform fmt without any flags in a directory with Terraform configuration files check the formatting of those files without changing their contents.
Question # 85
When you use a backend that requires authentication, it is best practice to:
Question # 86
You have a simple Terraform configuration containing one VM (virtual machine) in a cloud provider. You run terraform apply and the VM is created successfully. What will happen if you run terraform apply again immediately afterwards without changing any Terraform code?
Question # 88
You have never used Terraform before and would like to test it out using a shared team account for a cloud provider. The shared team account already contains 15 virtual machines (VM). You develop a Terraform configuration containing one VM. perform terraform apply, and see that your VM was created successfully. What should you do to delete the newly-created VM with Terraform?
Question # 89
terraform validate reports syntax check errors for which of the following?
Question # 92
You need to determine from which paths Terraform is loading the providers referenced in your *.tf files.
How can you enable additional logging to see this information?
Question # 94
What is the provider for the resource shown in the Exhibit?
resource " aws_vpc " " main " {
name = " test "
}
Question # 95
Which command generates DOT (Document Template) formatted data to visualize Terraform dependencies?
Question # 96
Which of the following ate advantages of using infrastructure as code (laC) instead of provisioning with a graphical user interface (GUI)? Choose two correct answers.
Question # 97
Your team adopts AWS CloudFormation as the standardized method for provisioning public cloud resources.
Which scenario presents a challenge for your team?
Question # 98
A module block used in your configuration is shown in the exhibit. You have been asked to update the version of this module from 4.2.1 to 5.0.0.
Exhibit:
module " compute " {
source = " Azure/compute/azurerm "
version = " 4.2.1 "
}
Which two steps must you take to accomplish this?
Question # 101
Before you can use a new backend or HCP Terraform/Terraform Cloud integration, you must first execute terraform init.
Question # 102
Which is a benefit of using infrastructure as code (IaC) tools compared to native platform APIs?
Question # 103
You have developed a new cloud-based service that uses proprietary APIs and want to use Terraform to create, manage, and delete users from the service. How can Terraform interact with the service?
Question # 105
You ' re building a CI/CD (continuous integration/continuous delivery) pipeline and need to inject sensitive variables into your Terraform run. How can you do this safely?
Question # 106
Which of the following is not a benefit of adopting infrastructure as code?
Question # 107
Your team uses HCP Terraform to manage infrastructure. You need to make a change to an infrastructure stack running in a public cloud. Which pattern follows Infrastructure as Code best practices for making the change?
Question # 108
You want to define a single input variable to capture configuration values for a server. The values must represent memory as a number, and the server name as a string.
Which variable type could you use for this input?
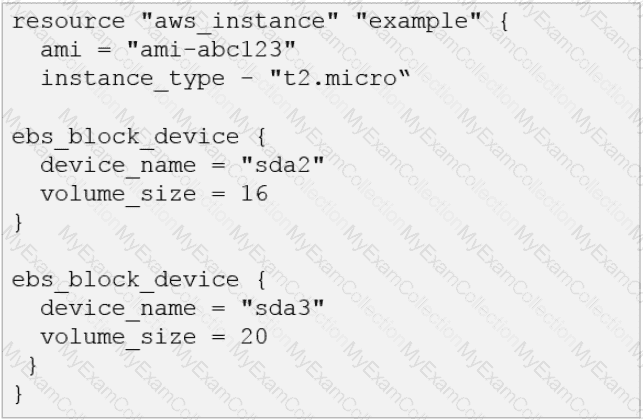
Question # 109
How would you reference the volume IDs associated with the ebs_block_device blocks in this configuration?
Question # 110
Your team adopts AWS CloudFormation as the standardized method for provisioning public cloud resources. Which scenario presents a challenge for your team?
Question # 111
What does Terraform use to deploy infrastructure for different cloud providers?
Question # 112
You want to use API tokens and other secrets within your team ' s Terraform workspaces. Where does HashiCorp recommend you store these sensitive values? (Pick 3)
Question # 113
Which of the following arguments are required when declaring a Terraform output?
Question # 114
You are updating a child module with the resource block shown in the exhibit below. The public_ip attribute of the resource needs to be accessible to the parent module.
Exhibit:
resource " aws_instance " " example " {
ami = " ami-0a123456789abcdef "
instance_type = " t3.micro "
}
How do you meet this requirement?