Question # 4
You need to recommend a solution to scan the application code. The solution must meet the application development requirements. What should you include in the recommendation?
Question # 5
You need to recommend a solution for securing the landing zones. The solution must meet the landing zone requirements and the business requirements.
What should you configure for each landing zone?
Question # 6
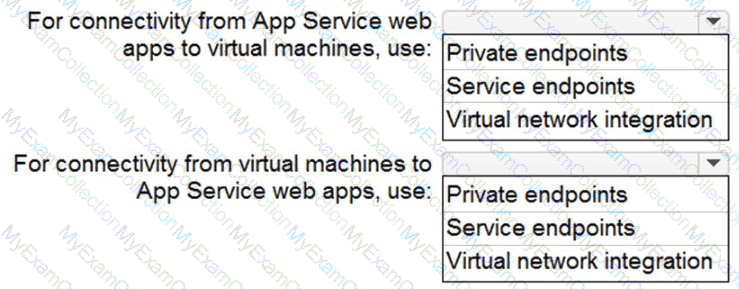
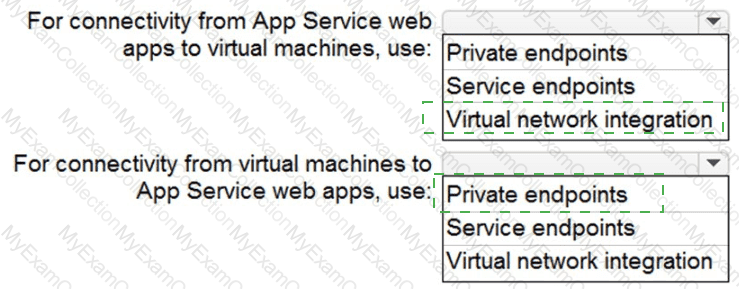
You need to recommend a strategy for App Service web app connectivity. The solution must meet the landing zone requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE Each correct selection is worth one point.
Question # 7
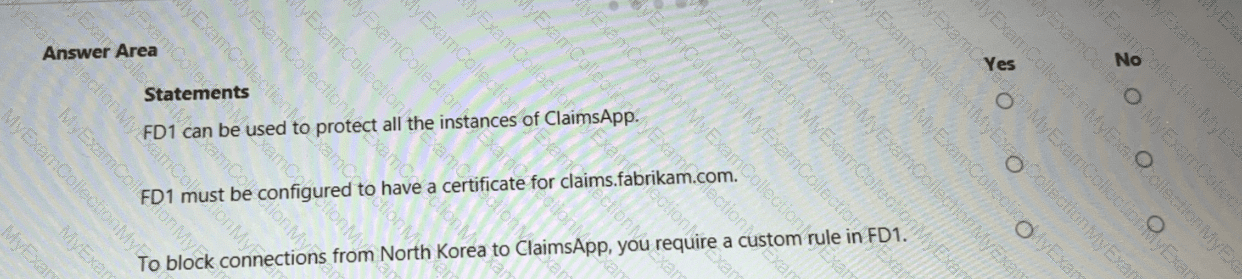
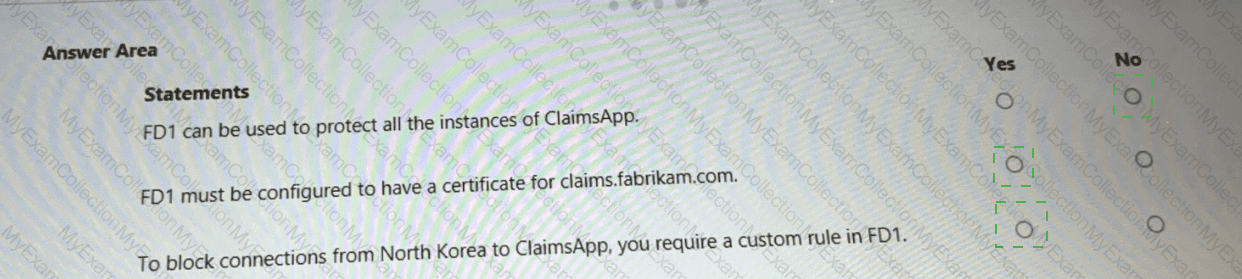
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
Question # 8
You need to recommend a solution to meet the security requirements for the virtual machines.
What should you include in the recommendation?
Question # 9
You need to recommend a solution to secure the MedicalHistory data in the ClaimsDetail table. The solution must meet the Contoso developer requirements.
What should you include in the recommendation?
Question # 10
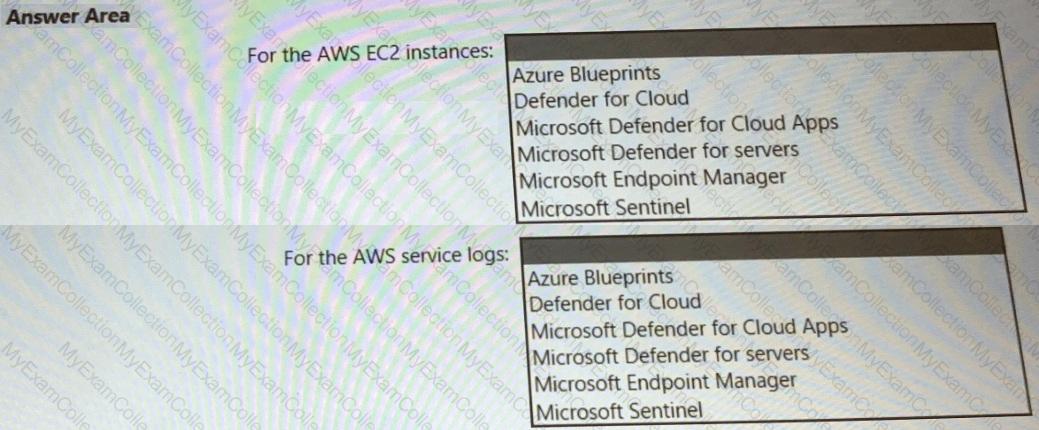
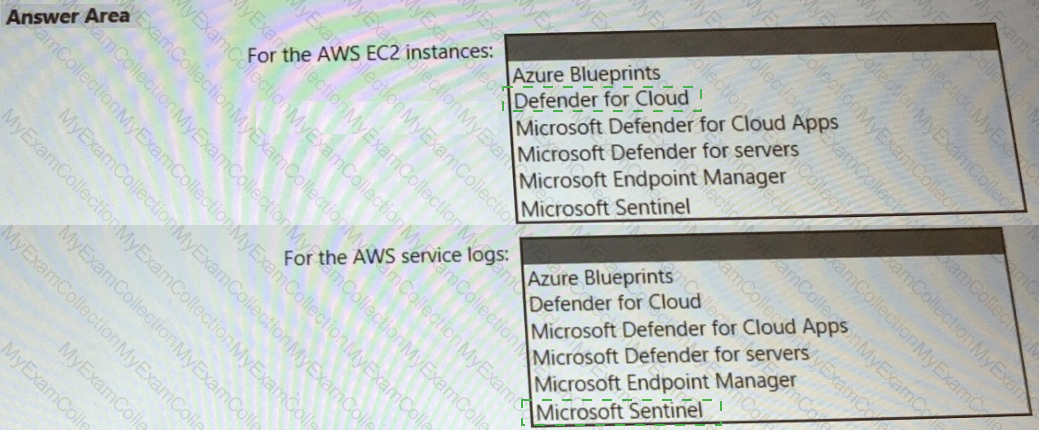
You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 11
You need to recommend a solution to meet the security requirements for the InfraSec group.
What should you use to delegate the access?
Question # 12
You need to design a strategy for securing the SharePoint Online and Exchange Online data. The solution must meet the application security requirements.
Which two services should you leverage in the strategy? Each correct answer presents part of the solution. NOTE; Each correct selection is worth one point.
Question # 13
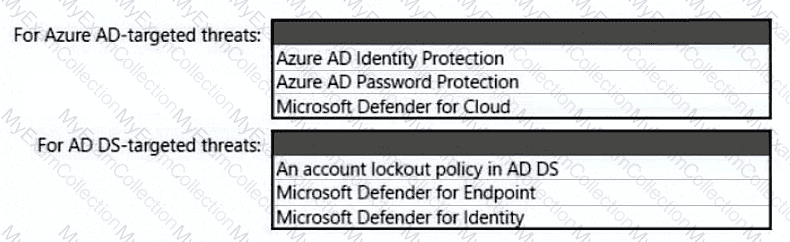
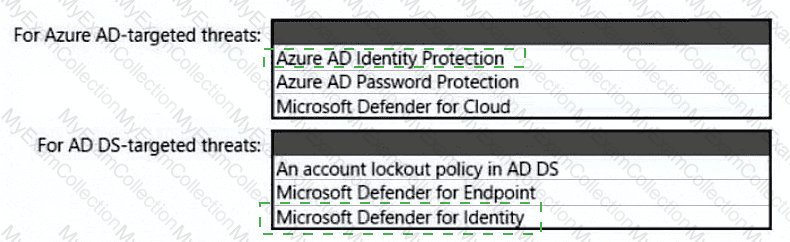
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.
Question # 14
To meet the application security requirements, which two authentication methods must the applications support? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
Question # 15
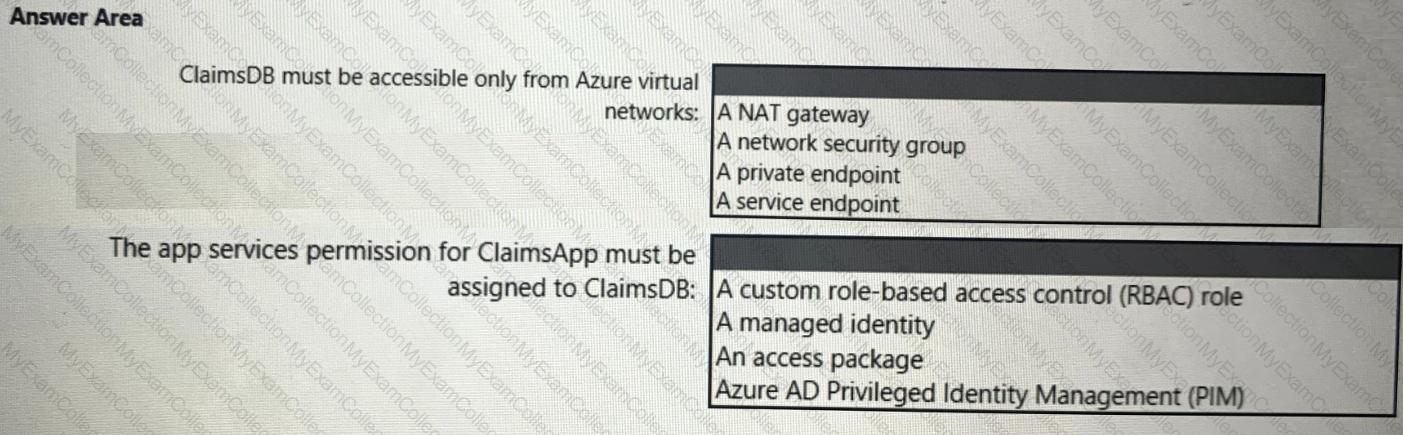
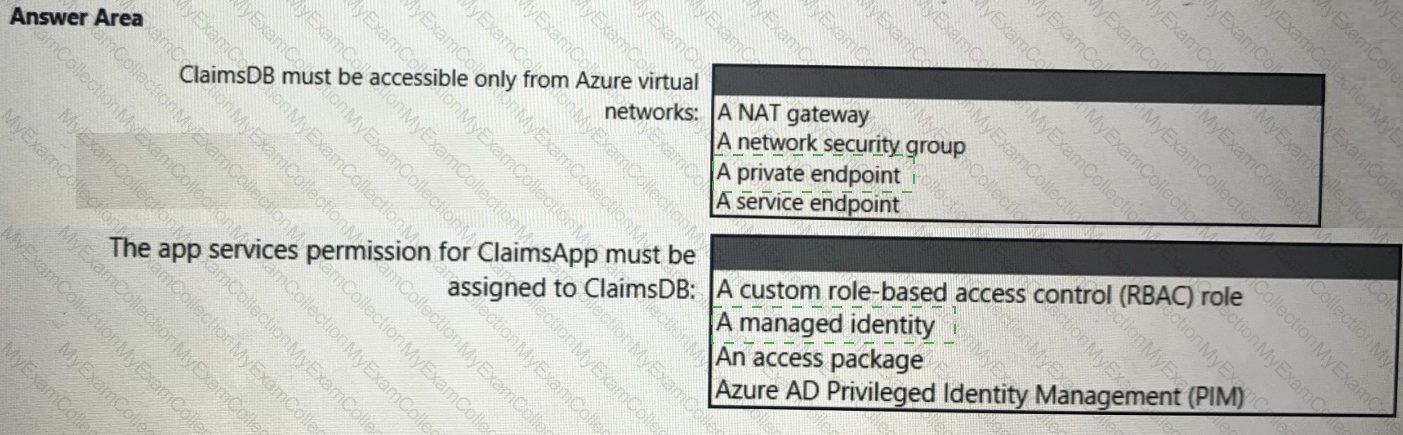
You need to recommend a solution to meet the requirements for connections to ClaimsDB.
What should you recommend using for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 16
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 17
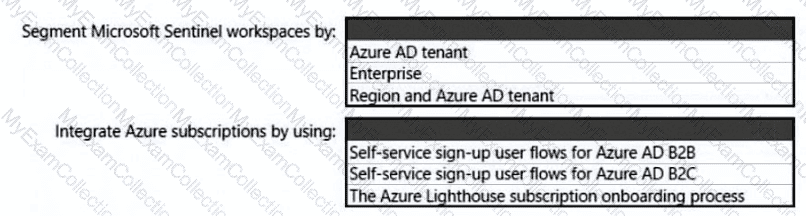
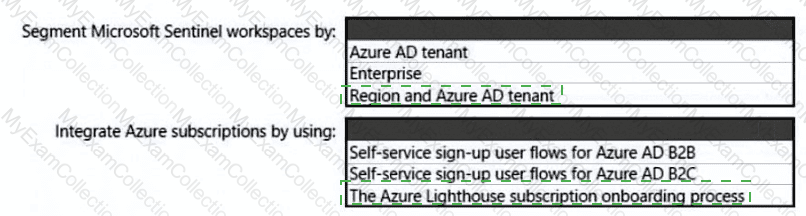
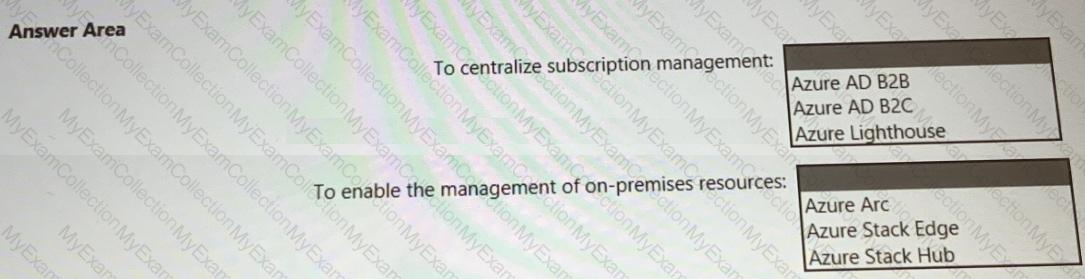
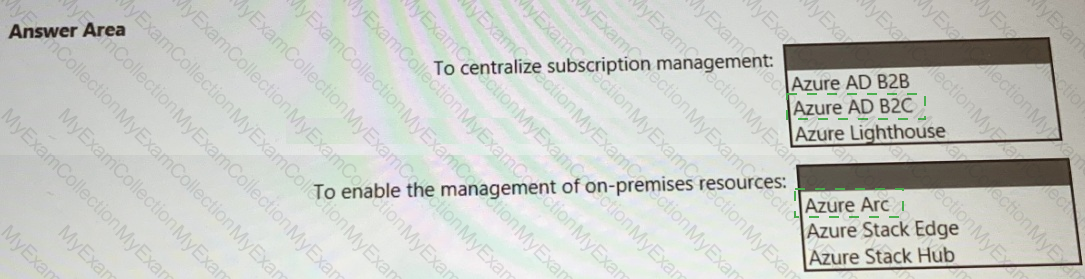
You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 18
You need to recommend a solution to resolve the virtual machine issue. What should you include in the recommendation? (Choose Two)
Question # 19
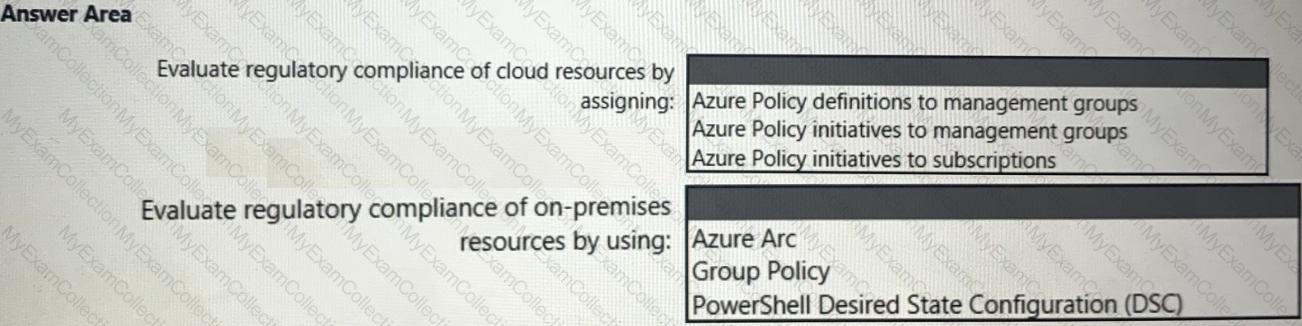
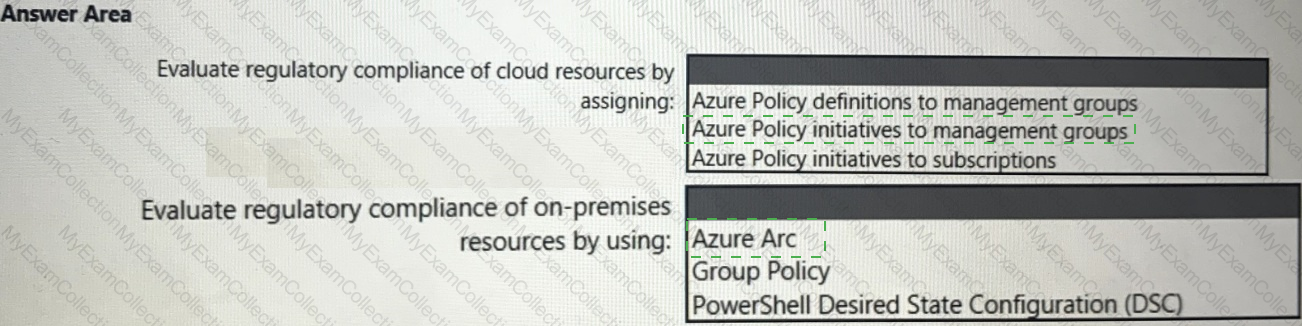
You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 20
Your company has an office in Seattle.
The company has two Azure virtual machine scale sets hosted on different virtual networks.
The company plans to contract developers in India.
You need to recommend a solution provide the developers with the ability to connect to the virtual machines over SSL from the Azure portal. The solution must meet the following requirements:
• Prevent exposing the public IP addresses of the virtual machines.
• Provide the ability to connect without using a VPN.
• Minimize costs.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Question # 21
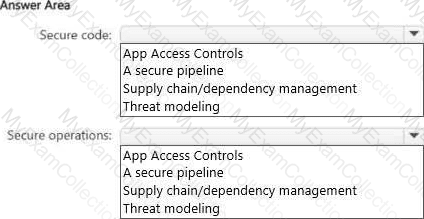
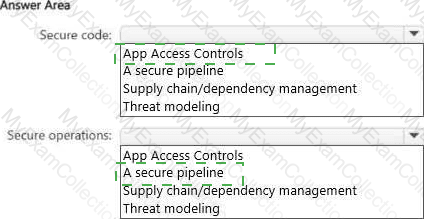
You have an Azure DevOps organization that is used to manage the development and deployment of internal apps to multiple Azure subscriptions.
You are developing a DevSecOps strategy.
You need to apply DevSecOps controls for the secure code stage and the secure operations stage. The solution must be based on Microsoft Cloud Adoption Framework for Azure principles.
What should you apply for each stage? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 22
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points.
You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend enabling just-in-time (JIT) VM access on all virtual machines.
Does this meet the goal?
Question # 23
Your company plans to evaluate the security of its Azure environment based on the principles of the Microsoft Cloud Adoption Framework for Azure.
You need to recommend a cloud-based service to evaluate whether the Azure resources comply with the National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF).
What should you recommend?
Question # 24
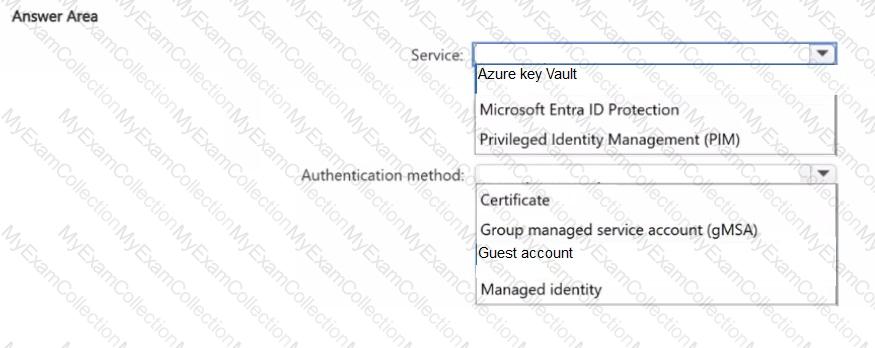
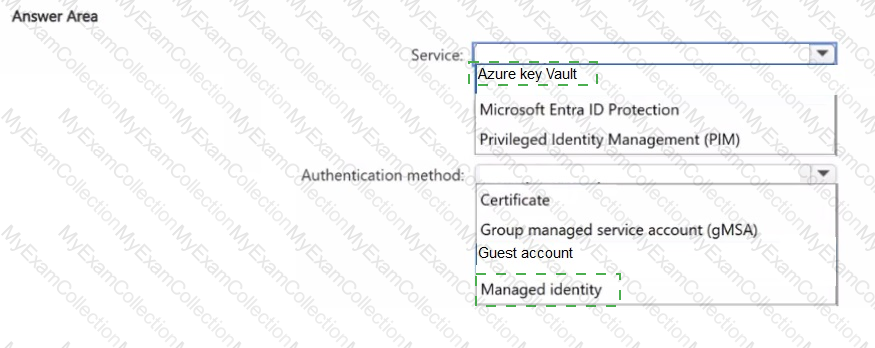
You have an Azure subscription.
You plan to deploy an Azure App Service web app named App1 that will access an external web service by using a username and password.
You need to recommend a password storage solution for App1 that meets the following requirements:
• Ensures that the password is stored securely
• Ensures that App1 can authenticate to the service that will store the password
Which service should you use to store the password, and which authentication method should App1 use to access the service? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 25
Your on-premises network contains an Active Directory Domain Services (AD DS) domain named corpxontoso.com and an AD DS-integrated application named App1.
Your perimeter network contains a server named Server1 that runs Windows Server.
You have a Microsoft Entra tenant named contoso.com that syncs with corp.contoso.com.
You plan to implement a security solution that will include the following configurations:
• Manage access to App1 by using Microsoft Entra Private Access.
• Deploy a Microsoft Entra application proxy connector to Server1.
• Implement single sign-on (SSO) for App1 by using Kerberos constrained delegation.
• For Server1, configure the following rules in Windows Defender Firewall with Advanced Security:
o Rule1: Allow TCP 443 inbound from a designated set of Azure URLs.
o Rule2: Allow TCP 443 outbound to a designated set of Azure URLs.
o Rule3: Allow TCP 80 outbound to a designated set of Azure URLs.
o Rule4: Allow TCP 389 outbound to the domain controllers on corp.contoso.com.
You need to maximize security for the planned implementation. The solution must minimize the impact on the connector.
Which rule should you remove?
Question # 26
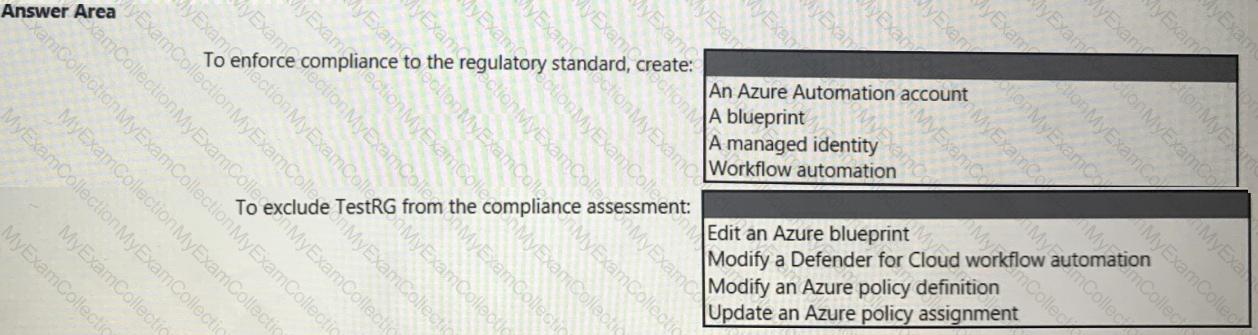
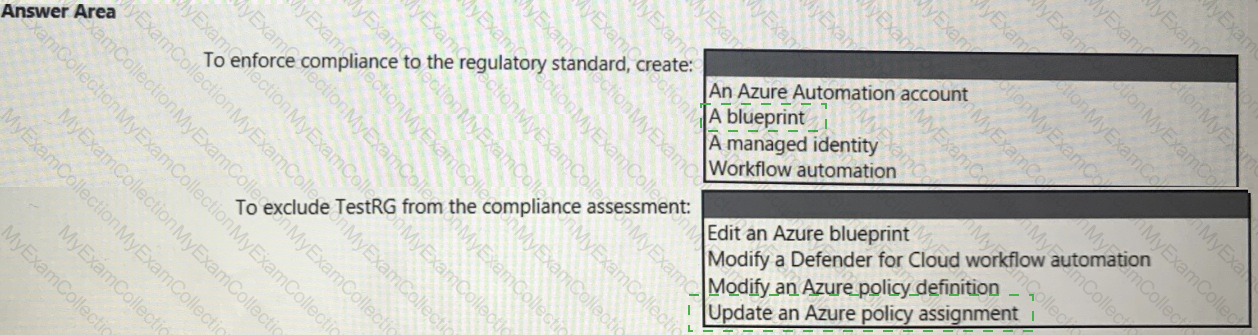
You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 27
You have a Microsoft Entra tenant named contoso.com and use Microsoft Intune. Each user in contoso.com has a Microsoft Entra ID P1 license and a Windows 11 device that has the Global Secure Access client deployed.
You plan to deploy the following configuration of Microsoft Entra Internet Access:
• Enable a baseline profile.
• Create a security profile named Profile` that has a priority of 300 and contains a single web content filtering policy named WCFPolicy configure WCFPolicy1 as follows:
o Set Action to allow.
o Include a single rule that has a fully qualified domain name (FQDN) destination of ‘. adatum.com.
• Link Profile1 to a Conditional Access policy named CAPolicy1, apply CAPolicy1 to all users, and grant access unless a user ' s device is noncompliant
You need to evaluate the impact of the planned deployment on traffic to the following resources:
• https://www.adatum.com:8433
• https://www.fabrikam.com
Which two traffic scenarios will occur? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point
Question # 28
You have to Azure subscriptions that contain 100 role-based access control (RBAC) role assignments.
You plan to consolidate the role assignments.
You need to recommend a solution to identify which role assignments were NOT used during the last 90 days. The solution must minimize administrative effort.
What should you include in the recommendation?
Question # 29
You are designing a security strategy for providing access to Azure App Service web apps through an Azure Front Door instance.
You need to recommend a solution to ensure that the web apps only allow access through the Front Door instance.
Solution: You recommend configuring gateway-required virtual network integration.
Does this meet the goal?
Question # 30
You have an Azure subscription.
You have a DNS domain named contoso.com that is hosted by a third-party DNS registrar.
Developers use Azure DevOps to deploy web apps to App Service Environments- When a new app is deployed, a CNAME record for the app is registered in contoso.com.
You need to recommend a solution to secure the DNS record tor each web app. The solution must meet the following requirements:
• Ensure that when an app is deleted, the CNAME record for the app is removed also
• Minimize administrative effort.
What should you include in the recommendation?
Question # 31
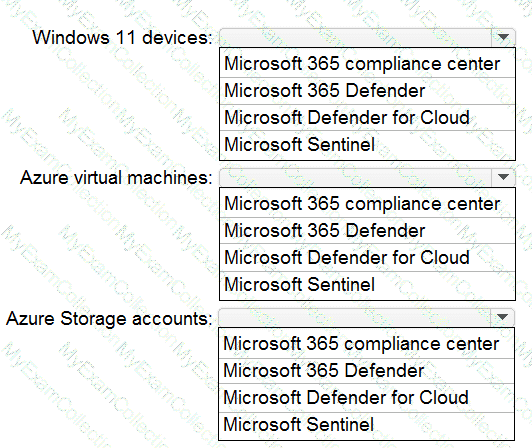
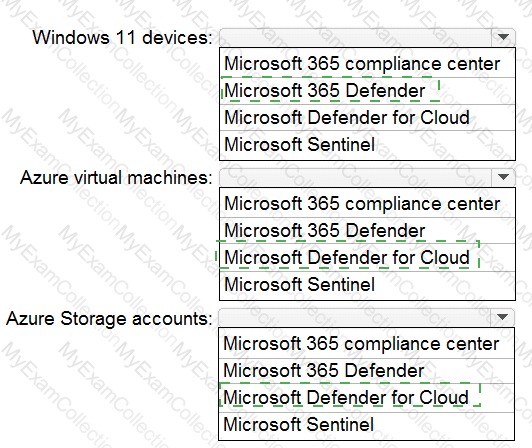
You have a Microsoft 365 E5 subscription and an Azure subscripts You need to evaluate the existing environment to increase the overall security posture for the following components:
• Windows 11 devices managed by Microsoft Intune
• Azure Storage accounts
• Azure virtual machines
What should you use to evaluate the components? To answer, select the appropriate options in the answer area.
Question # 32
You have on-premises servers and virtual machines that run Windows Server or Red Hat Enterprise Linux (RHEL).
You have an Azure subscription The subscription contains virtual machines that run Windows Server Datacentet: Azure Edition.
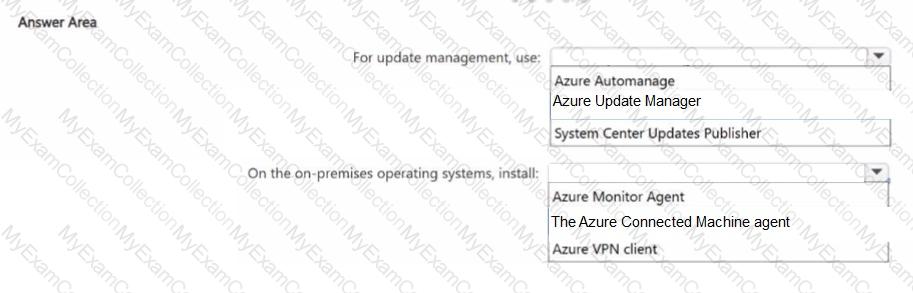
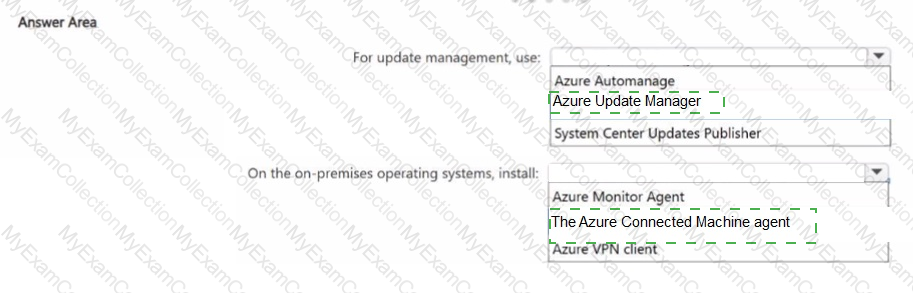
You need to recommend a solution to manage operating system updates for the on-premises servers and the virtual machines. The solution must meet the following requirements:
• Enable hotpatching for the Azure virtual machines.
• Enable the on demand inventory and deployment of updates.
• Enable the deployment of Extended Security Update (ESU) patches to the on-premises servers.
What should you include in the recommendation? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
Question # 33
Your company is moving a big data solution to Azure.
The company plans to use the following storage workloads:
• Azure Storage blob containers
• Azure Data Lake Storage Gen2
• Azure Storage file shares
• Azure Disk Storage
Which two storage workloads support authentication by using Azure Active Directory (Azure AD)?
Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
Question # 34
Azure subscription that uses Azure Storage.
The company plans to share specific blobs with vendors. You need to recommend a solution to provide the vendors with secure access to specific blobs without exposing the blobs publicly. The access must be t\me-Vim\ted. What should you include in the recommendation?
Question # 35
You have a multicloud environment that contains an Azure subscription, an Amazon Web Services (AWS) subscription, and a Google Cloud Platform (GCP) subscription.
You plan to assess data security and compliance.
You need to design a Compliance Manager solution that meets the following requirements:
• Provides recommended improvement actions that include detailed implementation guidance
• Automatically monitors regulatory compliance
• Minimizes administrative effort
What should you include in the solution?
Question # 36
Your company is preparing for cloud adoption.
You are designing security for Azure landing zones.
Which two preventative controls can you implement to increase the secure score? Each NOTE: Each correct selection is worth one point.
Question # 37
You are designing the security standards for containerized applications onboarded to Azure. You are evaluating the use of Microsoft Defender for Containers.
In which two environments can you use Defender for Containers to scan for known vulnerabilities? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
Question # 38
You have an Azure subscription that contains multiple Azure Blob Storage accounts.
You need to recommend a solution to detect threats in files after the files are uploaded to a blob container.
What should you include in the recommendation?
Question # 39
A customer has a hybrid cloud infrastructure that contains a Microsoft 365 E5 subscription and an Azure subscription.
All the on-premises servers in the perimeter network are prevented from connecting directly to the internet.
The customer recently recovered from a ransomware attack.
The customer plans to deploy Microsoft Sentinel.
You need to recommend configurations to meet the following requirements:
• Ensure that the security operations team can access the security logs and the operation logs.
• Ensure that the IT operations team can access only the operations logs, including the event logs of the servers in the perimeter network.
Which two configurations can you include in the recommendation? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.
Question # 40
You have multiple Azure subscriptions that each contains multiple resource groups.
You need to identify the privileged role assignments in each subscription and any associated security risks. The solution must minimize administrative effort.
What should you use?
Question # 41
Your company plans to provision blob storage by using an Azure Storage account The blob storage will be accessible from 20 application sewers on the internet. You need to recommend a solution to ensure that only the application servers can access the storage account. What should you recommend using to secure the blob storage?
Question # 42
You have a Microsoft 365 subscription that contains 1,000 Microsoft Exchange Online mailboxes. You need to identify which users are susceptible to phishing attacks. What should you use?
Question # 43
You have a Microsoft 365 £5 subscription.
You plan to implement Microsoft Priva Subject Rights Requests for Microsoft 365 data.
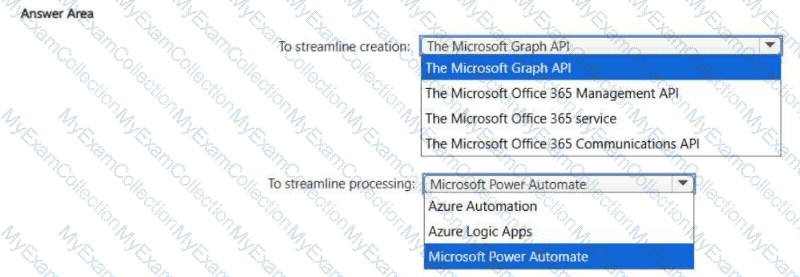
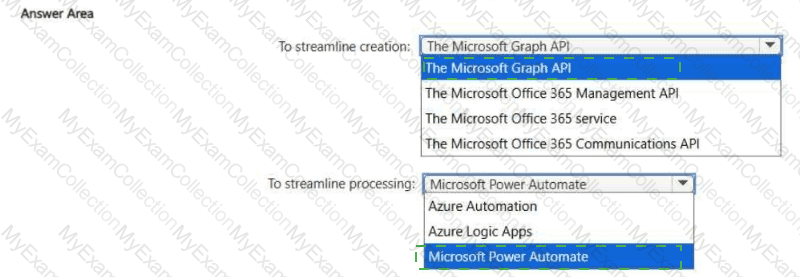
You need to streamline the creation and processing of subject rights requests. The solution must minimize development effort.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 44
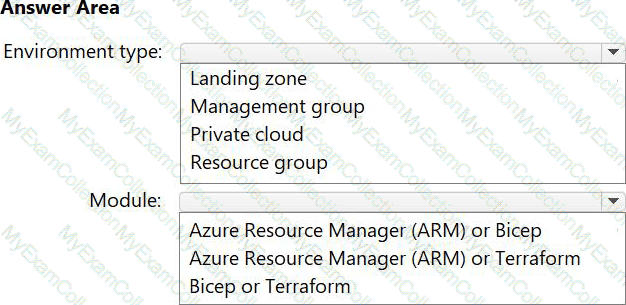
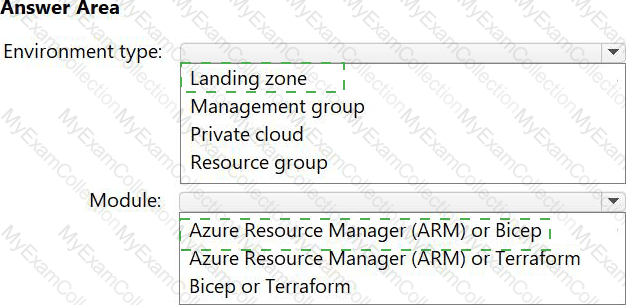
You are designing new Azure applications based on security best practices from the Microsoft Cloud Adoption Framework for Azure .
Each application will be deployed to a dedicated and secure environment that will contain isolated instances of the following key Azure security resources:
• Azure Key Vault
• Virtual networks
• An Azure subscription
• Azure Policy assignments
• Network security groups (NSGs)
• Role-based access control (RBAC) assignments
You need to recommend which type of environment and which module to use to deploy the applications. The solution must use infrastructure as code (IaC) to deploy each application environment.
What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 45
You have an Azure subscription that contains 100 virtual machines. The virtual machines are accessed by using Azure Bastion.
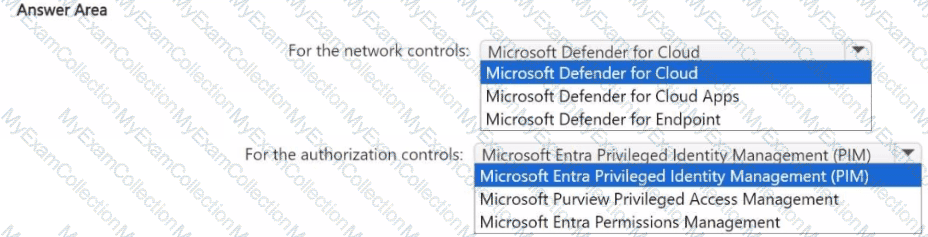
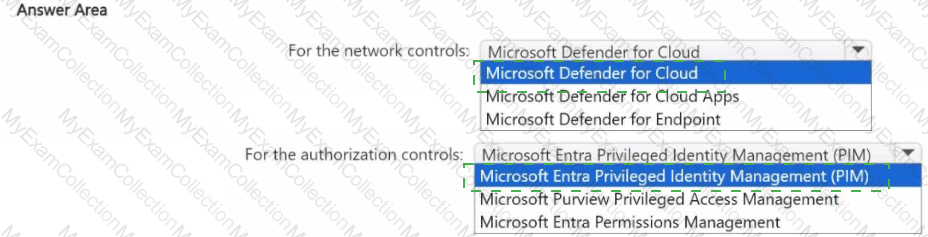
You need to recommend a solution to ensure that only specific users in specific locations can access the virtual machines. The solution must meet the following requirements:
• Restrict access to the virtual machines based on an originating IP address or a connection request by using just-in-time (JIT) VM access network-based controls.
• Restrict access to the virtual machines based on role-based access control (RBAC) role assignments by using JIT VM access authorization controls.
Which Microsoft cloud services should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question # 46
You have an Azure subscription that contains multiple apps. The apps are deployed by using continuous integration and continuous delivery (CI/CD) pipelines in Azure DevOps.
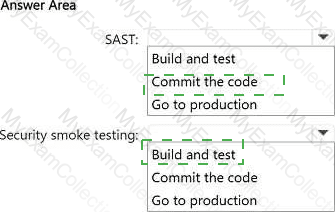
You need to integrate static application security testing (SAST) and security smoke testing into the pipelines based on Microsoft Cloud Adoption Framework for Azure principles.
At which stage of the CI/CID process should each type of test be integrated? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 47
You have an on-premises datacenter named Site1.
You have an Azure subscription that contains a virtual network named VNet1 and multiple Azure App Service apps. Site1 is connected to VNet1 by using a Site-to-Site (P2S) VPN connection. The apps are accessed by using public internet connections.
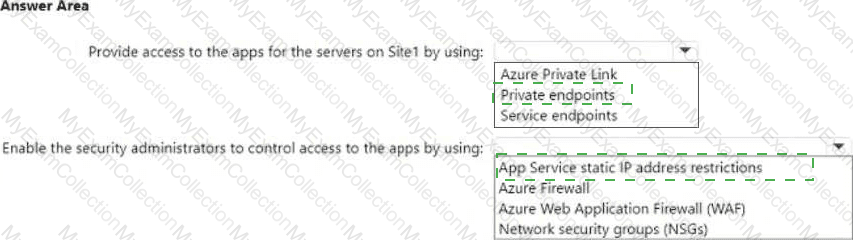
You need to recommend a solution for providing secure access to the apps .
The solution must meet the following requirements:
• Servers on Site1 must use a VPN connection to access the apps.
• Access to the apps must be restricted to specific servers on Site1.
• Security administrators for VNet1 must be able to control which servers can access the apps.
• Costs must be minimized.
What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 48
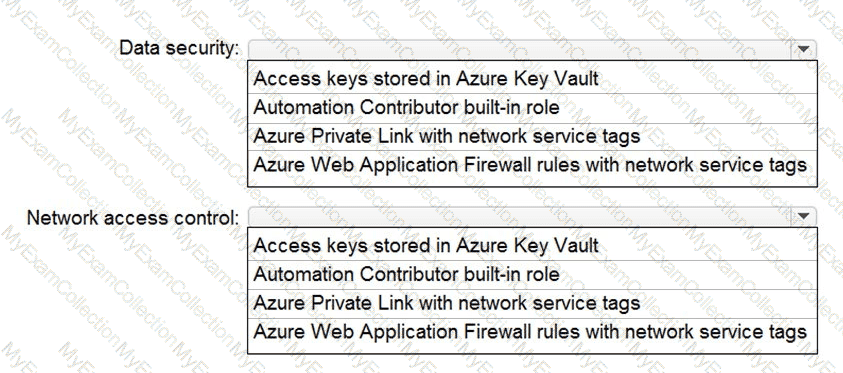
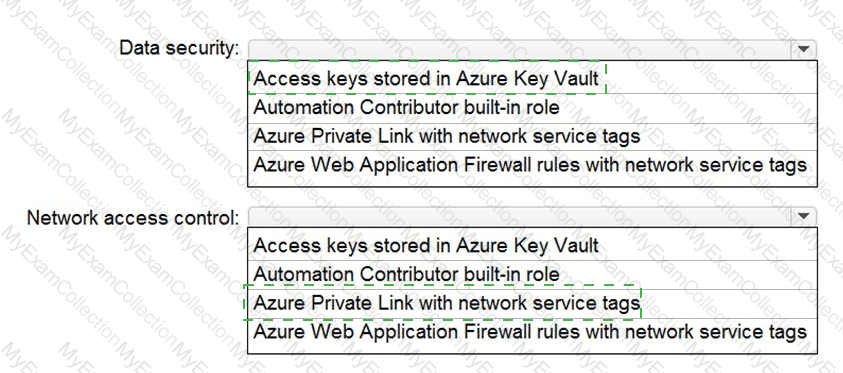
You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Question # 49
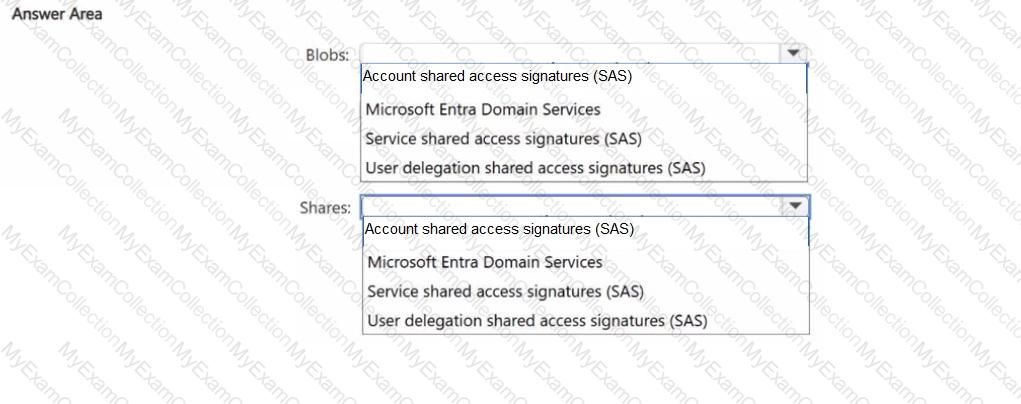
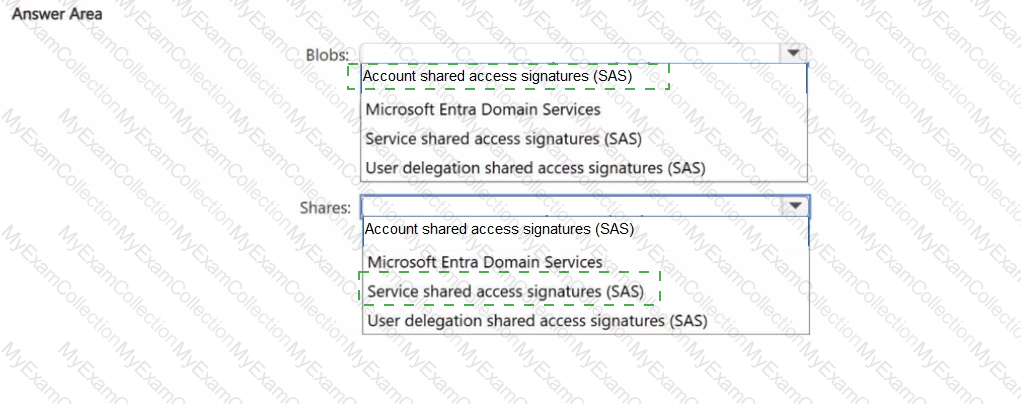
You have an Azure subscription that contains multiple Azure Storage blobs and Azure Files shares.
You need to recommend a security solution for authorizing access to the blobs and shares. The solution must meet the following requirements:
• Support access to the shares by using the SMB protocol.
• Limit access to the blobs to specific periods of time.
• Include authentication support when possible.
What should you recommend for each resource? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
Question # 50
Your company has a Microsoft 365 E5 subscription.
The Chief Compliance Officer plans to enhance privacy management in the working environment. You need to recommend a solution to enhance the privacy management. The solution must meet the following requirements:
• Identify unused personal data and empower users to make smart data handling decisions.
• Provide users with notifications and guidance when a user sends personal data in Microsoft Teams.
• Provide users with recommendations to mitigate privacy risks.
What should you include in the recommendation?
Question # 51
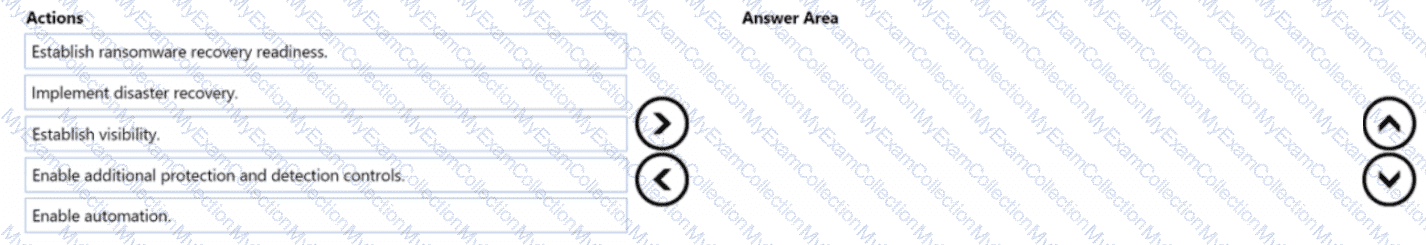
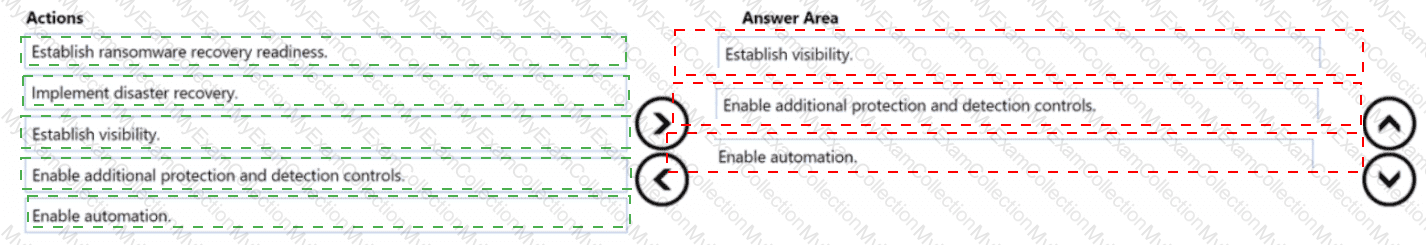
You are designing a security operations strategy based on the Zero Trust framework.
You need to increase the operational efficiency of the Microsoft Security Operations Center (SOC).
Based on the Zero Trust framework, which three deployment objectives should you prioritize in sequence? To answer, move the appropriate objectives from the list of objectives to the answer area and arrange them in the correct order.
Question # 52
You have Windows 11 devices and Microsoft 365 E5 licenses.
You need to recommend a solution to prevent users from accessing websites that contain adult content such as gambling sites. What should you include in the recommendation?
Question # 53
You have an Azure subscription. The subscription contains 100 virtual machines that run Linux on Windows Server. The subscription uses Microsoft Defender for Servers Plan 1.
You need to recommend a solution to identify and remediate virtual machines that have the following characteristics:
• Are NOT onboarded to Defender for Servers
• Are missing critical updates
• Have risky apps installed
The solution must minimize administrative effort.
What should you include in the recommendation?
Question # 54
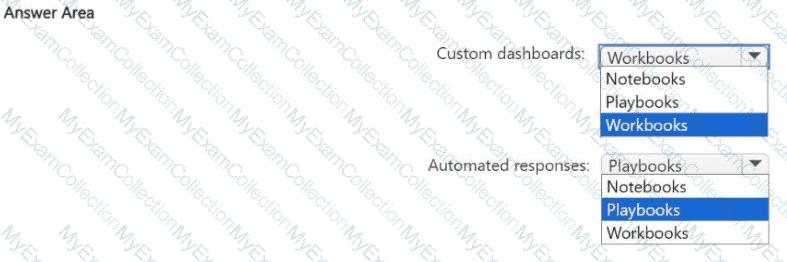
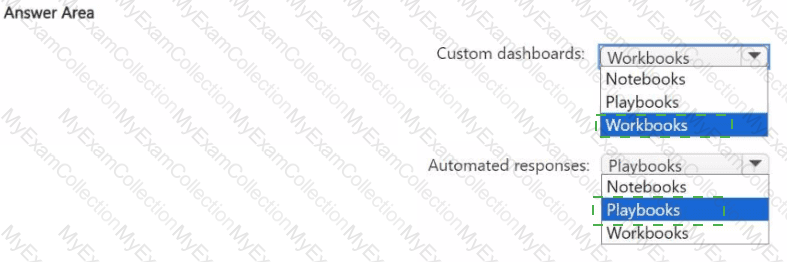
You have an Azure subscription that contains a Microsoft Sentinel workspace named WS1.
You need to configure WS1 to meet the following requirements:
• Create custom dashboards to visualize the workload of security analysts that use Microsoft Sentinel.
• Enable automated responses for the security alerts generated by Microsoft Sentinel analytics rules.
What should you use for each requirement? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.