Pre-Winter Sale Special - Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: mxmas70

Home > Fortinet > Fortinet Network Security Expert > NSEI_OTS_AR-7.6

NSEI_OTS_AR-7.6 Fortinet NSE I - OT Security 7.6 Architect Question and Answers

Question # 4

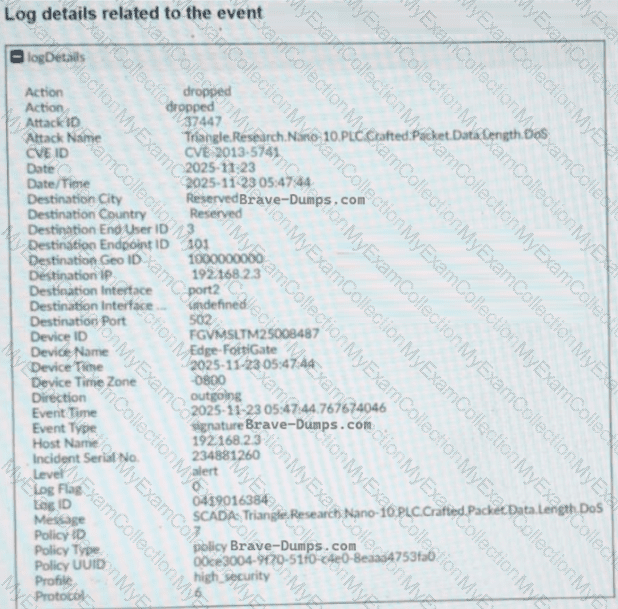
Refer to the exhibits.
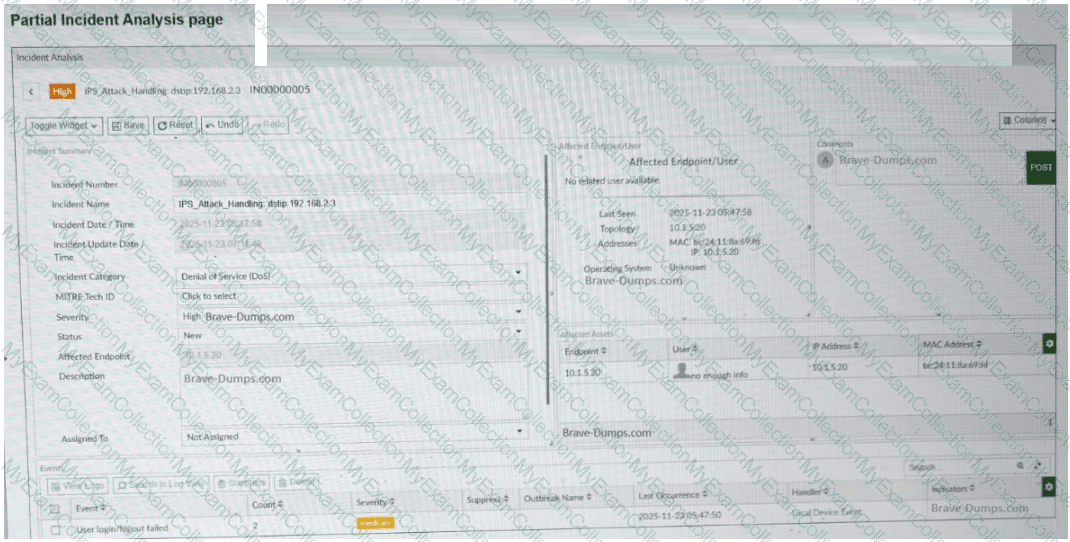
A partial Incident Analysis page and the log details related to the event are shown. An attack is reported on your OT network. You analyze the corresponding incident. Based on the information provided on the Incident Analysis page and the log details, which two statements are correct? (Choose two answers)

A.

The attack uses the Modbus protocol.

B.

The attack is mitigated.

C.

The attack uses the IEC 104 protocol.

D.

The event severity is high.

E.

The target device IP address is 10.1.5.20.

Full Access
Question # 5

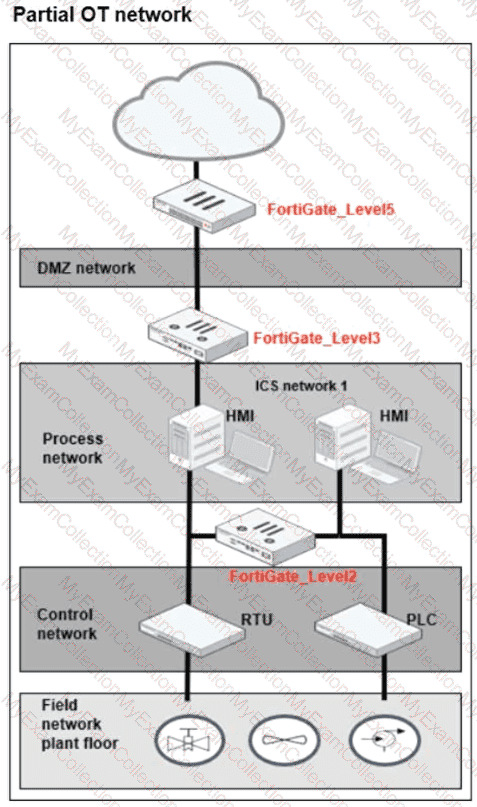
Refer to the exhibit.

A partial OT network is shown.

You have recently removed the air gap in the network to provide full connectivity.

What must you configure to protect your OT network from external attacks?

A.

OT signatures on FortiGate_Level3

B.

Virtual patching on FortiGate_Level2

C.

OT application control on all FortiGate devices

D.

IPS on FortiGate_Level5

Full Access
Question # 6

You want to protect OT devices that are not updated against known vulnerabilities so you apply virtual patching to the firewall policies. What must you check to confirm that the OT devices are virtually patched? (Choose one answer)

A.

The output of the CLI command get virtual-patch profile

B.

The OT View page

C.

The output of the CLI command get rule otvp status

D.

The Asset Identity List page

Full Access
Question # 7

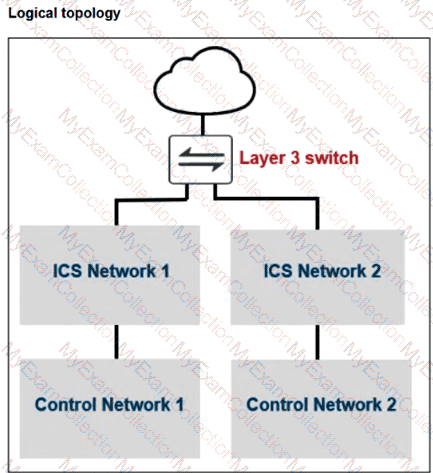
Refer to the exhibit.

A partial OT network is shown. You must improve the security of this OT network and implement internal segmentation between network 1 and network 2. How can you achieve the segmentation? (Choose one answer)

A.

You can configure universal ZTNA.

B.

You can configure one traffic VDOM.

C.

You can configure an explicit software switch.

D.

You can configure forward domain IDs for each network.

Full Access
Question # 8

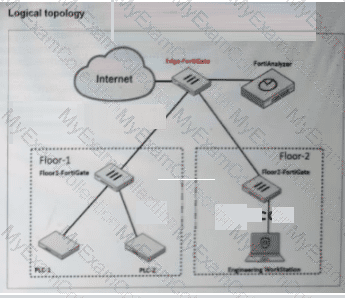
Refer to the exhibit.

A partial OT network is shown. You want to configure an automated alert sent by FortiAnalyzer when an attack occurs on a FortiGate device. Which two configurations must you implement? (Choose two answers)

A.

You must configure a stitch on the root FortiGate.

B.

You must configure a LOCALHOST task in the FortiAnalyzer playbook.

C.

You must configure an intrusion prevention security profile on all FortiGate devices.

D.

You must configure an event handler on FortiAnalyzer.

Full Access
Question # 9

What is the main OT component for monitoring and controlling industrial processes? (Choose one answer)

A.

Programmable Logical Controller (PLC)

B.

Supervisory Control and Data Acquisition (SCADA)

C.

Industrial Control System (ICS)

D.

Industrial Internet of Things (IIoT)

Full Access
Question # 10

You would like to customize your current FortiAnalyzer report to provide a better risk assessment of your OT network. Which two options can you use to enhance your report? (Choose two answers)

A.

The FortiView library

B.

The Datasets library

C.

The Log View library

D.

The Chart library

E.

The Dashboard library

Full Access
Question # 11

You want to improve access control for your large OT network using passive authentication. What must you configure on FortiGate? (Choose one answer)

A.

Fortinet Single-Sign On (FSSO)

B.

Local users

C.

Two-factor authentication

D.

A FortiAuthenticator device as a remote server

Full Access
Question # 12

As the first step in your OT network protection plan, you must identify the OT protocols that the FortiGate device supports. Which two configurations must you implement on this FortiGate device? (Choose two answers)

A.

You must enable Device detection on all the interfaces.

B.

You must implement an Application Control security profile that monitors OT.

C.

You must enable the OT signatures.

D.

You must implement an Intrusion Prevention security profile that monitors OT.

Full Access
Question # 13

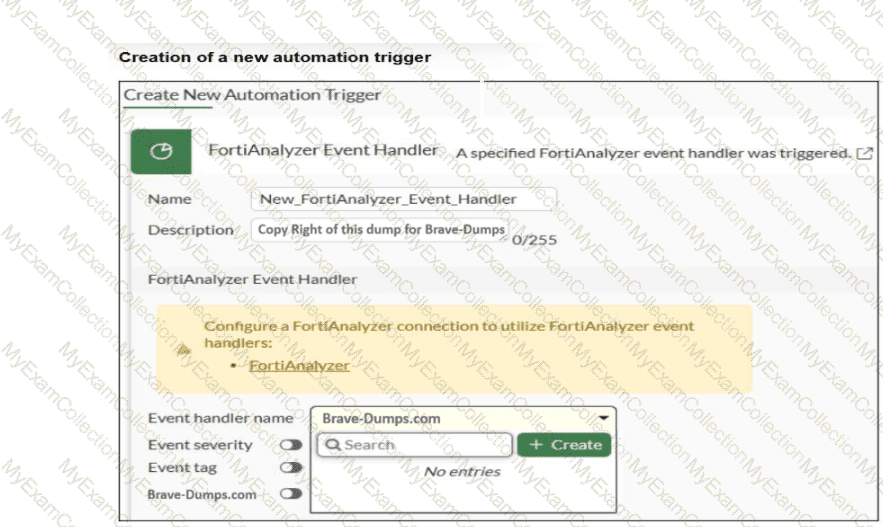
Refer to the exhibit.

An automation trigger creation wizard is shown. You want to automate some tasks in your OT network. In a FortiGate device, you create a new automation trigger based on a FortiAnalyzer event handler. When you want to configure the Event handler name field, the event handler created in FortiAnalyzer is not shown. What are two reasons for this? (Choose two answers)

A.

You must configure the Fabric settings on the FortiGate device.

B.

You must enable Automation Stitch in the event handler on FortiAnalyzer.

C.

You must click + Create in the Event handler name field.

D.

You must add the FortiGate device to FortiAnalyzer and authorize it.

Full Access
Question # 14

Refer to the exhibit.

Based on the information provided on the partial Event Monitor page shown in the exhibit, how was the attack detected? (Choose one answer)

A.

Automatically by a stitch

B.

Manually by an administrator

C.

Automatically by a playbook

D.

Automatically by an event handler

Full Access
Question # 15

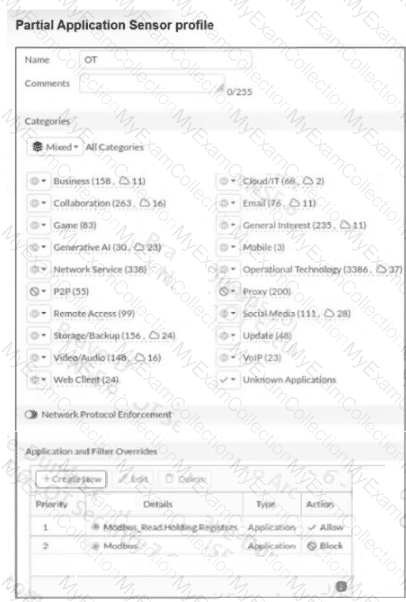
Refer to the exhibit.

A partial Application Sensor profile is shown. When you apply this profile in firewall policy, which two statements are correct? (Choose two answers)

A.

OT signatures are enabled.

B.

All OT protocols are monitored.

C.

Modbus write commands are blocked.

D.

A log is provided for each Modbus read holding registers command.

Full Access
Question # 16

What is the next step if FortiGate cannot detect a device locally? (Choose one answer)
A.

FortiGate queries FortiGuard servers.

B.

FortiGate queries the profiling rules.

C.

FortiGate queries OT servers through service connectors.

D.

FortiGate queries the local device database (CIDB).

Full Access