

Question # 4
Which two configurations are required for Agentless ZTNA to work? (Choose two.)
A.
Proxy user single sign-on (SSO)
B.
FortiGate with ZTNA proxy
C.
FortiClient Agent
D.
SD-WAN Private Access (SPA)
Full Access
Answer:
A, D
Explanation:
A and D are correct. Fortinet ' s FortiSASE material identifies two fundamental prerequisites for agentless ZTNA/private application access: an SSO configuration for proxy users and an existing Secure Private Access (SPA) configuration. The Administrator Study Guide states explicitly that agentless support for private applications requires both an SPA configuration and a Secure Web Gateway SSO configuration.
Proxy user SSO (A) provides the identity-verification component. When an agentless user accesses the FortiSASE bookmark portal through a browser, the user must authenticate using SSO. The Enterprise Administrator workflow confirms that authentication occurs through FortiSASE proxy SSO user authentication before authorized application bookmarks are displayed.
SPA (D) provides connectivity from FortiSASE to the protected private applications. After authentication and policy evaluation, the application session is routed through FortiSASE SPA, which functions as the gateway for agentless ZTNA access.
B is incorrect because a FortiGate ZTNA access proxy is not itself a mandatory prerequisite for agentless ZTNA; SPA can be implemented through the supported private-access architecture. C is incorrect by definition: agentless ZTNA is designed for endpoints, including BYOD devices, that do not require FortiClient.
Study Guide Reference: SPA > Agentless ZTNA; Secure Private Access > Private Access for Agentless Users.
Question # 5
Which configuration is a valid use case for FortiSASE features in supporting remote users?
A.
Enabling secure SaaS access through SD-WAN integration, protecting against web-based threats with data loss prevention, and monitoring user connectivity with shadow IT visibility.
B.
Monitoring SaaS application performance, isolating browser sessions for all websites, and integrating with SD-WAN for data loss prevention.
C.
Enabling secure web browsing to protect against threats, providing explicit application access with zero-trust or SD-WAN integration, and addressing shadow IT visibility with data loss prevention.
D.
Providing secure web browsing through remote browser isolation, addressing shadow IT with zero-trust access, and protecting data at rest only.
Full Access
Answer:
C
Explanation:
According to the FortiSASE 7.6 Architecture Guide and FCP - FortiSASE 24/25 Administrator materials, the solution is built around three primary use cases that support a hybrid workforce:
Secure Internet Access (SIA): This enables secure web browsing by applying security profiles such as Web Filter, Anti-Malware, and SSL Inspection in the SASE cloud. It protects remote users from internet-based threats regardless of their location.
Secure Private Access (SPA): This provides granular, explicit access to private applications hosted in data centers or the cloud. It is achieved through ZTNA (Zero Trust Network Access) for session-based security or through SD-WAN integration where FortiSASE acts as a spoke to an existing corporate SD-WAN hub.
SaaS Security: FortiSASE utilizes Inline-CASB and Shadow IT visibility to monitor and control the use of cloud applications. Data Loss Prevention (DLP) is integrated into these workflows to prevent sensitive corporate data from being uploaded to unauthorized SaaS platforms.
Why other options are incorrect:
Option A: While it mentions SD-WAN and Shadow IT, it misses the core definition of SIA (secure web browsing) which is the primary driver for SASE deployments.
Option B: Remote Browser Isolation (RBI) is typically applied to risky or uncategorized websites, not " all websites, " due to the high performance and resource overhead.
Option D: FortiSASE is designed to protect data in motion (via security profiles) as well as data stored in sanctioned cloud apps, not " at rest only " .
Question # 6
Refer to the exhibit.
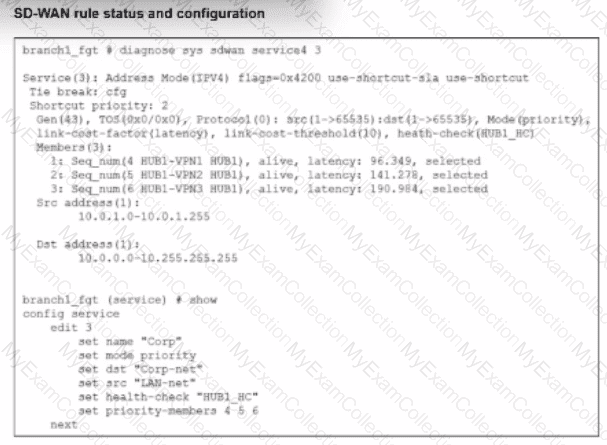
The SD-WAN rule status and configuration is shown. Based on the exhibit, which change in the measured latency will first make HUB1-VPN3 the new preferred member?
A.
When HUB1-VPN3 has a latency of 80 ms
B.
When HUB1-VPN3 has a lower latency than HUB1-VPN1 and HUB1-VPN2
C.
When HUB1-VPN1 has a latency of 200 ms
D.
When HUB1-VPN3 has a latency of 90 ms
Full Access
Answer:
A
Explanation:
According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, the selection of a preferred member in a Best Quality (priority) rule is determined by the measured quality metric (latency, in this case) and the link-cost-threshold.
Rule Logic (Best Quality): In the exhibit, the SD-WAN rule is configured with set mode priority, which corresponds to the Best Quality strategy. This strategy ranks members based on the link-cost-factor, which is set to latency.
The Link-Cost-Threshold: The exhibit shows link-cost-threshold(10), which is the default 10% value. This threshold is designed to prevent " link flapping " . To replace the current preferred member, a new member must not only have a better latency but must be better by more than 10%.
The Calculation:
The current preferred member is HUB1-VPN1 with a real latency of 96.349 ms.
To calculate the " target " latency a lower-priority member must achieve to take over, we use the formula: $Target = \frac{Current\_Latency}{(1 + \frac{Threshold}{100})}$.
$\frac{96.349}{1.1} = \mathbf{87.59\text{ ms}}$.
Evaluating Options:
Option A (80 ms): Since 80 ms is lower than the required 87.59 ms target, HUB1-VPN3 successfully overcomes the 10% advantage of HUB1-VPN1 and becomes the new preferred member.
Option D (90 ms): While 90 ms is lower than 96.349 ms, it is not lower than 87.59 ms. Therefore, the 10% threshold prevents a member switch, and HUB1-VPN1 remains preferred.
Option B: Incorrect because having a " lower " latency is not enough due to the 10% threshold.
Option C: If HUB1-VPN1 moved to 200 ms, HUB1-VPN2 (at 141.278 ms) would likely become the new preferred member before HUB1-VPN3 (at 190.984 ms).
Question # 7
What is the primary function of FortiView on FortiSASE?
A.
Presents raw log data in graphical format only, without sorting criteria or aggregated views.
B.
Generates real-time alerts for security events and presents them in a single text-based console without metadata.
C.
Displays individual logs on the GUI without aggregation, allowing administrators to sort events by time only.
D.
Provides consolidated consoles to analyze security events over time using graphical or text-based log views.
Full Access
Answer:
D
Explanation:
FortiView is designed to transform FortiSASE log information into aggregated, consolidated views that make operational and security analysis easier than reviewing individual raw log entries. The study guide describes FortiView as a consolidated series of consoles that enables administrators to analyze security events over a selected time period and according to different sorting criteria. It can display the resulting information through both graphical and text-based consoles and presents metadata derived from available logs rather than simply listing every log individually. FortiSASE_25_Administrator_Stud… Therefore, option D accurately describes FortiView. Options A and C incorrectly remove aggregation and flexible sorting, while B incorrectly characterizes FortiView primarily as an alert-generation mechanism and limits its presentation to a single text console. FortiView ' s core purpose is consolidated visibility and analysis.
================
Question # 8
What is the purpose of the priority/failover connection feature in FortiSASE Geofencing for managing VPN connections?
A.
It automatically balances VPN traffic across all available security POPs without prioritizing on-premises devices.
B.
It allows administrators to define rules to prioritize on-premises FortiGate connections for users in specific countries, with failover to a security POP if the FortiGate device is unavailable.
C.
It forces all remote users to connect only to the nearest security POP regardless of location.
D.
It restricts VPN access to users based on their geolocation without allowing failover options.
Full Access
Answer:
B
Explanation:
The priority/failover connection feature uses the remote user ' s geolocation to determine the preferred location where the VPN connection should terminate. Administrators can build country-based rules that prioritize either an on-premises FortiGate VPN gateway or a FortiSASE security POP. The FortiSASE study guide gives a specific example in which users connecting from Canada first attempt to establish the VPN with an on-premises FortiGate; if that device is unavailable, FortiClient fails over to the configured FortiSASE security POP. FortiSASE_25_Administrator_Stud… This is particularly useful for global organizations that want selected users to continue using regional on-premises infrastructure while retaining cloud-based resiliency. It is not load balancing across every POP, mandatory nearest-POP selection, or simple geolocation blocking. Therefore, option B precisely describes the feature ' s purpose.
Question # 9
A FortiGate device is in production. To optimize WAN link use and improve redundancy, you enable and configure SD-WAN.
What must you do as part of this configuration update process? (Choose one answer)
A.
Replace references to interfaces used as SD-WAN members in the firewall policies.
B.
Replace references to interfaces used as SD-WAN members in the routing configuration.
C.
Disable the interface that you want to use as an SD-WAN member.
D.
Purchase and install the SD-WAN license, and reboot the FortiGate device.
Full Access
Answer:
A
Explanation:
According to the SD-WAN 7.6 Core Administrator study guide and the FortiOS 7.6 Administration Guide, when you are migrating a production FortiGate to use SD-WAN, the most critical step involves reconfiguring how traffic is permitted and routed.
Reference Removal Requirement: Before an interface (such as wan1 or wan2) can be added as an SD-WAN member, it must be " unreferenced " in most parts of the FortiGate configuration. Specifically, if an interface is currently being used in an active Firewall Policy, the system will prevent you from adding it to the SD-WAN bundle.
Firewall Policy Migration (Option A): In a production environment, you must replace the references to the physical interfaces in your firewall policies with the new SD-WAN virtual interface (or an SD-WAN Zone). For example, if your previous policy allowed traffic from internal to wan1, you must update that policy so the Outgoing Interface is now SD-WAN. This allows the SD-WAN engine to take over the traffic and apply its steering rules.
Modern Tools: While this used to be a purely manual process, FortiOS 7.x includes an Interface Migration Wizard (found under Network > Interfaces). This tool automates the " search and replace " function, moving all existing policy and routing references from the physical port to the SD-WAN object to ensure minimal downtime.
Why other options are incorrect:
Option B: While you do need to update your routing (e.g., creating a static route for 0.0.0.0/0 pointing to the SD-WAN interface), the curriculum specifically emphasizes the replacement of references in firewall policies as the primary administrative hurdle, as policies are often more numerous and complex than the single static route required for SD-WAN.
Option C: You do not need to disable the interface. It must be up and configured, just removed from other configuration references so it can be " absorbed " into the SD-WAN bundle.
Option D: SD-WAN is a base feature of FortiOS and does not require a separate license or a reboot to enable.
Question # 10
Which two methods are available for provisioning FortiClient on endpoints using FortiSASE? (Choose two.)
A.
FortiClient can be provisioned using SCCM or GPO, but only through an external portal and not through the FortiSASE portal.
B.
FortiClient can be provisioned using installers with an invitation code from the FortiSASE portal and deployed through SCCM or GPO, or mobile device management (MDM) software.
C.
FortiClient can be provisioned by distributing the installer to end users for manual installation.
D.
FortiClient provisioning is limited to using mobile device management (MDM) software or manual installation without requiring an invitation code.
E.
FortiClient can be provisioned only by distributing installers to end users through the FortiSASE portal without an invitation code.
Full Access
Answer:
B, C
Explanation:
B and C are correct. The FortiSASE Administrator Study Guide explicitly states that FortiClient can be provisioned using installers embedded with an invitation code obtained from the FortiSASE portal. Administrators can then deploy the installer through enterprise software-distribution mechanisms such as Microsoft System Center Configuration Manager (SCCM) or Group Policy Object (GPO). The same installer can also be distributed through mobile device management (MDM) software.
The study guide also explicitly identifies manual installation as a supported deployment method: administrators can distribute the FortiClient installer directly to end users and have them install it on their endpoints. Consequently, C is also correct.
Invitation codes are important because they allow FortiClient to register with and become managed by the appropriate FortiSASE instance. The Enterprise Administrator material further explains that the default invitation code is embedded in preconfigured Windows and macOS installers, while custom invitation codes can place newly onboarded endpoints into specified endpoint groups and associated profiles.
A, D, and E are incorrect because they unnecessarily restrict supported deployment methods or incorrectly claim that an invitation code is not required.
Study Guide Reference: User Onboarding and Additional Features > FortiClient Deployment; Endpoint Management > Invitation Codes.
Question # 11
An existing Fortinet SD-WAN customer who has recently deployed FortiSASE wants to have a comprehensive view of, and combined reports for, both SD-WAN branches and remote users. How can the customer achieve this?
A.
Forward the logs from FortiSASE to Fortinet SOCaaS.
B.
Forward the logs from FortiGate to FortiSASE.
C.
Forward the logs from FortiSASE to the external FortiAnalyzer.
D.
Forward the logs from the external SD-WAN FortiAnalyzer to FortiSASE.
Full Access
Answer:
C
Explanation:
For customers with hybrid environments (on-premises SD-WAN branches and remote FortiSASE users), the FortiOS 7.6 and FortiSASE curriculum recommends centralized log aggregation for unified visibility.
Centralized Reporting: The standard architectural best practice is to forward logs from FortiSASE to an external FortiAnalyzer (Option C).
Unified View: Since the customer ' s on-premises FortiGate SD-WAN branches are already sending logs to an existing FortiAnalyzer, adding the FortiSASE log stream to that same FortiAnalyzer allows for the creation of combined reports.
Fabric Integration: This setup leverages the Security Fabric, enabling the FortiAnalyzer to provide a single pane of glass for monitoring security events, application usage, and SD-WAN performance metrics across the entire distributed network.
Why other options are incorrect:
Option A: SOCaaS is a managed service for threat monitoring, not a primary tool for an administrator to generate combined SD-WAN/SASE operational reports.
Option B: FortiSASE is not designed to act as a log collector or reporting hub for external on-premises FortiGates.
Option D: Data flows from the source (FortiSASE) to the collector (FortiAnalyzer), not the other way around.
Question # 12
The IT team is wondering whether they will need to continue using MDM tools for future FortiClient upgrades.
What options are available for handling future FortiClient upgrades?
A.
Enable the Endpoint Upgrade feature on the FortiSASE portal.
B.
FortiClient will need to be manually upgraded.
C.
Perform onboarding for managed endpoint users with a newer FortiClient version.
D.
A newer FortiClient version will be auto-upgraded on demand.
Full Access
Answer:
A
Explanation:
According to the FortiSASE 7.6 Feature Administration Guide and the latest updates to the NSE 5 SASE curriculum, FortiSASE has introduced native lifecycle management for FortiClient agents to reduce the operational burden on IT teams who previously relied solely on third-party MDM (Mobile Device Management) or GPO (Group Policy Objects) for every update.
The Endpoint Upgrade feature, found under System > Endpoint Upgrade in the FortiSASE portal, allows administrators to perform the following:
Centralized Version Control: Administrators can see which versions are currently deployed and which " Recommended " versions are available from FortiGuard.
Scheduled Rollouts: You can choose to upgrade all endpoints or specific endpoint groups at a designated time, ensuring that upgrades do not disrupt business operations.
Status Monitoring: The portal provides a real-time dashboard showing the progress of the upgrade (e.g., Downloading, Installing, Reboot Pending, or Success).
Manual vs. Managed: While MDM is still highly recommended for the initial onboarding (the first time FortiClient is installed and connected to the SASE cloud), all subsequent upgrades can be handled natively by the FortiSASE portal.
Why other options are incorrect:
Option B: Manual upgrades are inefficient for large-scale deployments (~400 users in this scenario) and are not the intended " feature-rich " solution provided by FortiSASE.
Option C: " Onboarding " refers to the initial setup. Re-onboarding every time a version changes would be redundant and counterproductive.
Option D: While the system can manage the upgrade, it is not " auto-upgraded on demand " by the client itself without administrative configuration in the portal. The administrator must still define the target version and schedule.
Question # 13
You want FortiGate to use SD-WAN rules to steer ping local-out traffic. Which two constraints should you consider? (Choose two.)
A.
You must configure each local-out feature individually to use SD-WAN.
B.
By default, FortiGate uses SD-WAN rules only for local-out traffic that corresponds to ping and traceroute.
C.
You can steer local-out traffic only with SD-WAN rules that use the manual strategy.
D.
By default, FortiGate uses SD-WAN rules only for local-out traffic that corresponds to ping and traceroute.
Full Access
Answer:
A, B
Explanation:
In the SD-WAN 7.6 Core Administrator curriculum, steering " local-out " traffic (traffic generated by the FortiGate itself, such as DNS queries, FortiGuard updates, or diagnostic pings) requires specific configuration because this traffic follows a different path than " forward " traffic.
Individual Configuration (Option A): By default, local-out traffic bypasses the SD-WAN engine and uses the standard system routing table (RIB/FIB). To use SD-WAN rules for specific features like DNS or RADIUS, you must individually enable the sdwan interface-select-method within that feature ' s configuration (e.g., config system dns or config user radius).
Default Steerable Traffic (Option B): In FortiOS 7.6, while most local-out traffic is excluded from SD-WAN by default, the system is designed so that when SD-WAN is active, it primarily considers SD-WAN rules for specific diagnostic local-out traffic—specifically ping and traceroute—to allow administrators to verify path quality using the same logic as user traffic.
Why other options are incorrect:
Option C: Local-out traffic can be steered using any SD-WAN strategy (Manual, Best Quality, etc.), provided the interface-selection-method is set to sdwan.
Question # 14
Which secure internet access (SIA) use case minimizes individual endpoint configuration? (Choose one answer)
A.
Agentless remote user internet access
B.
SIA for FortiClient agent remote users
C.
Site-based remote user internet access
D.
SIA using ZTNA
Full Access
Answer:
C
Explanation:
According to the FortiSASE 7.6 Architecture Guide and Administration Guide, the Site-based remote user internet access use case is the only deployment model that completely eliminates the need for individual endpoint configuration.
Centralized Enforcement: In a site-based deployment, a " thin edge " device (such as a FortiExtender or a FortiGate in LAN extension mode) is installed at the remote site. This device establishes a secure tunnel to the FortiSASE Point of Presence (PoP).
Zero Endpoint Configuration: Because the traffic redirection happens at the network gateway level, individual devices (laptops, IoT devices, mobile phones) behind the site-based device do not require any specialized software or settings. They simply connect to the local network as they would normally, and their traffic is automatically secured by the SASE cloud.
Comparison with Other Modes:
Agent-based (Option B): Requires the installation and maintenance of FortiClient software on every device, often managed via MDM tools.
Agentless (Option A): While it doesn ' t need an agent, it typically requires the configuration of Explicit Web Proxy settings or the distribution of a PAC (Proxy Auto-Configuration) file via GPO or SCCM to each device ' s browser.
ZTNA (Option D): Generally requires an endpoint agent (FortiClient) to perform posture checks and identity verification, involving significant endpoint-level configuration.
Why other options are incorrect:
Option A: Agentless mode is often confused with being " configuration-free, " but it still requires endpoints to be pointed toward the FortiSASE proxy.
Option B: This is the most configuration-intensive mode, requiring full software lifecycles for every endpoint.
Option D: ZTNA is an access methodology that adds configuration complexity (tags, certificates, posture checks) rather than minimizing it.
Question # 15
Refer to the exhibit.
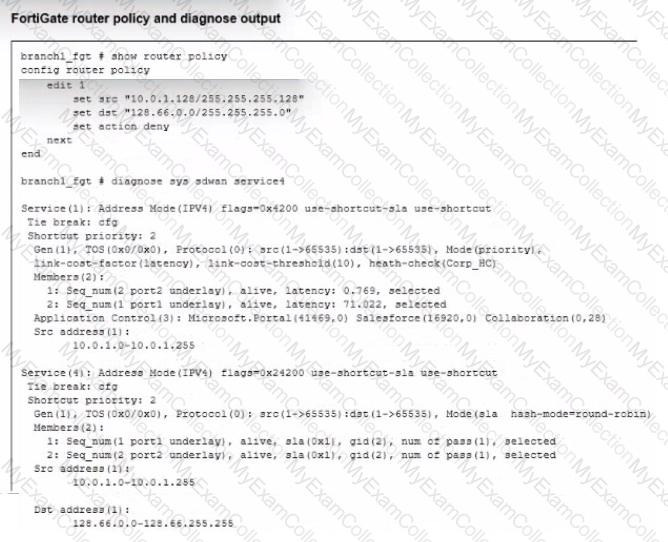
How does FortiGate handle the traffic with the source IP 10.0.1 130 and the destination IP 128 66.0 125?
A.
FortiGate steers the traffic flow through port2
B.
FortiGate drops the traffic flow
C.
FortiGate routes the traffic flow according to the FIB.
D.
FortiGate load balances the traffic flow through port1 and port2
Full Access
Answer:
C
Explanation:
The correct answer is C. FortiGate routes the traffic flow according to the FIB. The exhibit shows a regular policy route configured with source 10.0.1.128/255.255.255.128 and destination 128.66.0.0/255.255.255.0. The test source 10.0.1.130 belongs to the 10.0.1.128/25 subnet, and destination 128.66.0.125 belongs to 128.66.0.0/24; therefore, the traffic matches this policy route.
Crucially, the route contains set action deny. For a router policy, this does not mean that FortiGate discards the packet as a firewall DENY would. It represents Stop Policy Routing. Fortinet explains that when a packet matches this action, FortiGate stops policy-route processing and routes the packet using the forwarding information base (FIB).
Regular policy routes also have precedence over SD-WAN rules. Consequently, even though SD-WAN service 4 shown in the exhibit matches source 10.0.1.0-10.0.1.255 and destination 128.66.0.0-128.66.255.255, its round-robin selection of port1 and port2 does not control this flow. The matching regular policy route terminates policy routing first.
Study Guide Reference: SD-WAN Configuration and Monitoring > Policy Routes > Route Lookup and FIB Processing, pages 423–424.

