Question # 4
When Dynamic Host Configuration Protocol (DHCP) snooping is enabled on a FortiSwitch VLAN, which two statements are true? (Choose two answers)
Question # 5
Refer to the exhibit.
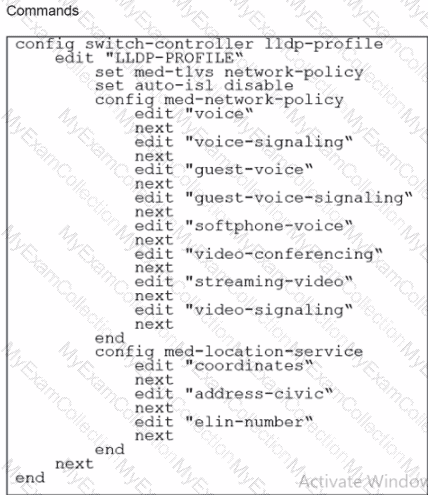
The profile shown in the exhibit is assigned to a group of managed FortiSwitch ports, and these ports are connected to endpoints which are powered by PoE.
Which configuration action can you perform on the LLDP profile to cause these endpoints to exchange PoE information and negotiate power with the managed FortiSwitch?
Question # 6
Refer to the diagnostic output:
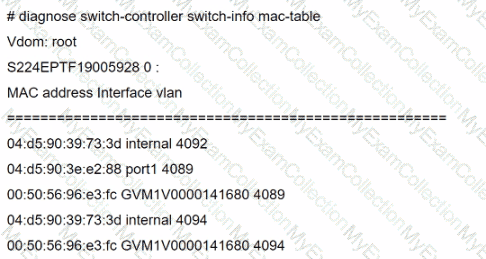
Two entries in the exhibit show that the same MAC address has been used in two different VLANs. Which MAC address is shown in the above output?
Question # 7
Refer to the exhibits.
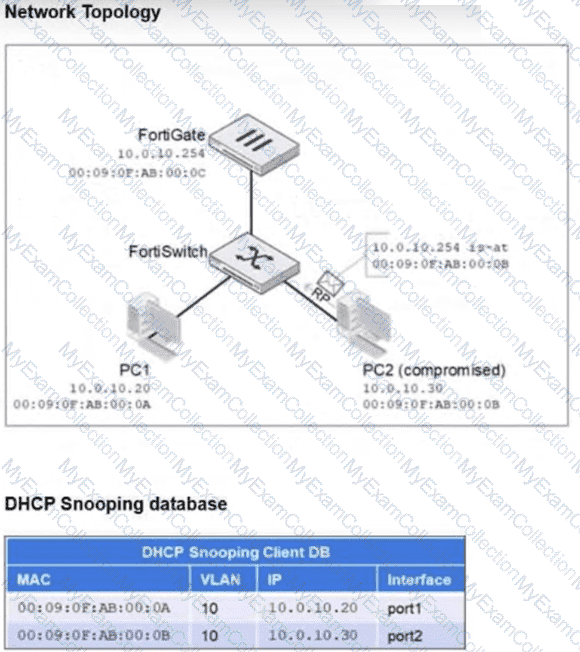
All three FortiSwitch-connected ports are configured in VLAN 10. FortiGate acts as the Dynamic Host Configuration Protocol (DHCP) server and is connected to a DHCP snooping trusted trunk port. PC1 and PC2 are connected to ports configured as untrusted for Dynamic ARP Inspection (DAI), and no static bindings are configured in the IP source guard (IPSG) database. PC2 is compromised and attempts to spoof the FortiGate IP address by sending forged Address Resolution Protocol (ARP) replies with its own MAC address. What will FortiSwitch do with the ARP packets from PC2? (Choose one answer)
Question # 8
You are designing a FortiSwitch backbone where every FortiSwitch device must connect to every other FortiSwitch for maximum redundancy. To maintain connectivity while preventing loops, which protocol or feature must you configure on the switches? (Choose one answer)
Question # 9
What happens if FortiSwitch fails to discover either FortiEdge Cloud or a FortiGate with FortiLink?
Question # 11
Refer to the exhibit.
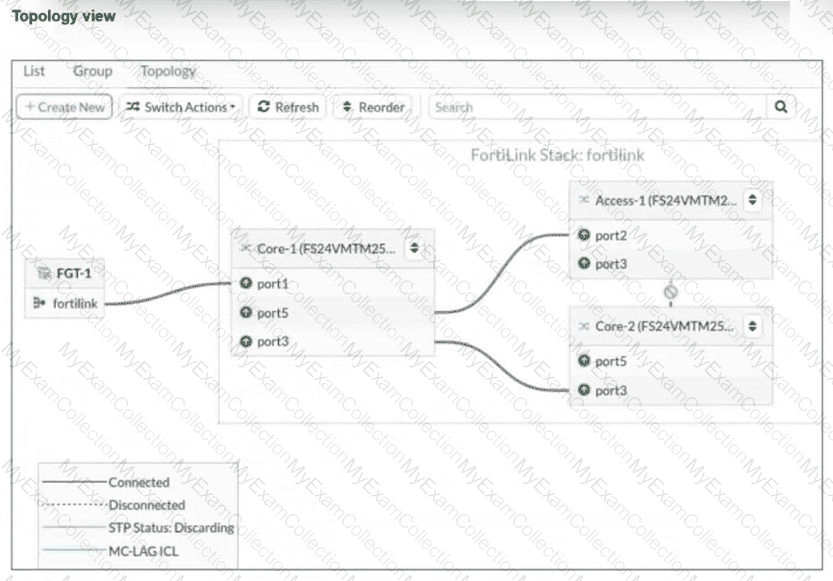
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)
Question # 12
Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)
Question # 13
Which LLDP-MED Type-Length-Values does FortiSwitch collect from endpoints to track network devices and determine their characteristics?
Question # 14
(Full question statement start from here)
You enable Dynamic Host Configuration Protocol (DHCP) snooping on a VLAN and configure a FortiSwitch port astrustedfor DHCP snooping. What additional step is required to configure the port as trusted forDynamic ARP Inspection (DAI)? (Choose one answer)
Question # 15
Refer to the exhibit.
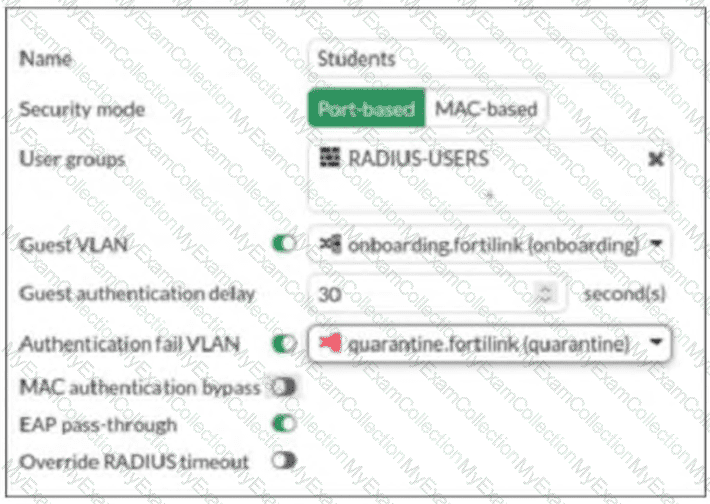
The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)
Question # 16
How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?
Question # 17
You are deploying a new FortiSwitch device in a branch office and you want it to be automatically detected and managed by FortiGate. Which FortiSwitch feature enables automatic detection during deployment? (Choose one answer)
Question # 18
(Full question statement start from here)
A FortiGate is connected to a pair of FortiSwitch devices.
For redundancy, FortiGate must use uplinks on both switches simultaneouslywithout depending on Spanning Tree Protocol (STP).
Which configuration is required? (Choose one answer)
Question # 19
Refer to the exhibit.
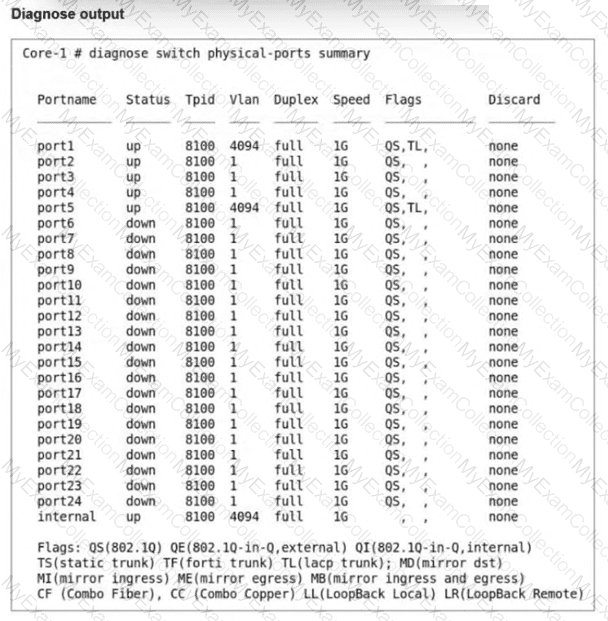
The command diagnose switch physical-ports summary is executed on FortiSwitch.
Based on the VLAN assignments shown in the output, what is the most likely management configuration of this FortiSwitch? (Choose one answer)
Question # 20
In which two ways can you assign a FortiSwitch port to a VDOM using multi-tenancy setup? (Choose two.)
Question # 21
Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)
Question # 22
Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?
Question # 23
You are designing a multi-tenant network using FortiSwitch devices in standalone mode. Security is a priority and each tenant’s servers must be completely isolated from one another, and from all other servers in the network, to prevent lateral communication. However, all servers must have access to the shared FortiGate firewall for internet access. Which type of private VLAN (PVLAN) configuration should you apply to meet these security requirements? (Choose one answer)
Question # 24
Refer to the exhibits
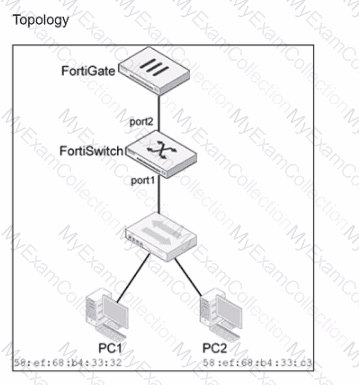
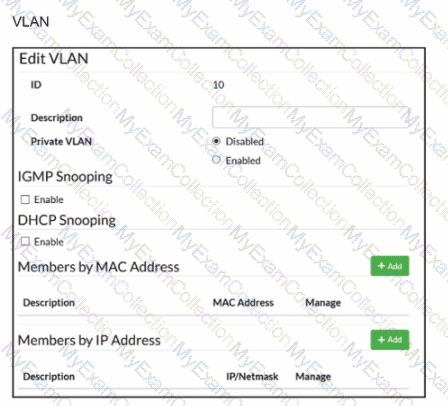
Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch. Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)
Question # 25
In which two ways can you assign a FortiSwitch port to a VDOM using a multi-tenancy setup? (Choose two answers)
Question # 26
(Full question statement start from here)
What is one key advantage of using a sniffer profile on FortiSwitch compared to using the sniffer command? (Choose one answer)
Question # 27
What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)
Question # 28
What are two ways in which automatic MAC address quarantine works on FortiSwitch? (Choose two.)
Question # 29
Refer to the exhibit.
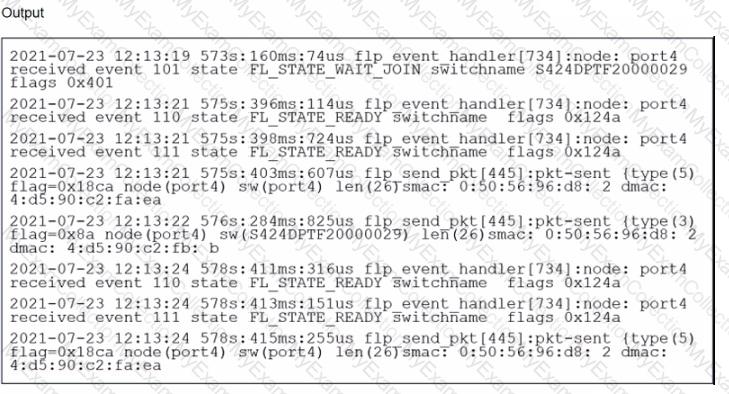
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)
Question # 30
Which two statements about the FortiLink authorization process are true? (Choose two.)
Question # 31
Refer to the exhibit.
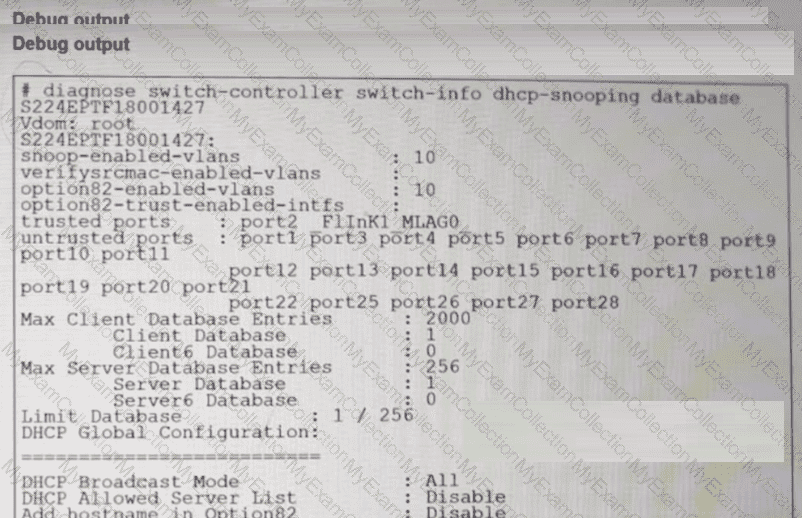
After reviewing the CLI command output, which two conclusions can you make about the Dynamic Host Configuration Protocol (DHCP) snooping configuration? (Choose two answers)
Question # 32
(Full question statement start from here)
Refer to the exhibits.
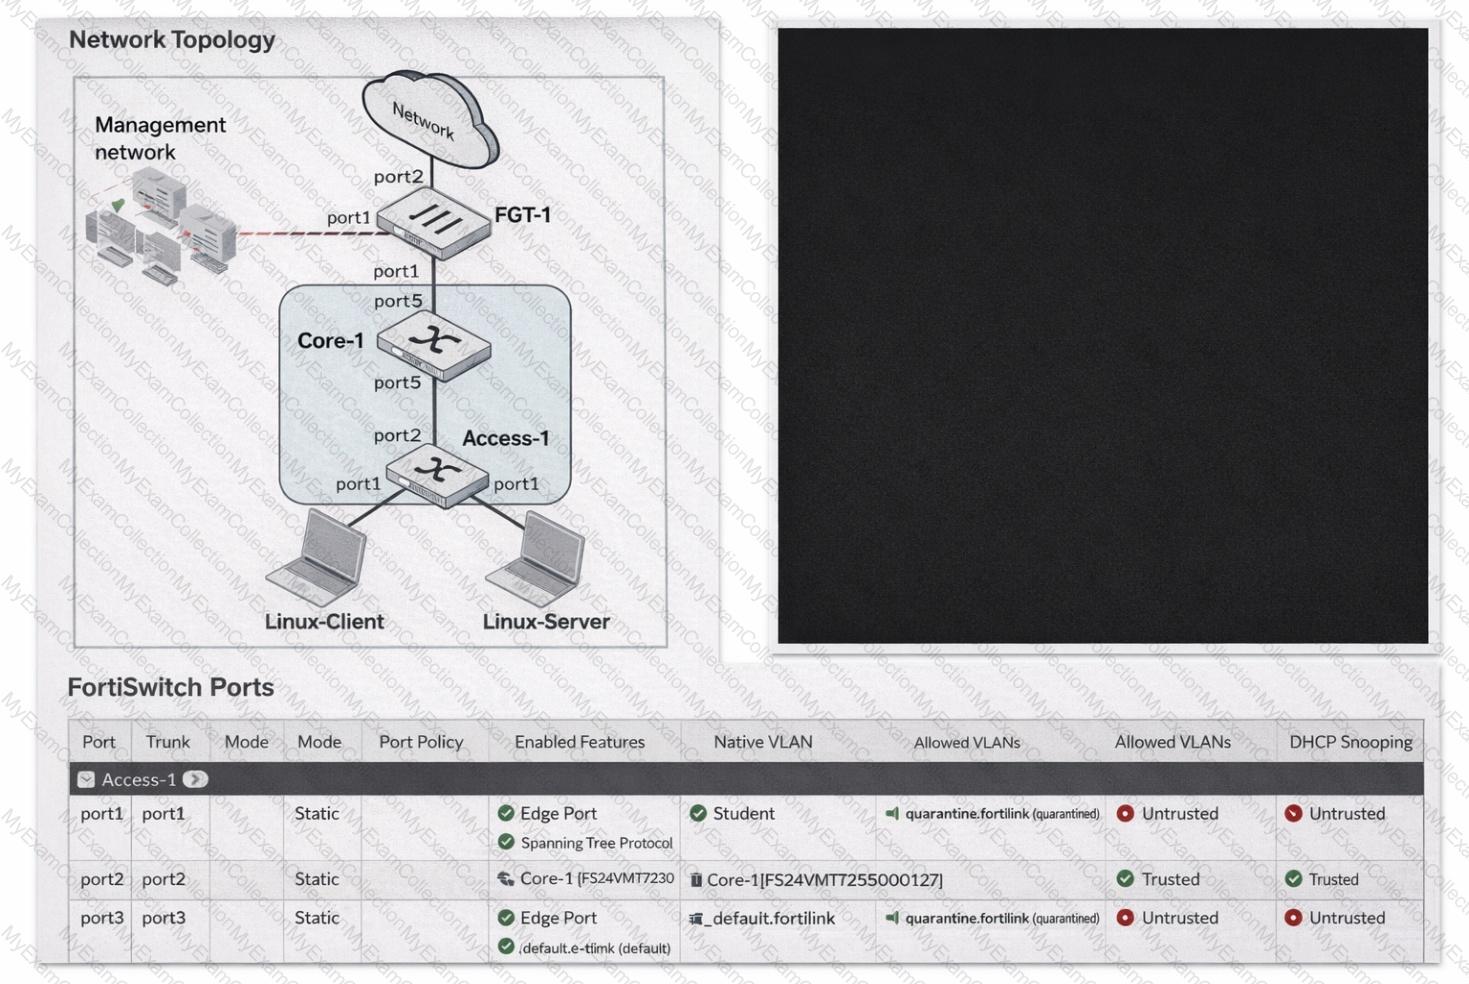
You enable Dynamic Host Configuration Protocol (DHCP) snooping on the VLAN,Student. The Linux-Client VM sends DHCP requests, and tcpdump confirms the broadcasts. However, the Linux-Server VM, acting as a DHCP server, receives no DHCP traffic. What is the most likely cause of this intra-VLAN traffic being blocked? (Choose one answer)
Question # 33
Refer to the exhibit.
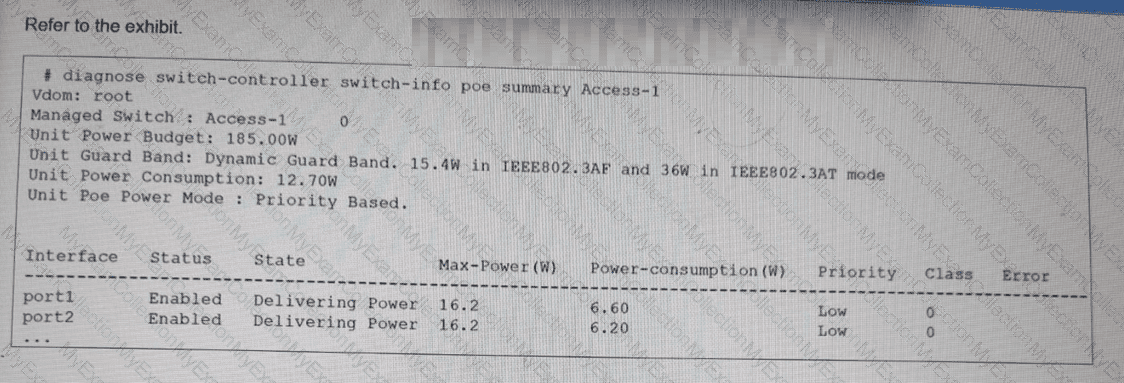
The FortiSwitch CLI output of the diagnose switch-controller switch-info poe summary command for the switch Access-1 is shown. It shows that two ports have Power over Ethernet (PoE) enabled and are already in use. What is the most important consideration if you want to connect additional PoE devices to FortiSwitch? (Choose one answer)
Question # 34
Which QoS mechanism maps packets with specific CoS or DSCP markings to an egress queue?