Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: my75ex

Home > WatchGuard > Locally-Managed Fireboxes > Network-Security-Essentials

Network-Security-Essentials Network Security Essentials for Locally-Managed Fireboxes Question and Answers

Question # 4

As you troubleshoot a Branch Office VPN tunnel, you see the log message below. Which settings can you modify in the BOVPN virtual interface configuration to resolve this issue? (Select one.)

(Log message: msg='iprocess: SA Proposal mismatch on Phase 2 negotiation')

A.

Phase 1 Settings

B.

Phase 2 Settings

C.

VPN Routes

D.

BOVPN-Allow policies

E.

Gateway Settings

Full Access
Question # 5

You want to create a branch office VPN virtual interface between a remote Firebox and your headquarters Firebox so the remote Firebox can send log data to a server at headquarters. For the log data to be sent from the remote Firebox over the VPN successfully, what BOVPN virtual interface setting must you configure? (Select one.)

A.

An IPSec certificate, instead of a Pre-shared key

B.

IKEv2 in the Phase 1 settings

C.

Dead Peer Detection (DPD)

D.

Perfect Forward Secrecy (PFS)

E.

Virtual IP addresses

Full Access
Question # 6

If the Firebox does not have a feature key installed, which of these statements are true? (Select three.)

A.

You cannot upgrade the Firebox

B.

You cannot configure subscription services

C.

You cannot run the Web Setup Wizard

D.

You cannot save configuration changes to the Firebox

E.

Only one user can connect to the Internet through the Firebox

Full Access
Question # 7

You configured your Firebox as a DHCP server and want to verify the status of the leased addresses. You found this information in Firebox System Manager > Status Report. What is true about DHCP leases in this deployment? (Select two.)

DHCP Leases Log Extract:

lease 10.20.1.100 {

interface vlan20;

starts 4 2023/03/09 21:42:25;

ends 4 2023/03/09 22:42:25;

binding state active;

hardware ethernet 00:50:56:9a:75:d0;

client-hostname "Laptop1";

}

Summary for 10.20.1.0/24: 1 out of 51 IPs are leased

lease 10.0.1.2 {

interface eth1;

starts 4 2023/03/09 21:42:33;

ends 5 2023/03/10 05:42:33;

binding state active;

hardware ethernet 00:50:56:b6:22:9f;

client-hostname "Server1";

}

Summary for 10.0.1.0/24: 1 out of 253 IPs are leased

Summary for all: 2 out of 304 IPs are leased

A.

The MAC address for the host using 10.0.1.2 is 00:50:56:9a:75

B.

DHCP leases for the 10.0.1.0/24 network are valid for 8 hours

C.

DHCP leases for the 10.20.1.0/24 network are valid for 24 hours

D.

252 IP addresses are currently available in the address pool for the 10.0.1.0/24 network

E.

The hostname Server1 is associated with the IP address 10.20.1.100

Full Access
Question # 8

What steps must you take to send log messages from a Firebox to WatchGuard Cloud? (Select two.)

A.

Enable WatchGuard Cloud in the Firebox configuration

B.

Add the FQDN of your WatchGuard Cloud account as a Log Server on the Firebox

C.

Define an Authentication Key that all your Fireboxes use to communicate with WatchGuard Cloud

D.

Configure Dimension to synchronize log messages with WatchGuard Cloud

E.

Use the WatchGuard Cloud Add Device wizard to add the Firebox to WatchGuard Cloud

Full Access
Question # 9

You configured email notifications in WatchGuard Cloud for your Firebox Device Alarms and want to receive an email when your users download any .exe files through an HTTP proxy. You must enable what type of log message in the Firebox configuration? (Select one.)

A.

Allowed traffic logs for the HTTP proxy policy

B.

Alarm logs for the EXE/DLL Body Content rule in the HTTP proxy

C.

Diagnostic logs for Gateway AntiVirus

D.

Alarm logs for when a virus is detected in the HTTP proxy

E.

Denied traffic logs for the HTTP proxy policy

Full Access
Question # 10

Which of these is a network IP address? (Select one.)

A.

1G2 153 10 O 1

B.

1Q2 158.10 0-24

C.

172 16 100 1/12

D.

10 0.1 255 8

E.

10.10.10.255/24

Full Access
Question # 11

You have an existing network infrastructure built out that uses tagged and untagged VLAN networks. Based on the diagram below, which VLANs must you add to the Firebox interface? (Select one.)
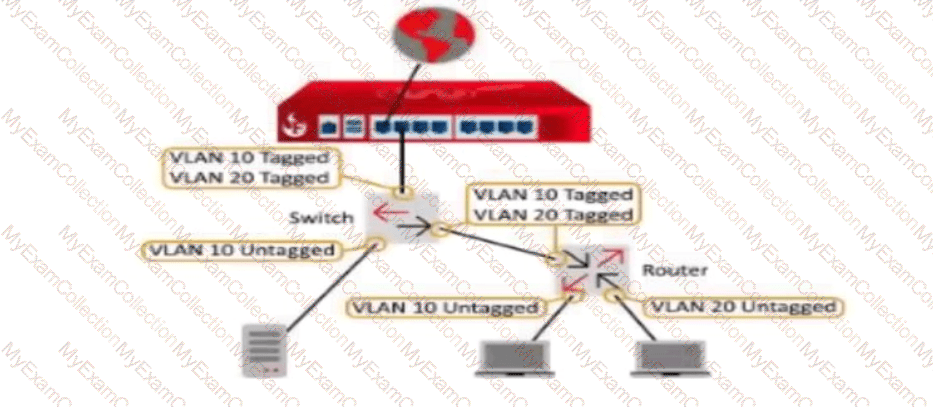
A.

VLAN 10 Untagged and VLAN 20 Untagged

B.

VLAN 10 Tagged and VLAN 20 Tagged

C.

VLAN 10 Untagged and VLAN 20 Tagged

D.

VLAN 10 Tagged and VLAN 20 Untagged

E.

VLAN 10 Untagged, VLAN 10 Tagged, and VLAN 20 Tagged

Full Access
Question # 12

What type of NAT enables clients on a private network to connect to servers on the Internet? (Select one.)

A.

Static NAT

B.

Dynamic NAT

C.

NAT loopback

D.

Hairpin NAT

Full Access
Question # 13

Which of these statements are true for this log message? (Select three.)

(Log context: A Traffic Monitor log entry detailing an HTTP connection through an HTTP-proxy policy that was terminated due to a signature match by Gateway AntiVirus)

A.

Application Control detected the application as a virus

B.

The URL path matched the proxy content type restrictions

C.

The connection used an HTTP Proxy

D.

Gateway AntiVirus detected a virus

E.

The connection was denied

F.

The connection used an HTTP Packet Filter

Full Access
Question # 14

When does a network host make an ARP request? (Select one.)

A.

To find the IP address associated with a hostname

B.

To find the IP address of the default gateway

C.

To find the hostname associated with an IP address

D.

To find the MAC address associated with an IP address

E.

To find the IP address associated with a MAC address

Full Access
Question # 15

Which of these is a valid host IP address in the subnet 10.0.1.0/24? (Select one.)

A.

10.0.10.24/24

B.

10.0.1.255/24

C.

10.0.1.100/24

D.

10.0.0.1/24

E.

10.0.1.0/24

Full Access
Question # 16

Your network was the target of an attack last week. You want to learn more about the source of the attack. What monitoring tools can you use to get started? (Select one.)

A.

Traffic Monitor in Firebox System Manager

B.

FireWatch in Fireware Web UI

C.

Discovery in Fireware Web UI

D.

WatchGuard Log Catalog

E.

Log Search and reports in WatchGuard Cloud or Dimension

Full Access
Question # 17

A Firebox has an external IP address of 203.0.113.100. A public web server with the IP address 10.0.1.80 is connected to a Firebox internal network. What is the effect of the policy shown in this image? (Select one.)
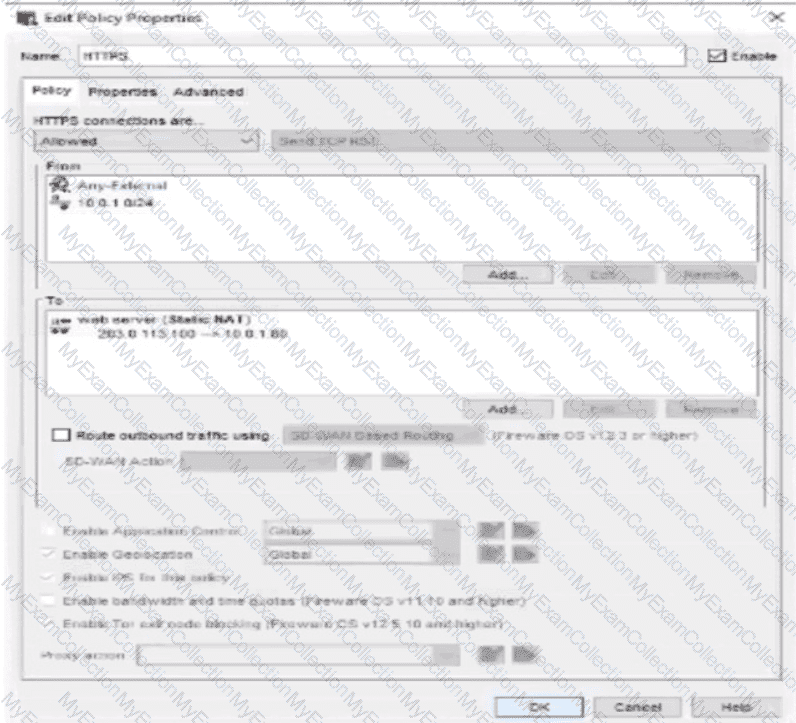
A.

Allows users on the Internet to connect to the 10.0.1.80 IP address of the web server

B.

Applies dynamic NAT to the 10.0.1.80 IP address of the web server to allow inbound connections

C.

Allows users on the Internet and the 10.0.1.0/24 network to use the internal IP address of the Firebox to connect to the web server

D.

Allows users on the Internet and the 10.0.1.0/24 network to use the external IP address of the Firebox to connect to the web server

Full Access
Question # 18

In a Mobile VPN configuration, why would you choose default-route (full tunnel) VPN instead of split tunnel VPN? (Select one.)
A.

Default-route VPN uses less bandwidth.

B.

Default-route VPN enables your Firebox to examine all remote user traffic.

C.

Default-route VPN uses less processing power.

D.

Default-route VPN automatically allows dynamic NAT.

E.

Default-route VPN is the only option you can use to apply security services to connections routed to your internal servers.

Full Access