Question # 4
Which two statements about proxy IDs are correct? (Choose two.)
A.
Proxy IDs cannot override default Junos behavior.
B.
By default, for a route-based IPsec VPN, a Junos security device sets the proxy ID to 0.0.0.0/0.
C.
Proxy IDs must match on both peers for a Phase 2 tunnel to establish.
D.
Proxy IDs are created during IKE Phase 1.
Full Access
Answer:
B, C
Explanation:
The correct answers are B and C. In Junos route-based IPsec VPNs, the default proxy ID is broad: local 0.0.0.0/0, remote 0.0.0.0/0, and service any. This default behavior allows routed traffic entering the secure tunnel interface to determine what is protected by the VPN rather than requiring a narrow policy-based encryption domain. Juniper’s IPsec VPN configuration guidance also states that proxy IDs are used in Phase 2 negotiations, and that a proxy ID mismatch is one of the common causes of Phase 2 failure. For interoperability with some third-party VPN peers, Juniper notes that proxy IDs may need to be manually configured to match the peer.
Option A is wrong because proxy IDs can override default route-based behavior when manually configured, especially when a peer requires specific local and remote protected subnets. Option D is wrong because proxy IDs are not created during IKE Phase 1. Phase 1 builds the secure IKE channel; proxy IDs belong to Phase 2/IPsec SA negotiation, where the peers agree on traffic selectors for encrypted traffic. Reference topics: IPsec VPN, route-based VPNs, proxy IDs, Phase 2 negotiation, traffic selectors, third-party VPN interoperability.
Question # 5
Which two statements are correct about Juniper Secure Connect? (Choose two.)
A.
Juniper Secure Connect uses a policy-based VPN.
B.
Juniper Secure Connect can use a self-signed certificate.
C.
Juniper Secure Connect uses a route-based VPN.
D.
Juniper Secure Connect cannot use a self-signed certificate.
Full Access
Answer:
B, C
Explanation:
The correct answers are B and C. Juniper Secure Connect uses route-based VPN connectivity, not policy-based VPN connectivity. Juniper’s Secure Connect user guide contrasts Dynamic VPN and Juniper Secure Connect and identifies Juniper Secure Connect as using route-based VPN connectivity, with a tunnel interface selected or created to bind the VPN. This is why SRX configurations for Juniper Secure Connect use an st0 tunnel interface and routing/security policy logic, rather than policy-based encryption tied directly to individual firewall policies.
Option B is also correct because Juniper Secure Connect can use a self-signed certificate. Juniper’s certificate deployment guidance states that before deploying Juniper Secure Connect, the SRX should use an appropriate certificate, which can be a signed certificate, a self-signed certificate, or a Let’s Encrypt-signed certificate. The documentation also shows generating a self-signed certificate and binding it to the SRX for Secure Connect use.
Option A is wrong because policy-based VPN describes older Dynamic VPN behavior, not Juniper Secure Connect. Option D is directly contradicted by Juniper’s certificate guidance. Reference topics: Juniper Secure Connect, route-based VPN, st0 tunnel interface, certificate deployment, self-signed certificate support.
Question # 6
How does the SSL proxy service identify SSL traffic?
A.
by examining the URL
B.
by using AppID results
C.
by examining the destination port
D.
by reading the server certificate
Full Access
Answer:
B
Explanation:
The correct answer is B. by using AppID results. Junos SSL proxy does not identify SSL/TLS sessions by assuming that encrypted traffic always uses TCP/443. That would be technically weak because SSL/TLS can run on nonstandard ports, and non-SSL applications can also use common HTTPS ports. Juniper’s SSL proxy documentation explains that SSL proxy works with application security services and that AppID is used in the encrypted-traffic inspection workflow. In earlier wording from Juniper AppSecure material, SSL proxy uses application identification services to determine whether a session is SSL encrypted; in current Junos documentation, SSL proxy and AppID are tightly linked so encrypted sessions can be identified, decrypted, inspected, and then re-encrypted for enforcement.
Option A is wrong because the URL is inside the HTTP payload, and in HTTPS much of the meaningful HTTP content is encrypted before SSL proxy inspection occurs. Option C is wrong because destination port is only a rough hint, not a reliable detection method. Option D is wrong because certificates are used in the SSL/TLS handshake and proxy trust model, but the service’s traffic classification relies on AppID results, not merely reading the server certificate. Reference topics: SSL Proxy, AppID, encrypted session detection, SSL/TLS inspection, application security services.
Question # 7
Which statement is correct about Active Directory as an identity source for identity-aware security policies?
A.
It supports a maximum of two domains.
B.
It supports logical systems.
C.
It supports 20 Active Directory servers per domain.
D.
It tracks non-Windows Active Directory users.
Full Access
Answer:
A
Explanation:
The correct answer is A. It supports a maximum of two domains. Juniper’s Active Directory identity-source configuration guidance states that an SRX Series Firewall using the integrated user firewall/Active Directory identity source can be configured for a maximum of two domains. That is the exact limit relevant to this question. The same Juniper configuration page separately states that a maximum of 10 domain controllers can be configured, which directly eliminates option C because the supported figure is not 20 Active Directory servers per domain.
Option B is wrong because Active Directory identity source is not presented as a logical-systems feature in the JNCIS-SEC identity-aware firewall context. Option D is wrong because the primary Active Directory mechanism reads Windows domain controller event logs and uses WMI/DCOM plus LDAP to build IP-to-user and group mappings. Juniper describes the SRX as reading and monitoring the Windows event log on the domain controller, then using LDAP to obtain user/group information. Non-domain or non-Windows cases typically require alternate authentication behavior such as captive portal, not native Active Directory event-log tracking.
Reference topics: Identity-Aware Security Policies, Active Directory identity source, integrated user firewall, domain limits, domain controllers, WMIC, LDAP mapping.
Question # 8
You work on the security operations team that manages firewalls only. In your data center, there are two SRX chassis clusters. These clusters operate on VLAN 1042. The network team advises you that they see the same MAC address coming from both chassis clusters for reth0.
Why is this occurring?
A.
The same cluster ID was used on both clusters.
B.
RGO is active on both node0 and node1 due to split-brain.
C.
Chassis clusters must be on separate VLANs.
D.
Link Aggregation Control Protocol is not synchronized.
Full Access
Answer:
A
Explanation:
The correct answer is A. The same cluster ID was used on both clusters. In an SRX chassis cluster, a redundant Ethernet interface, or reth, uses a cluster-derived virtual MAC address. When two separate chassis clusters are placed in the same Layer 2 domain and use the same cluster ID, their corresponding reth interfaces can generate the same virtual MAC address. That is exactly why the network team sees the same MAC address for reth0 from both clusters on VLAN 1042. Juniper community guidance states bluntly that the reth interface MAC address is derived from the cluster ID and that two clusters using the same ID produce identical MAC addresses.
Option B is wrong because split-brain would describe both nodes inside the same cluster thinking they are primary, not two separate chassis clusters producing the same reth MAC address. Option C is wrong because multiple SRX clusters can exist on the same VLAN if their cluster IDs are unique. Option D is wrong because LACP synchronization affects bundled link operation, not the generation of the reth virtual MAC address. The correction is to assign unique cluster IDs to clusters sharing the same Layer 2 segment. Reference topics: HA Clustering, chassis cluster ID, reth virtual MAC address, duplicate MAC prevention, Layer 2 cluster design.
Question # 9
In Juniper high availability (HA) SRX Series device implementations, which interface will be used to exchange session state, configuration files, and ensure session continuity across nodes using the proprietary Trivial Network Protocol?
A.
fab
B.
fxp0
C.
fxp1
D.
swfab
Full Access
Answer:
A
Explanation:
The correct answer is A. fab. In SRX Series chassis clustering, the fabric interface, shown as fab0/fab1, is the data-plane HA link used between cluster nodes. Juniper states that SRX chassis clusters use the fabric interface for session synchronization and traffic forwarding, and that the fabric link synchronizes dynamic runtime state, including session-state objects created by NAT, ALG, authentication, and IPsec processing. This is what enables stateful failover and session continuity when traffic processing moves between nodes.
Option B, fxp0, is wrong because fxp0 is the out-of-band management interface, not the chassis-cluster synchronization path. Option C, fxp1, is tempting but wrong for this question: fxp1 is the control-link interface used for control-plane cluster functions such as heartbeats and cluster control communication, not the main session-state synchronization path. Option D, swfab, is not the standard SRX chassis-cluster fabric interface name used for this function. Juniper’s clustering configuration examples specifically define fab0 and fab1 as the interfaces used for the fabric connection and data-plane RTO/session synchronization.
Question # 10
Which two steps are necessary to prepare the Active Directory domain for a JIMS installation? (Choose two.)
A.
Create two limited access user accounts.
B.
Create three limited access user accounts.
C.
Add one full access user account to Active Directory groups.
D.
Add limited access user accounts to Active Directory groups.
Full Access
Answer:
A, D
Explanation:
The correct answers are A and D. Preparing Active Directory for JIMS requires creating limited-permission service accounts and assigning those accounts to the required Active Directory groups. Juniper’s JIMS deployment guidance states that you must create service accounts so JIMS can read from the defined directory services and identity producers; if PC probing is used, a service account is also required for that function. The same JIMS documentation includes a section named Configure Limited-Permission User Accounts, followed by Add Limited Permission User Accounts to Active Directory Groups.
Option A is correct because the JIMS preparation workflow commonly uses limited-permission accounts for event log access and PC probe access. Juniper identifies accounts such as JIMS-EventLogRemoteAccess and JIMS-PC-Probe in the Active Directory group-membership procedure. Option D is correct because those limited accounts must be added to the proper AD groups, including Event Log Readers and the groups required for remote management or PC probe operation.
Option B is wrong because the tested preparation requirement is not three limited-access accounts. Option C is wrong because JIMS should not be prepared by adding a broad full-access account; the course objective is least-privilege identity collection. Reference topics: JIMS, Active Directory preparation, limited-permission service accounts, Event Log Readers, PC probe account.
Question # 11
What are two properties negotiated during IKE Phase 2? (Choose two.)
A.
routing protocol
B.
tunneling protocol
C.
aggressive mode
D.
Perfect Forward Secrecy
Full Access
Answer:
B, D
Explanation:
The correct answers are B and D. IKE Phase 2 negotiates the IPsec security associations used to protect actual user data through the VPN tunnel. Juniper explains that after Phase 1 establishes a secure authenticated channel, Phase 2 negotiates SAs for the data transmitted through the IPsec tunnel. A Phase 2 proposal includes the IPsec security protocol, which is either ESP or AH, along with selected encryption and authentication algorithms. In the wording of this question, that maps to the tunnel/security protocol property.
Option D, Perfect Forward Secrecy, is also correct because Phase 2 proposals can specify a Diffie-Hellman group when PFS is desired. PFS forces a new DH key exchange for Phase 2 keys so that compromise of earlier keying material does not expose later IPsec encryption keys. Option A is wrong because routing protocols are not negotiated by IKE Phase 2; routing is handled separately over or toward the tunnel interface. Option C is wrong because aggressive mode is an IKEv1 Phase 1 exchange mode, not a Phase 2 property. Juniper specifically states that Phase 2 always uses quick mode in IKEv1. Reference topics: IKE Phase 2, IPsec SA negotiation, ESP/AH, Perfect Forward Secrecy, quick mode.
Question # 12
What is a function of the Juniper Identity Management Service?
A.
encrypting user e-mail
B.
logging malicious code sent through ingress and egress ports
C.
encrypting network data traffic
D.
maintaining a centralized authentication table
Full Access
Answer:
D
Explanation:
The correct answer is D. maintaining a centralized authentication table. Juniper Identity Management Service, or JIMS, is used with SRX Series Firewalls to collect user-identity information from identity sources such as Microsoft Active Directory, domain controllers, and Exchange servers, then provide that identity data to SRX enforcement points. Juniper describes JIMS as storing IP address, username, and group-relationship information in its cache and generating authentication entries used for user-based or group-based access control on SRX firewalls. Juniper’s Identity-Aware Firewall documentation also states that the authentication table contains the IP address, username, and group mapping information used as the authentication source.
Option A is wrong because JIMS is not an email-encryption service. Option B is wrong because malicious-code logging belongs to security inspection features such as antivirus, IDP, or ATP workflows, not JIMS. Option C is wrong because network data encryption is handled by technologies such as IPsec VPN or SSL/TLS, not identity management. JIMS exists to centralize identity-to-IP mapping so identity-aware security policies can match users and groups instead of relying only on source IP addresses. Reference topics: Identity-Aware Security Policies, JIMS, authentication table, user-to-IP mapping, group-based policy enforcement.
Question # 13
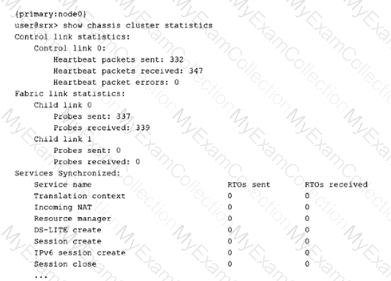
Referring to the exhibit, which two statements are correct? (Choose two.)
A.
Fabric link 0 is working.
B.
The control link is working.
C.
Fabric link 1 is failing.
D.
The control link is failing.
Full Access
Answer:
A, B
Explanation:
The correct answers are A and B. The exhibit shows show chassis cluster statistics. Under Control link statistics, Control link 0 has heartbeat packets sent and received, with heartbeat packet errors: 0. That is the clearest indication that the control link is operating normally. Juniper describes chassis-cluster control-plane verification as checking control-link heartbeat packets sent and received, along with heartbeat errors. If both send and receive counters are incrementing and errors are zero, the control link is functioning.
Option A is also correct because under Fabric link statistics, Child link 0 shows probes sent and probes received. Juniper uses fabric-link probe counters to verify fabric-link operation; nonzero sent and received probe counters indicate that the link is participating in fabric monitoring. Option C is not the safest conclusion from this exhibit alone. Child link 1 shows zero probes sent and received, but the output does not prove that a second fabric child link is configured and failing; it could simply be unused or not configured in this deployment. Option D is directly contradicted by the healthy heartbeat counters. Reference topics: HA Clustering, chassis cluster statistics, control-link heartbeat, fabric-link probes, cluster health verification.
Question # 14
Using Junos Space Security Director, you want to configure a unique firewall policy for a specific SRX Series device.
Which firewall policy rule would satisfy the requirement?
A.
all devices policy prerules
B.
group policy prerules
C.
device policy rules
D.
all devices policy postrules
Full Access
Answer:
C
Explanation:
The correct answer is C. device policy rules. In Junos Space Security Director, a firewall rule that must apply uniquely to one SRX Series device belongs in the device-specific policy layer, not in global or group-level policy. Juniper’s Security Director documentation states that a device can have a device-specific policy and can also be part of multiple group policies; the rule processing order places policies applied before device-specific policies first, then device-specific policies, then policies applied after device-specific policies. Juniper also explains that rules applied before device-specific policies take priority and cannot be overridden, while rules applied after device-specific policies can be overridden by adding a rule in the device-specific policy.
Option A is wrong because all-devices prerules are global mandatory rules applied before device-specific policy, not unique device exceptions. Option B is wrong because group policy prerules apply to a group of devices, not one specific SRX. Option D is wrong because all-devices postrules are still global policy rules, although they can be overridden. For a unique policy requirement on one SRX device, device policy rules are the precise Security Director construct. Reference topics: Security Director, firewall policies, device-specific policies, policy rule precedence, global/group/device rule hierarchy.
Question # 15
You are configuring a redundancy group using Ethernet interfaces.
In this scenario, which two actions must be performed? (Choose two.)
A.
Assign a physical interface from each node to the reth0 interface.
B.
Set the retry interval
C.
Define the number of reth interfaces in a cluster under the chassis cluster hierarchy.
D.
Configure the heartbeat interval.
Full Access
Answer:
A, C
Explanation:
The correct answers are A and C. In an SRX chassis cluster, redundant Ethernet interfaces are configured as reth interfaces. Juniper defines a reth interface as a pseudointerface that includes at least one physical interface from each node in the cluster. Therefore, assigning a physical interface from node0 and a physical interface from node1 to the same reth interface is mandatory for redundant Ethernet operation. Juniper also states that before configuring chassis cluster redundant Ethernet interfaces, you must set the number of redundant Ethernet interfaces.
Option C maps to the required reth-count configuration under the chassis cluster hierarchy. Without defining the number of reth interfaces, Junos does not know how many redundant Ethernet pseudointerfaces are available for the cluster configuration. Option B is wrong because setting a retry interval is not a required step for creating a reth interface or redundancy group. Option D is wrong because heartbeat behavior belongs to cluster control-link monitoring and chassis-cluster node health, not to the required configuration steps for Ethernet reth membership. The required design steps are: define reth capacity, create/configure the reth interface, assign child physical links from both nodes, and associate the reth with the proper redundancy group. Reference topics: HA Clustering, redundant Ethernet interfaces, reth-count, reth child interfaces, redundancy groups.
Question # 16
Which two statements are correct about client-protection Secure Socket Layer (SSL) proxy configurations? (Choose two.)
A.
Server certificate is required.
B.
Root certificate authority (CA) configuration is required.
C.
Root certificate authority (CA) configuration is not required.
D.
Server certificate is not required.
Full Access
Answer:
B, D
Explanation:
The correct answers are B and D. In Junos SSL proxy terminology, client protection maps to SSL forward proxy. In a forward-proxy deployment, the SRX sits between internal clients and external SSL/TLS servers. The firewall intercepts the server certificate, generates a substitute certificate, signs it with the configured root CA, decrypts the SSL session for inspection, and then re-encrypts traffic toward the destination server. Juniper’s SSL proxy configuration table shows that a forward-proxy profile uses root-ca configured = Yes and server-certificate configured = No. It also states that configuring neither certificate type fails commit validation, while configuring both root-ca and server-certificate in the same profile is unsupported.
Option A is wrong because a server certificate is required for reverse proxy/server protection, not for client-protection forward proxy. Option C is wrong because without a trusted root CA, client browsers would not trust the certificates generated by the SRX during interception. Juniper separately notes that the root CA certificate is required for client browsers to trust certificates signed by the firewall. Reference topics: SSL Proxy, client protection, SSL forward proxy, root CA, server protection, SSL reverse proxy.
Question # 17
Which two statements are correct about a chassis cluster? (Choose two.)
A.
If the cluster ID is set to 0, the HA configuration is ignored.
B.
You must reboot the device anytime you change the node ID configuration.
C.
If the node ID is set to 0, the HA configuration is ignored.
D.
You must have multiple Layer 2 domains if you require more than 255 node IDs.
Full Access
Answer:
A, B
Explanation:
The correct answers are A and B. In an SRX chassis cluster, the cluster ID identifies the chassis cluster, and valid operational cluster IDs are nonzero values. Juniper’s chassis cluster command documentation states that the system uses the chassis cluster ID and node ID to apply the correct node-specific configuration, and the command writes the chassis cluster ID and node ID to EPROM. When the cluster ID is set to 0, clustering is disabled; therefore, the HA cluster configuration is effectively ignored because the device is no longer operating as a chassis-cluster member.
Option B is also correct because Juniper states that chassis cluster ID and node ID changes take effect only after the system is rebooted. That is why the operational command format includes the reboot behavior when setting cluster-id and node. Option C is wrong because node ID 0 is valid; it identifies node0 in the two-node cluster. Option D is wrong because SRX chassis clusters use node IDs 0 and 1 only; the 1–255 range applies to cluster IDs, not node IDs. Reference topics: HA Clustering, cluster ID, node ID, EPROM, chassis cluster enablement, node-specific configuration.
Question # 18
Which three algorithms are used to encrypt IP packets? (Choose three.)
A.
Data Encryption Standard (DES)
B.
Secure Hash Algorithm (SHA) - 1
C.
Message Digest 5 (MD5)
D.
Triple Data Encryption Standard (3DES)
E.
Advanced Encryption Standard (AES)
Full Access
Answer:
A, D, E
Explanation:
The correct answers are A, D, and E. In IPsec VPN terminology, DES, 3DES, and AES are encryption algorithms used to provide confidentiality for protected IP traffic. Juniper’s IPsec material identifies AES, DES, and Triple DES/3DES as IPsec encryption standards, while separating them from authentication hash algorithms such as MD5, SHA-1, and SHA-2. This distinction matters heavily in JNCIS-SEC because IPsec proposals contain different cryptographic functions: encryption protects packet confidentiality, while authentication/hash algorithms validate integrity and origin.
Option B, SHA-1, is incorrect because SHA-1 is a hashing/authentication algorithm, not an encryption algorithm. It produces a message digest used for integrity checking and authentication, commonly as an HMAC variant. Option C, MD5, is also incorrect for the same reason: MD5 is a message-digest algorithm used for authentication/integrity, not for encrypting payload data. AES is the modern preferred encryption family because it is cryptographically stronger than DES and 3DES at comparable key strengths, while DES and 3DES remain historically recognized IPsec encryption algorithms. Reference topics: IPsec VPN, IPsec proposals, encryption algorithms, authentication algorithms, DES, 3DES, AES, SHA, and MD5.
Question # 19
Which two functions does Juniper ATP Cloud perform to reduce delays in the inspection of files? (Choose two.)
A.
Juniper ATP Cloud allows the creation of allowlists.
B.
Juniper ATP Cloud uses a single antivirus software package to analyze files.
C.
Juniper ATP Cloud allows end users to bypass the inspection of files.
D.
Juniper ATP Cloud performs a cache lookup on files.
Full Access
Answer:
A, D
Explanation:
The correct answers are A and D. Juniper ATP Cloud reduces inspection delay in two practical ways: trusted allowlists and cache lookup. An allowlist contains known trusted IP addresses, hashes, email addresses, and URLs; Juniper states that content downloaded from locations on the allowlist does not have to be inspected for malware. That eliminates unnecessary cloud-analysis cycles for known trusted sources or objects.
Option D is also correct because ATP Cloud performs a real-time cache lookup before deeper analysis. Juniper explains that when a file is uploaded, ATP Cloud first checks whether the file has been analyzed before; if it has, the stored verdict is returned to the SRX Series Firewall and there is no need to re-analyze the file. This directly reduces inspection delay and enables faster enforcement. Option B is wrong because ATP Cloud does not rely on a single antivirus engine; it uses a pipeline that can include cache lookup, antivirus, static analysis, dynamic analysis, and machine learning. Option C is wrong because inspection bypass is not delegated to end users. Reference topics: ATP Cloud, allowlists, file inspection workflow, cache lookup, malware analysis pipeline.
Question # 20
You are asked to ensure that traffic that matches an IDP policy is not impacted until administrators have a chance to evaluate it.
In this scenario, which IP action should be configured for the policy?
A.
ip-block
B.
ip-notify
C.
ip-connection-rate-limit
D.
ip-close
Full Access
Answer:
B
Explanation:
The correct answer is B. ip-notify. When administrators want visibility without enforcement impact, ip-notify is the correct IP action. Juniper Security Director documentation defines IP Notify as an IP action that does not take any action against future traffic but logs the event. That is exactly the requirement in the question: traffic matching the IDP condition must not be blocked, closed, or rate-limited until administrators have reviewed the events and decided whether enforcement is appropriate.
Option A, ip-block, is wrong because it blocks future packets matching the IP action rule. That would immediately impact traffic. Option C, ip-connection-rate-limit, is wrong because it limits the connection rate and therefore changes traffic behavior before administrators complete evaluation. Option D, ip-close, is also wrong because it closes matching future sessions by sending reset packets to the client and server, which is disruptive. In a safe evaluation or tuning phase, the proper approach is to log and observe first, then move to stronger actions such as block, close, or rate-limit only after the detected condition has been validated. Reference topics: IDP IP actions, ip-notify, event logging, non-disruptive evaluation mode, IDP policy tuning.