

Question # 4
A customer must retain all privileged-access records for 7 years. The environment has approximately 2000 users who create nearly 100 GB of session recordings each day.
How should CyberArk PAS be designed to meet this requirement for PSM recordings?
A.
Set a low PSM Recording Retention period and use Secure Replicate to offload recordings for archival storage.
B.
Connect Vault servers to SAN storage and increase disk size whenever free disk space monitoring sends an alert.
C.
Connect external storage to PSM servers to more evenly distribute the storage requirements.
D.
Set Audit Retention Master Policy and PSMRecording Safe object retention to 2555 days (365 days * 7 years).
Full Access
Answer:
A
Explanation:
CyberArk Privileged Session Manager records administrative sessions and stores completed recordings in designated Recording Safes within the Digital Vault.
At approximately 100 GB per day, retaining seven years of recordings requires substantial storage capacity.
The estimated volume is:
100 GB × 365 × 7 = 255,500 GB
This represents approximately 255.5 TB before accounting for filesystem overhead, additional metadata, growth, and redundancy.
Retaining this entire volume within the operational Digital Vault would introduce considerable storage, backup, and recovery requirements.
The more appropriate approach is to establish a shorter operational recording-retention period and use CyberArk replication or supported archival processes to transfer recordings into secure long-term storage.
Secure Replicate can support the transfer of Vault data into an external backup environment, reducing dependence on continuously expanding primary Vault storage.
However, the archival solution must independently enforce the required seven-year retention period, integrity protection, recoverability, and audit requirements. A backup copy alone does not automatically establish regulatory compliance.
Option B relies on reactive storage expansion. Option C incorrectly treats PSM servers as the permanent recording archive. Option D does not address practical capacity management and incorrectly combines different retention mechanisms.
[Reference:CyberArk Digital Vault — Secure Replicate, Vault Backup and Recovery, PSM Recording Safes, Recording Retention and Long-Term Archival Design.]
Question # 5
A customer needs to implement CyberArk with the lowest possible recovery time objective for a Vault server failure in both the primary and secondary datacenters.
Which architecture is most suitable for this?
A.
Deploy a multi cloud, multi region Architecture with 4 vaults. 2 vaults per public cloud across different regions.
B.
Deploy both Primary and DR vault clusters in primary and secondary datacenters.
C.
Deploy Distributed vaults. 1 Primary vault and 1 satellite vault in the primary datacenter and 2 satellite vaults in the secondary datacenter.
D.
Deploy Primary and DR standalone vaults in a single public cloud environment within the same region across different availability zones.
Full Access
Answer:
B
Explanation:
Recovery Time Objective (RTO) defines the maximum acceptable duration of service interruption following a failure.
For a CyberArk deployment requiring minimal recovery time from individual Vault server failures in both datacenters, high-availability Vault clusters provide an appropriate architecture.
A CyberArk Vault cluster consists of two Vault nodes configured to operate as a single logical Vault service. The Cluster Vault Manager coordinates availability and failover between the active and passive nodes.
If the active node fails, the surviving cluster node can assume operations through the supported failover mechanism, minimizing interruption without requiring a full datacenter disaster recovery procedure.
Deploying a Primary Vault cluster in the primary datacenter and a DR Vault cluster in the secondary datacenter combines local high availability with geographic disaster recovery.
This design protects against individual server failures at either location while retaining a standby recovery environment if the primary datacenter becomes unavailable.
The distinction is important: automatic cluster-node failover does not necessarily mean instantaneous disaster recovery promotion between geographically separated Vault clusters.
Option B directly addresses the customer's requirement for local server-failure resilience at both locations.
[Reference:CyberArk PAM Self-Hosted — Vault Cluster Architecture, Cluster Vault Manager, High Availability, Disaster Recovery and RTO Planning.]
Question # 6
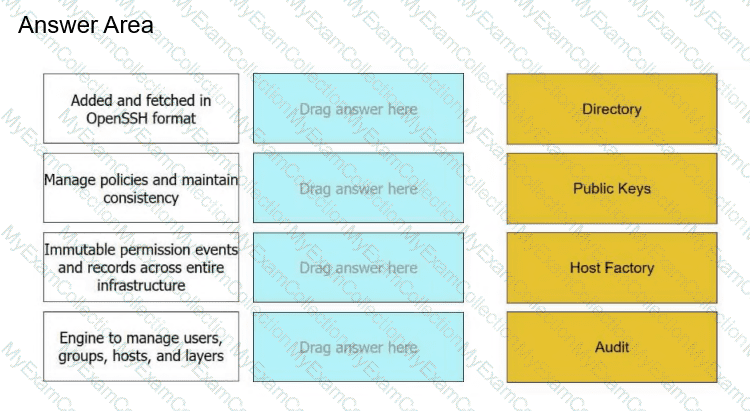
Match the Conjur services and options:
Full Access
Answer:
Answer: 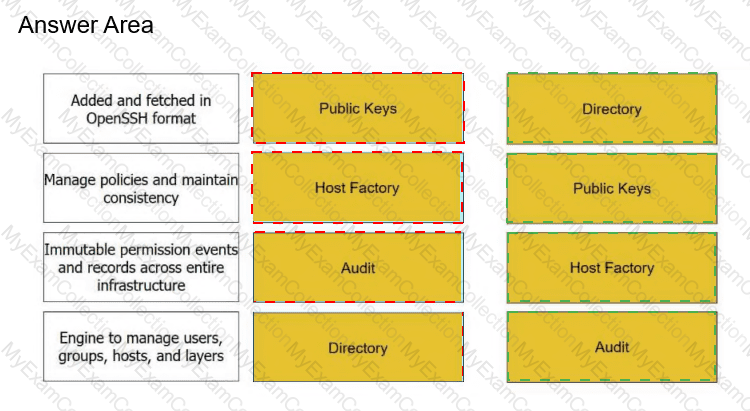
Explanation:
Original description / order
Correct match
Added and fetched in OpenSSH format
Public Keys
Manage policies and maintain consistency
Host Factory — intended by elimination
Immutable permission events and records across entire infrastructure
Audit
Engine to manage users, groups, hosts, and layers
Directory
CyberArk Conjur includes services for managing machine identities, authorization policies, cryptographic public keys, and security audit information.
The Public Keys service manages public keys associated with Conjur identities. These keys can support SSH-based authentication and are commonly represented in OpenSSH format.
The Directory service organizes identity resources, including users, groups, hosts, and layers. These resources provide the foundation for policy-based authorization and controlled secrets retrieval.
The Audit service records security-relevant activities, including authentication and authorization events. Such records support operational investigation, accountability, and security monitoring. Audit durability depends on the deployment and protected log-storage configuration.
Host Factory enables automated creation and enrollment of host identities. It uses policy-controlled, time-limited enrollment tokens to allow newly provisioned workloads to become members of authorized Conjur layers without granting broad administrative permissions.
The second description in the exhibit is technically imprecise. Host Factory is not the general mechanism for maintaining Conjur policies. Policy files and Conjur's policy-management interfaces govern authorization definitions.
Nevertheless, Host Factory is the intended remaining match among the four supplied choices.
Technical warning / qualification: The second description should be rewritten to Automates the creation and enrollment of host identities using policy-controlled tokens.
[Reference:CyberArk Conjur — Public Keys API, Host Factory, Policy Management, Identity Resources and Audit Services.]
Question # 7
Your customer has used CyberArk PAS for more than five years and has successfully onboarded over 35 local built-in administrator accounts.
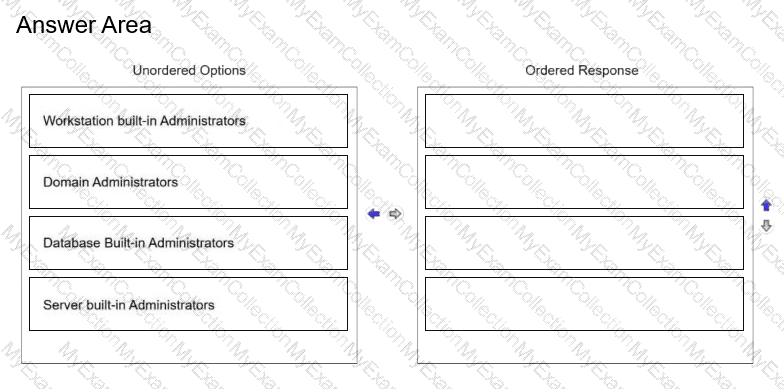
A new CISO has assumed responsibility and wants to rapidly broaden privileged access management across the organization. Based on the use cases provided, prioritize them according to CyberArk's Blueprint methodology, from most critical first to least critical last.
Drag & Drop
Original drag-and-drop exhibit (answer area unselected)
Full Access
Answer:
Answer: 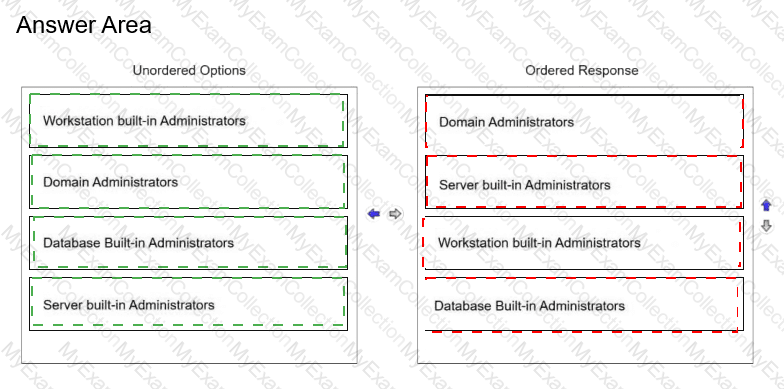
Explanation:
Original description / order
Correct match
1
Domain Administrators
2
Server built-in Administrators
3
Workstation built-in Administrators
4
Database Built-in Administrators
The CyberArk Blueprint prioritizes privileged identities according to their potential impact on enterprise security, particularly their ability to facilitate credential theft, lateral movement, and privilege escalation.
Domain Administrator accounts receive the highest priority because their compromise can provide extensive control over Active Directory, including authentication infrastructure, domain controllers, and other domain-managed resources. These identities represent a substantial enterprise-wide risk.
Server built-in Administrator accounts follow because they provide powerful local privileges on infrastructure that frequently hosts sensitive applications, databases, and business services. Securing these accounts reduces opportunities for attackers to establish persistence or move between critical servers.
Workstation built-in Administrator accounts are subsequently prioritized because shared or poorly managed endpoint credentials can facilitate credential reuse and lateral movement across large workstation populations.
Database built-in Administrator accounts remain important because they can provide extensive control over business-critical information. Within the Blueprint sequence represented by this question, these identities are addressed in a later stage of enterprise security expansion.
This ordering reflects CyberArk's staged implementation model rather than an assertion that every database credential is inherently less sensitive than every workstation credential. Actual onboarding priorities should additionally consider privilege scope, asset criticality, and business impact.
[Reference:CyberArk Blueprint — Rapid Risk Reduction, Domain Administrator Protection, Server Local Administrator Accounts, Workstation Administrator Accounts, Enterprise Security Controls.]
Question # 8
The Active Directory manager asks you to temporarily enable Object Level Access Control (OLAC) on a Safe they own so they can control which users may use a particular Domain Admin account.
What OLAC limitation should you explain to them?
A.
OLAC does not enable granular control of which users can use a specific object.
B.
Once enabled, object level access control cannot be disabled.
C.
With object level access control enabled, PSM operations on the managed accounts are not supported.
D.
New accounts cannot be added to the safe, once OLAC is enabled.
Full Access
Answer:
B
Explanation:
Object Level Access Control (OLAC) provides granular authorization over individual objects stored within CyberArk Safes.
In a standard Safe configuration, users receive access according to their Safe membership and assigned authorizations. OLAC extends this authorization model by allowing permissions to be managed at the individual-object level.
This is particularly useful when a Safe contains sensitive privileged accounts requiring different access restrictions.
For example, an Active Directory administrator may need to restrict access to a Domain Administrator credential without applying identical restrictions to every account in the same Safe.
However, OLAC introduces an important configuration limitation: once enabled for a Safe, it cannot subsequently be disabled through the supported configuration mechanism .
Therefore, OLAC is unsuitable as a temporary access-control feature.
Administrators should evaluate the long-term authorization model, application dependencies, Safe ownership, and ongoing administration requirements before enabling it.
Option A contradicts OLAC's purpose, which is to provide object-specific authorization. Option C incorrectly suggests that PSM session management becomes universally unavailable. Option D incorrectly states that new objects cannot be stored in the Safe.
The correct architectural recommendation is to design the required granular permissions before permanently enabling OLAC.
[Reference:CyberArk PAM Self-Hosted — Safes, Object Level Access Control, Object Permissions and Safe Configuration Restrictions.]
Question # 9
What are the three Guiding Principles of the CyberArk Blueprint?
A.
Credential Theft, Lateral and Vertical Movement, Privilege Escalation and Abuse.
B.
Identity Security, Credential Theft, Lateral and Vertical Movement.
C.
Attack and Defend capability, Credential Theft, Least Privilege.
D.
Quick return on investment, Password Management, Credential Theft.
Full Access
Answer:
A
Explanation:
The CyberArk Blueprint is based on three security principles designed to interrupt the identity attack chain used by malicious actors to compromise enterprise systems.
The first principle is preventing credential theft . Attackers frequently obtain passwords, authentication tokens, SSH keys, and other privileged credentials through phishing, malware, exposed configuration files, or credential repositories. CyberArk mitigates these risks through secure credential storage, controlled retrieval, password rotation, and session isolation.
The second principle is stopping lateral and vertical movement . After obtaining initial access, attackers attempt to move between systems or cross security boundaries to reach more valuable resources. Unique privileged credentials, segmentation, and controlled privileged sessions reduce opportunities for such movement.
The third principle is limiting privilege escalation and abuse . Attackers may attempt to elevate compromised identities into administrative roles or misuse existing privileges. Least-privilege controls, session monitoring, application control, and just-in-time access help restrict these activities.
Together, these principles support the Blueprint's phased implementation methodology. Organizations can prioritize security controls according to their ability to reduce identity-related attack risk.
Option A correctly identifies all three areas, although CyberArk commonly presents them as preventative actions rather than simply naming the attack techniques.
[Reference:CyberArk Blueprint — Three Guiding Principles: Prevent Credential Theft, Stop Lateral and Vertical Movement, Limit Privilege Escalation and Abuse.]
Question # 10
The ‘LogRetention’ parameter in the DBParm.ini file specifies how long log records are retained.
When are the expired logs cleared?
A.
It needs to be cleared manually.
B.
It will not be cleared automatically. It will show warning.
C.
Whenever the Server is stopped.
D.
Whenever the Server is started.
Full Access
Answer:
D
Explanation:
The CyberArk Digital Vault uses the DBParm.ini configuration file to define operational parameters affecting the Vault Server, including logging, communication, and service behavior.
The LogRetention parameter specifies how long relevant Vault log records are retained before they become eligible for removal.
According to the behavior described by this legacy parameter, expired log records are cleared during the Vault Server startup process. At startup, the server can evaluate retention settings and perform the corresponding cleanup operations.
This means the retention period defines the eligibility threshold for removing records, while the server lifecycle determines when the cleanup operation is performed.
Stopping the service does not independently execute the startup cleanup operation. Additionally, an administrator is not ordinarily required to perform individual manual deletions of expired records governed by this mechanism.
It is important to distinguish operational log retention from other CyberArk retention controls. Vault audit records, external SIEM archives, privileged session recordings, and disaster recovery replicas may have separate retention requirements.
Administrators should therefore validate the relevant logging configuration and applicable audit obligations before modifying retention settings.
[Reference:CyberArk Digital Vault —DBParm.iniParameter Reference,LogRetention, Vault Server Startup and Logging Configuration.]
Question # 11
You are installing the Digital Vault on AWS.
When does hardening occur?
A.
After the initial installation is completed.
B.
It is not recommended to harden the Vault in AWS.
C.
During the installation procedure.
D.
Before the installation starts by running script.
Full Access
Answer:
A
Explanation:
CyberArk Digital Vault hardening establishes the security controls required to protect the Vault operating system and minimize exposure to unauthorized access.
These controls include restrictive network communication, operating-system configuration, service hardening, and the removal or disabling of unnecessary system functionality.
In the AWS deployment procedure referenced by this question, the standard Vault installation and hardening sequence differs from the conventional installation process.
During the initial Vault installation, the administrator selects the option to skip automatic machine hardening.
After completing the initial installation, the applicable AWS-specific hardening procedure is performed.
This sequence accounts for cloud infrastructure requirements, including instance configuration, virtual networking, supported access mechanisms, and cloud-specific operating-system dependencies.
Skipping hardening during the initial installation does not mean that hardening is optional.
The final deployed Vault must still satisfy CyberArk's supported security requirements before being placed into production.
Option B is incorrect because a cloud-hosted Vault requires appropriate hardening. Option C describes the conventional installation sequence rather than the specific AWS procedure presented. Option D does not reflect the documented sequence for this deployment method.
Technical warning / qualification: This answer applies to the AWS installation procedure represented by the Guardian source. CyberArk-provided cloud images and automated deployment scripts may implement hardening differently in newer releases.
[Reference:CyberArk PAM Self-Hosted — Digital Vault Installation on AWS, Machine Hardening, AWS-Specific Installation Procedures and Vault Security Standard.]
Question # 12
What is required for a Privilege Cloud Connector Server?
A.
Public Facing IP
B.
IIS Server 10
C.
IPv6 Address
D.
Joined to the domain
Full Access
Answer:
D
Explanation:
In standard CyberArk Privilege Cloud deployments, the Connector server (which hosts the CPM and PSM components) is typically joined to the corporate Active Directory domain . This allows the connector to leverage domain Group Policy Objects (GPOs) for server hardening and properly manage Windows domain accounts and target systems. (Note: While an "out-of-domain" deployment option exists for specific isolated environments, domain-joined is the standard requirement tested on the CyberArk Guardian
Question # 13
Select the two controls that can be configured at the Master Policy level.
Choose two
A.
Require dual control password access approval.
B.
Enforce one-time password access.
C.
Automatically reconcile password when changing.
D.
PSM recording retention period.
E.
Set number of password versions to be retained.
Full Access
Answer:
A, B
Explanation:
CyberArk Master Policy provides centralized control over key privileged-access and password-management requirements across managed platforms.
The Require dual control password access approval setting establishes an approval workflow for privileged credential retrieval.
When this rule is enabled, users must obtain authorization from designated approvers before accessing protected account credentials, unless a supported exception applies.
This is particularly useful for sensitive administrative accounts requiring separation of duties and additional access oversight.
The Enforce one-time password access rule controls the reuse of privileged credentials. When enabled, the password-management process changes the managed password after account usage, subject to the configured validity and workflow requirements.
This reduces the period during which a retrieved credential remains usable.
Automatic reconciliation is implemented through password-management platform settings and reconciliation-account configuration. It is not the specific Master Policy rule represented by option C.
PSM recording retention is configured through the relevant recording-retention and Safe-management mechanisms rather than being one of the two controls requested.
Similarly, password-version retention is governed by applicable Vault or Safe configuration rather than the Master Policy rules listed.
Options A and B therefore correctly identify the two Master Policy controls.
[Reference:CyberArk PAM Self-Hosted — Master Policy, Dual Control, One-Time Password Access, Automatic Password Management and Recording Retention.]
Question # 14
A customer has asked you to onboard more than 1,000 Local Admin accounts. All of the accounts are used by the same team and are in a control zone.
Which CyberArk feature provides an automated way to accomplish this task?
A.
Password Upload Utility
B.
Auto-Detection
C.
Auto-Reconcile
D.
Remote Control Agent
Full Access
Answer:
A
Explanation:
CyberArk Password Upload Utility (PUU) supports bulk onboarding of privileged accounts into the Digital Vault, reducing the administrative effort associated with manually creating large numbers of managed accounts.
In this scenario, the customer needs to onboard more than 1,000 local administrative accounts belonging to the same operational team and security control zone.
The Password Upload Utility allows administrators to prepare structured account information, typically using a delimited input file containing target addresses, usernames, passwords, Safe assignments, and relevant platform information.
The utility processes the supplied information and creates the corresponding account objects within CyberArk, subject to the configured permissions and supported platform requirements.
Before executing the bulk import, administrators should confirm the Safe design, account ownership, platform assignments, and password-management configurations.
After onboarding, CPM can manage the accounts according to the assigned platform policies, including automated password verification, rotation, and reconciliation.
Auto-Detection concerns account discovery rather than the direct bulk import of a prepared account inventory. Auto-Reconcile is associated with credential recovery operations, while the Remote Control Agent supports Vault administration and monitoring.
Modern CyberArk environments can also use REST APIs for automated account onboarding, but the Password Upload Utility is the correct option among those provided.
[Reference:CyberArk PAM Self-Hosted — Password Upload Utility, Bulk Account Onboarding, Safe Assignment and Automated Password Management.]
Question # 15
A financial institution uses CyberArk Privileged Session Manager (PSM) to monitor privileged access to production servers.
The security team requires authorized auditors to terminate suspicious privileged sessions immediately when potentially malicious administrative activity is detected.
An auditor can view active sessions in PVWA but cannot terminate them. The administrator confirms that session monitoring is enabled and the PSM infrastructure is functioning correctly.
What configuration should be implemented to allow the auditor to terminate active privileged sessions?
A.
Add the auditor to the Vault Administrators group and grant full administrative access to all Recording Safes.
B.
Enable the Require Dual Control Password Access Approval rule in the Master Policy and assign the auditor as an approver.
C.
Add the auditor to the PSMLiveSessionTerminators group and ensure that this group has the required membership in the Safes containing the managed accounts.
D.
Assign the auditor the Retrieve Accounts permission on the relevant Safes and enable automatic password reconciliation.
Full Access
Answer:
C
Explanation:
CyberArk Privileged Session Manager provides real-time monitoring and control of privileged sessions, enabling security teams to investigate potentially dangerous activity and intervene when necessary.
Session monitoring and session termination are distinct authorization capabilities. Being able to view an active privileged session does not automatically grant permission to terminate it.
In CyberArk PAM Self-Hosted, the PSMLiveSessionTerminators group provides the authorization framework for terminating active PSM sessions.
To enable this capability, the administrator must add the designated auditor to the PSMLiveSessionTerminators group.
Additionally, this group must have the necessary membership in the Safes containing the account objects associated with the sessions that the auditor is authorized to terminate.
Both requirements are important because session termination authorization must respect the organization's privileged-account access boundaries.
Where PSM uses RDP over SSL, additional connection-component configuration may be required for the monitoring and termination functions to operate correctly.
Granting broad Vault Administrator privileges would violate least-privilege principles. Dual Control regulates password-access approvals rather than active-session termination.
Similarly, credential retrieval and password reconciliation permissions do not independently authorize session termination.
This configuration enables controlled security intervention without unnecessarily exposing privileged credentials or granting unrestricted Vault administration.
[Reference: CyberArk Knowledge Base — How to Configure Live Session Termination for Audit Users; PSM Live Session Monitoring; PSMLiveSessionTerminators Group and Safe Authorizations., community.cyberark.com]
Question # 16
ClientABC is moving into the DevOps space. They currently use CCP and are considering Conjur. They have noticed there is considerable overlap.
How would you explain the difference between the two?
Choose two
A.
Conjur is well suited for the velocity of the CI/CD pipeline because it includes native authentication such as API keys, 1AM, and OAuth. You store the secret at the project folder level.
B.
CCP is a good choice if you're using client certificate authentication. With CCP you need to authenticate and pass an application ID and your query for your secret.
C.
Conjur is best suited for static secrets. You only need to pass an API key to make the call. This is suited well for the velocity of the CI/CD pipeline because it integrates seamlessly with containers.
D.
CCP is best used for ad-hoc scripts. It's a great choice because you're able to use enhanced authentication mechanisms such as 'Path' and 'Hash'.
E.
When trying to decide between the two, you should generally choose CCP, as Conjur cannot be integrated with the same vault that is used for CyberArk PAM.
Full Access
Answer:
A, B
Explanation:
CyberArk Central Credential Provider (CCP) and Conjur both provide secure credential retrieval, but they address different application architectures and operational requirements.
CCP is an agentless credential retrieval service accessed through HTTPS. Applications authenticate using supported methods, including client certificates, and submit requests containing an authorized Application ID and criteria identifying the requested account.
This makes CCP suitable for traditional applications, automation scripts, and systems that can integrate with an HTTPS-based credential retrieval interface.
Conjur is designed primarily for cloud-native applications, containers, orchestration platforms, and CI/CD workflows.
It supports workload-oriented authentication mechanisms, including API-key authentication and integrations with cloud identity services and signed identity tokens.
Conjur also supports policy-based secrets management, allowing development teams to define application identities and authorized access through structured policies.
Option C incorrectly suggests that Conjur is limited to static secrets and that all workloads authenticate exclusively through API keys.
Option D incorrectly attributes local executable path and hash authentication mechanisms to CCP as its defining capability. Option E is incorrect because supported Conjur architectures can integrate with CyberArk PAM through synchronization mechanisms.
[Reference:CyberArk Secrets Manager (Conjur) — Workload Authentication, Policy-as-Code, CI/CD Integration, Central Credential Provider and Vault Synchronizer.]
Question # 17
The following message appears in a log: PSMSV1230E: Vault files download completed with errors. Some of the files may be missing.
On which system would you most likely see this message?
A.
PSM for SSH
B.
CPM
C.
PSM
D.
Vault
Full Access
Answer:
C
Explanation:
CyberArk components use distinct message prefixes to identify the originating service or subsystem. These identifiers help administrators determine where a problem occurred and which diagnostic records should be examined.
The message PSMSV1230E belongs to the Privileged Session Manager service message family.
Privileged Session Manager (PSM) establishes and controls privileged sessions, isolates credentials from users, and supports monitoring and recording of administrative activity.
During initialization and normal operations, PSM communicates with the Digital Vault to obtain configuration data and other files required by its services.
The error indicates that a Vault file download operation completed unsuccessfully and that some expected files may not have been retrieved.
Potential causes include Vault connectivity problems, insufficient Safe permissions, unavailable objects, authentication failures, or incomplete component configuration.
Administrators should investigate the corresponding PSM service logs and correlate the event with Vault connectivity and authentication records.
PSM for SSH uses a different service architecture and message families, while CPM primarily produces password-management and credential-processing diagnostics.
Although the underlying communication involves the Digital Vault, the PSMSV prefix identifies the PSM component as the expected logging source.
[Reference:CyberArk Privileged Session Manager — PSM Service Messages, Vault Communication, Component Initialization and Troubleshooting.]
Question # 18
Put the events in the correct order for the PSM for SSH MFA Caching authentication workflow, available beginning with v12.1.
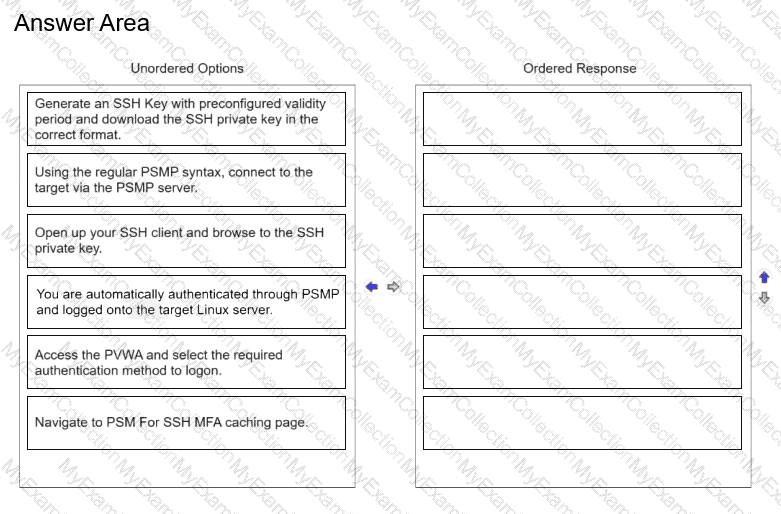
Full Access
Answer:
Answer: 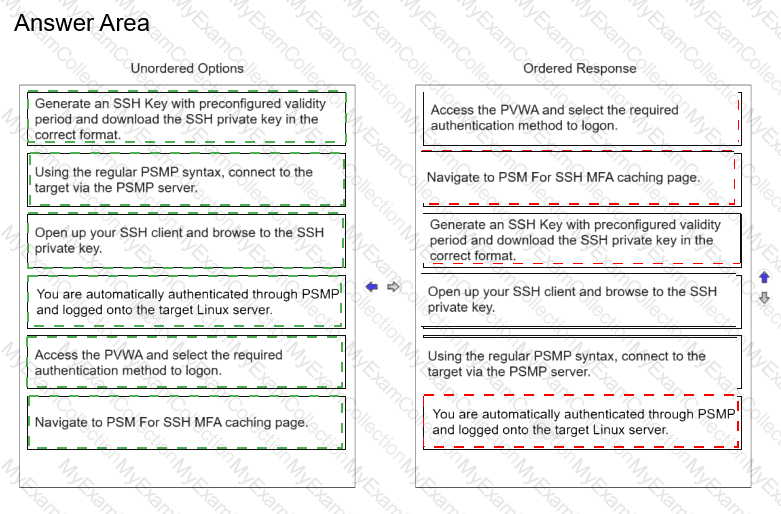
Explanation:
See correct matching / sequence below.
Original description / order
Correct match
1
Access the PVWA and select the required authentication method to logon.
2
Navigate to PSM for SSH MFA caching page.
3
Generate an SSH key with preconfigured validity period download the SSH private key in the correct format.
4
Open up your SSH client and browse to the SSH private key.
5
Using the regular PSMP syntax, connect to the target via the PSMP server.
6
You are automatically authenticated through PSMP and logged onto the target Linux server.
CyberArk PSM for SSH MFA Caching enables administrators to authenticate through supported PVWA authentication mechanisms and subsequently establish SSH sessions without repeating the complete multifactor authentication process for every connection.
The workflow begins when the user authenticates to PVWA using the required authentication method.
After successful authentication, the user navigates to the PSM for SSH MFA Caching interface and generates a temporary SSH authentication key.
The key is issued with a configured validity period and downloaded in a format supported by the user's SSH client.
The administrator then configures the SSH client to use the generated private key.
Using the standard PSM for SSH connection syntax, the user establishes an SSH connection through the PSMP server.
PSM for SSH validates the presented authentication material and applicable cached authentication context before initiating the authorized target connection.
This architecture allows organizations to retain multifactor authentication requirements while improving usability for administrators who establish frequent SSH sessions.
The private key must remain protected because it represents temporary authentication material. Expiration, revocation, and endpoint security controls remain essential.
[Reference:CyberArk PSM for SSH — MFA Caching, SSH Key Authentication, PVWA Authentication Integration and PSMP Connection Syntax.]

