Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: my75ex

Home > Microsoft > GitHub Administrator > GH-200

GH-200 GitHub Actions Exam Question and Answers

Question # 4

Which files are required for a Docker container action in addition to the source code? (Choose two.)

A.

Dockerfile

B.

Actionfile

C.

metadata.yml

D.

action.yml

Full Access
Question # 5

What is a role of GitHub Marketplace when using GitHub Actions?

A.

GitHub Marketplace restricts the use of third-party actions to only public repositories.

B.

GitHub Marketplace serves only as a billing dashboard for tracking paid actions.

C.

GitHub Marketplace provides a centralized location to discover, share, and publish reusable GitHub Actions workflows created by the community or vendors.

D.

GitHub Marketplace allows a user to deploy GitHub Actions workflows to any repository automatically without requiring permissions.

Full Access
Question # 6

What are the two most significant advantages of adding documentation while distributing custom actions? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.

A.

It creates a readme.md for the consuming workflow.

B.

It shares the description of the action to the users.

C.

It provides an example of the action.

D.

It generates auto completion when using the action in a workflow.

Full Access
Question # 7

Which default GitHub environment variable indicates the name of the person or app that initiated a workflow?

A.

ENV_ACTOR

B.

GITHUB_WORKFLOW_ACTOR

C.

GITHUB_ACTOR

D.

GITHUB_USER

Full Access
Question # 8

As a DevOps engineer, you need to execute a deployment to different environments like development and testing based on the labels added to a pull request. The deployment should use the releases branch and trigger only when there is a change in the files under apps folder. Which code block should be used to define the deployment workflow trigger?

A.

on:pull_request_label:branches:- ' releases ' paths:- ' apps/** '

B.

on:pull_request_review:types: [labeled]branches:- ' releases ' paths:- ' apps/** '

C.

on:pull_request:types: [labeled]branches:- ' releases/** ' paths:- ' apps '

D.

on:pull_request:types: [labeled]branches:- ' releases ' paths:- ' apps/** '

Full Access
Question # 9

Which of the following is the proper syntax to specify a custom environment variable named MY_VARIABLE with the value my-value?

A.

env:

MY_VARIABLE = my-value

B.

environment:

MY_VARIABLE = my-value

C.

env:

MY_VARIABLE: my-value

D.

var:

MY_VARIABLE: my-value

E.

var:

MY_VARIABLE = my-value

F.

environment:

MY_VARIABLE: my-value

Full Access
Question # 10

As a DevOps engineer, you are developing a composite action. You have a step that needs to be executed against a subdirectory. Which code snippet should you use within the composite action to specify the directory?

A.

runs:using: " composite " steps:- run: $GITHUB_ACTION_PATH/script.shdirectory: ${{ inputs.dir }}shell: bash

B.

runs:using: " composite " directory: ${{ inputs.dir }}steps:- run: $GITHUB_ACTION_PATH/script.shshell: bash

C.

runs:using: " composite " working-directory: ${{ inputs.dir }}steps:- run: $GITHUB_ACTION_PATH/script.shshell: bash

D.

runs:using: " composite " steps:- run: $GITHUB_ACTION_PATH/script.shworking-directory: ${{ inputs.dir }}shell: bash

Full Access
Question # 11

What are the two types of environment protection rules you can configure? (Choose two.)

A.

required reviewers

B.

branch protections

C.

wait timer

D.

artifact storage

Full Access
Question # 12

As a DevOps engineer, you are developing a composite action. You have a step that needs to be executed against a subdirectory. Which code snippet should you use within the composite action to specify the directory?

A.

runs:

using: " composite "

steps:

- run: $GITHUB_ACTION_PATH/script.sh

directory: ${{ inputs.dir }}

shell: bash

B.

runs:

using: " composite "

steps:

- run: $GITHUB_ACTION_PATH/script.sh

working-directory: ${{ inputs.dir }}

shell: bash

Full Access
Question # 13

Custom environment variables can be defined at multiple levels within a workflow file, including which three levels?

(Each correct answer presents a complete solution. Choose three.)

A.

Stage level

B.

Default level

C.

Step level

D.

Runner level

E.

Top level

F.

Job level

Full Access
Question # 14

In which of the following scenarios should you use self-hosted runners? Each correct answer presents a complete solution.

NOTE: Each correct answer is worth one point.

A.

when the workflow jobs must be run on Windows 10

B.

when jobs must run for longer than 6 hours

C.

when you want to use macOS runners

D.

when GitHub Actions minutes must be used for the workflow runs

E.

when a workflow job needs to install software from the local network

Full Access
Question # 15

You need to create a reusable GitHub Actions workflow template named ci.yml. The solution must ensure that ci.yml appears on the New workflow interface of GitHub Actions. Where should you store ci.yml?

A.

.github/workflows

B.

.github/templates

C.

.github/workflow-templates

D.

the root directory of each repository

Full Access
Question # 16

Which workflow event is used to manually trigger a workflow run?

A.

create

B.

workflow_dispatch

C.

workflow_run

D.

status

Full Access
Question # 17

How should you print a debug message in your workflow?

A.

echo " Set variable MyVariable to true " > > $DEBUG_MESSAGE

B.

echo " ::debug::Set variable MyVariable to true "

C.

echo " ::add-mask::Set variable MyVariable to true "

D.

echo " debug_message=Set variable MyVariable to true " > > $GITHUB_OUTPUT

Full Access
Question # 18
A.

Scheduled workflows run on the:

B.

latest commit and branch on which the workflow was triggered,

C.

latest commit from the branch named schedule,

D.

latest commit from the branch named main,

E.

specified commit and branch from the workflow YAML file,

F.

latest commit on the default or base branch

Full Access
Question # 19

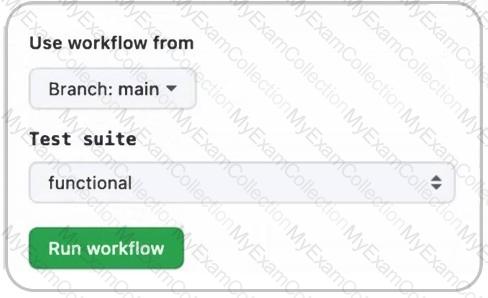
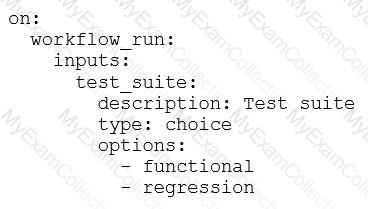
As a developer, you want to run a workflow from the Actions tab in GitHub. Which YAML snippet should you use to match the interface in this image?
A)
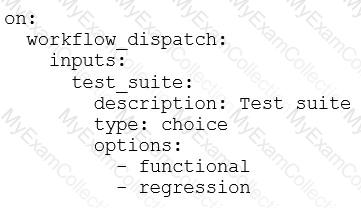
B)
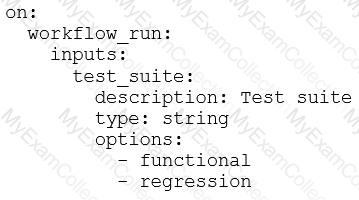
C)

D)
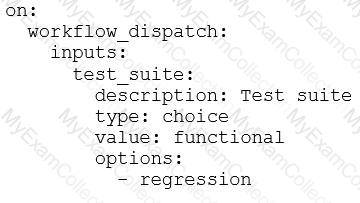
A.

Option A

B.

Option B

C.

Option C

D.

Option D

Full Access
Question # 20

As a developer, you need to create a custom action written in Python. Which action type should you choose?

As a developer, you need to create a custom action written in Python. Which action type should you choose?

A.

JavaScript action

B.

composite run step

C.

Python action

D.

Docker container action

Full Access
Question # 21

Which run: command will set a step ' s output?

A.

run: echo " MY_OUTPUT=foo " > > $GITHUB_OUTPUT

B.

run: export MY_OUTPUT=foo

C.

run: echo ${{ $GITHUB_OUTPUT=foo }}

D.

run: echo " ::set-env name=MY OUTPUT::foo "

Full Access
Question # 22

You need to create new workflows to deploy to an unfamiliar cloud provider. What is the fastest and safest way to begin?

A.

Create a custom action to wrap the cloud provider ' s CLI.

B.

Search GitHub Marketplace for verified actions published by the cloud provider.

C.

Use the actions/jenkins-plugin action to utilize an existing Jenkins plugin for the cloud provider.

D.

Search GitHub Marketplace for actions created by GitHub.

E.

Download the CLI for the cloud provider and review the associated documentation.

Full Access
Question # 23

Which native method should you use to pass files between jobs within the same GitHub Actions workflow?

A.

Use artifact storage.

B.

Use job outputs.

C.

Use the copy action with the cache parameter to cache the data.

D.

Use an external blob store

Full Access
Question # 24

Which default GitHub environment variable indicates the owner and repository name?

A.

REPOSITORY NAME

B.

GITHUB REPOSITORY

C.

ENV REPOSITORY

D.

GITHUB WORKFLOW REPO

Full Access
Question # 25

Disabling a workflow allows you to stop a workflow from being triggered without having to delete the file from the repo. In which scenarios would temporarily disabling a workflow be most useful? (Choose two.)

A.

A workflow sends requests to a service that is down.

B.

A workflow error produces too many, or wrong, requests, impacting external services negatively.

C.

A workflow is configured to run on self-hosted runners

D.

A workflow needs to be changed from running on a schedule to a manual trigger

E.

A runner needs to have diagnostic logging enabled.

Full Access
Question # 26

In the following workflow file, line 5 interprets lines 3 and 4 as Python. Which of the following is a valid option to complete line 5?

1 steps:

2 - run: |

3 import os

4 print(os.environ[ ' PATH ' ])

5

A.

with: python

B.

shell: bash

C.

working-directory: .github/python

D.

shell: python

Full Access
Question # 27

What menu options in a repository do you need to select in order to use a starter workflow that is provided by your organization?

A.

Actions > Load workflow

B.

Workflow > New workflow

C.

Workflow > Load workflow

D.

Actions > New workflow

Full Access
Question # 28

Which of the following statements are true regarding the use of GitHub Actions on a GitHub Enterprise Server instance? (Choose three.)

A.

Use of GitHub Actions on GitHub Enterprise Server requires a persistent internet connection

B.

Actions created by GitHub are automatically available and cannot be disabled

C.

Most GitHub authored actions are automatically bundled for use on GitHub Enterprise Server

D.

Third party actions can be used on GitHub Enterprise Server by configuring GitHub Connect

E.

Actions must be defined in the .github repository

F.

Third party actions can be manually synchronized for use on GitHub Enterprise Server

Full Access
Question # 29

Which statement is true about using default environment variables?

A.

The environment variables can be read in workflows using the ENV: variable_name syntax.

B.

The environment variables created should be prefixed with GITHUB_ to ensure they can be accessed in workflows

C.

The environment variables can be set in the defaults: sections of the workflow

D.

The GITHUB_WORKSPACE environment variable should be used to access files from within the runner.

Full Access
Question # 30

You create a self-hosted runner labeled as runner1.

You need to ensure that a GitHub Actions workflow job runs only on runner1.

Which YAML statement should you use?

A.

runs-on: [self-hosted, linux-xlarge]

B.

runs-on: - self-hosted - ubuntu-latest

C.

runs-on: [self-hosted, runner1]

D.

runs-on: self-hosted

Full Access
Question # 31

When should you use the GITHUB_TOKEN in a workflow?

A.

When you want to make authenticated calls to the GitHub API.

B.

When you want to connect to the runner via SSH.

C.

When you want to access repository-level secrets.

D.

When you want to call an action from GitHub Marketplace.

Full Access
Question # 32

As a developer, you are optimizing a GitHub workflow that uses and produces many different files. You need to determine when to use caching versus workflow artifacts. Which two statements are true? (Choose two.)

A.

Use caching when reusing files that change rarely between jobs or workflow runs.

B.

Use artifacts when referencing files produced by a job after a workflow has ended.

C.

Use caching to store cache entries for up to 30 days between accesses.

D.

Use artifacts to access the GitHub Package Registry and download a package for a workflow

Full Access
Question # 33

What is a valid scenario regarding environment secrets?

A.

Ensuring a job cannot access environment secrets until approval is obtained from a required reviewer.

B.

Ensuring only a specific step can access an environment secret.

C.

Configuring environment secrets for connecting to GitHub Enterprise Server.

D.

Configuring environment secrets to automatically pull from Azure Key Vault.

Full Access
Question # 34

As a developer, which of the following snippets will enable you to run the commands npm ci and npm run build as part of a workflow?

A.

- run: |

npm ci

npm run build

B.

- shell:

npm ci

npm run build

C.

- shell: |

npm ci

npm run build

D.

- run:

npm ci

npm run build

Full Access
Question # 35

Your organization has a secret that must be available to all the repositories within GitHub Actions workflows.

You need to store the secret. The solution must minimize administrative effort.

What should you do in GitHub?

A.

For each GitHub repository, select Settings > Secrets and variables > Actions, and then add the secret.

B.

From your personal GitHub profile, select Settings > Developer settings > Secrets, and then add the secret.

C.

From the organization ' s page, select Settings > Security > Secrets, and then add the secret.

D.

From the organization ' s page, select Settings > Secrets and variables > Actions, and then add the secret.

Full Access
Question # 36

As a developer, you created a JavaScript action. What is the best way to test your JavaScript action?

A.

Package your JavaScript action inside a Docker container image and run it.

B.

Create a workflow that only executes your specific JavaScript action.

C.

Create a workflow that includes the actions/debug-javascript action.

D.

Use a tool called @vercel/ncc to compile your code.

Full Access
Question # 37

You are a DevOps engineer working on deployment workflows. You need to execute the deploy job only if the current branch name is feature-branch. Which code snippet will help you implement the conditional execution of the job?

A.

jobs:

deploy:

if: github.branch_name == ' feature-branch '

runs-on: ubuntu-latest

B.

jobs:

deploy:

if: github.ref_name == ' feature-branch '

runs-on: ubuntu-latest

C.

jobs:

deploy:

if: github.ref.name = ' feature-branch '

runs-on: ubuntu-latest

D.

jobs:

deploy:

if: github.branch.name == ' feature-branch '

runs-on: ubuntu-latest

Full Access
Question # 38

An organization ' s policies specify that only local actions are allowed. How should actions be distributed for this organization?

A.

Via the GitHub Marketplace

B.

Via the .github repository owned by the organization

C.

Via a repository owned by a third party

D.

Via repositories owned by the organization

Full Access
Question # 39

You are a DevOps engineer working on custom Actions development. You need to handle errors or exceptions as part of the JavaScript-based action code. What should be added to the following code block to handle errors?

const core = require( ' @actions/core ' );

try {

// action code

} catch (error) {

// insert snippet here

}

A.

core.setException(error.message);

B.

core.action.setException(error.message);

C.

core.setFailed(error.message);

D.

action.setError(error.message);

Full Access
Question # 40

As a developer, you need to integrate a GitHub Actions workflow with a third-party code quality provider that uses the Checks API. How should you trigger a follow-up workflow?

A.

Add the workflow_run webhook event as a trigger for the workflow for the code quality integration name

B.

Add the check_run webhook event as a trigger for the workflow when the code quality integration is completed

C.

Add the pull_request webhook event as a trigger for the workflow when the code quality integration is synchronized

D.

Add the deployment webhook event as a trigger for the workflow when the code quality integration is completed

Full Access
Question # 41

As a developer, you need to make sure that only actions from trusted sources are available for use in your GitHub Enterprise Cloud organization. Which of the following statements are true? (Choose three.)
A.

Specific actions can individually be enabled for the organization, including version information.

B.

GitHub-verified actions can be collectively enabled for use in the enterprise.

C.

Actions can be restricted to only those available in the enterprise.

D.

Actions created by GitHub are automatically enabled and cannot be disabled.

E.

Individual third-party actions enabled with a specific tag will prevent updated versions of the action from introducing vulnerabilities.

F.

Actions can be published to an internal marketplace.

Full Access