Question # 4
Vulnerabilities have been detected on an organization ' s systems. Applications installed on these systems will not operate if the underlying servers are updated. Which of the following is the risk practitioner ' s BEST course of action?
A.
Recommend the business change the application.
B.
Recommend a risk treatment plan.
C.
Include the risk in the next quarterly update to management.
D.
Implement compensating controls.
Full Access
Answer:
B
Explanation:
A risk treatment plan typically includes the following elements2:
Risk description: A brief summary of the risk, its causes, and its consequences.
Risk owner: The person or entity who is responsible for managing the risk and implementing the risk treatment plan.
Risk response: The strategy or method chosen to deal with the risk, such as avoid, reduce, transfer, or accept.
Risk actions: The specific tasks or steps that need to be performed to execute the risk response.
Risk resources: The human, financial, technical, or other resources that are required or available to support the risk actions.
Risk timeline: The schedule or deadline for completing the risk actions and achieving the desired risk level.
By recommending a risk treatment plan, the risk practitioner can help the organization to:
Analyze and prioritize the vulnerabilities detected on the systems, and determine their impact and likelihood.
Evaluate and compare the possible risk responses, and select the most suitable and feasible one for each vulnerability.
Define and assign the roles and responsibilities for the risk treatment process, and ensure the accountability and collaboration of the stakeholders.
Monitor and measure the progress and effectiveness of the risk treatment process, and report the results and outcomes to the management.
The other options are not the best course of action, because:
Recommending the business change the application is not a realistic or practical option, as it may be costly, time-consuming, or technically challenging to modify the application to make it compatible with the updated servers. It may also create other issues or risks, such as compatibility problems with other systems, performance degradation, or user dissatisfaction.
Including the risk in the next quarterly update to management is not a proactive or timely option, as it may delay or defer the risk treatment process and increase the exposure or vulnerability of the systems. It may also indicate a lack of urgency or importance of the risk, and undermine the credibility or trust of the management.
Implementing compensating controls is not a sufficient or comprehensive option, as it may not address the root cause or the source of the risk. Compensating controls are alternative or additionalcontrols that are implemented when the primary or preferred controls are not feasible or effective3. They may reduce the impact or likelihood of the risk, but they may not eliminate or resolve the risk.
References =
Risk Treatment Plan - CIO Wiki
Risk Treatment Plan Template - ISACA
Compensating Control - CIO Wiki
Question # 5
Which of the following would MOST effectively enable a business operations manager to identify events exceeding risk thresholds?
A.
Continuous monitoring
B.
A control self-assessment
C.
Transaction logging
D.
Benchmarking against peers
Full Access
Answer:
A
Explanation:
Events exceeding risk thresholds are situations or occurrences that result in the actual level of risk exceeding the acceptable or tolerable level of risk, as defined by the organization’s risk appetite, criteria, and objectives12.
The most effective way to enable a business operations manager to identify events exceeding risk thresholds is to implement continuous monitoring, which is a process that involves collecting and analyzing data and information on the performance and status of the business processes, systems, and controls, and detecting and reporting any deviations, anomalies, or issues that may indicate a risk event34.
Continuous monitoring is the most effective way because it provides timely and accurate visibility and insight into the risk landscape, and enables the business operations manager to identify and respond to the events exceeding risk thresholds before they escalate or cause significant harm or damage to the organization34.
Continuous monitoring is also the most effective way because it supports the risk management process and objectives, which are to identify and address the risks that may affect the achievement of the organization’s goals and the delivery of value to the stakeholders34.
The other options are not the most effective ways, but rather possible tools or techniques that may complement or enhance the continuous monitoring. For example:
A control self-assessment is a technique that involves engaging and empowering the business process owners and operators to evaluate and report on the effectiveness and efficiency of the controls that are designed and implemented to mitigate the risks56. However, this technique is not the most effective way because it is periodic rather than continuous, and it may not capture or communicate the events exceeding risk thresholds in a timely or consistent manner56.
Transaction logging is a tool that involves recording and storing the details and history of the transactions or activities that are performed by the business processes or systems, and providing an audit trail for verification or investigation purposes78. However, this tool is not the most effective way because it is passive rather than active, and it may not detect or report the events exceeding risk thresholds unless they are analyzed or queried78.
Benchmarking against peers is a technique that involves comparing and contrasting the performance and practices of the business processes or systems with those of the similar or leading organizations in the same or related industry, and identifying the gaps or opportunities for improvement . However, this technique is not the most effective way because it is external rather than internal, and it may not reflect or align with the organization’s specific risk appetite, criteria, and objectives . References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: Continuous Monitoring - ISACA1
4: Continuous Monitoring: A New Approach to Risk Management - ISACA Journal2
5: Risk and control self-assessment - KPMG Global3
6: Control Self Assessments - PwC4
7: Transaction Log - Wikipedia5
8: Transaction Logging - IBM6
Benchmarking - Wikipedia7
Benchmarking: Definition, Types, Process, Advantages & Examples
Question # 6
A risk assessment has identified that an organization may not be in compliance with industry regulations. The BEST course of action would be to:
A.
conduct a gap analysis against compliance criteria.
B.
identify necessary controls to ensure compliance.
C.
modify internal assurance activities to include control validation.
D.
collaborate with management to meet compliance requirements.
Full Access
Answer:
A
Explanation:
 According to the CRISC Review Manual (Digital Version), the best course of action when a risk assessment has identified that an organization may not be in compliance with industry regulations is to conduct a gap analysis against compliance criteria, which is a method of comparing the current state of compliance with the desired or required state of compliance. Conducting a gap analysis against compliance criteria helps to:
Identify and evaluate the differences or discrepancies between the compliance requirements and the actual compliance practices and capabilities
Assess the impact and severity of the compliance gaps on the organization’s objectives and performance
Prioritize the compliance gaps based on their urgency and importance
Develop and implement appropriate actions or measures to close or reduce the compliance gaps
Monitor and measure the effectiveness and efficiency of the actions or measures taken to address the compliance gaps
References = CRISC Review Manual (Digital Version), Chapter 1: IT Risk Identification, Section 1.5: IT Risk Identification Methods and Techniques, pp. 34-351
Question # 7
Which of the following is MOST helpful in reducing the likelihood of inaccurate risk assessment results?
A.
Involving relevant stakeholders in the risk assessment process
B.
Updating organizational risk tolerance levels
C.
Reviewing the applicable risk assessment methodologies
D.
Having internal audit validate control effectiveness
Full Access
Answer:
A
Explanation:
Involving stakeholders ensures all perspectives are considered, leading to more accurate risk identification, assessment, and prioritization.
[Reference:CRISC Manual – Domain 2, Slide 256, , , , ]
Question # 8
Which of the following is a KEY consideration for a risk practitioner to communicate to senior management evaluating the introduction of artificial intelligence (Al) solutions into the organization?
A.
Al requires entirely new risk management processes.
B.
Al potentially introduces new types of risk.
C.
Al will result in changes to business processes.
D.
Third-party Al solutions increase regulatory obligations.
Full Access
Answer:
B
Explanation:
Artificial intelligence (AI) solutions can offer significant benefits to an organization, such as improved efficiency, accuracy, and innovation. However, AI also poses new challenges and risks that need to be considered and addressed by senior management. Some of these risks include:
Ethical and social risks: AI solutions may have unintended or undesirable impacts on human values, rights, and behaviors, such as privacy, fairness, accountability, and transparency. For example, AI systems may exhibit bias, discrimination, or manipulation, or may infringe on personal data or autonomy.
Technical and operational risks: AI solutions may have vulnerabilities, errors, or failures that affect their performance, reliability, or security. For example, AI systems may be subject to hacking, tampering, or misuse, or may malfunction or produce inaccurate or harmful outcomes.
Legal and regulatory risks: AI solutions may have unclear or conflicting legal or regulatory implications or obligations, such as liability, compliance, or governance. For example, AI systems may raise questions about ownership, responsibility, or accountability, or may violate existing laws or regulations, or create new ones.
Therefore, a risk practitioner should communicate to senior management that AI potentially introduces new types of risk that need to be identified, assessed, and managed in alignment with the organization’s objectives, values, and risk appetite. References = ISACA CRISC Review Manual, 7th Edition, Chapter 3, Section 3.2.2, page 113.
Question # 9
During a post-implementation review for a new system, users voiced concerns about missing functionality. Which of the following is the BEST way for the organization to avoid this situation in the future?
A.
Test system reliability and performance.
B.
Adopt an Agile development approach.
C.
Conduct user acceptance testing (UAT).
D.
Adopt a phased changeover approach.
Full Access
Answer:
C
Explanation:
Conducting User Acceptance Testing (UAT) is the best way for an organization to avoid situations where users voice concerns about missing functionality after a system implementation.
User Acceptance Testing (UAT):
Definition:UAT involves testing the system with actual users to ensure it meets their needs and requirements. It verifies that the system performs in real-world scenarios as expected by the users.
Involvement of Users:UAT includes the end-users in the testing process, ensuring that their feedback is incorporated and that the system functionalities align with their expectations.
Benefits:
Identifying Gaps:UAT helps in identifying gaps between the delivered system and user expectations. This early detection allows for adjustments before the system goes live.
Improved Satisfaction:By involving users in the testing process, the likelihood of the system meeting their needs increases, leading to higher user satisfaction and reduced post-implementation issues.
[References:, The CRISC Review Manual and best practices in project management emphasize the importance of UAT in ensuring that the system meets user requirements and avoids post-implementation functionality concerns ., , , , , , , , , , , ]
Question # 10
Mapping open risk issues to an enterprise risk heat map BEST facilitates:
A.
risk response.
B.
control monitoring.
C.
risk identification.
D.
risk ownership.
Full Access
Answer:
A
Explanation:
 A risk heat map is a visualization tool that shows the likelihood and impact of different risks on a matrix, using colors to indicate the level of risk. A risk heat map can help prioritize the risks that need the most attention and resources, and support the decision making and planning process for risk management. Mapping open risk issues to an enterprise risk heat map best facilitates risk response, which is the process of selecting and implementing the appropriate actions to address the risks. Risk response can include strategies such as mitigating, transferring, avoiding, or accepting risks. By mapping open risk issues to a risk heat map, an organization can identify the most suitable risk response for each risk, based on the risk appetite, criteria, and objectives. A risk heat map can also help evaluate the effectiveness and efficiency of the risk response, by showing the change in the level of residual risk after the risk response has been executed. References = What Is a Risk Heat Map & How Can It Help Your Risk Management Strategy, What Is a Risk Heat Map, and How Can It Help Your Risk Management Strategy, Risk Map (Risk Heat Map), How To Use A Risk Heat Map.
Question # 11
Which of the following should be the PRIMARY area of focus when reporting changes to an organization ' s risk profile to executive management?
A.
Risk management resources
B.
Risk tolerance
C.
Cyberattack threats
D.
Risk trends
Full Access
Answer:
D
Question # 12
Which of the following is the MOST important information to cover in a business continuity awareness training program for all employees of the organization?
A.
Recovery time objectives (RTOs)
B.
Communication plan
C.
Critical asset inventory
D.
Separation of duties
Full Access
Answer:
B
Question # 13
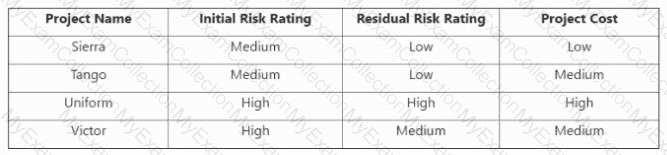
What can be determined from the risk scenario chart?
A.
Relative positions on the risk map
B.
Risk treatment options
C.
Capability of enterprise to implement
D.
The multiple risk factors addressed by a chosen response
Full Access
Answer:
A
Explanation:
The risk scenario chart shows the initial and residual risk ratings, and the project cost, for four projects named Sierra, Tango, Uniform, and Victor. The initial risk rating is the level of risk before applying any controls or mitigation measures, while the residual risk rating is the level of risk after applying the controls or measures. The project cost is the amount of resources required to implement the project. These three factors can be used to determine the relative positions of the projects on a risk map, which is a graphical tool for displaying the risks based on their impact and likelihood. The risk map can help to prioritize and compare the risks, and to select the most appropriate risk response strategy. The other options are not the best answers, as they are not directly shown or derived from the risk scenario chart. The risk treatment options are the possible actions that can be taken to address the risks, such as accept, avoid, mitigate, or transfer. The capability of enterprise to implement is the ability of the organization to execute the risk response plan,considering the available resources, skills, and constraints. The multiple risk factors addressed by a chosen response are the various elements that contribute to or affect the risk, such as the threat sources, events, vulnerabilities, assets, and impacts. These factors are not explicitly stated or measured in the risk scenario chart, and may require further analysis or information. References = How to Write Strong Risk Scenarios and Statements - ISACA; Identifying the Right Risk Scenarios to Measure with FAIR; How to write good risk scenarios and statements
Question # 14
An organization recently invested in an identity and access management (IAM) solution to manage user activities across corporate mobile devices. Which of the following is MOST important to update in the risk register?
A.
Inherent risk
B.
Risk appetite
C.
Risk tolerance
D.
Residual risk
Full Access
Answer:
D
Explanation:
Residual risk is the remaining risk after implementing risk responses, such as controls or mitigation strategies. With the deployment of an IAM solution, the organization has addressed certain access-related risks. Updating the risk register to reflect the new residual risk levels ensures accurate tracking and informs future risk management decisions.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 3: Risk Response and Reporting, Section: Risk Response., , , , , , , ]
Question # 15
A threat intelligence team has identified an indicator of compromise related to an advanced persistent threat (APT) actor. Which of the following is the risk practitioner ' s BEST course of action?
A.
Review the most recent vulnerability scanning report.
B.
Determine the business criticality of the asset.
C.
Determine the adequacy of existing security controls.
D.
Review prior security incidents related to the asset.
Full Access
Answer:
B
Question # 16
Which of the following is the MOST important criteria for selecting key risk indicators (KRIs)?
A.
Historical data availability
B.
Implementation and reporting effort
C.
Ability to display trends
D.
Sensitivity and reliability
Full Access
Answer:
D
Explanation:
Sensitivity and reliability are the most important criteria for selecting KRIs, as they indicate how well the KRIs reflect the changes in the risk level and how consistent and accurate the KRIs are in measuring the risk.Sensitivity means that the KRIs should respond quickly and proportionally to the variations in the risk exposure, and provide early warning signals of potential risk events. Reliability means that the KRIs should be based on valid and verifiable data sources, and produce consistent and comparable results over time and across different units or functions. Historical data availability, implementation and reporting effort, and ability to display trends are also useful criteria, but they are not as critical as sensitivity and reliability.
[References:, •ISACA, Risk IT Framework, 2nd Edition, 2019, p. 751, •ISACA, Risk and Information Systems Control Review Manual, 7th Edition, 2020, p. 2122, , , , , , , , , , , ]
Question # 17
Which of the following BEST facilitates the identification of appropriate key performance indicators (KPIs) for a risk management program?
A.
Reviewing control objectives
B.
Aligning with industry best practices
C.
Consulting risk owners
D.
Evaluating KPIs in accordance with risk appetite
Full Access
Answer:
D
Explanation:
The best way to facilitate the identification of appropriate key performance indicators (KPIs) for a risk management program is to evaluate KPIs in accordance with risk appetite. KPIs are metrics that measure the performance and effectiveness of the risk management program, and help monitor and report on the achievement of the risk objectives and outcomes. Risk appetite is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives. Evaluating KPIs in accordance with risk appetite helps to identify the appropriate KPIs, because it helps to align the KPIs with the organization’s mission, vision, values, and strategy, and to ensure that the KPIs reflect the organization’s risk tolerance and threshold. Evaluating KPIs in accordance with risk appetite also helps to communicate and coordinate the KPIs with the organization’s stakeholders, such as the board, management, and business units, and to facilitate the risk decision-making and reporting processes. The other options are not as effective as evaluating KPIs in accordance with risk appetite, although they may be part of or derived from the KPI identification process. Reviewing control objectives, aligning with industry best practices, and consulting risk owners are all activities that can help to define or refine the KPIs, but they are not the best way to facilitate the identification of appropriate KPIs. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.5.1, page 4-38.
Question # 18
The MOST appropriate key performance indicator (KPI) to communicate the effectiveness of an enterprise IT risk management program is:
A.
The percentage of risk scenarios that are within organizational tolerance
B.
The percentage of IT staff trained in risk management
C.
The number of critical business services covered by a risk assessment
D.
The amount of IT risk realized that impacted the business
Full Access
Answer:
A
Explanation:
The KPI that best measureseffectivenessof risk management is one that showsrisk alignment with tolerance levels.
CRISC defines:
“Risk management effectiveness is demonstrated when risk scenarios are managed within the organization’s defined tolerance.â€
BandCare activity-based, not outcome-based.
Dmeasures realized losses, not ongoing control success.
Hence,A. The percentage of risk scenarios within organizational tolerancedirectly reflects program effectiveness.
CRISC Reference:Domain 4 – Risk and Control Monitoring and Reporting, Topic: Key Risk and Performance Indicators.
Question # 19
Which of the following would BEST help to ensure that suspicious network activity is identified?
A.
Analyzing intrusion detection system (IDS) logs
B.
Analyzing server logs
C.
Using a third-party monitoring provider
D.
Coordinating events with appropriate agencies
Full Access
Answer:
A
Explanation:
An intrusion detection system (IDS) is a network security tool that monitors and analyzes network traffic for signs of malicious or suspicious activity, such as unauthorized access, data exfiltration, malware infection, or denial-of-service attack. An IDS can detect and alert the organization to potential threats based on predefined rules or signatures, or based on anomalies or deviations from normal network behavior. An IDS can also generate logs that record the details of the network events and incidents, such as the source, destination, content, and context of the network traffic. By analyzing the IDS logs, the organization can identify and validate the suspicious network activity, and determine its scope, impact, and root cause. The organization can also use the IDS logs to support the incident response and remediation process, and to improve the network security and resilience. The other options are less effective ways to ensure that suspicious network activity is identified. Analyzing server logs can provide some information about the network activity, but it may not be sufficient or timely to detect and validate the suspicious or malicious activity, as server logs only capture the events or activities that occur on the server, and not on the entire network. Using a third-party monitoring provider can help to outsource the network monitoring and analysis function, but it may not be the best option, as it may introduce additional risks, such as data privacy, vendor reliability, or service quality issues. Coordinating events with appropriate agencies can help to share information and resources with other organizations or authorities, such as law enforcement, regulators, or industry peers, but it may not be the best option, as it may depend on the availability andcooperation of theagencies, and it may not be feasible or desirable to disclose the network activity to external parties. References = Monitoring for Suspicious Network Activity: Key Tips to Secure Your Network 1
Question # 20
Which of the following is the MOST important consideration when selecting either a qualitative or quantitative risk analysis?
A.
Expertise in both methodologies
B.
Maturity of the risk management program
C.
Time available for risk analysis
D.
Resources available for data analysis
Full Access
Answer:
C
Explanation:
The most important consideration when selecting either a qualitative or quantitative risk analysis is the time available for risk analysis, as this affects the level of detail and accuracy that can be achieved in the risk assessment process. Qualitative risk analysis is a method that uses subjective judgments and ratings to measure and prioritize the risks based on their likelihood and impact, as well as other factors such as urgency, velocity, and persistence. Qualitative risk analysis is usually faster and simpler than quantitative risk analysis, but it may also be less precise and consistent. Quantitative risk analysis is a method that uses numerical data and mathematicalmodels to measure and prioritize the risks based on theirprobability and magnitude, as well as other factors such as frequency, duration, and correlation. Quantitative risk analysis is usually more complex and time-consuming than qualitative risk analysis, but it may also provide more objective and reliable results. The other options are not the most important considerations when selecting either a qualitative or quantitative risk analysis, although they may have some influence or relevance. Expertise in both methodologies is desirable, but it does not determine the choice of the risk analysis method, as it depends on the availability and suitability of the experts for the specific risk context and objectives. Maturity of the risk management program is important, but it does not dictate the choice of the risk analysis method, as it depends on the level of integration and alignment of the risk management activities with the enterprise’s strategy and goals. Resources available for data analysis are relevant, but they do not decide the choice of the risk analysis method, as they depend on the quality and availability of the data sources and tools for the risk assessment process. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Assessment, page 81.ST
Question # 21
Who is PRIMARILY accountable for risk treatment decisions?
A.
Risk owner
B.
Business manager
C.
Data owner
D.
Risk manager
Full Access
Answer:
A
Explanation:
The risk owner is primarily accountable for risk treatment decisions, as they are the person or entity with the authority and responsibility to manage a particular risk. The risk owner shouldevaluate the available risk response options, select the most appropriate one, implement the chosen response, and monitor its effectiveness. The risk owner should also communicate and report on the risk status and any issues or changes. The business manager, data owner, and risk manager are not primarily accountable for risk treatment decisions, although they may be involved in the risk management process. The business manager is responsible for the overall performance and objectives of a business unit or function. The data owner is responsible for the security and quality of a specific data asset. The risk manager is responsible for facilitating and coordinating the risk management activities across the organization. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Identification, page 47.
Question # 22
Which of the following should be the PRIMARY consideration when assessing the automation of control monitoring?
A.
impact due to failure of control
B.
Frequency of failure of control
C.
Contingency plan for residual risk
D.
Cost-benefit analysis of automation
Full Access
Answer:
D
Explanation:
Automation of control monitoring is the application of technology to allow continuous or high-frequency, automated monitoring of controls to validate the effectiveness of controls designed to mitigate risk1.
Automation of control monitoring can provide benefits such as increased test coverage, improved timeliness, reduced risk velocity, greater visibility, improved consistency, and the ability to identify trends23.
However, automation of control monitoring also involves costs such as the acquisition, implementation, maintenance, and updating of the technology, as well as the training and support of the staff who use it45.
Therefore, the primary consideration when assessing the automation of control monitoring is the cost-benefit analysis of automation, which compares the expected benefits and costs of automation and determines whether the benefits outweigh the costs or vice versa45.
The other options are not the primary consideration, but rather secondary or tertiary factors that may influence the decision to automate or not. For example, the impact due to failure of controland the frequency of failure of control are aspects of the risk assessment that may indicatethe need for automation, but they do not provide the basis for evaluating the feasibility and desirability of automation45. Similarly, the contingency plan for residual risk is a component of the risk response that may include automation as a risk mitigation strategy, but it does not measure the effectiveness and efficiency of automation45. References =
2: A Practical Approach to Continuous Control Monitoring, ISACA Journal, Volume 2, 2015
3: Continuous Controls Monitoring: The Next Generation Of Controls Testing, Forbes Technology Council, June 2, 2022
1: Making Continuous Controls Monitoring Work for Everyone, ISACA Now Blog, June 13, 2022
4: Controls Automation - Monitoring vs. Operation - Part 3, Turnkey Consulting, July 29, 2021
5: What’s Continuous Control Monitoring and Why Is It Important?, MetricStream Blog, October 15, 2019
Question # 23
An organization has asked an IT risk practitioner to conduct an operational risk assessment on an initiative to outsource the organization ' s customer service operations overseas. Which of the following would MOST significantly impact management ' s decision?
A.
Time zone difference of the outsourcing location
B.
Ongoing financial viability of the outsourcing company
C.
Cross-border information transfer restrictions in the outsourcing country
D.
Historical network latency between the organization and outsourcing location
Full Access
Answer:
C
Explanation:
The most significant factor that would impact management’s decision when conducting an operational risk assessment on an initiative to outsource the organization’s customer service operations overseas is the cross-border information transfer restrictions in the outsourcing country. Cross-border information transfer restrictions are the laws, regulations, standards, or contracts that govern the collection, processing, storage, or transmission of information across national or regional boundaries. Cross-border information transfer restrictions may affect the organization’s outsourcing initiative, because they may impose limitations, obligations, or penalties on the organization or the outsourcing company, such as requiring consent, notification, or authorization, or prohibiting or restricting certain types or categories of information. Cross-border information transfer restrictions may also create challenges or risks for the organization’s outsourcing initiative, such as compliance, legal, reputational, or operational risks, or conflicts orinconsistencies with the organization’s own policies, regulations, standards, or contracts. The other options are not as significant as the cross-border information transfer restrictions, although they may also pose some difficulties or limitations for the organization’s outsourcing initiative. Time zone difference of the outsourcing location, ongoing financial viability of the outsourcing company, and historical network latency between the organization and outsourcing location are all factors that could affect the efficiency and effectiveness of the outsourcing initiative, but they do not directly affect the legality or security of the outsourcing initiative. References = 3
Question # 24
Which of the following would be MOST helpful to a risk practitioner when preparing a summary of current IT risk for senior management review?
A.
Changes in risk mitigation plans
B.
Resolution status of audit findings
C.
Areas of elevated risk
D.
Industry risk management benchmarks
Full Access
Answer:
C
Explanation:
Senior management requireshigh-level, decision-relevantinformation. CRISC guidance states that the most valuable elements to communicate areareas of elevated risk, because these represent conditions that may exceed risk appetite or require immediate action. Changes in mitigation plans and audit findings are important operational details but do not provide a clear picture of current exposure. Industry benchmarks offer context but do not describe the organization’s actual risk posture. Highlighting elevated risks helps executives prioritize resources, make treatment decisions, and determine whether escalations are required.
[Reference:CRISC Review Manual – Risk and Control Monitoring and Reporting (executive risk communication)., ========================================, ]
Question # 25
External penetration tests MUST include:
A.
use of consultants to ensure completeness.
B.
communications to users of the target systems.
C.
changes to target data to prove the attack was successful.
D.
advance approval from system owners.
Full Access
Answer:
D
Question # 26
The number of tickets to rework application code has significantly exceeded the established threshold. Which of the following would be the risk practitioner s BEST recommendation?
A.
Perform a root cause analysis
B.
Perform a code review
C.
Implement version control software.
D.
Implement training on coding best practices
Full Access
Answer:
A
Explanation:
A root cause analysis is a process of identifying and understanding the underlying or fundamental causes or factors that contribute to or result in a problem or incident that has occurred or may occur in the organization. A root cause analysis can provide useful insights and solutions on the origin and nature of the problem or incident, and prevent or reduce its recurrence or impact.
Performing a root cause analysis is the risk practitioner’s best recommendation when the number of tickets to rework application code has significantly exceeded the established threshold, because it can help the organization to address the following questions:
Why did the application code require rework?
What were the errors or defects in the application code?
How did the errors or defects affect the functionality or usability of the application?
Who was responsible or accountable for the application code development and testing?
When and how were the errors or defects detected and reported?
What were the costs or consequences of the rework for the organization and its stakeholders?
How can the errors or defects be prevented or minimized in the future?
Performing a root cause analysis can help the organization to improve and optimize the application code quality and performance, and to reduce or eliminate the need for rework. It can also help the organization to align the application code development and testing with the organization’s objectives and requirements, and to comply with the organization’s policies and standards.
The other options are not the risk practitioner’s best recommendations when the number of tickets to rework application code has significantly exceeded the established threshold, because they do not address the main purpose and benefit of performing a root cause analysis, which is to identify and understand the underlying or fundamental causes or factors that contribute to or result in the problem or incident.
Performing a code review is a process of examining and evaluating the application code for its quality, functionality, and security, using the input and feedback from the peers, experts, or tools. Performing a code review can help the organization to identify and resolve the errors or defects in the application code, but it is not the risk practitioner’s best recommendation, because it doesnot indicate why the application code required rework, and how the errors or defects affected the organization and its stakeholders.
Implementing version control software is a process of using a software tool to manage and track the changes and modifications to the application code, and to ensure the consistency and integrity of the application code. Implementing version control software can help theorganization to control and monitor the application code development and testing, but it is not the risk practitioner’s best recommendation, because it does not indicate why the application code required rework, and how the errors or defects affected the organization and its stakeholders.
Implementing training on coding best practices is a process of providing and facilitating the learning and development of the skills and knowledge on the principles, guidelines, and standards for the application code development and testing. Implementing training on coding best practices can help the organization to enhance the competence and performance of the application code developers and testers, but it is not the risk practitioner’s best recommendation, because it does not indicate why the application code required rework, and how the errors or defects affected the organization and its stakeholders. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 189
CRISC Practice Quiz and Exam Prep
Question # 27
Which of the following is the MOST important consideration for prioritizing risk treatment plans when faced with budget limitations?
A.
Inherent risk and likelihood
B.
Management action plans associated with audit findings
C.
Residual risk relative to appetite and tolerance
D.
Key risk indicator (KRI) trends
Full Access
Answer:
C
Explanation:
When prioritizing risk treatment plans under budget constraints, the focus should be onresidual risk relative to appetite and tolerance. This ensures that resources are allocated to risks that exceed the organization’s risk appetite, aligning treatment efforts with strategic objectives and minimizing critical exposure.
Question # 28
Which of the following is the PRIMARY benefit of integrating risk and security requirements in an organization ' s enterprise architecture (EA)?
A.
Adherence to legal and compliance requirements
B.
Reduction in the number of test cases in the acceptance phase
C.
Establishment of digital forensic architectures
D.
Consistent management of information assets
Full Access
Answer:
D
Explanation:
Integrating risk and security requirements in an organization’s enterprise architecture (EA) helps to ensure that information assets are consistently managed throughout their life cycle, and that the risks associated with them are identified and mitigated. (Risk and Information Systems Control Review Questions, Answers & Explanations Manual, 5th Edition, page 112)
Question # 29
Which of the following is the BEST recommendation to address recent IT risk trends that indicate social engineering attempts are increasing in the organization?
A.
Conduct a simulated phishing attack.
B.
Update spam filters
C.
Revise the acceptable use policy
D.
Strengthen disciplinary procedures
Full Access
Answer:
A
Explanation:
The best recommendation to address recent IT risk trends that indicate social engineering attempts are increasing in the organization is to conduct a simulated phishing attack, as it tests the awareness and behavior of the employees in responding to a realistic and targeted email scam, and identifies the areas and individuals that need improvement or training. Updating spam filters, revising the acceptable use policy, and strengthening disciplinary procedures are not the best recommendations, as they may not address the human factor of the risk, or may be too reactive or punitive, respectively. References = CRISC Review Manual, 7th Edition, page 155.
Question # 30
Which of the following is the PRIMARY role of the board of directors in corporate risk governance?
A.
Approving operational strategies and objectives
B.
Monitoring the results of actions taken to mitigate risk
C.
Ensuring the effectiveness of the risk management program
D.
Ensuring risk scenarios are identified and recorded in the risk register
Full Access
Answer:
B
Question # 31
Which of the following should be the PRIMARY consideration when identifying and assigning ownership of IT-related risk?
A.
Accountability for control operation
B.
Ability to design controls to mitigate the risk
C.
Accountability for losses due to impact
D.
Span of control within the organization
Full Access
Answer:
C
Explanation:
The correct answer isCbecause the primary consideration when assigning ownership of IT-related risk isaccountability for losses due to impact. Risk ownership should be assigned to the person or function with the authority and accountability for the business consequences if the risk materializes. Ownership should align to business accountability, not just technical control operation.
The other options are less appropriate:
A. Accountability for control operationmay belong to a control owner, but that is not always the same as the risk owner.
B. Ability to design controls to mitigate the riskis relevant to implementation, not primary ownership.
D. Span of control within the organizationmay influence practicality, but it is not the key principle for assigning risk ownership.
Exact Extracts supporting the answer:
“Accountability for business risk related to IT primarily lies with users of IT services.â€
“For an IT system supporting a critical business process senior managers should be accountable for the risk.â€
“For an organizational business unit the most accurate description of risk-related roles and responsibilities is that the management team owns the risk and is responsible for identifying assessing and mitigating risk and reporting to the appropriate support functions and the board of directors.â€
“The best basis for establishing risk ownership is mapping identified risk to a specific business process.â€
“During the risk assessment process it is most important to establish a clear line of accountability to ensure that risk ownership is assigned to the appropriate level.â€
These extracts show that risk ownership must align with the party accountable for the business impact of the risk. Therefore, the primary consideration isaccountability for losses due to impact.
Question # 32
Which of the following potential scenarios associated with the implementation of a new database technology presents the GREATEST risk to an organization?
A.
The organization may not have a sufficient number of skilled resources.
B.
Application and data migration cost for backups may exceed budget.
C.
Data may not be recoverable due to system failures.
D.
The database system may not be scalable in the future.
Full Access
Answer:
C
Explanation:
The potential scenario that presents the greatest risk to an organization when implementing a new database technology is that data may not be recoverable due to system failures. Data recovery is the process of restoring or retrieving data that has been lost, corrupted, or damaged due to system failures, such as hardware malfunctions, software errors, power outages, or natural disasters. Data recovery is essential for the continuity and integrity of the organization’s operations and information, as data is one of the most valuable and critical assets of the organization. Data recovery is also important for the compliance and accountability of the organization, as data may be subject to legal or regulatory requirements, such as retention, backup, or audit. Data recovery may be challenging or impossible when implementing a new database technology, because the new technology may not be compatible or interoperable with the existing systems, applications, or backups, or because the new technology may nothave adequate or tested recovery mechanisms or procedures. Data recovery may also be costly or time-consuming when implementing a new database technology, because the new technology may require additional or specialized resources, tools, or expertise, or because the new technology may involve large or complex data sets or structures. The other options are not as risky as data recovery, although they may also pose some difficulties or limitations for the new database technology implementation. The organization may not have a sufficient number of skilled resources, application and data migration cost for backups may exceed budget, and the database system may not be scalable in the future are all factors that could affect the feasibility and sustainability of the new database technology, but they do not directly affect the continuity and integrity of the organization’s operations and information. References = 2
Question # 33
Which of the following would MOST effectively reduce the potential for inappropriate exposure of vulnerabilities documented in an organization ' s risk register?
A.
Limit access to senior management only.
B.
Encrypt the risk register.
C.
Implement role-based access.
D.
Require users to sign a confidentiality agreement.
Full Access
Answer:
C
Explanation:
A risk register is a document that contains information about potential cybersecurity risks that could threaten a project’s success, or even the business itself2. Therefore, it is important to protect the confidentiality and integrity of the risk register from unauthorized or inappropriate access, modification, or disclosure. One way to do this is to implement role-based access, which is a method of restricting access to the risk register based on the roles or responsibilities of the users1. This way, only authorized users who need to view or edit the risk register for legitimate purposes can do so, and the access rights can be revoked or modified as needed. This would most effectively reduce the potential for inappropriate exposure of vulnerabilities documented in the risk register. The other options are not as effective or feasible as option C, as they do not address the need to balance the security and availability of the risk register. Option A, limiting access to senior management only, would compromise the availability and usefulness of the risk register, as other stakeholders such as project managers, risk owners, or auditors may need to access therisk register for risk identification, analysis, response, or monitoring purposes3. Option B, encrypting the risk register, would enhance the security of the risk register, but it would not prevent authorized users from exposing the vulnerabilities to unauthorized parties, either intentionally or unintentionally. Encryption also adds complexity and cost to the risk register management process, and may affect the performance or usability of the risk register4. Option D, requiring users to sign a confidentiality agreement, would rely on the compliance and ethics of the users, but it would not prevent or detect any breaches of the agreement. A confidentiality agreement also does not specify the access rights or roles of the users, and may not be legally enforceable in some cases5.
Question # 34
An organization has implemented immutable backups to prevent successful ransomware attacks. Which of the following is the MOST effective control for the risk practitioner to review?
A.
Data recovery testing of the backups
B.
Physical security of the backups
C.
Configuration of the backup solution
D.
Retention policy for the backups
Full Access
Answer:
C
Question # 35
Which of the following is MOST important to sustainable development of secure IT services?
A.
Security training for systems development staff
B.
\Well-documented business cases
C.
Security architecture principles
D.
Secure coding practices
Full Access
Answer:
A
Explanation:
The most important factor for sustainable development of secure IT services is security training for systems development staff. Security training helps to ensure that the staff members are aware of the security risks, requirements, and best practices that affect the IT services they develop. Security training also helps to improve the security skills and knowledge of the staff members,and to foster a security culture and behavior within the development team. Security training can also help to prevent or reduce security defects, vulnerabilities, or incidents in the IT services, and to enhance the security performance and quality of the IT services. Well-documented business cases, security architecture principles, and secure coding practices are also important factors for sustainable development of secure IT services, but they are not as important as security trainingfor systems development staff. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 5, Section 5.1.1.2, page 2291
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 653.
Question # 36
Improvements in the design and implementation of a control will MOST likely result in an update to:
A.
inherent risk.
B.
residual risk.
C.
risk appetite
D.
risk tolerance
Full Access
Answer:
B
Explanation:
 Residual risk is the risk that remains after applying controls to mitigate the inherent risk. Inherent risk is the risk that exists before considering the controls. Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk tolerance is the acceptable level of variation from the risk appetite. Improvements in the design and implementation of a control will most likely result in an update to the residual risk, because they will reduce the likelihood and impact of the risk event, and therefore lower the risk exposure and value. By improving the design and implementation of a control, the organization can enhance the effectiveness and efficiency of the control, and ensure that it is aligned with the risk objectives, expectations, and outcomes. The improvement can also address any gaps, overlaps, redundancies, or conflicts among the controls, and any changes or enhancements that are needed to optimize the controls. The other options are less likely to be updated due to improvements in the design and implementation of a control. The inherent risk will not change, as it is based on the nature and value of the asset and the threats and vulnerabilities that exist. The risk appetite and the risk tolerance will also not change, as they are based on the organization’s culture, strategy, and stakeholder expectations. Therefore, the most likely factor to be updated is the residual risk, as it reflects the actual risk level that the organization faces after applying the controls. References = Risk IT Framework, ISACA, 2022, p. 131
Question # 37
An organization has established a single enterprise-wide risk register that records high-level risk scenarios. The IT risk department has created its own register to record more granular scenarios applicable to IT. Which of the following is the BEST way to ensure alignment between these two registers?
A.
Map the granular risk scenarios to the high-level risk register items.
B.
List application and server vulnerabilities in the IT risk register.
C.
Identify overlapping risk scenarios between the two registers.
D.
Maintain both high-level and granular risk scenarios in a single register.
Full Access
Answer:
A
Explanation:
Mapping granular scenarios to high-level register items ensures consistency and alignment across different levels of risk management. This approach supportsIntegrated Risk Management Frameworks.
Question # 38
Which of the following should be the PRIMARY focus of an independent review of a risk management process?
A.
Accuracy of risk tolerance levels
B.
Consistency of risk process results
C.
Participation of stakeholders
D.
Maturity of the process
Full Access
Answer:
D
Explanation:
The primary focus of an independent review of a risk management process is to evaluate the maturity of the process, which means the extent to which the process is aligned with the organization’s objectives, culture, and governance, and how well it is integrated, implemented, and monitored across the organization. A mature risk management process is one that is consistent, effective, efficient, and adaptable to changing circumstances and environments. A maturity assessment can help to identify the strengths and weaknesses of the risk management process, as well as the opportunities and challenges for improvement. The other options are not the primary focus, but they may be secondary or tertiary aspects of the review. Accuracy of risk tolerance levels is a measure of how well the organization defines and communicates its risk appetite and risk limits, which are important inputs for the risk management process, but not the main outcome. Consistency of risk process results is a measure of how reliable and repeatable the risk management process is, which reflects the quality and validity of the data, assumptions, methods, and tools used in the process, but not the overall effectiveness and efficiency of the process. Participation of stakeholders is a measure of how well the organization engages and involves its internal and external stakeholders in the risk management process, which enhancesthe awareness, ownership, andaccountability of the process, but not the alignment and integration of the process. References = Assessing the Risk Management Process, p. 9-10.
Question # 39
Which of the following is the PRIMARY reason for a risk practitioner to examine a post-implementation review report for a control automation tool?
A.
To verify that budget for the project is managed effectively
B.
To confirm compliance with project management methodology
C.
To ensure the risk is managed to an acceptable level
D.
To ensure audit findings are addressed in a timely manner
Full Access
Answer:
C
Explanation:
The main purpose of implementing controls is to reduce risk to an acceptable level. Reviewing the effectiveness of the new tool post-implementation ensures the control objective has been achieved.
[Reference:CRISC Manual – Domain 3, Slide 345-346, 388, , , , ]
Question # 40
Which of the following is the GREATEST benefit of having a mature enterprise architecture (EA) in place?
A.
Standards-based policies
B.
Audit readiness
C.
Efficient operations
D.
Regulatory compliance
Full Access
Answer:
C
Explanation:
The greatest benefit of having a mature enterprise architecture (EA) in place is efficient operations, as EA provides a holistic view of the organization’s business processes, information systems, and technology infrastructure, and enables alignment, integration, and optimization of these components. Standards-based policies, audit readiness, and regulatory compliance are also benefits of EA, but they are not the greatest benefit. References = CRISC Review Manual, 7th Edition, page 145.
Question # 41
The PRIMARY benefit of conducting continuous monitoring of access controls is the ability to identify:
A.
inconsistencies between security policies and procedures
B.
possible noncompliant activities that lead to data disclosure
C.
leading or lagging key risk indicators (KRIs)
D.
unknown threats to undermine existing access controls
Full Access
Answer:
B
Explanation:
The primary benefit of conducting continuous monitoring of access controls is the ability to identify possible noncompliant activities that lead to data disclosure. Continuous monitoring of access controls is a process that involves collecting, analyzing, and reporting on the performance and effectiveness of the access controls on a regular basis. Continuous monitoring of access controls helps to detect and prevent any unauthorized or inappropriate access to information assets, and to ensure that the access controls arealigned with the enterprise’s security policies and standards. Continuous monitoring of access controls also helps to identify possible noncompliant activities that lead to data disclosure, such as data leakage, data theft, data tampering, or data breach. By identifying these activities, the enterprise can take timely and appropriate actions to mitigate the risk and protect the confidentiality, integrity, and availability of the information assets. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.3.2, page 1411
Question # 42
Which of the following risk scenarios would be the GREATEST concern as a result of a single sign-on implementation?
A.
User access may be restricted by additional security.
B.
Unauthorized access may be gained to multiple systems.
C.
Security administration may become more complex.
D.
User privilege changes may not be recorded.
Full Access
Answer:
B
Explanation:
 According to the CRISC Review Manual1, single sign-on (SSO) is a method of authentication that allows a user to access multiple systems or applications with a single set of credentials. SSO can improve user convenience and productivity, but it also introduces some security risks. The greatest concern as a result of a single sign-on implementation is that unauthorized access may be gained to multiple systems, as this can compromise the confidentiality, integrity, and availability of the data and resources stored on those systems. If an attacker obtains the SSO credentials of a user, either by phishing, malware, or other means, they can Laccess all the systems or applications that the user is authorized for, without any additional authentication or verification. This can expose the organization to various threats, such as data leakage, theft, loss, corruption, manipulation, or misuse2345. References = CRISC Review Manual1, page 240, 253.
Question # 43
Which of the following will BEST help to ensure implementation of corrective action plans?
A.
Contracting to third parties
B.
Establishing employee awareness training
C.
Setting target dates to complete actions
D.
Assigning accountability to risk owners
Full Access
Answer:
D
Explanation:
Assigning accountability to risk owners is the best way to ensure implementation of corrective action plans, because it clarifies the roles and responsibilities of those who are in charge of managing and mitigating the risks. Contracting to third parties, establishing employee awareness training, and setting target dates tocomplete actions are all helpful measures, but they do not guarantee the implementation of corrective action plans without accountability. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.3, page 105
Question # 44
Which of the following practices MOST effectively safeguards the processing of personal data?
A.
Personal data attributed to a specific data subject is tokenized.
B.
Data protection impact assessments are performed on a regular basis.
C.
Personal data certifications are performed to prevent excessive data collection.
D.
Data retention guidelines are documented, established, and enforced.
Full Access
Answer:
A
Explanation:
Personal data is any information that relates to an identified or identifiable individual, such as name, address, email, phone number, etc. Processing personal data involves collecting, storing, using, disclosing, or deleting it. Processing personal data poses various risks to the privacy and security of the data subjects,such as unauthorized access, disclosure, modification, or loss. Therefore, processing personal data requires appropriate technical and organizational measures to safeguard the data and to comply with the relevant laws and regulations. One of the most effective practices to safeguard the processing of personal data is to use tokenization. Tokenization is a technique that replaces sensitive data elements with non-sensitive equivalents, called tokens, that have no meaning or value outside of a specific system or context. Tokenization reduces the risk of exposing personal data to unauthorized parties, as the tokens cannot be reversed or linked back to the original data without the proper key or algorithm. Tokenization also helps to minimize the amount of personal data that is stored or transmitted, and to limit the scope of compliance requirements. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2.2, p. 196-197
Question # 45
Which of the following trends would cause the GREATEST concern regarding the effectiveness of an organization ' s user access control processes? An increase in the:
A.
ratio of disabled to active user accounts.
B.
percentage of users with multiple user accounts.
C.
average number of access entitlements per user account.
D.
average time between user transfers and access updates.
Full Access
Answer:
D
Explanation:
The average time between user transfers and access updates is a trend that would cause the greatest concern regarding the effectiveness of an organization’s user access control processes, as it indicates thedelay or inefficiency in updating the user access rights and privileges according to the user’s current role and responsibilities. This can result in unauthorized or excessive access to the organization’s information assets, and increase the risk of data leakage, fraud, or misuse. The user access control processes should ensure that the user access rights and privileges are reviewed and modified regularly, and especially when the user’s role or status changes, such as transfer, promotion, demotion, or termination. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question241. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 241. CRISC Sample Questions 2024, Question 241.
Question # 46
Which of the following activities is a responsibility of the second line of defense?
A.
Challenging risk decision making
B.
Developing controls to manage risk scenarios
C.
Implementing risk response plans
D.
Establishing organizational risk appetite
Full Access
Answer:
A
Explanation:
The second line of defense is responsible for challenging the risk decision making of the first line of defense, which is the business process owners and managers. The second line of defense also provides oversight, guidance, and support to the first line of defense in implementing andmaintaining effective risk management practices. The second line of defense includes functions such as risk management, compliance, quality assurance, and internal audit. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.2: IT Risk Management Roles and Responsibilities, Page 14.
Question # 47
An organization wants to grant remote access to a system containing sensitive data to an overseas third party. Which of the following should be of GREATEST concern to management?
A.
Transborder data transfer restrictions
B.
Differences in regional standards
C.
Lack of monitoring over vendor activities
D.
Lack of after-hours incident management support
Full Access
Answer:
A
Question # 48
Which of the following is the BEST key performance indicator (KPI) for a server patch management process?
A.
The percentage of servers with allowed patching exceptions
B.
The number of servers with local credentials to install patches
C.
The percentage of servers patched within required service level agreements
D.
The number of servers running the software patching service
Full Access
Answer:
C
Explanation:
This KPI measures how well the server patch management process meets the agreed-upon standards and expectations for timeliness, quality, and security. It reflects the efficiency and effectiveness of the patch deployment and the compliance with the patch policy. It also helps to identify and address any issues or delays that may affect the patching performance.
References
•Patch Management KPI Metrics - Motadata
•KPI Examples for Patch and Vulnerability Management - Heimdal Security
•Measuring the Effectiveness of Your Patch Management Strategy - Automox
Question # 49
Which of the following is a PRIMARY objective of privacy impact assessments (PIAs)?
A.
To identify threats introduced by business processes
B.
To identify risk when personal information is collected
C.
To ensure senior management has approved the use of personal information
D.
To ensure compliance with data privacy laws and regulations
Full Access
Answer:
D
Question # 50
Which of the following is MOST important to consider when selecting key risk indicators (KRIs)? The ability to:
A.
Measure changes in the threat landscape.
B.
Refine the organization’s risk appetite.
C.
Monitor the performance of a process.
D.
Assess the risk associated with risk scenarios.
Full Access
Answer:
D
Explanation:
The BEST answer is D because a KRI must be linked to a specific risk or risk scenario and should provide an early warning of increased risk exposure. ISACA’s CRISC exam outline includes defining, implementing, refining, monitoring, and analyzing KRIs, KPIs, and KCIs as supporting CRISC tasks. ISACA’s risk indicator explanation distinguishes indicators clearly: a KRI gives an early signal of increased exposure to risk, while a KPI measures performance over time for a specific objective. The uploaded CRISC notes directly support this: the most important consideration when implementing KRIs is linking the metric to a specific risk, and the most important attribute of an effective KRI is that it is linked to a specific risk.
A is too narrow because KRIs may measure many types of risk exposure, not only threat landscape changes. B is incorrect because risk appetite is normally set by governance/senior leadership; KRIs monitor exposure against appetite/tolerance, not refine appetite themselves. C describes a KPI more than a KRI, because process performance monitoring is performance-focused rather than risk-exposure-focused.
Question # 51
Which of the following is the MAIN benefit to an organization using key risk indicators (KRIs)?
A.
KRIs provide an early warning that a risk threshold is about to be reached.
B.
KRIs signal that a change in the control environment has occurred.
C.
KRIs provide a basis to set the risk appetite for an organization.
D.
KRIs assist in the preparation of the organization ' s risk profile.
Full Access
Answer:
A
Explanation:
The main benefit of using key risk indicators (KRIs) for an organization is that they provide an early warning that a risk threshold is about to be reached. KRIs are metrics that measure the likelihood and impact of risks, and help monitor and prioritize the most critical risks. KRIs also help to trigger timely and appropriate risk responses, before the risk becomes unmanageable orunacceptable. The other options are not the main benefit of using KRIs, although they may be secondary benefits or outcomes. KRIs signal that a change in the control environment has occurred, provide a basis to set the risk appetite for an organization, and assist in the preparation of the organization’s risk profile. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.1, page 4-36.
Question # 52
Which stakeholders are PRIMARILY responsible for determining enterprise IT risk appetite?
A.
Audit and compliance management
B.
The chief information officer (CIO) and the chief financial officer (CFO)
C.
Enterprise risk management and business process owners
D.
Executive management and the board of directors
Full Access
Answer:
D
Explanation:
The stakeholders who are PRIMARILY responsible for determining enterprise IT risk appetite are the executive management and the board of directors, because they are the ones who set thestrategic direction and objectives of the enterprise, and who define the acceptable level of risk exposure and tolerance for achieving those objectives. The other options are not the primary stakeholders, because:
Option A: Audit and compliance management are responsible for providing assurance and oversight on the effectiveness of the risk management process and the compliance with internal and external requirements, but they do not determine the enterprise IT risk appetite.
Option B: The CIO and the CFO are responsible for managing the IT resources and the financial resources of the enterprise, respectively, but they do not determine the enterprise IT risk appetite.
Option C: Enterprise risk management and business process owners are responsible for identifying, assessing, and responding to the risks that affect their domains, but they do not determine the enterprise IT risk appetite. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 83.
Question # 53
Which of the following is MOST important for a risk practitioner to consider when analyzing the risk associated with migrating to a new cloud service provider?
A.
The cloud service provider ' s control environment
B.
The complexity of the cloud services
C.
The date of the cloud service provider ' s last risk assessment
D.
Past incidents related to acquired cloud services
Full Access
Answer:
A
Question # 54
During a risk assessment, what should an assessor do after identifying threats to organizational assets?
A.
Request funding for the security program
B.
Determine threats to be reported to upper management
C.
Implement controls to achieve target risk levels
D.
Evaluate the controls currently in place
Full Access
Answer:
D
Explanation:
The CRISC risk assessment process follows asequence:
Identify assets →
Identify threats →
Identify vulnerabilities →
Evaluate existing controls→
Assess likelihood and impact.
Per ISACA CRISC guidance:
“After identifying threats, the next step is to evaluate the effectiveness of existing controls to determine residual risk.â€
Implementing new controls (Option C) happensafterrisk evaluation and treatment planning.
Hence,D. Evaluate the controls currently in placeis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Risk Identification and Control Evaluation Steps.
Question # 55
Which of the following would require updates to an organization ' s IT risk register?
A.
Discovery of an ineffectively designed key IT control
B.
Management review of key risk indicators (KRls)
C.
Changes to the team responsible for maintaining the register
D.
Completion of the latest internal audit
Full Access
Answer:
A
Explanation:
An IT risk register is a document that records and tracks the identified IT risks, their likelihood, impact, and mitigation strategies. It is a living document that needs to be updated regularly to reflect the current risk profile of the organization. One of the situations that would require updates to the IT risk register is the discovery of an ineffectively designed key IT control, as this would increase the likelihood or impact of the related IT risk. Management review of key risk indicators (KRIs), changes to the team responsible for maintaining the register, and completion of the latest internal audit are not reasons to update the IT risk register, as they do not affect the identified IT risks or their mitigation strategies. References = [CRISC Review Manual (DigitalVersion)], page 97; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 198.
Question # 56
An organization is developing a risk awareness program for contractors and consultants. Which of the following is MOST important for the organization to keep confidential?
A.
Key risk indicator (KRI) threshold methodology
B.
Names of key cloud providers
C.
Unmitigated vulnerabilities
D.
Corporate security policies
Full Access
Answer:
C
Explanation:
The correct answer isCbecauseunmitigated vulnerabilitiesare the most important information to keep confidential. Revealing known weaknesses that have not yet been addressed could directly increase the likelihood of exploitation by insiders, contractors, consultants, or external parties who gain access to that information.
The other options are less sensitive in this context:
A. Key risk indicator (KRI) threshold methodologyis sensitive governance information, but it is not as directly exploitable as known vulnerabilities.
B. Names of key cloud providersmay be known or inferable and are not as dangerous as exposing actual weaknesses.
D. Corporate security policiesare often shared broadly to support compliance and awareness, and employees or contractors typically need to know them.
Exact Extracts supporting the answer:
“The MOST critical observation when reviewing system configuration files for a critical enterprise application system is access to configuration files is not restricted.â€
“The MOST concern to the risk practitioner regarding applications running in production is backdoors.â€
“A lack of adequate controls represents a vulnerability exposing sensitive processes and/or data to potential malicious damage or unauthorized access.â€
“The MOST serious vulnerability allowing attackers to access data through a web application is when validation checks are missing in data input fields enabling attacks like SQL injection.â€
These extracts support that vulnerabilities are highly sensitive because they expose the organization to direct attack. Therefore,unmitigated vulnerabilitiesare the most important to keep confidential.
===========
Question # 57
Which of the following BEST prevents control gaps in the Zero Trust model when implementing in the environment?
A.
Relying on multiple solutions for Zero Trust
B.
Utilizing rapid development during implementation
C.
Establishing a robust technical architecture
D.
Starting with a large initial scope
Full Access
Answer:
C
Question # 58
Which of the following BEST helps to mitigate risk associated with excessive access by authorized users?
A.
Monitoring user activity using security logs
B.
Revoking access for users changing roles
C.
Granting access based on least privilege
D.
Conducting periodic reviews of authorizations granted
Full Access
Answer:
C
Explanation:
The principle of least privilege is a key concept in information security that aims to provide users with the minimum level of access—or permissions—necessary to perform their job functions. Byensuring that users only have the access they need, organizations can significantly reduce the risk associated with excessive access by authorized users.
Understanding Least Privilege
The principle of least privilege restricts access rights for users to the bare minimum permissions they need to perform their work. This minimizes the potential damage from accidents or malicious activities.
Least privilege should be applied to all user accounts, including administrative and service accounts.
Implementation
Implementing least privilege involves a detailed analysis of job functions and the necessary access required for each role.
Regularly review and update access permissions to ensure they remain aligned with current job responsibilities and organizational needs.
Mitigating Risk
By limiting access to only what is necessary, organizations can prevent users from having permissions that could be exploited, intentionally or unintentionally, to cause harm.
This also includes revoking unnecessary privileges when users change roles or no longer need access.
Comparison with Other Options
A. Monitoring user activity using security logs: While monitoring can detect inappropriate activity, it does not prevent it.
B. Revoking access for users changing roles: This is a necessary practice but does not address the initial allocation of excessive privileges.
D. Conducting periodic reviews of authorizations granted: Periodic reviews are important but are reactive rather than proactive.
References
Sybex-CISSP-Official-Study-Guide-9-Edition.pdf, p. 641, discussing the principle of least privilege and its implementation​​.
Question # 59
When updating a risk register with the results of an IT risk assessment, the risk practitioner should log:
A.
high impact scenarios.
B.
high likelihood scenarios.
C.
treated risk scenarios.
D.
known risk scenarios.
Full Access
Answer:
D
Explanation:
When updating a risk register with the results of an IT risk assessment, the risk practitioner should log the known risk scenarios, because they are the risk scenarios that have been identified and assessed in the IT risk assessment process. The risk register should document and track the known risk scenarios, their characteristics, their status, and their responses. The other options are not the ones that should be logged, because:
Option A: High impact scenarios are the risk scenarios that have a high potential impact on the business objectives and processes, but they are not the only ones that should be logged. The risk register should include all the known risk scenarios, regardless of their impact level.
Option B: High likelihood scenarios are the risk scenarios that have a high probability of occurrence, but they are not the only ones that should be logged. The risk register should include all the known risk scenarios, regardless of their likelihood level.
Option C: Treated risk scenarios are the risk scenarios that have been addressed by the risk response actions, but they are not the only ones that should be logged. The risk register shouldinclude all the known risk scenarios, regardless of their treatment status. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 108.
Question # 60
An organization recently received an independent security audit report of its cloud service provider that indicates significant control weaknesses. What should be done NEXT in response to this report?
A.
Migrate all data to another compliant service provider.
B.
Analyze the impact of the provider ' s control weaknesses to the business.
C.
Conduct a follow-up audit to verify the provider ' s control weaknesses.
D.
Review the contract to determine if penalties should be levied against the provider.
Full Access
Answer:
B
Explanation:
An independent security audit report is a document that provides an objective and comprehensive assessment of the security posture and practices of a cloud service provider (CSP), based on a set of standards, criteria, or frameworks1. An independent security audit report can help an organization to evaluate the risks and benefits of using a CSP, and to ensure that the CSP meets the organization’s security and compliance requirements2.
If an organization receives an independent security audit report of its CSP that indicates significant control weaknesses, the next step that should be done in response to this report is to analyze the impact of the provider’s control weaknesses to the business. This means that the organization should:
Identify and prioritize the business processes, functions, or objectives that depend on or are affected by the CSP’s services
Assess the potential consequences and likelihood of the control weaknesses leading to security incidents, breaches, or losses
Estimate the financial, operational, reputational, or legal impacts of the security incidents, breaches, or losses
Compare the impacts with the organization’s risk appetite and tolerance, and determine the level of risk exposure and acceptance
Communicate the results of the analysis to the relevant stakeholders and decision-makers3
References = What is a Security Audit?, Cloud Security Audit: A 10-Step Checklist, Independent security audits are essential for cloud service providers. Here’s why
Question # 61
Which of the following is the BEST indication that an organization ' s IT asset life cycle is poorly managed?
A.
Increased hardware maintenance costs
B.
Sensitive data found on discarded devices
C.
Lack of asset labeling
D.
Inadequate employee training
Full Access
Answer:
B
Explanation:
The correct answer isBbecause findingsensitive data on discarded devicesis the clearest indication that the IT asset life cycle is poorly managed. This points to failure in end-of-life handling, media sanitization, disposal controls, ownership accountability, and policy enforcement. It is a direct indicator of life cycle control breakdown with significant security and compliance consequences.
The other options are less conclusive:
A. Increased hardware maintenance costsmay indicate inefficiency, but not necessarily poor life cycle control.
C. Lack of asset labelingis a weakness, but less severe and less direct than improper disposal of sensitive data.
D. Inadequate employee trainingmay contribute to problems, but it is not the strongest indicator by itself.
Exact Extracts supporting the answer:
“When data are no longer needed by a particular process they should be handled according to policy.â€
“Information that is no longer required to support the main purpose of the enterprise from an information security perspective should be managed under the retention policy.â€
“The data security control that BEST protects the confidentiality of data stored on backup media in transit to a third-party storage facility is encryption.â€
“The BEST safeguard against a data breach is security awareness training.â€
These extracts support that assets and the data on them must be handled according to policy throughout the life cycle, especially when no longer needed. Sensitive data remaining on discarded devices is therefore the strongest indication of poor asset life cycle management.
===========
Question # 62
The MAJOR reason to classify information assets is
A.
maintain a current inventory and catalog of information assets
B.
determine their sensitivity and critical
C.
establish recovery time objectives (RTOs)
D.
categorize data into groups
Full Access
Answer:
B
Explanation:
Information asset classification is the process of assigning a level of sensitivity and criticality to an information asset based on its value, importance, and impact to the organization. The major reason to classify information assets is to determine their sensitivity and criticality, which are the measures of how confidential, proprietary, or sensitive the information is, and how essential, urgent, or time-sensitive the information is for the business operations. By determining the sensitivity and criticality of information assets, the organization can prioritize the protection and recovery of the information assets, implement the appropriate security controls and safeguards, comply with the regulatory and contractual requirements, and manage the information lifecycle and disposal. References = CRISC Review Manual, 7th Edition, page 74.
Question # 63
When evaluating a number of potential controls for treating risk, it is MOST important to consider:
A.
risk appetite and control efficiency.
B.
inherent risk and control effectiveness.
C.
residual risk and cost of control.
D.
risk tolerance and control complexity.
Full Access
Answer:
C
Explanation:
The most important factors to consider when evaluating a number of potential controls for treating risk are the residual risk and the cost of control. Residual risk is the risk that remains after the implementation of the controls. Cost of control is the amount of resources and efforts required to implement and maintain the controls. By considering the residual risk and the cost of control, the organization can optimize the balance between the risk exposure and the control investment, and choose the most effective and efficient controls. Risk appetite and control efficiency, inherent risk and control effectiveness, and risk tolerance and control complexity are other possible factors, but they are not as important as residual risk and cost of control. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 8; CRISC Review Manual, 6th Edition, page 97.
Question # 64
What should a risk practitioner do FIRST when a shadow IT application is identified in a business owner ' s business impact analysis (BIA)?
A.
Include the application in the business continuity plan (BCP).
B.
Determine the business purpose of the application.
C.
Segregate the application from the network.
D.
Report the finding to management.
Full Access
Answer:
B
Explanation:
Determining the business purpose of the application is the first thing that a risk practitioner should do when a shadow IT application is identified in a business owner’s business impactanalysis (BIA), because it helps to understand the rationale and value of the application, and the potential risks and issues that it may introduce or affect. A shadow IT application is an IT system or application that is used by the business units or employees without the knowledge or approval of the IT department or management. A shadow IT application may offer benefits such as convenience, efficiency, or innovation, but it may also pose risks such as security breaches, data loss, compatibility issues, or regulatory non-compliance. A BIA is a process of analyzing the potential impact of disruption to the critical business functions or processes, and identifying the recovery priorities and requirements. A BIA may reveal the existence of ashadow IT application, as it may be used to support or enable a critical business function or process. Determining the business purpose of the application is the first thing to do, as it helps to evaluate the necessity and suitability of the application, and to plan the appropriate actions to address the shadow IT application. Including the application in the business continuity plan (BCP), segregating the application from the network, and reporting the finding to management are all possible things to do after determining the business purpose of the application, but they are not the first thing to do, as they depend on the results of the evaluation of the application. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 143
Question # 65
The FIRST step for a startup company when developing a disaster recovery plan (DRP) should be to identify:
A.
Current vulnerabilities
B.
Recovery time objectives (RTOs)
C.
Critical business processes
D.
A suitable alternate site
Full Access
Answer:
C
Explanation:
Thefoundationof any DRP is identifying whichbusiness processes are criticalto the organization’s operations and survival.
CRISC guidance:
“The initial step in disaster recovery and business continuity planning is identifying and prioritizing critical business processes and the resources required to support them.â€
From there, RTOs and recovery strategies are developed.
Hence,C. Critical business processesis correct.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Business Impact and Continuity Planning.
Question # 66
Which of the following contributes MOST to the effective implementation of risk responses?
A.
Clear understanding of the risk
B.
Comparable industry risk trends
C.
Appropriate resources
D.
Detailed standards and procedures
Full Access
Answer:
C
Explanation:
Appropriate resources contribute most to the effective implementation of risk responses. Resources include people, time, money, equipment, and materials that are needed to execute the risk responses. Without appropriate resources, the risk responses may not be implemented properly, timely, or efficiently, and may not achieve the desired outcomes. The other options are not as important as appropriate resources, as they are related to the understanding, comparison, or documentation of the risk responses, which are less critical than the execution of the riskresponses. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Question # 67
Which of the following is a risk practitioner ' s MOST important action to reduce the likelihood of internal fraud?
A.
Recommend fraud awareness training for staff
B.
Communicate legal consequences for internal fraud.
C.
Update the internal fraud risk likelihood in the risk register.
D.
Verify the effectiveness of separation of duties.
Full Access
Answer:
D
Explanation:
The correct answer isDbecause the most important action to reduce the likelihood of internal fraud is toverify the effectiveness of separation of duties. Separation of duties is a core preventive control that reduces the opportunity for fraudulent activity by ensuring no single individual has end-to-end control over critical transactions or processes.
The other options are less effective:
A. Recommend fraud awareness training for staffis useful, but it is not as strong a preventive control as segregation of duties.
B. Communicate legal consequences for internal fraudmay deter misconduct, but it does not directly reduce control weakness.
C. Update the internal fraud risk likelihood in the risk registeris documentation, not risk reduction.
Exact Extracts supporting the answer:
“The PRIMARY reason that an enterprise would establish segregation of duties controls is to prevent errors or fraudulent activity on high-risk transactions.â€
“The MOST effective control to prevent segregation of duties violations is implementing role-based access.â€
“The control that focuses directly on preventing the risk of collusion is mandatory job rotation.â€
“An independent review of audit logs is the best compensating control when a segregation of duties conflict exists in a small IT department.â€
These extracts show that preventive control effectiveness, especially segregation of duties, is the strongest way to reduce the likelihood of internal fraud.
Question # 68
The BEST indication that risk management is effective is when risk has been reduced to meet:
A.
risk levels.
B.
risk budgets.
C.
risk appetite.
D.
risk capacity.
Full Access
Answer:
C
Explanation:
 The best indication that risk management is effective is when risk has been reduced to meet the risk appetite of the enterprise. Risk appetite is the amount and type of risk that an enterprise is willing to accept in pursuit of its objectives. Risk appetite reflects the enterprise’s risk culture, strategy, and values, and provides a basis for setting risk tolerance levels and risk response strategies. Risk management is effective when it enables the enterprise to align its risk exposure with its risk appetite, and to optimize the risk-return trade-off. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.1, page 181
Question # 69
Which of the following would be a weakness in procedures for controlling the migration of changes to production libraries?
A.
The programming project leader solely reviews test results before approving the transfer to production.
B.
Test and production programs are in distinct libraries.
C.
Only operations personnel are authorized to access production libraries.
D.
A synchronized migration of executable and source code from the test environment to the production environment is allowed.
Full Access
Answer:
A
Explanation:
The programming project leader solely reviewing test results before approving the transfer to production would be a weakness in procedures for controlling the migration of changes to production libraries, because it violates the principle of segregation of duties, and it exposes the production libraries to the risk of unauthorized or erroneous changes. The programming project leader is responsible for developing and testing the changes, but not for approving and deploying them. The approval and deployment of the changes should be done by an independent and authorized party, such as the change control board or the operations manager. The other options are not weaknesses, but rather good practices, because:
Option B: Test and production programs being in distinct libraries is a good practice, because it prevents the accidental or intentional overwriting or mixing of the test and production programs, and it ensures the integrity and security of the production libraries.
Option C: Only operations personnel being authorized to access production libraries is a good practice, because it restricts the access and modification of the production libraries to the qualified and accountable staff, and it prevents the unauthorized or inappropriate access or modification of the production libraries by other parties.
Option D: A synchronized migration of executable and source code from the test environment to the production environment being allowed is a good practice, because it ensures the consistency and completeness of the changes, and it avoids the potential errors or discrepancies that may arise from the manual or partial migration of the changes. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 215.
Question # 70
Which of the following is the MOST important component of effective security incident response?
A.
Network time protocol synchronization
B.
Identification of attack sources
C.
Early detection of breaches
D.
A documented communications plan
Full Access
Answer:
D
Explanation:
The most important component of effective security incident response is a documented communications plan. A communications plan defines the roles and responsibilities, channels and methods, frequency and timing, and content and format of the communications that take place during and after a security incident. A communications plan helps to ensure that the relevant stakeholders are informed and updated about the incident status and outcome, and that the incident response activities are coordinated and consistent. A communications plan also helps to manage the expectations and perceptions of the stakeholders, and to maintain the trust and reputation of the enterprise. Network time protocol synchronization, identification of attack sources, and early detection of breaches are also important components of effective security incident response, but they are not as important as a documented communications plan. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.1.2, page 1931
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 660.
Question # 71
During a risk assessment, a key external technology supplier refuses to provide control design and effectiveness information, citing confidentiality concerns. What should the risk practitioner do NEXT?
A.
Escalate the non-cooperation to management
B.
Exclude applicable controls from the assessment.
C.
Review the supplier ' s contractual obligations.
D.
Request risk acceptance from the business process owner.
Full Access
Answer:
C
Explanation:
The next step for the risk practitioner when a key external technology supplier refuses to provide control design and effectiveness information is to review the supplier’s contractual obligations. The contract between the organization and the supplier should specify the terms and conditions for the provision of the service or function, including the requirements for control design and effectiveness information. By reviewing the contract, the risk practitioner can determine if the supplier is breaching the contract and take appropriate actions to enforce the contract or terminate the relationship. Escalating the non-cooperation to management, excluding applicable controls from the assessment, and requesting risk acceptance from the business process owner are other possible steps, but they are not as effective as reviewing the supplier’s contractual obligations. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Question # 72
Which of the following should be determined FIRST when a new security vulnerability is made public?
A.
Whether the affected technology is used within the organization
B.
Whether the affected technology is Internet-facing
C.
What mitigating controls are currently in place
D.
How pervasive the vulnerability is within the organization
Full Access
Answer:
A
Explanation:
 When a new security vulnerability is made public, the first step is to determine whether the affected technology is used within the organization. This will help to assess the impact and exposure of the vulnerability on the organization’s assets, processes, and objectives. If the affected technology is not used within the organization, then the vulnerability does not pose a direct threat and no further action is required. However, if the affected technology is used within the organization, then the next steps are to identify the systems and components that are vulnerable, evaluate the severity and likelihood of the vulnerability being exploited, and implement appropriate mitigating controls or remediation actions. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.2.1, p. 240-241
Question # 73
When establishing leading indicators for the information security incident response process it is MOST important to consider the percentage of reported incidents:
A.
that results in a full root cause analysis.
B.
used for verification within the SLA.
C.
that are verified as actual incidents.
D.
resolved within the SLA.
Full Access
Answer:
D
Explanation:
When establishing leading indicators for the information security incident response process, it is most important to consider the percentage of reported incidents that are resolved within the service levelagreement (SLA). A leading indicator is a metric that can predict or influence the future performance or outcome of a process or activity. A leading indicator for the information security incident response process should measure how well the process is achieving its objectives, such as minimizing the impact of incidents, restoring normal operations as quickly as possible, and preventing recurrence of incidents. The percentage of reported incidents that are resolved within the SLA is a leading indicator that reflects the efficiency and effectiveness of the information security incident response process. It shows how well the process is meeting the expectations and requirements of the stakeholders, such as the business units, customers, and regulators. It also shows how well the process is managing the resources, such as time, budget, and personnel, that are allocated for incident response. A high percentage of reported incidents that are resolved within the SLA indicates that the information security incident response process is performing well and delivering value to the organization. A low percentage of reported incidents that are resolved within the SLA indicates that the information security incident response process is facing challenges and needs improvement. The percentage of reported incidents that are resolved within the SLA can also help identify the root causes of incidents, the gaps in the process, and the areas for improvement. For example, if the percentage of reported incidents that are resolved within the SLA is low, it may indicate that the process has issues with the following aspects: - Incident detection and reporting: The process may not have adequate tools, techniques, or procedures to detect and report incidents in a timely and accurate manner. - Incident prioritization and classification: The process may not have clear and consistent criteria to prioritize and classify incidents based on their severity, impact, and urgency. - Incident analysis and investigation: The process may not have sufficient skills, knowledge, or evidence to analyze and investigate the incidents and determine their root causes, scope, and consequences. - Incident containment and eradication: The process may not have effective methods or measures to contain and eradicate the incidents and prevent them from spreading or escalating. - Incidentrecovery and restoration: The process may not have reliable backup and recovery plans or systems to restore the normal operations and functionality of the affected systems or services. - Incident communication and escalation: The process may not have proper communication and escalation channels or protocols to inform and involve the relevant stakeholders, such as the management, the users, the vendors, or the authorities. - Incident documentation and closure:The process may not have adequate documentation and closure procedures to record and report the incidents and their resolution. - Incident review and improvement: The process may not have regular review and improvement activities to evaluate and enhance the process and its performance. Therefore, the percentage of reported incidents that are resolved within the SLA is the most important leading indicator for the information security incident response process, as it can provide valuable insights and feedback for the process and its improvement. References = Information Security Incident Response | Process Street1, Key Performance Indicators (KPIs) for Security Operations and Incident Response2, 7 Incident Response Metrics and How to Use Them3
Question # 74
Which of the following is MOST useful when performing a quantitative risk assessment?
A.
RACI matrix
B.
Financial models
C.
Management support
D.
Industry benchmarking
Full Access
Answer:
B
Question # 75
Which of the following would provide the BEST evidence of an effective internal control environment/?
A.
Risk assessment results
B.
Adherence to governing policies
C.
Regular stakeholder briefings
D.
Independent audit results
Full Access
Answer:
D
Explanation:
 The best evidence of an effective internal control environment is the independent audit results. Independent audit results are the outcomes or findings of an external or independent party that evaluates the design, implementation, and operation of the internal controls. Independent audit results can provide an objective, reliable, and consistent assessment of the internal control environment, and identify the strengths, weaknesses, gaps, or issues of the internal controls. Independent audit results can also provide assurance, recommendations, or improvement opportunities for the internal control environment. The other options are not as good as independent audit results, as they are related to the inputs, processes, oroutputs of the internal control environment, not the evaluation or verification of the internal controlenvironment. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: IT Control Assessment, page 69.
Question # 76
An organization mandates the escalation of a service ticket when a key application is offline for 5 minutes or more due to potential risk exposure. The risk practitioner has been asked by management to prepare a report of application offline times using both 3- and 5-minute thresholds. What does the 3-minute threshold represent?
A.
Recovery Time Objective (RTO)
B.
Key Risk Indicator (KRI)
C.
Recovery Point Objective (RPO)
D.
Key Performance Indicator (KPI)
Full Access
Answer:
B
Explanation:
The 3-minute threshold is a KRI designed to act as an early warning before a more critical limit (5 minutes) is breached, helping prevent risk realization.
[Reference:CRISC Manual – Domain 4, Slide 380-382, , , , ]
Question # 77
Which of the following is the GREATEST risk associated with an environment that lacks documentation of the architecture?
A.
Unknown vulnerabilities
B.
Legacy technology systems
C.
Network isolation
D.
Overlapping threats
Full Access
Answer:
A
Explanation:
Architecture is the design and structure of a system or a process, such as an IT system or a business process. Architecture documentation is the document that describes and explains the architecture, such as its components, functions, relationships, requirements, constraints, orstandards. Architecture documentation can help to understand, communicate, and improve the system or the process1.
An environment that lacks documentation of the architecture faces a great risk of unknown vulnerabilities, which are the weaknesses or flaws in the system or the process that could be exploited by threats or attackers, but are not identified or addressed by the organization. Unknown vulnerabilities can pose a serious risk to the organization, because they can:
Compromise the confidentiality, integrity, and availability of the system or the process, and the information or resources that it handles or supports
Cause financial, operational, reputational, or legal damages or losses to the organization, such as data breaches, fraud, errors, delays, or fines
Remain undetected or unresolved for a long time, and increase the exposure or impact of the risk over time
Require more resources or efforts to mitigate or recover from the risk, and reduce the efficiency or effectiveness of the risk management process23
Lack of documentation of the architecture can increase the risk of unknown vulnerabilities, because it can:
Prevent or hinder the identification and assessment of the vulnerabilities, and the evaluation and prioritization of the risks
Impede or delay the implementation and enforcement of the controls or safeguards to prevent or reduce the vulnerabilities, and the monitoring and reporting of the risk status and progress
Obstruct or limit the communication and coordination among the stakeholders, and the awareness and accountability of the risk owners and users
Restrict or hamper the review and improvement of the system or the process, and the learning and feedback of the risk management4
The other options are not the greatest risks associated with an environment that lacks documentation of the architecture, but rather some of the possible causes or consequences of it.Legacy technology systems are outdated or obsolete systems that are still in use by the organization, but are no longer supported or maintained by the vendors or developers. Legacy technology systems can be a cause of lack of documentation of the architecture, as they may have been developed or acquired without proper documentation, or the documentation may have been lost or discarded over time. Network isolation is the separation or segregation of a network or a system from other networks or systems, either physically or logically, to prevent or limit the access or communication between them. Network isolation can be a consequence of lack of documentation of the architecture, as it may result from the inability or difficulty to integrate or connect the system or the process with other systems or processes. Overlapping threats are threats that affect more than one system or process, or have similar or related sources or causes, such as natural disasters, cyberattacks, or human errors. Overlapping threats can be a consequence of lack of documentation of the architecture, as they may arise from the lack of understanding or coordination of the system or the process with other systems or processes. References =
Architecture Documentation - ISACA
Vulnerability - ISACA
The Risks of Not Having a Vulnerability Management Program
The Importance of Architecture Documentation - ISACA
[The Risk of Poor Document Control - ComplianceBridge]
[CRISC Review Manual, 7th Edition]
Question # 78
Which of the following is the MAIN reason for documenting the performance of controls?
A.
Obtaining management sign-off
B.
Demonstrating effective risk mitigation
C.
Justifying return on investment
D.
Providing accurate risk reporting
Full Access
Answer:
D
Explanation:
The main reason for documenting the performance of controls is to provide accurate risk reporting. Risk reporting is a process that communicates and discloses the relevant and reliable information about the risks and their management to the stakeholders and decision makers. Risk reporting is an essential component of the risk management process, as it helps to monitor and evaluate the effectiveness and efficiency of the risk identification, assessment, response, and monitoring activities, as well as to support and inform the risk governance and oversight functions. Documenting the performance of controls is a technique that records and tracks the results and outcomes of the controls that are implemented to address the risks, such as the control objectives,
Question # 79
An organization has decided to commit to a business activity with the knowledge that the risk exposure is higher than the risk appetite. Which of the following is the risk practitioner ' s MOST important action related to this decision?
A.
Recommend risk remediation
B.
Change the level of risk appetite
C.
Document formal acceptance of the risk
D.
Reject the business initiative
Full Access
Answer:
C
Explanation:
The risk practitioner’s most important action related to the decision to commit to a business activity with the knowledge that the risk exposure is higher than the risk appetite is to document formal acceptance of the risk. Formal acceptance of the risk means that the organization acknowledges and agrees to bear the risk and its potential consequences. Formal acceptance of the risk should be documented and approved by the appropriate authority level, such as senior management or the board of directors. Formal acceptance of the risk should also include the rationale, assumptions, and conditions for accepting the risk, as well as the monitoring and reporting mechanisms for the risk. Formal acceptance of the risk provides evidence and accountability for the risk management decision and helps to avoid disputes or misunderstandings in the future. The other options are not as important as documenting formalacceptance of the risk, as they are related to the alternatives, adjustments, or rejections of the risk, not the actual acceptance of the risk. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.2: IT Risk Response Options, page 133.
Question # 80
An organization must make a choice among multiple options to respond to a risk. The stakeholders cannot agree and decide to postpone the decision. Which of the following risk responses has the organization adopted?
A.
Transfer
B.
Mitigation
C.
Avoidance
D.
Acceptance
Full Access
Answer:
C
Explanation:
Risk avoidance is a type of risk response that involves eliminating the risk entirely by not engaging in the activity that causes the risk or changing the conditions that create the risk1. Riskavoidance is usually applied when the potential impact or likelihood of the risk is high or unacceptable, and when the benefits of avoiding the risk outweigh the costs or losses of doing so2.
In this case, the organization has adopted risk avoidance as its risk response, because it has decided to postpone the decision that could trigger the risk. By delaying the decision, the organization is avoiding therisk of making a wrong or unfavorable choice among the multiple options. However, this may not be the best or most effective risk response, as it could also result in missed opportunities, wasted resources, or increased uncertainty3. The organization shouldconsider the trade-offs and consequences of avoiding the risk, and explore other possible risk responses that could reduce or transfer the risk.
The other options are not the risk responses that the organization has adopted. Risk transfer means shifting the responsibility or burden of the risk to another party, such as a vendor or an insurer2. The organization has not transferred the risk to anyone else, but rather avoided it by postponing the decision. Risk mitigation means implementing controls or safeguards to minimize the negative effects of the risk2. The organization has not mitigated the risk by reducing its impact or likelihood, but rather avoided it by delaying the decision. Risk acceptance means acknowledging the risk and its consequences without taking any action to address it2. The organization has not accepted the risk by tolerating its potential outcomes, but rather avoided it by postponing the decision. References =
10 Risk Mitigation techniques you need to know - Stakeholdermap.com
Risk Response Strategies: Types & Examples (+ Free Template)
[CRISC Review Manual, 7th Edition]
Question # 81
When determining risk ownership, the MAIN consideration should be:
A.
who owns the business process.
B.
the amount of residual risk.
C.
who is responsible for risk mitigation.
D.
the total cost of risk treatment.
Full Access
Answer:
A
Question # 82
A large organization is replacing its enterprise resource planning (ERP) system and has decided not to deploy the payroll module of the new system. Instead, the current payroll system will continue to be
used. Of the following, who should own the risk if the ERP and payroll system fail to operate as expected?
A.
The business owner
B.
The ERP administrator
C.
The project steering committee
D.
The IT project manager
Full Access
Answer:
A
Explanation:
The business owner should own the risk if the ERP and payroll system fail to operate as expected, because the business owner is ultimately responsible for the business processes and objectives that depend on the systems. The other options are not the risk owners, because:
Option B: The ERP administrator is responsible for the technical aspects of the ERP system, but not the payroll system or the business outcomes.
Option C: The project steering committee is responsible for overseeing the project of replacing the ERP system, but not the ongoing operation and maintenance of the systems or the business risks.
Option D: The IT project manager is responsible for managing the project of replacing the ERP system, but not the payroll system or the business risks. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 90.
Question # 83
Which of the following aspects of an IT risk and control self-assessment would be MOST important to include in a report to senior management?
A.
Changes in control design
B.
A decrease in the number of key controls
C.
Changes in control ownership
D.
An increase in residual risk
Full Access
Answer:
D
Explanation:
An IT risk and control self-assessment (RCSA) is a process that helps organizations identify and evaluate operational risks and assess the effectiveness of their control measures12. It is a structured approach that involves identifying, assessing, mitigating, and monitoring risks across all levels of an organization12.
A report to senior management is a document that summarizes and communicates the results and findings of the RCSA, and provides recommendations and action plans for improving the risk management and control processes34.
The most important aspect of an IT risk and control self-assessment to include in a report to senior management is an increase in residual risk, which is the risk remaining after risk treatment, and represents the exposure or potential impact of the risk on the organization’s objectives56.
An increase in residual risk is the most important aspect because it indicates the level of risk that the organization is willing to accept or tolerate, and the gap between the current and desired risk profile56.
An increase in residual risk is also the most important aspect because it requires the attention and decision of the senior management, who are responsible for defining the organization’s risk appetite, strategy, and criteria, and for ensuring that the residual risk is within the acceptable range56.
The other options are not the most important aspects, but rather possible components or outcomes of an IT risk and control self-assessment that may support or complement the report to senior management. For example:
Changes in control design are components of an IT risk and control self-assessment that involve modifying or updating the control measures to address the changes in the risk environment or the organization’s objectives56. However, changes in control design are not the most importantaspect because they do not measure or reflect the residual risk, which is the ultimate goal of the risk treatment56.
A decrease in the number of key controls is an outcome of an IT risk and control self-assessment that indicates the improvement or optimization of the control processes, and the reduction of the complexity or redundancy of the control measures56. However, a decrease in the number of key controls is not the most important aspect because it does not indicate or imply the residual risk, which may depend on other factors such as the effectiveness or efficiency of the controls56.
Changes in control ownership are components of an IT risk and control self-assessment that involve assigning or reassigning the responsibility and accountability for the control processes to the appropriate individuals or groups within the organization56. However,changes in control ownership are not the most important aspect because they do not affect or determine the residual risk, which is independent of the control owners56. References =
1: Risk and control self-assessment - KPMG Global1
2: Control Self Assessments - PwC2
3: How-To Guide: Implementing Risk Control Self-Assessment Steps4
4: RISK MANAGEMENT SELF-ASSESSMENT TEMPLATE - Smartsheet5
5: Risk IT Framework, ISACA, 2009
6: IT Risk Management Framework, University of Toronto, 2017
Question # 84
During a risk assessment of a financial institution, a risk practitioner discovers that tellers can initiate and approve transactions of significant value. This team is also responsible for ensuring transactions are recorded and balances are reconciled by the end of the day. Which of the following is the risk practitioner ' s BEST recommendation to mitigate the associated risk?
A.
Implement continuous monitoring.
B.
Require a second level of approval.
C.
Implement separation of duties.
D.
Require a code of ethics.
Full Access
Answer:
C
Question # 85
Which of the following is the BEST indication of the effectiveness of a business continuity program?
A.
Business continuity tests are performed successfully and issues are addressed.
B.
Business impact analyses are reviewed and updated in a timely manner.
C.
Business continuity and disaster recovery plans are regularly updated.
D.
Business units are familiar with the business continuity plans and process.
Full Access
Answer:
A
Explanation:
According to the Section 4: Quiz 40 - Business Continuity Plan Flashcards, the best indication of the effectiveness of a business continuity program is the successful performance of business continuity tests and the resolution of any issues that arise. Business continuity tests are exercises that simulate various scenarios of disruption or disaster and evaluate the organization’s ability to recover and resume its critical functions. Business continuity tests can help to validate the assumptions, objectives, and strategies of the business continuity program, as well as to identify and address any gaps, weaknesses, or errors in the business continuity and disaster recovery plans. By performing business continuity tests regularly and effectively, the organization can ensure that its business continuity program is aligned with its needs andexpectations, and that it can cope with any potential crisis. References = Section 4: Quiz 40 - Business Continuity Plan Flashcards
Question # 86
Which of the following is the BEST approach to use when creating a comprehensive set of IT risk scenarios?
A.
Derive scenarios from IT risk policies and standards.
B.
Map scenarios to a recognized risk management framework.
C.
Gather scenarios from senior management.
D.
Benchmark scenarios against industry peers.
Full Access
Answer:
B
Explanation:
IT risk scenarios are the descriptions or representations of the possible or hypothetical situations or events that may cause or result in an IT risk for the organization. IT risk scenarios usually consist of three elements: a threat or source of harm, a vulnerability or weakness, and an impact or consequence.
The best approach to use when creating a comprehensive set of IT risk scenarios is to map scenarios to a recognized risk management framework, which is an established or recognized model or standard that provides the principles, guidelines, and best practices for the organization’s IT risk management function. Mapping scenarios to a recognized risk management framework can help the organization to create a comprehensive set of IT risk scenarios by providing the following benefits:
It can ensure that the IT risk scenarios are relevant, appropriate, and proportional to the organization’s IT objectives and needs, and that they support the organization’s IT strategy and culture.
It can ensure that the IT risk scenarios are consistent and compatible with the organization’s IT governance, risk management, and control functions, and that they reflect the organization’s IT risk appetite and tolerance.
It can provide useful references and benchmarks for the identification, analysis, evaluation, and communication of the IT risk scenarios, and for the alignment and integration of the IT risk scenarios with the organization’s IT risk policies and standards.
The other options are not the best approaches to use when creating a comprehensive set of IT risk scenarios, because they do not provide the same level of detail and insight that mapping scenarios to a recognized risk management framework provides, and they may not be specific or applicable to the organization’s IT objectives and needs.
Deriving scenarios from IT risk policies and standards means creating or generating the IT risk scenarios based on the rules or guidelines that define and describe the organization’s IT risk management function, and that specify the expectations and requirements for the organization’s IT risk management function. Deriving scenarios from IT risk policies and standards can help the organization to create a consistent and compliant set of IT risk scenarios, but it is not the best approach, because it may not cover all the relevant or significant IT risks that may affect the organization, and it may not support the organization’s IT strategy and culture.
Gathering scenarios from senior management means collecting or obtaining the IT risk scenarios from the senior management or executives that oversee or direct the organization’s IT activities or functions. Gathering scenarios from senior management can help the organization to create a high-level and strategic set of IT risk scenarios, but it is not the best approach, because it may not reflect the operational or technical aspects of the IT risks, and it may not involve the input or feedback from the other stakeholders or parties that are involved or responsible for the IT activities or functions.
Benchmarking scenarios against industry peers means comparing and contrasting the IT risk scenarios with those of other organizations or industry standards, and identifying the strengths, weaknesses, opportunities, or threats that may affect the organization’s IT objectives oroperations. Benchmarking scenarios against industry peers can help the organization to create a competitive and innovative set of IT risk scenarios, but it is not the best approach, because it may not be relevant or appropriate for the organization’s IT objectives and needs, and it may not comply with the organization’s IT policies and standards. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 199
CRISC Practice Quiz and Exam Prep
Question # 87
Which of the following is MOST important to consider before determining a response to a vulnerability?
A.
The likelihood and impact of threat events
B.
The cost to implement the risk response
C.
Lack of data to measure threat events
D.
Monetary value of the asset
Full Access
Answer:
C
Explanation:
 A vulnerability is a weakness or flaw in the IT system or environment that could be exploited by a threat. A threat event is an occurrence or action that exploits a vulnerability and causes harm or damage to the IT system or environment. The lack of data to measure threat events is the most important factor, because it may affect the accuracy and reliability of the risk assessment and evaluation, and consequently, the risk response and strategy. The lack of data to measure threat events may also create challenges or risks for the organization, such as compliance, legal, reputational, or operational risks, or conflicts or inconsistencies with the organization’s risk appetite, risk objectives, or risk policies. The other options are not as important as the lack of data to measure threat events, although they may also influence the risk response and strategy. The likelihood and impact of threat events, the cost to implement the risk response, and the monetary value of the asset are all factors that could affect the feasibility and sustainability of the risk response and strategy, but they do not necessarily affect the validity and quality of the risk assessment and evaluation
Question # 88
An organization has detected unauthorized logins to its client database servers. Which of the following should be of GREATEST concern?
A.
Potential increase in regulatory scrutiny
B.
Potential system downtime
C.
Potential theft of personal information
D.
Potential legal risk
Full Access
Answer:
C
Explanation:
Potential theft of personal information should be of greatest concern for an organization that has detected unauthorized logins to its client database servers, as it poses a serious threat to theconfidentiality, integrity, and availability of the client data and the reputation and trust of the organization. Potential theft of personal information is a scenario that involves the unauthorized access, disclosure, or use of the client data by malicious actors, such as hackers, competitors, or insiders. Potential theft of personal information can have significant impacts and consequences for the organization and its clients, such as:
It can compromise the privacy and security of the client data, and expose the clients to identity theft, fraud, or blackmail.
It can violate the legal and regulatory obligations and requirements of the organization, such as the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), or the Payment Card Industry Data Security Standard (PCI DSS), and result in fines, penalties, or lawsuits.
It can damage the reputation and credibility of the organization, and erode the confidence and loyalty of the clients, and lead to loss of business or market share.
The other options are not the greatest concerns for an organization that has detected unauthorized logins to its client database servers. Potential increase in regulatory scrutiny is a possibleconsequence of the unauthorized logins, as it may trigger audits, investigations, or sanctions by the relevant authorities, but it is not the most critical or immediate concern. Potential system downtime is a possible consequence of the unauthorized logins, as it may disrupt or degrade the performance or availability of the database servers or the applications that depend on them, but it is not the most severe or lasting concern. Potential legal risk is a possible consequence of the unauthorized logins, as it may expose the organization to litigation or liability claims by the affected clients or parties, but it is not the most direct or urgent concern. References = Data Breach Response: A Guide for Business - Federal Trade Commission, IT Risk Resources | ISACA, How to Prevent Unauthorized Access to Your Database - ScaleGrid
Question # 89
Which of the following is MOST important for successful incident response?
A.
The quantity of data logged by the attack control tools
B.
Blocking the attack route immediately
C.
The ability to trace the source of the attack
D.
The timeliness of attack recognition
Full Access
Answer:
D
Explanation:
The most important factor for successful incident response is the timeliness of attack recognition. Incident response is the process of detecting, analyzing, containing, eradicating, recovering, and reporting on security incidents that could affect the organization’s IT systems or data. The timeliness of attack recognition is the speed and accuracy with which the organization can identify and confirm that an attack has occurred or is in progress. The timeliness of attack recognition is crucial for successful incident response, as it affects the ability and effectiveness of the organization to respond to and mitigate the attack, and to minimize the damage and impact of the attack. The other options are not as important as the timeliness of attack recognition, although they may also contribute to or influence the incident response. The quantity of data logged by the attack control tools, the ability to trace the source of the attack, and the blocking of the attack route immediately are all factors that could help or hinder the incident response, but they are not the most important factor for successful incident response. References = CISA Review Manual, 27th Edition, Chapter 5, Section 5.4.1, page 5-32.
Question # 90
During a routine check, a system administrator identifies unusual activity indicating an intruder within a firewall. Which of the following controls has MOST likely been compromised?
A.
Data validation
B.
Identification
C.
Authentication
D.
Data integrity
Full Access
Answer:
C
Explanation:
Authentication is a control that verifies the identity of a user or a system that tries to access a computer system or network. Authentication can be based on something the user or system knows (such as a password or a PIN), something the user or system has (such as a token or asmart card), or something the user or system is (such as a fingerprint or a retina scan). Authentication is a crucial control for preventing unauthorized or malicious access to a system or network, as well as for ensuring the accountability and traceability of the actions performed by the user or system. If the authentication control is compromised, it means that the user or system can bypass or break the verification process and gain access to the system or network without being identified or authorized. This can expose the system or network to various threats, such as data theft, data corruption, data leakage, or denial of service. Therefore, the authentication control has most likely been compromised if a system administrator identifies unusual activity indicating an intruder within a firewall. A firewall is a device or a software that monitors and filters the incoming and outgoing network traffic based on predefined rules and policies. A firewall can help to protect the system or network from external or internal attacks by blocking or allowing the traffic based on the source, destination, protocol, or content. However, a firewall cannot prevent an intruder from accessing the system or network if the intruder has already authenticated or impersonated a legitimate user or system. The other options are not the most likely controls to be compromised if a system administrator identifies unusual activity indicating an intruder within a firewall, although they may be affected or related. Data validation is a control that checks the accuracy, completeness, and quality of the data that is entered, processed,or stored by a system or anetwork. Data validation can help to prevent or detect data errors, anomalies, or inconsistencies that may affect the performance, functionality, or reliability of the system or network. However, data validation does not prevent or detect unauthorized or malicious access to the system or network, as it only focuses on the data, not the user or system. Identification is a control that assigns a unique identifier to a user or a system that tries to access a computer system or network. Identification can be based on a username, an email address, a phone number, or a certificate. Identification is a necessary but not sufficient control for preventing unauthorized or malicious access to a system or network, as it only declares who or what the user or system is, but does not prove it. Identification needs to be combined with authentication to verify the identity of the user or system. Data integrity is a control that ensures that the data is accurate, consistent, and complete throughout its lifecycle. Data integrity can be achieved by implementing various controls, such as encryption, hashing, checksum, digital signature, or backup. Data integrity can help to protect the data from unauthorized or accidental modification, deletion, or corruption that may affect the value, meaning, or usability of the data. However, data integrity does not prevent or detect unauthorized or malicious access to the system or network, as it only protects the data, not the user or system. References = CRISC Review Manual, pages 164-1651; CRISC Review Questions, Answers & Explanations Manual, page 952; What is Authentication? - Definition from Techopedia3; What is a Firewall? - Definition from Techopedia4
Question # 91
A business unit has decided to accept the risk of implementing an off-the-shelf, commercial software package that uses weak password controls. The BEST course of action would be to:
A.
obtain management approval for policy exception.
B.
develop an improved password software routine.
C.
select another application with strong password controls.
D.
continue the implementation with no changes.
Full Access
Answer:
A
Explanation:
 A policy exception is a deviation from the established policies, standards, or procedures of the enterprise, such as the information security policy. A policy exception may be granted by the management when there is a valid business reason or justification for the deviation, and when the risk associated with the deviation is acceptable or mitigated. The best course of action when a business unit has decided to accept the risk of implementing an off-the-shelf, commercialsoftware package that uses weak password controls is to obtain management approval for policy exception. This will ensure that the business unit is aware of the implications and consequences of the policy exception, and that the management agrees with the risk acceptance and approves the policy exception. The other options are not the best course of action, as they involve different risk response strategies or outcomes:
Develop an improved password software routine means that the business unit modifies or enhances the password controls of the software package, such as by increasing the password length, complexity, or expiration. This may not be a feasible or effective way to address the risk of weak password controls, as it may violate the terms and conditions of the software vendor, or may not be compatible or consistent with the software package.
Select another application with strong password controls means that the business unit replaces the software package with another application that has better password controls, such as by using encryption, authentication, or authorization. This may not be a desirable or efficient way to address the risk of weak password controls, as it may incur additional costs, delays, or complexities, or may not meet the business requirements or expectations of the business unit.
Continue the implementation with no changes means that the business unit proceeds with the software package without any modifications or improvements to the password controls, or without any approval or documentation of the policy exception. This may not be a responsible or ethical way to address the risk of weak password controls, as it may expose the enterprise to legal, financial, or reputational risks, or may compromise the security or compliance of the enterprise. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.4.1.1, pp. 121-122.
Question # 92
An organization uses an automated vulnerability scanner to identify potential vulnerabilities on various enterprise systems. Who is accountable for ensuring the vulnerabilities are mitigated?
A.
Data owners
B.
Information security manager
C.
System administrators
D.
System owners
Full Access
Answer:
D
Explanation:
System ownershold ultimate accountability for managing risks associated with their systems, including vulnerability mitigation.
ISACA CRISC defines:
“The system owner is responsible for ensuring that security controls are implemented and that vulnerabilities identified in their systems are addressed.â€
System administrators perform mitigation activities, but accountability (oversight and confirmation) remains with thesystem owner.
A: Data owners focus on data classification.
B: InfoSec managers oversee policy, not execution.
C: Admins implement controls but don’t own the risk.
Dis correct becauseownership equates to accountability.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Roles and Responsibilities in Risk Management.
Question # 93
The risk associated with a high-risk vulnerability in an application is owned by the:
A.
security department.
B.
business unit
C.
vendor.
D.
IT department.
Full Access
Answer:
B
Explanation:
A high-risk vulnerability in an application is a system flaw or weakness in the application’s code that can be exploited by a malicious actor, potentially leading to a security breach. The risk associated with a high-risk vulnerability in an application is the possibility and impact of such a breach occurring. The risk owner of a high-risk vulnerability in an application is the person or entity who has the authority and responsibility for managing the risk. The risk owner should be able to define the risk appetite, assess the risk level, select and implement the risk response, monitor and report the risk status, and ensure the risk alignment with the business objectives and strategy. The risk owner of a high-risk vulnerability in an application is the business unit, which is the organizational unit that operates the application and derives value from it. The businessunit understands the business needs and expectations of the application, and the potential consequences of a security breach. The business unit also has the resources and incentives to address the risk effectively and efficiently. Therefore, the business unit is the most appropriate risk owner of a high-risk vulnerability in an application. References = Why Assigning a Risk Owner is Important and How to Do It Right, CRISC 351-400 topic3, Foundations of Project Management : Week 2.
Question # 94
Which of the following is MOST important to ensure before using risk reports in decision making?
A.
Root cause analysis is included.
B.
Risk analysis results are validated.
C.
Real-time risk information is provided.
D.
Quantitative risk data is provided.
Full Access
Answer:
B
Explanation:
Validation of risk analysis results ensures the data is accurate, reliable, and can be trusted for making informed decisions. It minimizes the risk of acting on flawed insights.
[Reference:CRISC Manual – Domain 2: Risk Assessment, Slide 162-164, , , , ]
Question # 95
An organization has determined that risk is not being adequately tracked and
managed due to a distributed operating model. Which of the following is the
BEST way to address this issue?
A.
Increase the frequency of risk assessments.
B.
Revalidate the organization ' s risk appetite
C.
Create a centralized portfolio of risk scenarios.
D.
Create dashboards for risk metrics.
Full Access
Answer:
C
Question # 96
An organization maintains independent departmental risk registers that are not automatically aggregated. Which of the following is the GREATEST concern?
A.
Management may be unable to accurately evaluate the risk profile.
B.
Resources may be inefficiently allocated.
C.
The same risk factor may be identified in multiple areas.
D.
Multiple risk treatment efforts may be initiated to treat a given risk.
Full Access
Answer:
A
Explanation:
The greatest concern of maintaining independent departmental risk registers that are not automatically aggregated is that management may be unable to accurately evaluate the risk profile. The risk profile is the overall view of the risks that the organization faces and their impact on the organization’s objectives. It helps management to prioritize and allocate resources for risk management and to align the risk appetite and strategy. If the departmental risk registers are not aggregated, management may not have a complete and consistent picture of the risks across the organization. They may miss some important risks, overestimate or underestimate some risks, or have conflicting or redundant risk information. This may lead to poor risk management decisions and outcomes. The other options are also concerns, but they are not ascritical as the inability to evaluate the risk profile. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.2: IT Risk Analysis, page 63.
Question # 97
Which of the following is the GREATEST risk of relying on artificial intelligence (Al) within heuristic security systems?
A.
Al may result in less reliance on human intervention.
B.
Malicious activity may inadvertently be classified as normal during baselining.
C.
Risk assessments of heuristic security systems are more difficult.
D.
Predefined patterns of malicious activity may quickly become outdated.
Full Access
Answer:
B
Explanation:
ï‚· AI in Heuristic Security Systems:
Heuristic security systems use artificial intelligence (AI) to identify and respond to potential threats by learning from data patterns and behaviors.
ï‚· Risk of Misclassification:
During the baselining process, AI systems establish what is considered normal behavior. If malicious activity is present during this period, it may be incorrectly classified as normal.
This misclassification can lead to undetected security breaches, as the system will not recognize these activities as threats in the future.
ï‚· Impact of Misclassification:
Misclassified malicious activities can lead to significant security risks, allowing attackers to operate undetected within the system.
It undermines the effectiveness of the heuristic system, reducing its ability to protect the organization from real threats.
ï‚· Comparing Other Risks:
Less Reliance on Human Intervention:This is a general concern but does not directly impact the accuracy of threat detection.
Difficulty in Risk Assessments:While a challenge, it is not the greatest risk compared to misclassification of malicious activity.
Outdated Patterns:While a concern, the primary risk lies in initial misclassification during baselining.
ï‚· References:
The CRISC Review Manual discusses the challenges of AI in security systems, particularly the risk of misclassification during the learning phase (CRISC Review Manual, Chapter 4: Information Technology and Security, Section 4.7.4 Artificial Intelligence) .
Question # 98
An IT risk practitioner ' s report includes a treatment plan and projected risk ratings if recommendations are implemented. Once corrective actions are taken by the system owner, which of the following types of risk will the projected risk become?
A.
Control
B.
Inherent
C.
Residual
D.
Compliance
Full Access
Answer:
C
Explanation:
The correct answer isCbecause once corrective actions are implemented, the remaining projected risk becomesresidual risk. Residual risk is the exposure that remains after controls or treatment actions have been applied.
The other options are incorrect:
A. Controlis not a type of risk in this context.
B. Inherentrisk exists before controls are implemented.
D. Compliancerisk is a category of risk, not the remaining level after treatment.
Exact Extracts supporting the answer:
“Residual risk is best reflected as risk remaining after the implementation of new or enhanced controls.â€
“The primary objective of a risk management program is to maintain residual risk at an acceptable level.â€
“Acceptable risk for an enterprise is achieved when residual risk is within tolerance levels.â€
“The risk most likely to be reduced to achieve acceptable risk is residual risk.â€
These extracts directly show that once corrective actions are taken, the projected remaining risk isresidual risk.
===========
Question # 99
Of the following, who is responsible for approval when a change in an application system is ready for release to production?
A.
Information security officer
B.
IT risk manager
C.
Business owner
D.
Chief risk officer (CRO)
Full Access
Answer:
C
Explanation:
 The business owner is the person who is responsible for approval when a change in an application system is ready for release to production. The business owner is the person who has the authority and accountability for the business process or function that is supported by the application system. The business owner should approve the change to ensure that it meets the business requirements, objectives, and expectations, and that it does not introduce any adverse impacts or risks to the business operations. The information security officer, the IT risk manager, and the chief risk officer (CRO) are not responsible for the approval of the change, although they may provide input, feedback, or oversight. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.1, page 3-32.
Question # 100
A.
To gain stakeholder support for the implementation of controls
B.
To address multiple risk scenarios mitigated by technical controls
C.
To comply with industry best practices by balancing multiple types of controls
D.
To improve the effectiveness of controls that mitigate risk
Full Access
Answer:
D
Explanation:
Administrative controls complement technical controls to enhance the overall effectiveness of risk mitigation. While technical controls implement the specific security mechanisms, administrative controls such as policies, procedures, and training ensure consistent and correct use of these technical controls, increasing their effectiveness in mitigating risk. This layered approach ensures that control measures are reinforced and integrated within the enterprise’s risk management strategy.
Question # 101
Which of the following should be done FIRST when information is no longer required to support business objectives?
A.
Archive the information to a backup database.
B.
Protect the information according to the classification policy.
C.
Assess the information against the retention policy.
D.
Securely and permanently erase the information
Full Access
Answer:
C
Explanation:
A retention policy is a set of rules and guidelines that define how long and under what conditions the information should be kept or disposed of by the organization, based on its value, sensitivity, and legal or regulatory requirements.
When information is no longer required to support business objectives, the first thing that should be done is to assess the information against the retention policy. This means that the information should be reviewed and evaluated to determine if it should be retained or deleted, and for how long and by whom.
Assessing the information against the retention policy helps to ensure that the information is managed and disposed of in a consistent and compliant manner, that the information is protected from unauthorized access, use, disclosure, modification, or destruction, and that the information is available for future reference or audit purposes if needed.
The other options are not the first things that should be done when information is no longer required to support business objectives. They are either secondary or not essential for information management.
The references for this answer are:
Risk IT Framework, page 28
Information Technology & Security, page 22
Risk Scenarios Starter Pack, page 20
Question # 102
A systems interruption has been traced to a personal USB device plugged into the corporate network by an IT employee who bypassed internal control procedures. Of the following, who should be accountable?
A.
Business continuity manager (BCM)
B.
Human resources manager (HRM)
C.
Chief risk officer (CRO)
D.
Chief information officer (CIO)
Full Access
Answer:
D
Explanation:
A systems interruption caused by a personal USB device plugged into the corporate network by an IT employee who bypassed internal control procedures is a serious breach of information security and IT risk management. The person who should be accountable for this incident is the chief information officer (CIO), who is responsible for overseeing the IT function and ensuring compliance with IT policies and standards. The CIO should also ensure that appropriate corrective and preventive actions are taken to prevent such incidents from recurring and to mitigate the impact of the systems interruption on the business operations and objectives. The CIO should also report the incident to the senior management and the board of directors, and communicate with the relevant stakeholders about the incident and the actions taken. References = Risk IT Framework, ISACA, 2022, p. 181
Question # 103
IT management has deployed a major update to reduce the risk of system compromise. What is the BEST way to validate the effectiveness of this control?
A.
Conduct social engineering testing.
B.
Perform penetration testing.
C.
Run vulnerability scans.
D.
Review mean time to apply critical patches.
Full Access
Answer:
B
Explanation:
The correct answer is B because penetration testing validates whether the implemented control actually resists realistic compromise attempts. The uploaded CRISC notes state that penetration testing offers the greatest level of assurance regarding the effectiveness of implemented security controls and that penetration testing is the best way to ensure network security against external attacks.
ISACA also states that control testing demonstrates whether controls are mitigating risk as intended, including assessing network security and testing controls designed to prevent or detect unauthorized access, data breaches, and system failures. ISACA further explains that penetration testing evaluates vulnerabilities and supports effective risk response decisions.
C, vulnerability scanning, is useful for identifying known vulnerabilities, and it may be appropriate for validating a patching program. However, the question asks for the BEST way to validate effectiveness of a major update intended to reduce system compromise, making penetration testing stronger. A is too narrow because social engineering tests people rather than the technical control. D is only a metric and does not validate whether the update reduced compromise risk.
Question # 104
Which of the following would be a risk practitioner ' s MOST important action upon learning that an IT control has failed?
A.
Implement a replacement control.
B.
Adjust residual risk rating.
C.
Escalate to senior management.
D.
Review compensating controls.
Full Access
Answer:
D
Explanation:
Upon discovering that an IT control has failed, the risk practitioner ' s most important action is to review compensating controls. This involves assessing whether other existing controls can mitigate the risk associated with the failed control. Evaluating compensating controls helps determine the immediate impact of the control failure and guides decisions on necessary remediation steps.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 3: Risk Response and Reporting, Section: Control Monitoring and Reporting., , , , , , , ]
Question # 105
Which of the following is the BEST evidence that a user account has been properly authorized?
A.
An email from the user accepting the account
B.
Notification from human resources that the account is active
C.
User privileges matching the request form
D.
Formal approval of the account by the user ' s manager
Full Access
Answer:
C
Explanation:
 According to the CRISC Review Manual, formal approval of the account by the user’s manager is the best evidence that a user account has been properly authorized, because it ensures that the user’s role and access rights are consistent with the business needs and the principle of least privilege. The user’s manager is responsible for verifying the user’s identity, job function, and access requirements, and for approving or rejecting the account request. The other options are not the best evidence of proper authorization, because they do not involve the user’s manager’s approval. An email from the user accepting the account is a confirmation of the account creation, but it does not indicate that the account was authorized by the user’s manager. Notification from human resources that the account is active is an administrative process that does not verify the user’s access rights and role. User privileges matching the request form is a verification of the account configuration, but it does not ensure that the request form was approved by the user’s manager. References = CRISC Review Manual, 7th Edition, Chapter 4, Section 4.1.2, page 163.
Question # 106
Which of the following is the BEST approach to mitigate the risk associated with outsourcing network management to an external vendor who will have access to sensitive information assets?
A.
Prepare a skills matrix to illustrate tasks and required expertise.
B.
Require periodic security assessments of the vendor within the contract.
C.
Perform due diligence to enable holistic assessment of the vendor.
D.
Plan a phased approach for the transition of processes to the vendor.
Full Access
Answer:
C
Explanation:
Performing due diligence is the most effective initial step in mitigating risks associated with outsourcing. This comprehensive assessment evaluates the vendor ' s capabilities, security posture, compliance with regulations, and overall suitability for handling sensitive information assets. It ensures that potential risks are identified and addressed before entering into a contractual agreement.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 2: IT Risk Assessment, Section: Third-Party Risk Management., , , , , , , ]
Question # 107
In response to the threat of ransomware, an organization has implemented cybersecurity awareness activities. The risk practitioner ' s BEST recommendation to further reduce the impact of ransomware attacks would be to implement:
A.
two-factor authentication.
B.
continuous data backup controls.
C.
encryption for data at rest.
D.
encryption for data in motion.
Full Access
Answer:
B
Explanation:
Continuous data backup controls are the best recommendation to further reduce the impact of ransomware attacks, as they enable the organization to restore the data that has been encrypted or deleted by the ransomware without paying the ransom or losing the data. Continuous data backup controls ensure that the data is regularly and automatically backed up to a secure and separate location, and that the backup data is tested and verified for integrity and availability. Two-factor authentication, encryption for data at rest, and encryption for data in motion are not the best recommendations to further reduce the impact of ransomware attacks, as they do not address the recovery of the data that has been compromised by the ransomware. These controls may help to prevent or mitigate ransomware attacks, butnot to reduce their impact. References = CRISC by Isaca Actual Free Exam Q & As, question 207; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 207.
Question # 108
Which of the following BEST enables the selection of appropriate risk treatment in the event of a disaster?
A.
Business impact analysis (BIA)
B.
Risk scenario analysis
C.
Failover procedures
D.
Risk treatment plan
Full Access
Answer:
A
Explanation:
Thebusiness impact analysis (BIA)identifies critical services, acceptable downtime limits, and the business consequences of disruptions. CRISC emphasizes that the BIA is the foundation for deciding risk treatment strategies because it defines what must be restored first and to what level. Scenario analysis identifies risks but does not determine business priorities. Failover procedures are themselves a treatment, not a method for selecting treatments. A risk treatment plan documents chosen actions but depends entirely on the BIA to inform those decisions. Therefore, the BIA is the key input enabling proper treatment selection during disasters.
[Reference:CRISC Review Manual – Risk Response and Mitigation (BIA-driven decision making)., , , , ]
Question # 109
Which of the following is the BEST way to support communication of emerging risk?
A.
Update residual risk levels to reflect the expected risk impact.
B.
Adjust inherent risk levels upward.
C.
Include it on the next enterprise risk committee agenda.
D.
Include it in the risk register for ongoing monitoring.
Full Access
Answer:
C
Explanation:
 Emerging risk is a risk that is new or evolving, and has the potential to significantly affect the enterprise’s objectives, performance, or reputation. Emerging risk can arise from changes in the internal or external environment, such as technological innovations, regulatory developments, or social trends. The best way to support communication of emerging risk is to include it on the next enterprise risk committee agenda. The enterprise risk committee is a group of senior executives who oversee the enterprise-wide risk management program, and provide guidance and direction to the risk owners and practitioners. By including the emerging risk on the agenda, the risk practitioner can ensure that the enterprise risk committee is aware of the risk, its causes, impacts, and likelihood, and can decide on the appropriate risk response strategy and actions. The other options are not the best way to support communication of emerging risk, as they involve different aspects of the risk management process:
Update residual risk levels to reflect the expected risk impact means that the risk practitioner adjusts the risk levels after considering the existing or planned risk responses. This may not befeasible or accurate for emerging risk, as the risk responses may not be defined or implemented yet, or may not be effective for the new or evolving risk.
Adjust inherent risk levels upward means that the risk practitioner increases the risk levels before considering any risk responses. This may not reflect the true nature or magnitude of the emerging risk, as the inherent risk levels are based on the assumptions and estimates of the risk practitioner, and may not account for the uncertainties or complexities of the emerging risk.
Include it in the risk register for ongoing monitoring means that the risk practitioner records and tracks the emerging risk, its causes, impacts, likelihood, responses, and owners. This is an important step in the risk management process, but it does not necessarily support communication ofthe emerging risk, as the risk register may not be accessible or visible to all the relevant stakeholders, or may not be updated or reviewed frequently enough to capture the changes in the emerging risk. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.2.2, pp. 21-22.
Question # 110
Which of the following is MOST helpful in identifying loss magnitude during risk analysis of a new system?
A.
Recovery time objective (RTO)
B.
Cost-benefit analysis
C.
Business impact analysis (BIA)
D.
Cyber insurance coverage
Full Access
Answer:
C
Explanation:
Business impact analysis (BIA) is the most helpful tool in identifying loss magnitude during risk analysis of a new system, as it involves estimating the potential financial and operational losses resulting from the disruption or degradation of the system. Recovery time objective (RTO), cost-benefit analysis, and cyber insurance coverage are not the most helpful tools, as they are more related to the recovery, evaluation, andtransfer of the risk, respectively, rather than the identification of the loss magnitude. References = CRISC Review Manual, 7th Edition, page 108.
Question # 111
A web-based service provider with a low risk appetite for system outages is reviewing its current risk profile for online security. Which of the following observations would be MOST relevant to escalate to senior management?
A.
An increase in attempted distributed denial of service (DDoS) attacks
B.
An increase in attempted website phishing attacks
C.
A decrease in achievement of service level agreements (SLAs)
D.
A decrease in remediated web security vulnerabilities
Full Access
Answer:
A
Explanation:
A web-based service provider is an organization that offers online services or applications to its customers or users, such as e-commerce, social media, cloud computing, etc. A web-based service provider depends on the availability, reliability, and security of its web servers, networks, and systems to deliver its services or applications.
A low risk appetite for system outages means that the organization is not willing to accept a high level or frequency of system outages, which are interruptions or disruptions in the normal operation or functionality of the web servers, networks, or systems. System outages can cause customer dissatisfaction, revenue loss, reputation damage, or legal liability for the web-based service provider.
A current risk profile for online security is the current state or condition of the online security risks that may affect the web-based service provider’s objectives and operations. It includes the identification, analysis, and evaluation of the online security risks, and the prioritization and response to them based on their significance and urgency.
The most relevant observation to escalate to senior management is an increase in attempted distributed denial of service (DDoS) attacks, which are malicious attacks that aim to overwhelm or overload the web servers, networks, or systems with a large volume or frequency of requests or traffic, and prevent them from responding to legitimate requests or traffic. An increase in attempted DDoS attacks indicates a high likelihood and impact of system outages, and a high level of threat or vulnerability for the web-based service provider’s online security. Escalating this observation to senior management can help them to understand the severity and urgency of the risk, and to decide on the appropriate risk response and allocation of resources.
The other options are not the most relevant observations to escalate to senior management, because they do not indicate a high likelihood or impact of system outages, and they may not be relevant or actionable for senior management.
An increase in attempted website phishing attacks means an increase in malicious attempts to deceive or trick the web-based service provider’s customers or users into providing their personal or financial information, such as usernames, passwords, credit card numbers, etc., by impersonating the web-based service provider’s website or email. An increase in attemptedwebsite phishing attacks indicates a high level of threat or vulnerability for the web-based service provider’s online security, but it may not directly cause system outages, unless thephishing attacks are used to compromise the web servers, networks, or systems. Escalating this observation to senior management may not be the most relevant, because it may not reflect the web-based service provider’s risk appetite for system outages, and it may not require senior management’s involvement or approval.
A decrease in achievement of service level agreements (SLAs) means a decrease in the extent or degree to which the web-based service provider meets or exceeds the agreed or expected standards or criteria for the quality, performance, or availability of its services or applications, as specified in the contracts or agreements with its customers or users. A decrease in achievement of SLAs indicates a low level of customer satisfaction, retention, or loyalty, and a low level of competitiveness or profitability for the web-based service provider. Escalating this observation to senior management may not be the most relevant, because it may not reflect the web-based service provider’s risk appetite for system outages, and it may not require senior management’s involvement or approval.
A decrease in remediated web security vulnerabilities means a decrease in the number or percentage of web security vulnerabilities that have been identified and resolved or mitigated by the web-based service provider. Web security vulnerabilities are weaknesses or flaws in the web servers, networks, or systems that can be exploited by malicious attackers to compromise or damage the web-based service provider’s online security. A decrease in remediated web security vulnerabilities indicates a low level of effectiveness or efficiency for the web-based service provider’s web security controls or processes. Escalating this observation to senior management may not be the most relevant, because it may not reflect the web-based service provider’s risk appetite for system outages, and it may not require senior management’s involvement or approval. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 161
CRISC Practice Quiz and Exam Prep
Question # 112
Which of the following would BEST mitigate the ongoing risk associated with operating system (OS) vulnerabilities?
A.
Temporarily mitigate the OS vulnerabilities
B.
Document and implement a patching process
C.
Evaluate permanent fixes such as patches and upgrades
D.
Identify the vulnerabilities and applicable OS patches
Full Access
Answer:
B
Explanation:
 The best way to mitigate the ongoing risk associated with operating system (OS) vulnerabilities is to document and implement a patching process. A patching process is a set of procedures and guidelines that define how to identify, evaluate, test, apply, and monitor patches for the OS. Patches are updates or fixes that address the known vulnerabilities or bugs in the OS. By documenting and implementing a patching process, the organization can ensure that the OS is regularly updated and protected from the potential exploits or attacks that may exploit the vulnerabilities. The other options are not as effective as documenting and implementing a patching process, as they are related to the temporary, partial, or reactive measures to deal with the OS vulnerabilities, not the proactive and continuous measures to prevent or reduce the OS vulnerabilities. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Question # 113
Which of the following should be initiated when a high number of noncompliant conditions are observed during review of a control procedure?
A.
Disciplinary action
B.
A control self-assessment
C.
A review of the awareness program
D.
Root cause analysis
Full Access
Answer:
D
Explanation:
A root cause analysis is a systematic process of identifying the underlying factors that caused the noncompliant conditions during the review of a control procedure. A root cause analysis can help to prevent the recurrence of the noncompliance, improve the effectiveness of the control procedure, and enhance the risk management process. A root cause analysis can be performed using various tools and techniques, such as the 5 whys, fishbone diagram, Pareto chart, or fault tree analysis. The other options are not as appropriate as a root cause analysis, because they do not address the source of the problem, but rather the symptoms or consequences of the noncompliance. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.3, page 130.
Question # 114
Which of the following is the MOST important consideration when determining whether to accept residual risk after security controls have been implemented on a critical system?
A.
Cost versus benefit of additional mitigating controls
B.
Annualized loss expectancy (ALE) for the system
C.
Frequency of business impact
D.
Cost of the Information control system
Full Access
Answer:
A
Explanation:
 Residual risk is the risk that remains after security controls have been implemented on a system. Residual risk can be accepted, transferred, avoided, or further mitigated. The most important consideration when deciding whether to accept residual risk is the cost versus benefit of additional mitigating controls. This means comparing the potential impact of the residual risk with the cost and effectiveness of implementing more controls to reduce it. If the cost of additional controls outweighs the benefit of reducing the residual risk, then it may be acceptableto accept the residual risk. However, if the benefit of additional controls exceeds the cost, then it may be advisable to implement more controls to lower the residual risk to an acceptable level. References = Risk and Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.4: Risk Response Selection, p. 156-157.
Question # 115
An assessment of information security controls has identified ineffective controls. Which of the following should be the risk practitioner ' s FIRST course of action?
A.
Determine whether the impact is outside the risk appetite.
B.
Request a formal acceptance of risk from senior management.
C.
Report the ineffective control for inclusion in the next audit report.
D.
Deploy a compensating control to address the identified deficiencies.
Full Access
Answer:
A
Explanation:
The risk practitioner’s first course of action when an assessment of information security controls has identified ineffective controls should be A. Determine whether the impact is outside the risk appetite1
According to the CRISC Review Manual, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite reflects the organization’s risk culture, strategy, and values2
When an assessment of information security controls has identified ineffective controls, it means that the controls are not providing the expected level of protection or assurance for the information assets or processes. This may result in increased exposure or vulnerability to threats, or reduced ability to achieve objectives. Therefore, the risk practitioner should first determine whether the impact of the ineffective controls is outside the risk appetite, as this would indicate the need for urgent action or escalation3
The other options are not the first course of action when an assessment of information security controls has identified ineffective controls, because:
•B. Requesting a formal acceptance of risk from senior management may be appropriate if the impact of the ineffective controls is within the risk appetite, and the organization decides to accept the risk as it is. However, this should not be the first course of action, as it may not address the root cause of the ineffective controls, or the potential consequences or opportunities for improvement4
•C. Reporting the ineffective control for inclusion in the next audit report may be part of the risk communication and reporting process, but it should not be the first course of action, as it may delay the resolution or mitigation of the issue, or the implementation of corrective actions. Moreover, the next audit report may not be timely or relevant for the decision-makers or stakeholders who need to be informed of the ineffective controls5
•D. Deploying a compensating control to address the identified deficiencies may be a possible risk response option, but it should not be the first course of action, as it may require further analysis, evaluation, and approval. Moreover, deploying a compensating control may not be the most effective or efficient solution, as it may introduce additional complexity, cost, or risk.
1: CRISC Review Questions, Answers & Explanations Database, Question ID: 100003 2: CRISC Review Manual, 7th Edition, page 28 3: CRISC Review Manual, 7th Edition, page 223 4: CRISC Review Manual, 7th Edition, page 224 5: CRISC Review Manual, 7th Edition, page 225 : CRISC Review Manual, 7th Edition, page 226
Question # 116
Which of the following should a risk practitioner review FIRST when evaluating risk events associated with the organization ' s data flow model?
A.
Results of data classification activities
B.
Recent changes to enterprise architecture (EA)
C.
High-level network diagrams
D.
Notes from interviews with the data owners
Full Access
Answer:
A
Question # 117
The MOST significant benefit of using a consistent risk ranking methodology across an organization is that it enables:
A.
allocation of available resources
B.
clear understanding of risk levels
C.
assignment of risk to the appropriate owners
D.
risk to be expressed in quantifiable terms
Full Access
Answer:
B
Explanation:
The most significant benefit of using a consistent risk ranking methodology across an organization is that it enables a clear understanding of risk levels, as this facilitates the comparison and prioritization of risks, the communication and reporting of risks, and the alignment of risk management with the enterprise’s objectives and strategy. A consistent risk ranking methodology is a set of criteria and scales that are used to measure and rate the likelihood and impact of risks, as well as other factors such as urgency, velocity, and persistence. A consistent risk ranking methodology ensures that the risk assessment results are objective, reliable, and comparable across different business units, processes, and projects. The other options are not the most significant benefits of using a consistent risk ranking methodology,although they may be secondary benefits or outcomes of doing so. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Assessment, page 97.
Question # 118
Which of the following activities would BEST contribute to promoting an organization-wide risk-aware culture?
A.
Performing a benchmark analysis and evaluating gaps
B.
Conducting risk assessments and implementing controls
C.
Communicating components of risk and their acceptable levels
D.
Participating in peer reviews and implementing best practices
Full Access
Answer:
C
Explanation:
A risk-aware culture is a culture that recognizes, understands, and values the importance of risk management in achieving the organization’s objectives and goals. A risk-aware culture is also a culture that supports and encourages the identification, assessment, response, and monitoring of risks across the organization, as well as the sharing and learning of risk information and best practices. One of the activities that would best contribute to promoting an organization-wide risk-aware culture is communicating components of risk and their acceptable levels. This is a technique to inform and educate the stakeholders and decision makers about the nature and scope of the risks that the organization faces, as well as the criteria and standards that the organization uses to measure and manage the risks. Communicating components of risk and their acceptable levels can help to increase the awareness and understanding of the risks and their impact on the organization’s performance and value, as well as to align the expectations and behaviors of the stakeholders and decision makers with the organization’s risk appetite and tolerance. Communicating components of risk and their acceptable levels can also help to foster a transparent and collaborative environment for risk management, where the stakeholders and decision makers can openly discuss and address the risks and their implications, as well as to provide and receive feedback and support. The other options are not the best activities to promote an organization-wide risk-aware culture, although they may be relevant and useful. Performing a benchmark analysis and evaluating gaps is a technique to compare and improve the organization’s risk management process and performance with the industry standards or best practices, as well as to identify and close the gaps or weaknesses in the organization’s risk management capabilities or maturity. However, this technique does not necessarily promote a risk-aware culture, as it focuses on the process and performance of risk management, not the attitude and behavior of risk management. Conducting risk assessments and implementing controls is a technique to identify and analyze the risks that the organization faces, as well as to select and execute the appropriate actions to address the risks, such as avoiding, transferring, mitigating, or accepting the risks. However, this technique does not directly promote a risk-aware culture, as it focuses on the actions and outcomes of risk management, not the values and beliefs of risk management. Participating in peer reviews and implementing best practices is a technique to evaluate and enhance the quality and effectiveness of the organization’s risk management activities anddeliverables, as well as to adopt and apply the proven and successful methods or solutions for risk management. However, this technique does not effectively promote a risk-aware culture, as it focuses on the improvement and optimization of risk management, not the communication and collaboration of risk management. References = CRISC Review Manual, pages 22-231; CRISC Review Questions, Answers & Explanations Manual, page 982; The 6 keyelements to creating and maintaining a good risk culture3; How to increase risk awareness - Project Management Institute4
Question # 119
IT disaster recovery point objectives (RPOs) should be based on the:
A.
maximum tolerable downtime.
B.
maximum tolerable loss of data.
C.
need of each business unit.
D.
type of business.
Full Access
Answer:
B
Explanation:
IT disaster recovery point objectives (RPOs) should be based on the:
B. maximum tolerable loss of data.
RPOs are determined by how much data loss an organization can withstand in the event of a disaster. It’s a measure of the maximum age of files that an organization must recover from backup storage for normal operations to resume after a disaster. Therefore, RPOs are directly related to the maximum tolerable loss of data.
Question # 120
When reviewing management ' s IT control self-assessments, a risk practitioner noted an ineffective control that links to several low residual risk scenarios. What should be the NEXT course of action?
A.
Assess management ' s risk tolerance.
B.
Recommend management accept the low-risk scenarios.
C.
Propose mitigating controls
D.
Re-evaluate the risk scenarios associated with the control
Full Access
Answer:
B
Explanation:
IT control self-assessments are techniques that involve identifying and evaluating the effectiveness and efficiency of the IT controls that are designed and implemented to mitigate the IT risks, by the managers and staff within the organization12.
An ineffective control is a control that does not achieve its intended objective or purpose, or does not operate as designed or expected34.
A low residual risk scenario is a situation or occurrence that has a low likelihood and impact of affecting the organization’s objectives, performance, or value creation, after considering the existing controls and their effectiveness56.
The next course of action when reviewing management’s IT control self-assessments and noting an ineffective control that links to several low residual risk scenarios is to recommend management accept the low-risk scenarios, which is a risk response strategy that involves acknowledging and tolerating the level of risk exposure, and not taking any further action to reduce or eliminate it78.
Recommending management accept the low-risk scenarios is the next course of action because it is the most cost-effective and reasonable option, given that the level of risk exposure is low andacceptable, and the cost and effort of implementing or improving the control may outweigh the potential benefits or value78.
Recommending management accept the low-risk scenarios is also the next course of action because it is consistent with the risk management process and objectives, which are to identifyand address the risks that may affect the achievement of the organization’s goals and the delivery of value to the stakeholders, and to optimize the balance between risk and reward78.
The other options are not the next course of action, but rather possible alternatives or steps that may be considered or followed in different circumstances or scenarios. For example:
Assessing management’s risk tolerance is a step that involves determining and communicating the acceptable or tolerable level of risk exposure for the organization or its business units, based on the organization’s risk appetite, criteria, and objectives78. However, this stepis not the next course of action because it is usually done before or during the risk assessment process, and not after noting an ineffective control that links to several low residual risk scenarios78.
Proposing mitigating controls is a course of action that involves suggesting or recommending additional or alternative controls that can reduce or eliminate the level of risk exposure, and improve the effectiveness and efficiency of the risk management process78. However, this course of action is not the next course of action because it is not necessary or appropriate for low residual risk scenarios, as the cost and effort of implementing or improving the controls may outweigh the potential benefits or value78.
Re-evaluating the risk scenarios associated with the control is a course of action that involves revising and updating the likelihood and impact of the risk scenarios, and the level of risk exposure or tolerance for the organization, based on the current or changed conditions or factors that influence the risk landscape78. However, this course of action is not the next course of action because it is not required or relevant for low residual risk scenarios, as the level of risk exposure is already low and acceptable, and the ineffective control does not significantly affect the risk assessment78. References =
1: Control Self Assessments - PwC1
2: Control self-assessment - Wikipedia2
3: Ineffective Controls: What They Are and How to Identify Them3
4: Ineffective Controls: What They Are and How to Identify Them4
5: Residual Risk - Definition and Examples5
6: Residual Risk: Definition, Formula & Management6
7: Risk IT Framework, ISACA, 2009
8: IT Risk Management Framework, University of Toronto, 2017
Question # 121
A chief risk officer (CRO) has asked to have the IT risk register integrated into the enterprise risk management (ERM) process. Which of the following will BEST facilitate the reporting of IT risk at the enterprise level?
A.
Aggregating the IT risk scenarios into a maturity benchmark value
B.
Using an IT risk heat map to depict likelihood and impact
C.
Using the same risk taxonomy across the organization
D.
Providing a summary of open IT risk-related audit findings
Full Access
Answer:
C
Explanation:
Using aconsistent risk taxonomyensures that IT risks can be aggregated and compared with enterprise-level risks in a meaningful way. ISACA emphasizes that standardized risk language and categories are critical to integrating IT risk with ERM processes.
===========
Question # 122
Which of the following has the MOST validity for conducting risk assessments?
A.
Internal control effectiveness measured through inference from external assessment
B.
Control effectiveness determined through subject matter expertise estimation
C.
Inferences of internal control effectiveness from peer reports
D.
Internal control effectiveness measured through direct testing
Full Access
Answer:
D
Explanation:
The correct answer isDbecauseinternal control effectiveness measured through direct testingprovides the most valid basis for conducting risk assessments. Direct testing produces objective evidence about whether controls are designed appropriately and operating effectively. It is stronger and more reliable than estimates, external inference, or peer-based assumptions because it evaluates the actual control environment of the organization.
The other options are less valid:
A. Internal control effectiveness measured through inference from external assessmentmay provide useful insight, but it is indirect and may not reflect the organization’s actual internal control performance.
B. Control effectiveness determined through subject matter expertise estimationcan support assessment, but it remains judgment-based rather than evidence-based.
C. Inferences of internal control effectiveness from peer reportsare indirect and may not be relevant to the organization’s own environment, systems, or risk exposure.
Exact Extracts supporting the answer:
“To best identify information systems control deficiencies gap analysis is used. It highlights the discrepancies between desired control objectives and actual control design and operational effectiveness.â€
“The MOST important criterion when reviewing information security controls is ensuring that the controls are effectively addressing risk.â€
“The BEST way to ensure that an information systems control is appropriate and effective is to verify that the risk associated with the control is mitigated.â€
“To determine control effectiveness it ' s essential to verify that the control meets the test results of intended objectives.â€
“Testing the control to ensure that the risk has been adequately mitigated is the best action to take once a new control has been implemented validating that the control effectively addresses the identified risk.â€
These extracts support that the most valid evidence of control effectiveness comes from actual verification and testing, not from assumptions or indirect sources. Therefore,direct testingprovides the strongest validity for risk assessments.
===========
Question # 123
An organization is participating in an industry benchmarking study that involves providing customer transaction records for analysis Which of the following is the MOST important control to ensure the privacy of customer information?
A.
Nondisclosure agreements (NDAs)
B.
Data anonymization
C.
Data cleansing
D.
Data encryption
Full Access
Answer:
B
Explanation:
Data anonymization is the most important control to ensure the privacy of customer information when participating in an industry benchmarking study that involves providing customer transaction records for analysis. Data anonymization is the process of removing or modifying personally identifiable information (PII) from data sets, such as names, addresses, phone numbers, email addresses, etc., so that the data cannot be traced back to specific individuals.Data anonymization protects the confidentiality and privacy of customers, while still allowing for meaningful analysis and comparison of data. Nondisclosure agreements (NDAs), data cleansing, and data encryption are also useful controls, but they do not eliminate the risk of data breaches or unauthorized access to PII. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-21.
Question # 124
Management has required information security awareness training to reduce the risk associated with credential compromise. What is the BEST way to assess the effectiveness of the training?
A.
Conduct social engineering testing.
B.
Audit security awareness training materials.
C.
Administer an end-of-training quiz.
D.
Perform a vulnerability assessment.
Full Access
Answer:
A
Explanation:
Conducting social engineering testing is the best way to assess the effectiveness of the security awareness training, as it helps to measure and evaluate the actual behavior and response of the employees to simulated real-world attacks that exploit human vulnerabilities. Social engineering testing is a type of security testing that involves performing authorized and ethical hacking activities on the employees to manipulate them into revealing sensitive information, such as credentials, or performing malicious actions, suchas clicking on a phishing link or opening a malicious attachment. Social engineering testing can help to assess the effectiveness of the security awareness training by providing the following benefits:
It tests the employees’ knowledge and skills in recognizing and resisting social engineering attacks, such as phishing, vishing, baiting, or impersonation.
It identifies and measures the strengths and weaknesses of the employees’ security awareness and behavior, and the impact and severity of their actions on the security posture and risk exposure of the organization.
It provides feedback and learning opportunities for the employees to improve their security awareness and behavior, and to reinforce the key concepts and practices taught in the training.
It communicates and reports the results and findings of the testing to the management and the stakeholders, and supports the development and implementation of corrective or preventive actions.
The other options are not the best ways to assess the effectiveness of the security awareness training. Auditing security awareness training materials is a good practice to ensure that the training content is accurate, relevant, and up-to-date, but it does not measure or evaluate the employees’ security awareness and behavior. Administering an end-of-training quiz is a useful method to test the employees’ comprehension and retention of the training content, but it does not reflect or simulate the employees’ security awareness and behavior in real-world situations. Performing a vulnerability assessment is an important step to identify and analyze the potential vulnerabilities in the systems and software, but it does not assess or address the human vulnerabilities or the employees’ security awareness and behavior. References = 3 ways to assess the effectiveness of security awareness training …, IT Risk Resources | ISACA, Measuring the Effectiveness of Security Awareness Training - Hut Six
Question # 125
A cloud service provider has completed upgrades to its cloud infrastructure to enhance service availability. Which of the following is the MOST important key risk indicator (KRI) for management to monitor?
A.
Peak demand on the cloud service during business hours
B.
Percentage of technology upgrades resulting in security breaches
C.
Number of incidents with downtime exceeding contract threshold
D.
Percentage of servers not patched per policy
Full Access
Answer:
C
Explanation:
Monitoring the number of incidents with downtime exceeding the contract threshold is a critical KRI for assessing the effectiveness of infrastructure upgrades aimed at enhancing service availability. This metric directly reflects the provider ' s ability to meet agreed-upon service levels and helps identify areas requiring further improvement.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 4: Information Technology and Security, Section: Key Risk Indicators., , , , , , , ]
Question # 126
Which of the following would be MOST helpful to a risk owner when making risk-aware decisions?
A.
Risk exposure expressed in business terms
B.
Recommendations for risk response options
C.
Resource requirements for risk responses
D.
List of business areas affected by the risk
Full Access
Answer:
A
Explanation:
Risk exposure is the potential loss or negative impact that may result from a risk. Expressing risk exposure in business terms means translating the technical or quantitative aspects of risk into meaningful and understandable information for the risk owner and other stakeholders. This canhelp the risk owner to make risk-aware decisions, as it can provide a clear and consistent basis for comparing and prioritizing risks, evaluating the cost-benefit of risk responses, and aligning the risk management strategy with the business objectives and value. The other options are not as helpful as risk exposure expressed in business terms, because they do not provide a comprehensive and relevant view of the risk, but rather focus on specific or partial aspects of the risk. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.1, page 45.
Question # 127
Which of the following is the PRIMARY purpose of analyzing control effectiveness during risk analysis?
A.
To enable a control cost-benefit analysis
B.
To evaluate the risk impact
C.
To determine the likelihood of occurrence
D.
To determine the current risk level
Full Access
Answer:
D
Explanation:
During risk analysis, CRISC distinguishes between inherent risk (without controls) and residual or current risk (with controls). Analyzingcontrol effectiveness—both in design and operation—is central to determining thecurrent risk level. Effective controls reduce either the likelihood of occurrence, the impact, or both. The assessment of their strength, coverage, and reliability allows the practitioner to adjust the initial inherent risk estimate down to a realistic residual risk figure and compare this to appetite and tolerance. Cost-benefit analysis of controls is a later step in risk response decision-making. Impact evaluation depends more on the nature of assets and processes than on controls. Likelihood is influenced by controls, but the primary purpose of control effectiveness analysis is to calculate the updated (residual) risk level, not just likelihood independently.
[Reference:CRISC Review Manual – Risk Assessment (control analysis and inherent vs residual risk)., ===========, ]
Question # 128
Which of the following is the MOST significant risk associated with using cloud computing for disaster recovery?
A.
Cloud vendor lock-in and dependency
B.
Lack of adequate incident management capabilities
C.
Use of multiple cloud access service brokers (CASBs)
D.
Availability issues with cloud storage solutions
Full Access
Answer:
A
Explanation:
In cloud-based disaster recovery, CRISC emphasizes that the most impactful strategic risk isvendor lock-in and dependency. When disaster recovery capabilities rely on a single cloud provider, organizations become fully dependent on that provider’s technology, APIs, and platform architecture. This dependency makes it difficult and costly to migrate to another provider, limits flexibility in recovery options, and increases exposure if the provider experiences outages or changes service terms. While availability issues, CASB usage, and incident management gaps are important, they do not present the same level of strategic long-term operational and resilience impact as vendor lock-in.
[Reference:CRISC Review Manual – IT Risk Assessment (third-party and cloud dependency risks)., ========================================, ]
Question # 129
Which of the following is the MOST critical element to maximize the potential for a successful security implementation?
A.
The organization ' s knowledge
B.
Ease of implementation
C.
The organization ' s culture
D.
industry-leading security tools
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual, the organization’s culture is the most critical element to maximize the potential for a successful security implementation, because it influences the behavior, attitude, and perception of the stakeholders towards security. The organization’s culture includes the values, beliefs, norms, and practices that are shared by the members of the organization. A positive and supportive culture can foster the awareness, commitment, and collaboration of the stakeholders in achieving the security objectives and complying with the security policies and standards. The other options are not the most critical elements, as they are less influential or less challenging than the organization’s culture. The organization’s knowledge is the collective understanding and expertise of the organization regardingsecurity, which can be enhanced through training and education. Ease of implementation is the degree of difficulty and complexity of implementing security, which can be reduced by using appropriate methods and tools. Industry-leading security tools are the best-in-class solutions and technologies that can provide effective and efficient security, which can be acquired through market research and evaluation. References = CRISC Review Manual, 7th Edition, Chapter 1, Section 1.3.1, page 32.
Question # 130
Which of the following is the BEST approach for an organization in a heavily regulated industry to comprehensively test application functionality?
A.
Use production data in a non-production environment
B.
Use masked data in a non-production environment
C.
Use test data in a production environment
D.
Use anonymized data in a non-production environment
Full Access
Answer:
D
Explanation:
 Using anonymized data in a non-production environment is the best approach for an organization in a heavily regulated industry to comprehensively test application functionality. Anonymized data is data that has been stripped of any personally identifiable information (PII) or other sensitive data, such as names, addresses, phone numbers, email addresses, etc. Anonymized data protects the privacy and security of the data, while still preserving the structure and format of the original data. Using anonymized data in a non-production environment allows the organization to test the application functionality without risking data breaches or violating regulations. Using production data, masked data, or test data in either production or non-production environments are not as optimal as using anonymized data, because they may introduce errors, inconsistencies, or vulnerabilities in the data or the application. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-21.
Question # 131
Which of The following is the MOST comprehensive input to the risk assessment process specific to the effects of system downtime?
A.
Business continuity plan (BCP) testing results
B.
Recovery lime objective (RTO)
C.
Business impact analysis (BIA)
D.
results Recovery point objective (RPO)
Full Access
Answer:
C
Explanation:
The most comprehensive input to the risk assessment process specific to the effects of system downtime is the business impact analysis (BIA). The BIA is a process of analyzing the potential impacts of disruptive events on the business processes, functions, and resources. The BIA identifies the criticality, dependencies, recovery priorities, and recovery objectives of the business processes, and quantifies the financial and non-financial impacts of system downtime. The BIA provides valuable information for the risk assessment process, as it helps to evaluate the likelihood and impact of the risks, and to determine the appropriate risk responses. Business continuity plan (BCP) testing results, recovery time objective (RTO), and recovery point objective (RPO) are not as comprehensive as the BIA, as they are derived from the BIA and focus on specific aspects of the business continuity and recovery strategies. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 130.
Question # 132
Which of the following is MOST important to review when evaluating the ongoing effectiveness of the IT risk register?
A.
The costs associated with mitigation options
B.
The status of identified risk scenarios
C.
The cost-benefit analysis of each risk response
D.
The timeframes for risk response actions
Full Access
Answer:
B
Explanation:
The status of identified risk scenarios, because it helps to monitor and track the current level and direction of the IT risks, and to determine whether the risk responses and controls are adequate and effective. An IT riskregister is a document that records and tracks the key IT risks that an organization faces, along with their likelihood, impact, and response strategies. An IT risk scenario is a hypothetical situation or event that describes the source, cause, consequence, and impact of an IT risk. The status of identified risk scenarios is the most important factor, as it reflects the actual and potential outcomes of the IT risks, and the performance and progress of the risk management process. The costs associated with mitigation options, the cost-benefit analysis of each risk response, and the timeframes for risk response actions are all possible factors to review when evaluating the ongoing effectiveness of the IT risk register, but they are not the most important factor, as they do not directly measure and report the status of the IT risk scenarios.
Question # 133
The BEST key performance indicator (KPI) to measure the effectiveness of a backup process would be the number of:
A.
resources to monitor backups
B.
restoration monitoring reports
C.
backup recovery requests
D.
recurring restore failures
Full Access
Answer:
D
Explanation:
The number of recurring restore failures is the best key performance indicator (KPI) to measure the effectiveness of a backup process, as it helps to evaluate the reliability and quality of the backup data and the backup system. A backup process is a process of creating and storing copies of data or systems to enable recovery in case of data loss, corruption, or disaster. A restore process is a process of retrieving and restoring the backup data or systems to the original or alternative location or state. A restore failure is an event that occurs when the restore processfails to complete successfully or correctly, due to various reasons, such as corrupted or missing backup data, incompatible or outdated backup system, or insufficient or unavailable resources. A recurring restore failure is a restore failure that happens repeatedly or frequently, indicating a persistent or systemic problem with the backup process.
The number of recurring restore failures helps to measure the effectiveness of the backup process by providing the following benefits:
It indicates the extent and magnitude of the backup process performance and quality issues, and the impact and severity of the backup process failures on the data or system availability and integrity.
It identifies and analyzes the root causes and contributing factors of the backup process failures, and the gaps or weaknesses in the backup process design, implementation, operation, or monitoring.
It provides feedback and learning opportunities for the backup process improvement and enhancement, and guides the development and implementation of corrective or preventive actions.
It communicates and reports the backup process status and results to the relevant stakeholders, and supports the alignment of the backup process with the organizational strategy and objectives.
The other options are not the best key performance indicators (KPIs) to measure the effectiveness of a backup process. The number of resources to monitor backups is a measure of the inputs or costs of the backup process, but it does not indicate the outputs or benefits of the backup process. The number of restoration monitoring reports is a measure of the documentation or communication of the backup process, but it does not reflect the actual or potential performance or quality of the backup process. The number of backup recovery requests is a measure of the demand or frequency of the backup process, but it does not evaluate the reliability or quality of the backup process. References = 12 Process KPIs to Monitor Process Performance in 2024 - AIMultiple, IT Risk Resources | ISACA, Mastering RTO and RPO in Backup Strategies: A Key to Data Recovery Success
Question # 134
Which of the following is MOST important to consider when determining the risk associated with re-identification of obfuscated personal data?
A.
The type of shared data
B.
The level of residual risk after data loss prevention (DLP) controls are implemented
C.
The monetary value of the unique records that could be re-identified
D.
The impact to affected stakeholders
Full Access
Answer:
D
Explanation:
The impact to affected stakeholdersis the most critical factor when considering risks tied to re-identification. ISACA notes that risk is ultimately measured by how it affects stakeholders—including customers, partners, and regulators—particularly when personal data is involved.
===========
Question # 135
A risk practitioner wants to identify potential risk events that affect the continuity of a critical business process. Which of the following should the risk practitioner do FIRST?
A.
Evaluate current risk management alignment with relevant regulations.
B.
Determine if business continuity procedures are reviewed and updated on a regular basis.
C.
Review the methodology used to conduct the business impact analysis (BIA).
D.
Conduct a benchmarking exercise against industry peers.
Full Access
Answer:
C
Explanation:
Reviewing the methodology used to conduct the business impact analysis (BIA) is the first thing that a risk practitioner should do when wanting to identify potential risk events that affect the continuity of a critical business process, because it helps to ensure that the BIA is conducted in a consistent, comprehensive, and reliable manner, and that it covers all the relevant aspects and scenarios of the business process and its continuity. A BIA is a process of analyzing the potential impact of disruption to the critical business functions or processes, and identifying the recovery priorities and requirements. A BIA methodology is a set of principles, standards, and techniques that guide and support the BIA process, such as the scope, objectives, data sources, data collection methods, data analysis methods, and reporting methods. Reviewing the BIA methodology is the first thing to do, as it helps to establish the foundation and framework for the BIA process, and to ensure that the BIA results are valid and useful for identifying the potential risk events and their consequences. Evaluating current risk management alignment with relevant regulations, determining if business continuity proceduresare reviewed and updated on a regular basis, and conducting a benchmarking exercise against industry peers are all possible things to do after reviewing the BIA methodology, but they are not the first thing to do, as they depend on the quality and accuracy of the BIA process and outcomes. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 143
Question # 136
The PRIMARY reason for tracking the status of risk mitigation plans is to ensure:
A.
the proposed controls are implemented as scheduled.
B.
security controls are tested prior to implementation.
C.
compliance with corporate policies.
D.
the risk response strategy has been decided.
Full Access
Answer:
A
Explanation:
The primary reason for tracking the status of risk mitigation plans is to ensure that the proposed controls are implemented as scheduled, as this can help to reduce the risk exposure of the organization and to achieve the desired risk objectives. Tracking the status of risk mitigation plans can also help to monitor and evaluate the performance and effectiveness of the risk controls, and to identify and address any issues or gaps that may arise during the implementation.Tracking the status of risk mitigation plans can also provide feedback and information to the risk owners and stakeholders, and enable them to adjust the risk strategy and response actions accordingly. References = CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 251. CRISC Sample Questions 2024, Question 251. ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 251. CRISC by Isaca Actual Free Exam Q & As, Question 9.
Question # 137
A user has contacted the risk practitioner regarding malware spreading laterally across the organization ' s corporate network. Which of the following is the risk practitioner’s BEST course of action?
A.
Review all log files generated during the period of malicious activity.
B.
Perform a root cause analysis.
C.
Notify the cybersecurity incident response team.
D.
Update the risk register.
Full Access
Answer:
C
Explanation:
Notifying the incident response team ensures immediate action to contain and remediate the malware spread, limiting further impact. This aligns withIncident Response and Containmentprotocols under risk management.
Question # 138
Which of the following is MOST helpful in aligning IT risk with business objectives?
A.
Introducing an approved IT governance framework
B.
Integrating the results of top-down risk scenario analyses
C.
Performing a business impact analysis (BlA)
D.
Implementing a risk classification system
Full Access
Answer:
B
Explanation:
Integrating the results of top-down risk scenario analyses is the most helpful in aligning IT risk with business objectives, as it helps to identify and prioritize the IT-related risks that could affect the achievement of the business goals and strategies. A top-down risk scenario analysis is a method of risk assessment that starts from the business perspective and considers the potential impact and likelihood of various risk events on the business outcomes and performance. A top-down risk scenario analysis can help to align IT risk with business objectives by providing the following benefits:
It ensures that the IT risk assessment is driven by the business needs and priorities, rather than by the IT technical details or assumptions.
It enables a holistic and comprehensive view of the IT risk landscape and its interdependencies with the business processes and functions.
It facilitates the communication and collaboration among the business and IT stakeholders and enhances their understanding and awareness of the IT risk exposure and control environment.
It supports the development and implementation of effective and efficient IT risk response and mitigation strategies that are aligned with the business risk appetite and objectives.
The other options are not the most helpful in aligning IT risk with business objectives. Introducing an approved IT governance framework is a good practice to establish the principles, policies, and processes for the governance of IT, but it does not directly address the IT riskalignment with the business objectives. Performing a business impact analysis (BIA) is an important step to assess the potential consequences of IT disruptions on the business operations and continuity, but it does not provide information on the likelihood or sources of the IT risk events. Implementing a risk classification system is a useful tool to categorize and organize the IT risks based on their characteristics and attributes, but it does not link the IT risks with the business objectives or outcomes. References = Risk Scenarios Toolkit - ISACA, IT Risk Resources | ISACA, How to reduce risk by aligning business strategy and IT strategy - QuoStar
Question # 139
Which of the following is the MOST important reason for a risk practitioner to identify stakeholders for each IT risk scenario?
A.
To ensure enterprise-wide risk management
B.
To establish control ownership
C.
To enable a comprehensive view of risk
D.
To identify key risk indicators (KRIs)
Full Access
Answer:
C
Explanation:
Identifying stakeholders ensures that all perspectives are considered, contributing to a holistic view of risk and improving communication and response planning.
[Reference:CRISC Manual – Domain 1: Governance, Slide 405-408, , , , ]
Question # 140
An IT department originally planned to outsource the hosting of its data center at an overseas location to reduce operational expenses. After a risk assessment, the department has decided to keep the data center in-house. How should the risk treatment response be reflected in the risk register?
A.
Risk mitigation
B.
Risk avoidance
C.
Risk acceptance
D.
Risk transfer
Full Access
Answer:
B
Explanation:
 The risk treatment response that should be reflected in the risk register when an IT department decides to keep the data center in-house instead of outsourcing it to an overseas location is risk avoidance. Risk avoidance is a risk response strategy that involves eliminating the source of the risk, or changing the plan or scope of the activity, to avoid the risk altogether. Risk avoidance can help to reduce the risk exposure and impact to zero, by removing the possibility of the risk occurrence. In this case, the IT department avoids the risk of outsourcing the data center to an overseas location, which could involve various threats, vulnerabilities, and uncertainties, such as data security, legal compliance, service quality, communication, or cultural issues. By keeping the data center in-house, the IT department maintains the control and ownership of the data center, and eliminates the potential risk associated with the outsourcing. Risk mitigation, risk acceptance, and risk transfer are not the correct risk treatment responses, as they do not reflect the actual decision and action taken by the IT department, and they do not eliminate the risk source or occurrence. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 51.
Question # 141
Which of the following is the PRIMARY purpose of a risk register?
A.
It guides management in determining risk appetite.
B.
It provides management with a risk inventory.
C.
It aligns risk scenarios to business objectives.
D.
It monitors the performance of risk and control owners.
Full Access
Answer:
B
Question # 142
Which of the following IT controls is MOST useful in mitigating the risk associated with inaccurate data?
A.
Encrypted storage of data
B.
Links to source data
C.
Audit trails for updates and deletions
D.
Check totals on data records and data fields
Full Access
Answer:
D
Explanation:
 Check totals are IT controls that verify the accuracy and completeness of data by comparing the sum or count of data records or data fields with a predetermined or expected value. Check totals can help detect and prevent errors, omissions, or alterations in data entry, processing, or transmission. Check totals can also help identify and correct data discrepancies or anomalies. Therefore, check totals are the most useful IT controls in mitigating the risk associated with inaccurate data. The other options are not the best answers because they do not directly address the risk of inaccurate data. Encrypted storage of data is an IT control that protects the confidentiality and integrity of data by preventing unauthorized access or modification. However, encryption does not ensure the accuracy or validity of the data itself. Links to source data are IT controls that provide traceability and transparency of data by allowing users to access or view the original data from which the derived or aggregated data is obtained. However, links to source data do not verify or correct the data quality or consistency. Audit trails for updates and deletions are IT controls that record thehistory and changes of data by capturing the date, time, user, and action performed on the data. Audit trails can help monitor and review the data activities and transactions, but they do not prevent or detect the data errors or inaccuracies. References = CRISC Review Manual, pages 164-1651; CRISC Review Questions, Answers & Explanations Manual, page 722
Question # 143
The PRIMARY objective of collecting information and reviewing documentation when performing periodic risk analysis should be to:
A.
Identify new or emerging risk issues.
B.
Satisfy audit requirements.
C.
Survey and analyze historical risk data.
D.
Understand internal and external threat agents.
Full Access
Answer:
A
Explanation:
The primary objective of collecting information and reviewing documentation when performing periodic risk analysis is to identify new or emerging risk issues that may affect the enterprise’s objectives, processes, or resources. This helps to update the risk profile and prioritize the risk responses accordingly. Satisfying audit requirements, surveying and analyzing historical risk data, and understanding internal and external threat agents are secondary objectives that support the primary objective of risk identification. References = Risk IT Framework, 2nd Edition, page 22; CRISC Review Manual, 6th Edition, page 64.
Question # 144
Which of the following is the PRIMARY objective of aggregating the impact of IT risk scenarios and reflecting the results in the enterprise risk register?
A.
To ensure IT risk appetite is communicated across the organization
B.
To ensure IT risk impact can be compared to the IT risk appetite
C.
To ensure IT risk ownership is assigned at the appropriate organizational level
D.
To ensure IT risk scenarios are consistently assessed within the organization
Full Access
Answer:
B
Explanation:
The primary objective of aggregating the impact of IT risk scenarios and reflecting the results in the enterprise risk register is to ensure IT risk impact can be compared to the IT risk appetite, as it enables the organization to measure and evaluate the overall level and exposure of the IT risk, and to align and prioritize the IT risk response and strategy with the organizational objectives and regulations. The other options are not the primary objectives, as they are more related to the communication, assignment, or assessment of the IT risk scenarios, respectively, rather than the aggregation or reflection of the IT risk scenarios. References = CRISC Review Manual, 7th Edition, page 109.
Question # 145
To enable effective integration of IT risk scenarios and ERM, it is MOST important to have a consistent approach to reporting:
A.
Risk impact and likelihood
B.
Risk velocity
C.
Key risk indicators (KRIs)
D.
Risk response plans and owners
Full Access
Answer:
A
Explanation:
Aconsistent approach to reporting risk impact and likelihoodis essential for integrating IT risk into the broader enterprise risk management (ERM) framework. It allows for proper aggregation and alignment, ensuring IT risks are understood in context with overall enterprise risk.
===========
Question # 146
An IT license audit has revealed that there are several unlicensed copies of co be to:
A.
immediately uninstall the unlicensed software from the laptops
B.
centralize administration rights on laptops so that installations are controlled
C.
report the issue to management so appropriate action can be taken.
D.
procure the requisite licenses for the software to minimize business impact.
Full Access
Answer:
C
Explanation:
An IT license audit is a process that verifies the compliance of the IT software and hardware assets with the licensing agreements and regulations. An IT license audit can reveal the existence of unlicensed copies of software, which can expose the enterprise to legal, financial, and reputational risks. The best course of action in such a situation is to report the issue to management so that appropriate action can be taken. Management can then decide on the most suitable risk response strategy, such as procuring the necessary licenses, uninstalling the unlicensed software, or negotiating with the software vendor. Reporting the issue to managementcan also help to prevent further violations, identify the root causes, and implement corrective and preventive measures. The other options are not the best course of action, as they may not address the issue effectively, efficiently, or ethically. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.1.1, pp. 156-157.
Question # 147
Which of the following is the MOST important consideration when selecting key risk indicators (KRIs) to monitor risk trends over time?
A.
Ongoing availability of data
B.
Ability to aggregate data
C.
Ability to predict trends
D.
Availability of automated reporting systems
Full Access
Answer:
A
Explanation:
Ongoing availability of data is the most important consideration when selecting key risk indicators (KRIs) to monitor risk trends over time, as it ensures that the KRIs can provide timely and reliable information on the current and future risk status and performance. KRIs are metrics that measure the level of risk exposureand the effectiveness of risk response strategies, and they should be aligned with the enterprise’s risk appetite and objectives. Ongoing availability ofdatameans that the data sources and collection methods for the KRIs are consistent, accessible, and sustainable, and that the data quality and integrity are maintained and verified. Ability to aggregate data, ability to predict trends, and availability of automated reporting systems are not the most important considerations, as they do not affect the validity and usefulness of the KRIs, but rather the presentation and analysis of the KRI data. References = CRISC Certified in Risk and Information Systems Control – Question213; ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 213.
Question # 148
Which of the following is the BEST way to quantify the likelihood of risk materialization?
A.
Balanced scorecard
B.
Threat and vulnerability assessment
C.
Compliance assessments
D.
Business impact analysis (BIA)
Full Access
Answer:
B
Explanation:
A threat and vulnerability assessment is a process that identifies and evaluates the potential sources and impacts of risk events on an organization’s assets, processes, and objectives. It also estimates the probability of occurrence and the severity of consequences for each risk event. A threat and vulnerability assessment is the best way to quantify the likelihood of risk materialization, as it provides a numerical or qualitative measure of the risk exposure and the level of uncertainty associated with the risk scenarios. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.2, p. 68-69
Question # 149
An organization ' s IT department wants to complete a proof of concept (POC) for a security tool. The project lead has asked for approval to use the production data for testing purposes as it will yield the best results. Which of the following is the risk practitioner ' s BEST recommendation?
A.
Accept the risk of using the production data to ensure accurate results.
B.
Assess the risk of using production data for testing before making a decision.
C.
Benchmark against what peer organizations are doing with POC testing environments.
D.
Deny the request, as production data should not be used for testing purposes.
Full Access
Answer:
B
Explanation:
Assessing the risk of using production data for testing before making a decision is the best recommendation for the risk practitioner, because it helps to balance the benefits and drawbacks of using real data for the proof of concept (POC) of a security tool. A POC is a demonstration or trial of a proposed solution or product to verify its feasibility, functionality, and value. A security tool is a software or hardware device that helps to protect the IT systems or networks from threats or attacks. Using production data for testing purposes can yield the best results, as it reflects the actual data that the security tool will handle in the operational environment. However, using production data for testing also poses risks, such as data leakage, data corruption, data privacy violation, or regulatory non-compliance. Therefore, assessing the risk ofusing production data for testing before making a decision is the best recommendation, as it helps to identify and evaluate the potential risks and issues, and to determine the appropriate controls or mitigating factors to reduce or eliminate them. Accepting the risk of using the production data, benchmarking against what peer organizations are doing, and denying the request are all possible recommendations, but they are not the best recommendation, as they do not consider the risk assessment process and the trade-offs involved in using production data for testing. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.4.1, page 208
Question # 150
Which of the following observations would be GREATEST concern to a risk practitioner reviewing the implementation status of management action plans?
A.
Management has not determined a final implementation date.
B.
Management has not completed an early mitigation milestone.
C.
Management has not secured resources for mitigation activities.
D.
Management has not begun the implementation.
Full Access
Answer:
D
Explanation:
The observation that would be of GREATEST concern to a risk practitioner reviewing the implementation status of management action plans is that management has not begun the implementation, because it indicates that the management action plans are not being executed or monitored, and that the risks are not being addressed or mitigated. The lack of implementation may also imply that the management action plans are not realistic, feasible, or aligned with the enterprise’s strategy and objectives. The other options are not as concerning as the lack of implementation, because:
Option A: Management has not determined a final implementation date is a concern, but not the greatest one, because it may affect the timely completion and delivery of the management action plans, but it does not necessarily mean that the management action plans are not being executed or monitored.
Option B: Management has not completed an early mitigation milestone is a concern, but not the greatest one, because it may indicate a delay or deviation in the progress and performance of the management action plans, but it does not necessarily mean that the management action plans are not being executed or monitored.
Option C: Management has not secured resources for mitigation activities is a concern, but not the greatest one, because it may affect the quality and effectiveness of the management actionplans, but it does not necessarily mean that the management action plans are not being executed or monitored. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 123.
Question # 151
The BEST way to mitigate the high cost of retrieving electronic evidence associated with potential litigation is to implement policies and procedures for:
A.
data classification and labeling.
B.
data logging and monitoring.
C.
data retention and destruction.
D.
data mining and analytics.
Full Access
Answer:
C
Question # 152
Which of the following is the BEST method to identify unnecessary controls?
A.
Evaluating the impact of removing existing controls
B.
Evaluating existing controls against audit requirements
C.
Reviewing system functionalities associated with business processes
D.
Monitoring existing key risk indicators (KRIs)
Full Access
Answer:
C
Explanation:
 The best method to identify unnecessary controls is reviewing system functionalities associated with business processes, because this can help to determine whether the controls are relevant, effective, and efficient for the current business needs and objectives. System functionalities are the capabilities and features of IT systems that support the execution and performance of business processes. Business processes are the set of interrelated activities that transform inputs into outputs to deliver value to customers or stakeholders. By reviewing system functionalities associated with business processes, an organization can assess whether the controls are aligned with the process requirements, expectations, and outcomes, and whether they add value or create waste. The review can also identify any gaps, overlaps, redundancies, or conflicts among the controls, and any changes or improvements that are needed to optimize the controls. The other options are less effective methods to identify unnecessary controls. Evaluating the impact of removing existing controls can help to measure the benefits and costs of the controls, but it does not address the root causes or sources of the unnecessary controls. Evaluating existing controls against audit requirements can help to ensure compliance and assurance, but it does not considerthe business context or purpose of the controls. Monitoring existing key risk indicators (KRIs) can help to measure the level and impact of risks, but it does not evaluate the suitability oradequacy of the controls. References = Surveying Staff to Identify Unnecessary Internal Controls - Methodology and ResultsÂ
Question # 153
Which of the following would be MOST useful when measuring the progress of a risk response action plan?
A.
Percentage of mitigated risk scenarios
B.
Annual loss expectancy (ALE) changes
C.
Resource expenditure against budget
D.
An up-to-date risk register
Full Access
Answer:
D
Explanation:
A risk response action plan is a document that outlines the specific tasks, resources, timelines, and deliverables for the risk responses, which are the actions or strategies that are taken to address the risks that may affect the organization’s objectives, performance, or value creation12.
The most useful tool when measuring the progress of a risk response action plan is an up-to-date risk register, which is a document that records and tracks the significant risks that the organization faces, and the responses and actions that are taken to address them34.
An up-to-date risk register is the most useful tool because it provides a comprehensive and consistent view of the risk landscape, and the status and performance of the risk responses and actions34.
An up-to-date risk register is also the most useful tool because it enables the monitoring and evaluation of the risk response action plan, and the identification and communication of any issues or gaps that need to be resolved or improved34.
The other options are not the most useful tools, but rather possible metrics or indicators that may be used to measure the progress of a risk response action plan. For example:
Percentage of mitigated risk scenarios is a metric that measures the proportion of risk scenarios that have been reduced or eliminated by the risk responses and actions56. However, this metric is not the most useful tool because it does not provide a comprehensive and consistent view of the risk landscape, and it may not capture the residual or emerging risks that may arise after the risk responses and actions56.
Annual loss expectancy (ALE) changes is a metric that measures the difference between the expected annual losses before and after the risk responses and actions78. However, this metric is not the most useful tool because it does not provide a comprehensive and consistent view of the risk landscape, and it may not reflect the qualitative or intangible impacts of the risks or the risk responses and actions78.
Resource expenditure against budget is a metric that measures the amount of resources and funds that have been spent or allocated for the risk responses and actions, compared to the planned or estimated budget . However, this metric is not the most useful tool because it does not provide acomprehensive and consistent view of the risk landscape, and it may not indicate the effectiveness or efficiency of the risk responses and actions . References =
1: Risk Response Plan in Project Management: Key Strategies & Tips1
2: How to Create the Ultimate Risk Response Plan | Wrike2
3: Risk Register Template and Examples | Prioritize and Manage Risk3
4: Risk Register Examples for Cybersecurity Leaders4
5: Risk Scenarios Toolkit, ISACA, 2019
6: Risk Scenarios Starter Pack, ISACA, 2019
7: Annualized Loss Expectancy (ALE) - Definition and Examples5
8: Annualized Loss Expectancy (ALE) Calculator6
Project Budgeting: How to Estimate Costs and Manage Budgets7
Project Budget Template - Download Free Excel Template8
Question # 154
After identifying new risk events during a project, the project manager s NEXT step should be to:
A.
determine if the scenarios need 10 be accepted or responded to.
B.
record the scenarios into the risk register.
C.
continue with a qualitative risk analysis.
D.
continue with a quantitative risk analysis.
Full Access
Answer:
B
Explanation:
After identifying new risk events during a project, the project manager’s next step should be to record the scenarios into the risk register, which is a document that records and tracks the identified risks, their causes, impacts, likelihood, responses, owners, and status. Recording the scenarios into the risk registerhelps to document and communicate the risks to the project team and stakeholders, and to facilitate the subsequent risk analysis and response processes. The other options are not the next steps, but rather the subsequent steps after recording the scenarios into the risk register. Determining if the scenarios need to be accepted or responded to is part of the risk evaluation and treatment process, which requires a prior risk analysis. Continuing with a qualitative or quantitative risk analysis is part of the risk assessment process, which requires a prior risk identification and documentation. References = Risk Register: A Project Manager’s Guide with Examples [2023] • Asana; Risk Identification in Project Management; 6.3. The 5 Steps of the Risk Management Process
Question # 155
A bank is experiencing an increasing incidence of customer identity theft. Which of the following is the BEST way to mitigate this risk?
A.
Implement monitoring techniques.
B.
Implement layered security.
C.
Outsource to a local processor.
D.
Conduct an awareness campaign.
Full Access
Answer:
B
Explanation:
The best way to mitigate the risk of customer identity theft is to implement layered security. Layered security is a defense-in-depth approach that applies multiple and diverse security controls at different levels and stages of the information system and the data lifecycle. Layered security can include physical, technical, and administrative controls, such as locks, firewalls, encryption, authentication, authorization, backup, audit, and policy. Layered security can help to protect the customer data and identity from unauthorized access, use, modification, disclosure, or destruction, by creating multiple barriers and deterrents for potential attackers, and by reducing the impact and likelihood of a successful breach. Layered security can also help to comply with the legal and regulatory requirements and standards for data privacy and protection, such as the Gramm-Leach-Bliley Act (GLBA), the Fair Credit Reporting Act (FCRA), and the Payment Card Industry Data Security Standard (PCI DSS)123.The other options are not the best way to mitigate the risk of customer identity theft, although they may be useful or complementary to layered security. Implementing monitoring techniques is a part of the layered security approach, but it is not sufficient, as it mainly focuses on detecting and responding to the incidents, rather than preventing or deterring them. Outsourcing to a local processor is a business decision that may or may not improve the security of the customer data and identity, depending on the quality and reliability of the service provider, and the terms and conditions of the outsourcing contract. Conducting an awareness campaign is a good practice that can help to educate and inform the customers and the employees about the common types, methods, and indicators of identity theft, and the best practices and precautions to prevent or report it, but it does not directly apply or enforce any security controls to the information system or the data.
Question # 156
Which of the following is MOST important to compare against the corporate risk profile?
A.
Industry benchmarks
B.
Risk tolerance
C.
Risk appetite
D.
Regulatory compliance
Full Access
Answer:
B
Explanation:
Risk tolerance is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk tolerance is an important component of the corporate risk profile, as it defines the boundaries and limits of the acceptable risk exposure for the organization. Comparing the risk tolerance against the corporate risk profile can help to ensure that the organization’s risk strategy and objectives are aligned with its risk appetite and capacity, and that the organization is not taking on more risk than it can handle or afford. Comparing the risk tolerance against the corporate risk profile can also help to monitor and adjust the risk management process and controls, and to optimize the risk-return trade-off. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 249. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 249. CRISC Sample Questions 2024, Question 249. CRISC by Isaca Actual Free Exam Q & As, Question 9.
Question # 157
A business manager wants to leverage an existing approved vendor solution from another area within the organization. Which of the following is the risk practitioner ' s BEST course of action?
A.
Recommend allowing the new usage based on prior approval.
B.
Request a new third-party review.
C.
Request revalidation of the original use case.
D.
Assess the risk associated with the new use case.
Full Access
Answer:
D
Explanation:
 A risk practitioner’s best course of action when a business manager wants to leverage an existing approved vendor solution from another area within the organization is to assess the risk associated with the new use case. This is because the new use case may introduce different or additional risks that were not considered or addressed in the original approval. For example, the new use case may involve different data types, volumes, or sensitivities; different business processes, functions, or objectives; different regulatory or contractual requirements; or different technical or operational dependencies. Therefore, the risk practitioner should perform a vendor risk assessment (VRA) to identify, evaluate, and mitigate the potential risks of the new use case and ensure that the vendor solution meets the organization’s riskappetite and tolerance12. Recommending allowing the new usage based on prior approval is not the best course of action, as it may overlook or underestimate the risks of the new use case and expose the organization to unacceptable levels of risk. Requesting a new third-party review is not the best course of action,as it may be unnecessary or redundant if the vendor solution has already been reviewed and approved for another use case within the organization. Requesting revalidation of the original use case is not the best course of action, as it may not address the specific risks of the new use case and may also delay or disrupt the existing use case. References = Risk and Information SystemsControl Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.
Question # 158
Which of the following would be MOST useful to senior management when determining an appropriate risk response?
A.
A comparison of current risk levels with established tolerance
B.
A comparison of cost variance with defined response strategies
C.
A comparison of current risk levels with estimated inherent risk levels
D.
A comparison of accepted risk scenarios associated with regulatory compliance
Full Access
Answer:
A
Explanation:
A comparison of current risk levels with established tolerance is the most useful information for senior management when determining an appropriate risk response, as it shows the gap between the actual risk exposure and the desired risk exposure of the enterprise. This gap indicates the need and urgency for risk response actions, and helps senior management to prioritize and allocate resources for risk mitigation. A comparison of current risk levels with established tolerance also reflects the effectiveness of the existing risk management process and controls, and enables senior management to monitor and adjust the risk strategy and objectives accordingly. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 234. CRISC by Isaca Actual Free Exam Q & As, Question 9. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 234. CRISC Sample Questions 2024, Question 234.
Question # 159
Which of the following is the MOST important objective of establishing an enterprise risk management (ERM) function within an organization?
A.
To have a unified approach to risk management across the organization
B.
To have a standard risk management process for complying with regulations
C.
To optimize risk management resources across the organization
D.
To ensure risk profiles are presented in a consistent format within the organization
Full Access
Answer:
A
Explanation:
The most important objective of establishing an enterprise risk management (ERM) function within an organization is to have a unified approach to risk management across the organization. An ERM function is a centralized and coordinated function that oversees and supports the risk management activities of the organization, such as risk identification, assessment, response, monitoring, and reporting. An ERM function helps to ensure that the risk management process is consistent, comprehensive, and integrated with the organization’s strategy, objectives, and culture. An ERM function also helps to align the risk management activities with the organization’s risk appetite and tolerance, and to provide a holistic view of the organization’s risk profile and exposure. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.1.1, page 131
Question # 160
Who should have the authority to approve an exception to a control?
A.
information security manager
B.
Control owner
C.
Risk owner
D.
Risk manager
Full Access
Answer:
B
Explanation:
 The control owner is the person who has the authority to approve an exception to a control. A control is a policy, procedure, or technical measure that is implemented to prevent or mitigate a risk. A control owner is responsible for the design, implementation, operation, and maintenance of the control, as well as for monitoring and reporting its performance and effectiveness. A control owner is also accountable for the approval of any changes or exceptions to the control, based on the risk assessment and business justification. An information security manager, a risk owner, and a risk manager are not the best choices, as they do not have the same level of authority, responsibility, and knowledge as the control owner in relation to the control. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 35.
Question # 161
The PRIMARY objective of a risk identification process is to:
A.
evaluate how risk conditions are managed.
B.
determine threats and vulnerabilities.
C.
estimate anticipated financial impact of risk conditions.
D.
establish risk response options.
Full Access
Answer:
B
Explanation:
The primary objective of a risk identification process is to determine threats and vulnerabilities, which are the sources and causes of the risks that may affect the organization’sobjectives. Threats are any events or circumstances that have the potential to harm or exploit the organization’s assets, such as people, information, systems, processes, or infrastructure1. Vulnerabilities are any weaknesses or gaps in the organization’s capabilities, controls, or defenses that may increase the likelihood or impact of the threats2. By determining threats and vulnerabilities, the organization can:
Identify and document all possible risks, regardless of whether they are internal or external, current or emerging, or positive or negative3.
Understand the nature and characteristics of the risks, such as their sources, causes, consequences, and interrelationships4.
Provide the basis for further risk analysis and evaluation, such as assessing the probability and severity of the risks, and prioritizing the risks according to their significance and urgency5.
References =
Threat - CIO Wiki
Vulnerability - CIO Wiki
Risk Identification - CIO Wiki
Risk Identification and Analysis - The National Academies Press
Risk Analysis - CIO Wiki
Question # 162
A recent risk workshop has identified risk owners and responses for newly identified risk scenarios. Which of the following should be the risk practitioner ' s NEXT step?
A.
Develop a mechanism for monitoring residual risk.
B.
Update the risk register with the results.
C.
Prepare a business case for the response options.
D.
Identify resources for implementing responses.
Full Access
Answer:
B
Explanation:
The next step for the risk practitioner after identifying risk owners and responses for newly identified risk scenarios is to update the risk register with the results. The risk register is a document that records the details of the risks, such as their sources, causes, consequences, likelihood, impact, and responses. By updating the risk register with the results of the risk workshop, the risk practitioner can ensure that the risk information is current, accurate, and complete, and that the risk owners and responses are clearly defined and communicated. Developing a mechanism for monitoring residual risk, preparing a business case for the response options, and identifying resources for implementing responses are possible steps that may follow the updating of the risk register, but they are not the next step. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Question # 163
Which of the following is the MOST important document regarding the treatment of sensitive data?
A.
Encryption policy
B.
Organization risk profile
C.
Digital rights management policy
D.
Information classification policy
Full Access
Answer:
D
Explanation:
The information classification policy is the most important document regarding the treatment of sensitive data, because it defines the categories and criteria for classifying data according to their sensitivity, confidentiality, and value to the organization, and specifies the appropriate handling and protection measures for each category. Sensitive data are data that contain personal,proprietary, or confidential information that may cause harm or damage to the organization or its stakeholders if disclosed, modified, or destroyed without authorization. An information classification policy helps to ensure that sensitive data are identified and treated in a consistent and secure manner, and that the organization complies with the applicable laws andregulations regarding data protection and privacy. An encryption policy, an organization risk profile, and a digital rights management policy are all useful documents for the treatment of sensitive data, but they are not the most important document, as they do not directly address the classification and handling of sensitive data. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 158
Question # 164
Which of the following is MOST effective against external threats to an organizations confidential information?
A.
Single sign-on
B.
Data integrity checking
C.
Strong authentication
D.
Intrusion detection system
Full Access
Answer:
C
Explanation:
 Strong authentication is the most effective measure against external threats to an organization’s confidential information. Confidential information is any data or information that is sensitive, proprietary, or valuable to the organization, and that should not be disclosed to unauthorized parties1. External threats are malicious actors outside the organization who attempt to gain unauthorized access to the organization’s networks, systems, and data, using various methods such as malware, hacking, or social engineering2. Strong authentication is a method of verifying the identity and legitimacy of a user or device before granting access to the organization’s resources or data3. Strong authentication typically involves the use of multiple factors or methods of authentication, such as passwords, tokens, biometrics, orcertificates4. Strong authentication can prevent or reduce the risk of external threats to the organization’s confidential information, by making it more difficult and costly for the attackers to compromise the credentials or devices of the authorized users, and by limiting the access to the data or resourcesthat are relevant and necessary for the users’ roles and responsibilities5. The other options are not the most effective measures against external threats to the organization’s confidential information, as they are either less secure or less relevant than strong authentication. Single sign-on is a method of allowing a user to access multiple systems or applications with a single set of credentials, without having to log in separately for each system or application6. Single sign-on can improve the user experience and convenience, as well as reduce the administrative burden and cost of managing multiple accounts and passwords. However, single sign-on is not the most effective measure against external threats to the organization’s confidential information, as it can also increase the risk of credential compromise or misuse, and create a single point of failure or attack for the attackers to access multiple systems or data. Data integrity checking is a method of ensuring that the data or information is accurate, complete, and consistent, and that it has not been altered or corrupted by unauthorized parties or processes. Data integrity checking can involve the use of techniques such as checksums, hashes, digital signatures, or encryption. Data integrity checking can enhance the quality and reliability of the data or information, as well as detect and prevent any unauthorized or malicious changes or tampering. However, data integrity checking is not the most effective measure against external threats to the organization’s confidential information, as it does not prevent or reduce the risk of data theft or leakage, and it does not verify the identity or legitimacy of the users or devices accessing the data. Intrusion detection system is a system that monitors the network or system activities and events, and detects and alerts any suspicious ormalicious behaviors or anomalies that may indicate an attempted or successful breach or attack. Intrusion detection system can help to identify and respond to external threats to the organization’s networks, systems, and data, by providing visibility and awareness of the network or system status and activities, and by enabling timely and appropriate actions or countermeasures. However, intrusion detection system is not the most effective measure againstexternal threats to the organization’s confidential information, as it is a reactive or passive system that does not prevent or block the attacks, and it may generate false positives or negatives that can affect its accuracy and efficiency. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.1, Page 189.
Question # 165
Which of the following should be the PRIMARY input to determine risk tolerance?
A.
Regulatory requirements
B.
Organizational objectives
C.
Annual loss expectancy (ALE)
D.
Risk management costs
Full Access
Answer:
B
Explanation:
Organizational objectives should be the primary input to determine risk tolerance, as they define the desired outcomes and performance of the organization, and guide the selection of the acceptable level of risk that the organization is willing to take to achieve those objectives. Regulatory requirements, annual loss expectancy (ALE), and risk management costs are not the primary inputs, as they are more related to the external or internal constraints or factors that affect the risk tolerance, rather than the drivers or determinants of the risk tolerance. References = CRISC Review Manual, 7th Edition, page 109.
Question # 166
Which of the following is the MOST appropriate role to determine risk appetite and tolerance?
A.
Senior management
B.
Internal auditor
C.
Risk owner
D.
Business process owner
Full Access
Answer:
A
Explanation:
The correct answer isAbecausesenior managementis the most appropriate role to determinerisk appetite and tolerance. These are enterprise-level governance decisions that guide how much risk the organization is willing to accept in pursuit of its objectives. Senior management sets and approves these boundaries in alignment with business strategy.
The other options are less appropriate:
B. Internal auditorprovides independent assurance and does not determine appetite or tolerance.
C. Risk ownermanages specific risks within the defined appetite and tolerance, but does not set enterprise-wide limits.
D. Business process ownerowns risk within a process, but enterprise appetite and tolerance are set at senior management level.
Exact Extracts supporting the answer:
“Senior management is responsible for approving an enterprise’s risk appetite and tolerance related to information security.â€
“Management culture and predisposition toward risk taking are most important when considering the risk appetite of an enterprise.â€
“Risk tolerance is the permissible deviation from declared risk appetite levels in an enterprise.â€
“The board of directors is accountable for overall enterprise strategy for risk governance.â€
These extracts directly support thatsenior managementis the most appropriate role to determine risk appetite and tolerance.
===========
Question # 167
Which of the following is the PRIMARY purpose of creating and documenting control procedures?
A.
To facilitate ongoing audit and control testing
B.
To help manage risk to acceptable tolerance levels
C.
To establish and maintain a control inventory
D.
To increase the likelihood of effective control operation
Full Access
Answer:
B
Explanation:
The primary purpose of creating and documenting control procedures is to help manage risk to acceptable tolerance levels. Control procedures are the specific actions or steps that are performed to achieve the control objectives and mitigate the risks. Control procedures should be documented to provide clear guidance, consistency, and accountability for the control activities. Documenting control procedures also helps to monitor and evaluate the effectiveness andefficiency of the controls, and to identify and address any gaps or weaknesses. The other options are not the primary purpose of creating and documenting control procedures, although they may be secondary benefits or outcomes. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, page 1-15.
Question # 168
Which of the following data would be used when performing a business impact analysis (BIA)?
A.
Cost-benefit analysis of running the current business
B.
Cost of regulatory compliance
C.
Projected impact of current business on future business
D.
Expected costs for recovering the business
Full Access
Answer:
D
Explanation:
A business impact analysis (BIA) is a process that identifies and assesses the effects that accidents, emergencies, disasters, and other unplanned, negative events could have on a business. The BIA (sometimes also called business impact assessment) predicts how a business will be affected by everything from a hurricane to a labor strike1.
One of the data that would be used when performing a BIA is the expected costs for recovering the business. This data can help to estimate the amount of resources and funds that would be needed to restore the normal operations and functions of the business after a disruption. The expected costs for recovering the business can include:
The costs of repairing or replacing damaged or lost assets, such as equipment, inventory, or facilities
The costs of hiring or training additional staff, or outsourcing some tasks or services
The costs of implementing alternative or backup systems or processes, such as cloud computing or manual procedures
The costs of communicating and coordinating with customers, suppliers, partners, regulators, and other stakeholders
The costs of complying with legal or contractual obligations, or paying fines or penalties
The costs of mitigating or preventing further losses or damages, such as insurance premiums or security measures23
The expected costs for recovering the business can help to determine the priority and urgency of the recovery activities, and to allocate the available resources and funds accordingly. The expected costs for recovering the business can also help to evaluate the cost-effectiveness and feasibility of the recovery strategies and options, and to justify the investment in the business continuity planning and management4.
The other options are not the data that would be used when performing a BIA, but rather the data that would be used for other purposes or processes. A cost-benefit analysis of running the current business is a data that would be used to compare the advantages and disadvantages of different business decisions or alternatives, such as launching a new product or service, or expanding to a new market. A cost-benefit analysis can help to assess the profitability and viability of the current business, but it does not measure the impact of a disruption on the business5. A cost of regulatory compliance is a data that would be used toestimate the amount of resources and funds that would be required to meet the rules and standards set by the authorities or agencies that govern the business, such as laws, regulations, or policies. A cost of regulatory compliance can help to ensure the legality and accountability of the business, but it does not measure the impactof a disruption on the business. A projected impact of current business on future business is a data that would be used to forecast the potential outcomes and consequences of the current business activities or strategies on the future business performance and growth, such as sales, revenue, market share, or customer satisfaction. A projected impact of current business on future business can help to plan and optimize the future business, but it does not measure the impact of a disruption on the current business. References =
Business Impact Analysis | Ready.gov
Business Impact Analysis Toolkit | Smartsheet
Business Impact Analysis (BIA): Prepare for Anything [2023] • Asana
How To Conduct Business Impact Analysis in 8 Easy Steps - G2
Cost Benefit Analysis - ISACA
[Regulatory Compliance - ISACA]
[Impact Analysis - ISACA]
[CRISC Review Manual, 7th Edition]
Question # 169
Which of the following represents a vulnerability?
A.
An identity thief seeking to acquire personal financial data from an organization
B.
Media recognition of an organization ' s market leadership in its industry
C.
A standard procedure for applying software patches two weeks after release
D.
An employee recently fired for insubordination
Full Access
Answer:
C
Explanation:
 A vulnerability is a weakness or gap in a system, application, or network that can be exploited by a threat to cause harm or gain unauthorized access1. A vulnerability can be caused by various factors, such as design flaws, coding errors, configuration errors, or outdated software2.
Among the four options given, only option C (a standard procedure for applying software patches two weeks after release) represents a vulnerability. This is because software patches are updates or fixes that address security weaknesses or bugs in software applications or systems3. By applying software patches two weeks after release, the organization is exposing itself to the risk of being attacked or compromised by malicious actors who may exploit the known vulnerabilities in the software before they are patched. This risk is especially high if the software is internet-facing or critical to the organization’s operations4.
References = What is a Vulnerability?, Vulnerability Definition & Meaning - Merriam-Webster, Vulnerability Patching: A Resource Guide - Rezilion, Why is Software Vulnerability Patching Crucial for Your Software and …
Question # 170
A robotic process automation (RPA) project has implemented new robots to enhance the efficiency of a sales business process. Which of the following provides the BEST evidence that the new controls have been implemented successfully?
A.
A post-implementation review has been conducted by key personnel.
B.
A qualified independent party assessed the new controls as effective.
C.
Senior management has signed off on the design of the controls.
D.
Robots have operated without human interference on a daily basis.
Full Access
Answer:
B
Explanation:
Independent Assessment:
Objective Evaluation: An assessment by a qualified independent party ensures that the evaluation of the new controls is unbiased and thorough. It provides a credible verification of the control ' s effectiveness.
Expertise and Standards: Independent assessors bring specialized expertise and follow established standards and best practices, ensuring a comprehensive review of the control implementation.
Validation and Assurance: This assessment provides assurance to stakeholders that the controls are functioning as intended and meet the required security and operational standards.
Comparison with Other Options:
Post-Implementation Review by Key Personnel: While valuable, this review may lack the objectivity and thoroughness of an independent assessment.
Senior Management Sign-Off: Sign-off from senior management is important but does not provide the detailed validation of control effectiveness that an independent assessment offers.
Daily Operation of Robots without Human Interference: This indicates operational stability but does not verify that all controls are functioning as intended.
Best Practices:
Regular Independent Assessments: Schedule regular independent assessments to continuously validate the effectiveness of controls.
Comprehensive Reporting: Ensure that the independent assessment includes comprehensive reporting on findings and recommendations for improvement.
Follow-Up Actions: Implement any recommended actions from the assessment to address identified gaps or weaknesses in the controls.
[References:, CRISC Review Manual: Recommends independent assessments as a best practice for validating control effectiveness and ensuring comprehensive risk management., ISACA Standards: Support the use of independent assessments to provide objective and credible evaluations of control implementations., , , , , , , , , , ]
Question # 171
Which of the following is the MOST important objective of embedding risk management practices into the initiation phase of the project management life cycle?
A.
To deliver projects on time and on budget
B.
To assess inherent risk
C.
To include project risk in the enterprise-wide IT risk profit.
D.
To assess risk throughout the project
Full Access
Answer:
B
Explanation:
The most important objective of embedding risk management practices into the initiation phase of the project management life cycle is to assess inherent risk. Inherent risk is the risk that exists before any controls or mitigations are applied. By assessing inherent risk in the initiation phase, the project team can identify the potential sources, causes, and impacts of risk that may affect the project objectives, scope, and deliverables. Assessing inherent risk in the initiation phase also helps to prioritize the risks, determine the risk appetite and tolerance, and plan the risk responses. Delivering projects on time and on budget, including project risk in the enterprise-wide IT risk profile, and assessing risk throughout the project are important objectives of risk management,but they are not the most important objective of embedding risk management practices into the initiation phase. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1.1, page 511
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 658.
Question # 172
From a risk management perspective, the PRIMARY objective of using maturity models is to enable:
A.
solution delivery.
B.
resource utilization.
C.
strategic alignment.
D.
performance evaluation.
Full Access
Answer:
C
Explanation:
Maturity models are tools that help organizations assess and improve their risk management processes and capabilities. They provide a set of criteria or standards that define different levels of maturity, from ad-hoc to innovative. The primary objective of using maturity models in risk management is to enable strategic alignment, which means ensuring that the risk management activities and objectives are consistent with and support the organization’s mission, vision, values, and goals. By using maturity models, organizations can identify their current level of risk management maturity, compare it with their desired level, and plan and implement actions to close the gap. This way, they can align their risk management practices with their strategic direction and priorities, and enhance their performance and value creation. References = How to Use a Maturity Model in Risk Management — RiskOptics - Reciprocity, Using a Maturity Model to Assess Your Risk Management Program, How to Use a Risk Maturity Model to Level Up · Riskonnect
Question # 173
Which of the following is the BEST key performance indicator (KPI) to measure the effectiveness of IT policies? The number of:
A.
IT policy exceptions granted.
B.
Senior management approvals.
C.
Key technology controls covered by IT policies.
D.
Processes covered by IT policies.
Full Access
Answer:
C
Question # 174
Which of the following would BEST facilitate the implementation of data classification requirements?
A.
Assigning a data owner
B.
Implementing technical control over the assets
C.
Implementing a data loss prevention (DLP) solution
D.
Scheduling periodic audits
Full Access
Answer:
A
Explanation:
Assigning a data owner would best facilitate the implementation of data classification requirements. A data owner is responsible for defining the classification of the data, ensuring that the data is properly labeled, and approving access requests. Implementing technical control over the assets, implementing a data loss prevention (DLP) solution, and scheduling periodic audits are important activities, but they are not as effective as assigning a data owner. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 8; CRISC Review Manual, 6th Edition, page 97.
Question # 175
Digital signatures are an effective control method for information exchange over an insecure network because they:
A.
authenticate the user biometrically.
B.
are under the sole custody of the receiver.
C.
are constant over time.
D.
enable nonrepudiation.
Full Access
Answer:
D
Explanation:
Digital signatures use asymmetric cryptography to bind a signer’s identity to a specific message hash. In the CRISC context, they provide multiple security properties—integrity (changes to the message alter the signature) and authentication of the signer—but the key feature asked here isnonrepudiation: the signer cannot plausibly deny having signed the message, assuming private keys are properly protected. Biometrics are unrelated to digital signatures; authentication may be biometric at login, but the signature mechanism is cryptographic. The signature is not necessarily “constant over time†because signatures differ with different messages and may rely on different hash algorithms across periods. Custody of the signature is not limited to the receiver; any verifier with the signer’s public key can validate it. Nonrepudiation is therefore the best and most precise control objective associated with digital signatures in insecure networks.
[Reference:CRISC Review Manual – Risk Response and Mitigation (security controls; cryptographic controls and nonrepudiation)., ===========, ]
Question # 176
The PRIMARY reason for a risk practitioner to review business processes is to:
A.
Benchmark against peer organizations.
B.
Identify appropriate controls within business processes.
C.
Assess compliance with global standards.
D.
Identify risk owners related to business processes.
Full Access
Answer:
D
Explanation:
A review of business processes is crucial for identifying risk owners, as risk ownership is tied to specific processes within the organization. Risk owners are accountable for managing and mitigating risks within their respective areas. This ensures that risks are effectively addressed where they arise and aligns mitigation efforts with business objectives. Properly identifying risk owners supports better governance, accountability, and alignment with the organization ' s risk management strategy.
Question # 177
Which of the following would be a risk practitioner ' s BEST course of action when a project team has accepted a risk outside the established risk appetite?
A.
Reject the risk acceptance and require mitigating controls.
B.
Monitor the residual risk level of the accepted risk.
C.
Escalate the risk decision to the project sponsor for review.
D.
Document the risk decision in the project risk register.
Full Access
Answer:
C
Explanation:
 Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite can be expressed in qualitative or quantitative terms, and can vary depending on the context and the stakeholder. Risk appetite should be defined and communicated by the senior management or the board of directors, and should guide the risk management decisions and actions throughout the organization. When a project team has accepted a risk outside the established risk appetite, the risk practitioner’s best course of action is to escalate the risk decision to the project sponsor for review, meaning that the risk practitioner should report the risk acceptance and its rationale to the project sponsor, who is the person or group that provides the resources and support for the project, and is accountable for its success. The project sponsor should review the risk decision and determine whether it is aligned with the organization’s objectives and strategy, and whether it requires any further approval oraction. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.1, p. 25-26
Question # 178
Well-developed, data-driven risk measurements should be:
A.
reflective of the lowest organizational level.
B.
a data feed taken directly from operational production systems.
C.
reported to management the same day data is collected.
D.
focused on providing a forward-looking view.
Full Access
Answer:
D
Explanation:
Well-developed, data-driven risk measurements should be focused on providing a forward-looking view, as they enable the organization to anticipate and prepare for the potential changes and impacts of the risk level and exposure, and to take proactive and appropriate actions toaddress the risk. The other options are not the characteristics of well-developed, data-driven risk measurements, as they may not reflect the strategic, comprehensive, or timely aspects of the risk measurements, respectively. References = CRISC Review Manual, 7th Edition, page 110.
Question # 179
Which of the following activities BEST facilitates effective risk management throughout the organization?
A.
Reviewing risk-related process documentation
B.
Conducting periodic risk assessments
C.
Performing a business impact analysis (BIA)
D.
Performing frequent audits
Full Access
Answer:
B
Explanation:
Risk management is the process of identifying, analyzing, evaluating, treating, monitoring, and communicating the risks that may affect the achievement of an organization’s objectives. The activity that best facilitates effective risk management throughout the organization is conducting periodic risk assessments, which are the systematic and structured methods of identifying and analyzing the potential sources and consequences of risk events. By conducting periodic risk assessments, an organization can proactively identify and prioritize the risks that pose the greatest threat or opportunity, and implement theappropriate risk responses to optimize the risk exposure and align it with the risk appetite and tolerance. References = CRISC Review Manual, 7th Edition, page 63.
Question # 180
Which of the following is the BEST time for an enterprise project management team to use risk analysis?
A.
When the final testing phase begins
B.
During the project initiation phase
C.
At the end of the project
D.
During business impact analysis (BIA)
Full Access
Answer:
B
Question # 181
Which of the following is MOST important when defining controls?
A.
Identifying monitoring mechanisms
B.
Including them in the risk register
C.
Aligning them with business objectives
D.
Prototyping compensating controls
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual1, controls are the policies, procedures, practices, and organizational structures that are designed and implemented to manage risk. The most important factor when defining controls is to align them with the business objectives, as this helps to ensure that the controls support the achievement of the organization’s strategy, goals, and values. Aligning controls with business objectives also helps to optimize the benefits and costs of controls, and to prioritize and allocate resources for control implementation and maintenance. References = CRISC Review Manual1, page 202.
Question # 182
Which of the following is the MOST significant risk related to an organization ' s use of AI technology?
A.
The AI system ' s contract does not include a right-to-audit clause
B.
The AI system is being used beyond its intended purpose
C.
The AI system is on unsupported infrastructure
D.
The AI system results have not been validated
Full Access
Answer:
D
Explanation:
Unvalidated AI outputs pose considerable integrity and operational risks, potentially leading to erroneous decisions or compliance lapses. ISACA CRISC guidance underscores that ensuring results validity is a highest-priority control for new technologies such as AI.
Question # 183
A recent risk workshop has identified risk owners and responses for newly identified risk scenarios. Which of the following should be the risk practitioner s NEXT step? r
A.
Prepare a business case for the response options.
B.
Identify resources for implementing responses.
C.
Develop a mechanism for monitoring residual risk.
D.
Update the risk register with the results.
Full Access
Answer:
D
Explanation:
The risk practitioner’s next step after identifying risk owners and responses for newly identified risk scenarios in a recent risk workshop is to update the risk register with the results, as it involves documenting and communicating the risk information and decisions, and maintaining the accuracy and completeness of the risk register. Preparing a business case for the response options, identifying resources for implementing responses, and developing a mechanism for monitoring residual risk are possible steps, but they are not the next step, as they require the prior update of the risk register with the new risk information and decisions. References = CRISC Review Manual, 7th Edition, page 109.
Question # 184
An organization ' s control environment is MOST effective when:
A.
controls perform as intended.
B.
controls operate efficiently.
C.
controls are implemented consistent
D.
control designs are reviewed periodically
Full Access
Answer:
A
Explanation:
 The control environment is the set of standards, processes, and structures that provide the basis for carrying out internal control across the organization. The control environment is most effective when the controls perform as intended, meaning that they achieve their objectives, mitigate the risks, and comply with the policies and regulations. The other options are desirable attributes of the controls, but they do not necessarily indicate the effectiveness of the control environment. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: IT Control Assessment, page 69.
Question # 185
Which of the following roles should be assigned accountability for monitoring risk levels?
A.
Risk practitioner
B.
Business manager
C.
Risk owner
D.
Control owner
Full Access
Answer:
C
Explanation:
 The risk owner should be assigned accountability for monitoring risk levels, as they have the authority and responsibility to manage the risk and its associated controls, and to report on the risk status and performance. The risk practitioner, the business manager, and the control owner are not the best choices, as they have different roles and responsibilities related to risk identification, assessment, response, and reporting, but they are not accountable for the risk and its monitoring. References = CRISC Review Manual, 7th Edition, page 101.
Question # 186
Which of me following is MOST helpful to mitigate the risk associated with an application under development not meeting business objectives?
A.
Identifying tweets that may compromise enterprise architecture (EA)
B.
Including diverse Business scenarios in user acceptance testing (UAT)
C.
Performing risk assessments during the business case development stage
D.
Including key stakeholders in review of user requirements
Full Access
Answer:
D
Explanation:
The most helpful way to mitigate the risk associated with an application under development not meeting business objectives is to include key stakeholders in the review of user requirements, because this ensures that the application is designed and developed according to the needs and expectations of the end users and the business owners. Including key stakeholders in the review of user requirements also helps to avoid scope creep, requirement changes, or miscommunication that may affect the quality, functionality, or usability of the application. The other options are not the most helpful ways to mitigate the risk, although they may also be useful in reducing the likelihood or impact of the risk. Identifying threats that may compromise enterprise architecture (EA), including diverse business scenarios in user acceptance testing (UAT), and performing risk assessments during the business case development stage are examples of preventive or detective controls that aim to identify and address the potential issues or problems that may arise during the application development process, but they do not address the alignment of the applicationwith the business objectives. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 187
Which of the following will BEST mitigate the risk associated with IT and business misalignment?
A.
Establishing business key performance indicators (KPIs)
B.
Introducing an established framework for IT architecture
C.
Establishing key risk indicators (KRIs)
D.
Involving the business process owner in IT strategy
Full Access
Answer:
D
Explanation:
IT and business misalignment is the risk that the IT objectives, plans, and activities are not aligned with the business goals, needs, and expectations. This can result in wasted resources, missed opportunities, poor performance, and customer dissatisfaction. One of the best ways to mitigate this risk is to involve the business process owner in IT strategy. The business process owner is the person who has the authority and responsibility for a specific business process and its outcomes. By involving the business process owner in IT strategy, the organization can ensure that the IT initiatives and solutions are relevant, effective, and beneficial for the business process and its stakeholders. The business process owner can also provide valuable input, feedback, and support for the IT strategy and its implementation. The other options are not the best ways to mitigate the risk associated with IT and business misalignment, although they may be helpful and complementary. Establishing business key performance indicators (KPIs) is a technique to measure and monitor the achievement of business objectives and outcomes. However, KPIs do not necessarily ensure that the IT strategy is aligned with the business strategy or that the IT activities support the business activities. Introducing an established framework for IT architecture is a method to design and implement the IT infrastructure, systems, and services in a consistent and coherent manner. However, an IT architecture framework does not guarantee that the IT architecture is aligned with the business architecture or that the IT capabilities meet the business requirements. Establishing key risk indicators (KRIs) is a tool to monitor and communicate the level of exposure to a given risk or the potential impact of a risk. However, KRIs do not directly address the risk of IT and business misalignment or the actions needed to align them. References = CRISC Review Manual, pages 22-231; CRISC Review Questions, Answers & Explanations Manual, page 76
Question # 188
Which of the following provides The MOST useful information when determining a risk management program ' s maturity level?
A.
Risk assessment results
B.
A recently reviewed risk register
C.
Key performance indicators (KPIs)
D.
The organization ' s risk framework
Full Access
Answer:
C
Explanation:
Key performance indicators (KPIs) are measurable values that demonstrate how effectively an organization is achieving its key objectives. KPIs can be used to evaluate the progress and performance of a risk management program, as well as to identify the areas for improvement and alignment with the organization’s strategy. KPIs can provide the most useful information when determining a risk management program’s maturity level, because they can reflect the extent to which the program is integrated, consistent, proactive, and value-adding. KPIs can also be compared with industry benchmarks or best practices to assess the program’s maturity level relative to other organizations. The other options are not as useful as KPIs, because they do not provide a clear and comprehensive picture of the risk management program’s maturity level, but rather focus on specific aspects or outputs of the program. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, page 18.
Question # 189
An organization is reviewing a contract for a Software as a Service (SaaS) sales application with a 99.9% uptime service level agreement (SLA). Which of the following BEST describes ownership of availability risk?
A.
The risk is shared by both organizations.
B.
The liability for the risk is owned by the cloud provider.
C.
The risk is transferred to the cloud provider.
D.
The liability for the risk is owned by the sales department.
Full Access
Answer:
A
Explanation:
Even with SLAs in place, both parties must manage aspects of availability risk. The provider manages infrastructure, while the organization is responsible for business impact.
[Reference:CRISC Manual – Domain 1: Governance, Slide 41, 268, , , , ]
Question # 190
An organization has identified that terminated employee accounts are not disabled or deleted within the time required by corporate policy. Unsure of the reason, the organization has decided to monitor the situation for three months to obtain more information. As a result of this decision, the risk has been:
A.
avoided.
B.
accepted.
C.
mitigated.
D.
transferred.
Full Access
Answer:
B
Explanation:
 Risk acceptance is a risk response strategy that involves acknowledging the existence and potential impact of a risk, but deciding not to take any action to reduce or eliminate it. Risk acceptance can be appropriate when the cost or effort of implementing a risk response outweighs the benefit, or when there are no feasible or effective risk responses available. An organization has identified that terminated employee accounts are not disabled or deleted within the time required by corporate policy, which poses a security risk to the organization. The organization is unsure of the reason for this issue, and has decided to monitor the situation for three months to obtain more information, rather than taking any immediate action to resolve the issue. As a result of this decision, the risk has been accepted, as the organization has chosen to tolerate the risk exposure for a certain period of time, and has not implemented any controls or measures to prevent or reduce the risk occurrence or impact. References = Risk Response Strategies: Avoid, Transfer, Mitigate, Accept, Risk Response Strategies: What They Are and How to Use Them, Risk Response Strategy: Definition, Types, and Examples.
Question # 191
When classifying and prioritizing risk responses, the areas to address FIRST are those with:
A.
low cost effectiveness ratios and high risk levels
B.
high cost effectiveness ratios and low risk levels.
C.
high cost effectiveness ratios and high risk levels
D.
low cost effectiveness ratios and low risk levels.
Full Access
Answer:
C
Explanation:
 The areas to address first when classifying and prioritizing risk responses are those with high cost effectiveness ratios and high risk levels, as they represent the most optimal and urgent risk responses that can reduce the risk exposure and impact significantly with a reasonable cost. Theother options are not the areas to address first, as they may indicate suboptimal or less urgent risk responses that may not align with the risk tolerance and appetite of the organization. References = CRISC Review Manual, 7th Edition, page 109.
Question # 192
Which of the following conditions presents the GREATEST risk to an application?
A.
Application controls are manual.
B.
Application development is outsourced.
C.
Source code is escrowed.
D.
Developers have access to production environment.
Full Access
Answer:
D
Explanation:
 The production environment is the environment where the application is deployed and used by the end users. The production environment should be protected from unauthorized or unintended changes that could compromise the availability, integrity, or confidentiality of the application and its data. Developers have access to the production environment presents the greatest risk to an application, as it could allow them tobypass the change management process, introduce errors or vulnerabilities, or manipulate the application or its data for malicious purposes. The other options are not as risky as developers having access to the production environment, as they involve different aspects of the application lifecycle:
Application controls are manual means that the application relies on human intervention to perform some functions or validations, such as data entry, reconciliation, or authorization. This could increase the risk of human error, fraud, or inefficiency, but it does not directly affect the production environment.
Application development is outsourced means that the application is developed by a third party, such as a vendor or a contractor. This could increase the risk of quality issues, contractual disputes, or intellectual property rights, but it does not directly affect the production environment.
Source code is escrowed means that the source code of the application is deposited with a trusted third party, such as a lawyer or a bank. This could provide assurance and continuity in case the original developer is unable or unwilling to maintain or support the application, but it does not directly affect the production environment. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.1.1.1, pp. 144-145.
Question # 193
Which of the following describes the relationship between Key risk indicators (KRIs) and key control indicators (KCIS)?
A.
KCIs are independent from KRIs KRIs.
B.
KCIs and KRIs help in determining risk appetite.
C.
KCIs are defined using data from KRIs.
D.
KCIs provide input for KRIs
Full Access
Answer:
D
Explanation:
Key risk indicators (KRIs) are metrics that provide information on the level of exposure to a given risk. Key control indicators (KCIs) are metrics that measure the performance or effectiveness of a control in mitigating a risk. KCIs provide input for KRIs, because they help to assess the residual risk after applying the control. For example, if the KRI is the number of security incidents, and the KCI is the percentage of incidents detected by the intrusion prevention system (IPS), then the KCI provides input for the KRI by showing how well the IPS is reducing the risk of security breaches. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 194
An organization moved its payroll system to a Software as a Service (SaaS) application. A new data privacy regulation stipulates that data can only be processed within the countrywhere it is collected. Which of the following should be done FIRST when addressing this situation?
A.
Analyze data protection methods.
B.
Understand data flows.
C.
Include a right-to-audit clause.
D.
Implement strong access controls.
Full Access
Answer:
B
Explanation:
The first step when addressing the situation of moving the payroll system to a SaaS application and complying with the new data privacy regulation is to understand the data flows. This means identifying where the data is collected, stored, processed, and transferred, and who has access to it. Understanding the data flows can help to determine the scope and impact of the regulation, as well as the potential risks and gaps in the current state. It can also help to identify the roles and responsibilities of the organization and the SaaS provider regarding data protection and compliance. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.1.2, p. 237-238
Question # 195
What is the BEST course of action when the business impact of a risk event is rated high, but the likelihood of risk materialization has decreased?
A.
Adjust risk tolerance thresholds.
B.
Adjust the associated key risk indicator (KRI).
C.
Further mitigate the risk.
D.
Accept the risk if within tolerance.
Full Access
Answer:
D
Explanation:
The correct answer isDbecause even though thebusiness impact remains high, thelikelihood has decreased, so the overall risk may now fall within acceptable tolerance. In CRISC, the appropriate course of action is to compare the resulting risk level against appetite and tolerance. If the residual exposure is now acceptable, the organization may accept the risk.
The other options are less appropriate:
A. Adjust risk tolerance thresholdsshould not be done simply because one risk has changed.
B. Adjust the associated key risk indicator (KRI)may be considered later if monitoring needs refinement, but it is not the primary action.
C. Further mitigate the riskmay be unnecessary if the risk is already within tolerance.
Exact Extracts supporting the answer:
“It is most important to reduce risk to a level that the enterprise is willing to accept when defining risk management strategies.â€
“Residual risk is best reflected as risk remaining after the implementation of new or enhanced controls.â€
“Acceptable risk for an enterprise is achieved when residual risk is within tolerance levels.â€
“The risk treatment plan should be developed when risk levels exceed risk appetite or tolerance.â€
These extracts support that the decision should be based on whether the remaining risk is within tolerance. If it is, the best course is toaccept the risk.
Question # 196
Which of the following is the BEST recommendation to senior management when the results of a risk and control assessment indicate a risk scenario can only be partially mitigated?
A.
Implement controls to bring the risk to a level within appetite and accept the residual risk.
B.
Implement a key performance indicator (KPI) to monitor the existing control performance.
C.
Accept the residual risk in its entirety and obtain executive management approval.
D.
Separate the risk into multiple components and avoid the risk components that cannot be mitigated.
Full Access
Answer:
A
Explanation:
 Implementing controls to bring the risk to a level within appetite and accept the residual risk is the best recommendation to senior management when the results of a risk and control assessment indicate a risk scenario can only be partially mitigated, as it helps to balance the costs and benefits of the risk management and control processes, and to align them with the organizational strategy and objectives. A risk and control assessment is a process of identifying, analyzing, and evaluating the risks and controls associated with a specific activity, process, or objective. A risk scenario is a description of a possible event or situation that could cause harm or loss to the organization or its stakeholders. A risk scenario can only be partially mitigated when the existing or proposed controls are not sufficient or effective to reduce the risk to an acceptable level. A risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. A residual risk is the risk that remains after the implementation of controls or risk treatments.
Implementing controls to bring the risk to a level within appetite and accept the residual risk helps to provide the following benefits:
It enables a data-driven and evidence-based approach to risk management and reporting, rather than relying on subjective or qualitative judgments.
It facilitates a consistent and standardized way of measuring and communicating risk levels and exposure across the organization and to the external stakeholders.
It supports the development and implementation of effective and efficient risk response and mitigation strategies and actions that are aligned with the business risk appetite and objectives.
It provides feedback and learning opportunities for the risk management and control processes, and helps to foster a culture of continuous improvement and innovation.
The other options are not the best recommendations to senior management when the results of a risk and control assessment indicate a risk scenario can only be partially mitigated. Implementing a key performance indicator (KPI) to monitor the existing control performance is a useful method to measure and monitor the effectiveness and efficiency of the controls, but it does not address the residual risk or the risk appetite. Accepting the residual risk in its entirety andobtaining executive management approval is a possible option to deal with the risk scenario, but it may expose the organization to excessive or unacceptable risk, and it may not comply with the legal or regulatory obligations or requirements. Separating the risk into multiple components and avoiding the risk components that cannot be mitigated is a possible option to deal with the risk scenario, but it may not be feasible or practical, and it may create new or additional risks or challenges. References = Risk and Control Self-Assessment (RCSA) - Management Study Guide, IT Risk Resources | ISACA, Risk Mitigation: What It Is and How to Implement It (Free Templates …
Question # 197
A large organization recently restructured the IT department and has decided to outsource certain functions. What action should the control owners in the IT department take?
A.
Conduct risk classification for associated IT controls.
B.
Determine whether risk responses still effectively address risk.
C.
Perform vulnerability and threat assessments.
D.
Analyze and update IT control assessments.
Full Access
Answer:
B
Explanation:
According to the ISACA Risk and Information Systems Control study guide and handbook, the control owners in the IT department should determine whether risk responses still effectively address risk after a restructuring and outsourcing of certain functions. This is because the restructuring and outsourcing may have changed the risk profile, the control environment, and the control activities of the IT department. The control owners should review the existing risk responses and evaluate if they are still appropriate, adequate, and efficient in mitigating the risks associated with the outsourced functions. The control owners should also monitor the performance and compliance of the service providers and ensure that the contractual obligations and service level agreements are met12
1: ISACA Risk and Information Systems Control Study Guide, 4th Edition, page 33 2: ISACA Risk and Information Systems Control Handbook, 1st Edition, page 25
Question # 198
Which of the following provides the MOST useful information when developing a risk profile for management approval?
A.
Residual risk and risk appetite
B.
Strength of detective and preventative controls
C.
Effectiveness and efficiency of controls
D.
Inherent risk and risk tolerance
Full Access
Answer:
A
Explanation:
A risk profile is a summary of the key risks that an organization faces, along with the corresponding risk responses, risk owners, and risk indicators1. A risk profile is a useful tool for communicating and reporting the risk status and performance to the management and other stakeholders2. When developing a risk profile for management approval, the most useful information to include is the residual risk and the risk appetite, because:
Residual risk is the level of risk that remains after the implementation of risk responses3. It indicates the degree of exposure or uncertainty that the organization still faces, and the potential impact or consequences of the risk events. Residual risk helps the management to evaluate the effectiveness and adequacy of the risk responses, and to decide whether to accept, reduce, transfer, or avoid the risk4.
Risk appetite is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives5. It reflects the organization’s risk culture, strategy, and priorities, and provides a basis for setting risk thresholds and targets. Risk appetite helps the management to align the risk profile with the organizational goals and values, and to ensure that the risk responses are consistent and proportional to the risk level6.
The other options are not the most useful information when developing a risk profile for management approval, because:
Strength of detective and preventative controls is a measure of how well the controls can identify or prevent the occurrence or impact of the risk events7. It is a part of the risk response information, but it does not provide a comprehensive or holistic view of the risk profile. It does not show the residual risk or the risk appetite, which are more relevant and important for the management approval.
Effectiveness and efficiency of controls is a measure of how well the controls achieve their intended objectives and how well they use the available resources8. It is a part of the risk performance information, but it does not provide a complete or balanced view of the risk profile.It does not show the residual risk or the risk appetite, which are more significant and meaningful for the management approval.
Inherent risk and risk tolerance are related but different concepts from residual risk and risk appetite. Inherent risk is the level of risk that exists before the implementation of risk responses3. Risk tolerance is the acceptable variation or deviation from the risk appetite or the risk objectives5. They are useful for the risk assessment and analysis, but they do not provide the current or desired state of the risk profile. They do not show the residual risk or the risk appetite, which are more critical and valuable for the management approval.
References =
Risk Profile - CIO Wiki
Risk Profile: Definition, Example, and How to Create One
Residual Risk - CIO Wiki
What is Residual Risk? - Definition from Techopedia
Risk Appetite - CIO Wiki
Risk Appetite: What It Is and Why It Matters - Gartner
Preventive and Detective Controls - CIO Wiki
Control Effectiveness and Efficiency - CIO Wiki
Question # 199
Which of the following should be a risk practitioner ' s NEXT action after identifying a high probability of data loss in a system?
A.
Enhance the security awareness program.
B.
Increase the frequency of incident reporting.
C.
Purchase cyber insurance from a third party.
D.
Conduct a control assessment.
Full Access
Answer:
D
Explanation:
A control assessment is the process of evaluating the design and effectiveness of controls that are implemented to mitigate risks. A control assessment can help identify the root causes of data loss, thegaps in the existing controls, and the potential solutions to improve the control environment. A control assessment should be conducted after identifying a high probability of data loss in a system, as it can provide valuable information for risk response and reporting. References = Risk and Information Systems Control Study Manual, Chapter 3: Risk Response and Mitigation, Section 3.2: Control Assessment, p. 147-149.
Question # 200
Which of the following would BEST help an enterprise prioritize risk scenarios?
A.
Industry best practices
B.
Placement on the risk map
C.
Degree of variances in the risk
D.
Cost of risk mitigation
Full Access
Answer:
B
Explanation:
A risk map, also known as a risk heat map, is a visual tool that helps an enterprise prioritize risk scenarios by plotting them on a matrix based on their likelihood and impact. A risk map can help to compare and contrast different risk scenarios, as well as to identify the most critical and urgent risks that require attention. A risk map can also help to communicate and report the risk profile and status to the stakeholders and decision makers. Therefore, the placement on the risk map would best help an enterprise prioritize risk scenarios. The other options are not the best ways to help an enterprise prioritize risk scenarios, although they may be relevant and useful. Industry best practices are the standards or guidelines that are widely accepted and followed by the organizations in a specific industry or domain. Industry best practices can help to benchmark and improve the risk management process and performance, but they may not reflect the specific risk context and needs of the enterprise. Degree of variances in the risk is the measure of the variability or uncertainty of the risk, which may affect the accuracy or reliability of the risk assessment and response. Degree of variances in the risk can help to adjust and refine the risk analysis and treatment, but it may not indicate the priority or importance of the risk. Cost of risk mitigation is the amount of resources or expenses that are required or allocated to implement the risk response actions, such as avoiding, transferring, mitigating, or accepting the risk. Cost of risk mitigation can help to evaluate and optimize therisk response options, but it may not determine the priority or urgency of the risk. References = CRISC Review Manual, pages 38-391; CRISC Review Questions, Answers & Explanations Manual, page 892
Question # 201
Which of the following is the PRIMARY factor in determining a recovery time objective (RTO)?
A.
Cost of offsite backup premises
B.
Cost of downtime due to a disaster
C.
Cost of testing the business continuity plan
D.
Response time of the emergency action plan
Full Access
Answer:
B
Explanation:
A recovery time objective (RTO) is the maximum acceptable time or duration that a business process or function can be disrupted or unavailable due to a disaster or incident, before it causes unacceptable or intolerable consequences for the organization. It is usually expressed in hours, days, or weeks, and it is aligned with the organization’s business continuity and disaster recovery objectives and requirements.
The primary factor in determining a RTO is the cost of downtime due to a disaster, which is the estimated loss or damage that the organization may suffer if a business process or function is disrupted or unavailable for a certain period of time. The cost of downtime can be expressed in terms of financial, operational, reputational, or legal consequences, and it can help the organization to assess the impact and urgency of the disaster, and to decide on the appropriate recovery strategy and resources.
The other options are not the primary factors in determining a RTO, because they do not address the fundamental question of how long the organization can tolerate the disruption or unavailability of a business process or function.
The cost of offsite backup premises is the cost of acquiring, maintaining, or using an alternative or secondary location or facility that can be used to resume or continue the business process or function in case of a disaster or incident. The cost of offsite backup premises is important to consider when selecting or implementing a recovery strategy, but it is not the primary factor in determining a RTO, because it does not indicate the impact or urgency of the disaster, and it may not reflect the organization’s business continuity and disaster recovery objectives and requirements.
The cost of testing the business continuity plan is the cost of conducting, evaluating, or improving the tests or exercises that are performed to verify or validate the effectiveness and efficiency of the business continuity plan, which is the document that describes the actions and procedures that the organization will take to recover or restore the business process or function in case of a disaster or incident. The cost of testing the business continuity plan is important to consider when developing or updating the business continuity plan, but it is not the primary factor in determining a RTO, because it does not indicate the impact or urgency of the disaster, and it may not reflect the organization’s business continuity and disaster recovery objectives and requirements.
The response time of the emergency action plan is the time or duration that it takes for the organization to initiate or execute the emergency action plan, which is the document that describes the immediate actions and procedures that the organization will take to protect the life, health, and safety of the people, and to minimize the damage or loss of the assets,in case of adisaster or incident. The response time of the emergency action plan is important to consider when preparing or reviewing the emergency action plan, but it is not the primary factor in determining a RTO, because it does not indicate the impact or urgency of the disaster, and it may not reflect the organization’s business continuity and disaster recovery objectives and requirements. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 62-63, 66-67, 70-71, 74-75, 78-79
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 165
CRISC Practice Quiz and Exam Prep
Question # 202
Which of the following is MOST important when developing key performance indicators (KPIs)?
A.
Alignment to risk responses
B.
Alignment to management reports
C.
Alerts when risk thresholds are reached
D.
Identification of trends
Full Access
Answer:
A
Explanation:
Key performance indicators (KPIs) are quantifiable measures of progress toward an intended result, such as a strategic objective or a desired outcome12.
The most important factor when developing KPIs is the alignment to risk responses, which are the actions taken to address the risks that may affect the achievement of the intended result12.
Alignment to risk responses means that the KPIs should reflect the effectiveness and efficiency of the risk responses, and provide feedback and guidance for improving the risk responses12.
Alignment to risk responses also means that the KPIs should be consistent and compatible with the risk responses, and support the risk management process and objectives12.
The other options are not the most important factor, but rather possible aspects or features of KPIs that may vary depending on the context and purpose of the KPIs. For example:
Alignment to management reports is an aspect of KPIs that relates to the communication and presentation of the KPIs to the relevant stakeholders, such as senior management,board members, or external parties12. However, this aspect does not determine the quality or validity of the KPIs, or the alignment to the intended result12.
Alerts when risk thresholds are reached is a feature of KPIs that relates to the monitoring and control of the KPIs, and the triggering of actions or decisions when the KPIs exceed or fall below a certain level or range12. However, this feature does not define the content or scope of the KPIs, or the alignment to the intended result12.
Identification of trends is a feature of KPIs that relates to the analysis and interpretation of the KPIs, and the identification of patterns or changes in the KPIs over time or across different dimensions12. However, this feature does not specify the criteria or methodology of the KPIs, or the alignment to the intended result12. References =
1: What is a Key Performance Indicator (KPI)? Guide & Examples - Qlik3
2: What is a Key Performance Indicator (KPI)? - KPI.org4
Question # 203
Which of the following should be the risk practitioner ' s FIRST course of action when an organization plans to adopt a cloud computing strategy?
A.
Request a budget for implementation
B.
Conduct a threat analysis.
C.
Create a cloud computing policy.
D.
Perform a controls assessment.
Full Access
Answer:
C
Question # 204
Which of the following is the BEST key performance indicator (KPI) for determining how well an IT policy is aligned to business requirements?
A.
Total cost to support the policy
B.
Number of exceptions to the policy
C.
Total cost of policy breaches
D.
Number of inquiries regarding the policy
Full Access
Answer:
B
Explanation:
An IT policy is a document that defines the rules, standards, and procedures for the use, management, and security of IT resources within an organization. An IT policy should be aligned to the business requirements, which are the needs, expectations, and objectives of the business stakeholders, such as customers, employees, managers, partners, regulators, etc. An IT policy that is aligned to the business requirements can help support the business strategy, improve the business performance, and enhance the business value. A key performance indicator (KPI) is a metric that measures the achievement of a specific goal or objective. A KPI should be relevant, measurable, achievable, realistic, and time-bound. The best KPI for determining how well an IT policy is aligned to the business requirements is the number of exceptions to the policy. An exception to the policy is a deviation or violation of the policy rules, standards, or procedures, which may be intentional or unintentional, authorized or unauthorized, justified or unjustified. The number of exceptions to the policy can indicate how well the policy is understood, communicated, implemented, and enforced within the organization. The number of exceptions to the policy can also indicate how well the policy reflects the current and future business needs and expectations, and how flexible and adaptable the policy is to the changing business environment. A low number of exceptions to the policy can suggest that the policy is well aligned to the business requirements, while a high number of exceptions to the policy can suggest that the policy is misaligned or outdated, and may need to be reviewed or revised. References = Key Performance Indicator (KPI): Definition, Types, andExamples, Business KPIs: 5 important characteristics to be effective, What is a KPI? How To Choose the Best KPIs for Your Business - HubSpot Blog.
Question # 205
Which of the following is the MOST useful information for a risk practitioner when planning response activities after risk identification?
A.
Risk register
B.
Risk appetite
C.
Risk priorities
D.
Risk heat maps
Full Access
Answer:
C
Explanation:
The most useful information for a risk practitioner when planning response activities after risk identification is the risk priorities. Risk priorities are the order or ranking of the risks based on their level of importance or urgency. Risk priorities help the risk practitioner to focus on the most critical risks, and allocate the resources and efforts accordingly. Risk priorities are usuallydetermined by using a combination of factors, such as the likelihood and impact of the risks, the risk appetite and tolerance of the organization, and the cost and benefit of the risk responses. Theother options are not as useful as the risk priorities, although they may provide some input or context for the risk response planning. The risk register is the document that records the details of all identified risks, but it does not necessarily indicate the risk priorities. The risk appetite is the amount and type of risk that the organization is willing to pursue, retain, or take, but it does not specify the risk priorities. The risk heat maps are graphical tools that display the risk level of each risk based on the likelihood and impact, but they do not show the risk priorities. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Question # 206
Which of the following is the MOST important objective of an enterprise risk management (ERM) program?
A.
To create a complete repository of risk to the organization
B.
To create a comprehensive view of critical risk to the organization
C.
To provide a bottom-up view of the most significant risk scenarios
D.
To optimize costs of managing risk scenarios in the organization
Full Access
Answer:
B
Explanation:
The most important objective of an enterprise risk management (ERM) program is to create a comprehensive view of critical risk to the organization, as it enables the organization to identify, assess, and prioritize the key risks that may affect its objectives and strategy, and to implement appropriate risk responses and controls. A comprehensive view of critical risk also helps the organization to align its risk appetite and tolerance with its business goals and value creation, and to enhance its risk culture and governance. A comprehensive view of critical risk can be achieved by integrating risk management across all levels and functions of the organization, and by using consistent and reliable risk information and reporting. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 242. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 242. CRISC Sample Questions 2024, Question 242.
Question # 207
A risk practitioner is developing a set of bottom-up IT risk scenarios. The MOST important time to involve business stakeholders is when:
A.
updating the risk register.
B.
validating the risk scenarios.
C.
documenting the risk scenarios.
D.
identifying risk mitigation controls.
Full Access
Answer:
B
Explanation:
According to the CRISC Review Manual, the most important time to involve business stakeholders in the development of bottom-up IT risk scenarios is when validating the risk scenarios, as they can provide valuable input on the relevance, completeness, and accuracy of the scenarios and their impact on the business objectives and processes2
1: CRISC Review Questions, Answers & Explanations Database, Question ID: 100001 2: CRISC Review Manual, 7th Edition, page 97
Question # 208
Which of the following provides the MOST insight regarding an organization ' s risk culture?
A.
Awareness training participation rate
B.
Risk assessment results
C.
Senior management interviews
D.
Risk management framework
Full Access
Answer:
C
Explanation:
Risk culture reflects how leadership and staff actually perceive, discuss, and act on risk. CRISC emphasizes tone at the top, decision-making behavior, openness to reporting issues, and integration of risk considerations into strategic choices as key indicators of culture.Senior management interviewsreveal these aspects directly—how leaders prioritize risk, how they respond to bad news, and whether risk considerations are embedded in planning and performance expectations. Training participation rates show awareness activity but not necessarily attitudes or behavior change. Risk assessment results are more about the organization’s risk profile than underlying culture. A documented risk management framework is a formal structure; it may be well designed but not actually lived. Interviews with senior leadership provide qualitative but rich insight into whether the framework and policies are truly influencing behavior.
[Reference:CRISC Review Manual – Governance domain (risk culture and tone at the top)., ===========, ]
Question # 209
Using key risk indicators (KRIs) to illustrate changes in the risk profile PRIMARILY helps to:
A.
communicate risk trends to stakeholders.
B.
assign ownership of emerging risk scenarios.
C.
highlight noncompliance with the risk policy
D.
identify threats to emerging technologies.
Full Access
Answer:
A
Explanation:
 The primary purpose of using key risk indicators (KRIs) to illustrate changes in the risk profile is to communicate risk trends to stakeholders. KRIs are metrics that provide an early warning of increasing risk exposure in various areas of the organization. By using KRIs to illustrate changes in the risk profile, the organization can communicate the risk trends to the stakeholders, such as the board, senior management, business units, and external parties, and enable them to take appropriate actions to manage the risk. Assigning ownership of emerging risk scenarios, highlighting noncompliance with the risk policy, and identifying threats to emerging technologies are other possible purposes, but they are not as important as communicating risk trends to stakeholders. References = ISACA Certified in Risk and Information Systems Control(CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
Question # 210
A risk practitioner discovers that an IT operations team manager bypassed web filtering controls by using a mobile device, in violation of the network security policy. Which of the following should the risk practitioner do FIRST?
A.
Report the incident.
B.
Plan a security awareness session.
C.
Assess the new risk.
D.
Update the risk register.
Full Access
Answer:
A
Explanation:
According to the CRISC exam content outline2, one of the tasks of a risk practitioner is to “report on risk, in line with organizational reporting requirements, to enable decision making andescalationâ€. Therefore, the first thing that the risk practitioner should do after discovering apolicy violation is to report the incident to the appropriate authority, such as the IT security manager or the risk management committee. This will ensurethat the incident is properly documented, investigated, and resolved, and that any potential impact or consequences are minimized.
The other options are not the first actions that the risk practitioner should take. Planning a security awareness session (B) may be a preventive measure to avoid future incidents, but it does not address the current one. Assessing the new risk © may be part of the risk response process, but it should be done after reporting the incident and gathering more information. Updating the risk register (D) may be a result of the risk assessment and response, but it should not be done before reporting the incident and following the organizational procedures.
Question # 211
Which of the following will BEST help ensure that risk factors identified during an information systems review are addressed?
A.
Informing business process owners of the risk
B.
Reviewing and updating the risk register
C.
Assigning action items and deadlines to specific individuals
D.
Implementing new control technologies
Full Access
Answer:
C
Explanation:
A risk factor is a condition or event that may increase the likelihood or impact of a risk, which is the effect of uncertainty on objectives1. An information systems review is a process that involves examining and evaluating the adequacy and effectiveness of the information systems and their related controls, policies, and procedures2. The purpose of an information systems review is to identify and report the risk factors that may affect the confidentiality, integrity, availability, and performance of the information systems and their outputs3. The best way to ensure that the risk factors identified during an information systems review are addressed is to assign action items and deadlines to specific individuals, who are responsible and accountable for implementing the appropriate risk responses. A risk response is an action taken or plannedto mitigate or eliminate the risk, such as avoiding, transferring, reducing, or accepting the risk4. By assigning action items and deadlines to specific individuals, the organization can ensure that the risk factors are properly and promptly addressed, and that the progress and results of the risk responses are monitored and reported5. Informing business process owners of the risk, reviewing and updating the risk register, and implementing new control technologies are not the best ways to ensure that the risk factors identified during an information systems review are addressed, as they do not provide the same level of accountability and effectiveness as assigning action items anddeadlines to specific individuals. Informing business process owners of the risk is a process that involves communicating and sharing the risk information with the persons who have the authority and accountability for a business process that is supported or enabled by the information systems6. Informing business process owners of the risk can help to raise their awareness and understanding of the risk, but it does not ensure that they will take the necessary actions to address the risk. Reviewing and updating the risk register is a process that involves checking and verifying that the risk register, which is a document that records and tracks the risks and their related information, is current, complete, and consistent7. Reviewing and updating the risk register can help to reflect the changes and updates in the risk factors and their status, but it does not ensure that the risk factors are resolved or reduced. Implementing new control technologies is a process that involves introducing or applying new software or hardware that can help to prevent, detect, or correct the risk factors affecting the information systems8. Implementing new control technologies can help to improve the security and performance of the information systems, but it does not ensure that the risk factors are eliminated or mitigated. References = 1: Risk Factors - an overview | ScienceDirect Topics2: InformationSystems Audit and Control Association (ISACA) - ISACA3: Information Systems Audit: The Basics4: Risk Response Strategy and Contingency Plans - ProjectManagement.com5: Risk and Information Systems Control Study Manual, Chapter 3: Risk Response, Section 3.1: Risk Response Options, pp. 113-115.6: [Business Process Owner - Gartner IT Glossary] 7: Risk Register: A Proje ct Manager’s Guide with Examples [2023] • Asana8: Technology Control Automation: Improving Efficiency, Reducing … - ISACA : [Business Process Owner - Roles and Responsibilities] : [Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.1: Risk Identification, pp. 57-59.] : [Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.]
Question # 212
Business areas within an organization have engaged various cloud service providers directly without assistance from the IT department. What should the risk practitioner do?
A.
Recommend the IT department remove access to the cloud services.
B.
Engage with the business area managers to review controls applied.
C.
Escalate to the risk committee.
D.
Recommend a risk assessment be conducted.
Full Access
Answer:
D
Explanation:
The best action for the risk practitioner to take when business areas within an organization have engaged various cloud service providers directly without assistance from the IT department is to recommend a risk assessment be conducted. A risk assessment is a process of identifying, analyzing, and evaluating the risks associated with the use of cloud services, such as financial, privacy, compliance, security, performance, quality, and technical risks12. A risk assessment can help to determine the current and potential risk exposure and impact of the cloud services, as well as the effectiveness and efficiency of theexisting or proposed controls. A risk assessment can also help to prioritize the risks and to develop and implement appropriate risk response strategies and plans, such as risk avoidance, reduction, sharing, or acceptance. Recommending a risk assessment is the best action, because it can provide valuable information and guidance to the business areas and the IT department for managing the cloud services in a consistent, effective, and efficient manner, and for aligning the cloud services with the organizational objectives, strategy, and risk appetite. The other options are not the best action, although they may be related or subsequent steps in the risk management process. Recommending the IT department remove access to the cloud services is a drastic and impractical action, as it may disrupt the business operations and services, and it may not address the underlying causes or drivers of the cloud service adoption. Engaging with the business area managers to review controls applied is a useful and collaborative action, as it can help to understand and evaluate the current state and practices of the cloud service usage, and to identify and address any gaps or issues in the control environment. However, this action should be based on or supported by a risk assessment, rather than preceding or replacing it. Escalating to the risk committee is a reporting and communication action, as it can help to inform and involve the senior management and other stakeholders in the risk management process, and to obtain their support and approval for the risk response actions. However, this action should be done after or along with a risk assessment, rather than before or instead of it. References = Best Practices to Manage Risks in the Cloud - ISACA, Cloud Risk Management - PwC UK
Question # 213
The PRIMARY reason for periodically monitoring key risk indicators (KRIs) is to:
A.
rectify errors in results of KRIs.
B.
detect changes in the risk profile.
C.
reduce costs of risk mitigation controls.
D.
continually improve risk assessments.
Full Access
Answer:
B
Explanation:
The primary reason for periodically monitoring key risk indicators (KRIs) is to detect changes in the risk profile of the enterprise. KRIs are metrics that provide information on the level of exposure to a specific risk or a group of risks. By monitoring KRIs, the enterprise can identifyany deviations from the expected risk level, and take appropriate actions to adjust the risk response or the risk appetite. Monitoring KRIs also helps to validate the effectiveness of risk mitigation controls and the accuracy of risk assessments. Rectifying errors in results of KRIs, reducing costs of risk mitigation controls, and continually improving risk assessments are possible benefits of monitoring KRIs, but they are not the primary reason. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.1.1.2, page 175.
Question # 214
When creating a program to manage data privacy risk, which of the following is MOST important to ensure that the program is successful?
A.
Compliance with industry frameworks
B.
Alignment with applicable legal and regulatory requirements
C.
Approval of mitigating and compensating controls
D.
Adoption of mission and vision statements
Full Access
Answer:
B
Explanation:
Privacy risk management programs must align withspecific regulatory obligations(e.g., GDPR, HIPAA) to be effective and compliant. Legal alignment defines scope, control requirements, and accountability.
[Reference:CRISC Manual – Domain 1, Slide 106-108, , , , ]
Question # 215
Which of the following is the MOST important consideration when multiple risk practitioners capture risk scenarios in a single risk register?
A.
Aligning risk ownership and control ownership
B.
Developing risk escalation and reporting procedures
C.
Maintaining up-to-date risk treatment plans
D.
Using a consistent method for risk assessment
Full Access
Answer:
D
Explanation:
A risk register is a document that records and tracks the information and status of the identified risks and their responses. It includes the risk description, category, source, cause, impact, probability, priority, response, owner, action plan, status, etc.
A risk scenario is a description or representation of a possible or hypothetical situation or event that may cause or result in a risk for the organization. A risk scenario usually consists of three elements: a threat or source of harm, a vulnerability or weakness, and an impact or consequence.
Multiple risk practitioners are the individuals or groups that are involved or responsible for the identification, analysis, evaluation, and communication of the risks and their responses. They may include the risk owners, risk managers, risk analysts, risk consultants, risk auditors, etc.
A single risk register is a risk register that is shared or used by multiple risk practitioners across the organization, and that contains the information and status of all the risks and their responses that are relevant or applicable to the organization.
The most important consideration when multiple risk practitioners capture risk scenarios in a single risk register is using a consistent method for risk assessment, which is the process of determining the significance and urgency of the risks that may affect the organization’s objectives and operations. Risk assessment involves measuring and comparing the likelihood and impact of various risk scenarios, and prioritizing them based on their magnitude and importance.
Using a consistent method for risk assessment when multiple risk practitioners capture risk scenarios in a single risk register ensures that the risk scenarios are captured and recorded in a uniform and standardized way, and that they are comparable and compatible with each other. It alsohelps to avoid or reduce the inconsistencies, discrepancies, or conflicts that may arise from the different perspectives, assumptions, or judgments of the multiple risk practitioners, and to ensure the accuracy, reliability, and validity of the risk register.
The other options are not the most important considerations when multiple risk practitioners capture risk scenarios in a single risk register, because they do not address the main challenge or issue that may arise from the multiple risk practitioners capturing risk scenarios in a single risk register, which is the lack of consistency or standardization in the risk assessment method.
Aligning risk ownership and control ownership means ensuring that the individuals or groups that are accountable and responsible for the risks and their responses are clearly defined and assigned, and that they have the authority and resources to perform their roles and duties. Aligning risk ownership and control ownership is important when multiple risk practitioners capture risk scenarios in a single risk register, but it is not the most important consideration, because it does not ensure that the risk scenarios are captured and recorded in a uniform and standardized way, and that they are comparable and compatible with each other.
Developing risk escalation and reporting procedures means establishing and implementing the processes and guidelines for communicating and sharing the information and status of the risks and their responses among the relevant stakeholders, and for escalating or transferring the risks and their responses to the appropriate levels or parties when necessary or required. Developing risk escalation and reporting procedures is important when multiple risk practitioners capture riskscenarios in a single risk register, but it is not the most important consideration, because itdoes not ensure that the risk scenarios are captured and recorded in a uniform and standardized way, and that they are comparable and compatible with each other.
Maintaining up-to-date risk treatment plans means updating and revising the actions or plans that are selected and implemented to address or correct the risks and their responses, based on the changes or developments that may occur in the risk environment or performance. Maintaining up-to-date risk treatment plans is important when multiple risk practitioners capture risk scenarios in a single risk register, but it is not the most important consideration, because it does not ensure that the risk scenarios are captured and recorded in a uniform and standardized way, and that they are comparable and compatible with each other. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 178
CRISC Practice Quiz and Exam Prep
Question # 216
Which of the following is MOST important to the successful development of IT risk scenarios?
A.
Cost-benefit analysis
B.
Internal and external audit reports
C.
Threat and vulnerability analysis
D.
Control effectiveness assessment
Full Access
Answer:
C
Explanation:
IT risk scenarios are hypothetical situations that describe how IT-related risks can affect the organization’s objectives, operations, or assets1. IT risk scenarios help to make IT risk more concrete and tangible, and to enable proper risk analysis and assessment2. IT risk scenarios are developed after IT risks are identified, and are used as inputs for risk analysis, where the frequency and impact of the scenarios are estimated3.
The most important factor to the successful development of IT risk scenarios is threat and vulnerability analysis. Threat and vulnerability analysis is the process of identifying and evaluating the potential sources and causes of IT risks, such as malicious actors, natural disasters, human errors, or technical failures4. Threat and vulnerability analysis can help to:
Define the scope and boundaries of the IT risk scenarios, and ensure that they are relevant and realistic
Identify the critical assets, processes, or functions that are exposed or affected by the IT risks, and assess their value and importance to the organization
Determine the likelihood and methods of the threat events, and the existing or potential weaknesses or gaps in the IT control environment
Estimate the potential consequences and impacts of the IT risks, such as financial losses, operational disruptions, reputational damages, or compliance violations5
References = IT Scenario Analysis in Enterprise Risk Management - ISACA, IT Risk Scenarios - Morland-Austin, Threat and Vulnerability Analysis - Wikipedia, Threat and Vulnerability Analysis - ISACA
Question # 217
Which of the following would be a risk practitioners’ BEST recommendation for preventing cyber intrusion?
A.
Establish a cyber response plan
B.
Implement data loss prevention (DLP) tools.
C.
Implement network segregation.
D.
Strengthen vulnerability remediation efforts.
Full Access
Answer:
D
Explanation:
A cyber intrusion is an unauthorized or malicious access to a computer system or network by an attacker. A cyber intrusion can compromise the confidentiality, integrity, or availability of the system or network, as well as the data and services that it hosts. A cyber intrusion can also cause damage, disruption, or theft to the organization or its stakeholders. One of the best ways toprevent cyber intrusion is to strengthen vulnerability remediation efforts, which means to identify and fix the weaknesses or flaws in the system or network that can be exploited by the attackers. Vulnerability remediation efforts can include conducting regularvulnerability assessments, applying security patches and updates, configuring security settings and policies, and implementing security controls and measures. By strengthening vulnerability remediation efforts, the organization can reduce the attack surface and the likelihood of cyber intrusion, as well as enhance the resilience and protection of the system or network. The other options are not the best recommendations for preventing cyber intrusion, although they may be helpful and complementary. Establishing a cyber response plan is a technique to prepare for and respond to a cyber incident, such as a cyber intrusion, by defining the roles, responsibilities, procedures, and resources that are needed to manage and recover from the incident. However, a cyber response plan is a reactive and contingency measure, while strengthening vulnerability remediation efforts is a proactive and preventive measure. Implementing data loss prevention (DLP) tools is a technology that tries to detect and stop sensitive data breaches, or data leakage incidents, in an organization. DLP tools can help to protect the data from being disclosed to an unauthorized person, whether it is deliberate or accidental. However, DLP tools do not prevent cyber intrusion itself, as they only focus on the data, not the system or network. Implementing network segregation is a method to divide a network into smaller segments or subnetworks, each with its own security policies and controls. Network segregation can help to isolate and contain the impact of a cyber intrusion, as well as to limit the access and movement of the attackers within the network. However, network segregation does not prevent cyber intrusion from occurring, as it does not address thevulnerabilities or flaws in the system or network. References = CRISC Review Manual, pages 164-1651; CRISC Review Questions, Answers & Explanations Manual, page 902; What Are Security Controls? - F53; Assessing Security Controls: Keystone of the Risk Management … - ISACA4
Question # 218
How does the identification of risk scenarios contribute to effective IT risk management?
A.
By facilitating post-incident investigations
B.
By enabling proactive risk assessment
C.
By identifying cybersecurity incidents
D.
By creating awareness of risk mitigation strategies
Full Access
Answer:
B
Explanation:
Identifyingrisk scenariosallows organizations to anticipatehowthreats can materialize, what assets may be affected, and the potential impact. According to CRISC, scenario development is a core component of proactive risk assessment because it enables organizations to evaluate likelihood, impact, and existing controls before incidents occur. It also supports risk quantification and prioritization. Post-incident investigations relate to after-the-fact analysis, whereas scenario analysis occurs beforehand. Identifying incidents is a monitoring activity, not a scenario-building function. Awareness is a secondary outcome, not the primary purpose.
[Reference:CRISC Review Manual – IT Risk Assessment (scenario development)., ========================================, ]
Question # 219
Which of the following is MOST important for an organization to have in place when developing a risk management framework?
A.
A strategic approach to risk including an established risk appetite
B.
A risk-based internal audit plan for the organization
C.
A control function within the risk management team
D.
An organization-wide risk awareness training program
Full Access
Answer:
A
Explanation:
 The most important thing for an organization to have in place when developing a risk management framework is a strategic approach to risk including an established risk appetite, as this provides the direction, scope, and objectives of the risk management process, and defines the level of risk that the organization is willing to accept or avoid in pursuit of its goals. A strategic approach to risk aligns the risk management framework with the organization’s vision, mission, values, and strategy, and ensures that the risk management activities support the achievement of the desired outcomes. An established risk appetite sets the boundaries and criteria for risk decision making, and guides the selection and implementation of risk responses. The other options are not the most important things for an organization to have in place when developing a risk management framework, although they may be useful or necessary components of it. A risk-based internal audit plan is a tool that helps to evaluate and improve the effectiveness of the risk management framework, but it does not define or drive the risk management process. A control function within the risk management team is a role that helps to implement and monitor the risk controls, but it does not determine or influence the risk strategy or appetite. An organization-wide risk awareness training program is a method that helps to enhance the risk culture and competence of the organization, but it does not establish or communicate the risk approach or appetite. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, page 23.
Question # 220
Which of the following is the GREATEST benefit when enterprise risk management (ERM) provides oversight of IT risk management?
A.
Aligning IT with short-term and long-term goals of the organization
B.
Ensuring the IT budget and resources focus on risk management
C.
Ensuring senior management ' s primary focus is on the impact of identified risk
D.
Prioritizing internal departments that provide service to customers
Full Access
Answer:
A
Explanation:
Enterprise risk management (ERM) is a holistic and strategic approach to managing the risks that an organization faces across its various functions, processes, and activities. ERM aims to align the organization’s risk appetite and tolerance with its objectives and vision, and to optimize the value and performance of the organization1.
IT risk management is a subset of ERM that focuses on identifying, assessing, and mitigating the risks related to the use of information technology (IT) in the organization. IT risk management aims to ensure the confidentiality, integrity, and availability of IT resources and information, and to support the IT governance and strategy of the organization2.
The greatest benefit when ERM provides oversight of IT risk management is aligning IT with short-term and long-term goals of the organization, because it can help to:
Integrate IT risk management with the overall business strategy and risk management, and ensure that IT risks are considered and addressed at the enterprise level
Align IT risk appetite and tolerance with the business risk appetite and tolerance, and ensure that IT risks are balanced with the expected benefits and opportunities
Enhance IT risk awareness and communication among the stakeholders, and ensure that IT risks are reported and escalated appropriately
Optimize IT risk response and control, and ensure that IT risks are managed efficiently and effectively
Demonstrate IT risk value and impact, and ensure that IT risks are measured and monitored against the business objectives and performance34
The other options are not the greatest benefit when ERM provides oversight of IT risk management, but rather some of the outcomes or consequences of it. Ensuring the IT budget and resources focus on risk management is a benefit that can help to allocate and prioritize the IT resources and funds according to the IT risk level and the business needs. Ensuring senior management’s primary focus is on the impact of identified risk is a benefit that can help to increase the senior management’s involvement and accountability in IT risk management, and to support the IT risk decision making and reporting. Prioritizing internal departments that provide service to customers is a benefit that can help to improve the quality and efficiency of the IT service delivery and customer satisfaction. References =
Enterprise Risk Management - ISACA
IT Risk Management - ISACA
Aligning IT risks with Enterprise Risk Management (ERM)
Five Benefits of Enterprise Risk Management : Articles : Resources …
[CRISC Review Manual, 7th Edition]
Question # 221
When creating a separate IT risk register for a large organization, which of the following is MOST important to consider with regard to the existing corporate risk ' register?
A.
Leveraging business risk professionals
B.
Relying on generic IT risk scenarios
C.
Describing IT risk in business terms
D.
Using a common risk taxonomy
Full Access
Answer:
D
Explanation:
Using a common risk taxonomy is the most important factor to consider when creating a separate IT risk register for a large organization with regard to the existing corporate risk register, as it ensures consistency, clarity, and alignment of the IT risk identification, classification, and reporting with the corporate risk management framework and strategy. Leveraging business risk professionals, relying on generic IT risk scenarios, and describing IT risk in business terms are not the most important factors, as they are more related to the resources, inputs, or outputs of the IT risk register, respectively, rather than the structure or format of the IT risk register. References = CRISC Review Manual, 7th Edition, page 100.
Question # 222
In addition to the risk exposure, which of the following is MOST important for senior management to understand prior to approving the use of artificial intelligence (Al) solutions?
A.
Potential benefits from use of Al solutions
B.
Monitoring techniques required for AI solutions
C.
Changes to existing infrastructure to support Al solutions
D.
Skills required to support Al solutions
Full Access
Answer:
A
Question # 223
A risk practitioner has identified that the agreed recovery time objective (RTO) with a Software as a Service (SaaS) provider is longer than the business expectation. Which ot the following is the risk practitioner ' s BEST course of action?
A.
Collaborate with the risk owner to determine the risk response plan.
B.
Document the gap in the risk register and report to senior management.
C.
Include a right to audit clause in the service provider contract.
D.
Advise the risk owner to accept the risk.
Full Access
Answer:
A
Explanation:
The best course of action for the risk practitioner who has identified that the agreed RTO with a SaaS provider is longer than the business expectation is to collaborate with the risk owner to determine the risk response plan. The risk owner is the person who has the authority and accountability to manage the risk within their scope of responsibility. The risk response plan is the document that describes the actions and resources needed to address the risk. By collaborating with the risk owner, the risk practitioner can help toanalyze the gap between the agreed RTO and the business expectation, evaluate the potential impact and consequences, and select the most appropriate risk response option, such as avoiding, reducing, transferring, or accepting the risk. Documenting the gap in the risk register, including a right to audit clause in the service provider contract, or advising the risk owner to accept the risk are not the best courses of action, because they do not address the root cause of the problem, or provide a solution to reduce the risk to an acceptable level. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Question # 224
Which of the following provides the MOST useful information to senior management about risk mitigation status?
A.
Risk strategy
B.
Risk register
C.
Gap analysis
D.
Business impact analysis (BIA)
Full Access
Answer:
B
Explanation:
A risk register is the primary tool for communicating progress: it consolidates risk scenarios, mitigation plans, current status, and residual risk in a structured format. Senior management relies on it to make informed decisions.
Question # 225
Which of the following is the PRIMARY benefit of using a risk map with stakeholders?
A.
Consolidates risk response options by severity
B.
Aligns risk appetite with business objectives
C.
Correlates risk scenarios to risk appetite
D.
Defines an organizational risk taxonomy
Full Access
Answer:
C
Explanation:
Arisk maphelps stakeholders understand how risk scenarios align with the organization’srisk appetite. This visualization facilitates informed decision-making and ensures risk responses are consistent with organizational priorities.
===========
Question # 226
Which of the following statements BEST describes risk appetite?
A.
The amount of risk an organization is willing to accept
B.
The effective management of risk and internal control environments
C.
Acceptable variation between risk thresholds and business objectives
D.
The acceptable variation relative to the achievement of objectives
Full Access
Answer:
A
Explanation:
Risk appetite is defined as " the amount of risk that an organization is willing to accept in pursuit of its objectives, before action is deemed necessary to reduce the risk. " 1 It represents a balance between the potential benefits of innovation and the threats that change inevitably brings. Risk appetite reflects the organization’s risk attitude and its willingness to accept risk in specific scenarios, with a governance model in place for risk oversight. Risk appetite helps to guide the organization’s approach to risk and risk management, and to align its risk decisions with its business objectives and context. The other options are not the best descriptions of risk appetite, as they are either too vague (the effective management of risk and internal control environments), too narrow (acceptable variation between risk thresholds and business objectives), or confusing (the acceptable variation relative to the achievement of objectives). References = Risk Appetite vs. Risk Tolerance: What is the Difference?
Question # 227
Which of the following BEST mitigates the risk associated with inadvertent data leakage by users who work remotely?
A.
Conducting training on the protection of organizational assets
B.
Configuring devices to use virtual IP addresses
C.
Ensuring patching for end-user devices
D.
Providing encrypted access to organizational assets
Full Access
Answer:
D
Explanation:
Providing encrypted access to organizational assets is the best method to mitigate the risk of inadvertent data leakage by remote workers. Encryption ensures that data remains secure, even if accessed over unsecured networks.
Question # 228
A risk practitioner is concerned with potential data loss in the event of a breach at a hosted third-party provider. Which of the following is the BEST way to mitigate this risk?
A.
Include an indemnification clause in the provider ' s contract.
B.
Monitor provider performance against service level agreements (SLAs).
C.
Purchase cyber insurance to protect against data breaches.
D.
Ensure appropriate security controls are in place through independent audits.
Full Access
Answer:
D
Explanation:
Conducting independent audits to verify that appropriate security controls are in place is the most effective way to mitigate the risk of data loss at a third-party provider. These audits provide assurance that the provider adheres to security best practices and complies with relevant standards and regulations. While contractual clauses and insurance can provide financial remedies post-incident, proactive verification of security controls helps prevent breaches from occurring in the first place.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 3: Risk Response and Reporting, Section: Third-Party Risk Management., , , , , , , ]
Question # 229
Which of We following is the MOST effective control to address the risk associated with compromising data privacy within the cloud?
A.
Establish baseline security configurations with the cloud service provider.
B.
Require the cloud prowler 10 disclose past data privacy breaches.
C.
Ensure the cloud service provider performs an annual risk assessment.
D.
Specify cloud service provider liability for data privacy breaches in the contract
Full Access
Answer:
D
Explanation:
Specifying cloud service provider liability for data privacy breaches in the contract is the most effective control to address the risk associated with compromising data privacy within the cloud, because it establishes the roles and responsibilities of the cloud service provider and the customer in case of a data breach, and defines the compensation or remediation measures that the cloud service provider should provide. This control also creates an incentive for the cloud service provider to implement adequate security measures to protect the customer’s data and comply with the relevant laws and regulations. The other options are not the most effective controls, although they may also be helpful in reducing the risk of data privacy breaches. Establishing baseline security configurations with the cloud service provider, requiring the cloud service provider to disclose past data privacy breaches, and ensuring the cloud service provider performs an annual risk assessment are examples of preventive or detective controls that aim to reduce the likelihood or impact of a data breach, but they do not address the accountability or liability of the cloud service provider in case of a data breach. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 230
The PRIMARY basis for selecting a security control is:
A.
to achieve the desired level of maturity.
B.
the materiality of the risk.
C.
the ability to mitigate risk.
D.
the cost of the control.
Full Access
Answer:
C
Explanation:
 The PRIMARY basis for selecting a security control is the ability to mitigate risk, because it is the measure of how well the control can prevent or reduce the occurrence or impact of the risk, and how effectively the control can achieve the desired level of security and protection for the system and the data. The ability to mitigate risk is the most important criterion for selecting a security control, as it directly relates to the purpose and value of the control. The other options are not the primary basis, because:
Option A: To achieve the desired level of maturity is a goal of selecting a security control, but not the primary basis. The desired level of maturity is the state or condition of the security control that reflects its quality, consistency, and reliability, and it should be aligned with the organization’s security objectives and standards. The desired level of maturity is a result of selecting a security control, not a reason for selecting it.
Option B: The materiality of the risk is a factor of selecting a security control, but not the primary basis. The materiality of the risk is the degree or extent of the risk that affects the organization’s performance, reputation, and value, and it should be considered when selecting a security control, but it is not the only or the most important factor. The materiality of the risk is an input to selecting a security control, not an output of selecting it.
Option D: The cost of the control is a constraint of selecting a security control, but not the primary basis. The cost of the control is the amount of resources and expenditure that are required to implement and maintain the control, and it should be balanced with the benefit and effectiveness ofthe control, but it is not the only or the most important constraint. The cost of the control is a limitation of selecting a security control, not a motivation for selecting it. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 211.
Question # 231
Which of the following activities is MOST likely to be assigned to the second line in the three lines model?
A.
Validating whether IT risk control systems are operational
B.
Monitoring IT security policy compliance
C.
Calculating phishing attack key risk indicators (KRIs)
D.
Appropriately configuring the web application firewall (WAF)
Full Access
Answer:
B
Explanation:
In the three lines model, thesecond lineprovides oversight and monitoring of risk and compliance. CRISC states that functions such as risk management, compliance monitoring, and policy oversight belong to the second line. Monitoring IT security policy compliance fits this role because it evaluates whether operational controls align with requirements. The first line (operations) configures systems like WAFs and calculates operational KRIs. The third line (internal audit) validates whether controls are functioning independently. Thus, the responsibility most aligned with the second line is monitoring compliance.
[Reference:CRISC Review Manual – Governance (three lines model)., ========================================, ]
Question # 232
Reviewing which of the following BEST helps an organization gain insight into its overall risk profile?
A.
Threat landscape
B.
Risk appetite
C.
Risk register
D.
Risk metrics
Full Access
Answer:
C
Explanation:
Reviewing the risk register is the best way to help an organization gain insight into its overall risk profile, because it provides a comprehensive and structured representation of all the key risks that the organization faces, along with their likelihood, impact, and response strategies. A risk register is a tool that records and tracks the current status of risks, their sources, causes, consequences, and controls. A risk register helps to facilitate the communication and reporting of risks, and to support the risk-based decision making and prioritization. A risk profile is a summary of the key risks that an organization faces, and their implications forthe organization’s objectives and strategy. Reviewing the risk register is the best way to understand the risk profile, as it reflects the nature and level of exposure that the organization has from the various risk sources and scenarios. Reviewing the threat landscape, the risk appetite, and the risk metrics are all useful ways to help an organization gain insight into its overall risk profile, but they are not the best way, as they do not provide a comprehensive and structured view of the risks and theirresponses. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.1, page 83
Question # 233
Which of the following is the PRIMARY benefit of using an entry in the risk register to track the aggregate risk associated with server failure?
A.
It provides a cost-benefit analysis on control options available for implementation.
B.
It provides a view on where controls should be applied to maximize the uptime of servers.
C.
It provides historical information about the impact of individual servers malfunctioning.
D.
It provides a comprehensive view of the impact should the servers simultaneously fail.
Full Access
Answer:
D
Explanation:
Using an entry in the risk register to track the aggregate risk associated with server failure provides a comprehensive view of the impact should the servers simultaneously fail, as it considers the combined effect of the server failure on the enterprise’s objectives and operations. The risk register is a document that records and tracks the identified risks, their likelihood, impact, and mitigation strategies. By aggregating the risk associated with server failure, the risk register can help to estimate the worst-case scenario and to prioritize the risk response accordingly. It provides a cost-benefit analysis on controloptions available for implementation, it provides a view on where controls should be applied to maximize the uptime of servers, and it provides historical information about the impact of individual servers malfunctioning are not the primary benefits of using an entry in the risk register to track the aggregate risk associated with server failure, but rather the possible outcomes or actions of using the risk register. References = CRISC Certified in Risk and Information Systems Control –Question220; ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 220.
Question # 234
Which of the following is MOST important to enable well-informed cybersecurity risk decisions?
A.
Determine and understand the risk rating of scenarios.
B.
Conduct risk assessment peer reviews.
C.
Identify roles and responsibilities for security controls.
D.
Engage a third party to perform a risk assessment.
Full Access
Answer:
A
Explanation:
To make well-informed cybersecurity risk decisions, it is most important to determine and understand the risk rating of scenarios. A risk rating is a measure of the severity and priority of a risk, based on the combination of its impact and likelihood. A risk scenario is a description of a potential event or situation that could adversely affect the organization’s objectives, assets, or processes. By determining and understanding the risk rating of scenarios, the organization can identify the most critical and urgent risks, and select the appropriate risk response strategies accordingly. The other options are not as important as determining and understanding the risk rating of scenarios, because they do not provide a clear and comprehensive view of the risk, butrather focus on specific or partial aspects of the risk management process. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.1, page 45.
Question # 235
Which of the following is the MOST important consideration when selecting digital signature software?
A.
Availability
B.
Nonrepudiation
C.
Accuracy
D.
Completeness
Full Access
Answer:
B
Explanation:
ï‚· Digital Signature Software:
Digital signatures are used to verify the authenticity and integrity of a message, document, or software. They provide cryptographic proof that the information has not been altered and that it comes from a verified source.
ï‚· Importance of Nonrepudiation:
Nonrepudiation ensures that the sender of the message cannot deny having sent the message and the recipient cannot deny having received it. This is critical for legal and security purposes, as it provides undeniable proof of the origin and integrity of the information.
ï‚· Selecting Digital Signature Software:
When selecting digital signature software, the most important consideration is that it provides strong nonrepudiation capabilities. This ensures that all parties involved can trust the authenticity and integrity of the signed data.
ï‚· Comparing Other Considerations:
Availability:Ensures the software is accessible when needed but does not directly impact the trustworthiness of the signatures.
Accuracy:Important but generally inherent in properly functioning digital signature software.
Completeness:Ensures all required information is included but nonrepudiation is the critical factor for security and legal purposes.
ï‚· References:
The CISSP Study Guide emphasizes the importance of nonrepudiation in digital signature technology to ensure authenticity and accountability (Sybex CISSP Study Guide, Chapter 7: PKI and Cryptographic Applications)​​.
Question # 236
Which of the following would be MOST helpful to a risk practitioner when ensuring that mitigated risk remains within acceptable limits?
A.
Building an organizational risk profile after updating the risk register
B.
Ensuring risk owners participate in a periodic control testing process
C.
Designing a process for risk owners to periodically review identified risk
D.
Implementing a process for ongoing monitoring of control effectiveness
Full Access
Answer:
D
Explanation:
The most helpful activity for a risk practitioner when ensuring that mitigated risk remains within acceptable limits is to implement a process for ongoing monitoring of control effectiveness. This would enable the risk practitioner to track the performance of the controls, identify any deviations or gaps, and take corrective actions as needed. Ongoing monitoring of control effectiveness would also provide assurance that the risk responses are working as intended, and that the residual risk is aligned with the risk appetite and tolerance of the enterprise. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.3.1, page 188.
Question # 237
Which of the following is MOST important for a risk practitioner to confirm once a risk action plan has been completed?
A.
The risk register has been updated.
B.
The risk tolerance has been recalibrated.
C.
The risk has been mitigated to the intended level.
D.
The risk owner has reviewed the outcomes.
Full Access
Answer:
C
Explanation:
Confirming that the risk has been mitigated to the intended level is paramount to ensure that the risk response was effective. This ties toRisk Mitigation and Treatment, ensuring that controls implemented have reduced the risk to within the organization ' s appetite. Updating registers or recalibrating tolerances comes secondary to verifying the effectiveness of mitigation.
Question # 238
An organization is analyzing the risk of shadow IT usage. Which of the following is the MOST important input into the assessment?
A.
Business benefits of shadow IT
B.
Application-related expresses
C.
Classification of the data
D.
Volume of data
Full Access
Answer:
C
Explanation:
The most important input into the assessment of the risk of shadow IT usage is the classification of the data that is being processed, stored, or transmitted by the unauthorized applications or devices. This determines the level of confidentiality, integrity, and availability that is required for the data and the potential impact of a breach or loss. Business benefits of shadow IT, application-related expenses, and volume of data are less important inputs that may affect the risk analysis, but not as much as the data classification. References = Risk IT Framework, 2nd Edition, page 28; CRISC Review Manual, 6th Edition, page 98.
Question # 239
Which of the following is the MOST important key performance indicator (KPI) to monitor the effectiveness of disaster recovery processes?
A.
Percentage of IT systems recovered within the mean time to restore (MTTR) during the disaster recovery test
B.
Percentage of issues arising from the disaster recovery test resolved on time
C.
Percentage of IT systems included in the disaster recovery test scope
D.
Percentage of IT systems meeting the recovery time objective (RTO) during the disaster recovery test
Full Access
Answer:
D
Explanation:
 The most important key performance indicator (KPI) to monitor the effectiveness of disaster recovery processes is the percentage of IT systems meeting the recovery time objective (RTO) during the disaster recovery test. The RTO is the maximum acceptable time that a system orprocess can be unavailable after a disruption. The disaster recovery test is a simulation of a disaster scenario to evaluate the readiness and capability of the organization to restore its critical functions and systems. By measuring the percentage ofIT systems meeting the RTO during the test, the organization can assess how well the disaster recovery processes meet the predefined objectives and standards. Percentage of IT systems recovered within the mean time to restore (MTTR), percentage of issues arising from the disaster recovery test resolved on time, and percentage of IT systems included in the disaster recovery test scope are other possible KPIs, but they are not as important as the percentage of IT systems meeting the RTO. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
Question # 240
Before assigning sensitivity levels to information it is MOST important to:
A.
define recovery time objectives (RTOs).
B.
define the information classification policy
C.
conduct a sensitivity analyse
D.
Identify information custodians
Full Access
Answer:
B
Explanation:
Before assigning sensitivity levels to information, it is most important to define the information classification policy. The information classification policy is a document that establishes the criteria, categories, roles, responsibilities, and procedures for classifying information according to its sensitivity, value, and criticality. The information classification policy provides the basis, guidance, and consistency for assigning sensitivity levels to information, and ensures that the information is protected and handled appropriately. The other options are not as important as defining the information classification policy, as they are related to the specific steps, activities, or outputs of the information classification process, not the overall structure and quality of the information classification process. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.4: Key Control Indicators, page 211.
Question # 241
Which of the following should be the FIRST step when a company is made aware of new regulatory requirements impacting IT?
A.
Perform a gap analysis.
B.
Prioritize impact to the business units.
C.
Perform a risk assessment.
D.
Review the risk tolerance and appetite.
Full Access
Answer:
D
Explanation:
New regulatory requirements impacting IT are those that impose new obligations, restrictions, or standards on how an organization uses, manages, or secures its IT systems, data, or services1. Examples of such regulations include the GDPR, the CCPA, the HIPAA, or the PCI-DSS2. New regulatory requirements impacting IT can pose significant challenges and risks for an organization, such as:
Compliance costs and efforts, such as updating policies, procedures, and systems, training staff, or hiring experts
Noncompliance penalties and consequences, such as fines, lawsuits, sanctions, or reputational damages
Operational disruptions or inefficiencies, such as system changes, data migrations, or service interruptions
Competitive disadvantages or opportunities, such as losing or gaining customers, partners, or markets3
The first step that should be done when a company is made aware of new regulatory requirements impacting IT is to review the risk tolerance and appetite. Risk tolerance is the acceptable level of variation that an organization is willing to accept around its risk appetite. Risk appetite is the amount and type of risk that an organization is willing to take in order to meet its strategic objectives. By reviewing the risk tolerance and appetite, the company can:
Establish a clear and consistent understanding of the organization’s goals, values, and expectations regarding the new regulatory requirements impacting IT
Assess the current and potential impacts of the new regulatory requirements impacting IT on the organization’s performance, operations, or assets
Determine the level of risk exposure and acceptance that the organization is comfortable with, and identify the risk thresholds or limits that should not be exceeded
Align the risk management strategies and actions with the organization’s risk tolerance and appetite, and prioritize the most critical and urgent risks to be addressed
Communicate and report the risk tolerance and appetite to the stakeholders and regulators, and ensure transparency and accountability
References = Regulating emerging technology | Deloitte Insights, Ten Key Regulatory Challenges of 2024 - kpmg.com, The Risks of Non-Compliance with Data Protection Laws, [Risk Tolerance - COSO], [Risk Appetite - COSO] , [Risk Appetite and Tolerance - IRM]
Question # 242
Which of the following is the PRIMARY reason to ensure policies and standards are properly documented within the risk management process?
A.
It facilitates the use of a framework for risk management.
B.
It establishes a means for senior management to formally approve risk practices.
C.
It encourages risk-based decision making for stakeholders.
D.
It provides a basis for benchmarking against industry standards.
Full Access
Answer:
B
Explanation:
Policies and standards are important components of the risk management process, as they define the objectives, expectations, and requirements for managing risk within the organization. Policies and standards are also the means by which senior management formally approves and communicates the risk practices to the stakeholders, ensuring that the risk management process is aligned with the organizational strategy, culture, and values. Policies and standards also provide the authority and accountability for the risk management roles and responsibilities, as well as the criteria and metrics for measuring and reporting risk performance.
Question # 243
For a large software development project, risk assessments are MOST effective when performed:
A.
before system development begins.
B.
at system development.
C.
at each stage of the system development life cycle (SDLC).
D.
during the development of the business case.
Full Access
Answer:
C
Explanation:
Risk assessments are most effective when performed at each stage of the system development life cycle (SDLC). The SDLC is a framework that defines the phases and activities of developing, implementing, and maintaining a system. The SDLC typically consists of the following stages: initiation, planning, analysis, design, development, testing, implementation, and maintenance. Performing risk assessments at each stage of the SDLC helps to identify, analyze, and evaluate the risks that could affect the system objectives, requirements, functionality, quality, or performance. Performing risk assessments at each stage of the SDLC also helps to select and implement the appropriate risk responses, such as avoiding, transferring, mitigating, or accepting the risks. Performing risk assessments at each stage of the SDLC also helps to monitor and report the risk status and performance, and to update and adjust the risk assessment and response as the system changes or evolves. Performing risk assessments before system development begins, at system development, or during the development of the business case are not as effective as performing risk assessments at each stage of the SDLC, as they are either too early or too late, and they do not capture the full scope and complexity of the system risks. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 49.
Question # 244
Reviewing results from which of the following is the BEST way to identify information systems control deficiencies?
A.
Vulnerability and threat analysis
B.
Control remediation planning
C.
User acceptance testing (UAT)
D.
Control self-assessment (CSA)
Full Access
Answer:
D
Explanation:
Information systems control deficiencies are the weaknesses or flaws in the design or implementation of the controls that are intended to ensure the confidentiality, integrity, availability, and reliability of the information systems and resources. Information systems control deficiencies may reduce the effectiveness or efficiency of the controls, and expose the organization to various risks, such as unauthorized access, data loss, system failure, etc.
Reviewing results from control self-assessment (CSA) is the best way to identify information systems control deficiencies, because CSA is a process of evaluating and verifying the adequacy and effectiveness of the information systems controls, using the input and feedback from the individuals or groups that are involved or responsible for the information systems activities or functions. CSA can help the organization to identify and document the information systems control deficiencies, and to align them with the organization’s information systems objectives and requirements.
CSA can be performed using various techniques, such as questionnaires, surveys, interviews, workshops, etc. CSA can also be integrated with the organization’s governance, risk management, and compliance functions, and aligned with the organization’s policies and standards.
The other options are not the best ways to identify information systems control deficiencies, because they do not provide the same level of detail and insight that CSA provides, and they may not be relevant or actionable for the organization.
Vulnerability and threat analysis is a process of identifying and evaluating the weaknesses or flaws in the organization’s assets, processes, or systems that can be exploited or compromised by the potential threats or sources of harm that may affect the organization’s objectives or operations. Vulnerability and threat analysis can help the organization to assess and prioritize the risks, and to design and implement appropriate controls or countermeasures to mitigate or prevent the risks, but it is not the best way to identify information systems control deficiencies, because it does not indicate whether the existing information systems controls are adequate and effective, and whether they comply with the organization’s policies and standards.
Control remediation planning is a process of selecting and implementing the actions or plans to address or correct the information systems control deficiencies that have been identified,analyzed, and evaluated. Control remediation planning involves choosing one ofthe following types of control responses: mitigate, transfer, avoid, or accept. Control remediation planning can help the organization to improve and optimize the information systems controls, and to reduce or eliminate the information systems control deficiencies, but it is not the best way to identify information systems control deficiencies, because it is a subsequent or follow-up process that depends on the prior identification of the information systems control deficiencies.
User acceptance testing (UAT) is a process of verifying and validating the functionality and usability of the information systems and resources, using the input and feedback from the endusers or customers that interact with the information systems and resources. UAT can help the organization to ensure that the information systems and resources meet the user or customer expectations and requirements, and to identify and resolve any issues or defects that may affect the user or customer satisfaction, but it is not the best way to identify information systems control deficiencies, because it does not focus on the information systems controls, and it may not cover all the relevant or significant information systems control deficiencies that may exist or arise. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 186
CRISC Practice Quiz and Exam Prep
Question # 245
Which of the following is the PRIMARY reason to conduct risk assessments at periodic intervals?
A.
To ensure emerging risk is identified and monitored
B.
To establish the maturity level of risk assessment processes
C.
To promote a risk-aware culture among staff
D.
To ensure risk trend data is collected and reported
Full Access
Answer:
A
Question # 246
Before implementing instant messaging within an organization using a public solution, which of the following should be in place to mitigate data leakage risk?
A.
A data extraction tool
B.
An access control list
C.
An intrusion detection system (IDS)
D.
An acceptable usage policy
Full Access
Answer:
D
Explanation:
According to the CRISC Review Manual1, an acceptable usage policy is a document that defines the rules and guidelines for the appropriate and secure use of IT resources within an organization. It helps to mitigate data leakage risk by establishing the roles and responsibilities of users, the types and purposes of data that can be shared or transmitted, the authorized methods and channels of communication, the security controls and measures to protect data, and the consequences of non-compliance. An acceptable usage policy also educates and raises awareness among users about the potential risks and threats associated with instant messaging and other forms of online communication. Therefore, before implementing instant messaging within an organization using a public solution, an acceptable usage policy should be in place to mitigate data leakage risk. References = CRISC Review Manual1, page 237.
Question # 247
When developing a response plan to address security incidents regarding sensitive data loss, it is MOST important
A.
revalidate current key risk indicators (KRIs).
B.
revise risk management procedures.
C.
review the data classification policy.
D.
revalidate existing risk scenarios.
Full Access
Answer:
C
Explanation:
When developing a response plan to address security incidents regarding sensitive data loss, it is most important to review the data classification policy. A data classification policy is a document that defines the categories and levels of data based on their sensitivity, value, and criticality, and specifies the appropriate security measures and handling procedures for each data type. A data classification policy helps to identify and protect the sensitive data that could be exposed or compromised in a security incident, and to comply with the relevant laws, regulations, standards, and contracts. Reviewing the data classification policy is important when developing a response plan, because it helps to determine the scope, impact, and priority of the security incident, and to select the most appropriate and effective response actions and strategies. Reviewing the data classification policy also helps to communicate and coordinate the response plan with the internal and external stakeholders, such as the data owners, users, custodians, and regulators, and to report and disclose the security incident as required. The other options are not as important as reviewing the data classification policy, although they may be part of or derived from the response plan. Revalidating current key risk indicators (KRIs), revising risk management procedures, and revalidating existing risk scenarios are all activities that can help to improve or update the risk management process, but they are not the most important when developing aresponse plan. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.1, page 5-25.
Question # 248
The MOST important objective of information security controls is to:
A.
Identify threats and vulnerability
B.
Ensure alignment with industry standards
C.
Provide measurable risk reduction
D.
Enforce strong security solutions
Full Access
Answer:
C
Explanation:
The most important objective of information security controls is to provide measurable risk reduction. Information security controls are the policies, procedures, techniques, or technologies that are implemented to protect the confidentiality, integrity, and availability of information assets. The main purpose of information security controls is to reduce the risk of unauthorized access, use, disclosure,modification, or destruction of information assets, and to ensure that the information assets support the enterprise’s objectives and performance. Information security controls should be measurable, meaning that they should have clear and quantifiable criteria for evaluating their effectiveness and efficiency in reducing the risk exposure to an acceptable level. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.1.1, page 1151
Question # 249
Which of the following is MOST important for a risk practitioner to review during an IT risk assessment?
A.
Published records of loss from peer organizations
B.
The organization ' s historical threats and monetary loss
C.
Information system assets and associated threats
D.
Information system control weaknesses and audit findings
Full Access
Answer:
C
Question # 250
Which of the following is the MOST important factor when deciding on a control to mitigate risk exposure?
A.
Relevance to the business process
B.
Regulatory compliance requirements
C.
Cost-benefit analysis
D.
Comparison against best practice
Full Access
Answer:
C
Explanation:
 The most important factor when deciding on a control to mitigate risk exposure is the cost-benefit analysis. This is a process that compares the costs and benefits of implementing a control, and determines whether the control is worth the investment. A cost-benefit analysis helps to ensure that the control is efficient and effective in reducing the risk to an acceptable level, and that it does not introduce new risks or adversely affect other objectives. A cost-benefit analysis also helps to prioritize the controls based on their value and feasibility, and to allocate the resources accordingly. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.5, page 1861
Question # 251
Which of the following roles would be MOST helpful in providing a high-level view of risk related to customer data loss?
A.
Customer database manager
B.
Customer data custodian
C.
Data privacy officer
D.
Audit committee
Full Access
Answer:
C
Explanation:
A data privacy officer is a role that is responsible for ensuring that the organization complies with the applicable laws, regulations, and standards regarding the collection, processing, storage, and disclosure of customer data1. A data privacy officer is also responsible for developing and implementing policies, procedures, and controls to protect the privacy and security of customer data, and to prevent or mitigate the risk of customer data loss2. A data privacy officer is the most helpful role in providing a high-level view of risk related to customer data loss, because:
A data privacy officer has the knowledge and expertise of the legal and ethical requirements and best practices for customer data protection, and can identify and assess the potential threats and vulnerabilities that may compromise customer data3.
A data privacy officer has the authority and accountability to oversee and monitor the customer data lifecycle, and to ensure that the organization follows the principles of data minimization, purpose limitation, accuracy, integrity, confidentiality, and accountability4.
A data privacy officer has the visibility and communication skills to report and advise the management and other stakeholders on the customer data risk profile, and to recommend and implement appropriate risk responses and improvement actions5.
The other options are not the most helpful roles in providing a high-level view of risk related to customer data loss, because:
A customer database manager is a role that is responsible for designing, developing, maintaining, and optimizing the database systems that store and manage customer data6. A customer database manager may have some technical skills and knowledge to protect the customer data from unauthorized access, modification, or deletion, but may not have the comprehensive or holistic view of the customer data risk, as they may focus only on the database level, and not on the organizational or regulatory level.
A customer data custodian is a role that is responsible for handling, processing, and storing customer data according to the instructions and permissions of the data owner7. A customer data custodian may have some operational duties and responsibilities to safeguard the customer data from accidental or intentional loss, damage, or disclosure, but may not have the strategic or analyticalview of the customer data risk, as they may follow only the predefined rules and procedures, and not the risk management principles and practices.
An audit committee is a group of independent directors or members that is responsible for overseeing and evaluating the organization’s financial reporting, internal control, and auditfunctions. An audit committee may have some oversight and assurance roles andresponsibilities to review and verify the organization’s compliance and performance regarding customer data protection, but may not have the direct or proactive view of the customer data risk, as they may rely only on the audit reports and findings, and not on the risk assessment and analysis.
References =
Data Privacy Officer - CIO Wiki
What is a Data Protection Officer (DPO)? - Definition from Techopedia
Data Privacy Officer: Roles and Responsibilities - ISACA
Data Protection Principles - CIO Wiki
Data Privacy Officer: How to Be One and Why You Need One - ISACA
Database Manager - CIO Wiki
Data Custodian - CIO Wiki
[Audit Committee - CIO Wiki]
Question # 252
The PRIMARY benefit associated with key risk indicators (KRls) is that they:
A.
help an organization identify emerging threats.
B.
benchmark the organization ' s risk profile.
C.
identify trends in the organization ' s vulnerabilities.
D.
enable ongoing monitoring of emerging risk.
Full Access
Answer:
D
Explanation:
Key risk indicators (KRIs) are metrics that provide information on the level of exposure to a given risk. They enable ongoing monitoring of emerging risk by alerting the organization when the risk level exceeds thepredefined threshold or tolerance. By using KRIs, the organization can track the changes in the risk environment and take timely and appropriate actions to mitigate or avoid the risk.
Helping an organization identify emerging threats, benchmarking the organization’s risk profile, and identifying trends in the organization’s vulnerabilities are all possible uses of KRIs, but they are not the primary benefit. The primary benefit is to enable ongoing monitoring of emerging risk, which encompasses all these aspects and more. References = CRISC Review Manual, 7th Edition, ISACA, 2020, page 27-281
Question # 253
An IT risk practitioner has been asked to regularly report on the overall status and effectiveness of the IT risk management program. Which of the following is MOST useful for this purpose?
A.
Balanced scorecard
B.
Capability maturity level
C.
Internal audit plan
D.
Control self-assessment (CSA)
Full Access
Answer:
A
Explanation:
A balanced scorecard is a strategic management tool that helps to measure and communicate the performance of an organization or a program against its goals and objectives. A balanced scorecard typicallyconsists of four perspectives: financial, customer, internal process, and learning and growth. Each perspective has a set of key performance indicators (KPIs) that reflect the critical success factors and desired outcomes of the organization or the program1.
A balanced scorecard is most useful for reporting on the overall status and effectiveness of the IT risk management program, because it can provide a comprehensive and balanced view of the program’s performance across multiple dimensions. A balanced scorecard can help to align the IT risk management program with the business strategy and vision, and to demonstrate the value and impact of the program to the stakeholders. A balanced scorecard can also help to identify the strengths and weaknesses of the IT risk management program, and to monitor and improve the program’s processes and outcomes2.
The other options are not as useful as a balanced scorecard for reporting on the overall status and effectiveness of the IT risk management program. A capability maturity level is a measure of the maturity and quality of a process or a practice, based on a predefined set of criteria andstandards. A capability maturity level can help to assess and benchmark the IT risk management program’s processes and practices, but it does not provide a holistic view of the program’s performance and results3. An internal audit plan is a document that outlines the scope, objectives, and methodology of an internal audit activity. An internal audit plan can help to evaluate and verify the IT risk management program’s controls and compliance, but it does not provide a strategic view of the program’s goals and outcomes4. A control self-assessment (CSA) is a technique that involves the participation of the process owners and the staff in assessing the effectiveness and efficiency of their own controls. A CSA can help to enhance the awareness and ownership of the IT risk management program’s controls, but it does not provide an objective and independent view of the program’s performance and impact. References =
Balanced Scorecard Basics - Balanced Scorecard Institute
Using the Balanced Scorecard to Measure and Manage IT Risk
Capability Maturity Model Integration (CMMI) Overview
Internal Audit Planning: The Basics - The IIA
[Control Self-Assessment - ISACA]
Question # 254
Which of the following is the BEST evidence that risk management is driving business decisions in an organization?
A.
Compliance breaches are addressed in a timely manner.
B.
Risk ownership is identified and assigned.
C.
Risk treatment options receive adequate funding.
D.
Residual risk is within risk tolerance.
Full Access
Answer:
C
Explanation:
Risk treatment options are the actions or plans that are implemented to modify or reduce the risk exposure of the organization. Risk treatment options receive adequate funding when the organization allocatessufficient resources and budget to support the risk response actions, and to ensure that the risk controls are effective and efficient. This is the best evidence that risk management is driving business decisions in the organization, as it shows that the organizationprioritizes and values the risk management process, and that it aligns its risk strategy and objectives with its business goals and value creation. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 245. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 245. CRISC Sample Questions 2024, Question 245.
Question # 255
Which of the following is the MOST important reason to validate that risk responses have been executed as outlined in the risk response plan ' '
A.
To ensure completion of the risk assessment cycle
B.
To ensure controls arc operating effectively
C.
To ensure residual risk Is at an acceptable level
D.
To ensure control costs do not exceed benefits
Full Access
Answer:
C
Explanation:
The most important reason to validate that risk responses have been executed as outlined in the risk response plan is to ensure that the residual risk is at an acceptable level. Residual risk is the risk that remains after applying a risk response. The risk response plan is the document thatdescribes the actions and resources needed to address the risk. Validating the risk response execution is the process of verifying that the risk response actions have been performed as planned, and that they have achieved the desired results. Validating the risk response execution helps to measure and monitor the residual risk, and to ensure that it is within the risk tolerance of the organization and its stakeholders. The other reasons are not as important as ensuring that the residual risk is at an acceptable level, although they may be secondary benefits or outcomes of validating the risk response execution. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Question # 256
The design of procedures to prevent fraudulent transactions within an enterprise resource planning (ERP) system should be based on:
A.
stakeholder risk tolerance.
B.
benchmarking criteria.
C.
suppliers used by the organization.
D.
the control environment.
Full Access
Answer:
D
Explanation:
Fraudulent transactions are those that involve deception, manipulation, or misrepresentation of information or data to obtain an unauthorized or improper benefit or advantage1. Fraudulenttransactions can pose significant risks and losses for an organization, such as financial damages, legal liabilities, reputational damages, or operational disruptions2.
Enterprise resource planning (ERP) systems are integrated software applications that support the core business processes and functions of an organization, such as accounting, finance, human resources, supply chain, inventory, or customer relationship management3. ERP systems can facilitate the efficiency, accuracy, and security of business transactions, but they can also be vulnerable to fraudulent transactions, such as:
Creating fake vendors or customers and processing false invoices or payments
Manipulating or falsifying financial or accounting data or reports
Changing or deleting critical or sensitive information or records
Abusing or misusing access privileges or credentials
Bypassing or compromising the system controls or security measures4
The design of procedures to prevent fraudulent transactions within an ERP system should be based on the control environment. The control environment is the set of standards, processes, and structures that provide the basis for carrying out internal control across the organization. The control environment comprises the following elements:
The tone at the top, which reflects the leadership’s commitment and attitude towards internal control and ethical conduct
The organizational structure, which defines the roles and responsibilities, reporting lines, and authority levels for internal control
The human resource policies and practices, which ensure that the staff have the appropriate skills, competencies, and incentives for internal control
The risk assessment process, which identifies and evaluates the potential risks and threats to the organization’s objectives and transactions
The control activities, which are the specific policies, procedures, and mechanisms that prevent, detect, or correct errors or fraud in transactions
The information and communication systems, which provide reliable and timely data and information for internal control and decision-making
The monitoring and evaluation activities, which measure and report the performance and effectiveness of internal control and ensure continuous improvement
By basing the design of procedures to prevent fraudulent transactions within an ERP system on the control environment, the organization can:
Ensure that the procedures are aligned with the organization’s objectives, values, and expectations regarding internal control and fraud prevention
Provide clear and consistent guidance and instructions for the staff and stakeholders involved in the transactions and the ERP system
Implement adequate and appropriate controls and safeguards to mitigate the risks and vulnerabilities of the transactions and the ERP system
Monitor and evaluate the compliance and effectiveness of the procedures and the ERP system, and identify and address any issues or gaps
References = What is Fraud?, Fraud Risk Management - AICPA, What is ERP?, ERP Fraud: How to Prevent It - ERP Focus, [COSO – Control Environment - Deloitte], [How to use COSO to assess IT controls - Journal of Accountancy]
Question # 257
Which of the following is the MOST important course of action to foster an ethical, risk-aware culture?
A.
Implement a fraud detection and prevention framework.
B.
Ensure the alignment of the organization ' s policies and standards to the defined risk appetite.
C.
Establish an enterprise-wide ethics training and awareness program.
D.
Perform a comprehensive review of all applicable legislative frameworks and requirements.
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual, an enterprise-wide ethics training and awareness program is one of the key elements of a strong risk culture, as it helps to promote ethical behavior, raise awareness of risk management principles and practices, and foster a culture of accountability and transparency2
1: Developing Collective Risk Leadership Through CRISC - ISACA 2: CRISC Review Manual, 7th Edition, page 23
Question # 258
Which of the following is MOST helpful in verifying that the implementation of a risk mitigation control has been completed as intended?
A.
An updated risk register
B.
Risk assessment results
C.
Technical control validation
D.
Control testing results
Full Access
Answer:
D
Explanation:
Control testing is the process of verifying that the risk mitigation controls are designed and operating effectively, and that they achieve the intended objectives and outcomes. Control testing can involve various methods, such as observation, inspection, inquiry, re-performance, or simulation. Control testing results can provide evidence and assurance that the implementation of a risk mitigation control has been completed as intended, and that the control is functioning properly and consistently. Control testing results can also identify any issues or deficiencies in the control design or operation, and recommend corrective actions or improvements. The other options are not as helpful as control testing results, because they do not provide a direct and objective verification of the control implementation, but rather focus on other aspects or outputs of the risk management process, as explained below:
A. An updated risk register is a document that records and tracks the identified risks, their characteristics, and their status. An updated risk register can reflect the changes in the risk profile and exposure after the implementation of a risk mitigation control, but it does not verify that the control implementation has been completed as intended, or that the control is effective and reliable.
B. Risk assessment results are the outputs of the risk analysis and evaluation process, which measure the impact and likelihood of the risks, and assign a risk rating and priority. Risk assessment results can indicate the level of risk exposure and the need for risk mitigation controls, but they do not verify that the control implementation has been completed as intended, or that the control is effective and reliable.
C. Technical control validation is the process of ensuring that the technical aspects of a control, such as hardware, software, or network components, are configured and functioning correctly. Technical control validation can verify that the control implementation meets the technical specifications and requirements, but it does not verify that the control implementation has been completed as intended, or that the control is effective and reliable from a businessperspective. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.3, page 130.
Question # 259
Which of the following is the BEST method to mitigate the risk of an unauthorized employee viewing confidential data in a database ' '
A.
Implement role-based access control
B.
Implement a data masking process
C.
Include sanctions in nondisclosure agreements (NDAs)
D.
Install a data loss prevention (DLP) tool
Full Access
Answer:
B
Explanation:
Implementing a data masking process is the best method to mitigate the risk of an unauthorized employee viewing confidential data in a database. Data masking is the process of replacing sensitive data with fictitious but realistic data, such as changing names, addresses, phone numbers, etc. Data masking protects the privacy and confidentiality of the data, while still allowing for testing, analysis, or training purposes. Implementing role-based access control, including sanctions in NDAs, and installing a DLP tool are also useful methods to reduce the risk of data exposure, but they are not as effective as data masking, which prevents the data from being accessed in the first place. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.1, page 3-21.
Question # 260
Which of the following is the BEST recommendation when a key risk indicator (KRI) is generating an excessive volume of events?
A.
Reevaluate the design of the KRIs.
B.
Develop a corresponding key performance indicator (KPI).
C.
Monitor KRIs within a specific timeframe.
D.
Activate the incident response plan.
Full Access
Answer:
A
Explanation:
Reevaluating the design of the key risk indicators (KRIs) is the best recommendation when a KRI is generating an excessive volume of events, because it helps to determine whether the KRI is relevant, reliable, and valid, and whether it needs to be modified or replaced. A KRI is a metric or indicator that helps to monitor and evaluate the likelihood or impact of a risk, or the effectiveness or efficiency of a control. A KRI can be quantitative or qualitative, and can be derived from internal or external sources. An event is an occurrence or incident that may indicate a change or trend in the risk level or performance. A KRI that generates an excessivevolume of events may indicate that the KRI is not well-designed or well-aligned with the risk objectives or criteria, and that it may produce false positives or negatives, or irrelevant or misleading information. Therefore, reevaluating the design of the KRIs is the best recommendation, as it helps to improve the quality and usefulness of the KRIs, and to avoid unnecessary or inappropriate actions or responses. Developing a corresponding key performance indicator (KPI), monitoring KRIs within a specific timeframe, and activating the incident response plan are all possible actions to perform after reevaluating the design of the KRIs, but they are not the best recommendation, as they do not address the root cause of the excessive volume of events. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2, page 97
Question # 261
Several network user accounts were recently created without the required management approvals. Which of the following would be the risk practitioner ' s BEST recommendation to address this situation?
A.
Conduct a comprehensive compliance review.
B.
Develop incident response procedures for noncompliance.
C.
Investigate the root cause of noncompliance.
D.
Declare a security breach and Inform management.
Full Access
Answer:
C
Explanation:
Several network user accounts were recently created without the required management approvals. This indicates that there is a risk of unauthorized access, use, disclosure, modification, or destruction of the network resources or data, which may affect the confidentiality, integrity, and availability of the network.
The best recommendation to address this situation is to investigate the root cause of noncompliance. This means that the risk practitioner should analyze the factors or reasons that led to the creation of the network user accounts without the required management approvals, such as human error, negligence, malice, system failure, process flaw, etc.
Investigating the root cause of noncompliance helps to identify and correct the source of the problem, prevent or reduce the recurrence of the problem, and improve the compliance and security of the network user accounts.
The other options are not the best recommendations to address this situation. They are either secondary or not effective for noncompliance.
The references for this answer are:
Risk IT Framework, page 31
Information Technology & Security, page 25
Risk Scenarios Starter Pack, page 23
Question # 262
It is MOST important to the effectiveness of an IT risk management function that the associated processes are:
A.
aligned to an industry-accepted framework.
B.
reviewed and approved by senior management.
C.
periodically assessed against regulatory requirements.
D.
updated and monitored on a continuous basis.
Full Access
Answer:
D
Explanation:
The effectiveness of an IT risk management function depends on how well it can identify, analyze, evaluate, and treat the IT-related risks that may affect the organization’s objectives and performance. To achieve this, the IT risk management function needs to have processes that are updated and monitored on a continuous basis, so that they can capture the changes in the IT environment, the business context, the risk appetite and tolerance, and the regulatory requirements. Updating and monitoring the IT risk management processes also helps to ensure that they are consistent, reliable, and efficient, and that they provide timely and accurate information for decision making and reporting12. Aligning the IT risk management processes to an industry-accepted framework is important, but not the most important factor for the effectiveness of the function. A framework provides a common language, structure, and methodology for IT risk management, but it does not guarantee that the processes are updated and monitored on a continuous basis. A framework also needs to be customized and adapted to the specific needs and context of theorganization3. Reviewing and approving the IT risk management processes by senior management is important, but not the most important factor for the effectiveness of the function. Senior management support and endorsement are essential for establishing the tone and culture of IT risk management, as well as for allocating the necessary resources and authority for the function. However, senior management review and approval alone do not ensure that the processes are updated and monitored on a continuous basis. Senior management also need to oversee and evaluate the performance and outcomes of the IT riskmanagement function4. Periodically assessing the IT risk management processes against regulatory requirements is important, but not the most important factor for the effectiveness of the function. Regulatory compliance is one of the objectives and drivers of IT risk management, and it requires the function to adhere to the applicable laws, rules, and standards. However, regulatory requirements are not the only source of IT risk, and they may not cover all the aspects and dimensions of IT risk management.Moreover, periodic assessment may not be sufficient to capture the dynamic and evolving nature of IT risk. Therefore, the IT risk management processes need to be updated and monitored on a continuous basis, not only to meet the regulatoryrequirements, but also to address the other sources and impacts of IT risk5. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.1: Risk Response Process, pp. 121-123.
Question # 263
Which of the following is MOST important to ensure when reviewing an organization ' s risk register?
A.
Risk ownership is recorded.
B.
Vulnerabilities have separate entries.
C.
Control ownership is recorded.
D.
Residual risk is less than inherent risk.
Full Access
Answer:
A
Explanation:
 The most important factor to ensure when reviewing an organization’s risk register is that the risk ownership is recorded, as it indicates the authority and responsibility for managing the risk and its associated controls, and facilitates the communication and accountability of the risk management process and activities. The other options are not the most important factors, as they are more related to theidentification, classification, or measurement of the risk, respectively, rather than the management of the risk. References = CRISC Review Manual, 7th Edition, page 101.
Question # 264
Which of the following is the MAIN benefit of involving stakeholders in the selection of key risk indicators (KRIs)?
A.
Improving risk awareness
B.
Obtaining buy-in from risk owners
C.
Leveraging existing metrics
D.
Optimizing risk treatment decisions
Full Access
Answer:
A
Explanation:
 The main benefit of involving stakeholders in the selection of key risk indicators (KRIs) is improving risk awareness, as it helps to communicate the risk exposure, appetite, and tolerance of the organization to the relevant parties. KRIs are metrics that provide information on the level of exposure to a given operational risk1. By involving stakeholders in the selection of KRIs, the risk practitioner can ensure that the KRIs are aligned with the stakeholder expectations, needs, and objectives, and that they reflect the most significant risks that affect the organization. This also helps to foster a risk culture and a shared understanding of risk among the stakeholders, which can enhance the risk management process and performance. The other options are not the main benefit of involving stakeholders in the selection of KRIs, although they may be some of the outcomes or advantages of doing so. Obtaining buy-in from risk owners, leveraging existing metrics, and optimizing risk treatment decisions are all important aspects of risk management, but they are not the primary reason for involving stakeholders in the selection of KRIs. References = Key Risk Indicators; Key Risk Indicators: A Practical Guide; The 10 Types of Stakeholders That You Meet in Business; What are Stakeholders? Stakeholder Definition | ASQ
Question # 265
Which of the following is the BEST approach for a risk practitioner to use for identifying the level of technical debt in an organization?
A.
Review business cases for large organizational projects.
B.
Measure the alignment of technical standards with information security policies.
C.
Analyze trends in technology investments over time.
D.
Compare the current state to the target enterprise architecture (EA).
Full Access
Answer:
D
Explanation:
Technical debt is best understood by identifying the gap between current capabilities and the desired future-state architecture. CRISC states that this is done most effectively bycomparing the current environment to the target enterprise architecture (EA). This comparison identifies outdated technologies, unsupported platforms, integration issues, and areas requiring modernization. Reviewing business cases or investment trends provides financial insights but does not quantify technical debt. Comparing standards with policies highlights compliance issues, not architectural deficiencies. EA comparison allows organizations to quantify how far they are from the strategic architectural roadmap, making it the most accurate method.
[Reference:CRISC Review Manual – Risk Assessment (technical debt evaluation)., ========================================, ]
Question # 266
An organization is developing a risk universe to create a holistic view of its overall risk profile. Which of the following is the GREATEST barrier to achieving the initiative ' s objectives?
A.
Lack of cross-functional risk assessment workshops within the organization
B.
Lack of common understanding of the organization ' s risk culture
C.
Lack of quantitative methods to aggregate the total risk exposure
D.
Lack of an integrated risk management system to aggregate risk scenarios
Full Access
Answer:
B
Explanation:
Lack of common understanding of the organization’s risk culture is the greatest barrier to achieving the initiative’s objectives, because it hinders the alignment and integration of risk management across the organization. Risk culture is the set of shared values, beliefs, and behaviors that influence how risk is perceived and managed in an organization. A risk universe is a comprehensive and structured representation of all the sources and types of risk that an organization faces. Developing a risk universe requires a common understanding of the organization’s risk culture, as it affects the risk appetite, tolerance, and strategy of the organization. Lack of cross-functional risk assessment workshops, lack of quantitative methods to aggregate the total risk exposure, and lack of an integrated risk management system are all challenges that may affect thedevelopment of a risk universe, but they are not the greatest barrier, as they can be overcome with appropriate tools and techniques. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.1, page 44
Question # 267
While reviewing the risk register, a risk practitioner notices that different business units have significant variances in inherent risk for the same risk scenario. Which of the following is the BEST course of action?
A.
Update the risk register with the average of residual risk for both business units.
B.
Review the assumptions of both risk scenarios to determine whether the variance is reasonable.
C.
Update the risk register to ensure both risk scenarios have the highest residual risk.
D.
Request that both business units conduct another review of the risk.
Full Access
Answer:
B
Explanation:
The risk register is a document that records the identified risks, their analysis, and their responses. It is a useful tool for monitoring and controlling the risks throughout the project lifecycle. However, the risk register is not a static document and it should be updated regularly to reflect the changes in the risk environment and the project status. Therefore, when reviewing therisk register, a risk practitioner should not only look at the risk ratings, but also the assumptions and the rationale behind them. Different business units may have different perspectives, contexts, and data sources for the same risk scenario, which can result in significant variances in inherent risk. Inherent risk is the risk level before considering the existing controls or responses. Therefore, the best course of action is to review the assumptions of both risk scenarios to determine whether the variance is reasonable or not. This can help to identify any errors, inconsistencies, or biases in the risk assessment process, and to ensure that the risk register reflects the current and accurate state of the risks. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.1, p. 106-107
Question # 268
Which of the following is the PRIMARY objective for automating controls?
A.
Reducing the need for audit reviews
B.
Facilitating continuous control monitoring
C.
Improving control process efficiency
D.
Complying with functional requirements
Full Access
Answer:
B
Explanation:
The primary objective of automating controls is to facilitate continuous control monitoring. Automation enables real-time or near-real-time oversight of control activities, allowing for prompt detection and response to control failures or anomalies. This continuous monitoring enhances the organization ' s ability to maintain compliance and manage risks effectively.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 4: Information Technology and Security, Section: Control Monitoring and Automation., , , , , , , ]
Question # 269
Which of the following should be determined FIRST when a new security vulnerability is made public?
A.
How severe the vulnerability is across the industry
B.
Whether the affected technology is internet-facing
C.
Whether the affected technology is used within the organization
D.
What mitigating controls are currently in place
Full Access
Answer:
C
Explanation:
The very first action in vulnerability management is confirmingwhether the affected technology exists in the organization’s environment.
CRISC notes:
“Before prioritizing or mitigating, it is critical to determine whether the enterprise uses the affected asset or service.â€
If the organization isnot usingthe affected technology, no further response is required.
After that, severity and mitigating controls are reviewed.
Hence,Cis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Vulnerability and Asset Validation.
Question # 270
The MAIN purpose of a risk register is to:
A.
document the risk universe of the organization.
B.
promote an understanding of risk across the organization.
C.
enable well-informed risk management decisions.
D.
identify stakeholders associated with risk scenarios.
Full Access
Answer:
C
Explanation:
The main purpose of a risk register is to enable well-informed risk management decisions by providing a comprehensive and up-to-date record of all the identified risks, their analysis, and their responses. A risk register is a tool that helps to document, monitor, and communicate the status and outcome of risk management activities. A risk register also facilitates the review and evaluation of the effectiveness of risk management processes and controls. Documenting the risk universe, promoting an understanding of risk,and identifying stakeholders are possible benefits of a risk register, but they are not the main purpose. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1.3, page 531
1: ISACA Certified in Risk and Information Systems Control (CRISC®) Exam Guide, Answer to Question 640.
Question # 271
While reviewing an organization ' s monthly change management metrics, a risk practitioner notes that the number of emergency changes has increased substantially Which of the following would be the BEST approach for the risk practitioner to take?
A.
Temporarily suspend emergency changes.
B.
Document the control deficiency in the risk register.
C.
Conduct a root cause analysis.
D.
Continue monitoring change management metrics.
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual, a root cause analysis is a technique that identifies the underlying causes of an event or a problem. It helps to determine the most effective actions to prevent or mitigate the recurrence of the event or problem. A root cause analysis is the best approach for the risk practitioner to take in this scenario, because it will help to understand why the number of emergency changes has increased substantially and what can be done to address the issue. The other options are not the best approaches, because they do not address the underlying causes of the problem. Temporarily suspending emergency changes may disrupt the business operations and create more risks. Documenting the control deficiency in the risk register is a passive action that does not resolve the problem. Continuing monitoring change management metrics is an ongoing activity that does not provide any insight into the problem. References = CRISC Review Manual, 7th Edition, Chapter 3, Section 3.2.4, page 130.
Question # 272
Which of the following shortcomings of perimeter security does Zero Trust aim to resolve?
A.
Lack of access verification for systems on the internal network
B.
Identification and authentication failures for users
C.
Poorly configured firewall rules introducing security breaches
D.
Ineffective load balancing on network devices
Full Access
Answer:
A
Explanation:
Zero Trustassumes that no system or user is inherently trustworthy—even within the internal network. It addresses theinadequacy of perimeter securityby enforcing continuous verification for every access request.
[Reference:CRISC Manual – Domain 2, Slide 128-129, , , , ]
Question # 273
Which of the following provides the BEST evidence that robust risk management practices are in place within an organization?
A.
A management-approved risk dashboard
B.
A current control framework
C.
A regularly updated risk register
D.
Regularly updated risk management procedures
Full Access
Answer:
C
Explanation:
ï‚· Importance of a Risk Register:
A risk register is a critical tool for documenting, tracking, and managing risks within an organization. It serves as a central repository for all identified risks, detailing their status, impact, likelihood, and the actions taken to mitigate them.
A regularly updated risk register demonstrates an active and ongoing risk management process, reflecting the organization ' s commitment to identifying and addressing risks promptly.
ï‚· Evidence of Robust Risk Management:
The risk register shows the organization ' s proactive approach to risk management by continuously monitoring and updating risks.
It provides transparency and accountability, allowing stakeholders to see how risks are being managed and mitigated over time.
Regular updates ensure that new risks are identified and existing risks are reassessed, indicating a dynamic and responsive risk management practice.
ï‚· Comparing Other Options:
Management-Approved Risk Dashboard:While useful for summarizing risk information, a dashboard does not provide the detailed, ongoing updates and comprehensive tracking found in a risk register.
Current Control Framework:A control framework outlines the controls in place but does not detail specific risks or their management.
Regularly Updated Risk Management Procedures:Procedures are important but do not provide the same level of detailed risk tracking and management as a risk register.
ï‚· References:
The CRISC Review Manual emphasizes the importance of a risk register in consolidating and tracking risk data, making it an essential component of robust risk management practices (CRISC Review Manual, Chapter 2: IT Risk Assessment, Section 2.6 Risk Register)​​ .
Question # 274
Which of the following is the MOST important step to ensure regulatory requirements are adequately addressed within an organization?
A.
Obtain necessary resources to address regulatory requirements
B.
Develop a policy framework that addresses regulatory requirements
C.
Perform a gap analysis against regulatory requirements.
D.
Employ IT solutions that meet regulatory requirements.
Full Access
Answer:
B
Explanation:
The most important step to ensure regulatory requirements are adequately addressed within an organization is to develop a policy framework that addresses regulatory requirements. A policy framework is a set of principles, rules, and standards that guide the organization’s actions and decisions. By developing a policy framework that addresses regulatory requirements, the organization can establish a clear and consistent direction, expectation, and accountability for complying with the relevant laws and regulations. Obtaining necessary resources, performing a gap analysis, and employing IT solutions are other possible steps, but they are not as important as developing a policy framework. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 4; CRISC Review Manual, 6th Edition, page 153.
Question # 275
Which of the following is the FIRST step in managing the security risk associated with wearable technology in the workplace?
A.
Identify the potential risk.
B.
Monitor employee usage.
C.
Assess the potential risk.
D.
Develop risk awareness training.
Full Access
Answer:
A
Explanation:
The security risk associated with wearable technology in the workplace is the possibility and impact of unauthorized access, disclosure, or use of the data or information that are collected, stored, or transmitted by the wearable devices, such as smartwatches, fitness trackers, or glasses, that are worn or used by the employees12.
The first step in managing the security risk associated with wearable technology in the workplace is to identify the potential risk, which is the process of recognizing and describing the sources,causes, and consequences of the risk, and the potential impacts on the organization’s objectives, performance, and value creation34.
Identifying the potential risk is the first step because it provides the basis and input for the subsequent steps of the risk management process, such as assessing, treating, monitoring, and communicating the risk34.
Identifying the potential risk is also the first step because it enables the organization to understand and prioritize the risk, and to allocate the appropriate resources and controls for the risk management process34.
The other options are not the first step, but rather possible subsequent steps that may depend on or follow the identification of the potential risk. For example:
Monitoring employee usage is a step that involves collecting and analyzing data and information on the frequency, duration, and purpose of the wearable devices that are used by the employees, and detecting and reporting any deviations, anomalies, or issues that may indicate a security risk5 . However, this step is not the first step because it requires theidentification of the potential risk to provide the guidance and standards for the monitoring process5 .
Assessing the potential risk is a step that involves estimating and evaluating the likelihood and impact of the risk, and the level of risk exposure or tolerance for the organization34. However, this step is not the first step because it requires the identification of the potential risk to provide the information and data for the assessment process34.
Developing risk awareness training is a step that involves educating and training the employees and other stakeholders on the security risks and best practices associated with the wearable technology, and informing them of their roles, obligations, and responsibilities for the risk management process . However, this step is not the first step because it requires the identification of the potential risk to provide the content and objectives for the training process . References =
1: Wearable Devices in the Workplace: Security Threats and Protection1
2: 10 security risks of wearables | CSO Online2
3: Risk IT Framework, ISACA, 2009
4: IT Risk Management Framework, University of Toronto, 2017
5: Continuous Monitoring - ISACA3
Continuous Monitoring: A New Approach to Risk Management - ISACA Journal4
What Is Security Awareness Training and Why Is It Important? - Kaspersky5
Security Awareness Training - Cybersecurity Education Online | Proofpoint US
Question # 276
A risk practitioner is reporting on an increasing trend of ransomware attacks in the industry. Which of the following information is MOST important to include to enable an informed response decision by key stakeholders?
A.
Methods of attack progression
B.
Losses incurred by industry peers
C.
Most recent antivirus scan reports
D.
Potential impact of events
Full Access
Answer:
D
Explanation:
The potential impact of events is the estimated magnitude and likelihood of the consequences that may result from a risk scenario. The potential impact of events can help key stakeholders understand the severity and urgency of the risk, and prioritize the appropriate response actions. The potential impact of events can be expressed in quantitative or qualitative terms, such as financial loss, operational disruption, reputational damage, legal liability, etc. The potential impact of events is the most important information to include when reporting on an increasing trend of ransomware attacks in the industry, as it can help stakeholders assess the level of risk exposure and the adequacy of the existing controls. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: Risk Analysis, p. 87-89.
Question # 277
A risk practitioner has been asked to propose a risk acceptance framework for an organization. Which of the following is the MOST important consideration for the risk practitioner to address in the framework?
A.
Consistent forms to document risk acceptance rationales
B.
Acceptable scenarios to override risk appetite or tolerance thresholds
C.
Individuals or roles authorized to approve risk acceptance
D.
Communication protocols when a risk is accepted
Full Access
Answer:
C
Explanation:
When proposing a risk acceptance framework for an organization, the most important consideration for the risk practitioner is to clearly define the individuals or roles authorized to approve risk acceptance. This ensures that the process is controlled, accountable, and aligned with the organization’s risk management policies.
Risk Acceptance Framework:
Purpose:A risk acceptance framework provides structured criteria and processes for deciding whether to accept a risk. This includes evaluating the risk against the organization ' s risk appetite and tolerance.
Authorization:Identifying who has the authority to accept risk is critical. This ensures that only those with the appropriate knowledge, experience, and understanding of the organization ' s risk appetite and strategic objectives can make these decisions.
Importance of Authorized Individuals:
Accountability:Clearly defined roles for risk acceptance ensure accountability. It is essential that those making the decisions are accountable for the outcomes and understand the potential impact of their decisions.
Consistency:By defining specific roles, the organization ensures consistency in risk acceptance decisions, reducing the likelihood of ad-hoc or inconsistent risk management practices.
Alignment with Strategy:Authorized individuals are typically those who understand the strategic objectives of the organization, ensuring that risk acceptance aligns with these goals.
[References:, The CRISC Review Manual emphasizes that risk acceptance must be formally authorized by individuals with the appropriate level of authority and responsibility within the organization​​., According to ISACA’s guidelines, effective risk management frameworks must include clear definitions of who can accept risks to ensure proper oversight and alignment with organizational goals ., , , , , , , , , , , ]
Question # 278
Which of the following BEST enables a proactive approach to minimizing the potential impact of unauthorized data disclosure?
A.
Cyber insurance
B.
Data backups
C.
Incident response plan
D.
Key risk indicators (KRIs)
Full Access
Answer:
D
Explanation:
Key Risk Indicators (KRIs) are metrics used by organizations to provide early warning signs of potential risks, including unauthorized data disclosure. By monitoring KRIs, organizations can proactively identify vulnerabilities and take corrective actions before a risk materializes. This proactive approach is essential in minimizing the potential impact of data breaches.​
According to ISACA ' s CRISC Review Manual, KRIs are defined as " metrics capable of showing that the enterprise is, or has a high probability of being, subject to a risk that exceeds the defined risk appetite. " They are critical to the measurement and monitoring of risk and performance optimization. ​ISACA
While data backups (Option B) are vital for data recovery post-incident, they do not prevent unauthorized disclosures. An incident response plan (Option C) is reactive, focusing on responding after an incident has occurred. Cyber insurance (Option D) provides financial compensation post-incident but does not prevent the occurrence of data breaches.​
Therefore, implementing and monitoring KRIs is the most proactive approach to minimizing the potential impact of unauthorized data disclosure.
Question # 279
Which of the following would have the GREATEST impact on reducing the risk associated with the implementation of a big data project?
A.
Data processing
B.
Data quality
C.
Data scalability
D.
Data governance
Full Access
Answer:
D
Explanation:
Data governanceprovides a structured framework for handling data access, classification, compliance, and security. It ensures accountability, roles, and control mechanisms—critical formanaging risk in big data environments.
[Reference:CRISC Manual – Domain 3, Slide 310-311, , , , ]
Question # 280
Who is the BEST person to an application system used to process employee personal data?
A.
Compliance manager
B.
Data privacy manager
C.
System administrator
D.
Human resources (HR) manager
Full Access
Answer:
B
Explanation:
The data privacy manager is the best person to an application system used to process employee personal data, because they are responsible for ensuring that the organization complies with the applicable data protection laws and regulations, and that the personal data of employees are collected, stored, processed, and disposed of in a secure and ethical manner. The data privacy manager is also responsible for establishing and maintaining the data privacy policies, procedures, and controls, and for conducting data privacy impact assessments and audits. The compliance manager, the system administrator, and the human resources (HR) manager are all involved in the of the application system, but they are not the best person to it, as they do not have the primary accountability and expertise for data privacy. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 158
Question # 281
Which of the following is the MOST reliable validation of a new control?
A.
Approval of the control by senior management
B.
Complete and accurate documentation of control objectives
C.
Control owner attestation of control effectiveness
D.
Internal audit review of control design
Full Access
Answer:
D
Explanation:
ï‚· Internal Audit Review:
An internal audit review of control design involves a thorough examination of the control’s structure, implementation, and effectiveness.
Auditors use a systematic, disciplined approach to evaluate and improve the effectiveness of risk management, control, and governance processes.
ï‚· Steps in Audit Review:
Understand Control Objectives:Auditors ensure that the control is designed to meet specific risk management objectives.
Evaluate Implementation:Check whether the control has been implemented as designed.
Test Effectiveness:Perform tests to verify that the control operates effectively and consistently over time.
ï‚· Importance of Audit Review:
Provides independent and objective assurance that the control is appropriately designed and functioning as intended.
Identifies any deficiencies or areas for improvement in the control design.
ï‚· Comparing Other Validation Methods:
Senior Management Approval:Indicates support but does not validate effectiveness.
Documentation of Control Objectives:Important for understanding intent but not validation.
Control Owner Attestation:Provides insight but lacks the independence of an audit.
ï‚· References:
The CRISC Review Manual highlights the role of internal audits in validating control design and ensuring effective risk management (CRISC Review Manual, Chapter 3: Risk Response and Mitigation, Section 3.9 Control Testing and Effectiveness Evaluation)​​.
Question # 282
In an organization dependent on data analytics to drive decision-making, which of the following would BEST help to minimize the risk associated with inaccurate data?
A.
Establishing an intellectual property agreement
B.
Evaluating each of the data sources for vulnerabilities
C.
Periodically reviewing big data strategies
D.
Benchmarking to industry best practice
Full Access
Answer:
C
Explanation:
Periodically reviewing big data strategies is the best option to minimize the risk of inaccurate data, because it allows the organization to assess the quality, validity, and reliability of the data sources and the analytics methods. It also enables the organization to identify and address any gaps, errors, or inconsistencies in the data and the results. By reviewing the big data strategies, the organization can ensure that the data analytics are aligned with the business objectives and the risk appetite.
Establishing an intellectual property agreement is not relevant to the risk of inaccurate data, as it is a legal measure to protect the ownership and use of the data, not its quality or accuracy.
Evaluating each of the data sources for vulnerabilities is a good practice, but it is not sufficient to minimize the risk of inaccurate data, as it only focuses on the security aspect of the data, not the validity or reliability of the data itself.
Benchmarking to industry best practice is a useful way to compare the performance and results of the data analytics, but it does not directly address the risk of inaccurate data, as it assumes that the data and the methods are already valid and reliable. References = Risk IT Framework, 2nd Edition, ISACA, 2019, page 62-63.
Question # 283
Which of the following is the PRIMARY objective of risk management?
A.
Identify and analyze risk.
B.
Achieve business objectives
C.
Minimi2e business disruptions.
D.
Identify threats and vulnerabilities.
Full Access
Answer:
B
Explanation:
The primary objective of risk management is to achieve business objectives, as risk management involves identifying, assessing, responding, and monitoring the risks that may affect the desired outcomes and performance of the organization, and aligning them with the risk tolerance and appetite of the organization. Identifying and analyzing risk, minimizing business disruptions, andidentifying threats and vulnerabilities are not the primary objectives, as they are more related to the process, outcome, or source of risk management, respectively, rather than the purpose or value of risk management. References = CRISC Review Manual, 7th Edition, page 99.
Question # 284
A risk practitioner is reviewing a vendor contract and finds there is no clause to control privileged access to the organization ' s systems by vendor employees. Which of the following is the risk practitioner ' s BEST course of action?
A.
Contact the control owner to determine if a gap in controls exists.
B.
Add this concern to the risk register and highlight it for management review.
C.
Report this concern to the contracts department for further action.
D.
Document this concern as a threat and conduct an impact analysis.
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual1, the contracts department is responsible for drafting, reviewing, and negotiating contracts with vendors and other third parties. The contracts department should ensure that the contracts include adequate clauses and terms to address the risks and controls related to the vendor services and activities. Therefore, the best course of action for the risk practitioner when finding a missing clause to control privileged access to the organization’s systems by vendor employees is to report this concern to the contracts department for further action. The contracts department can then revise the contract to include the necessary clause, or seek alternative solutions to mitigate the risk of unauthorized or inappropriate access by vendor employees. References = CRISC Review Manual1, page 229.
Question # 285
Which of the following risk management practices BEST facilitates the incorporation of IT risk scenarios into the enterprise-wide risk register?
A.
Key risk indicators (KRls) are developed for key IT risk scenarios
B.
IT risk scenarios are assessed by the enterprise risk management team
C.
Risk appetites for IT risk scenarios are approved by key business stakeholders.
D.
IT risk scenarios are developed in the context of organizational objectives.
Full Access
Answer:
D
Explanation:
 IT risk scenarios are hypothetical situations that describe how IT-related events or incidents could adversely affect an organization’s objectives, assets, or operations. IT risk scenarios can help to identify, analyze, and prioritize IT risks, and to develop appropriate responses and controls1.
An enterprise-wide risk register is a document that records and tracks the significant risks that an organization faces across its various functions, processes, and activities. An enterprise-wide risk register can help to provide a comprehensive and consistent view of the organization’s risk profile, and to support the decision making and reporting of the risk management function2.
The best practice that facilitates the incorporation of IT risk scenarios into the enterprise-wide risk register is to develop IT risk scenarios in the context of organizational objectives. This means that IT risk scenarios should be aligned with and derived from the organization’s strategic goals, mission, vision, and values. IT risk scenarios should also consider the interdependenciesand interactions between IT and other business domains, and the potential impact of IT risks on the organization’s performance and reputation3.
By developing IT risk scenarios in the context of organizational objectives, the organization can ensure that the IT risk scenarios are relevant, realistic, and meaningful for the enterprise-wide risk management. The organization can also ensure that the IT risk scenarios are consistent and comparable with other types of risk scenarios, such as financial, operational, or reputational risk scenarios. This can facilitate the integration and consolidation of IT risk scenarios into the enterprise-wide risk register, and enable a holistic and balanced assessment and reporting of the organization’s risks4.
The other options are not as effective as developing IT risk scenarios in the context of organizational objectives for incorporating IT risk scenarios into the enterprise-wide risk register. Developing key risk indicators (KRIs) for key IT risk scenarios can help to monitor and measure the IT risk exposure and performance, but it does not ensure that the IT risk scenarios are aligned with the organizational objectives or integrated with other risk scenarios. Assessing IT risk scenarios by the enterprise risk management team can help to validate and prioritize the IT risk scenarios, but it does not ensure that the IT risk scenarios are derived from the organizational objectives or consistent with other risk scenarios. Approving risk appetites for IT risk scenarios by key business stakeholders can help to establish the acceptable level of IT risk taking andtolerance, but it does not ensure that the IT risk scenarios are based on the organizational objectives or comparable with other risk scenarios. References =
IT Risk Scenario Development - ISACA
Risk Register - ISACA
Identifying Risks and Scenarios Threatening the Organization as an Enterprise - A New Enterprise Risk Identification Framework
Risk Register 2021-2022 - UNECE
[CRISC Review Manual, 7th Edition]
Question # 286
From a business perspective, which of the following is the MOST important objective of a disaster recovery test?
A.
The organization gains assurance it can recover from a disaster
B.
Errors are discovered in the disaster recovery process.
C.
All business-critical systems are successfully tested.
D.
All critical data is recovered within recovery time objectives (RTOs).
Full Access
Answer:
D
Explanation:
A disaster recovery test is a simulation of a disaster scenario that evaluates the effectiveness and readiness of the disaster recovery plan. The main purpose of a disaster recovery test is to ensure that the organization can resume its normal operations as quickly as possible after a disaster, with minimal or no data loss. Therefore, the most important objective of a disaster recovery test from a business perspective is to verify that all critical data can be recovered within the RTOs, which are the maximum acceptable time frames for restoring the data and systems after a disaster. If the RTOs are not met, the organization may face significant financial, operational, and reputationallosses. The other options are not the most important objectives of a disaster recovery test, although they may be beneficial outcomes. Gaining assurance that the organization can recover from a disaster is a subjective and qualitative goal, while recovering data within RTOs is a measurable and quantitative goal. Discovering errors in the disaster recovery process is a valuable result of a disaster recovery test, but it is not the primary objective. The objective is to correct the errors and improve the process, not just to find them. Testing all business criticalsystems is a necessary step in a disaster recovery test, but it is not the ultimate goal. The goal is to ensure that the systems can be restored and function properly within the RTOs. References = CRISC Review Manual, pages 197-1981; CRISC Review Questions, Answers & Explanations Manual, page 572
Question # 287
Senior management has asked a risk practitioner to develop technical risk scenarios related to a recently developed enterprise resource planning (ERP) system. These scenarios will be owned by the system manager. Which of the following would be the BEST method to use when developing the scenarios?
A.
Cause-and-effect diagram
B.
Delphi technique
C.
Bottom-up approach
D.
Top-down approach
Full Access
Answer:
A
Explanation:
A cause-and-effect diagram, also known as a fishbone diagram or an Ishikawa diagram, is a graphical tool that helps to identify and analyze the potential causes and effects of a problem or an event. A cause-and-effect diagram can be used to develop technical risk scenarios related to a recently developed ERP system, because it can help to:
Break down the complex problem or event into manageable and measurable categories and subcategories of causes and effects
Visualize the relationships and interactions among the various factors that contribute to the problem or event
Identify the root causes and the most significant effects of the problem or event
Generate ideas and hypotheses for testing and validating the problem or event
Communicate and present the problem or event clearly and logically to the stakeholders1
A cause-and-effect diagram can be constructed by following these steps:
Define the problem or event and write it in a box on the right side of the diagram
Draw a horizontal line from the box to the left side of the diagram, representing the main spine of the fishbone
Identify the major categories of causes that affect the problem or event, such as people, process, technology, environment, etc., and write them on the branches of the spine
For each category, brainstorm and list the possible subcategories and specific causes that influence the problem or event, and write them on the sub-branches of the spine
For each cause, identify and list the possible effects or consequences that result from the problem or event, and write them on the sub-sub-branches of the spine
Analyze the diagram and prioritize the causes and effects based on their frequency, severity, and controllability
Develop technical risk scenarios based on the most critical causes and effects, and describe how they could affect the ERP system and the organization1
Question # 288
As part of its risk strategy, an organization decided to transition its financial system from a cloud-based provider to an internally managed system. Which of the following should the risk practitioner do FIRST?
A.
Reassess whether the risk responses properly address known risks and vulnerabilities
B.
Analyze the risk register to identify potential updates and changes
C.
Evaluate existing control test plans of the system for potential changes
D.
Update the processes within impacted financial control assessments
Full Access
Answer:
A
Explanation:
Whenever there is achange in sourcing strategy, such as moving from cloud to internal hosting, thefirst stepis to reassess theeffectiveness and completeness of existing risk responsesand confirm that they still mitigate the risks appropriately.
CRISC emphasizes:
“When transitioning services or changing control environments, practitioners should reassess risk responses and validate that previously identified risks and vulnerabilities remain properly addressed.â€
Only after reassessment should the practitioner proceed to update registers, controls, and audit plans.
Hence,Ais the correct answer.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Managing Control Changes.
Question # 289
Which of the following should be the PRIMARY focus of an IT risk awareness program?
A.
Ensure compliance with the organization ' s internal policies
B.
Cultivate long-term behavioral change.
C.
Communicate IT risk policy to the participants.
D.
Demonstrate regulatory compliance.
Full Access
Answer:
B
Explanation:
The primary focus of an IT risk awareness program is to cultivate long-term behavioral change. An IT risk awareness program is a program that educates and informs the stakeholders, such as the employees, managers, customers, or partners, about the IT risks and the IT risk management activities. An IT risk awareness program helps to increase the knowledge and understanding of the IT risks and the IT risk management objectives, strategies, and processes, and to promote the participation and collaboration of the stakeholders in the IT risk management activities. Theprimary focus of an IT risk awareness program is to cultivate long-term behavioral change, which is the change in the attitudes, beliefs, values, and actions of the stakeholders regarding the IT risks and the IT risk management activities. Cultivating long-term behavioral change helps to create and sustain a risk-aware culture, which is a culture that recognizes,respects, and supports the IT risk management activities, and that encourages the stakeholders to take responsibility and ownership of the IT risks and the IT risk management activities. Cultivating long-term behavioral change also helps to improve the effectiveness and efficiency of the IT risk management activities, and to align the IT risk management activities with the business goals and values. Ensuring compliance with the organization’s internal policies, communicating IT risk policy to the participants, and demonstrating regulatory compliance are not the primary focus of an IT risk awareness program, as they are either the benefits or the objectives of the IT risk awareness program, and they do not address the primary need of changing the behavior of the stakeholders. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 36.
Question # 290
Which of the following should be the FIRST course of action if the risk associated with a new technology is found to be increasing?
A.
Re-evaluate current controls.
B.
Revise the current risk action plan.
C.
Escalate the risk to senior management.
D.
Implement additional controls.
Full Access
Answer:
B
Explanation:
A risk action plan is a document that outlines the actions to be taken to mitigate or avoid a risk. A risk action plan should be revised when the risk associated with a new technology is found to be increasing, as this indicates that the current plan is not effective or sufficient. Revising the risk action plan can help identify the root causes of the risk increase, evaluate the effectiveness of current controls, and implement additional or alternative controls as needed. Re-evaluatingcurrent controls, escalating the risk to senior management, and implementing additional controls are possible steps in the revision process, but they are not the first course of action. The first course of action should be to update the risk action plan to reflect the current risk situation and the appropriate risk response.
Question # 291
When updating the risk register after a risk assessment, which of the following is MOST important to include?
A.
Historical losses due to past risk events
B.
Cost to reduce the impact and likelihood
C.
Likelihood and impact of the risk scenario
D.
Actor and threat type of the risk scenario
Full Access
Answer:
C
Explanation:
A risk register is a document that records and tracks the information about the risks that may affect the organization’s objectives, such as the risk description, category, source, cause, impact, probability, status, owner, response, etc.
When updating the risk register after a risk assessment, the most important information to include is the likelihood and impact of the risk scenario. This means that the risk registershouldreflect the current or updated estimates of the probability and consequence of the risk scenario, based on the risk analysis and evaluation methods and criteria.
The likelihood and impact of the risk scenario helps to determine the risk level and priority, select the most appropriate risk response, allocate the resources and budget for risk management, and monitor and report the risk performance and outcomes.
The other options are not the most important information to include when updating the risk register after a risk assessment. They are either secondary or not essential for risk management.
The references for this answer are:
Risk IT Framework, page 29
Information Technology & Security, page 23
Risk Scenarios Starter Pack, page 21
Question # 292
Which of the following is the BEST way to determine whether system settings are in alignment with control baselines?
A.
Configuration validation
B.
Control attestation
C.
Penetration testing
D.
Internal audit review
Full Access
Answer:
A
Explanation:
The best way to determine whether system settings are in alignment with control baselines is to perform configuration validation. Configuration validation is the process of verifying that the system settings and parameters are consistent with the predefined standards and requirements, and that they reflect the current and desired state of the system. Configuration validation helps to ensure that the system is configured correctly and securely, and that it complies with the relevant policies, regulations, and bestpractices. Configuration validation also helps to identify and correct any deviations or errors in the system settings, and to prevent or mitigate any potential risks or issues. The other options are not as effective as configuration validation, although they may provide some input or information for the system alignment. Control attestation, penetration testing, and internal audit review are all activities that can help to assess or evaluate the system alignment, but they do not necessarily determine or validate the system settings. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.1, page 3-11.
Question # 293
Which of the following is MOST important for a risk practitioner to confirm when reviewing an organization’s information security policies?
A.
Aligned with information security procedures.
B.
Written at a high level to communicate the organization’s intentions.
C.
Frequently updated to address minor technology changes.
D.
Drafted at a technical level to focus on common security industry practices.
Full Access
Answer:
B
Explanation:
The correct answer is B . Policies should communicate management’s direction, intent, and governing principles at a high level. Procedures provide detailed implementation steps; standards provide mandatory specific requirements. The uploaded study material states that policies state management direction and governing principles, while standards define required criteria and procedures describe steps. It also defines policies as high-level statements outlining the organization’s stance on information security.
A is useful, but procedures should align to policy rather than define the policy’s primary quality. C is incorrect because minor technology changes usually belong in standards/procedures. D is incorrect because technical detail belongs in standards or procedures, not high-level policy.
===========
Question # 294
Which of the following techniques is MOST helpful when quantifying the potential loss impact of cyber risk?
A.
Cost-benefit analysis
B.
Penetration testing
C.
Business impact analysis (BIA)
D.
Security assessment
Full Access
Answer:
C
Explanation:
ï‚· Understanding Business Impact Analysis (BIA):
BIA is a process used to identify and evaluate the potential effects (impact) of interruptions to critical business operations as a result of a disaster, accident, or emergency.
It helps quantify the potential loss impact of cyber risks by assessing the financial and operational consequences of disruptions.
ï‚· Quantifying Loss Impact:
BIA involves determining the value of business processes and the impact of their loss. This includes evaluating factors such as revenue loss, additional operational costs, legal penalties, and reputational damage.
By analyzing the criticality of business functions and their dependencies, BIA provides a detailed understanding of potential impacts, aiding in the development of risk mitigation strategies.
ï‚· Comparing Other Techniques:
Cost-Benefit Analysis:Useful for evaluating the cost-effectiveness of controls but does not provide a comprehensive assessment of potential loss impacts.
Penetration Testing:Identifies vulnerabilities but does not quantify the business impact of exploiting those vulnerabilities.
Security Assessment:Evaluates security controls but is not focused on the broader business impact of potential disruptions.
ï‚· References:
The CRISC Review Manual emphasizes the role of BIA in assessing the impact of risks on business operations and quantifying potential losses (CRISC Review Manual, Chapter 2: IT Risk Assessment, Section 2.7 Business Impact Analysis)​​.
Question # 295
Which of the following will MOST likely change as a result of the decrease in risk appetite due to a new privacy regulation?
A.
Key risk indicator (KRI) thresholds
B.
Risk trends
C.
Key performance indicators (KPIs)
D.
Risk objectives
Full Access
Answer:
A
Explanation:
KRI thresholds are the levels or points that trigger an action or a response when a KRI reaches or exceeds them. They reflect the risk appetite of the organization, which is the amount and type of risk that it is willing to accept in pursuit of its objectives. A new privacy regulation may reduce the risk appetite of the organization, as it may impose stricter requirements and penalties for non-compliance. Therefore, the organization may need to adjust its KRI thresholds to lower levels, to ensure that it can identify and manage privacy risks more effectively and proactively
Question # 296
Which of the following is the MOST important objective of regularly presenting the project risk register to the project steering committee?
A.
To allocate budget for resolution of risk issues
B.
To determine if new risk scenarios have been identified
C.
To ensure the project timeline is on target
D.
To track the status of risk mitigation actions
Full Access
Answer:
D
Explanation:
Project risk register: A document that records the identified risks, their likelihood, impact, and mitigation strategies for a project1.
Project steering committee: A group of senior stakeholders and experts who oversee and support a project from a higher level2.
Risk mitigation actions: The measures taken to prevent, reduce, or transfer the risks that may affect a project3.
The most important objective of regularly presenting the project risk register to the project steering committee is to track the status of risk mitigation actions. Tracking the status of risk mitigation actions can help the project steering committee to:
Monitor and measure the performance and effectiveness of the risk management process and controls
Evaluate the progress and outcomes of the risk mitigation actions against the project goals and objectives
Identify and resolve any issues, challenges, or gaps in the risk mitigation actions
Provide guidance, feedback, and support to the project manager and the project team
Adjust or revise the risk mitigation actions as needed to reflect the changes in the project scope, schedule, budget, or environment
The other options are not the most important objective of regularly presenting the project risk register to the project steering committee, although they may be relevant or beneficial. Allocating budget for resolution of risk issues, which means assigning financial resources to address and resolve the risks that may affect a project, may be a part of the risk management process, but it is not the primary purpose of presenting the project risk register, which is more focused on tracking and reporting the risk status and actions. Determining if new risk scenarios have been identified, which means finding out if there are any additional or emerging risks that may impact a project, may be a useful outcome of presenting the project risk register, but it is not the main objective, which is more concerned with tracking and reporting the existing risk status and actions. Ensuring the project timeline is on target, which means verifying that the project is progressing according to the planned schedule and milestones, may be a benefit of presenting the project risk register, but it is not the key objective, which is more related to tracking and reporting the risk status and actions.
References = Risk Register: A Project Manager’s Guide with Examples [2023] • Asana, Project Steering Committee: Roles, Best Practices, Challenges, Risk Mitigation: Definition, Strategies, and Examples
Question # 297
An updated report from a trusted research organization shows that attacks have increased in the organization ' s industry segment. What should be done FIRST to integrate this data into risk assessments?
A.
Average the ransomware attack frequencies together
B.
Revise the threat frequency for ransomware attack types
C.
Adjust impact amounts based on the average ransom
D.
Use the new frequency as the maximum value in a Monte Carlo simulation
Full Access
Answer:
B
Explanation:
New threat intelligence primarily impacts thefrequency componentof risk calculations.
CRISC states:
“When new information about threats is available, it must be incorporated into risk assessment by adjusting threat event frequencies in related scenarios.â€
AandDare statistical manipulations, not practical first steps.
Caddresses impact, not likelihood.
Hence,B. Revise the threat frequencyis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Incorporating Threat Intelligence.
Question # 298
The annualized loss expectancy (ALE) method of risk analysis:
A.
helps in calculating the expected cost of controls
B.
uses qualitative risk rankings such as low. medium and high.
C.
can be used m a cost-benefit analysts
D.
can be used to determine the indirect business impact.
Full Access
Answer:
C
Explanation:
The annualized loss expectancy (ALE) method of risk analysis is a quantitative method that estimates the expected monetary loss that can result from a risk over a one year period. The ALE is calculated by multiplying the single loss expectancy (SLE), which is the monetary loss from a single occurrence of a risk, by the annualized rate of occurrence (ARO), which is the frequency of the risk occurring in a year. The ALE can be used in a cost-benefit analysis to compare the cost of implementing a control or a risk response with the expected benefit of reducing the loss. The ALE can help to justify the investment in risk management and to prioritize the risks based on their financial impact. The other options are not accurate descriptions of the ALE method of risk analysis, as they involve different aspects or methods of risk analysis. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.3.2.1, pp. 60-61.
Question # 299
Which of the following risk register updates is MOST important for senior management to review?
A.
Extending the date of a future action plan by two months
B.
Retiring a risk scenario no longer used
C.
Avoiding a risk that was previously accepted
D.
Changing a risk owner
Full Access
Answer:
C
Explanation:
A risk register is a document that records and tracks the information and status of the identified risks and their responses. It includes the risk description, category, source, cause, impact, probability, priority, response, owner, action plan, status, etc.
A risk register update is a change or modification to the information or status of the risks and their responses in the risk register. It may be triggered by the occurrence or resolution of a risk event, the identification or evaluation of a new or emerging risk, the implementation or completion of a risk response, the monitoring or review of the risk performance, etc.
The most important risk register update for senior management to review is avoiding a risk that was previously accepted, which means that the organization has decided to eliminate or withdraw from the risk exposure or activity that may cause the risk, instead of tolerating or retaining the risk as before. This may indicate a significant change in the organization’s risk appetite, strategy, objectives, or environment, and it may have a major impact on the organization’s performance and value.
The other options are not the most important risk register updates for senior management to review, because they do not indicate a significant change or impact on the organization’s risk profile or performance.
Extending the date of a future action plan by two months means that the organization has postponed the implementation or completion of the planned actions or measures to address the risk, due to some reasons or constraints. This may indicate a delay or deviation from the expected or desired risk outcome, but it may not have a major impact on the organization’s performance and value, unless the risk is very urgent or critical.
Retiring a risk scenario no longer used means that the organization has removed or discarded the risk scenario that is no longer relevant or applicable to the organization’s objectives or operations, due to some changes or developments. This may indicate a reduction or improvement in the organization’s risk exposure or level, but it may not have a major impact on the organization’s performance and value, unless the risk scenario was very significant or influential.
Changing a risk owner means that the organization has assigned or transferred the responsibility and accountability for the risk and its response to a different person or role, due to some reasons or circumstances. This may indicate a change or improvement in the organization’s risk governance or culture, but it may not have a major impact on the organization’s performance and value, unless the risk owner was very ineffective or inappropriate. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 160
CRISC Practice Quiz and Exam Prep
Question # 300
Which of the following is MOST important for management to consider when deciding whether to invest in an IT initiative that exceeds management ' s risk appetite?
A.
Risk management budget
B.
Risk management industry trends
C.
Risk tolerance
D.
Risk capacity
Full Access
Answer:
C
Explanation:
The most important factor for management to consider when deciding whether to invest in an IT initiative that exceeds management’s risk appetite is C. Risk tolerance1
According to the CRISC Review Manual, risk tolerance is the acceptable level of variation that management is willing to allow for any specific risk as the enterprise pursues its objectives. Risk tolerance reflects the degree of uncertainty that an organization is prepared to accept in relation to achieving its goals2
When an IT initiative exceeds management’s risk appetite, it means that the potential benefits of the initiative are outweighed by the potential negative consequences or losses that could result from the initiative. However, management may still decide to invest in the initiative if the level of uncertainty or variation is within the organization’s risk tolerance. For example, management may accept a higher level of risk for a strategic or innovative initiative that could provide a competitive advantage or a significant return on investment3
Question # 301
Which of the following is the MOST effective control to maintain the integrity of system configuration files?
A.
Recording changes to configuration files
B.
Implementing automated vulnerability scanning
C.
Restricting access to configuration documentation
D.
Monitoring against the configuration standard
Full Access
Answer:
D
Explanation:
According to the CRISC Review Manual, monitoring against the configuration standard is the most effective control to maintain the integrity of system configuration files, because it ensures that any unauthorized or unintended changes are detected and corrected. Monitoring against the configuration standard involves comparing the actual configuration of the system with the approved baseline and identifying any deviations or discrepancies. The other options are not the most effective controls, because they do not ensure the integrity of the system configuration files. Recording changes to configuration files is a good practice, but it does not prevent unauthorized or unintended changes from occurring. Implementing automated vulnerability scanning is a preventive control that helps to identify and remediate potential weaknesses in the system, but it does not verify the integrity of the configuration files. Restricting access to configuration documentation is a security measure that limits the exposure of sensitive information, but it does not prevent unauthorized or unintended changes to the configuration files. References = CRISC Review Manual, 7th Edition, Chapter 4, Section 4.2.3, page 184.
Question # 302
An IT department has organized training sessions to improve user awareness of organizational information security policies. Which of the following is the BEST key performance indicator (KPI) to reflect effectiveness of the training?
A.
Number of training sessions completed
B.
Percentage of staff members who complete the training with a passing score
C.
Percentage of attendees versus total staff
D.
Percentage of staff members who attend the training with positive feedback
Full Access
Answer:
B
Explanation:
A key performance indicator (KPI) is a metric that reflects how well an organization is achieving its goals and objectives. A KPI should be specific, measurable, achievable, relevant, and time-bound. For an IT department that has organized training sessions to improve user awareness of organizational information security policies, the best KPI to reflect the effectiveness of the training is the percentage of staff members who complete the training with a passing score. This KPI measures the level of knowledge and understanding of the security policies among the staff members, as well as the quality and impact of the training sessions. It also indicates whether the training sessions have met the predefined criteria and standards for success. A high percentage of staff members who complete the training with a passing score implies that the training sessions have been effective in improving user awareness of organizational information security policies. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2, p. 117-118
Question # 303
Which of the following is the MOST important requirement when implementing a data loss prevention (DLP) system?
A.
Identifying users who have access
B.
Selecting an encryption solution
C.
Defining the data retention period
D.
Determining the value of data
Full Access
Answer:
D
Explanation:
Determining the value of data is essential when implementing a DLP system. Understanding data value helps prioritize protection efforts, allocate resources effectively, and ensure that critical information assets are adequately safeguarded against loss or unauthorized access.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 2: IT Risk Assessment, Section: Data Classification and Protection., , , , , , , , , ]
Question # 304
Which stakeholder is MOST important to include when defining a risk profile during me selection process for a new third party application?
A.
The third-party risk manager
B.
The application vendor
C.
The business process owner
D.
The information security manager
Full Access
Answer:
C
Explanation:
A risk profile is a summary of the nature and level of risk that an organization faces. It includes information such as the sources, causes, and consequences of the risks, their likelihood and impact, their interrelationships and dependencies, and their alignment with the risk appetite and tolerance. A risk profile is influenced by various factors, such as the organization’s objectives, strategies, activities, processes, resources, capabilities, culture, etc. When defining a risk profile during the selection process for a new third party application, the stakeholder that is most important to include is the business process owner, who is the person who has the authority and responsibility for the design, execution, and performance of a business process. The business process owner can provide valuable input and insight into the requirements, expectations, and dependencies of the business process that will use the new third party application, and the potential risks and opportunities that may arise from the selection of the application. The business process owner can also help to prioritize and address the risks, and ensure that the risk profile is aligned with the business objectives and strategies. References = 5
Question # 305
An organization has initiated a project to launch an IT-based service to customers and take advantage of being the first to market. Which of the following should be of GREATEST concern to senior management?
A.
More time has been allotted for testing.
B.
The project is likely to deliver the product late.
C.
A new project manager is handling the project.
D.
The cost of the project will exceed the allotted budget.
Full Access
Answer:
B
Explanation:
Being the first to market is a competitive advantage that can help an organization gain market share, customer loyalty, and brand recognition. However, this advantage can be lost if the projectis delayed and the competitors catch up or surpass the organization. Therefore, the project delivery time is of greatest concern to senior management, as it directly affects the strategic objective of the project. The other options are less critical, as they can be managed or mitigated by the project team. More time for testing can improve the quality and reliability of the product, a new project manager can bring fresh ideas and perspectives, and the cost overrun can be justified by the expected benefits and revenues of the product. References = Project Initiation: The First Step to Project Management [2023] • Asana, 12 Steps to Initiate and Plan a Successful Project
Question # 306
Who is BEST suited to provide objective input when updating residual risk to reflect the results of control effectiveness?
A.
Control owner
B.
Risk owner
C.
Internal auditor
D.
Compliance manager
Full Access
Answer:
C
Explanation:
The internal auditor is the best suited to provide objective input when updating residual risk to reflect the results of control effectiveness. The internal auditor is an independent and impartial function that evaluates the adequacy and effectiveness of the internal controls and reports on the findings and recommendations. The internal auditor can provide an unbiased and reliable assessment of the residual risk, which is the risk that remains after the controls are applied. The other options are not as objective as the internal auditor, as they may have vested interests orconflicts of interest in the control environment. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.4: IT Risk Response, page 87.
Question # 307
A process maturity model is MOST useful to the risk management process because it helps:
A.
determine the cost of control improvements
B.
determine the gap between actual and desired state.
C.
benchmark maturity against industry standards
D.
reduce audit and regulatory findings
Full Access
Answer:
B
Explanation:
The correct answer isBbecause aprocess maturity modelis primarily used to determine thegap between the actual state and the desired stateof the risk management process. This is its main value in CRISC: it helps the organization understand current capability, compare it with target capability, and identify where improvement is needed.
The other options are less accurate:
A. determine the cost of control improvementsmay be done separately through cost-benefit analysis, but it is not the main purpose of a maturity model.
C. benchmark maturity against industry standardscan be a secondary use, but the primary value is internal gap identification.
D. reduce audit and regulatory findingsmay occur as an indirect benefit, but it is not the principal purpose.
Exact Extracts supporting the answer:
“Improving an enterprise’s risk management process is most effectively achieved through the use of a maturity model.â€
“The most insightful tool for understanding an enterprise’s risk management capabilities is a capability maturity model review.â€
“A capability maturity model assists risk practitioners in measuring the existing level of development of risk management processes against the desired state.â€
“The PRIMARY benefit of using a maturity model to assess the enterprise’s data management process is that it helps identify gaps.â€
“Measuring the gap between actual and desired states is the primary use of capability models in assessing risk management processes.â€
These extracts directly support that the most useful purpose of a process maturity model is to identify the gap between current and target maturity.
===========
Question # 308
Which of the following is a risk practitioner ' s MOST important course of action after learning that an organization ' s industry peers have experienced an increase in ransomware attacks?
A.
Recommend additional preventive controls to reduce residual risk.
B.
Document this scenario as a risk event for further risk analysis.
C.
Propose risk acceptance until the organization is directly affected.
D.
Raise a security incident to proactively prevent similar attacks.
Full Access
Answer:
A
Question # 309
Which of the following practices would be MOST effective in protecting personality identifiable information (Ptl) from unauthorized access m a cloud environment?
A.
Apply data classification policy
B.
Utilize encryption with logical access controls
C.
Require logical separation of company data
D.
Obtain the right to audit
Full Access
Answer:
B
Explanation:
The most effective practice in protecting personally identifiable information (PII) from unauthorized access in a cloud environment is to utilize encryption with logical access controls. Encryption is a technique that transforms the data into an unreadable or unintelligible form, making it inaccessible or unusable by unauthorized parties. Logical access controls are the mechanisms or rules that regulate who can access, view, modify, or delete the data, based on their identity, role, or privilege. By utilizing encryption with logical access controls, the PII can be protected from unauthorized access, disclosure, or theft, both in transit and at rest, in a cloud environment. The other options are not as effective as utilizing encryption with logical access controls, as they are related to the classification, separation, or audit of the data, not the protection or security of the data. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Question # 310
A vendor’s planned maintenance schedule will cause a critical application to temporarily lose failover capabilities. Of the following, who should approve this proposed schedule?
A.
Business application owner
B.
Business continuity manager
C.
Chief risk officer (CRO)
D.
IT infrastructure manager
Full Access
Answer:
A
Explanation:
The business application owner is accountable for business impact and must approve any change that affects application availability. ISACA’s CRISC emphasis on ownership roles indicates business owners should approve changes with risk implications.
Question # 311
Which of the following statements in an organization ' s current risk profile report is cause for further action by senior management?
A.
Key performance indicator (KPI) trend data is incomplete.
B.
New key risk indicators (KRIs) have been established.
C.
Key performance indicators (KPIs) are outside of targets.
D.
Key risk indicators (KRIs) are lagging.
Full Access
Answer:
C
Explanation:
A risk profile report is a document that summarizes the current status and trends of the risks that an organization faces, as well as the actions taken or planned to manage them1. A risk profile report is a useful tool for senior management to monitor and oversee the organization’s risk management performance and to make informed decisions and adjustments as needed2. One of the key components ofa risk profile report is the key performance indicators (KPIs), which are metrics used to measure andevaluate the achievement of the organization’s objectives and strategies3. KPIs are aligned with the organization’s risk appetite and tolerance, and they have specific targets or benchmarks that indicate the desired level of performance4. Therefore, if the KPIs are outside of targets, it means that the organization is not meeting its objectives and strategies, and that there may be gaps or issues in the risk management process or the risk response actions. This is a cause for further action by senior management, as they need to investigate the root causes of the deviation, assess the impact and implications of the underperformance, and take corrective or preventive measures to improve the situation and bringthe KPIs back to the targets. Incomplete KPI trend data, new KRIs, and lagging KRIs are not the most critical statements in a risk profile report that require further action by senior management, as they do not directly indicate a failure or a problem in the risk management performance or the achievement of the objectives and strategies. Incomplete KPI trend data means that there is missing or insufficient information on the historical or projected changes in the KPIs over time. This may affect the accuracy and reliability of the risk profile report, but it does not necessarily mean that the KPIs are outside of targets or that the objectives and strategies are not met. Senior management may need to request or obtain the complete KPI trend data, but this is not as urgent or important as addressing the KPIs that are outside of targets. New KRIs means that there are additional or revised metrics used to measure and monitor the level of risk associated with a particular process, activity, or system within the organization. This may reflect the changes or updates in the risk environment, the risk appetite and tolerance, or the risk assessment methodology. However, new KRIs do not directly indicate a failure or a problem inthe risk management performance or the achievement of the objectives and strategies. Senior management may need to review and approve the new KRIs, but this is not as urgent or important as addressing the KPIs that are outside of targets. Lagging KRIs means that there are metrics that measure and monitor the level of risk after a risk event has occurred or a risk response has been implemented. This may provide useful feedback and lessons learned for the risk management process, but it does not directly indicate a failure or a problem in the risk management performance or the achievement of the objectives and strategies. Senior management may need to analyze and evaluate the lagging KRIs, but this is not as urgent or important as addressing the KPIs that are outside of targets. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.3: Risk Reporting, pp. 201-205.
Question # 312
An IT department has provided a shared drive for personnel to store information to which all employees have access. Which of the following parties is accountable for the risk of potential loss of confidential information?
A.
Risk manager
B.
Data owner
C.
End user
D.
IT department
Full Access
Answer:
B
Explanation:
The data owner is the person who has the authority and responsibility to classify, label, and protect the information assets of the organization. The data owner is accountable for the risk ofpotential loss of confidential information, as they are the ones who determine the level of protection and access required for the data. The risk manager is responsible for identifying, assessing, and mitigating the risks that may affect the organization, but they are not accountable for the data itself. The end user is the person who uses the information assets for their operational tasks, but they are not accountable for the data protection or classification. The IT department is responsible for providing the technical support and infrastructure for the information assets, but they are not accountable for the data ownership or risk management. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: Data Classification, p. 69-70.
Question # 313
A business unit is unable to fully implement the security policy on a critical business application. Which type of process should be in place to BEST manage the related risk?
A.
Change management
B.
Exception management
C.
Configuration management
D.
Incident management
Full Access
Answer:
B
Explanation:
The correct answer isBbecause when a business unit cannot fully implement a required security policy, the best way to manage the related risk is through anexception managementprocess. This allows the deviation to be formally reviewed, justified, approved by the appropriate authority, documented, and monitored with awareness of the resulting residual risk.
The other options are less appropriate:
A. Change managementcontrols how changes are introduced, but it does not formally manage policy deviations.
C. Configuration managementhelps maintain technical baselines, but it does not address acceptance of noncompliance with policy.
D. Incident managementis used after an event occurs, not for governing approved deviations from policy.
Exact Extracts supporting the answer:
“In the absence of a formal policy on personal devices in the workplace the risk practitioner should recommend implementing an exception process based on appropriate approvals.â€
“The primary reason for initiating a policy-exception process is the risk being justified by the benefit.â€
“When an enterprise wants to quickly implement a technical solution that deviates from the company’s policies the risk practitioner should recommend a risk assessment and subsequent implementation only if residual risk is accepted.â€
“The BEST way to ensure appropriate mitigation occurs on identified information systems vulnerabilities is by assigning action plans with deadlines to responsible personnel.â€
These extracts directly support that a formalexception managementprocess is the best mechanism for managing risk when policy cannot be fully implemented.
===========
Question # 314
Which of the following BEST mitigates ethical risk?
A.
Ethics committees
B.
Contingency scenarios
C.
Awareness of consequences for violations
D.
Routine changes in senior management
Full Access
Answer:
A
Explanation:
Ethics committees are typically responsible for developing, implementing, and overseeing an organization’s ethical guidelines and policies. They play a crucial role in mitigating ethical risk by ensuring that the organization’s operations align with its ethical standards123.
References
1What Is Ethically Informed Risk Management? - Journal of Ethics
2Five Ways to Reduce Ethics and Compliance Risk - Free Ethics Toolkit
35 Ways to Manage Ethical Risks - ClearRisk
Question # 315
Which of the following, who should be PRIMARILY responsible for performing user entitlement reviews?
A.
IT security manager
B.
IT personnel
C.
Data custodian
D.
Data owner
Full Access
Answer:
D
Explanation:
The person or entity who should be primarily responsible for performing user entitlement reviews is the data owner. A user entitlement review is a process that verifies and validates the access rights and privileges of the users to the data and resources in the IT environment. A user entitlement review helps to ensure that the users have the appropriate and necessary access to perform their roles and functions, and to prevent or detect any unauthorized or inappropriate access. A data owner is the person or entity that has the authority and responsibility to define, classify, and protect the data and resources in the IT environment. A data owner helps to perform user entitlement reviews, because they help to establish and enforce the access policies and standards for the data and resources, and to approve or revoke the access requests and changes for the users. A data owner also helps to monitor and report on the access performance and compliance for the data and resources, and to identify and address any issues or gaps in the access management activities. The other options are not the primary responsible party for performing user entitlement reviews, although they may be involved in the process. IT security manager, IT personnel, and data custodian are all examples of roles or functions that can help tosupport or implement the user entitlement reviews, but they do not necessarily have the authority or responsibility to define, classify, or protect the data and resources. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.2.1, page 5-14.
Question # 316
An IT operations team implements disaster recovery controls based on decisions from application owners regarding the level of resiliency needed. Who is the risk owner in this scenario?
A.
Business resilience manager
B.
Disaster recovery team lead
C.
Application owner
D.
IT operations manager
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual1, the application owner is the person who has the authority and accountability for the achievement of the application objectives and the management of the associated risks. The application owner is responsible for defining the level of resiliency needed for the application, which is the ability of the application to recover from disruptions and continue to operate. The application owner is also responsible for accepting or rejecting the residual risks after the implementation of the disaster recovery controls, which are the measures to restore the application functionality and data in the event of a disaster. Therefore, the risk owner in this scenario is the application owner, as they are the ones who will be affected by the potential impact of the disaster on the application and its objectives. References = CRISC Review Manual1, page 194.
Question # 317
The BEST metric to demonstrate that servers are configured securely is the total number of servers:
A.
exceeding availability thresholds
B.
experiencing hardware failures
C.
exceeding current patching standards.
D.
meeting the baseline for hardening.
Full Access
Answer:
D
Explanation:
The best metric to demonstrate that servers are configured securely is the total number of servers meeting the baseline for hardening. Hardening is the process of applying security configurations and settings to servers to reduce their attack surface and vulnerability. A baseline is a standard or benchmark that defines the minimum level of security required for servers. By measuring the number of servers that meet the baseline, the organization can assess the effectiveness of its hardening efforts and identify any gaps or deviations. The other metrics, such as exceeding availability thresholds, experiencing hardware failures, or exceeding current patching standards, are not directly related to the security configuration of servers, but rather to their performance, reliability, or maintenance. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.3.2, page 2-25.
Question # 318
An organization has outsourced its IT security operations to a third party. Who is ULTIMATELY accountable for the risk associated with the outsourced operations?
A.
The third party s management
B.
The organization ' s management
C.
The control operators at the third party
D.
The organization ' s vendor management office
Full Access
Answer:
B
Explanation:
Outsourcing IT security operations is a common practice that can provide benefits such as cost savings, access to specialized skills, and improved service quality12. However, outsourcing also introduces risks such as loss of control, dependency, contractual issues, and service failures12.
When an organization outsources its IT security operations to a third party, it does not transfer the accountability for the risk associated with the outsourced operations. Accountability is the obligation to answer for the execution of one’s assigned responsibilities34.
The organization’s management is ultimately accountable for the risk associated with the outsourced operations, as they are responsible for defining the organization’s risk appetite, strategy, and objectives, and for ensuring that the organization’s IT security operations are aligned with them34.
The organization’s management is also accountable for selecting, contracting, and overseeing the third party, and for ensuring that the third party meets the agreed service levels, standards, and compliance requirements34.
The organization’s management is also accountable for monitoring and reporting the risk associated with the outsourced operations, and for taking corrective actions when necessary34.
The other options are not ultimately accountable, but rather have different roles and responsibilities in relation to the outsourced operations. For example:
The third party’s management is responsible for delivering the IT security services according to the contract, and for managing the risk within their own organization34. They are accountable to the organization’s management, but not to the organization’s stakeholders.
The control operators at the third party are responsible for implementing and operating the IT security controls according to the service specifications, and for reporting any issues orincidents to the organization’s management34. They are accountable to the third party’s management, but not to the organization’s management or stakeholders.
The organization’s vendor management office is responsible for facilitating the relationship between the organization and the third party, and for supporting the organization’s management in the outsourcing process34. They are accountable to the organization’s management, but not for the risk associated with the outsourced operations. References =
1: Outsourcing IT Security: A Risk Management Perspective, ISACA Journal, Volume 2, 2019
2: The Cyber Security Risks Of Outsourcing, Cybersecurity Intelligence, January 4, 2022
3: Accountability for Information Security Roles and Responsibilities, Part 1, ISACA Journal, Volume 5, 2019
4: Risk IT Framework, ISACA, 2009
Question # 319
Who is the BEST person to the employee personal data?
A.
Human resources (HR) manager
B.
System administrator
C.
Data privacy manager
D.
Compliance manager
Full Access
Answer:
A
Explanation:
The HR manager is the person or entity that has the authority and responsibility to collect, process, and protect the personal data of the employees in the organization. The HR managerhelps to manage the employee personal data, because they help to establish and enforce the data policies and standards for the employees, and to comply with the legal and regulatory requirements, such as the GDPR. The HR manager also helps to monitor and report on the data performance and compliance for the employees, and to identify and address any issues or gaps in the data management activities. The other options are not the best person to manage the employee personal data, although they may be involved in the process. System administrator, data privacy manager, and compliance manager are all examples of roles or functions that can help to support or implement the data management activities, but they do not necessarily have the authority or responsibility to collect, process, or protect the employee personal data
Question # 320
An organization recently implemented new technologies that enable the use of robotic process automation. Which of the following is MOST important to reassess?
A.
Risk profile
B.
Risk tolerance
C.
Risk capacity
D.
Risk appetite
Full Access
Answer:
A
Explanation:
The risk profile is the most important thing to reassess when an organization implements new technologies that enable the use of robotic process automation (RPA). The risk profile is a comprehensive and dynamic view of the organization’s risks, their ratings, responses, and status. RPA can introduce new risks or change the existing risks related to the organization’s objectives, operations, and performance. For example, RPA can create risks such as system failures, databreaches, compliance violations, human errors, or ethical dilemmas. Therefore, the organization should reassess its risk profile to identify, assess, treat, monitor, and review the risks associated with RPA, and to ensure that the risk management strategy is aligned with the business needs and expectations.
[References:, •ISACA, Robotic Process Automation for Internal Audit1, •ISACA, Key Considerations for Robotic Process Automation2, , , , , , , , , , ]
Question # 321
During which phase of the system development life cycle (SDLC) should information security requirements for the implementation of a new IT system be defined?
A.
Monitoring
B.
Development
C.
Implementation
D.
Initiation
Full Access
Answer:
D
Explanation:
Information security requirements should be defined during theInitiationphase of the SDLC. This ensures that security is integrated into the design from the beginning, minimizing vulnerabilities and aligning security measures with business requirements. Early identification of security needs reduces rework and costs associated with later stages.
Question # 322
A department allows multiple users to perform maintenance on a system using a single set of credentials. A risk practitioner determined this practice to be high-risk. Which of the following is the MOST effective way to mitigate this risk?
A.
Single sign-on
B.
Audit trail review
C.
Multi-factor authentication
D.
Data encryption at rest
Full Access
Answer:
C
Explanation:
Multi-factor authentication is the most effective way to mitigate the risk of unauthorized access to the system, as it requires the users to provide more than one piece of evidence to prove their identity, such as a password, a token, a biometric feature, etc. This reduces the likelihood of compromising the credentials and ensures that only authorized users can perform maintenance on the system.
Single sign-on is a convenience feature that allows users to access multiple systems with one set of credentials, but it does not address the risk of sharing credentials among multiple users.
Audit trail review is a detective control that can help identify and investigate unauthorized access to the system, but it does not prevent or mitigate the risk of credential compromise.
Data encryption at rest is a security measure that protects the data stored on the system from unauthorized access, but it does not prevent or mitigate the risk of credential compromise. References = CRISC Review Manual, 7th Edition, ISACA, 2020, page 107-108.
Question # 323
An organization has four different projects competing for funding to reduce overall IT risk. Which project should management defer?
A.
Project Charlie
B.
Project Bravo
C.
Project Alpha
D.
Project Delta
Full Access
Answer:
D
Explanation:
Project Delta should be deferred by management, as it has the lowest return on investment (ROI) among the four competing projects. ROI is a measure of the profitability or efficiency of a project, calculated by dividing the net benefits by the total costs. Project Delta has a net benefit of $100,000 and a total cost of $200,000, resulting in an ROI of 0.5. The other projects have higher ROIs: Project Alpha has an ROI of 1.0, Project Bravo has an ROI of 0.8, and Project Charlie has an ROI of 0.6. Therefore, Project Delta is the least attractive option for reducingoverall IT risk, and management should prioritize the other projects instead. References = How to Manage Project Risk: A 5-Step Guide; Matching the right projects with the right resources; Risk Types in Project Management
Question # 324
Which of the following is the GREATEST benefit of using IT risk scenarios?
A.
They support compliance with regulations.
B.
They provide evidence of risk assessment.
C.
They facilitate communication of risk.
D.
They enable the use of key risk indicators (KRls)
Full Access
Answer:
C
Explanation:
The greatest benefit of using IT risk scenarios is that they facilitate communication of risk, as they provide a clear and realistic description of the risk sources, events, impacts, and responses, and enable the stakeholders to understand and appreciate the risk exposure and appetite of the organization. Supporting compliance with regulations, providing evidence of risk assessment, and enabling the use of key risk indicators (KRIs) are also benefits of using IT risk scenarios, but they are not the greatest benefit, as they are more related to the outcomes or consequences of risk communication, rather than the process or value of risk communication. References = CRISC Review Manual, 7th Edition, page 100.
Question # 325
Which of the following would be MOST helpful to an information security management team when allocating resources to mitigate exposures?
A.
Relevant risk case studies
B.
Internal audit findings
C.
Risk assessment results
D.
Penetration testing results
Full Access
Answer:
C
Explanation:
The most helpful factor for an information security management team when allocating resources to mitigate exposures is the risk assessment results. The risk assessment results provide a comprehensive and objective analysis of the risks facing the enterprise, including their likelihood, impact, and root causes. The risk assessment results also help to identify the gaps and weaknesses in the existing controls, and to prioritize the risks based on their severity and urgency. The risk assessment results enable the information security management team toallocate the resources in a cost-effective and risk-based manner, and to implement the most appropriate risk responses to reduce the exposures to an acceptable level. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.1.1, page 1751
Question # 326
Technical controls affecting access permissions for systems should be implemented according to:
A.
Integration testing requirements.
B.
Separation of duties.
C.
Configuration baselines.
D.
Contingency scenarios.
Full Access
Answer:
B
Explanation:
The correct answer isBbecause technical controls affecting access permissions should be implemented according toseparation of duties. Access permissions must be structured so that no single individual has incompatible responsibilities that could enable unauthorized activity, fraud, or unapproved changes. This is a core principle of access control governance and control design.
The other options are less appropriate:
A. Integration testing requirementsrelate to testing system interactions, not the primary basis for assigning access permissions.
C. Configuration baselinesare important for standard settings, but access authorization must first align with role separation and accountability.
D. Contingency scenariosare related to continuity and recovery, not normal access permission design.
Exact Extracts supporting the answer:
“The PRIMARY reason that an enterprise would establish segregation of duties controls is to prevent errors or fraudulent activity on high-risk transactions.â€
“The MOST effective control to prevent segregation of duties violations is implementing role-based access.â€
“To ensure that developers do not have access to implement changes to production applications an enterprise must have segregation of duties between application development and operations.â€
“The control a risk practitioner would recommend is segregation of duties†when personnel can both change system configuration settings and modify logs.
These extracts show that access permissions and technical access controls should be aligned withseparation of dutiesto prevent misuse and reduce risk.
===========
Question # 327
Which of the following is the BEST way to identify changes to the risk landscape?
A.
Internal audit reports
B.
Access reviews
C.
Threat modeling
D.
Root cause analysis
Full Access
Answer:
C
Explanation:
The risk landscape is the set of internal and external factors and conditions that may affect the organization’s objectives and operations, and create or influence the risks that the organization faces. The risk landscape is dynamic and complex, and it may change over time due to various drivers or events, such as technological innovations, market trends, regulatory changes, customer preferences, competitor actions, environmental issues, etc.
The best way to identify changes to the risk landscape is threat modeling, which is the process of identifying, analyzing, and prioritizing the potential threats or sources of harm that may exploit the vulnerabilities or weaknesses in the organization’s assets, processes, or systems, and cause adverse impacts or consequences for the organization. Threat modeling can help the organization to anticipate and prepare for the changes in the risk landscape, and to design and implement appropriate controls or countermeasures to mitigate or prevent the threats.
Threat modeling can be performed using various techniques, such as brainstorming, scenario analysis, attack trees, STRIDE, DREAD, etc. Threat modeling can also be integrated with the risk management process, and aligned with the organization’s objectives and risk appetite.
The other options are not the best ways to identify changes to the risk landscape, because they do not provide the same level of proactivity, comprehensiveness, and effectiveness of identifying and addressing the potential threats or sources of harm that may affect the organization.
Internal audit reports are the documents that provide the results and findings of the internal audits that are performed to assess and evaluate the adequacy and effectiveness of the organization’s governance, risk management, and control functions. Internal audit reports can provide useful information and recommendations on the current state and performance of the organization, and identify the issues or gaps that need to be addressed or improved, but they are not the best way to identify changes to the risk landscape, because they areusually retrospective and reactive, and they may not cover all the relevant or emerging threats or sources of harm that may affect the organization.
Access reviews are the processes of verifying and validating the access rights and privileges that are granted to the users or entities that interact with the organization’s assets, processes, orsystems, and ensuring that they are appropriate and authorized. Access reviews can provide useful information and feedback on the security and compliance of the organization’s access management, and identify and revoke any unauthorized or unnecessary access rights or privileges, but they are not the best way to identify changes to the risk landscape, because they are usually periodic and specific, and they may not cover all the relevant or emerging threats or sources of harm that may affect the organization.
Root cause analysis is the process of identifying and understanding the underlying or fundamental causes or factors that contribute to or result in a problem or incident that has occurred or may occur in the organization. Root cause analysis can provide useful insights and solutions on the origin and nature of the problem or incident, and prevent or reduce its recurrence or impact, but it is not the best way to identify changes to the risk landscape, because it is usually retrospective and reactive, and it may not cover all the relevant or emerging threats or sources of harm that may affect the organization. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 167
CRISC Practice Quiz and Exam Prep
Question # 328
Concerned about system load capabilities during the month-end close process, management requires monitoring of the average time to complete tasks and monthly reporting of the findings. What type of measure has been established?
A.
Service level agreement (SLA)
B.
Critical success factor (CSF)
C.
Key risk indicator (KRI)
D.
Key performance indicator (KPI)
Full Access
Answer:
D
Explanation:
Monitoring the average time to complete tasks and monthly reporting of the findings during the month-end close process aligns with the definition of a Key Performance Indicator (KPI).
Understanding KPIs:
Performance Measurement:KPIs are used to measure how effectively a company is achieving its key business objectives. Monitoring the average time to complete tasks during the month-end close process provides a performance metric.
Tracking Efficiency:By reporting these findings monthly, management can track the efficiency and performance of the system load capabilities.
Specific Measure:
Task Completion Time:The average time to complete tasks is a specific, measurable indicator of performance. It helps in understanding how well the system handles load and identifies areas for improvement.
Continuous Improvement:Regular monitoring and reporting encourage continuous improvement, which is a core aspect of using KPIs.
[References:, According to ISACA's guidelines on performance measurement, KPIs are critical for tracking the efficiency and effectiveness of processes and systems. They provide tangible metrics that help in decision-making and performance improvement., , , , , , , , , , , ]
Question # 329
The PRIMARY goal of conducting a business impact analysis (BIA) as part of an overall continuity planning process is to:
A.
obtain the support of executive management.
B.
map the business processes to supporting IT and other corporate resources.
C.
identify critical business processes and the degree of reliance on support services.
D.
document the disaster recovery process.
Full Access
Answer:
C
Explanation:
The primary goal of conducting a business impact analysis (BIA) as part of an overall continuity planning process is to identify critical business processes and the degree of reliance on support services. A BIA is a process of assessing the potential impact and consequences of a disruption or interruption of the business activities, operations, or functions. A continuity planning processis a process of developing, implementing, and maintaining a plan to ensure the continuity and recovery of the business activities, operations, or functions in the event of a disruption or interruption. The primary goal of conducting a BIA is to identify critical business processes and the degree of reliance on support services, which are the business processes that are essential for the survival and success of the business, and the support services that are required to enable or facilitate the critical business processes, such as IT systems, human resources, facilities, or suppliers. Identifying critical business processes and the degree of reliance on support services helps to determine the priorities and requirements for the continuity and recovery of the business activities, operations, or functions, and to select and implement the appropriate continuity andrecovery strategies and solutions. Obtaining the support of executive management, mapping the business processes to supporting IT and other corporate resources, and documenting the disaster recovery process are not the primary goals of conducting a BIA, as they are either the benefits or the outputs of the BIA process, and they do not address the primary need of assessing the impact and consequences of the business disruption or interruption. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 50.
Question # 330
From a data protection and regulatory compliance perspective, which of the following is the MOST important reason for a global organization to use immutable backups?
A.
Immutable backups can be used for data recovery testing.
B.
Data contains time stamps that indicate when it was backed up.
C.
Immutable backups enable effective disaster recovery response.
D.
Data cannot be tampered with through the use of encryption capabilities
Full Access
Answer:
D
Explanation:
The correct answer isDbecause the most important reason for usingimmutable backupsfrom a data protection and regulatory compliance perspective is that the datacannot be tampered with. The key compliance value of immutability is preserving integrity and protecting records from unauthorized alteration or deletion. This is especially important when proving that protected data and retained records remain trustworthy.
The other options are less important in this context:
A. Immutable backups can be used for data recovery testingis beneficial, but not the main regulatory reason.
B. Data contains time stamps that indicate when it was backed upis useful information, but not the core compliance value.
C. Immutable backups enable effective disaster recovery responseis important operationally, but the question emphasizes data protection and regulatory compliance.
Exact Extracts supporting the answer:
“The BEST method that provides message integrity authentication of the sender ' s identity and nonrepudiation is digital signatures.â€
“The MOST important consideration when transmitting personal information across networks is ensuring the privacy of the personal information.â€
“The purpose of system certification is to demonstrate that security controls and processes are assessed for effectiveness.â€
“The MOST important principle of data protection that a risk practitioner should advocate for is that data should be accurate.â€
These extracts support that from a compliance and data protection perspective, preserving integrity and preventing tampering is the highest concern. Therefore,Dis the best answer.
===========
Question # 331
A management team is on an aggressive mission to launch a new product to penetrate new markets and overlooks IT risk factors, threats, and vulnerabilities. This scenario BEST demonstrates an organization ' s risk:
A.
management.
B.
tolerance.
C.
culture.
D.
analysis.
Full Access
Answer:
C
Explanation:
 Risk culture is the system of values and behaviors present in an organization that shapes risk decisions of management and employees1. Risk culture influences how the organization perceives, responds to, and manages the risks that may affect its objectives, operations, or assets2.
The scenario described in the question best demonstrates an organization’s risk culture, because it shows how the management team’s attitude and actions towards risk are driven by the organization’s values and goals. In this case, the organization’s risk culture is characterized by:
A high risk appetite and tolerance, which means that the organization is willing to take and accept significant risks in order to achieve its strategic objectives of launching a new product and penetrating new markets
A low risk awareness and sensitivity, which means that the organization does not pay enough attention or consideration to the potential IT risk factors, threats, and vulnerabilities that may affect its product development and market entry
A weak risk governance and control, which means that the organization does not have adequate or effective policies, procedures, or mechanisms to identify, assess, respond, or monitor the IT risks and their impacts
References = Risk Culture of Companies | ERM - Enterprise Risk Management Initiative …, Taking control of organizational risk culture | McKinsey
Question # 332
Which of the following is the BEST method for identifying vulnerabilities?
A.
Batch job failure monitoring
B.
Periodic network scanning
C.
Annual penetration testing
D.
Risk assessments
Full Access
Answer:
B
Explanation:
The best method for identifying vulnerabilities is periodic network scanning. Network scanning is a process of scanning and probing the network devices, systems, and applications to discover and analyze their security weaknesses, such as configuration errors, outdated software, or open ports. Network scanning can help to identify the vulnerabilities that could be exploited by attackers to gain unauthorized access, compromise data, or disrupt services. Periodic network scanning is the best method, because it can provide a regular and comprehensive view of the network security posture, and it can detect and address the new or emerging vulnerabilities in a timely manner. Periodic network scanning can also help to comply with the legal and regulatory requirements and standards for network security, such as the ISO/IEC 27001, the NIST SP 800-53, or the PCI DSS123. The other options are not the best method, although they may be useful or complementary to periodic network scanning. Batch job failure monitoring is a process of monitoring and reporting the failures or errors that occur during the execution of batch jobs, such as data processing, backup, or synchronization. Batch job failure monitoring can help to identify the operational or technical issues that affect the performance or availability of the network services, but it does not directly identify the security vulnerabilities or the potential threats. Annual penetration testing is a process of simulating a real-world attack on the network devices, systems, and applications to evaluate their security defenses and resilience. Penetration testing can help to identify and exploit the vulnerabilities that could be used by attackers to compromise the network security, and to provide recommendations for improvement. However, annual penetration testing is not the best method, because it is not frequent or consistent enough to keep up with the changing and evolving network security landscape, and it may not cover all thenetwork components or scenarios. Risk assessments are a process of identifying, analyzing, and evaluating the risks associated with the network devices, systems, and applications. Risk assessments can help to estimate the probability and impact of the vulnerabilities and the threats, and to prioritize and respond to the risks accordingly. However, risk assessments are not the same as or a substitute for vulnerability identification, as they rely on the vulnerability information as an input, rather than an output. References = Vulnerability Testing: Methods, Tools, and 10 Best Practices, ISO/IEC 27001 Information Security Management, NIST SP 800-53 Rev. 5
Question # 333
Which of the following risk impacts should be the PRIMARY consideration for determining recovery priorities in a disaster recovery situation?
A.
Data security
B.
Recovery costs
C.
Business disruption
D.
Recovery resource availability
Full Access
Answer:
C
Explanation:
The primary consideration for determining recovery priorities in a disaster recovery situation is the impact of business disruption on the organization’s mission, objectives, and stakeholders. Business disruption can result in loss of revenue, reputation, customer satisfaction, market share, and competitive advantage. Therefore, the recovery priorities should be based on the criticality of the business processes and functions that support the organization’s value proposition and strategic goals. Data security (A), recovery costs (B), and recovery resource availability (D) are important factors, but they are secondary to the impact of business disruption. Data security should be ensured throughout the recovery process, but it does not determine the recovery order. Recovery costs should be balanced with the benefits of restoring the business operations, but they do not reflect the urgency of the recovery. Recovery resource availability should be assessed and allocated according to the recovery priorities, but it does not define the recovery sequence. (Risk and Information Systems Control Review Questions, Answers & Explanations Manual, 5th Edition, page 982)
Question # 334
Which of the following BEST indicates that an organization has implemented IT performance requirements?
A.
Service level agreements(SLA)
B.
Vendor references
C.
Benchmarking data
D.
Accountability matrix
Full Access
Answer:
A
Explanation:
Service level agreements (SLA) are contracts that define the expected level of performance and quality of service that an IT service provider will deliver to its customers. SLA are the best indicators that an organization has implemented IT performance requirements, as they specifythe measurable and verifiable criteria that the IT service provider must meet or exceed, such as availability, reliability, security, and responsiveness. SLA also establish the roles and responsibilities of the parties involved, the methods of monitoring and reporting the service performance, and the consequences of non-compliance or breach of the agreement. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 232. CRISC by Isaca Actual Free Exam Q & As, Question 9. CRISC Sample Questions 2024, Question 232. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 232.
Question # 335
Which of the following is MOST helpful to understand the consequences of an IT risk event?
A.
Fault tree analysis
B.
Historical trend analysis
C.
Root cause analysis
D.
Business impact analysis (BIA)
Full Access
Answer:
D
Explanation:
Business impact analysis (BIA) is a process that involves analyzing the potential consequences of an IT risk event on the organization’s critical business functions and processes. BIA can help to understand the severity and duration of the disruption, the financial and operational losses, the recovery time objectives, and the recovery point objectives. BIA can also help to prioritize the recovery activities and resources, as well as to determine the acceptable level of risk and the risk mitigation strategies. BIA is the most helpful tool to understand the consequences of an IT risk event, as it provides a comprehensive and quantitative assessment of the impact and the recovery requirements. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.2, p. 206-207
Question # 336
An organization ' s senior management is considering whether to acquire cyber insurance. Which of the following is the BEST way for the risk practitioner to enable management’s decision?
A.
Perform a cost-benefit analysis.
B.
Conduct a SWOT analysis.
C.
Provide data on the number of risk events from the last year.
D.
Report on recent losses experienced by industry peers.
Full Access
Answer:
A
Explanation:
Acost-benefit analysisevaluates the financial implications of acquiring cyber insurance versus the potential loss exposure. This approach enables informed decision-making by comparing the insurance cost with the potential savings from covered risks.
Question # 337
The risk associated with inadvertent disclosure of database records from a public cloud service provider (CSP) would MOST effectively be reduced by:
A.
encrypting the data
B.
including a nondisclosure clause in the CSP contract
C.
assessing the data classification scheme
D.
reviewing CSP access privileges
Full Access
Answer:
A
Explanation:
Encrypting the data would MOST effectively reduce the risk associated with inadvertent disclosure of database records from a public cloud service provider (CSP), because it is a control that protects the confidentiality and integrity of the data by transforming it into an unreadable and unmodifiable form, using a secret key or algorithm. Encrypting the data can prevent or minimize the unauthorized or accidental access, modification, or leakage of the data, especially when the data is stored, transmitted, or processed in a public cloud environment, which may have less security and control than a private or on-premise environment. The other options are not as effective as encrypting the data, because:
Option B: Including a nondisclosure clause in the CSP contract is a legal measure that can deter or penalize the CSP from disclosing the data to any third party, but it does not reduce the risk of inadvertent disclosure of the data, which may occur due to human error, system failure, or malicious attack, and it does not protect the data from unauthorized or accidental access, modification, or leakage.
Option C: Assessing the data classification scheme is a process that can help to identify and categorize the data according to its sensitivity, value, and criticality, and to determine the appropriate level of protection and handling for the data, but it does not reduce the risk of inadvertent disclosure of the data, which may affect any type or class of data, and it does not provide the specific or effective control to protect the data from unauthorized or accidental access, modification, or leakage.
Option D: Reviewing CSP access privileges is a procedure that can help to monitor and verify the access rights and permissions of the CSP to the data, and to ensure that they are aligned with the business needs and expectations, but it does not reduce the risk of inadvertent disclosure of the data, which may occur even with the legitimate or authorized access of the CSP, and it does not protect the data from unauthorized or accidental access, modification, or leakage by otherparties. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 211.
Question # 338
An IT manager insists on accepting an IT risk associated with a key business process due to the limited resources available to mitigate. Which of the following is the risk practitioner ' s MOST important action?
A.
Seek additional resources for risk mitigation.
B.
Document the business rationale for risk acceptance.
C.
Validate the decision with the process owner
D.
Conduct a follow-up business process analysis.
Full Access
Answer:
C
Explanation:
The correct answer isCbecause theprocess owneris the appropriate risk owner for a key business process, and therefore the most important action is tovalidate the decision with the process owner. An IT manager may provide operational input, but acceptance of business risk must be confirmed by the accountable business owner.
The other options are less important as the primary action:
A. Seek additional resources for risk mitigationmay be worthwhile, but first the acceptance decision must be validated by the actual risk owner.
B. Document the business rationale for risk acceptanceis necessary, but only after the correct owner has validated the decision.
D. Conduct a follow-up business process analysismay support the discussion, but the main issue is proper authority for accepting the risk.
Exact Extracts supporting the answer:
“For an IT system supporting a critical business process senior managers should be accountable for the risk.â€
“For an organizational business unit the most accurate description of risk-related roles and responsibilities is that the management team owns the risk and is responsible for identifying assessing and mitigating risk and reporting to the appropriate support functions and the board of directors.â€
“Accountability for a risk treatment plan lies with the risk owner.â€
“The PRIMARY objective of risk reporting is to provide the risk owner with information to initiate risk response.â€
“The risk practitioner’s primary role is to consult and recommend risk responses.â€
These extracts show that the business or process owner is the accountable party for accepting risk associated with a key business process. Therefore, the risk practitioner should firstvalidate the decision with the process owner.
===========
Question # 339
Which of the following is the PRIMARY benefit of stakeholder involvement in risk scenario development?
A.
Ability to determine business impact
B.
Up-to-date knowledge on risk responses
C.
Decision-making authority for risk treatment
D.
Awareness of emerging business threats
Full Access
Answer:
D
Explanation:
Risk scenario development is a process that involves identifying and describing the potential risk events that can affect an organization’s objectives and operations. Risk scenario development requires the input and participation of various stakeholders, such as the management, the staff, the customers, the suppliers, the regulators, and the competitors. The primary benefit of stakeholder involvement in risk scenario development is that it increases the awareness of emerging business threats, meaning that it helps to identify and anticipate the new or changingsources and impacts of risk that may not be captured by theexisting risk assessment methods or tools. Stakeholder involvement can also help to improve the quality and completeness of the risk scenarios, as well as to enhance the communication and collaborationamong the stakeholders regarding the risk management process. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.1.1, p. 66-67
Question # 340
A.
Some risk remediation activities from the last assessment are still in progress.
B.
The risk scenarios have never been updated.
C.
The risk scenario development process was led by an external consultant.
D.
The number of risk scenarios is very high.
Full Access
Answer:
B
Explanation:
Risk scenarios must be regularly reviewed and updated to remain relevant, especially given changing threat landscapes and business processes. A set of scenarios developed five years ago without update is likely outdated and may fail to capture current risks effectively. Ongoing remediation and external involvement are not inherently concerns if properly managed. The number of scenarios depends on scope and is less critical than currency and relevanceã€5:7, 5:256, 5:168†CRISC_SentenceinNOTE30.pptx】.
Question # 341
Which of the following is PRIMARILY responsible for providing assurance to the board of directors and senior management during the evaluation of a risk management program implementation?
A.
Risk management
B.
Business units
C.
External audit
D.
Internal audit
Full Access
Answer:
D
Explanation:
Internal audit provides independent assurance to the board and senior management regarding the effectiveness of risk management program implementation, consistent withGovernance and Assurance Principles.
Question # 342
Which of the following is the BEST way for a risk practitioner to help management prioritize risk response?
A.
Align business objectives to the risk profile.
B.
Assess risk against business objectives
C.
Implement an organization-specific risk taxonomy.
D.
Explain risk details to management.
Full Access
Answer:
B
Explanation:
The best way for a risk practitioner to help management prioritize risk response is to assess risk against business objectives. This means comparing the level and nature of the risks with the goals and strategies of the organization, and determining which risks pose the most significant threat or opportunity to the achievement of those objectives. By assessing risk against business objectives, the risk practitioner can help management identify the most critical and relevant risks, and prioritize the risk response actions accordingly. The risk response actions should be aligned with the organization’s risk appetite, which is the amount and type of risk that the organization is willing to take in order to meet its strategic goals1. The other options are not the best ways for a risk practitioner to help management prioritize risk response, as they are either less effective orless specific than assessing risk against business objectives. Aligning business objectives to the risk profile is a way of ensuring that the organization’s objectives are realistic and achievable, given the current and potential risks that the organization faces. However, this is not the same as prioritizing risk response, as it does not indicate which risks should be addressed first or howtheyshould be managed. Implementing an organization-specific risk taxonomy is a way of creating a common language and classification system for describing and categorizing risks. This can help improve the consistency and clarity of risk communication and reporting across the organization. However, this is not the same as prioritizing risk response, as it does not measure the likelihood and impact of the risks, or their relation to the organization’s objectives. Explaining risk details to management is a way of providing information and insight on the sources, drivers, consequences, and responses of the risks. This can help increase the awareness and understanding of the risks among the decision makers and stakeholders. However, this is not the same as prioritizing risk response, as it does not suggest or recommend the best course of action for managing the risks. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.6, Page 57.
Question # 343
Which of the following BEST enables risk-based decision making in support of a business continuity plan (BCP)?
A.
Impact analysis
B.
Control analysis
C.
Root cause analysis
D.
Threat analysis
Full Access
Answer:
A
Explanation:
The best tool to enable risk-based decision making in support of a business continuity plan (BCP) is an impact analysis. An impact analysis is a process of identifying and evaluating the potential effects of an interruption or disruption of business operations on the organization’scritical functions, processes, and resources. An impact analysis can help to determine the recovery priorities, objectives, and strategies forthe BCP. Control analysis, root cause analysis, and threat analysis are other possible tools, but they are not as effective as an impact analysis. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 12; CRISC Review Manual, 6th Edition, page 215.
Question # 344
An organization has been made aware of a newly discovered critical vulnerability in a regulatory reporting system. Which of the following is the risk practitioner ' s BEST course of action?
A.
Perform an impact assessment.
B.
Perform a penetration test.
C.
Request an external audit.
D.
Escalate the risk to senior management.
Full Access
Answer:
A
Explanation:
The risk practitioner’s best course of action when an organization has been made aware of a newly discovered critical vulnerability in a regulatory reporting system is to perform an impactassessment, as it involves estimating the potential consequences or damage that the vulnerability may cause to the system and its related business processes, and prioritizing the risk response accordingly. The other options are not the best courses of action, as they may not address the urgency or severity of the vulnerability, or may require the prior knowledge of the impact or risk level, respectively. References = CRISC Review Manual, 7th Edition, page 100.
Question # 345
Which of the following is the PRIMARY reason to perform ongoing risk assessments?
A.
Emerging risk must be continuously reported to management.
B.
New system vulnerabilities emerge at frequent intervals.
C.
The risk environment is subject to change.
D.
The information security budget must be justified.
Full Access
Answer:
C
Explanation:
The primary reason to perform ongoing risk assessments is that the risk environment is subject to change. The risk environment is the external and internal factors that influence the level and nature of the risks that the organization faces1. These factors include economic, political, social, technological, legal,and environmental aspects, as well as the organization’s objectives, strategies, culture, and resources2. The risk environment is dynamic and unpredictable, and may change due to various events, trends, ordevelopments that create new or modify existing risks3. Therefore, it is important to perform ongoing risk assessments to identify, analyze, and evaluate the changes in the risk environment, and to adjust the risk response and management accordingly. Ongoing risk assessments help to ensure that the organization’s risk profile is up to date and reflects the current reality, and that the organization’s risk appetite and tolerance are aligned with the changing risk environment4. The other options are not the primary reason to perform ongoing risk assessments, as they are either less comprehensive or less relevant than the changing risk environment. Emerging risk must be continuously reported to management. This option is a consequence or outcome of performing ongoing risk assessments, not a reason for doing so. Emerging risk is a new or evolving risk that has the potential to affect the organization’s objectives, operations, or performance5. Ongoing risk assessments can help to identify and monitor emerging risks, and to report them to management for decision making and action. However, this is not the main reason for performing ongoing risk assessments, as it does not cover the existing or modified risks that may also change due to the risk environment. Newsystem vulnerabilities emerge at frequent intervals. This option is a specific or narrow example of a changing risk environment, not a general or broad reason for performing ongoing risk assessments. System vulnerabilities are weaknesses or flaws in the design, implementation, or operation of information systems that can be exploited by threats to cause harm or loss6. Ongoing risk assessments can help to discover and assess new system vulnerabilities that may emerge due to technological changes, cyberattacks, or human errors. However, this is not the primary reason for performing ongoing risk assessments, as it does not encompass the other types or sources of risks that may also change due to the risk environment. The information security budget must be justified. This option is a secondary or incidental benefit of performing ongoing risk assessments, not a primary or essential reason for doing so. The information security budget is the amount of money that the organization allocates for implementing and maintaining information security measures and controls7. Ongoing risk assessments can help tojustify the information security budget by demonstrating the value and effectiveness of the security measures and controls in reducing the risks, and by identifying the gaps or needs for additional or improved security measures and controls. However, this is not the main reason for performing ongoing risk assessments, as it does not address the purpose or objective of risk assessment, which is to identify, analyze, and evaluate the risks and their impact on the organization. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1, Page 47.
Question # 346
Which of the following would provide the MOST reliable evidence of the effectiveness of security controls implemented for a web application?
A.
Penetration testing
B.
IT general controls audit
C.
Vulnerability assessment
D.
Fault tree analysis
Full Access
Answer:
A
Explanation:
The most reliable evidence of the effectiveness of security controls implemented for a web application is penetration testing. Penetration testing is a process that simulates an attack on the web application by exploiting its vulnerabilities, using the same tools and techniques as real attackers. Penetration testing helps to evaluate the effectiveness of security controls, because it helps to verify that the security controls can prevent, detect, or mitigate the attack, and to measure the impact and severity of the attack. Penetration testing also helps to identify and address any weaknesses or gaps in the security controls, and to provide recommendations andsolutions for improving the security of the web application. The other options are not as reliable as penetration testing, although they may provide some evidence of the effectiveness of security controls. IT general controls audit, vulnerability assessment, and fault tree analysis are all examples of analytical or evaluative methods, which may help to assess or estimate the effectiveness of security controls, but they do not necessarily test or measure the effectiveness of security controls in a realistic scenario. References = 10
Question # 347
An organization is conducting a review of emerging risk. Which of the following is the BEST input for this exercise?
A.
Audit reports
B.
Industry benchmarks
C.
Financial forecasts
D.
Annual threat reports
Full Access
Answer:
D
Explanation:
The best input for conducting a review of emerging risk is the annual threat reports. Emerging risk is the risk that arises from new or evolving sources, or from existing sources that have not been previously considered or recognized. Emerging risk may have significant impact on the organization’s objectives, strategies, operations, or reputation, and may require new or different risk responses. Annual threat reports are the reports that provide information and analysis on the current and future trends, developments, and challenges in the threat landscape, such as cyberattacks, natural disasters, geopolitical conflicts, or pandemics. Annual threat reports can help to identify and assess the emerging risk, as they can provide insights into the sources, drivers, indicators, and scenarios of the emerging risk, as well as the potential impact and likelihood of the emerging risk. Annual threat reports can also help to benchmark and compare the organization’s risk exposure and preparedness with the industry and the peers, and to prioritize and respond to the emerging risk. Audit reports, industry benchmarks, and financial forecasts are not as useful as annual threat reports, as they do not focus on the emerging risk, and may not capture the latest or future changes in the threat landscape. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 50.
Question # 348
How does an organization benefit by purchasing cyber theft insurance?
A.
It decreases the amount of organizational loss if risk events occur.
B.
It justifies the acceptance of risk associated with cyber theft events.
C.
It transfers risk ownership along with associated liabilities to a third party.
D.
It decreases the likelihood of risk events occurring.
Full Access
Answer:
A
Question # 349
How should an organization approach the retention of data that is no longer needed for business operations?
A.
Data should be retained for a reasonable period of time in case of system rollback.
B.
Data should be destroyed or retained on the basis of a cost-benefit analysis.
C.
Data should be retained based on regulatory requirements.
D.
Data should be destroyed to avoid any risk exposure.
Full Access
Answer:
C
Explanation:
Regulatory and legal compliance dictate data retention requirements, making them the primary basis for retention decisions.
[Reference:CRISC Manual – Domain 1, Slide 462, 560, , , , ]
Question # 350
A multinational company needs to implement a new centralized security system. The risk practitioner has identified a conflict between the organization ' s data-handling policy and local privacy regulations. Which of the following would be the BEST recommendation?
A.
Request a policy exception from senior management.
B.
Comply with the organizational policy.
C.
Report the noncompliance to the local regulatory agency.
D.
Request an exception from the local regulatory agency.
Full Access
Answer:
D
Question # 351
Which of the following BEST facilitates the mitigation of identified gaps between current and desired risk environment states?
A.
Develop a risk treatment plan.
B.
Validate organizational risk appetite.
C.
Review results of prior risk assessments.
D.
Include the current and desired states in the risk register.
Full Access
Answer:
A
Explanation:
Developing a risk treatment plan is the best way to facilitate the mitigation of identified gaps between current and desired risk environment states. A risk treatment plan is a document that outlines the actions and resources needed to implement the chosen risk response strategy for each risk scenario. A risk treatment plan should include the following elements:
Risk scenario description and risk ID
Risk owner and other stakeholders
Risk response strategy and objectives
Risk response actions and tasks
Resources, costs, and benefits
Roles and responsibilities
Timeline and milestones
Performance indicators and monitoring mechanisms
Contingency plans and triggers
A risk treatment plan helps to close the gaps between the current and desired risk environment states by providing a clear and comprehensive roadmap for risk mitigation. It also helps to ensure that the risk response actions are aligned with the organizational risk appetite, objectives, and priorities. A risk treatment plan also facilitates the communication, coordination, and collaboration among the risk owners and other stakeholders involved in the risk mitigation process.
The other options are not the best ways to facilitate the mitigation of identified gaps between current and desired risk environment states. Validating organizational risk appetite is an important step in establishing the risk criteria and thresholds for the risk assessment process, but it does not directly address the gaps between the current and desired risk environment states. Reviewing results of prior risk assessments can provide useful insights and lessons learned for the current risk assessment process, but it does not necessarily lead to the development and implementation of effective risk response actions. Including the current and desired states in the risk register can help to document and monitor the risk scenarios and their status, but it does not provide the details and guidance for risk mitigation. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4: Risk Response, Section 4.2: Risk Treatment, p. 189-191.
Question # 352
When of the following provides the MOST tenable evidence that a business process control is effective?
A.
Demonstration that the control is operating as designed
B.
A successful walk-through of the associated risk assessment
C.
Management attestation that the control is operating effectively
D.
Automated data indicating that risk has been reduced
Full Access
Answer:
D
Explanation:
Automated data indicating that risk has been reduced provides the most tenable evidence that a business process control is effective, because it shows the actual impact and outcome of thecontrol on the risk level. A demonstration that the control is operating as designed, a successful walk-through of the associated risk assessment, and a management attestation that the control is operating effectively are not the most tenable evidence, because they are based on subjective judgments, assumptions, or expectations, not on objective facts or results. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 353
A highly regulated enterprise is developing a new risk management plan to specifically address legal and regulatory risk scenarios What should be done FIRST by IT governance to support this effort?
A.
Request a regulatory risk reporting methodology
B.
Require critical success factors (CSFs) for IT risks.
C.
Establish IT-specific compliance objectives
D.
Communicate IT key risk indicators (KRIs) and triggers
Full Access
Answer:
C
Explanation:
The first thing that should be done by IT governance to support the development of a new risk management plan to specifically address legal and regulatory risk scenarios is to establish IT-specific compliance objectives. Compliance objectives are the goals or targets that the organization sets to ensure that its IT activities and processes comply with the relevant laws, regulations, standards, and contracts. Compliance objectives help to define the scope, criteria, and expectations for the IT compliance program, and to align the IT compliance activities with the organization’s strategy, risk appetite, and performance measures. Compliance objectives also help to communicate and demonstrate the organization’s commitment and accountability for IT compliance to the internal and external stakeholders, such as the board, management, regulators, auditors, and customers. The other options are not the first thing that should be done, although they may be useful or necessary steps or components of the IT compliance program. Requesting a regulatory risk reporting methodology, requiring critical success factors (CSFs) for IT risks, and communicating IT key risk indicators (KRIs) and triggers are all activities that can help to implement and monitor the IT compliance program, but they require the prior definition and agreement of the IT compliance objectives. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.4.1, page 2-37.
Question # 354
Which of the following is MOST important for a risk practitioner to consider when evaluating plans for changes to IT services?
A.
Change testing schedule
B.
Impact assessment of the change
C.
Change communication plan
D.
User acceptance testing (UAT)
Full Access
Answer:
B
Explanation:
According to the CRISC Review Manual1, impact assessment is the process of identifying and evaluating the potential effects of changes to IT services on the organization’s business objectives, processes, resources, and risks. Impact assessment is essential for ensuring that the changes are aligned with the organization’s strategy, goals, and risk appetite, and that the benefits of the changes outweigh the costs and risks. Impact assessment also helps to prioritize, plan, and implement the changes effectively and efficiently, and to monitor and measure the outcomes of the changes. Therefore, the most important factor for a risk practitioner to consider when evaluating plans for changes to IT services is the impact assessment of the change. References = CRISC Review Manual1, page 224.
Question # 355
Which of the following is the PRIMARY purpose of conducting risk and control self-assessments?
A.
To better understand inherent and residual risk within the organization
B.
To gain objective insight into the effectiveness and efficiency of controls
C.
To demonstrate compliance with regulatory and legal control requirements
D.
To facilitate timely and accurate updates to the risk register
Full Access
Answer:
A
Explanation:
Risk and control self-assessments (RCSAs) are designed to helpbusiness units evaluate their own risks and controls, leading to a deeperunderstanding of inherent and residual riskand more accurate risk profiles.
[Reference:CRISC Manual – Domain 4, Slide 392-395, , , , ]
Question # 356
Which of the following is the BEST way to help ensure risk will be managed properly after a business process has been re-engineered?
A.
Reassessing control effectiveness of the process
B.
Conducting a post-implementation review to determine lessons learned
C.
Reporting key performance indicators (KPIs) for core processes
D.
Establishing escalation procedures for anomaly events
Full Access
Answer:
A
Explanation:
 Business process re-engineering is the radical redesign of a business process to achieve significant improvements in performance, quality, cost, or customer satisfaction. Business process re-engineering can introduce new or modified risks to the organization, as well as affectthe existing controls and responses. Therefore, the best way to help ensure risk will be managed properly after a business process has been re-engineered is to reassess the control effectiveness of the process, meaning that the organization should evaluate whether the controls are still adequate, appropriate, and functioning as intended to mitigate the risks. Reassessing the control effectiveness can help to identify any gaps or weaknesses in the control environment, as well as to implement any necessary changes or improvements to the controls. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.2.2, p. 229-230
Question # 357
Which of the following is the ULTIMATE objective of utilizing key control indicators (KCIs) in the risk management process?
A.
To provide insight into the effectiveness of the internal control environment
B.
To provide a basis for determining the criticality of risk mitigation controls
C.
To provide benchmarks for assessing control design effectiveness against industry peers
D.
To provide early warning signs of a potential change in risk level
Full Access
Answer:
D
Explanation:
The ultimate objective of utilizing key control indicators (KCIs) in the risk management process is to provide early warning signs of a potential change in risk level, as they indicate the performance and adequacy of the controls, and alert the stakeholders to any control gaps or deficiencies that may affect the risk exposure and impact. The other options are not the ultimate objectives, as they are more related to the insight, basis, or benchmark of the risk managementprocess, respectively, rather than the early warning sign of the risk management process. References = CRISC Review Manual, 7th Edition, page 110.
Question # 358
A key risk indicator (KRI) is reported to senior management on a periodic basis as exceeding thresholds, but each time senior management has decided to take no action to reduce the risk. Which of the following is the MOST likely reason for senior management ' s response?
A.
The underlying data source for the KRI is using inaccurate data and needs to be corrected.
B.
The KRI is not providing useful information and should be removed from the KRI inventory.
C.
The KRI threshold needs to be revised to better align with the organization s risk appetite
D.
Senior management does not understand the KRI and should undergo risk training.
Full Access
Answer:
C
Explanation:
A key risk indicator (KRI) is a metric that measures the level and trend of a risk that may affect the organization’s objectives, operations, or performance1. A KRI threshold is a predefined value or range that indicates the acceptable or tolerable level of risk for the organization2. Theorganization’s risk appetite is the amount and type of risk that it is willing to take in order to meet its strategic goals3. Therefore, the most likely reason for senior management’s response is that the KRI threshold needs to be revised to better align with the organization’s risk appetite. This means that the current threshold is either too low or too high, resulting in false alarms or missed signals. By adjusting the threshold to reflect the organization’s risk appetite, senior management can ensure that the KRI provides relevant and actionable information for risk management and decision making. The other options are not the most likely reasons for senior management’s response, as they imply that the KRI is faulty, irrelevant, or misunderstood. The underlying data source for the KRI is using inaccurate data and needs to be corrected. This option assumes that the KRI is based on erroneous or unreliable data, which would affect its validity and reliability. However, this is not the most likely reason, as senior management would be expected to verify the data quality and accuracy before using the KRI for risk monitoring and reporting. The KRI is not providing useful information and shouldbe removed from the KRI inventory. This option assumes that the KRI is not aligned with the organization’s objectives, strategies, or risk profile, which would affect its usefulness and value. However, this is not the most likely reason, as senior management would be expected to review and update the KRI inventory periodically to ensure that the KRIs are relevant and meaningful for risk management. Senior management does not understand the KRI and should undergo risk training. This option assumes that senior management lacks the knowledge or skills to interpret and use the KRI for risk management, which would affect their competence and confidence. However, this is not the most likely reason, as senior management would be expected to have sufficient risk awareness and education to understand and apply the KRI for risk management. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.4, Page 53.
Question # 359
The risk associated with an asset before controls are applied can be expressed as:
A.
a function of the likelihood and impact
B.
the magnitude of an impact
C.
a function of the cost and effectiveness of control.
D.
the likelihood of a given threat
Full Access
Answer:
A
Explanation:
The risk associated with an asset before controls are applied is also known as the inherent risk. It is the level of risk that exists in the absence of any mitigating actions or measures. To express the inherent risk, one needs to consider two factors: the likelihood and the impact of a potential threat. The likelihood is the probability or frequency of a threat occurring, while the impact is the magnitude or severity of the consequences if the threat materializes. The inherent risk can be calculated by multiplying the likelihood and the impact, or by using a risk matrix that assigns a risk rating based on the combination of these two factors. The other options are not correct ways of expressing the inherent risk, as they do not account for both the likelihood and the impact of a threat. The magnitude of an impact is only one component of the risk, and it does not reflect how likely the threat is to happen. The function of the cost and effectiveness of control is related to the residual risk, which is the risk that remains after controls are applied. The likelihood of a given threat is also only one component of the risk, and it does not indicate how severe the impact would be if the threat occurs. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.1, Page 47.
Question # 360
Which of the following BEST indicates effective information security incident management?
A.
Monthly trend of information security-related incidents
B.
Average time to identify critical information security incidents
C.
Frequency of information security incident response plan testing
D.
Percentage of high-risk security incidents
Full Access
Answer:
B
Explanation:
 The average time to identify critical information security incidents is the best indicator of effective information security incident management, as it measures how quickly the organization can detect and respond to the most severe threats to its information assets. The faster the organization can identify critical incidents, the lower the potential impact and damage they can cause. The average time to identify critical incidents also reflects the efficiency and accuracy of the monitoring and reporting mechanisms, as well as the awareness and training of the staff and stakeholders. The other options are not the best indicators of effective information security incident management, as they do not directly measure the performance or quality of the incident response process. The monthly trend of information security-related incidents may show the frequency or severity of the incidents, but not how well they are managed. The frequency of information security incident response plan testing may show the preparedness or maturity of the organization, but not the actual effectiveness of the plan. The percentage of high-risk security incidents may show the risk exposure or appetite of the organization, but not the risk mitigationor treatment. References = 7 Types of Information Security Incidents and How to Respond; Annex A.16: Information Security Incident Management - ISMS.online; CISM Isaca Exam Questions and Answers - CertLibrary.com
Question # 361
Which of the following is MOST helpful to review when assessing the risk exposure associated with ransomware?
A.
Potentially impacted business processes
B.
Recent changes in the environment
C.
Key performance indicators (KPIs)
D.
Suspected phishing events
Full Access
Answer:
A
Question # 362
Which of the following provides the BEST evidence that a selected risk treatment plan is effective?
A.
Identifying key risk indicators (KRIs)
B.
Evaluating the return on investment (ROI)
C.
Evaluating the residual risk level
D.
Performing a cost-benefit analysis
Full Access
Answer:
C
Explanation:
 A risk treatment plan is a document that describes the actions and resources required to implement the chosen risk response for a specific risk scenario. A risk response can be to accept, avoid, transfer, or mitigate the risk. The effectiveness of a risk treatment plan can be measured by how well it reduces the risk exposure and achieves the desired outcomes. The best evidence that a selected risk treatment plan is effective is to evaluate the residual risk level, which is the remaining risk after the risk treatment plan has been implemented. The residual risk level should be within the organization’s risk appetite and tolerance, and should reflect the actual risk reduction and value creation of the risk treatment plan. Evaluating the residual risk level can also help to identify any gaps or issues that need to be addressed, and to monitor and report on the risk performance and improvement. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.2, p. 108-109
Question # 363
The BEST criteria when selecting a risk response is the:
A.
capability to implement the response
B.
importance of IT risk within the enterprise
C.
effectiveness of risk response options
D.
alignment of response to industry standards
Full Access
Answer:
C
Explanation:
The effectiveness of risk response options is the best criteria when selecting a risk response, because it reflects the degree to which the response can reduce the impact or likelihood of the risk, or enhance the benefit or opportunity of the risk. The effectiveness of risk response options can be evaluated by considering factors such as cost, feasibility, timeliness, and alignment with the organization’s objectives and risk appetite. The other options are not as good as the effectiveness of risk response options, because they do not measure the outcome or value of the response, but rather focus on the input or process of the response, as explained below:
A. Capability to implement the response is a criteria that considers the availability and adequacy of the resources, skills, and knowledge required to execute the response. While this is an important factor to consider, it does not indicate how well the response can address the risk or achieve the desired result.
B. Importance of IT risk within the enterprise is a criteria that considers the significance and priority of the risk in relation to the organization’s strategy, objectives, and operations. Whilethis is an important factor to consider, it does not indicate how well the response can address the risk or achieve the desired result.
D. Alignment of response to industry standards is a criteria that considers the compliance and conformity of the response with the best practices, norms, and expectations of the industry or sector. While this is an important factor to consider, it does not indicate how well the response can address the risk or achieve the desired result. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.2.2, page 40. How to Select Your Risk Responses -Rebel’s Guide to Project Management, Risk Response Plan in Project Management: Key Strategies & Tips, Risk Responses - options for managing risk - Stakeholdermap.com
Question # 364
Which of the following is a responsibility of the second line of defense in the three lines of defense model?
A.
Performing duties independently to provide assurance
B.
Alerting operational management to emerging issues
C.
Implementing corrective actions to address deficiencies
D.
Owning risk scenarios and bearing the consequences of loss
Full Access
Answer:
B
Explanation:
The second line (risk management, compliance) provides oversight and support to the first line (operations). It monitors risk-related activities, issues alerts, and helps ensure controls are properly designed and implemented, but does not own the risk.
[Reference:CRISC Manual – Domain 1, Slide 44-47, , , , ]
Question # 365
When prioritizing risk response, management should FIRST:
A.
evaluate the organization s ability and expertise to implement the solution.
B.
evaluate the risk response of similar organizations.
C.
address high risk factors that have efficient and effective solutions.
D.
determine which risk factors have high remediation costs
Full Access
Answer:
C
Explanation:
According to the Risk and Information Systems Control Study Manual, the first step in prioritizing risk response is to address the high risk factors that have efficient and effective solutions. This means that management should focus on the risks that have the most impact on the organization’s objectives and can be mitigated with the least amount of resources and effort. This approach helps to optimize the risk response process and achieve the best results in terms of risk reduction and value creation. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 5, Section 5.3.2, Page 223.
Question # 366
Which of the following is the PRIMARY consideration when determining the impact to an organization after the discovery of malware on an endpoint device?
A.
Asset criticality and sensitivity
B.
Currency of anti-malware signatures
C.
Availability of patches and security updates
D.
Currency of the incident response plan
Full Access
Answer:
A
Explanation:
The correct answer isAbecause when malware is discovered on an endpoint device, the first consideration in determiningimpactis thecriticality and sensitivity of the affected asset. The business importance of the device, the data it stores or accesses, and the role it plays in operations determine how serious the incident is to the organization.
The other options are less important for determining impact:
B. Currency of anti-malware signaturesrelates to control effectiveness, not the primary measure of business impact.
C. Availability of patches and security updatesis relevant to remediation, but not the main factor in assessing impact.
D. Currency of the incident response planaffects preparedness, not the actual impact of the malware event.
Exact Extracts supporting the answer:
“IT risk is measured by its impact on business operations.â€
“The primary reason risk professionals conduct risk assessments is to identify risk with the highest business impact.â€
“The main outcome of a business impact analysis (BIA) is the criticality of business processes.â€
“To determine the level of protection required for securing personally identifiable information a risk practitioner should PRIMARILY consider the sensitivity property of the information.â€
“The criticality of an IT infrastructure element can be quantified based on dependencies.â€
These extracts show that impact assessment is driven primarily by business criticality and information sensitivity. Therefore,asset criticality and sensitivityis the primary consideration.
===========
Question # 367
Which of the following is the BEST way to determine the ongoing efficiency of control processes?
A.
Perform annual risk assessments.
B.
Interview process owners.
C.
Review the risk register.
D.
Analyze key performance indicators (KPIs).
Full Access
Answer:
D
Explanation:
Control processes are the procedures and activities that aim to ensure the effectiveness and efficiency of the organization’s operations, the reliability of its information, and the compliance with its policies and regulations12.
The ongoing efficiency of control processes is the degree to which the control processes achieve their intended results with minimum resources, costs, or waste34.
The best way to determine the ongoing efficiency of control processes is to analyze key performance indicators (KPIs), which are quantifiable measures of progress toward an intended result, such as a strategic objective or a desired outcome56.
Analyzing KPIs is the best way because it provides a systematic and consistent method of evaluating the performance of the control processes, and identifying the areas of improvement or optimization56.
Analyzing KPIs is also the best way because it enables the organization to monitor and report the efficiency of the control processes to the relevant stakeholders, and to take corrective or preventive actions when necessary56.
The other options are not the best way, but rather possible sources of information or inputs that may support or complement the analysis of KPIs. For example:
Performing annual risk assessments is a way to identify and evaluate the risks that may affect the organization’s objectives, and to determine the adequacy and effectiveness ofthe control processes in mitigating those risks12. However, this way is not the best because it is periodic rather than continuous, and may not capture the changes or trends in the efficiency of the control processes12.
Interviewing process owners is a way to collect and verify the information and feedback from the people who are responsible for designing, implementing, and operating the control processes12. However, this way is not the best because it is subjective and qualitative, and may not provide reliable or comparable data on the efficiency of the control processes12.
Reviewing the risk register is a way to examine and update the documentation and status of the risks and the control processes that are associated with them12. However, this way is not the best because it is descriptive rather than analytical, and may not measure or evaluate the efficiency of the control processes12. References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: The Control Process | Principles of Management4
4: Control Management: What it is + Why It’s Essential | Adobe Workfront5
5: What is a Key Performance Indicator (KPI)? Guide & Examples - Qlik1
6: What is a Key Performance Indicator (KPI)? - KPI.org2
Question # 368
Which of the following activities should only be performed by the third line of defense?
A.
Operating controls for risk mitigation
B.
Testing the effectiveness and efficiency of internal controls
C.
Providing assurance on risk management processes
D.
Recommending risk treatment options
Full Access
Answer:
C
Explanation:
Providing assurance on risk management processes is the activity that should only be performed by the third line of defense, because it is the role and responsibility of the independent andobjective assurance function, such as internal audit or external audit, to evaluate and report on the effectiveness and efficiency of the risk management processes and controls. The third line of defense is the last layer of the three lines of defense model, which is a framework that defines the roles and responsibilities of different functions and levels within the organization for risk management and control. The first line of defense is the operational management and staff, who are responsible for identifying, assessing, and managing the risks and controls within their areas of responsibility. The second line of defense is the oversight and support functions, such as risk management, compliance, or legal, who are responsible for establishing and monitoring the risk policies, standards, and frameworks, and providing guidance and advice to the first line of defense. The third line of defense is the assurance function, who are responsible for providing independent and objective assurance on the adequacy and effectiveness of the risk management processes and controls, and reporting to the senior management and the board of directors. Operating controls for risk mitigation, testing the effectiveness and efficiency of internal controls, and recommending risk treatment options are all activities that can be performed by the first or second line of defense, but not by the third line of defense, as they are not part of the assurance function. References = Risk and Information Systems Control Study Manual, Chapter 2, Section 2.4.1, page 59
Question # 369
An organization has outsourced its backup and recovery procedures to a third-party cloud provider. Which of the following is the risk practitioner s BEST course of action?
A.
Accept the risk and document contingency plans for data disruption.
B.
Remove the associated risk scenario from the risk register due to avoidance.
C.
Mitigate the risk with compensating controls enforced by the third-party cloud provider.
D.
Validate the transfer of risk and update the register to reflect the change.
Full Access
Answer:
D
Explanation:
The risk practitioner’s BEST course of action is to validate the transfer of risk and update the register to reflect the change, because outsourcing the backup and recovery procedures to a third-party cloud provider does not eliminate the risk, but rather transfers it to the service provider. The risk practitioner should verify that the service provider has adequate controls and capabilities to handle the backup and recovery procedures, and that the contractual agreement specifies the roles and responsibilities of both parties. The risk practitioner should also update the risk register to reflect the new risk owner and the residual risk level. The other options are not the best course of action, because:
Option A: Accepting the risk and documenting contingency plans for data disruption is not the best course of action, because it implies that the risk practitioner is still responsible for the risk, even though it has been transferred to the service provider. Contingency plans are also reactive measures, rather than proactive ones.
Option B: Removing the associated risk scenario from the risk register due to avoidance is not the best course of action, because it implies that the risk has been eliminated, which is not the case. The risk still exists, but it has been transferred to the service provider. The risk register should reflect the current risk status and ownership.
Option C: Mitigating the risk with compensating controls enforced by the third-party cloud provider is not the best course of action, because it implies that the risk practitioner is still involved in the risk management process, even though the risk has been transferred to the service provider. The risk practitioner should rely on the service provider’s controls and capabilities, andmonitor their performance and compliance. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 196.
Question # 370
An organization is unable to implement a multi-factor authentication requirement until the next fiscal year due to budget constraints. Consequently, a policy exception must be submitted. Which of the following is MOST important to include in the analysis of the exception?
A.
Sections of the policy that may justify not implementing the requirement
B.
Risk associated with the inability to implement the requirement
C.
Budget justification to implement the new requirement during the current year
D.
Industry best practices with respect to implementation of the proposed control
Full Access
Answer:
B
Explanation:
The most important factor to include in the analysis of the policy exception is the risk associated with the inability to implement the multi-factor authentication requirement. A policy exception is a temporary orpermanent deviation from the established policies or standards of the organization, due to various reasons, such as budget constraints, technical limitations, or business needs. A policy exception must be submitted and approved by the appropriate authority, and it must include a clear and comprehensive analysis of the rationale, impact, and mitigation of the exception. The risk associated with the inability to implement the multi-factor authentication requirement is the most important factor to include in the analysis, because it evaluates the probability and severity of potential threats or incidents that could exploit the lack of multi-factor authentication, such as unauthorized access, data breach, or identity theft. The risk analysis also helps to justify the need and urgency of the policy exception, and to propose alternative or compensating controls to reduce or transfer the risk, such as password policies, access restrictions, or encryption. The other options are not the most important factor, although they may be relevant or supportive to the policy exception analysis. Sections of the policy that may justify not implementing the requirement are the clauses or provisions in the policy that allow or enable the policy exception, such as exemptions, waivers, or variances. These sections can help to validate the legitimacy and feasibility of the policy exception, but they do not assess the risk or the impact of the exception. Budget justification to implement the new requirement during the current year is the explanation and evidence of the financial resources and constraints that affect the implementation of the multi-factor authentication requirement. This justification can help to demonstrate the cost-benefit and return on investment of the requirement, but it does not measure the risk or the mitigation of the exception. Industry best practices with respect to implementation of the proposed control are the proven methods and standards that are adopted by the leading organizations in a specific field or sector for implementing the multi-factor authentication requirement. These best practices can help to benchmark and improve the quality and effectiveness of the requirement, but they do not quantify the risk or the impact of the exception. References = Policy Exception Management - ISACA, Multi-Factor Authentication Policy - University of Arkansas, Common Conditional Access policy: Require MFA for all users
Question # 371
Which of the following is MOST helpful when prioritizing action plans for identified risk?
A.
Comparing risk rating against appetite
B.
Obtaining input from business units
C.
Determining cost of controls to mitigate risk
D.
Ranking the risk based on likelihood of occurrence
Full Access
Answer:
A
Explanation:
Comparing risk rating against appetite is the most helpful criterion when prioritizing action plans for identified risk, as it helps to determine the urgency and importance of addressing the risk. Risk rating is the level of risk after considering the likelihood and impact of a risk event, and risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. By comparing risk rating against appetite, an organization can identify which risks are above, within, or below its tolerance level, and prioritize the action plans accordingly. Risks that are above the appetite level should be treated with the highest priority, as they pose asignificant threat to the organization’s objectives and performance. Risks that are within the appetite level should be monitored and controlled regularly, as they are acceptable but still require attention. Risks that are below the appetite level should be reviewed periodically, as they are negligible or insignificant.
[References:, •ISACA, Risk IT Framework, 2nd Edition, 2019, p. 751, •ISACA, Tips for Prioritizing Risk in Your Risk Register2, , , , , , , , , , , ]
Question # 372
Which of the following would MOST effectively reduce risk associated with an increase of online transactions on a retailer website?
A.
Scalable infrastructure
B.
A hot backup site
C.
Transaction limits
D.
Website activity monitoring
Full Access
Answer:
D
Explanation:
The most effective way to reduce risk associated with an increase of online transactions on a retailer website is to implement website activity monitoring. Website activity monitoring can help to detect and prevent fraudulent transactions, unauthorized access, data breaches, and other cyber threats that may compromise the security and integrity of the website and its data. Scalable infrastructure, a hot backup site, and transaction limits are other possible ways to reduce risk, but they are not as effective as website activity monitoring. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
Question # 373
Which of the following will help ensure the elective decision-making of an IT risk management committee?
A.
Key stakeholders are enrolled as members
B.
Approved minutes ate forwarded to senior management
C.
Committee meets at least quarterly
D.
Functional overlap across the business is minimized
Full Access
Answer:
A
Explanation:
The best way to ensure the effective decision-making of an IT risk management committee is to enroll key stakeholders as members. Key stakeholders are the individuals or groups who have an interest or influence in the IT risk management process, such as business owners, senior management, IT managers, auditors, regulators, customers, and suppliers. By involving key stakeholders in the IT risk management committee, the committee can benefit from their diverse perspectives, expertise, and experience, and ensure that the IT risk management decisions are aligned with the business objectives, priorities, and expectations. Key stakeholders can also provide valuable input, feedback, and support for the IT risk management activities, and help communicate and implement the IT risk management decisions across the organization. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 36.
Question # 374
Senior management has asked the risk practitioner for the overall residual risk level for a process that contains numerous risk scenarios. Which of the following should be provided?
A.
The sum of residual risk levels for each scenario
B.
The loss expectancy for aggregated risk scenarios
C.
The highest loss expectancy among the risk scenarios
D.
The average of anticipated residual risk levels
Full Access
Answer:
D
Explanation:
Residual risk is the remaining risk after the risk response has been implemented. Residual risk can be expressed as a combination of the probability and impact of the risk scenario, or as a single value such as loss expectancy. Residual risk can be compared with the inherent risk, which is the risk level before considering the existing controls or responses, to evaluate the risk reduction and value creation of the risk response. Senior management has asked the risk practitioner for the overall residual risk level for a process that contains numerous risk scenarios. The best way to provide this information is to calculate the average of anticipated residual risklevels for each risk scenario, and to present it as a single value or a range. This can help to provide a comprehensive and consistent view of the residual risk exposure and performance of the process, as well as to align it with the organization’s risk appetite and tolerance. The sum of residual risk levels for each scenario, the loss expectancy for aggregated risk scenarios, or the highest loss expectancy among the risk scenarios are not the best ways to provide the overall residual risk level, as they may overestimate or underestimate the risk exposure and performance of the process, and may not reflect the actual risk reduction and value creation of the risk response. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.2, p. 108-109
Question # 375
Which of the following provides the MOST useful information for developing key risk indicators (KRIs)?
A.
Business impact analysis (BIA) results
B.
Risk scenario ownership
C.
Risk thresholds
D.
Possible causes of materialized risk
Full Access
Answer:
D
Explanation:
Key risk indicators (KRIs) are metrics that provide an early warning of increasing risk exposure in various areas of the organization. They help to monitor changes in the level of risk and enable timely actions to mitigate the risk. The most useful information for developing KRIs is the possible causes of materialized risk, which are the factors or events that trigger or contribute to the occurrence of a risk. By identifying the possible causes of materialized risk, an organization can design KRIs that measure the likelihood and impact of the risk, and alert the management when the risk exceeds the acceptable level. References = CRISC Review Manual, 7th Edition, page 101.
Question # 376
Which of the following is the BEST way to mitigate the risk to IT infrastructure availability?
A.
Establishing a disaster recovery plan (DRP)
B.
Establishing recovery time objectives (RTOs)
C.
Maintaining a current list of staff contact delays
D.
Maintaining a risk register
Full Access
Answer:
A
Explanation:
The best way to mitigate the risk to IT infrastructure availability is to establish a disaster recovery plan (DRP), because a DRP is a document that defines the procedures and resources needed to restore the IT infrastructure and resume the critical business functions in the event of a disaster or disruption. A DRP helps to minimize the downtime, data loss, and financial impact of a disaster, and ensures the continuity of operations and services. The other options are not the best ways to mitigate the risk to IT infrastructure availability, although they may also be helpful in supporting the DRP. Establishing recovery time objectives (RTOs), maintaining a current list of staff contact details, and maintaining a risk register are examples of planning or monitoring activities that aim to define the requirements, roles, and responsibilities for the disaster recovery process, but they do not address the actual implementation or execution of the DRP. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 377
Which of the following is the BEST measure of the effectiveness of an employee deprovisioning process?
A.
Number of days taken to remove access after staff separation dates
B.
Number of days taken for IT to remove access after receipt of HR instructions
C.
Number of termination requests processed per reporting period
D.
Number of days taken for HR to provide instructions to IT after staff separation dates
Full Access
Answer:
A
Explanation:
 The effectiveness of an employee deprovisioning process can be measured by the number of days taken to remove access after staff separation dates, as this indicates how quickly and completely the organisation can revoke the privileges of former employees and reduce the risk of unauthorized access or data leakage. The number of days taken for IT to remove access after receipt of HR instructions is a measure of the efficiency of the IT department, but not the overall process. The number of termination requests processed per reporting period is a measure of the volume of the process, but not the quality or timeliness. The number of days taken for HR to provide instructions to IT after staff separation dates is a measure of the performance of the HR department, but not the entire process. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 152.
Question # 378
An organization has an approved bring your own device (BYOD) policy. Which of the following would BEST mitigate the security risk associated with the inappropriate use of enterprise applications on the devices?
A.
Periodically review application on BYOD devices
B.
Include BYOD in organizational awareness programs
C.
Implement BYOD mobile device management (MDM) controls.
D.
Enable a remote wee capability for BYOD devices
Full Access
Answer:
C
Explanation:
The best way to mitigate the security risk associated with the inappropriate use of enterprise applications on the BYOD devices is to implement BYOD mobile device management (MDM) controls. MDM controls are software tools or services that allow the organization to remotely manage, monitor, and secure the BYOD devices and the enterprise applications and data on them. MDM controls can help to enforce security policies, restrict unauthorized access, encrypt sensitive data, wipe data in case of loss or theft, and update or patch applications. The other options are not as effective as implementing MDM controls, as they are related to the review, awareness, or recovery of the BYOD devices and applications, not the prevention or protection of the security risk. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Question # 379
Which of the following is the PRIMARY reason for an organization to ensure the risk register is updated regularly?
A.
Risk assessment results are accessible to senior management and stakeholders.
B.
Risk mitigation activities are managed and coordinated.
C.
Key risk indicators (KRIs) are evaluated to validate they are still within the risk threshold.
D.
Risk information is available to enable risk-based decisions.
Full Access
Answer:
D
Explanation:
The PRIMARY reason for an organization to ensure the risk register is updated regularly is to make sure that risk information is available to enable risk-based decisions, because the risk register is a tool that documents and tracks the identified risks, their characteristics, their status, and their responses. The risk register provides a comprehensive and current view of the risk profile and exposure of the organization, and it supports the decision-making process and the risk management activities. The other options are not the primary reason, because:
Option A: Risk assessment results are accessible to senior management and stakeholders is a benefit of updating the risk register regularly, but not the primary reason. Risk assessment results are the outputs of the risk analysis process, and they should be recorded and communicated to the relevant parties, but they are not the only or the most important information in the risk register.
Option B: Risk mitigation activities are managed and coordinated is a result of updating the risk register regularly, but not the primary reason. Risk mitigation activities are the actions taken to address the identified risks, and they should be monitored and reported in the risk register, but they are not the only or the most important information in the risk register.
Option C: Key risk indicators (KRIs) are evaluated to validate they are still within the risk threshold is a process that involves updating the risk register regularly, but not the primary reason. KRIs are indicators that measure and monitor the risk exposure and performance of the organization, and they should be compared with the risk threshold to determine if the risk level is acceptable or not, and if any action is required, but they are not the only or the most important information in the risk register. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 108.
Question # 380
What would be MOST helpful to ensuring the effective implementation of a new cybersecurity program?
A.
Creating metrics to report the number of security incidents
B.
Hiring subject matter experts for the program
C.
Establishing a budget for additional resources
D.
Assigning clear ownership of the program
Full Access
Answer:
D
Explanation:
The most helpful action to ensure the effective implementation of a new cybersecurity program is assigning clear ownership of the program. Here ' s why:
Clear Ownership:
Assigning clear ownership ensures that there is accountability and responsibility for the implementation and success of the program.
The program owner will coordinate activities, allocate resources, and monitor progress to ensure that objectives are met.
Creating Metrics:
While metrics are important for monitoring and reporting, they do not directly ensure the effective implementation of the program.
Hiring Subject Matter Experts:
Subject matter experts are valuable for providing insights and guidance, but without clear ownership, their efforts may not be effectively coordinated or aligned with program goals.
Establishing a Budget:
A budget is necessary for securing resources, but it must be managed and directed by a responsible owner to ensure the effective use of those resources.
[References:, The CRISC Review Manual discusses the importance of assigning roles and responsibilities, including ownership, to ensure the effective implementation of risk management programs (CRISC Review Manual, Chapter 1: Governance, Section 1.2.1 RACI)., , , , , , , , , , , ]
Question # 381
An organization ' s risk register contains a large volume of risk scenarios that senior management considers overwhelming. Which of the following would BEST help to improve the risk register?
A.
Analyzing the residual risk components
B.
Performing risk prioritization
C.
Validating the risk appetite level
D.
Conducting a risk assessment
Full Access
Answer:
B
Explanation:
Performing risk prioritization would best help to improve the risk register, which is a document that records and summarizes the key information and data about the identified risks and the risk responses1. Risk prioritization is the process of ranking the risks according to their significance and urgency, based on their probability and impact2. By performing risk prioritization, the organization can:
Reduce the complexity and volume of the risk register, and focus on the most important and relevant risks that require immediate attention and action3.
Enhance the communication and understanding of the risks among the senior management and other stakeholders, and facilitate the decision-making and resource allocation for the risk responses4.
Improve the efficiency and effectiveness of the risk management process, and ensure that the risk register is aligned with the organization’s risk strategy, objectives, and appetite5.
The other options are not the best ways to improve the risk register, because:
Analyzing the residual risk components is not the best way, as it may not address the issue of the large volume of risk scenarios. Residual risk is the level of risk that remains after the implementation of risk responses6. Analyzing the residual risk components can help to measure the exposure or uncertainty of the assets, and to determine the need and extent of the risk responses. However, it may not reduce the complexity or volume of the risk register, as it may add more information or data to the risk register.
Validating the risk appetite level is not the best way, as it may not address the issue of the overwhelming risk scenarios. Risk appetite is the amount and type of risk that the organization is willing to accept or pursue in order to achieve its objectives7. Validating the risk appetite levelcan help to ensure that the risk register is consistent and proportional to the risk level, and that the risk responses are suitable and feasible. However, it may not reduce the complexity or volume of the risk register, as it may require more information or data to validate the risk appetite level.
Conducting a risk assessment is not the best way, as it may not address the issue of the existing risk scenarios. Risk assessment is the process of estimating the probability and impact of the risks, and prioritizing the risks based on their significance and urgency. Conducting a risk assessment can help to identify and analyze new or emerging risks, and to update or revise the risk register accordingly. However, it may not reduce the complexity or volume of the risk register, as it may introduce more information or data to the risk register.
References =
Risk Register - CIO Wiki
Risk Prioritization - CIO Wiki
Risk Prioritization: A Guide for Project Managers - ProjectManager.com
Risk Prioritization: How to Prioritize Risks in Project Management - Clarizen
Risk Prioritization: A Key Step in Risk Management - ISACA
Residual Risk - CIO Wiki
Risk Appetite - CIO Wiki
[Risk Assessment - CIO Wiki]
Question # 382
Which of the following is the BEST indication that key risk indicators (KRls) should be revised?
A.
A decrease in the number of critical assets covered by risk thresholds
B.
An Increase In the number of risk threshold exceptions
C.
An increase in the number of change events pending management review
D.
A decrease In the number of key performance indicators (KPls)
Full Access
Answer:
A
Explanation:
The best indication that key risk indicators (KRIs) should be revised is a decrease in the number of critical assets covered by risk thresholds. KRIs are metrics that provide information on the level of exposure to a given risk. Risk thresholds are the predefined values or ranges that indicate the acceptable or unacceptable level of risk exposure. Critical assets are the assets that are essential or vital for the achievement of the objectives or the continuity of the operations. A decrease in the number of critical assets covered by risk thresholds means that the KRIs are not capturing or reflecting the current and relevant risk exposure of the organization, and that they may not provide sufficient or accurate information for risk management decisions. Therefore, the KRIs should be revised to ensure that they cover all the critical assets and their risk thresholds.The other options are not as indicative as a decrease in the number of critical assets covered by risk thresholds, as they are related to the outcomes, impacts, or activities of the KRIs, not thescope or quality of the KRIs. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Key Performance Indicators, page 183.
Question # 383
When reviewing a risk response strategy, senior management ' s PRIMARY focus should be placed on the:
A.
cost-benefit analysis.
B.
investment portfolio.
C.
key performance indicators (KPIs).
D.
alignment with risk appetite.
Full Access
Answer:
D
Explanation:
According to the What To Look For When Assessing Your Organization’s Security Risk Posture article, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite should be aligned with the organization’s strategy, goals, and values, and should reflect the organization’s risk culture and capabilities. When reviewing a risk response strategy, senior management’s primary focus should be placed on the alignment with risk appetite, as this indicates how well the risk response strategy supports the organization’s objectives and expectations, and how consistent it is with the organization’s risk tolerance and risk profile. By ensuring the alignment with risk appetite, senior managementcan evaluate the effectiveness and efficiency of the risk response strategy, and determine if any adjustments or improvements are needed. References = What To Look For When Assessing Your Organization’s Security Risk Posture
Question # 384
Which of the following should a risk practitioner recommend FIRST when an increasing trend of risk events and subsequent losses has been identified?
A.
Conduct root cause analyses for risk events.
B.
Educate personnel on risk mitigation strategies.
C.
Integrate the risk event and incident management processes.
D.
Implement controls to prevent future risk events.
Full Access
Answer:
A
Explanation:
Conducting root cause analyses for risk events is the first recommendation that a risk practitioner should make when an increasing trend of risk events and subsequent losses has been identified, as this helps to identify the underlying causes and sources of the risk events, and to determine the appropriate actions to address them. Root cause analysis is a systematic process of collecting and analyzing data, finding the root causes, and implementing solutions to prevent recurrence or reduce the impact of the risk events. Educating personnel on risk mitigation strategies, integrating the risk event and incident management processes, and implementing controls to prevent future risk events are not the first recommendations, but rather the possible outcomes or actions of conducting root cause analyses for risk events. References = CRISC Certified in Riskand Information Systems Control – Question208; ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 208.
Question # 385
Which of the following approaches MOST effectively enables accountability for data protection?
A.
Establishing ownership for data within applications and systems
B.
Establishing discipline for policy violations by data owners
C.
Implementing data protection policies across the organization
D.
Conducting data protection awareness and training campaigns
Full Access
Answer:
A
Explanation:
Assigning ownership ensures accountability, as data owners are responsible for ensuring appropriate protections are in place and enforced.
[Reference:CRISC Manual – Domain 1, Slide 403, 471, , , , , ]
Question # 386
During an acquisition, which of the following would provide the MOST useful input to the parent company ' s risk practitioner when developing risk scenarios for the post-acquisition phase?
A.
Risk management framework adopted by each company
B.
Risk registers of both companies
C.
IT balanced scorecard of each company
D.
Most recent internal audit findings from both companies
Full Access
Answer:
B
Explanation:
The most useful input to the parent company’s risk practitioner when developing risk scenarios for the post-acquisition phase is the risk registers of both companies. The risk register is a document that records the details of the risks, such as their sources, causes, consequences, likelihood, impact, and responses. By reviewing the risk registers of both companies, the risk practitioner can identify the existing and potential risks that may affect the post-acquisition integration, performance, and value. The risk management framework, the IT balancedscorecard, and the most recent internal audit findings are other possible inputs, but they are not as useful as the risk registers. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Question # 387
Which of the following would be MOST helpful in assessing the risk associated with data loss due to human vulnerabilities?
A.
Reviewing password change history
B.
Performing periodic access recertification
C.
Conducting social engineering exercises
D.
Reviewing the results of security awareness surveys
Full Access
Answer:
C
Explanation:
Social engineering exercises are simulations of real-world attacks that exploit human vulnerabilities, such as phishing, baiting, pretexting, or quid pro quo. Conducting social engineering exercises can help assess the risk associated with data loss due to human vulnerabilities by measuring the employees’ susceptibility to such attacks, their awareness of security policies and procedures, and their response to incidents. Reviewing password change history, performing periodic access recertifications, and reviewing the results of security awareness surveys are also useful, but they do not directly test the employees’ behavior and resilience in the face of social engineering attacks.
Question # 388
Which of the following BEST helps to ensure disaster recovery staff members
are able to complete their assigned tasks effectively during a disaster?
A.
Performing parallel disaster recovery testing
B.
Documenting the order of system and application restoration
C.
Involving disaster recovery staff members in risk assessments
D.
Conducting regular tabletop exercises and scenario analysis
Full Access
Answer:
D
Question # 389
To minimize the risk of a potential acquisition being exposed externally, an organization has selected a few key employees to be engaged in the due diligence process. A member of the due diligence team realizes a close acquaintance is a high-ranking IT professional at a subsidiary of the company about to be acquired. What is the BEST course of action for this team member?
A.
Enforce segregation of duties.
B.
Disclose potential conflicts of interest.
C.
Delegate responsibilities involving the acquaintance.
D.
Notify the subsidiary ' s legal team.
Full Access
Answer:
B
Explanation:
A conflict of interest is a situation where a person’s personal or professional interests may interfere with their ability to act in the best interest of the organization or the project1. A conflict of interest can compromise the integrity, objectivity, and impartiality of the person, and create ethical or legal issues for the organization or the project2. In the context of due diligence, a conflict of interest can affect the quality and reliability of the information and analysis, and jeopardize the success and confidentiality of the acquisition3.
The best course of action for a member of the due diligence team who realizes a close acquaintance is a high-ranking IT professional at a subsidiary of the company about to be acquired is to disclose potential conflicts of interest. This means that the team member should inform the due diligence leader and the organization’s management about the relationship with the acquaintance, and explain how it may affect their role or responsibility in the due diligence process. By disclosing potential conflicts of interest, the team member can:
Demonstrate honesty and transparency, and uphold the ethical standards and values of the organization and the project4.
Enable the due diligence leader and the organization’s management to assess the situation and decide the appropriate course of action, such as reassigning the team member, implementing additional controls or safeguards, or obtaining consent or approval from the relevant parties5.
Avoid or minimize the negative consequences or risks that may arise from the conflict of interest, such as legal liability, reputational damage, or loss of trust and credibility6.
References =
Conflict of Interest - CIO Wiki
What is a Conflict of Interest? Give Me Some Examples - The Balance Careers
How to Avoid Conflicts of Interest in M & A Transactions - DealRoom
How to Handle Conflicts of Interest - Harvard Business Review
Conflict of Interest Policy - ISACA
Managing Conflicts of Interest in the Public Sector Toolkit - OECD
Question # 390
Read " rights to application files in a controlled server environment should be approved by the:
A.
business process owner.
B.
database administrator.
C.
chief information officer.
D.
systems administrator.
Full Access
Answer:
A
Explanation:
Read rights: The permission to view or access the content of a file or a folder1.
Application files: The files that contain the code, data, or resources of an application or a program2.
Controlled server environment: A server environment that is managed and secured by a set of policies, procedures, and tools3.
Business process owner: The person who is responsible for the design, execution, and performance of a business process.
Read rights to application files in a controlled server environment should be approved by the business process owner. The business process owner is the person who has the authority and accountability for the business process that uses or depends on the application files. The businessprocess owner should approve the read rights to application files in a controlled server environment to:
Ensure that the read rights are aligned with the business needs and objectives
Prevent unauthorized or unnecessary access to the application files
Protect the confidentiality, integrity, and availability of the application files
Comply with the relevant laws and regulations that govern the access to the application files
The other options are not the best choices for approving the read rights to application files in a controlled server environment, because they do not have the same level of authority, responsibility, or knowledge as the business process owner. The database administrator, who is the person who manages and maintains the database systems and data, may have the technical skills and access to grant the read rights to application files, but they may not have the business insight or approval to do so. The chief information officer, who is the person who oversees the IT strategy and operations of the organization, may have the executive power and oversight to approve the read rights to application files, but they may not have the specific or detailed knowledge of the business process or the application files. The systems administrator, who is the person who configures and maintains the server systems and networks, may have the administrative privileges and tools to grant the read rights to application files, but they may not have the business understanding or authorization to do so.
References = Read Permission - an overview | ScienceDirect Topics, What is an Application File? - Definition from Techopedia, What is a Server Environment? - Definition from Techopedia, [Business Process Owner: Definition, Roles, and Responsibilities]
Question # 391
Which of the following provides the BEST assurance of…..
A.
Penetration testing
B.
Service-level monitoring
C.
Service provider ' s control self-assessment (CSA)
D.
Independent assessment report
Full Access
Answer:
D
Question # 392
A risk practitioner ' s BEST guidance to help an organization develop relevant risk scenarios is to ensure the scenarios are:
A.
based on industry trends.
B.
mapped to incident response plans.
C.
related to probable events.
D.
aligned with risk management capabilities.
Full Access
Answer:
C
Explanation:
ï‚· Understanding the Question:
The question asks for the best guidance for developing relevant risk scenarios.
ï‚· Analyzing the Options:
A. Based on industry trends:Important but may not always be directly relevant to the specific organization.
B. Mapped to incident response plans:Useful but secondary to ensuring the scenarios are probable.
C. Related to probable events:Ensures the scenarios are realistic and likely, making them more relevant and actionable.
D. Aligned with risk management capabilities:Important for managing risks but not as critical as ensuring scenarios are probable.
ï‚·
Probable Events:Developing risk scenarios that are based on probable events ensures that the organization is prepared for the most likely risks. This makes risk management efforts more practical and focused on real threats.
Relevance:By focusing on probable events, the scenarios will be more relevant to the organization ' s actual risk environment, making it easier to allocate resources and plan responses effectively.
[References:, CRISC Review Manual, Chapter 2: IT Risk Assessment, emphasizes the importance of identifying and evaluating probable risk events to develop effective risk scenarios​​., , , , , , , , , , , ]
Question # 393
Which of the following will provide the BEST measure of compliance with IT policies?
A.
Evaluate past policy review reports.
B.
Conduct regular independent reviews.
C.
Perform penetration testing.
D.
Test staff on their compliance responsibilities.
Full Access
Answer:
B
Explanation:
Conducting regular independent reviews will provide the best measure of compliance with IT policies, as this ensures that the policies are implemented and followed consistently and effectively across the organization. Independent reviews can also identify any gaps, weaknesses, or violations in the compliance process, and recommend corrective actions or improvements.Independent reviews can be performed by internal or external auditors, regulators, or consultants, depending on the scope and purpose of the review. Evaluating past policy review reports, performing penetration testing, and testing staff on their complianceresponsibilities are not the best measures of compliance with IT policies, although they may be useful or complementary methods. Evaluating past policy review reports can provide some historical and comparative data, but it may not reflect the current or accurate situation of the compliance status. Performing penetration testing can assess the security and vulnerability of the IT systems and networks, but it does not measure the compliance with all the IT policies, such as those related to governance, operations, or quality. Testing staff on their compliance responsibilities can evaluate the awareness and knowledge of the staff, but it does not measure the actual behaviour or performance of the staff in complying with the IT policies. References = Risk and Information Systems Control Study Manual, Chapter 5: Risk and Control Monitoring and Reporting, page 187.
Question # 394
When performing a risk assessment of a new service to support a core business process, which of the following should be done FIRST to ensure continuity of operations?
A.
Define metrics for restoring availability.
B.
Identify conditions that may cause disruptions.
C.
Review incident response procedures.
D.
Evaluate the probability of risk events.
Full Access
Answer:
B
Explanation:
When performing a risk assessment of a new service to support a core business process, the first step is to identify the conditions that may cause disruptions to the service or the process. This involves identifying the sources and causes of potential risk events, such as natural disasters, cyberattacks, human errors, equipment failures, power outages, etc. that may affect the availability, integrity, or confidentiality of the service or the process. By identifying the conditions that may cause disruptions, the risk practitioner can then analyze the probability and impact of the risk events, evaluate the risk exposure, and determine theappropriate risk responses to ensure the continuity of operations. References = CRISC Review Manual, 7th Edition, page 66.
Question # 395
Which of the following elements of a risk register is MOST likely to change as a result of change in management ' s risk appetite?
A.
Key risk indicator (KRI) thresholds
B.
Inherent risk
C.
Risk likelihood and impact
D.
Risk velocity
Full Access
Answer:
A
Explanation:
According to the CRISC Review Manual (Digital Version), key risk indicator (KRI) thresholds are the most likely elements of a risk register to change as a result of change in management’s risk appetite, as they reflect the acceptable levels of risk exposure for the organization. KRIthresholds are the values or ranges that trigger an alert or a response when the actual KRI values deviate from the expected or desired values. KRI thresholds help to:
Monitor and measure the current risk levels and performance of the IT assets and processes
Identify and report any risk issues or incidents that may require attention or action
Evaluate the effectiveness and efficiency of the risk response actions and controls
Align the risk management activities and decisions with the organization’s risk appetite and risk tolerance
If the management’s risk appetite changes, the KRI thresholds may need to be adjusted accordingly to ensure that the risk register reflects the current risk preferences and expectations of the organization.
References = CRISC Review Manual (Digital Version), Chapter 4: IT Risk Monitoring and Reporting, Section 4.1: IT Risk Monitoring, pp. 217-2181
Question # 396
Which of the following would present the GREATEST challenge when assigning accountability for control ownership?
A.
Weak governance structures
B.
Senior management scrutiny
C.
Complex regulatory environment
D.
Unclear reporting relationships
Full Access
Answer:
D
Explanation:
Control ownership is the assignment of roles and responsibilities for the design, implementation, monitoring, and improvement of controls that mitigate risks. Control ownership can help ensure that the controls are effective, efficient, and aligned with the business objectives and risk appetite. Control ownership can also help facilitate the communication, coordination, and accountability among the stakeholders involved in the risk management process. One of the factors that would present the greatest challenge when assigning accountability for control ownership is unclear reporting relationships. Reporting relationships are the formal or informal lines of authority and communication that define who reports to whom, and who is accountable for what. Unclear reporting relationships can create confusion, ambiguity, and conflict among the control owners and other stakeholders, such as the risk owners, the business owners, the auditors, the regulators, etc. Unclear reporting relationships can also hinder the performance evaluation, feedback, and recognition of the control owners, and affect their motivation and commitment. Unclear reporting relationships can also increase the risk of duplication, inconsistency, or gaps in the control activities, and compromise the quality and reliability of the control environment. References = Defining, Assigning and Measuring: Accountability Challenges in 21st Century Governance, CRISC 351-400 topic3, Foundations of Project Management : Week 2.
Question # 397
Which of the following indicates an organization follows IT risk management best practice?
A.
The risk register template uses an industry standard.
B.
The risk register is regularly updated.
C.
All fields in the risk register have been completed.
D.
Controls are listed against risk entries in the register.
Full Access
Answer:
B
Explanation:
 According to the IT Risk Management - Basics and Best Practices article, one of the best practices for IT risk management is to keep the risk register up to date. A risk register is a document that records the identified risks, their causes, impacts, likelihood, responses, andstatus. A risk register is a vital tool for IT risk management, as it helps to track and monitor the risks throughout their lifecycle, and to communicate the risks to the relevant stakeholders. However, a risk register is only useful if it reflects the current situation and environment of the organization. Therefore, the risk register should be regularly updated to capture any changes in the risk profile, such as new risks, resolved risks, modified risks, or escalated risks. Updating the risk register will help to ensure that the risk management process is effective and efficient, and that the risk responses are appropriate and timely. References = IT Risk Management - Basics and Best Practices
Question # 398
An organization has recently updated its disaster recovery plan (DRP). Which of the following would be the GREATEST risk if the new plan is not tested?
A.
External resources may need to be involved.
B.
Data privacy regulations may be violated.
C.
Recovery costs may increase significantly.
D.
Service interruptions may be longer than anticipated.
Full Access
Answer:
D
Explanation:
 Testing a disaster recovery plan is essential to ensure its effectiveness and identify any gaps or weaknesses that might hinder the recovery process. Without testing, the organization may face longer service interruptions than anticipated, which could result in loss of revenue, customer dissatisfaction, reputational damage, and regulatory penalties. Some of the best practices for disaster recovery testing are1:
Test many scenarios
Test regularly
Document everything
Keep everyone updated
Define metrics
Evaluate the results
Test your disaster recovery plan
References = Best Practices For Disaster Recovery Testing | Snyk
Question # 399
Which of the following is a PRIMARY benefit of creating an organizational code of conduct?
A.
Clear expectations for employee behavior
B.
Identification of ethical risk facing the organization
C.
Improvement in workforce productivity
D.
Enhanced integrity of management
Full Access
Answer:
A
Explanation:
The correct answer isAbecause the primary benefit of an organizationalcode of conductis to establishclear expectations for employee behavior. A code of conduct communicates the standards of ethical and professional behavior expected within the organization and provides a common basis for decision-making, accountability, and awareness.
The other options are less appropriate:
B. Identification of ethical risk facing the organizationmay result indirectly, but this is not the primary purpose of a code of conduct.
C. Improvement in workforce productivitycould occur as a secondary effect, but it is not the main benefit.
D. Enhanced integrity of managementmay be supported, but the code of conduct applies across the organization and primarily clarifies expected behavior.
Exact Extracts supporting the answer:
“The most effective way to support adherence to an enterprise ' s code of ethics is by ensuring periodic training evaluation and attestation of employees.â€
“The most significant benefit when stakeholders promote and follow professional ethics is that it increases risk management effectiveness within an enterprise.â€
“The best proactive approach for practicing professional ethics within an enterprise is to provide ethics awareness training.â€
“Developing and practicing ethical behavior within an enterprise contributes the most to building the risk culture.â€
These extracts support that ethics-related governance mechanisms such as a code of conduct are intended to guide and reinforce expected behavior throughout the enterprise. Therefore, the primary benefit isclear expectations for employee behavior.
===========
Question # 400
Which of the following is MOST important when creating a program to reduce ethical risk?
A.
Defining strict policies
B.
Developing an organizational communication plan
C.
Conducting a gap analysis
D.
Obtaining senior management commitment
Full Access
Answer:
D
Question # 401
Which of the following is the MOST important component in a risk treatment plan?
A.
Technical details
B.
Target completion date
C.
Treatment plan ownership
D.
Treatment plan justification
Full Access
Answer:
C
Explanation:
A risk treatment plan is a document that outlines the approach and actions to be taken to address the unacceptable risks identified in the risk assessment process1. A risk treatment plan should include the following components2:
The risk identification number and description
The risk treatment option chosen (e.g., avoid, reduce, share, or accept)
The risk treatment owner, who is responsible for implementing and monitoring the risk treatment
The risk treatment actions, which are the specific tasks or steps to be performed to execute the risk treatment
The risk treatment resources, which are the human, financial, or technical resources required to support the risk treatment
The risk treatment target date, which is the deadline for completing the risk treatment
The risk treatment performance indicators, which are the measures to evaluate the effectiveness and efficiency of the risk treatment
The risk treatment status, which is the current progress or outcome of the risk treatment
Among the four options given, the most important component in a risk treatment plan is the treatment plan ownership. This is because the treatment plan ownership defines theaccountability and authority for the risk treatment, and ensures that the risk treatment actions are carried out as planned and reported as required3. The treatment plan ownership also facilitates the communication and coordination among the stakeholders involved in the risk treatment, and enables the escalation and resolution of any issues or challenges that may arise during the risk treatment process4.
References = Risk Treatment (With Examples), ISO 27001 Risk Assessment & Risk Treatment: The Complete Guide, Risk Management Framework - Treat Risks, Risk Management Plan Components
Question # 402
Which of the following changes would be reflected in an organization ' s risk profile after the failure of a critical patch implementation?
A.
Risk tolerance is decreased.
B.
Residual risk is increased.
C.
Inherent risk is increased.
D.
Risk appetite is decreased
Full Access
Answer:
B
Explanation:
A critical patch is a software update that fixes a security vulnerability or a bug that may affect the performance, functionality, or reliability of a system or a network. A critical patch implementation is a process that applies the software update to the system or network in a timely and effective manner. The failure of a critical patch implementation is a situation where the software update is not applied or not applied correctly, which may expose the system or networkto various threats, such as data theft, data corruption, data leakage, or denial of service. The failure of a critical patch implementation would be reflected in an organization’s risk profile by increasing the residual risk. Residual risk is the risk that remains after the risk response, which means the risk that is not avoided, transferred, or mitigated by the existing controls or measures. The failure of a critical patch implementation would increase the residual risk, as it would reduce the effectiveness or efficiency of the existing controls or measures that are supposed to address the security vulnerability or the bug. The failure of a critical patch implementation would also increase the likelihood or impact of the potential threats, as well as the exposure or consequences of the system or network. The other options are not the correct changes that would be reflected in an organization’s risk profile after the failure of a critical patch implementation, although they may be affected or related. Risk tolerance is the degree of variation from the risk appetite that the organization is not willing to accept. Risk tolerance may be decreased by the failure of a critical patch implementation, as the organization may become more cautious or conservative in accepting the risk, but it is not a direct or immediate change in the risk profile. Inherent risk is the risk that exists in the absence of any controls or measures, which means the risk that is inherent to the system or network or the environment. Inherent risk may be increased by the failure of a critical patch implementation, as the system or network may become more vulnerable or susceptible to the threats, but it is not a change in the risk profile, as the risk profile considers the existing controls or measures. Risk appetite is the amount and type of risk that the organization is willing to accept in pursuit of its objectives. Risk appetite may be decreasedby the failure of a critical patch implementation, as the organization may become less willing orable to accept the risk, but it is not a change in the risk profile, as the risk profile reflects the actual or current risk level, not the desired or expected risk level. References = CRISC Review Manual, pages 32-331 ; CRISC Review Questions, Answers & Explanations Manual, page 972; What is a Critical Patch? - Definition from Techopedia3; What is Residual Risk? - Definition from Techopedia4
Question # 403
Which of the following is MOST helpful in providing an overview of an organization ' s risk management program?
A.
Risk scenarios
B.
Risk management framework
C.
Risk assessment results
D.
Risk management treatment plan
Full Access
Answer:
B
Explanation:
Therisk management frameworkdefines the structure, objectives, roles, processes, and tools used by an organization to manage risk. It provides acomprehensive overviewof how the enterprise governs and implements risk management.
According to theCRISC Review Manualand ISACA’sRisk IT Framework:
“A risk management framework establishes and maintains a common risk language, defines principles and responsibilities, and ensures consistency of approach across the enterprise.â€
Whilerisk scenariosandassessment resultsare components of the program, they focus on specific areas. Theframeworkgives a holistic view—showing policies, processes, oversight mechanisms, governance linkages, and continuous improvement processes.
Hence, theRisk Management Framework(Option B) best provides an overview of the entire program.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Risk Management Framework and Governance Alignment.
Question # 404
During an internal IT audit, an active network account belonging to a former employee was identified. Which of the following is the BEST way to prevent future occurrences?
A.
Conduct a comprehensive review of access management processes.
B.
Declare a security incident and engage the incident response team.
C.
Conduct a comprehensive awareness session for system administrators.
D.
Evaluate system administrators ' technical skills to identify if training is required.
Full Access
Answer:
A
Explanation:
The best way to prevent future occurrences of active network accounts belonging to former employees is to conduct a comprehensive review of access management processes. This review should include verifying that the access rights of all employees are updated regularly, especially when they change roles or leave the organization. The review should also ensure that there are clear policies and procedures for granting, modifying, and revoking access rights, and that these are followed consistently and documented properly. The review should also identify and address any gaps or weaknesses in the access management processes that could lead to unauthorized orinappropriate access. By conducting a comprehensive review of access management processes, the organization can improve its security posture and reduce the risk of data breaches or misuse of resources. References = IT audit: The ultimate guide [with checklist] | Zapier, IT auditing and controls – planning the IT audit [updated 2021]
Question # 405
If preventive controls cannot be Implemented due to technology limitations, which of the following should be done FIRST to reduce risk7
A.
Evaluate alternative controls.
B.
Redefine the business process to reduce the risk.
C.
Develop a plan to upgrade technology.
D.
Define a process for monitoring risk.
Full Access
Answer:
A
Explanation:
If preventive controls cannot be implemented due to technology limitations, the first step to reduce risk is to evaluate alternative controls. Alternative controls are those that can achieve thesame or similar objectives as the original preventive controls, but using different methods or technologies. For example, if a firewall cannot be installed due to hardware compatibility issues, an alternative control could be a network segmentation or a proxy server. Evaluating alternative controls requires assessing their feasibility, effectiveness, efficiency, and cost-benefit. Redefining the business process, developing a plan to upgrade technology, and defining a process for monitoring risk are also possible actions to reduce risk, but they are not the first step, and they may not be feasible or desirable in some situations. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.1, page 4-23.
Question # 406
Which of the following BEST helps to identify significant events that could impact an organization?
Vulnerability analysis
A.
Control analysis
B.
Scenario analysis
C.
Heat map analysis
Full Access
Answer:
B
Explanation:
Â
Question # 407
The MOST important consideration when selecting a control to mitigate an identified risk is whether:
A.
the cost of control exceeds the mitigation value
B.
there are sufficient internal resources to implement the control
C.
the mitigation measures create compounding effects
D.
the control eliminates the risk
Full Access
Answer:
A
Explanation:
The most important consideration when selecting a control to mitigate an identified risk is whether the cost of control exceeds the mitigation value, because this determines the cost-benefit ratio of the control. A control should not be implemented if the cost of implementing and maintaining it is higher than the expected benefit of reducing the risk exposure. The other options are not the most important considerations, although they may also influence the control selection process. The availability of internal resources, the potential compounding effects, and the possibility of eliminating the risk are secondary factors that depend on the cost and value of the control. References = CRISC: Certified in Risk & Information Systems Control Sample Questions
Question # 408
Which of the following is the ULTIMATE objective of utilizing key control indicators (KCIs) in the risk management process?
A.
To provide a basis for determining the criticality of risk mitigation controls
B.
To provide early warning signs of a potential change in risk level
C.
To provide benchmarks for assessing control design effectiveness against industry peers
D.
To provide insight into the effectiveness of the intemnal control environment
Full Access
Answer:
D
Explanation:
Key control indicators (KCIs) are metrics that measure the performance of a control in reducing the causes, consequences, or likelihood of a risk. They help to evaluate the adequacy and efficiency of the internal control environment, which is the set of policies, procedures, and practices that support the achievement of organizational objectives and the management of risks. By monitoring KCIs, organizations can identify and address any gaps or weaknesses in their internal controls and ensure that they are operating as intended.
References
•ISACA CRISC Review Manual, 7th Edition, Domain 3: Risk Response, Section 3.2.2: Control Design and Implementation
•KRI Framework for Operational Risk Management | Workiva
•What is the difference between key risk indicators and key control indicators?
Question # 409
Which of the following BEST helps to balance the costs and benefits of managing IT risk?
A.
Prioritizing risk responses
B.
Evaluating risk based on frequency and probability
C.
Considering risk factors that can be quantified
D.
Managing the risk by using controls
Full Access
Answer:
A
Explanation:
Prioritizing risk responses helps to balance the costs and benefits of managing IT risk by ensuring that the most significant risks are addressed first and that the resources allocated to risk management are used efficiently and effectively. Evaluating risk based on frequency and probability is a part of risk analysis, not risk response. Considering risk factors that can be quantified is also a part of risk analysis, and it does not necessarily capture all the relevant aspects of risk. Managing the risk by using controls is a possible risk response, but it does not guarantee that the costs and benefits of risk management are balanced, as some controls may be too expensive or ineffective for the level of risk they mitigate. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 145.
Question # 410
An organization has established a contract with a vendor that includes penalties for loss of availability. Which risk treatment has been adopted by the organization?
A.
Acceptance
B.
Avoidance
C.
Transfer
D.
Reduction
Full Access
Answer:
C
Explanation:
The organization has adopted the risk treatment of transfer, which means that it has shifted some or all of the potential negative consequences of a risk event to another party, such as a vendor, an insurer, or a partner. By including penalties for loss of availability in the contract, the organization has transferred the financial impact of a service disruption to the vendor, who will be liable for compensating the organization for the loss. Transfer does not eliminate the risk, but it reduces the organization’s exposure to the risk.
[References:, •ISACA, Risk and Information Systems Control Review Manual, 7th Edition, 2020, p. 2111, •ISACA, A Nuanced View of Risk Response2, , , , , , , , , , ]
Question # 411
What is the GREATEST concern with maintaining decentralized risk registers instead of a consolidated risk register?
A.
Aggregated risk may exceed the enterprise ' s risk appetite and tolerance.
B.
Duplicate resources may be used to manage risk registers.
C.
Standardization of risk management practices may be difficult to enforce.
D.
Risk analysis may be inconsistent due to non-uniform impact and likelihood scales.
Full Access
Answer:
A
Explanation:
A risk register is a tool that records and tracks the identified risks, their causes, impacts, likelihood, responses, and owners. A decentralized risk register is maintained by each business unit or function, while a consolidated risk register is maintained at the enterprise level. The greatest concern with maintainingdecentralized risk registers instead of a consolidated risk register is that the aggregated risk may exceed the enterprise’s risk appetite and tolerance. Risk appetite is the amount and type of risk that an enterprise is willing to accept in pursuit of its objectives, while risk tolerance is the acceptable level of variation around the objectives. If the risk registers are not consolidated, the enterprise may not have a holistic view of its risk profile and may not be able to prioritize and allocate resources effectively. The other options are also concerns, but they are not as significant as the potential misalignment between the aggregated risk and the enterprise’s risk appetite and tolerance. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.2.2, pp. 21-22.
Question # 412
When documenting a risk response, which of the following provides the STRONGEST evidence to support the decision?
A.
Verbal majority acceptance of risk by committee
B.
List of compensating controls
C.
IT audit follow-up responses
D.
A memo indicating risk acceptance
Full Access
Answer:
D
Explanation:
The strongest evidence to support a risk response decision is a memo indicating risk acceptance. A memo is a formal and written document that can clearly communicate the rationale, criteria, and approval of the risk acceptance decision. Verbal majority acceptance of risk by committee, list of compensating controls, and IT audit follow-up responses are weaker evidence, as they may not be documented, verified, or aligned with the risk response decision. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 11; CRISC Review Manual, 6th Edition, page 144.
Question # 413
Which of the following would be the BEST way to help ensure the effectiveness of a data loss prevention (DLP) control that has been implemented to prevent the loss of credit card data?
A.
Testing the transmission of credit card numbers
B.
Reviewing logs for unauthorized data transfers
C.
Configuring the DLP control to block credit card numbers
D.
Testing the DLP rule change control process
Full Access
Answer:
A
Explanation:
A data loss prevention (DLP) control is a technology that tries to detect and stop sensitive data breaches, or data leakage incidents, in an organization. A DLP control is used to prevent sensitive data, such as credit card numbers, from being disclosed to an unauthorized person, whether it is deliberate or accidental1. The best way to help ensure the effectiveness of a DLP control that has been implemented to prevent the loss of credit card data is to test the transmission of credit card numbers. This is a technique to verify that the DLP control can successfully identify and block the credit card data when it is sent or received through various channels, such as email, messaging, or file transfers. Testing the transmission of credit card numbers can help to evaluate the accuracy and reliability of the DLP control, as well as to identify and correct any false positives or false negatives. The other options are not the best ways to help ensure the effectiveness of a DLP control that has been implemented to prevent the loss of credit card data, although they may be helpful and complementary. Reviewing logs forunauthorized data transfers is a technique to monitor and analyze the DLP control activities and incidents, such as who, what, when, where, and how the data was transferred. However, reviewing logs is a reactive and passive approach, while testing the transmission is a proactive and active approach. Configuring the DLP control to block credit card numbers is a technique to set up the DLP control rules and policies, such as defining the data patterns, the detection methods, and the response actions. However, configuring the DLP control is a prerequisite and a preparation step, while testing the transmission is a validation and a verification step. Testing the DLP rule change control process is a technique to ensure that the DLP control rules and policies are updated and maintained in a controlled and coordinated manner, such as obtaining approval, documenting the changes, testing the changes, and communicating the changes. However, testing the DLP rule change control process is a quality and governance step, while testing the transmission is a performance and functionality step. References = What is Data Loss Prevention (DLP)? | Digital Guardian1; CRISC Review Manual, pages 164-1652; CRISC Review Questions, Answers & Explanations Manual, page 833
Question # 414
Continuous monitoring of key risk indicators (KRIs) will:
A.
ensure that risk will not exceed the defined risk appetite of the organization.
B.
provide an early warning so that proactive action can be taken.
C.
provide a snapshot of the risk profile.
D.
ensure that risk tolerance and risk appetite are aligned.
Full Access
Answer:
B
Explanation:
Continuous monitoring of key risk indicators (KRIs) will provide an early warning so that proactive action can be taken, because it helps to detect and measure the changes or trends in the risk level or performance, and to alert the risk owners and stakeholders when the risk exceeds the predefined thresholds or targets. A KRI is a metric or indicator that helps to monitor and evaluate the likelihood or impact of a risk, or the effectiveness or efficiency of a control. A KRI can be quantitative or qualitative, and can be derived from internal or external sources. Continuous monitoring is a process of collecting and analyzing data on a regular or real-time basis, to provide timely and relevant information for decision making or action taking. Continuous monitoring of KRIs will provide an early warning, as it helps to identify and address the risk issues or incidents before they escalate or cause significant damage or disruption. Ensuring that risk will not exceed the defined risk appetite of the organization, providing a snapshot of the risk profile, and ensuring that risk tolerance and risk appetite are aligned are all possible outcomes of continuous monitoring of KRIs, but they are not the best answer, as they do not reflect the main purpose and benefit of continuous monitoring of KRIs, which is to provide an early warning. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.3.2, page 97
Question # 415
An IT project risk was identified during a monthly steering committee meeting. Which of the following roles is BEST positioned to approve the risk mitigation response?
A.
Product owner
B.
IT manager
C.
Project sponsor
D.
Project coordinator
Full Access
Answer:
C
Explanation:
The project sponsor holds the ultimate accountability for the project ' s success and is typically responsible for approving significant decisions, including risk mitigation responses. Their role involves ensuring that the project aligns with business objectives and that risks are managed appropriately to achieve desired outcomes.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 1: Governance, Section: Roles and Responsibilities., , , , , , , ]
Question # 416
A risk practitioner has learned that an effort to implement a risk mitigation action plan has stalled due to lack of funding. The risk practitioner should report that the associated risk has been:
A.
mitigated
B.
accepted
C.
avoided
D.
deferred
Full Access
Answer:
D
Explanation:
The risk practitioner should report that the associated risk has been deferred, as this means that the risk response has been postponed or delayed due to lack of resources or other constraints. Deferring a risk response implies that the risk owner acknowledges the risk and intends to implement the risk mitigation action plan at a later stage, when the resources or conditions are available. The other options are not correct, as they do not reflect the actual status of the risk response. Mitigating a risk means that the risk response has been implemented and the risk level has been reduced. Accepting a risk means that the risk response has been rejected or waived, and the risk level has been accepted as it is. Avoiding a risk means that the risk response has beenimplemented and the risk level has been eliminated or transferred. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 146.
Question # 417
An organizational policy requires critical security patches to be deployed in production within three weeks of patch availability. Which of the following is the BEST metric to verify adherence to the policy?
A.
Maximum time gap between patch availability and deployment
B.
Percentage of critical patches deployed within three weeks
C.
Minimum time gap between patch availability and deployment
D.
Number of critical patches deployed within three weeks
Full Access
Answer:
A
Explanation:
The best metric to verify adherence to the policy that requires critical security patches to be deployed in production within three weeks of patch availability is the maximum time gap between patch availability and deployment, as it measures the longest duration that the organization takes to apply the patches, and ensures that it does not exceed the policy limit. The other options are not the best metrics, as they may not reflect the actual or optimal compliance with the policy, or may not be relevant or measurable for the policy, respectively. References = CRISC Review Manual, 7th Edition, page 110.
Question # 418
The BEST way for management to validate whether risk response activities have been completed is to review:
A.
the risk register change log.
B.
evidence of risk acceptance.
C.
control effectiveness test results.
D.
control design documentation.
Full Access
Answer:
C
Explanation:
Reviewing the risk register change log is the best way for management to validate whether risk response activities have been completed, because it helps to track and monitor the changes and updates that have been made to the risk register, and to verify that the risk response activities have been implemented and closed. A risk register is a document that captures, identifies, assesses and tracks risk as part of the risk management process4. A risk register change log is a record that documents the date, description, and reason for each change or update that is made to the risk register. A risk response activity is an action or task that is performed to implement the chosen risk response strategy for a specific risk, such as avoid, transfer, mitigate, or accept. Reviewing the risk register change log is the best way, as it helps to ensure that the risk register is accurate and current, and that the risk response activities have been completed and reported. Reviewing evidence of risk acceptance, control effectiveness test results, and control design documentation are all possible ways to validate whether risk response activities have been completed, but they are not the best way, as they may not cover all the risk response activities, and they may not reflect the changes or updates in the risk register. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.1, page 101
Question # 419
Which of the following BEST indicates that an organizations risk management program is effective?
A.
Fewer security incidents have been reported.
B.
The number of audit findings has decreased.
C.
Residual risk is reduced.
D.
inherent risk Is unchanged.
Full Access
Answer:
C
Explanation:
Residual risk is the risk that remains after the implementation of risk responses. An effective risk management program should aim to reduce the residual risk to a level that is acceptable by the enterprise, in alignment with its risk appetite and tolerance. The reduction of residual risk indicates that the risk responses are appropriate and effective, and that the enterprise is achieving its objectives while managing its risks. The other options are not necessarily indicative of an effective risk management program, as they may depend on other factors, such as the reporting culture, the audit scope and methodology, and the nature and source of the inherent risk. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.3.1, pp. 24-25.
Question # 420
Which of the following is the BEST way to validate privileged access to database accounts?
A.
Regular reviews of privileged access
B.
Confirmation from users with privileged access
C.
Management approval of access requests
D.
Confirmation from the database administrator (DBA)
Full Access
Answer:
A
Explanation:
Regular reviewshelp detect inappropriate, outdated, or excessive access rights. This is a fundamental part of access control governance and supports the principle of least privilege.
[Reference:CRISC Manual – Domain 1, Slide 230-232, , , , ]
Question # 421
A.
Ensure compliance with local legislation because it has a higher priority.
B.
Conduct a risk assessment and develop mitigation options.
C.
Terminate the current cloud contract and migrate to a local cloud provider.
D.
Accept the risk because foreign legislation does not apply to the organization.
Full Access
Answer:
B
Explanation:
When regulatory conflicts arise, the best practice is to conduct a comprehensive risk assessment to understand the impact and develop appropriate mitigation strategies. Immediate termination may be premature without understanding options, and accepting risk without assessment may expose the organization to legal or compliance issues. Prioritizing compliance requires understanding the full scope of risks and controls necessaryã€5:35, 5:48†CRISC_SentenceinNOTE30.pptx】.
Question # 422
An employee lost a personal mobile device that may contain sensitive corporate information. What should be the risk practitioner ' s recommendation?
A.
Conduct a risk analysis.
B.
Initiate a remote data wipe.
C.
Invoke the incident response plan
D.
Disable the user account.
Full Access
Answer:
B
Explanation:
The best recommendation for a risk practitioner when an employee lost a personal mobile device that may contain sensitive corporate information is to initiate a remote data wipe. A remote data wipe is a process of erasing the data stored on a device remotely, using a command sent over anetwork or a wireless connection. A remote data wipe can help to prevent the unauthorized access, use, disclosure, or theft of the sensitive corporate information, and to minimize the potential impact of the loss on the enterprise’s reputation, operations, and compliance. A remote data wipe can also help to comply with the data breach notification laws and regulations, and to reduce the legal liability and penalties. Conducting a risk analysis, invoking the incident response plan, and disabling the user account are not as immediate and effective as initiating a remote data wipe, as they do not address the primary risk of data exposure and loss. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 217.
Question # 423
It was discovered that a service provider ' s administrator was accessing sensitive information without the approval of the customer in an Infrastructure as a Service (laaS) model. Which of the following would BEST protect against a future recurrence?
A.
Data encryption
B.
Intrusion prevention system (IPS)
C.
Two-factor authentication
D.
Contractual requirements
Full Access
Answer:
D
Explanation:
The best option to protect against a future recurrence of unauthorized access by a service provider’s administrator is D. Contractual requirements. Data encryption, intrusion prevention system, and two-factor authentication are all technical measures that can enhance the security of the data stored in the Infrastructure as a Service (IaaS) model, but they do not prevent the service provider’s administrator from accessing the data if they have the necessary credentials, keys, or permissions. Contractual requirements, on the other hand, are legal obligations that bind the service provider to respect the customer’s privacy and confidentiality, and to limit the access tothe data to only authorized and necessary personnel. Contractual requirements can also specify the penalties or remedies for any breach of contract, which can deter the service provider’s administrator from violating the terms of the agreement. Therefore, contractual requirements are the most effective way to protect against a future recurrence of unauthorized access by a service provider’s administrator12
1: What is Data Encryption? | Forcepoint 2: The elements of a contract: understanding contract requirements - Juro
Question # 424
Which of the following is MOST helpful in identifying new risk exposures due to changes in the business environment?
A.
Standard operating procedures
B.
SWOT analysis
C.
Industry benchmarking
D.
Control gap analysis
Full Access
Answer:
B
Explanation:
New risk exposures due to changes in the business environment are the possibilities and impacts of new or emerging threats or opportunities that may affect the organization’s objectives, performance, or value creation, as a result of changes in the internal or external factors that influence the organization’s operations, such as technology, competition, regulation, or customer behavior12.
The most helpful tool in identifying new risk exposures due to changes in the business environment is a SWOT analysis, which is a technique that involves identifying and analyzing the strengths, weaknesses, opportunities, and threats (SWOT) that are relevant to the organization’s situation, goals, and capabilities34.
A SWOT analysis is the most helpful tool because it helps the organization to scan and assess the business environment, and to identify and prioritize the new or emerging risk exposures that may arise from the changes in the environment34.
A SWOT analysis is also the most helpful tool because it helps the organization to align and adapt its strategy and actions to the changes in the environment, and to leverage its strengths and opportunities, and mitigate its weaknesses and threats34.
The other options are not the most helpful tools, but rather possible sources or inputs that may be used in a SWOT analysis. For example:
Standard operating procedures are documents that describe the routine tasks and processes that are performed by the organization, and the policies and standards that govern them56. However, these documents are not the most helpful tools because they may not reflect or capture the changes in the business environment, and they may need to be revised or updated to address the new or emerging risk exposures56.
Industry benchmarking is a technique that involves comparing and contrasting the performance and practices of the organization with those of the similar or leadingorganizations in the same or related industry, and identifying the gaps or opportunities for improvement78. However, this technique is not the most helpful tool because it may not provide a comprehensive or holistic view of the business environment, and it may not align with the organization’s specific situation, goals, or capabilities78.
Control gap analysis is a technique that involves assessing and evaluating the adequacy and effectiveness of the controls that are designed and implemented to mitigate the risks, and identifying and addressing the areas or aspects that need to be improved or added . However, this technique is not the most helpful tool because it is reactive rather than proactive, and it may not identify or anticipate the new or emerging risk exposures that may result from the changes in the business environment . References =
1: Risk IT Framework, ISACA, 2009
2: IT Risk Management Framework, University of Toronto, 2017
3: SWOT Analysis - ISACA1
4: SWOT Analysis: What It Is and When to Use It2
5: Standard Operating Procedure - Wikipedia3
6: How to Write Effective Standard Operating Procedures (SOP)4
7: Benchmarking - Wikipedia5
8: Benchmarking: Definition, Types, Process, Advantages & Examples6
Control Gap Analysis - ISACA7
Control Gap Analysis: A Step-by-Step Guide8
Question # 425
An organization has an internal control that requires all access for employees be removed within 15 days of their termination date. Which of the following should the risk practitioner use to monitor
adherence to the 15-day threshold?
A.
Operation level agreement (OLA)
B.
Service level agreement (SLA)
C.
Key performance indicator (KPI)
D.
Key risk indicator (KRI)
Full Access
Answer:
C
Explanation:
A key performance indicator (KPI) is a metric that measures the achievement of a specific goal or objective. A KPI for the internal control that requires all access for employees be removed within 15 days of their termination date could be the percentage of employees whose access was removed within the specified time frame. This KPI would help the risk practitioner to monitor the compliance and effectiveness of the control and identify any deviations or issues.
References
•Key Performance Indicators (KPIs) - ISACA
•How to Improve Risk Awareness in the Workplace [+ Template] - AlertMedia
•[SITXWHS
Question # 426
Which of the following should be a risk practitioner ' s GREATEST concern upon learning of failures in a data migration activity?
A.
Availability of test data
B.
Integrity of data
C.
Cost overruns
D.
System performance
Full Access
Answer:
B
Explanation:
The integrity of data should be the greatest concern for a risk practitioner upon learning of failures in a data migration activity, because it affects the accuracy, completeness, and consistency of the data that are transferred from one system or format to another. Data integrity is a property of data that ensures that the data are valid, reliable, and trustworthy, and that they have not been altered or corrupted by unauthorized or accidental means. Data migration is a process of moving or copying data from one system or format to another, usually as part of a system upgrade, consolidation, or transformation. Data migration can pose risks to the integrity of data, such as data loss, duplication, inconsistency, or corruption, due to factors such as incompatible formats, human errors, technical glitches, or malicious attacks. Therefore, the integrity of data should be the greatest concern, as it impacts the quality and usability of the data, and the performance and functionality of the system. The availability of test data, the cost overruns, and the system performance are all possible concerns for a risk practitioner, but they are not the greatest concern, as they do not directly affect the integrity of data. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.3.2, page 158
Question # 427
Which of the following should be considered FIRST when creating a comprehensive IT risk register?
A.
Risk management budget
B.
Risk mitigation policies
C.
Risk appetite
D.
Risk analysis techniques
Full Access
Answer:
C
Explanation:
 Risk appetite is the most important factor to consider first when creating a comprehensive IT risk register, as it defines the amount and type of risk that the organization is willing to accept in pursuit of its objectives, and guides the identification, assessment, response, and monitoring of the IT risks. The other options are not the most important factors, as they are more related to theresources, actions, or methods of the IT risk management, respectively, rather than the strategy or direction of the IT risk management. References = CRISC Review Manual, 7th Edition, page 109.
Question # 428
The BEST way to determine the likelihood of a system availability risk scenario is by assessing the:
A.
availability of fault tolerant software.
B.
strategic plan for business growth.
C.
vulnerability scan results of critical systems.
D.
redundancy of technical infrastructure.
Full Access
Answer:
C
Explanation:
A system availability risk scenario is a situation where a system or a service is not accessible or functional due to a failure or an attack. The likelihood of such a scenario depends on the vulnerabilities or weaknesses that exist in the system or the service, and the threats or attackers that could exploit them. Therefore, by scanning the critical systems or services for vulnerabilitiesand analyzing the results, one can estimate the probability or frequency of a system availability risk scenario1.
A vulnerability scan is a process of identifying and evaluating the potential security risks in a system or a service. A vulnerability scan report provides a list of vulnerabilities that have been detected, categorized by their severity levels, and accompanied by remediation recommendations. By reviewing the report, one can understand the current security posture of the system or the service, and the actions that need to be taken to address the vulnerabilities2.
The other options are not the best ways to determine the likelihood of a system availability risk scenario, but rather some of the factors or outcomes of it. Availability of fault tolerant software is a factor that can reduce the likelihood of a system availability risk scenario, as it means that the software can continue to operate without interruption even if some of its components fail. Fault tolerant software can achieve this by using backup or redundant components, or by implementing error detection and correction mechanisms3. Strategic plan for business growth is an outcome of a system availability risk scenario, as it can affect the organization’s objectives and strategies. A system availability risk scenario can have negative impacts on the organization’s performance, reputation, customer satisfaction, and competitive advantage, and thus hamper its growth potential4. Redundancy of technical infrastructure is a factor that can reduce the likelihood of a system availability risk scenario, as it means that the infrastructure has duplicate or alternativedevices or paths that can take over in case of a failure or an attack. Redundancy of technical infrastructure can ensure network availability and prevent data loss5. References =
Describe the risk scenarios | NZ Digital government
How to Read a Vulnerability Scan Report | Evolve Security
Learn about Fault Tolerant Servers | What is Fault Tolerance?-Stratus
The Importance of Redundancies in Your Infrastructure - INAP
What is Redundancy? - Your IT Department
[CRISC Review Manual, 7th Edition]
Question # 429
Which of the following is the GREATEST risk associated with the use of data analytics?
A.
Distributed data sources
B.
Manual data extraction
C.
Incorrect data selection
D.
Excessive data volume
Full Access
Answer:
C
Explanation:
According to the CRISC Review Manual1, data selection is the process of choosing the appropriate data sources and variables for data analysis. Data selection is the most critical step in data analytics, as it determines the quality and validity of the results and insights derived from the analysis. Incorrect data selection is the greatest risk associated with the use of data analytics, as it can lead to inaccurate, incomplete, irrelevant, or biased outcomes that can adversely affectthe decision making and performance of the organization. Incorrect data selection can also cause legal, regulatory, ethical, or reputational issues for the organization, if the data used for analysis is not authorized, reliable, or compliant. References = CRISC Review Manual1, page 255.
Question # 430
Which of the following would be a risk practitioner’s GREATEST concern related to the monitoring of key risk indicators (KRIs)?
A.
Logs are retained for longer than required.
B.
Logs are reviewed annually.
C.
Logs are stored in a multi-tenant cloud environment.
D.
Logs are modified before analysis is conducted.
Full Access
Answer:
D
Explanation:
Modifying logs before analysis compromises the integrity and reliability of monitoring processes. This action creates a risk of inaccurate data feeding into key risk indicators, which undermines the effectiveness of monitoring and decision-making. Maintaining log integrity is a foundational practice inRisk Monitoring and Reporting.
Question # 431
Which of the following is the PRIMARY reason to obtain independent reviews of risk assessment and response mechanisms?
A.
To ensure risk thresholds are properly defined
B.
To minimize the subjectivity of risk assessment results
C.
To correct errors in the risk assessment process
D.
To validate impact and probability ratings
Full Access
Answer:
B
Explanation:
The correct answer isBbecause the primary reason for obtainingindependent reviewsof risk assessment and response mechanisms is tominimize subjectivityand improve objectivity, consistency, and credibility in the assessment results. Independent reviewers help reduce bias and provide a more reliable evaluation of how risk is identified, analyzed, and responded to.
The other options are narrower or secondary outcomes:
A. To ensure risk thresholds are properly definedmay be part of a review, but it is not the primary reason.
C. To correct errors in the risk assessment processis beneficial, but independent review is broader than error correction.
D. To validate impact and probability ratingsis part of review activity, but the larger reason is reducing subjectivity and bias.
Exact Extracts supporting the answer:
“The most important reason for reviewing the risk management process by independent risk auditors and assessors is to ensure that the risk factors and risk profile are well-defined.â€
“An independent risk management professional should assess whether the risk profile and risk factors are properly defined during the risk management process review.â€
“Using representative and significant historical data addresses the potential for bias in developing risk scenarios.â€
“A peer review is BEST suited for reviewing IT risk analysis results before sending them to management.â€
“Assessments by an objective and independent third party are most relied upon by a regulatory body.â€
These extracts support that independence improves objectivity and reduces bias in risk assessment and response review. Therefore, the primary reason is tominimize the subjectivity of risk assessment results.
Question # 432
An organization is increasingly concerned about loss of sensitive data and asks the risk practitioner to assess the current risk level. Which of the following should the risk practitioner do FIRST?
A.
Review assignments of data ownership for key assets.
B.
Identify staff who have access to the organization’s sensitive data.
C.
Identify recent and historical incidents involving data loss.
D.
Review the organization ' s data inventory.
Full Access
Answer:
A
Explanation:
Review Assignments of Data Ownership for Key Assets:
Data Ownership: Ensuring that data ownership is clearly assigned helps establish accountability for data protection. Data owners are responsible for the classification, management, and protection of data.
Baseline Understanding: Reviewing data ownership assignments provides a baseline understanding of who is responsible for sensitive data and ensures that the responsibilities are clearly defined and understood.
Compliance and Control: Proper data ownership ensures that controls are in place and that there is compliance with data protection policies and regulations.
Comparison with Other Options:
Identify Staff Who Have Access to Sensitive Data: This is important but should follow the establishment of clear data ownership to ensure that access controls are appropriately applied.
Identify Recent and Historical Incidents Involving Data Loss: Reviewing incidents helps understand past issues but does not address current data ownership and accountability.
Review the Organization ' s Data Inventory: While important, a data inventory review is part of understanding data ownership and control but should not be the first step.
Best Practices:
Clear Documentation: Ensure that data ownership is clearly documented and communicated across the organization.
Regular Reviews: Conduct regular reviews of data ownership assignments to ensure they remain accurate and up-to-date.
Training and Awareness: Provide training to data owners on their roles and responsibilities regarding data protection and risk management.
[References:, CRISC Review Manual: Highlights the importance of data ownership in managing and protecting sensitive information within an organization., ISACA Guidelines: Recommend establishing clear data ownership and accountability as a foundational step in effective data risk management., , , , , , , , , , , ]
Question # 433
An organization uses one centralized single sign-on (SSO) control to cover many applications. Which of the following is the BEST course of action when a new application is added to the environment after testing of the SSO control has been completed?
A.
Initiate a retest of the full control
B.
Retest the control using the new application as the only sample.
C.
Review the corresponding change control documentation
D.
Re-evaluate the control during (he next assessment
Full Access
Answer:
A
Explanation:
The best course of action when a new application is added to the environment after testing of the SSO control has been completed is to initiate a retest of the full control, as it may reveal any new issues or gaps that the new application may introduce to the SSO control, and ensure that the control remains effective and adequate. Retesting the control using the new application as the only sample, reviewing the corresponding change control documentation, and re-evaluating the control during the next assessment are not the best courses of action, as they may not provide sufficient assurance, evidence, or timeliness of the control testing, respectively. References = CRISC Review Manual, 7th Edition, page 154.
Question # 434
An organization that has been the subject of multiple social engineering attacks is developing a risk awareness program. The PRIMARY goal of this program should be to:
A.
reduce the risk to an acceptable level.
B.
communicate the consequences for violations.
C.
implement industry best practices.
D.
reduce the organization ' s risk appetite
Full Access
Answer:
A
Explanation:
According to the CRISC Review Manual (Digital Version), the primary goal of a risk awareness program is to reduce the risk to an acceptable level by increasing the knowledge and understanding of the risk among the stakeholders. A risk awareness program should:
Educate the stakeholders about the sources, types and impacts of IT-related risks
Explain the roles and responsibilities of the stakeholders in the risk management process
Promote a risk-aware culture that supports the risk appetite and risk tolerance of the organization
Provide guidance and tools for identifying, assessing, responding and monitoring IT-related risks
Encourage the reporting and escalation of risk issues and incidents
Reinforce the benefits and value of effective risk management
References = CRISC Review Manual (Digital Version), Chapter 4: IT Risk Monitoring and Reporting, Section 4.2: IT Risk Reporting, pp. 224-2251
Question # 435
Which of the following is a risk practitioner ' s BEST recommendation to help reduce IT risk associated with scheduling overruns when starting a new application development project?
A.
Implement a tool to track the development team ' s deliverables.
B.
Review the software development life cycle.
C.
Involve the development team in planning.
D.
Assign more developers to the project team.
Full Access
Answer:
C
Explanation:
Involve the development team in planning is the best recommendation to help reduce IT risk associated with scheduling overruns when starting a new application development project. This is because involving the development team in planning can help ensure that the project scope, requirements, resources, and timeline are realistic, feasible, and agreed upon by all stakeholders. It can also help improve the communication, collaboration, and commitment of the development team, as well as identify and mitigate potential risks and issues early in the project life cycle. According to the CRISC Review Manual 2022, one of the key risk identification techniques for IT projects is to involve the project team and other relevant parties in the risk assessment process1. According to the CRISC Review Questions, Answers & Explanations Manual 2022, involving the development team in planning is the correct answer to this question2.
Implementing a tool to track the development team’s deliverables, reviewing the software development life cycle, and assigning more developers to the project team are not the best recommendations to help reduce IT risk associated with scheduling overruns. These are possible actions that can be taken during or after the planning phase, but they do not address the root cause of the risk, which is the lack of involvement of the development team in planning. Implementing a tool to track the development team’s deliverables can help monitor the project progress and performance, but it does not guarantee that the deliverables are aligned with the project objectives and expectations. Reviewing the software development life cycle can help ensure that the project follows a structured and standardized process, but it does not account for the specific needs and challenges of the project. Assigning more developers to the project team can help increase the project capacity and productivity, but it can also introduce new risks such as coordination, communication, and quality issues.
Question # 436
The PRIMARY advantage of involving end users in continuity planning is that they:
A.
have a better understanding of specific business needs
B.
can balance the overall technical and business concerns
C.
can see the overall impact to the business
D.
are more objective than information security management.
Full Access
Answer:
A
Explanation:
 Continuity planning is the process of developing strategies and plans to ensure the continuity of critical business functions and processes in the event of a disruption or disaster. Continuity planning involves identifying the risks, impacts, and recovery options for various scenarios, as well as testing and updating the plans regularly. The primary advantage of involving end users in continuity planning is that they have a better understanding of specific business needs, such as the operational requirements, the customer expectations, and the dependencies and interdependencies of the business processes. End users can provide valuable input and feedback on the continuity plans, as well as participate in the testing and validation of the plans. End users can also help to ensure the alignment of the continuity plans with the business objectives and priorities, as well as the compliance with the relevant standards and regulations. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.4.1, p. 204-205
Question # 437
Which of the following is a specific concern related to machine learning algorithms?
A.
Low software quality
B.
Lack of access controls
C.
Data breaches
D.
Data bias
Full Access
Answer:
D
Explanation:
Data biasin machine learning algorithms can lead to inaccurate predictions or decisions, as biases in training data are amplified in the output. Addressing bias is essential for ethical and reliable algorithm performance.
Question # 438
An organization ' s recovery team is attempting to recover critical data backups following a major flood in its data center. However, key team members do not know exactly what steps should be taken to address this crisis. Which of the following is the MOST likely cause of this situation?
A.
Failure to test the disaster recovery plan (DRP)
B.
Lack of well-documented business impact analysis (BIA)
C.
Lack of annual updates to the disaster recovery plan (DRP)
D.
Significant changes in management personnel
Full Access
Answer:
A
Explanation:
 The most likely cause of the situation where the recovery team does not know what steps to take to recover critical data backups following a major flood is the failure to test the disaster recovery plan (DRP). A DRP is a document that describes the procedures and resources needed to restore the normal operations of an organization after a disaster. Testing the DRP is essential to ensure that the plan is feasible, effective, and up-to-date. Testing the DRP also helps to train the recovery team members, identify and resolve any issues or gaps, and improve the confidence and readiness of the organization. The lack of a well-documented business impact analysis (BIA), the lack of annual updates to the DRP, and the significant changes in management personnel are also possible factors that could affect the recovery process, butthey are not as likely or as critical as the failure to test the DRP. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.3.1, page 5-19.
Question # 439
Which of the following is the BEST way for an organization to enable risk treatment decisions?
A.
Allocate sufficient funds for risk remediation.
B.
Promote risk and security awareness.
C.
Establish clear accountability for risk.
D.
Develop comprehensive policies and standards.
Full Access
Answer:
C
Explanation:
 Establishing clear accountability for risk is the best way for an organization to enable risk treatment decisions, as it ensures that the risk owners and stakeholders have the authority and responsibility to manage and mitigate the risks that they are assigned to. Establishing clear accountability for risk also facilitates communication and collaboration among the risk owners and stakeholders, and enables them to monitor and report the risk status and performance. Establishing clear accountability for risk also supports the risk governance and culture of the organization, and aligns the risk management process with the organization’s strategy and objectives. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, Question 250. CRISC: Certified in Risk & Information Systems Control Sample Questions, Question 250. CRISC Sample Questions 2024, Question 250. CRISC by Isaca Actual Free Exam Q & As, Question 9.
Question # 440
Which of the following is the GREATEST risk associated with inappropriate classification of data?
A.
Inaccurate record management data
B.
Inaccurate recovery time objectives (RTOs)
C.
Lack of accountability for data ownership
D.
Users having unauthorized access to data
Full Access
Answer:
D
Explanation:
The greatest risk associated with inappropriate classification of data is users having unauthorized access to sensitive information. Proper data classification ensures that access controls are applied appropriately, protecting sensitive data from unauthorized access.
Importance of Data Classification
Data classification involves categorizing data based on its level of sensitivity and the impact that unauthorized access, disclosure, modification, or destruction would have on the organization.
It ensures that appropriate security measures are applied according to the data ' s classification.
Risks of Inappropriate Classification
Unauthorized Access: If data is not classified correctly, sensitive information may not receive the necessary protections, leading to unauthorized access.
Lack of Accountability: Misclassification can result in unclear responsibilities for data protection, but the primary concern remains unauthorized access.
Inaccurate Recovery Time Objectives (RTOs): While important, this is secondary to the risk of unauthorized access.
Inaccurate Record Management Data: This can affect operational efficiency but is not as critical as unauthorized access.
Implementing Effective Classification
Organizations must have a clear data classification policy and ensure it is followed consistently.
Regular audits and reviews should be conducted to verify that data is classified appropriately and that access controls are enforced.
References
CISM Review Manual Full text.html, emphasizing the importance of proper data classification and the risks associated with misclassification, especially unauthorized access to data​​.
Question # 441
A bank recently incorporated Blockchain technology with the potential to impact known risk within the organization. Which of the following is the risk practitioner’s BEST course of action?
A.
Determine whether risk responses are still adequate.
B.
Analyze and update control assessments with the new processes.
C.
Analyze the risk and update the risk register as needed.
D.
Conduct testing of the control that mitigate the existing risk.
Full Access
Answer:
C
Question # 442
The MAIN purpose of conducting a control self-assessment (CSA) is to:
A.
gain a better understanding of the control effectiveness in the organization
B.
gain a better understanding of the risk in the organization
C.
adjust the controls prior to an external audit
D.
reduce the dependency on external audits
Full Access
Answer:
A
Explanation:
 A control self-assessment (CSA) is a technique that allows managers and work teams directly involved in business units, functions, or processes to participate in assessing the organization’s risk management and control processes. The main purpose of conducting a CSA is to gain a better understanding of the control effectiveness in the organization, which means how well the controls are designed, implemented, and operated to achieve the desired outcomes and mitigate the risks. A CSA can help to identify the strengths and weaknesses of the existing controls, as well as the gaps and opportunities for improvement. A CSA can also help to enhance the awareness, ownership, and accountability of the control environment among the managers and staff. The other options are not the main purpose of conducting a CSA, although they may be related or beneficial. Gaining a better understanding of the risk in the organization is a result of conducting a CSA, but it is not the primary goal. The primary goal is to evaluate the controls that address the risks, not the risks themselves. Adjusting the controls prior to an external audit is a possible action that may follow a CSA, but it is not the reason for conducting a CSA. The reasonfor conducting a CSA is to improve the control effectiveness, not to prepare for an audit. Reducing the dependency on external audits is a potential benefit of conducting a CSA, but it is not the objective of conducting a CSA. The objective of conducting a CSA is to enhance the internal control assurance, not to replace the external audit assurance. References = CRISC Review Manual, pages 153-1541; CRISC Review Questions, Answers & Explanations Manual, page 802
Question # 443
The MAIN reason a risk practitioner should review control assessment reports is to:
A.
Provide assurance on effective compliance.
B.
Determine exceptions for management acceptance.
C.
Determine overall efficiency of the control environment.
D.
Determine if controls effectively lower risk exposure.
Full Access
Answer:
D
Explanation:
The correct answer is D . In CRISC, the purpose of reviewing control assessment reports is to determine whether controls are effective in reducing risk exposure to an acceptable level. The uploaded CRISC notes state that the most important criterion when reviewing information security controls is ensuring that the controls are effectively addressing risk. They also state that effective control implementation primarily correlates with a decrease in residual risk.
A is more audit/compliance focused. B may happen after exceptions are identified, but it is not the main reason for reviewing reports. C focuses on efficiency, while CRISC prioritizes risk reduction and control effectiveness.
===========
Question # 444
Which of the following is the MOST important metric to monitor the performance of the change management process?
A.
Percentage of changes having separation of duties in code deployment
B.
Percentage of changes having completed post-implementation verification
C.
Percentage of changes having user acceptance testing (UAT) sign-off
D.
Percentage of changes having to invoke the rollback plan
Full Access
Answer:
B
Explanation:
Post-implementation verification ensures that changes achieve the desired outcomes without causing unintended issues. It validates the success of change deployment and minimizes operational disruption, making it the most direct indicator of change management effectiveness.
[Reference:CRISC Manual – Domain 4, Slide 430-432, , , , ]
Question # 445
Which of the following BEST indicates the condition of a risk management program?
A.
Number of risk register entries
B.
Number of controls
C.
Level of financial support
D.
Amount of residual risk
Full Access
Answer:
D
Explanation:
The best indicator of the condition of a risk management program is the amount of residual risk. Residual risk is the risk that remains after the implementation of risk responses. Residual risk reflects the effectiveness and efficiency of the risk management program in reducing the risk exposure to an acceptable level, and in aligning the risk profile with the risk appetite and tolerance of the enterprise. A low amount of residual risk indicates that the risk managementprogram is performing well, and that the controls are adequate and appropriate. A high amount of residual risk indicates that the risk management program is not functioning properly, and that the controls are insufficient or ineffective. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 1, Section 1.2.2, page 191
Question # 446
An IT risk practitioner has determined that mitigation activities differ from an approved risk action plan. Which of the following is the risk practitioner ' s BEST course of action?
A.
Report the observation to the chief risk officer (CRO).
B.
Validate the adequacy of the implemented risk mitigation measures.
C.
Update the risk register with the implemented risk mitigation actions.
D.
Revert the implemented mitigation measures until approval is obtained
Full Access
Answer:
B
Explanation:
This can help to:
Ensure that the implemented measures are effective and efficient in reducing the risk level to an acceptable level, and that they are aligned with the risk appetite and tolerance of the organization2.
Identify and address any gaps, issues, or challenges that may arise from the deviation from the approved risk action plan, and recommend and implement appropriate improvement actions or contingency plans3.
Communicate and report the results and outcomes of the validation to the relevant stakeholders, such as the risk owner, the risk committee, or the chief risk officer, and obtain their feedback and approval4.
The other options are not the best course of action, because:
Reporting the observation to the chief risk officer (CRO) is not the best course of action, as it may not provide sufficient information or evidence to support the deviation from the approved risk action plan. The CRO may not be able to evaluate or approve the implemented risk mitigation measures without knowing their adequacy or impact on the risk level5.
Updating the risk register with the implemented risk mitigation actions is not the best course of action, as it may not reflect the current or accurate risk status or performance. The risk register is a document that records and summarizes the key information and data about the identified risks and the risk responses6. Updating the risk register without validating the adequacy of the implemented risk mitigation measures may create inconsistencies or inaccuracies in the risk register.
Reverting the implemented mitigation measures until approval is obtained is not the best course of action, as it may expose the organization to higher or unacceptable levels of risk. Reverting the implemented mitigation measures may undo or negate the benefits or outcomes of the risk mitigation, and may increase the likelihood or impact of the risk events7.
References =
ISACA Risk Starter Kit provides risk management templates and policies
Risk Appetite and Tolerance - CIO Wiki
Risk Monitoring and Review - The National Academies Press
Risk Reporting - CIO Wiki
Chief Risk Officer - CIO Wiki
Risk Register - CIO Wiki
Risk Mitigation - CIO Wiki
Question # 447
An external data source has released an advisory about a critical vulnerability affecting a widely used software application. Which of the following should the risk practitioner do FIRST?
A.
Advise application owners to patch affected software
B.
Determine organizational exposure
C.
Notify senior management of the critical vulnerability
D.
Review the incident response plan
Full Access
Answer:
B
Explanation:
Upon receiving an external vulnerability alert, thefirst stepin the CRISC risk process is todetermine organizational exposure— i.e., whether and where the vulnerable software is actually used in the enterprise environment.
ISACA’s CRISC framework states:
“The initial step upon receiving notice of a new vulnerability is to assess the enterprise’s exposure to the threat to determine relevance and potential impact.â€
Only after confirming exposure should the practitioner recommend patching, escalation, or other actions. Acting prematurely without confirmation could cause unnecessary disruptions.
Hence,B. Determine organizational exposureis correct.
CRISC Reference:Domain 2 – IT Risk Assessment, Topic: Vulnerability Management and Exposure Analysis.
Question # 448
Which of the following is the GREATEST concern associated with insufficient focus on addressing blockchain interoperability in the SDLC?
A.
Limited blockchain adoption and support
B.
Reduced transaction speed and system responsiveness
C.
Reduced network integrity and availability
D.
Limited integration with external systems and blockchains
Full Access
Answer:
D
Explanation:
Limited integration with external systems and blockchainsis the greatest concern. Without considering interoperability during the SDLC, the system may not be able to connect seamlessly with partners or external networks, hindering business goals and limiting the blockchain’s benefits.
===========
Question # 449
Which of the following would present the MOST significant risk to an organization when updating the incident response plan?
A.
Obsolete response documentation
B.
Increased stakeholder turnover
C.
Failure to audit third-party providers
D.
Undefined assignment of responsibility
Full Access
Answer:
D
Explanation:
The most significant risk to an organization when updating the incident response plan is the undefined assignment of responsibility. An incident response plan is a document that defines the roles, responsibilities, procedures, and resources for responding to an incident that could disrupt the normal operations of the organization, or compromise its assets, reputation, or compliance. An incident response plan should clearly assign the responsibility for each task and activity involved in the incident response process, such as detection, containment, analysis, eradication, recovery, and reporting. Undefined assignment of responsibility could lead to confusion, duplication, conflict, or omission among the stakeholders, and impair the effectiveness and efficiency of the incident response process. Undefined assignment of responsibility could also increase the risk of escalation, recurrence, or impact of the incident, and affect the accountability and performance of the organization. Obsolete response documentation, increased stakeholder turnover, and failure to audit third-party providers are also risks, but they are not as significant as undefined assignment of responsibility, as they do not directly affect the execution and outcome of the incident response process. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 130.
Question # 450
Which of the following is the PRIMARY reason to use key control indicators (KCIs) to evaluate control operating effectiveness?
A.
To measure business exposure to risk
B.
To identify control vulnerabilities
C.
To monitor the achievement of set objectives
D.
To raise awareness of operational issues
Full Access
Answer:
C
Explanation:
 Key control indicators (KCIs) are metrics that measure how well a specific control is performing in reducing the causes, consequences, or likelihood of a risk1. KCIs are used to evaluate the control operating effectiveness, which is the degree to which a control achieves its intended objectives and mitigates the risk2.
The primary reason to use KCIs to evaluate control operating effectiveness is to monitor the achievement of set objectives. This means that KCIs help to:
Track and report the progress and performance of the control against the predefined targets, standards, or benchmarks
Identify and address any gaps, deviations, or issues in the control operation or outcome
Provide feedback and assurance to the stakeholders and regulators on the adequacy and reliability of the control
Support the continuous improvement and optimization of the control3
References = Key Control Indicator (KCI) - CIO Wiki, Evaluating and Improving Internal Control in Organizations - IFAC, A Methodical Approach to Key Control Indicators
Question # 451
Which of the following is MOST helpful in identifying gaps between the current and desired state of the IT risk environment?
A.
Analyzing risk appetite and tolerance levels
B.
Assessing identified risk and recording results in the risk register
C.
Evaluating risk scenarios and assessing current controls
D.
Reviewing guidance from industry best practices and standards
Full Access
Answer:
C
Explanation:
Evaluating risk scenarios and assessing current controls is the most helpful in identifying gaps between the current and desired state of the IT risk environment, because it allows the risk practitioner to compare the actual and expected outcomes of the IT processes and activities under different situations. A risk scenario is a hypothetical situation that describes a possible event or sequence of events that may affect the IT objectives and performance. A risk scenario can be based on various factors, such as the sources of risk, the risk drivers, the risk events, the risk impacts, and the risk responses. A risk scenario can also include the likelihood and severity of the risk, as well as the assumptions and uncertainties involved. Evaluating risk scenarios helps the risk practitioner to understand the nature and extent of the IT risks, as well as the potential consequences and opportunities that may arise from them. Assessing current controls is the process of examining and testing the existing controls that are implemented to manage the IT risks. A control is a measure or action that reduces the likelihood or impact of a risk, or enhances the benefits or opportunities of a risk. Assessing current controls helps the risk practitioner to determine the effectiveness and efficiency of the controls, as well as their alignment with the IT objectives and requirements. By evaluating risk scenarios and assessing current controls, the risk practitioner can identify the gaps between the current and desired state of the IT risk environment. The gaps can be related to the following aspects: - The IT objectives and performance: The gaps can indicate the difference between the actual and expected results of theIT processes and activities, as well as the deviation from the IT goals and targets. - The IT risk exposure and appetite: The gaps can indicate the difference between the actualand acceptable level of risk that the organization faces or is willing to take in pursuit of the IT objectives. - The IT risk management process and practices: The gaps can indicate the difference between the actual and expected performance of the IT risk management process, as well as the compliance with the IT risk management policies and standards. - The IT risk culture and awareness: The gaps can indicate the difference between the actual and desired level of risk awareness,understanding, and communication among the IT stakeholders, as well as the alignment with the organizational values and culture. Identifying the gaps between the current and desired state of the IT risk environment is important for the risk practitioner, as it can help to prioritize and address the IT risks, as well as to improve and optimize the IT risk management process and practices. References = Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.3: Risk Scenarios, pp. 63-681
Question # 452
Which of the following is the BEST way to detect zero-day malware on an end user ' s workstation?
A.
An antivirus program
B.
Database activity monitoring
C.
Firewall log monitoring
D.
File integrity monitoring
Full Access
Answer:
D
Explanation:
Zero-day malware is malware that exploits unknown and unprotected vulnerabilities. This novel malware is difficult to detect and defend against, making zero-day attacks a significant threat to enterprise cybersecurity1. The best way to detect zero-day malware on an end user’s workstation is to use file integrity monitoring, which is a technique that monitors and alerts on changes to files and directories that may indicate a malware infection or compromise2. By using fileintegrity monitoring, the end user can detect zero-day malware that may alter or damage the files or directories on their workstation, and take appropriate actions to remove or isolate the malware. File integrity monitoring can also help to prevent the spread of zero-day malware to other systems or networks, and to restore the integrity and availability of the affected files or directories. Antivirus program, database activity monitoring, and firewall log monitoring are not the best ways to detect zero-day malware on an end user’s workstation, as they are not as effective or reliable as file integrity monitoring. Antivirus program is a software that scans and removes known malware from a system or network3. Antivirus program can help to protect the end user’s workstation from common or known malware, but it may not be able to detect zero-day malware that does not have a signature or a pattern that matches the antivirus program’s database. Database activity monitoring is a technique that monitors and audits the activities and transactions on a database, such as queries, updates, or deletions4. Database activity monitoring can help to protect the end user’s database from unauthorized or malicious access or modification, but it may not be able to detect zero-day malware that does not target or affect the database. Firewall log monitoring is a technique that monitors and analyzes the logs generated by a firewall, which is a device or software that filters and controls the incoming and outgoing network traffic based on predefined rules. Firewall log monitoring can help to protect the enduser’s workstation from external or internal network attacks, but it may not be able to detect zero-day malwarethat bypasses or evades the firewall rules or that originates from the workstation itself. References = 1: What is Zero Day Malware? - Check Point Software2: File Integrity Monitoring - an overview | ScienceDirect Topics3: Antivirus Software - an overview | ScienceDirect Topics4: Database Activity Monitoring - an overview | ScienceDirect Topics : [Firewall Log Analysis - an overview | ScienceDirect Topics] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.1: Control Design, pp. 233-235.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.2: Control Implementation, pp. 243-245.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.3: Control Monitoring and Maintenance, pp. 251-253.] : [Zero-day attack detection: a systematic literature review | Artificial Intelligence Review] : [Zero-day Attacks Detection and Prevention Methods | Apriorit]Â
Question # 453
Which of the following would MOST likely result in agreement on accountability for risk scenarios?
A.
Using a facilitated risk management workshop
B.
Relying on generic risk scenarios
C.
Relying on external IT risk professionals
D.
Distributing predefined scenarios for review
Full Access
Answer:
A
Explanation:
The correct answer isAbecause afacilitated risk management workshopis most likely to result in agreement on accountability for risk scenarios. A workshop allows relevant stakeholders to discuss the scenarios together, align on business context, clarify roles, and agree on who owns the risk and who is responsible for treatment and escalation.
The other options are less effective:
B. Relying on generic risk scenariosreduces alignment with the specific business context and usually weakens ownership clarity.
C. Relying on external IT risk professionalsmay provide expertise, but accountability must be agreed internally by business stakeholders.
D. Distributing predefined scenarios for reviewis less effective than active facilitation because it does not create the same level of interaction and consensus.
Exact Extracts supporting the answer:
“An interdisciplinary team within the enterprise offers the best perspective on risk management to employees and stakeholders.â€
“To ensure the overall effectiveness of a risk management program it is essential to have the participation of relevant stakeholders.â€
“Clear detailed roles and responsibilities are MOST critical to ensure the three lines of defense work together effectively.â€
“The BEST approach when developing risk scenarios for an enterprise is to use both the top-down and the bottom-up approach because they have different perspectives.â€
“The management team owns the risk and is responsible for identifying assessing and mitigating risk and reporting to the appropriate support functions and the board of directors.â€
These extracts support that agreement on accountability is most likely when relevant stakeholders actively participate together in a structured discussion.
===========
Question # 454
An organization has identified a risk exposure due to weak technical controls in a newly implemented HR system. The risk practitioner is documenting the risk in the risk register. The risk should be owned by the:
A.
chief risk officer.
B.
project manager.
C.
chief information officer.
D.
business process owner.
Full Access
Answer:
D
Explanation:
The business process owner should be the risk owner for the risk exposure due to weak technical controls in a newly implemented HR system, because they are responsible for the performance and outcomes of the HR business process, and they understand the business requirements, expectations, and impact of the HR system. The business process owner can also evaluate the trade-offs between the potential benefits and costs of the HR system, and the potential risks and consequences of a failure or breach of the system. The business process owner can also communicate and justify their risk acceptance or mitigation decision to the senior management and other stakeholders, and ensure that the risk is monitored and reviewed regularly. The other options are less appropriate to be the risk owner for this risk exposure. The chief risk officer is responsible for overseeing the enterprise-wide risk management framework and process, which includesensuring the identification, assessment, and reporting of risks. However, they are not the owner of the HR system or the HR business process, and they may not have the full knowledge or authority to accept or mitigate the risk on behalf of the business. The project manager is responsible for managing the implementation of the HR system, which includes ensuring the delivery of the system within the scope, time, and budget constraints. However, they are not the owner of the HR system or the HR business process, and they may not have the full knowledge or authority to accept or mitigate the risk on behalf of the business. The chief information officeris responsible for managing the IT function and resources, which includes providing the technical support and security for the HR system. However, they are not the owner of the HRsystem or the HR business process, and they may not have the full knowledge or authority to accept or mitigate the risk on behalf of the business. References = Getting risk ownership right 1
Question # 455
An organization is outsourcing a key database to be hosted by an external service provider. Who is BEST suited to assess the impact of potential data loss?
A.
Database manager
B.
Public relations manager
C.
Data privacy manager
D.
Business manager
Full Access
Answer:
D
Explanation:
The business manager is best suited to assess the impact of potential data loss when outsourcing a key database to an external service provider.
Role of the Business Manager:
Understanding Business Impact:The business manager has a comprehensive understanding of the business processes, the criticality of the data, and the potential impact of data loss on business operations.
Decision Making:They are responsible for making decisions regarding risk tolerance, business continuity, and aligning the risk management practices with business objectives.
Assessment of Data Loss Impact:
Operational Impact:The business manager can evaluate how data loss would affect day-to-day operations and overall business continuity.
Financial and Reputational Impact:They can also assess the financial repercussions and potential damage to the organization’s reputation, providing a holistic view of the impact.
[References:, The CRISC Review Manual highlights the importance of involving business managers in assessing the impact of data loss due to their understanding of business operations and strategic objectives ., , , , , , , , , , , ]
Question # 456
Which of the following is the MOST appropriate risk owner for a payroll application that has recently been outsourced to a cloud software provider?
A.
IT executive.
B.
HR executive.
C.
Vendor management executive.
D.
Cloud service provider’s information security executive.
Full Access
Answer:
B
Explanation:
The correct answer is B . Payroll is a business process owned by HR, so the HR executive is the most appropriate risk owner. Outsourcing the application to a cloud software provider does not transfer business accountability for payroll risk. The uploaded CRISC notes state that ownership is best established by mapping identified risk to a specific business process. They also emphasize assignment of risk owners and accountability as critical to risk management.
The IT executive may manage technology controls, vendor management may oversee the contract, and the cloud provider may operate provider-side controls, but the business risk owner remains the HR executive.
===========
Question # 457
Which of the following is the MOST appropriate action when a tolerance threshold is exceeded?
A.
Communicate potential impact to decision makers.
B.
Research the root cause of similar incidents.
C.
Verify the response plan is adequate.
D.
Increase human resources to respond in the interim.
Full Access
Answer:
A
Explanation:
The most appropriate action when a tolerance threshold is exceeded is to communicate the potential impact to the decision makers. A tolerance threshold is the acceptable level of variation or deviation from the expected or planned performance or outcome of a risk response. When a tolerance threshold is exceeded, it means that the risk response is not effective or efficient enough to reduce the risk to an acceptable level, and that the enterprise is exposed to unacceptable levels of risk that could impair its ability to achieve its objectives. Therefore, the potential impact of the risk should be communicated to the decision makers, such as senior management, risk owners, or risk committee, who have the authority and responsibility to decide on the appropriate actions to address the risk situation. Communicating the potential impact can help to raise the awareness and urgency of the risk issue, and to facilitate the risk-based decision making process. Researching the root cause of similar incidents, verifying the response plan isadequate, and increasing human resources to respond in the interim are not as appropriate as communicating the potential impact, as they do not address the primary need of informing and involving the decision makers, and may not be feasible or effective in resolving the risk issue. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 41.
Question # 458
An organization has built up its cash reserves and has now become financially able to support additional risk while meeting its objectives. What is this change MOST likely to impact?
A.
Risk profile
B.
Risk capacity
C.
Risk indicators
D.
Risk tolerance
Full Access
Answer:
B
Explanation:
Risk capacity is the amount of risk that an organization can financially afford to take, without jeopardizing its ability to meet its objectives or obligations. Risk capacity is determined by factors such as the organization’s income, assets, liabilities, and cash flow. An organization that has built up its cash reserves has increased its risk capacity, as it has more financial resources and flexibility to support additional risk. This may enable the organization to pursue more opportunities or initiatives that involve higher risk and higher reward.
Risk profile is a summary of the key risks that an organization faces, and their implications for the organization’s objectives and strategy. Risk profile may change due to factors such as new technologies, business initiatives, or external events, but not necessarily due to changes in cash reserves.
Risk indicators are metrics or indicators that help to monitor and evaluate the likelihood or impact of a risk, or the effectiveness or efficiency of a control. Risk indicators may vary depending on the risk sources, scenarios, or responses, but not necessarily due to changes in cash reserves.
Risk tolerance is the amount of risk that an organization is willing to accept, based on its risk appetite and risk capacity. Risk tolerance is influenced by factors such as the organization’s culture, values, and objectives, as well as the risk environment and expectations. Risk tolerance may change due to changes in cash reserves, but it is not the most likely impact, as it also depends on the organization’s risk appetite and other factors.
Question # 459
Key risk indicators (KRIs) BEST support risk treatment when they:
A.
Set performance expectations for controls.
B.
Align with key business objectives.
C.
Indicate that the risk is approaching predefined thresholds.
D.
Articulate likelihood and impact in quantitative terms.
Full Access
Answer:
C
Explanation:
KRIs are most effective when they signal that a risk is nearing or exceeding predefined thresholds. This early warning enables organizations to take proactive measures to mitigate risks before they materialize into significant issues.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 3: Risk Response and Reporting, Section: Key Risk Indicators., , , , , , , ]
Question # 460
During a review of the asset life cycle process, a risk practitioner identified several unreturned and unencrypted laptops belonging to former employees. Which of the following is the GREATEST concern with this finding?
A.
Insufficient laptops for existing employees
B.
Abuse of leavers ' account privileges
C.
Unauthorized access to organizational data
D.
Financial cost of replacing the laptops
Full Access
Answer:
C
Explanation:
The greatest concern with finding unreturned and unencrypted laptops belonging to former employees is the risk of unauthorized access to organizational data. The laptops may containsensitive or confidential information that could be compromised if they fall into the wrong hands. This could result in data breaches, reputational damage, legal liabilities, or regulatory penalties for the organization. Therefore, it is important to have proper controls in place to ensure that the laptops are returned, wiped, or encrypted when the employees leave the organization.
[References: The answer is based on the following sources:, •CRISC Review Manual, 7th Edition, Chapter 4: Information Technology and Security, pages 224-2251, •CRISC Review Questions, Answers & Explanations Database, 12 Month Subscription, Question ID: QID-10032, •What is asset lifecycle management? | IBM1, , , , , , , , , , ]
Question # 461
Which of the following is MOST important to add to the risk register for a remediated risk scenario?
A.
Notification to technical teams of implementation schedules
B.
Sign-off by senior executives
C.
Evidence of successfully implemented controls
D.
Minutes from control design meetings
Full Access
Answer:
C
Explanation:
For closed risks, documented proof that controls are in place and working (e.g., logs, test results) is vital. ISACA’s CRISC Manual emphasizes that evidence is required to validate control effectiveness and support audit requirements
Question # 462
An organization is planning to acquire a new financial system. Which of the following stakeholders would provide the MOST relevant information for analyzing the risk associated with the new IT solution?
A.
Project sponsor
B.
Process owner
C.
Risk manager
D.
Internal auditor
Full Access
Answer:
B
Explanation:
The process owner is the stakeholder who is responsible for the business process that will be supported by the new IT solution. The process owner has the best knowledge of the businessrequirements, objectives, and risks associated with the process. The process owner can provide the most relevant information for analyzing the risk associated with the new IT solution, such as the expected benefits, costs, performance, functionality, security, and compliance of the solution. The process owner can also help to identify and evaluate the potential impact and likelihood of the risk scenarios related to the new IT solution. The other stakeholders may have some information or insights, but they are not as directly involved or affected by the new IT solution as the process owner. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.3.1.1, pp. 58-59.
Question # 463
It is MOST important that entries in an organization’s risk register be updated:
A.
when the key risk indicator (KRI) threshold has been reached.
B.
when required by internal audit.
C.
prior to a risk review.
D.
when aspects of the risk scenario change.
Full Access
Answer:
D
Explanation:
The risk register is a living document. CRISC states it should be maintained so that it accurately reflects current risk conditions, including changes in threats, vulnerabilities, impacts, controls, and ownership. Therefore, it is most important to update entrieswhen aspects of the risk scenario change—for example, when a new control is implemented, business processes change, threat activity increases, or the magnitude of impact alters. Waiting until KRI thresholds are reached may delay updating until risk is already elevated. Updating only when internal audit requires it or just before a periodic review undermines real-time visibility and decision-making. Timely updates when the scenario changes support effective monitoring, reporting, and governance, ensuring that management decisions are based on current, not outdated, risk information.
[Reference:CRISC Review Manual – Risk and Control Monitoring and Reporting (risk register maintenance)., ===========, ]
Question # 464
Which of the following is the PRIMARY reason for a risk practitioner to review an organization ' s IT asset inventory?
A.
To plan for the replacement of assets at the end of their life cycles
B.
To assess requirements for reducing duplicate assets
C.
To understand vulnerabilities associated with the use of the assets
D.
To calculate mean time between failures (MTBF) for the assets
Full Access
Answer:
C
Explanation:
 Understanding vulnerabilities associated with the use of the assets is the primary reason for a risk practitioner to review an organization’s IT asset inventory, as it helps to identify and assess the potential threats and risks to the assets. The other options are not the primary reasons for a risk practitioner to review an organization’s IT asset inventory, although they may be related to the process.
Question # 465
An organization ' s HR department has implemented a policy requiring staff members to take a minimum of five consecutive days leave per year to mitigate the risk of malicious insideractivities. Which of the following is the BEST key performance indicator (KPI) of the effectiveness of this policy?
A.
Number of malicious activities occurring during staff members leave
B.
Percentage of staff members seeking exception to the policy
C.
Percentage of staff members taking leave according to the policy
D.
Financial loss incurred due to malicious activities during staff members ' leave
Full Access
Answer:
C
Explanation:
 The best key performance indicator (KPI) of the effectiveness of the policy requiring staff members to take a minimum of five consecutive days leave per year to mitigate the risk ofmalicious insider activities is the percentage of staff members taking leave according to the policy. A KPI is a quantifiable measure that evaluates the performance of a process, activity, or outcome against a predefined target or objective. The percentage of staff members taking leave according to the policy is the best KPI, because it directly measures the compliance and adherence of the staff members to the policy, which is the main objective of the policy. The policy aims to reduce the risk of malicious insider activities by forcing the staff members to take a break from their work, which can help to deter, detect, or prevent any fraudulent or unauthorized actions, such as data theft, sabotage, or manipulation12. The percentage of staffmembers taking leave according to the policy can also help to evaluate the effectiveness and efficiency of the policy implementation and enforcement, and to identify and address any gaps or issues in the policy design or execution. The other options are not the best KPI, although they may be related or influential to the policy effectiveness. The number of malicious activities occurring during staff members’ leave is a measure of the occurrence and impact of the risk events that the policy aims to mitigate, but it is not a direct measure of the policy performance or compliance. The number of malicious activities occurring during staff members’ leave may also be affected by other factors or controls, such as the security systems, the audit procedures, or the external threats, which may not reflect the policy effectiveness. The percentage of staff members seeking exception to the policy is a measure of the resistance or dissatisfaction of the staff members to the policy, but it is not a direct measure of the policy performance or compliance. The percentage of staff members seeking exception to the policy may also be influenced by other factors or circumstances, such as the workload, the personal preferences, or the organizational culture, which may not indicate the policy effectiveness. The financial loss incurred due to malicious activities during staff members’ leave is a measure of the consequence and severity of the risk events that the policy aims to mitigate, but it is not a direct measure of the policy performance or compliance. The financial loss incurred due to malicious activities during staff members’ leave may also vary depending on the type, scale, or frequency of the malicious activities, or the recovery or compensation actions, which may not represent the policy effectiveness. References = How To Measure Risk Management KPI & Metrics - ERM Software, Key Performance Indicators (KPIs): The Ultimate Guide - ClearPoint Strategy
Question # 466
A risk practitioner notices that a particular key risk indicator (KRI) has remained below its established trigger point for an extended period of time. Which of the following should be done FIRST?
A.
Recommend a re-evaluation of the current threshold of the KRI.
B.
Notify management that KRIs are being effectively managed.
C.
Update the risk rating associated with the KRI In the risk register.
D.
Update the risk tolerance and risk appetite to better align to the KRI.
Full Access
Answer:
A
Explanation:
 The FIRST thing that should be done when a KRI has remained below its established trigger point for an extended period of time is to recommend a re-evaluation of the current threshold of the KRI, because it may indicate that the trigger point is set too high or too low, or that the KRI is not relevant or effective in measuring the risk exposure. A re-evaluation of the current threshold of the KRI may result in adjusting the trigger point, changing the KRI, or removing the KRI. The other options are not the first thing that should be done, because:
Option B: Notifying management that KRIs are being effectively managed is not the first thing that should be done, because it may not reflect the true risk status and performance. A KRI that remains below its trigger point for a long time may not be a valid or reliable indicator of the risk exposure, and it may not capture the changes or trends in the risk environment.
Option C: Updating the risk rating associated with the KRI in the risk register is not the first thing that should be done, because it may not be accurate or consistent. A risk rating is based on the likelihood and impact of the risk, and it should be derived from a comprehensive risk analysis, not just from a single KRI. A KRI that remains below its trigger point for a long time may not reflect the actual likelihood and impact of the risk, and it may not be aligned with the other risk indicators and assessments.
Option D: Updating the risk tolerance and risk appetite to better align to the KRI is not the first thing that should be done, because it may not be appropriate or feasible. Risk tolerance and risk appetite are the acceptable level of risk exposure and variation that the enterprise is willing to accept in pursuit of its objectives, and they are determined by the executive management and the board of directors, based on the enterprise’s strategy and goals. A KRI that remains below its trigger point for a long time may not represent the desired or optimal level of risk exposure and variation, and it may not be aligned with the enterprise’s strategy and goals. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 121.
Question # 467
A vendor ' s planned maintenance schedule will cause a critical application to temporarily lose failover capabilities. Of the following, who should approve this proposed schedule?
A.
IT infrastructure manager
B.
Chief Risk Officer (CRO)
C.
Business continuity manager
D.
Business application owner
Full Access
Answer:
D
Explanation:
The business application owner is responsible for the operation and risk decisions related to the application. Since the loss of failover may impact business continuity, their approval is essential.
[Reference:CRISC Manual – Domain 1, Slide 70, 214, , , , , , ]
Question # 468
Which of the following BEST enables senior management to make risk treatment decisions in line with the organization ' s risk appetite?
A.
Quantitative risk analysis
B.
Industry risk benchmarks
C.
Risk scenarios
D.
Risk remediation plans
Full Access
Answer:
A
Question # 469
Which of the following BEST helps to identify significant events that could impact an organization?
A.
Control analysis
B.
Vulnerability analysis
C.
Scenario analysis
D.
Heat map analysis
Full Access
Answer:
C
Explanation:
 Scenario analysis is the best method to identify significant events that could impact an organization. Scenario analysis is the process of creating and evaluating hypothetical situations or scenarios that represent plausible outcomes of various events or actions. Scenario analysis helps to anticipate and prepare for potential risks and opportunities, as well as to test the robustness and resilience of the organization’s strategies and plans. Control analysis, vulnerability analysis, and heat map analysis are not as effective as scenario analysis, because they focus on the existing or current state of the organization, rather than the future or alternative states. References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 4-13.
Question # 470
An organization has allowed several employees to retire early in order to avoid layoffs Many of these employees have been subject matter experts for critical assets Which type of risk is MOST likely to materialize?
A.
Confidentiality breach
B.
Institutional knowledge loss
C.
Intellectual property loss
D.
Unauthorized access
Full Access
Answer:
B
Explanation:
The type of risk that is most likely to materialize as a result of allowing several employees to retire early in order to avoid layoffs is institutional knowledge loss, as it represents the loss of valuable information, experience, and expertise that the employees have accumulated over time, and that may not be easily transferred or replaced. Confidentiality breach, intellectual property loss, and unauthorized access are not the most likely types of risk, as they are more related to the security, ownership, or access of information, respectively, rather than the retention or transfer of knowledge. References = CRISC Review Manual, 7th Edition, page 100.
Question # 471
Which of the following is the BEST success criterion for control implementation?
A.
Adequate resources are allocated to perform the control.
B.
Responsibilities for control execution are properly defined.
C.
Risk is at an acceptable level after the control is in place.
D.
Key risk indicators (KRIs) for the control are properly defined.
Full Access
Answer:
C
Question # 472
An organization is developing a plan to address new information security risks emerging from business changes. Which of the following BEST enables stakeholders to make decisions impacting organizational strategy?
A.
The impact of the new risk is clearly presented
B.
Benchmarking information is provided
C.
Technical expertise to address new risk scenarios is available
D.
The cost of implementing the strategy is within budget
Full Access
Answer:
A
Explanation:
CRISC emphasizesrisk communicationin decision-making. Stakeholders can only make effective strategic decisions if thebusiness impactof risk is clearly presented.
“The purpose of risk communication is to enable informed decision-making by clearly presenting the potential impact of risk on business objectives.â€
Benchmarking and cost data support the discussion but are secondary to understanding impact severity.
Hence,Ais correct.
CRISC Reference:Domain 4 – Risk Monitoring and Reporting, Topic: Risk Communication Principles.
Question # 473
An organization retains footage from its data center security camera for 30 days when the policy requires 90-day retention The business owner challenges whether the situation is worth remediating Which of the following is the risk manager s BEST response '
A.
Identify the regulatory bodies that may highlight this gap
B.
Highlight news articles about data breaches
C.
Evaluate the risk as a measure of probable loss
D.
Verify if competitors comply with a similar policy
Full Access
Answer:
C
Explanation:
A risk is the possibility of an event that may have a negative impact on the achievement of an organization’s objectives. A risk can be measured by the probability and impact of the event, which indicate the likelihood and consequence of the event. A risk manager is a person who is responsible for performing risk management activities, such as identifying, analyzing, evaluating, treating, monitoring, and communicating risks. When an organization retains footage from its data center security camera for 30 days when the policy requires 90-day retention, the risk manager’s best response to the business owner who challenges whether the situation is worth remediating is to evaluate the risk as a measure of probable loss, which means to estimate thepotential harm or damage that may result from the non-compliance with the policy. By evaluating the risk as a measure of probable loss, the risk manager can provide the business owner with the rationale and justification for the risk remediation, and help the business owner to understand the cost-benefit analysis of the risk response. References = CRISC Review Manual, 7th Edition, page 63.
Question # 474
After the review of a risk record, internal audit questioned why the risk was lowered from medium to low. Which of the following is the BEST course of action in responding to this inquiry?
A.
Obtain industry benchmarks related to the specific risk.
B.
Provide justification for the lower risk rating.
C.
Notify the business at the next risk briefing.
D.
Reopen the risk issue and complete a full assessment.
Full Access
Answer:
B
Explanation:
The best course of action in responding to the internal audit inquiry is to provide justification for the lower risk rating. This would demonstrate that the risk record was updated based on a valid and documented rationale, such as changes in the risk environment, risk drivers, risk indicators, or risk responses. Providing justification would also help to maintain the transparency and accountability of the risk management process, and ensure that the internal audit is satisfied with the risk assessment outcome. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.3, page 184.
Question # 475
Which of the following is MOST important to the effectiveness of a senior oversight committee for risk monitoring?
A.
Key risk indicators (KRIs)
B.
Risk governance charter
C.
Organizational risk appetite
D.
Cross-business representation
Full Access
Answer:
D
Explanation:
Cross-business representation is most important to the effectiveness of a senior oversight committee for risk monitoring. Here’s a
Importance of Cross-business Representation:
Comprehensive Risk Perspective: Having representatives from different business units ensures that the committee has a comprehensive view of risks across the entire organization. This diverse representation helps in identifying and assessing risks that may impact various parts of the business differently.
Informed Decision-Making: Members from different business areas can provide unique insights and expertise, leading to more informed and balanced decision-making processes.
Improved Communication: Cross-business representation facilitates better communication and collaboration across the organization, ensuring that risk management practices are understood and implemented consistently.
Comparison with Other Options:
Key Risk Indicators (KRIs): While important for monitoring specific risks, KRIs alone do not ensure the effectiveness of the oversight committee without a diverse representation to interpret and act on these indicators.
Risk Governance Charter: A risk governance charter outlines the roles, responsibilities, and processes for risk management, but its effectiveness depends on the active participation of diverse business representatives.
Organizational Risk Appetite: Understanding the organizational risk appetite is crucial, but without cross-business representation, the risk appetite may not be appropriately reflected or acted upon across all business areas.
Best Practices:
Diverse Membership: Ensure that the oversight committee includes members from all key business units and functions to provide a holistic view of organizational risks.
Regular Meetings: Schedule regular meetings to review and discuss risk management activities, KRIs, and emerging risks with input from all representatives.
Clear Communication: Establish clear communication channels between the oversight committee and business units to ensure that risk management practices are effectively implemented and monitored.
[References:, CRISC Review Manual: Emphasizes the importance of cross-functional representation in risk governance to ensure comprehensive risk management., ISACA Risk Management Framework: Highlights the need for diverse perspectives in risk oversight committees to enhance the effectiveness of risk monitoring and decision-making., Top of Form, Bottom of Form, , , , , , , , , , ]
Question # 476
A risk practitioner wants to identify potential risk events that affect the continuity of a critical business process. Which of the following should the risk practitioner do FIRST?
A.
Evaluate current risk management alignment with relevant regulations
B.
Determine if business continuity procedures are reviewed and updated on a regular basis
C.
Conduct a benchmarking exercise against industry peers
D.
Review the methodology used to conduct the business impact analysis (BIA)
Full Access
Answer:
D
Explanation:
The risk practitioner shouldfirst review the methodology of the BIAbecause the BIA identifies critical processes and the impacts of disruptions. This ensures that any identified risks are grounded in reliable, updated business impact data.
===========
Question # 477
After undertaking a risk assessment of a production system, the MOST appropriate action is fcr the risk manager to
A.
recommend a program that minimizes the concerns of that production system.
B.
inform the process owner of the concerns and propose measures to reduce them.
C.
inform the IT manager of the concerns and propose measures to reduce them.
D.
inform the development team of the concerns and together formulate risk reduction measures.
Full Access
Answer:
B
Explanation:
The most appropriate action for the risk manager to take after undertaking a risk assessment of a production system is to inform the process owner of the concerns and propose measures to reduce them, as the process owner has the authority and responsibility to manage the production system and its associated risks and controls, and to decide on the optimal risk response. Recommending a program that minimizes the concerns of that production system, informing the IT manager of the concerns and proposing measures to reduce them, and informing the development team of the concerns and together formulating risk reduction measures are not the most appropriate actions, as they may not involve the process owner, who is the key stakeholder and decision maker for the production system and its risks. References = CRISC Review Manual, 7th Edition, page 101.
Question # 478
Which of the following BEST assists in justifying an investment in automated controls?
A.
Cost-benefit analysis
B.
Alignment of investment with risk appetite
C.
Elimination of compensating controls
D.
Reduction in personnel costs
Full Access
Answer:
A
Explanation:
A cost-benefit analysis is the best method to assist in justifying an investment in automated controls, as it helps to compare and evaluate the costs and benefits of the investment and to determine its feasibility and profitability. A cost-benefit analysis is a process of identifying, measuring, and comparing the expected costs and benefits of a project or a decision, such asinvesting in automated controls. A cost-benefit analysis can help to justify an investment in automated controls by providing the following benefits:
It enables a data-driven and evidence-based approach to decision making, rather than relying on subjective or qualitative judgments.
It facilitates a consistent and standardized way of assessing and communicating the value and impact of the investment across the organization and to the external stakeholders.
It supports the alignment of the investment with the organizational strategy and objectives, and helps to evaluate the achievement of the desired outcomes.
It helps to identify and prioritize the opportunities and challenges of the investment, and to develop and implement appropriate strategies and actions to address them.
It provides feedback and learning opportunities for the investment and its outcomes, and helps to foster a culture of continuous improvement and innovation.
The other options are not the best methods to assist in justifying an investment in automated controls. Alignment of investment with risk appetite is an important aspect of risk management, but it does not directly address the costs and benefits of the investment. Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Alignment of investment with risk appetite helps to ensure that the investment is consistent with the organizational risk tolerance and preferences,and does not expose the organization to excessive or unacceptable risk. Elimination of compensating controls is a possible benefit of investing in automated controls, but it is not a method to justify the investment. Compensating controls are alternative or additional controls that are implemented to mitigate the risk when the primary or preferred controls are not feasible or effective. Elimination of compensating controls can help to reduce the complexity and costs of the control environment, and to improve the efficiency and reliability of the controls. Reduction in personnel costs is a possible benefit of investing in automated controls, but it is not a method to justify the investment. Personnel costs are the expenses related to the staff and employees involved in the processes or functions that are automated. Reduction in personnel costs can help to increase the profitability and productivity of the organization, and to allocate the resources more effectively and efficiently. References = Cost Benefit Analysis: An Expert Guide | Smartsheet, IT Risk Resources | ISACA, Automation - Efficiency, Cost-Savings, Robotics | Britannica
Question # 479
The PRIMARY objective of the board of directors periodically reviewing the risk profile is to help ensure:
A.
the risk strategy is appropriate
B.
KRIs and KPIs are aligned
C.
performance of controls is adequate
D.
the risk monitoring process has been established
Full Access
Answer:
A
Explanation:
 The PRIMARY objective of the board of directors periodically reviewing the risk profile is to help ensure that the risk strategy is appropriate, because the risk strategy defines the enterprise’s risk appetite, tolerance, and objectives, and guides the risk management process and activities. The board of directors should review the risk profile to ensure that it reflects the current internal and external environment, and that it aligns with the enterprise’s strategy and goals. The other options are not the primary objective, because:
Option B: KRIs and KPIs are aligned is a desirable outcome of the risk strategy, but not the primary objective of the board of directors reviewing the risk profile. KRIs and KPIs are indicators that measure and monitor the risk exposure and performance of the enterprise, respectively, and they should be consistent with the risk strategy and objectives.
Option C: Performance of controls is adequate is a result of the risk response, but not the primary objective of the board of directors reviewing the risk profile. Performance of controls is the degree to which the controls are effective and efficient in mitigating the risks, and it should be evaluated and reported by the risk management function and the internal audit function.
Option D: The risk monitoring process has been established is a prerequisite for the risk profile, but not the primary objective of the board of directors reviewing the risk profile. The risk monitoring process is the process of tracking and reporting the risk status and performance, and it should be implemented and executed by the risk management function and the business process owners. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 119.
Question # 480
During a risk assessment, the risk practitioner finds a new risk scenario without controls has been entered into the risk register. Which of the following is the MOST appropriate action?
A.
Include the new risk scenario in the current risk assessment.
B.
Postpone the risk assessment until controls are identified.
C.
Request the risk scenario be removed from the register.
D.
Exclude the new risk scenario from the current risk assessment
Full Access
Answer:
A
Explanation:
A new risk scenario without controls means that there is a potential threat or event that could adversely affect the organization’s objectives, and there are no existing measures to prevent or reduce the impact or likelihood of the risk. Therefore, the most appropriate action is to include the new risk scenario in the current risk assessment, so that the risk practitioner can analyze therisk, evaluate its severity and priority, and recommend suitable controls to mitigate the risk. By including the new risk scenario in the current riskassessment, the risk practitioner can ensure that the risk register is updated and reflects the current risk profile of the organization. The other options are not appropriate because they either ignore the new risk scenario, delay the risk assessment process, or remove valuable information from the risk register. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.1, page 95.
Question # 481
Which of the following is MOST important information to review when developing plans for using emerging technologies?
A.
Existing IT environment
B.
IT strategic plan
C.
Risk register
D.
Organizational strategic plan
Full Access
Answer:
D
Explanation:
The most important information to review when developing plans for using emerging technologies is the organizational strategic plan. The organizational strategic plan is a document that defines the vision, mission, goals, and objectives of the organization. It also outlines the strategies, actions, and resources that are needed to achieve them. The organizational strategic plan provides the direction, alignment, and guidance for the use of emerging technologies, and ensures that they are aligned with and support the organizational needs and priorities. The other options are not as important as the organizational strategic plan, as they are related to the current state, specific area, or potential issues of the use of emerging technologies, not the overall purpose and value of the use of emerging technologies. References = Risk and InformationSystems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.2: IT Risk Identification Methods, page 19.
Question # 482
Which of the following findings of a security awareness program assessment would cause the GREATEST concern to a risk practitioner?
A.
The program has not decreased threat counts.
B.
The program has not considered business impact.
C.
The program has been significantly revised
D.
The program uses non-customized training modules.
Full Access
Answer:
D
Explanation:
The greatest concern for a risk practitioner when reviewing the findings of a security awareness program assessment is that the program uses non-customized training modules. Non-customizedtraining modules are generic and may not address the specific security needs, issues, and challenges of the organization. They may also fail to engage and motivate the employees to follow the security policies and procedures, and to enhance their security knowledge and skills. The program not decreasing threat counts, not considering business impact, or being significantly revised are other possible findings, but they are not as concerning as the program using non-customized training modules. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
Question # 483
Which of the following is the MOST appropriate key risk indicator (KRI) for backup media that is recycled monthly?
A.
Time required for backup restoration testing
B.
Change in size of data backed up
C.
Successful completion of backup operations
D.
Percentage of failed restore tests
Full Access
Answer:
D
Explanation:
The most appropriate key risk indicator (KRI) for backup media that is recycled monthly is the percentage of failed restore tests. A KRI is a metric that measures the likelihood or impact of a risk, and provides an early warning signal of a potential risk event. The percentage of failed restore tests is a KRI that reflects the quality and reliability of the backup media, and indicates the possibility of data loss or corruption. A high percentage of failed restore tests would suggest that the backup media is not functioning properly, and that the risk of data unavailability is increasing. Therefore, this KRI would help the risk practitioner to monitor the risk and take corrective actions as needed. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 5, Section 5.2.2, page 235.
Question # 484
Prudent business practice requires that risk appetite not exceed:
A.
inherent risk.
B.
risk tolerance.
C.
risk capacity.
D.
residual risk.
Full Access
Answer:
C
Explanation:
Risk appetite is the amount and type of risk that an organization is willing to accept in order to achieve its objectives. Risk appetite reflects the organization’s risk attitude and its willingness to take on risk in specific scenarios. Risk appetite is usually expressed in a qualitative statement approved by the board of directors1.
Risk capacity is the maximum amount of risk that an organization can responsibly take on without jeopardizing its financial stability or other key objectives. Risk capacity is determined by objective factors like income, assets, liabilities, debts, insurance coverage, dependents, and time horizon. Risk capacity is usually expressed in a quantitative measure that sets the limit of how much risk the organization can handle2.
Prudent business practice requires that risk appetite not exceed risk capacity, because this would mean that the organization is taking on more risk than it can afford or sustain. If the risk appetiteis higher than the risk capacity, the organization may face serious consequences such as insolvency, bankruptcy, reputational damage, legal liability, or regulatory sanctions. Therefore, the organization should align its risk appetite with its risk capacity, and ensure that its risk exposure is within its risk tolerance3.
The other options are not correct. Inherent risk is the level of risk that exists in the absence of controls or mitigations. It is the natural level of risk inherent in a process or activity. Residual risk is the level of riskthat remains after the controls or mitigations have been applied. It is the remaining risk after the risk response has been implemented. Risk tolerance is the acceptable variation in the outcomes related to specific objectives or risks. It is the range of risk exposure that the organization is prepared to accept4. None of these concepts are directly comparable torisk appetite, and none of them represent the limit of how much risk the organization can take on. References =
Risk Appetite vs. Risk Tolerance: What is the Difference? - ISACA
What Is the Difference Between Risk Tolerance and Risk Capacity? - Investopedia
Risk Management: Understanding Risk Capacity, Appetite, and Tolerance - Consulting Edge
[CRISC Review Manual, 7th Edition]
Question # 485
Which of the following is MOST helpful to ensure effective security controls for a cloud service provider?
A.
A control self-assessment
B.
A third-party security assessment report
C.
Internal audit reports from the vendor
D.
Service level agreement monitoring
Full Access
Answer:
B
Explanation:
A third-party security assessment report is the most helpful to ensure effective security controls for a cloud service provider, because it provides an independent and objective evaluation of the cloud provider’s security posture, policies, and practices. A third-party security assessment report can help to verify and validate the cloud provider’s compliance with the relevant standards, regulations, and best practices, such as ISO 27001, PCI DSS, NIST, or CSA. A third-party security assessment report can also help to identify and address any gaps, weaknesses, or vulnerabilities in the cloud provider’s security controls, and to provide recommendations and guidance for improvement. A third-party security assessment report can also help to increase the trust and confidence of the cloud customers, and to facilitate the due diligence and risk management processes. The other options are less helpful to ensure effective security controls for a cloud service provider. A control self-assessment is a process that enables the cloud provider to assess its own security controls, using a predefined framework or questionnaire. However, a control self-assessment may not be as reliable or comprehensive as a third-party security assessment report, as it may be biased, incomplete, or inaccurate, and it may not cover all the aspects or dimensions of security. Internal audit reports from the vendor are documents that provide the results and findings of the internal audits conducted by the cloud provider’s ownauditors, to verify and validate the effectiveness and efficiency of the securitycontrols. However, internal audit reports from the vendor may not be as credible or trustworthy as a third-party security assessment report, as they may be influenced by the cloud provider’s interests, objectives, or agenda, and they may not follow the same standards or criteria as the external auditors. Service level agreement monitoring is a process that measures and evaluates the performance and availability of the cloud services, based on the predefined metrics and targets agreed between the cloud provider and the cloud customer. However, service level agreement monitoring may not be sufficient or relevant to ensure effective security controls for a cloud service provider, as it may not address the security aspects or requirements of the cloud services, such as confidentiality, integrity, or accountability, and it may not reflect the actual security risks or incidents that may occur in the cloud environment. References = Cloud Security Controls: Key Elements and 4 Control Frameworks 1
Question # 486
Which of the following should be the PRIMARY focus of a risk owner once a decision is made to mitigate a risk?
A.
Updating the risk register to include the risk mitigation plan
B.
Determining processes for monitoring the effectiveness of the controls
C.
Ensuring that control design reduces risk to an acceptable level
D.
Confirming to management the controls reduce the likelihood of the risk
Full Access
Answer:
C
Explanation:
The primary focus of a risk owner once a decision is made to mitigate a risk is to ensure that the control design reduces the risk to an acceptable level. This means that the risk owner shouldverify that the control objectives, specifications, and implementation are aligned with the risk mitigation plan, and that the control is effective in reducing the risk exposure to within the risk appetite and tolerance of the enterprise. The risk owner should also ensure that the control design is consistent with the enterprise’s policies, standards, and procedures, and that it complies with any relevant laws, regulations, or contractual obligations. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 4, Section 4.2.4, page 185.
Question # 487
What is the PRIMARY purpose of a business impact analysis (BIA)?
A.
To determine the likelihood and impact of threats to business operations
B.
To identify important business processes in the organization
C.
To estimate resource requirements for related business processes
D.
To evaluate the priority of business operations in case of disruption
Full Access
Answer:
D
Explanation:
 The primary purpose of a business impact analysis (BIA) is to evaluate the priority of business operations in case of disruption. A BIA is a process that identifies and analyzes the potential effects of various types of disruptions on the enterprise’s critical business functions and processes. A BIA helps to determine the recovery objectives, such as the recovery time objective (RTO) and the recovery point objective (RPO), for each business operation, based on the impactof disruption on the enterprise’s objectives, reputation, compliance, and stakeholders. A BIA also helps to identify the dependencies, resources, and interdependencies of the business operations, and to rank them according to their importance and urgency. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.2.1, page 671
Question # 488
it was determined that replication of a critical database used by two business units failed. Which of the following should be of GREATEST concern1?
A.
The underutilization of the replicated Iink
B.
The cost of recovering the data
C.
The lack of integrity of data
D.
The loss of data confidentiality
Full Access
Answer:
C
Explanation:
The lack of integrity of data is the greatest concern when replication of a critical database used by two business units failed. Data integrity means that the data is accurate, complete, consistent, and reliable. If the replication failed, it means that the data in the primary and secondary databases may not be synchronized and may have discrepancies or errors. This could affect the quality and reliability of the data and the business processes that depend on it. The other options are not as concerning as the lack of integrity of data, as they are related to the efficiency, cost, or confidentiality of the data, which are less critical than the accuracy and reliability of the data. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Key Performance Indicators, page 183.
Question # 489
An automobile manufacturer is considering implementing an Internet of Things (IoT) network to improve customer service by collecting customer and vehicle data. Which of the following would be the risk practitioner’s BEST recommendation?
A.
Establish secure design and coding practices for the IoT network and devices
B.
Conduct a pilot program before implementing the IoT network and devices
C.
Ensure backward compatibility of IoT devices with previous generations of vehicles
D.
Provide a range of IoT device options and configurations for customers
Full Access
Answer:
A
Explanation:
Thegreatest inherent riskin IoT adoption is the potential for vulnerabilities within device software and connectivity. Thebest way to reduce this riskis to implementsecure-by-design and secure-coding practicesfrom the outset.
CRISC guidance:
“For emerging technologies such as IoT, risk mitigation begins with embedding secure design, coding, and configuration practices throughout the development lifecycle.â€
Pilot testing is beneficial but occurs later; secure design is foundational.
Hence,Ais correct.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Secure System Development and Emerging Technologies.
Question # 490
Which of the following should a risk practitioner recommend FIRST when a risk assessment identifies the exposure of a significant number of personal customer records in a database?
A.
Revise the information security policy.
B.
Invoke the incident response plan (IRP).
C.
Update the risk register.
D.
Escalate the issue to senior management.
Full Access
Answer:
D
Explanation:
The correct answer is D . Exposure of a significant number of personal customer records may create serious legal, regulatory, financial, and reputational impact. Senior management must be informed so they can make risk treatment, notification, legal, and resource decisions. The uploaded CRISC notes state that when a significant vulnerability is discovered in a critical system, the system owner should be notified to take corrective action. They also state that newly discovered risk should be communicated to decision makers and relevant stakeholders at the end of the risk assessment phase.
B would be correct if an actual incident or breach is confirmed. C should happen, but after escalation. A is too slow and indirect for significant personal-data exposure.
Question # 491
A key risk indicator (KRI) threshold has reached the alert level, indicating data leakage incidents are highly probable. What should be the risk practitioner ' s FIRST course of action?
A.
Update the KRI threshold.
B.
Recommend additional controls.
C.
Review incident handling procedures.
D.
Perform a root cause analysis.
Full Access
Answer:
C
Explanation:
A key risk indicator (KRI) is a metric that measures the level of risk exposure or the likelihood of a risk event1. A KRI threshold is a predefined value or range that triggers an alert or action when the KRI reaches or exceeds it2. A data leakage incident is an unauthorized or accidental exposure of sensitive or confidential data to external parties3.
When a KRI threshold reaches the alert level, indicating that data leakage incidents are highly probable, the risk practitioner’s first course of action should be to review the incident handling procedures. Incident handling procedures are the plans and actions to be taken in the event of a data breach or security incident, such as data leakage4. Reviewing the incident handling procedures can help the risk practitioner to:
Verify the roles and responsibilities of the incident response team and other stakeholders
Confirm the communication and escalation channels and protocols
Identify the tools and resources available for incident detection, containment, analysis, eradication, recovery, and reporting
Evaluate the readiness and preparedness of the organization to respond to a data leakage incident
Update or revise the procedures as needed to reflect the current situation and risk level
Reviewing the incident handling procedures can help the risk practitioner to ensure that the organization can respond to a data leakage incident effectively and efficiently, minimizing the potential or expected impact on the organization’s operations, reputation, or objectives.
The other options are not the first course of action for the risk practitioner, although they may be relevant or necessary at later stages of the risk management process. Updating the KRI threshold, which means adjusting the value or range that triggers an alert or action, may be appropriate if the KRI threshold is too high or too low, but it does not address the imminent risk of data leakage or the response plan. Recommending additional controls, which means suggesting new or improved measures to prevent, detect, or mitigate data leakage, may be useful for reducing the risk exposure or impact, but it does not ensure that the organization is ready or capable to handle a data leakage incident. Performing a root cause analysis, which means finding and identifying the underlying factors that contributed to the risk event, may be helpful for learning from the incident and improving the risk management strategy, but it is usually done after the incident has occurred and resolved, not before.
References = Key Risk Indicators: Definition, Examples, and Best Practices, KRI Framework for Operational Risk Management | Workiva, What is Data Leakage? Definition, Causes, and Prevention, Incident Response Planning: Best Practices for Businesses
Question # 492
If concurrent update transactions to an account are not processed properly, which of the following will MOST likely be affected?
A.
Confidentiality
B.
Accountability
C.
Availability
D.
Integrity
Full Access
Answer:
D
Explanation:
Integrity is the property of data that ensures its accuracy, completeness, and consistency2. If concurrent update transactions to an account are not processed properly, the integrity of the data may be compromised, as it may lead to concurrency problems such as lost update, unrepeatable read, or phantom read3. These problems can cause the data to be incorrect, incomplete, or inconsistent, which may affect the reliability and validity of the data. Therefore, option D is the correct answer, as it reflects the impact of improper concurrent update transactions on the data integrity. The other options are not correct, as they do not directly relate to the effect of concurrent update transactions on the data. Option A, confidentiality, is the property of data that ensures its protection from unauthorized access or disclosure2. Concurrent update transactions do not necessarily affect the confidentiality of the data, as they do not involve exposing the data to unauthorized parties. Option B, accountability, is the property of data that ensures its traceability and auditability2. Concurrent update transactions do not necessarily affect the accountability of the data, as they do not involve losing the records or logs of the data transactions. Option C, availability, is the property of data that ensures its accessibility and usability2. Concurrent update transactions do not necessarily affect the availability of the data, as they do not involve preventing the access or use of the data.
Question # 493
A risk practitioner finds that data has been misclassified. Which of the following is the GREATEST concern?
A.
Unauthorized access
B.
Data corruption
C.
Inadequate retention schedules
D.
Data disruption
Full Access
Answer:
A
Question # 494
Which of the following should be the FIRST consideration when a business unit wants to use personal information for a purpose other than for which it was originally collected?
A.
Informed consent
B.
Cross border controls
C.
Business impact analysis (BIA)
D.
Data breach protection
Full Access
Answer:
A
Explanation:
According to the GDPR, personal data shall be collected for specified, explicit and legitimate purposes and not further processed in a manner that is incompatible with those purposes1. This means that a business unit can only use personal information for a different purpose if it has obtained the consent of the data subject, or if it has a clear legal basis or obligation to do so2. Therefore, informed consent should be the first consideration when a business unit wants to use personal information for a purpose other than for which it was originally collected.
References = GDPR Article 5 (1) (b) and Article 6 (4)1, ICO Principle (b): Purpose limitation2
Question # 495
Which of the following situations would cause the GREATEST concern around the integrity of application logs?
A.
Weak privileged access management controls
B.
Lack of a security information and event management (SIEM) system
C.
Lack of data classification policies
D.
Use of hashing algorithms
Full Access
Answer:
A
Question # 496
The MOST essential content to include in an IT risk awareness program is how to:
A.
define the IT risk framework for the organization
B.
populate risk register entries and build a risk profile for management reporting
C.
comply with the organization ' s IT risk and information security policies
D.
prioritize IT-related actions by considering risk appetite and risk tolerance
Full Access
Answer:
C
Explanation:
An IT risk awareness program shouldprimarily ensure that employees and stakeholders understand and comply with the organization ' s risk and information security policies. ISACA highlights that an awareness program must reinforce policy understanding to drive compliant and secure behavior across the organization.
===========
Question # 497
Which of the following is the MOST essential factor for managing risk in a highly dynamic environment?
A.
Ongoing sharing of information among industry peers
B.
Obtaining support from senior leadership
C.
Adhering to industry-recognized risk management standards
D.
Implementing detection and response measures
Full Access
Answer:
D
Explanation:
There is no definitive answer to this question, as different factors may be more or less important depending on the context and the nature of the risk. However, based on some web search results, one possible factor that could be considered essential for managing risk in a highly dynamic environment is D. Implementing detection and response measures.
Detection and response measures are the practices and procedures that enable an organization to identify and mitigate any potential or actual cybersecurity events that could compromise its network, systems, data, or assets. Detection and response measures can help an organization to reduce the impact and duration of a cyberattack, as well as to learn from the incident and improve its security posture and resilience. Detection and response measures can also help an organization to comply with regulatory and legal requirements, as well as to maintain its reputation and trust among its stakeholders.
Some examples of detection and response measures include:
•Using threat intelligence, user behavior analytics, and attacker behavior analytics to monitor and analyze the network activity and identify any anomalies or signs of compromise 12
•Implementing security continuous monitoring, intrusion detection and prevention systems, and antivirus and antimalware software to detect and block malicious traffic and malware 3
•Establishing incident response plans, teams, and tools to contain, eradicate, and recover from a cyberattack, as well as to communicate and coordinate with internal and external parties 45
•Conducting regular audits, assessments, and tests to evaluate the effectiveness of the detection and response measures and to identify any gaps or weaknesses 6
Therefore, implementing detection and response measures could be seen as an essential factor for managing risk in a highly dynamic environment, as it can help an organization to protect its critical assets and functions, and to respond quickly and effectively to any emerging or evolving threats.
Question # 498
A deficient control has been identified which could result in great harm to an organization should a low frequency threat event occur. When communicating the associated risk to senior management the risk practitioner should explain:
A.
mitigation plans for threat events should be prepared in the current planning period.
B.
this risk scenario is equivalent to more frequent but lower impact risk scenarios.
C.
the current level of risk is within tolerance.
D.
an increase in threat events could cause a loss sooner than anticipated.
Full Access
Answer:
A
Explanation:
The risk practitioner should explain to senior management that mitigation plans for threat events should be prepared in the current planning period, as this would demonstrate a proactive and responsible approach to risk management. Mitigation plans are documents that outline the actions and resources needed to reduce the likelihood and/or impact of a specific risk scenario. Mitigation plans should include the following elements:
Risk scenario description and risk ID
Risk owner and other stakeholders
Risk response strategy and objectives
Risk response actions and tasks
Resources, costs, and benefits
Roles and responsibilities
Timeline and milestones
Performance indicators and monitoring mechanisms
Contingency plans and triggers
Mitigation plans help to address the gap between the current and desired risk levels and align the risk response with the organizational risk appetite and objectives. Mitigation plans also facilitate the communication, coordination, and collaboration among the risk owners and other stakeholders involved in the risk response process. Mitigation plans should be prepared in the current planning period, as this would allow the organization to act timely and effectively in the event of a low frequency threat event. Preparing mitigation plans in advance would also help to avoid or minimize the potential harm to the organization and its reputation.
The other options are not the best ways to communicate the associated risk to senior management. Explaining that this risk scenario is equivalent to more frequent but lower impact risk scenarios may not accurately reflect the true nature and severity of the risk. Explaining that the current level of risk is within tolerance may not convey the urgency and importance of addressing the risk. Explaining that an increase in threat events could cause a loss sooner than anticipated may not provide a clear and actionable solution for the risk. References = Four steps for managing risk at the CEO level, IT Risk Resources | ISACA, How to Communicate Risk to Stakeholders | Anitian
Question # 499
An organization wants to develop a strategy to mitigate the risk associated with unethical actions by stakeholders. Which of the following should be done FIRST?
A.
Provide incentives for whistleblowers to report unethical actions
B.
Communicate sanctions and penalties for unethical actions
C.
Develop company-wide training on business ethics
D.
Create a policy regarding ethical behavior
Full Access
Answer:
D
Explanation:
The first step in establishing an ethical governance culture is tocreate a clear and formal policyoutlining acceptable behavior and consequences for violations.
ISACA guidance:
“Developing and approving an enterprise code of ethics or ethical policy establishes the foundation for enforcing ethical conduct and guiding all subsequent training and enforcement activities.â€
Training and enforcement follow policy creation.
Therefore,D. Create a policy regarding ethical behavioris correct.
CRISC Reference:Domain 1 – IT Risk Governance, Topic: Ethics and Governance Policies.
Question # 500
From an IT risk perspective, which of the following has the GREATEST impact on organizational strategy?
A.
Complexity of IT architecture
B.
Changes in IT risk tolerance
C.
Complexity of recovery plans
D.
Methodology for IT risk identification
Full Access
Answer:
B
Explanation:
The correct answer isBbecause changes inIT risk tolerancehave the strongest influence on organizational strategy. Risk tolerance affects how much uncertainty the enterprise is willing to accept in pursuing objectives, and this directly shapes strategic decisions, priorities, investments, and response choices. In CRISC terms, governance and risk management must align with enterprise goals, objectives, and business requirements; therefore, when risk tolerance changes, organizational strategy is impacted at the highest level.
The other options are less significant from a strategic perspective:
A. Complexity of IT architecturemainly affects implementation and operational management.
C. Complexity of recovery plansis important for resilience and continuity, but it is not the primary strategic driver.
D. Methodology for IT risk identificationis a process consideration and does not influence enterprise strategy as much as a change in tolerance levels.
Exact Extracts supporting the answer:
“When selecting a risk response technique the foremost consideration should be the enterprise goals and objectives.â€
“The most important aspect for an effective IT risk management process is aligning with enterprise risk management.â€
“The primary goal of an enterprise’s IT risk management process is to protect the enterprise and its ability to perform its mission.â€
“For successful IT delivery against business requirements it ' s crucial that risk appetite be aligned with business objectives.â€
“Risk tolerance is the permissible deviation from declared risk appetite levels in an enterprise.â€
Taken together, these extracts show that risk tolerance and risk appetite are directly linked to business objectives and enterprise decision-making. Because strategy is driven by those objectives, a change in risk tolerance has the greatest impact on organizational strategy.
Question # 501
An organization ' s capability to implement a risk management framework is PRIMARILY influenced by the:
A.
guidance of the risk practitioner.
B.
competence of the staff involved.
C.
approval of senior management.
D.
maturity of its risk culture.
Full Access
Answer:
D
Explanation:
The factor that primarily influences an organization’s capability to implement a risk management framework is the maturity of its risk culture, as it reflects the degree of awareness, understanding, and commitment of the organization’s stakeholders towards the risk management objectives, values, and practices, and affects the adoption and integration of the risk management framework across the organization. The other options are not the primary factors, as they are more related to the guidance, competence, or approval of the risk management framework, respectively, rather than the influence of the risk management framework. References = CRISC Review Manual, 7th Edition, page 99.
Question # 502
What is the BEST recommendation to reduce the risk associated with potential system compromise when a vendor stops releasing security patches and updates for a business-critical legacy system?
A.
Segment the system on its own network.
B.
Ensure regular backups take place.
C.
Virtualize the system in the cloud.
D.
Install antivirus software on the system.
Full Access
Answer:
A
Explanation:
The best recommendation to reduce the risk associated with potential system compromise when a vendor stops releasing security patches and updates for a business-critical legacy system is to segment the system on its own network. Network segmentation is the process of dividing a network into smaller subnetworks or segments, based on different criteria, such as function, location, or security level. Network segmentation helps to isolate the system from the rest of the network, and limit the exposure and access to the system. Network segmentation also helps to improve the performance and security of the network, by reducing the network traffic and congestion, and enhancing the monitoring and control capabilities. The other options are not as effective as segmenting the system on its own network, although they may provide some additional protection or recovery options. Ensuring regular backups take place, virtualizing the system in the cloud, and installing antivirus software on the system are all measures that can helpto reduce the risk of data loss or system damage, but they do not address the root cause of the risk, which is the lack of security patches and updates for the system. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.1, page 3-11.
Question # 503
Which of the following BEST describes the role of the IT risk profile in strategic IT-related decisions?
A.
It compares performance levels of IT assets to value delivered.
B.
It facilitates the alignment of strategic IT objectives to business objectives.
C.
It provides input to business managers when preparing a business case for new IT projects.
D.
It helps assess the effects of IT decisions on risk exposure
Full Access
Answer:
D
Explanation:
An IT risk profile is a document that summarizes the IT-related risks that an organization faces, as well as the information and actions related to those risks, such as the risk description, assessment, response, status, and owner. An IT risk profile is a valuable tool for managing and communicating IT risks and their impact on the organization’s objectives and operations. The best description of the role of the IT risk profile in strategic IT-related decisions is that it helps assess the effects of IT decisions on risk exposure. This means that the IT risk profile can help toevaluate the potential consequences and implications of different IT choices or actions on the level and nature of the IT risks that the organization faces. The IT risk profile can also help to identify and address the gaps or opportunities for improvement in the IT risk management process and performance. The other options are not the best descriptions of the role of the IT risk profile in strategic IT-related decisions, although they may be related or beneficial. Comparing performance levels of IT assets to value delivered is a technique to measure and optimize the efficiency and effectiveness of the IT resources and activities that support the organization’s goals and needs. However, this technique does not necessarily involve the IT risk profile, as it focuses on the output and outcome of the IT assets, not the input and impact of the IT risks. Facilitating the alignment of strategic IT objectives to business objectives is a technique toensure that the IT strategy and plans are consistent and compatible with the organization’s vision, mission, strategy, and objectives. However, this technique does not depend on the IT risk profile, as it focuses on the direction and purpose of the IT objectives, not the probability and threat of the IT risks. Providing input to business managers when preparing a business case for new IT projects is a technique to support and justify the initiation and implementation of new IT initiatives that can create value or solve problems for the organization. However, this technique does not require the IT risk profile, as it focuses on the cost and benefit of the IT projects, not the risk and response of the IT risks. References = CRISC Review Manual, pages 38-391; CRISC Review Questions, Answers & Explanations Manual, page 962; IT Risk Management Guide for 2022 | CIO Insight3; IT Risk Management Process, Frameworks & Templates4
Question # 504
An organization allows programmers to change production systems in emergency situations. Which of the following is the BEST control?
A.
Implementing an emergency change authorization process
B.
Periodically reviewing operator logs
C.
Limiting the number of super users
D.
Reviewing the programmers ' emergency change reports
Full Access
Answer:
A
Explanation:
Implementing an emergency change authorization process is the best control for an organization that allows programmers to change production systems in emergency situations, because it helps to ensure that the changes are justified, approved, documented, and tested before they are implemented, and that they are monitored and reviewed after they are implemented. An emergency change is a change that is required to resolve or prevent a critical issue or incident that may affect the availability, performance, or security of the production systems. A production system is a system that is used to support or enable the operational or business functions or processes of the organization. An emergency change authorization process is a process that defines the roles and responsibilities, criteria and procedures, and tools and techniques for managing and controlling the emergency changes. Implementing an emergency change authorization process is the best control, as it helps to minimize the risks and impacts of theemergency changes, and to maintain the integrity and reliability of the production systems. Periodically reviewing operator logs, limiting the number of super users, and reviewing the programmers’ emergency change reports are all possible controls for an organization that allows programmers to change production systems in emergency situations, but they are not the best control, as they do not provide a comprehensive and consistent approach to the emergency change management. References = Risk and Information Systems Control Study Manual, Chapter 5, Section 5.4.1, page 208
Question # 505
Which of the following controls BEST enables an organization to ensure a complete and accurate IT asset inventory?
A.
Prohibiting the use of personal devices for business
B.
Performing network scanning for unknown devices
C.
Requesting an asset list from business owners
D.
Documenting asset configuration baselines
Full Access
Answer:
B
Explanation:
 IT asset inventory is the process of tracking and managing the financial, physical, licensing, and contractual aspects of IT assets throughout their life cycle1. IT assets include hardware, software, and network components that an organization values and uses to achieve its objectives2. A complete and accurate IT asset inventory can help an organization to optimize its IT budget, reduce security risks, ensure compliance, and improve performance3.
One of the best controls to enable an organization to ensure a complete and accurate IT asset inventory is performing network scanning for unknown devices. Network scanning is the process of identifying and collecting information about the devices connected to a network, such as their IP addresses, operating systems, open ports, services, and vulnerabilities4. Network scanning can help an organization to:
Discover and inventory all the IT assets on the network, including those that are unauthorized, unmanaged, or hidden
Detect and remove any rogue or malicious devices that may pose a threat to the network security or performance
Update and verify the asset inventory data regularly and automatically, and alert on any changes or discrepancies
Support the asset lifecycle management and maintenance activities, such as patching, upgrading, or retiring assets5
References = IT Asset Valuation, Risk Assessment and Control Implementation Model, ITAM: The ultimate guide to IT asset management, Navigating Security Threats with IT Inventory Management, Network Scanning - Wikipedia, 8 Best IT Asset Management Software (2024)
Question # 506
Which of the following BEST enables the integration of IT risk management across an organization?
A.
Enterprise risk management (ERM) framework
B.
Enterprise-wide risk awareness training
C.
Robust risk reporting practices
D.
Risk management policies
Full Access
Answer:
A
Explanation:
ï‚· Understanding the Question:
The question asks what best enables the integration of IT risk management across an organization.
ï‚· Analyzing the Options:
A. Enterprise risk management (ERM) framework:Provides a comprehensive approach to integrating risk management across the entire organization.
B. Enterprise-wide risk awareness training:Important for education but doesn ' t ensure integration.
C. Robust risk reporting practices:Crucial for communication but not integration.
D. Risk management policies:Necessary but need to be part of an overall framework for effective integration.
ï‚·
ERM Framework:An ERM framework ensures that risk management practices are standardized and integrated throughout the organization. It aligns risk management with business objectives, ensuring that IT risk is considered within the broader context of enterprise risk.
Comprehensive Approach:ERM covers all aspects of risk, including IT, and facilitates a unified approach to managing risk across all departments and levels.
[References:, CRISC Review Manual, Chapter 1: Governance, details the role of an ERM framework in integrating risk management practices across an organization​​., , , , , , , , , , , , , , ]
Question # 507
Which of the following MUST be captured in a risk treatment plan?
A.
Risk owner
B.
Senior management
C.
Risk register details
D.
Risk financial impact
Full Access
Answer:
A
Explanation:
Arisk treatment plan(sometimes called a risk response plan) describes how selected risk treatments will be implemented, by whom, and by when. For the plan to be actionable and enforceable, every significant risk and its treatment must have a clearly assignedrisk owner.
CRISC guidance emphasizes that:
Accountability for risk treatment lies with the risk owner.
A risk treatment planprimarily provides treatment for identified risk that exceeds risk tolerance and should specify responsibility for implementing the chosen risk treatment.
Ensuring accountability and ownership is critical for the effectiveness of the risk management program.
While items such as financial impact and risk register references are useful supporting information, theone element that must be presentfor each treated risk is the person or roleresponsiblefor making sure the treatment is implemented and monitored.
Therefore:
A. Risk owner— REQUIRED in every risk treatment plan entry.
B. “Senior management†is too generic; they may approve the plan but are not always the specific treatment owners.
C. “Risk register details†are normally linked to or referenced, but they are not the keymust-havefield for effective execution.
D. “Risk financial impact†is important for prioritization and cost–benefit analysis, but without an owner, nothing guarantees action.
This is consistent with CRISC’s treatment-plan guidance that risk treatment plans“primarily specify the responsibility for implementing the chosen risk treatment and provide treatment for identified risk that exceeds risk tolerance.â€
Question # 508
Which of the following is MOST important for a risk practitioner to verify when evaluating the effectiveness of an organization ' s existing controls?
A.
Senior management has approved the control design.
B.
Inherent risk has been reduced from original levels.
C.
Residual risk remains within acceptable levels.
D.
Costs for control maintenance are reasonable.
Full Access
Answer:
C
Explanation:
Residual risk is the risk that remains after the implementation of controls. It is important for a risk practitioner to verify that the residual risk is within the acceptable levels defined by the enterprise’s risk appetite and tolerance. This ensures that the controls are effective in reducing the risk exposure to an acceptable level and align with the enterprise’s objectives and strategy. References = CRISC Review Manual 27th Edition, page 131. Most Asked CRISC Exam Questions and Answers.
Question # 509
A global company s business continuity plan (BCP) requires the transfer of its customer information….
event of a disaster. Which of the following should be the MOST important risk consideration?
A.
The difference In the management practices between each company
B.
The cloud computing environment is shared with another company
C.
The lack of a service level agreement (SLA) in the vendor contract
D.
The organizational culture differences between each country
Full Access
Answer:
B
Explanation:
The most important risk consideration when the global company’s business continuity plan (BCP) requires the transfer of its customer information to a cloud computing environment in the event of a disaster is that the cloud computing environment is shared with another company. A cloud computing environment is a service model that provides on-demand access to a shared pool of computing resources, such as servers, storage, networks, and applications. A shared cloud computing environment means that the same computing resources are used by multiple customers or tenants, and that the data and activities of one customer may affect or be affected by the data and activities of another customer. This may pose a significant risk to the security, privacy, and availability of the customer information, as it may be exposed, accessed, modified, or deleted by unauthorized or malicious parties. The other options are not as important as the cloud computing environment being shared with another company, as they are related to the differences, agreements, or cultures of the company or the country, not the environment or the platform of the customer information transfer. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.3: IT Risk Response Implementation, page 145.
Question # 510
A Software as a Service (SaaS) provider has determined that the risk of a client ' s sensitive data being compromised is low. Which of the following is the client ' s BEST course of action?
A.
Implement additional controls to address the risk
B.
Accept the risk based on the provider ' s risk assessment
C.
Review the provider ' s independent audit results
D.
Ensure the contract includes breach notification requirements
Full Access
Answer:
C
Explanation:
Instead of relying solely on the provider’s internal assessment, the client should validate control effectiveness throughindependent audit reports(e.g., SOC 2 Type II). These provide third-party assurance.
[Reference:CRISC Manual – Domain 3, Slide 304-305, , , , ]
Question # 511
Which of the following roles is BEST suited to help a risk practitioner understand the impact of IT-related events on business objectives?
A.
IT management
B.
Internal audit
C.
Process owners
D.
Senior management
Full Access
Answer:
C
Explanation:
 Process owners are the best suited to help a risk practitioner understand the impact of IT-related events on business objectives, as they have the responsibility and authority over the design, execution, and performance of business processes. Process owners are also accountable for the risks and controls associated with their processes, and they can provide valuable input and feedback on the likelihood and impact of IT-related events on the process outcomes and objectives.
The other options are not the best suited to help a risk practitioner understand the impact of IT-related events on business objectives. IT management is responsible for the delivery and support of IT services and solutions, but they may not have the full visibility or understanding of the business objectives and processes. Internal audit is responsible for providing independent and objective assurance and consulting services on the effectiveness and efficiency of governance, risk management, and control processes, but they may not have the direct involvement or influence on the business objectives and processes. Senior management is responsible for settingthe strategic direction and objectives of the organization, but they maynot have the detailed knowledge or experience of the business processes and their risks and controls. References = IT Risk Manager: Skills and Roles & Responsibilities, IT Risk Resources | ISACA, Managing information technology risk | Business Queensland
Question # 512
Which of the following is the MOST significant benefit of using quantitative risk analysis instead of qualitative risk analysis?
A.
Minimized time to completion
B.
Decreased structure
C.
Minimized subjectivity
D.
Decreased cost
Full Access
Answer:
C
Explanation:
Quantitative risk analysis provides numerical values for likelihood and impact, thereby reducing subjectivity. It enables risk practitioners to perform cost-benefit analysis and make data-driven decisions. Though time-consuming, its objectivity is its major advantage over qualitative methods.
[Reference:CRISC Manual – Domain 2, Slide 186-187, , , , ]
Question # 513
The PRIMARY purpose of using control metrics is to evaluate the:
A.
amount of risk reduced by compensating controls.
B.
amount of risk present in the organization.
C.
variance against objectives.
D.
number of incidents.
Full Access
Answer:
C
Explanation:
 The PRIMARY purpose of using control metrics is to evaluate the variance against objectives, because control metrics are measures that indicate the performance and effectiveness of the controls in achieving the desired outcomes and goals. Control metrics can help to identify and quantify the gaps or deviations between the actual and expected results of the controls, and to provide feedback and improvement for the control design and implementation. The other options are not the primary purpose, because:
Option A: Amount of risk reduced by compensating controls is a result of using control metrics, but not the primary purpose. Compensating controls are controls that provide an alternative or additional level of protection or assurance when the primary or preferred controls are not feasible or effective. Control metrics can help to measure and monitor the amount of risk reduced by compensating controls, but they are not the only or the most important measure of the control performance and effectiveness.
Option B: Amount of risk present in the organization is an input to using control metrics, but not the primary purpose. The amount of risk present in the organization is the level of exposure and uncertainty that the organization faces in pursuing its objectives and goals. Control metrics can help to assess and report the amount of risk present in the organization, but they are not the only or the most important measure of the risk profile and exposure.
Option D: Number of incidents is a source of using control metrics, but not the primary purpose. Incidents are events or occurrences that disrupt or threaten the normal operations or security of the organization. Control metrics can help to analyze and respond to the number of incidents, but they are not the only or the most important measure of the incident management andresolution. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 120.
Question # 514
Which of the following is the MOST important consideration when developing risk strategies?
A.
Organization ' s industry sector
B.
Long-term organizational goals
C.
Concerns of the business process owners
D.
History of risk events
Full Access
Answer:
B
Explanation:
Risk strategies are the plans and actions that an organization adopts to manage its risks and to achieve its objectives. Risk strategies should be aligned with the organization’s vision, mission, values, and culture, as well as its internal and external environment. The most important consideration when developing risk strategies is the long-term organizational goals, meaning that the risk strategies should support and enable the organization to pursue and attain its desired future state and outcomes. The long-term organizational goals should guide the risk identification, assessment, response, and monitoring processes, as well as the risk appetite and tolerance levels. The long-term organizational goals should also be communicated and cascaded throughout the organization to ensure the risk awareness and engagement of all stakeholders. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, p. 27-28
Question # 515
Which of the following is the MOST effective way to integrate risk and compliance management?
A.
Embedding risk management into compliance decision-making
B.
Designing corrective actions to improve risk response capabilities
C.
Embedding risk management into processes that are aligned with business drivers
D.
Conducting regular self-assessments to verify compliance
Full Access
Answer:
C
Explanation:
Embedding risk management into processes that are aligned with business drivers is the most effective way to integrate risk and compliance management, as it ensures that the risk management objectives and activities are consistent and supportive of the enterprise’s strategic goals and values. It also enables the identification and management of risks and compliance requirements across the enterprise, and the optimization of risk and compliance resources and performance. Embedding risk management into compliance decision-making, designingcorrective actions to improve risk response capabilities, and conducting regular self-assessments to verify compliance are not ways to integrate risk and compliance management, but rather components or outcomes of the risk and compliance management process. References = CRISC Practice Quiz and Exam Prep; CRISC: Certified in Risk & Information Systems Control Sample Questions, question 202.
Question # 516
From a risk management perspective, which of the following is the PRIMARY benefit of using automated system configuration validation tools?
A.
Residual risk is reduced.
B.
Staff costs are reduced.
C.
Operational costs are reduced.
D.
Inherent risk is reduced.
Full Access
Answer:
D
Explanation:
From a risk management perspective, the primary benefit of using automated system configuration validation tools is that they reduce the inherent risk, which is the risk that exists before any controls are applied. Automated system configuration validation tools can help to ensure that the system settings are consistent, compliant, and secure, and that they match the predefined standards and policies. This can reduce the likelihood and impact of errors, misconfigurations, vulnerabilities, or deviations that may compromise the system’s functionality, performance, or integrity. The other options are not the primary benefits of using automated system configuration validation tools, although they may be secondary benefits or outcomes of doing so. Residual risk is the risk that remains after the controls are applied, and it may not be directly affected by the automated system configuration validation tools. Staff costs and operational costs are related to the efficiency and economy of the system configuration process, but they are not the main risk management objectives. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk Response, page 150.
Question # 517
Which of the following is MOST useful for measuring the existing risk management process against a desired state?
A.
Balanced scorecard
B.
Risk management framework
C.
Capability maturity model
D.
Risk scenario analysis
Full Access
Answer:
C
Explanation:
The most useful tool for measuring the existing risk management process against a desired state is the capability maturity model, as it provides a structured and standardized way to assess the current and target levels of maturity, performance, and effectiveness of the risk management process, and to identify the gaps and improvement opportunities. The balanced scorecard, the risk management framework, and the risk scenario analysis are not the most useful tools, as they are more related to the evaluation, design, or identification of the risk management process, respectively, rather than the measurement of the risk management process. References = CRISC Review Manual, 7th Edition, page 154.
Question # 518
An organization uses a vendor to destroy hard drives. Which of the following would BEST reduce the risk of data leakage?
A.
Require the vendor to degauss the hard drives
B.
Implement an encryption policy for the hard drives.
C.
Require confirmation of destruction from the IT manager.
D.
Use an accredited vendor to dispose of the hard drives.
Full Access
Answer:
D
Explanation:
Data leakage is the unauthorized or accidental disclosure of sensitive or confidential data to unauthorized parties. Data leakage can cause serious damages or losses to the organization, such as data breaches, fines, lawsuits, reputational harm, or loss of customer trust. Data leakage can occur due to various reasons, such as human errors, malicious attacks, or inadequate controls1.
An organization that uses a vendor to destroy hard drives faces a risk of data leakage, as the vendor may not properly or securely destroy the hard drives, or may access or misuse the data stored on them. The best way to reduce this risk is to use an accredited vendor to dispose of the hard drives, because it means that the vendor:
Has been certified or verified by a reputable or recognized authority or organization, such as ISACA, NAID, or R2, to provide hard drive destruction services
Follows the industry standards and best practices for hard drive destruction, such as NIST 800-88 or DoD 5220.22-M, and ensures the compliance with the legal and regulatory requirements, such as HIPAA, PCI DSS, or GDPR
Provides a secure and transparent process for hard drive destruction, such as using a specialized shredder, issuing a certificate of destruction, or allowing the customer to witness the destruction
Maintains a high level of professionalism and integrity, and does not compromise the confidentiality or security of the customer’s data234
The other options are not the best ways to reduce the risk of data leakage, but rather some of the steps or aspects of hard drive destruction. Require the vendor to degauss the hard drives is a step that can help to erase the data on the hard drives by using a strong magnetic field. However,degaussing may not be effective or reliable for some types of hard drives, such as solid state drives (SSDs), and it may not prevent the vendor from accessing or misusing the data before degaussing5. Implement an encryption policy for the hard drives is an aspect that can help to protect the data on the hard drives by using a cryptographic algorithm to make it unreadable without a key. However, encryption may not be sufficient or applicable for some types of data, such as metadata, and it may not prevent the vendor from accessing or misusing the key or the encrypted data6. Require confirmation of destruction from the IT manager is a step that can help to verify that the hard drives have been destroyed by the vendor, and to document the process and the outcome. However, confirmation of destruction may not be accurate or authentic, and it may not prevent the vendor from accessing or misusing the data before destruction7. References =
Data Leakage - ISACA
Hard Drive Shredding Services | Hard Drive Destruction & Disposal
Hard Drive Shredding and Destruction Service | CompuCycle
Electronic Destruction & Recycling | Shred Nations
Degaussing - ISACA
Encryption - ISACA
Certificate of Destruction - ISACA
[CRISC Review Manual, 7th Edition]
Question # 519
Which of the following should be implemented to BEST mitigate the risk associated with infrastructure updates?
A.
Role-specific technical training
B.
Change management audit
C.
Change control process
D.
Risk assessment
Full Access
Answer:
C
Explanation:
The best way to mitigate the risk associated with infrastructure updates is to implement a change control process. A change control process is a set of procedures that ensures that any changes to the infrastructure are planned, approved, tested, implemented, and documented in a consistent and controlled manner. A change control process helps to reduce the risk of errors, conflicts, disruptions, or security breaches that could result from infrastructure updates. A change controlprocess also helps to monitor and evaluate the impact and effectiveness of the changes, and to ensure that they align with the enterprise’s objectives and requirements. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.3.1, page 1391
Question # 520
An organization is implementing Zero Trust architecture to improve its security posture. Which of the following is the MOST important input to develop the architecture?
A.
Cloud services risk assessments
B.
The organization ' s threat model
C.
Access control logs
D.
Multi-factor authentication (MFA) architecture
Full Access
Answer:
B
Question # 521
Which of the following is MOST important to consider when determining a recovery time objective (RTO)?
A.
Time between backups for critical data
B.
Sensitivity of business data involved
C.
Cost of downtime due to a disaster
D.
Maximum tolerable data loss after an incident
Full Access
Answer:
C
Explanation:
The Recovery Time Objective (RTO) is the maximum acceptable length of time that a system can be down after a failure or disaster. Determining the RTO involves assessing the cost of downtime and its impact on business operations to ensure that recovery strategies are cost-effective and aligned with business needs.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 3: Risk Response and Reporting, Section: Business Continuity and Disaster Recovery., , , , , , , ]
Question # 522
Which of the following would be considered a vulnerability?
A.
Delayed removal of employee access
B.
Authorized administrative access to HR files
C.
Corruption of files due to malware
D.
Server downtime due to a denial of service (DoS) attack
Full Access
Answer:
A
Explanation:
According to the CRISC Review Manual (Digital Version), a vulnerability is a flaw or weakness in an asset’s design, implementation, or operation and management that could be exploited by a threat. A delayed removal of employee access is a vulnerability, as it allows former employees to retain access to the organization’s IT assets and processes, which could lead to unauthorized disclosure, modification, or destruction of data or resources. A delayed removal of employee access could be caused by poor personnel management, lack of security awareness, or inadequate access control policies and procedures.
References = CRISC Review Manual (Digital Version), Chapter 1: IT Risk Identification, Section 1.5: IT Risk Identification Methods and Techniques, pp. 32-331
Question # 523
Which of the following is the MOST important consideration for a risk practitioner when making a system implementation go-live recommendation?
A.
Completeness of system documentation
B.
Results of end user acceptance testing
C.
Variances between planned and actual cost
D.
availability of in-house resources
Full Access
Answer:
B
Explanation:
End user acceptance testing is a process that verifies that a system or service meets the requirements and expectations of the end users, who are the actual or potential customers or beneficiaries of the system or service. End user acceptance testing is the final stage of testing before the system or service is deployed or released to the production environment. The results of end user acceptance testing are the most important consideration for a risk practitioner when making a system implementation go-live recommendation, as they indicate the quality, functionality, usability, and reliability of the system or service from the end user perspective. The results of end user acceptance testing can help to identify and resolve any defects, errors, or issues that may affect the performance, satisfaction, or acceptance of the system or service by the end users. The results of end user acceptance testing can also help to evaluate the benefits, value, and risks of the system or service for the end users and the organization. The other options are not the most important consideration for a risk practitioner when making a system implementation go-live recommendation, although they may be relevant and useful. The completeness of system documentation is a factor that affects the maintainability, supportability, and auditability of the system or service, but it does not measure the end user experience or satisfaction. The variances between planned and actual cost is a measure of the efficiency and budget management of the system or service development or implementation, but it does not reflect the end user needs or expectations. The availability of in-house resources is a resource that supports the system or service delivery and operation, but it does not ensure the end user acceptance or approval. References = CRISC Review Manual, pages 180-1811; CRISC Review Questions, Answers & Explanations Manual, page 87
Question # 524
An organization ' s finance team is proposing the adoption of a blockchain technology to provide a secure method for moving funds. Which of the following should the risk practitioner do FIRST?
A.
Recommend permissionless blockchain.
B.
Perform a risk assessment.
C.
Perform a business impact analysis (BIA).
D.
Recommend permissioned blockchain.
Full Access
Answer:
B
Explanation:
Before selecting technologies or deployment models, a risk assessment should be conducted to evaluate potential threats, vulnerabilities, and controls. This ensures the technology aligns with the risk appetite and regulatory requirements of the organization.
[Reference:CRISC Manual – Domain 2, Slide 178-180, 250, , , , ]
Question # 525
A compensating control is MOST appropriate when:
A.
Management wants to increase the number of controls.
B.
A vulnerability is identified.
C.
Existing controls are inadequate.
D.
A key control is already in place and operating effectively.
Full Access
Answer:
C
Explanation:
A compensating control addresses risk when the primary control cannot meet the required objectives due to practical constraints.
[Reference:CRISC Manual – Domain 3, Slide 345, , , , ]
Question # 526
Which of the following should be the risk practitioner s FIRST course of action when an organization has decided to expand into new product areas?
A.
Identify any new business objectives with stakeholders.
B.
Present a business case for new controls to stakeholders.
C.
Revise the organization ' s risk and control policy.
D.
Review existing risk scenarios with stakeholders.
Full Access
Answer:
A
Explanation:
The first course of action for the risk practitioner when an organization has decided to expand into new product areas is to identify any new business objectives with stakeholders. Business objectives are the specific, measurable, achievable, relevant, and time-bound (SMART) goals that the organization aims to accomplish through its products and services. Stakeholders are the parties who have an interest or influence in the organization and its products and services, such as customers, employees, shareholders, suppliers, regulators, or competitors. Identifying any new business objectives with stakeholders is the first course of action, because it helps to understand and define the purpose, scope, and criteria of the new product areas, and to align them with the organization’s vision, mission, and strategy. Identifying any new business objectives with stakeholders also helps to establish the expectations, needs, and requirements of the stakeholders, and to ensure their engagement and support for the new product areas. Identifying any newbusiness objectives with stakeholders is the basis for the subsequent risk management activities, such as identifying, analyzing, evaluating, and responding to the risks associated with the new product areas. The other options are not the first course of action, although they may be related or subsequent steps in the risk management process. Presenting a business case for new controls to stakeholders is a part of the risk response process, which involves selecting and executing the appropriate actions to reduce, avoid, share, or exploit the risks associated with the new product areas. Presenting a business case for new controls to stakeholders can help to justify and communicate the value and impact of the new controls, and to obtain the approval and resources for implementing them. However, this is not the first course of action, as it depends on the identification and prioritization of the business objectives and the risks. Revising the organization’s risk and control policy is a part of the risk governance process, which involves defining and updating the rules and guidelines for managing the risks and the controls associatedwith the new product areas. Revising the organization’s risk and control policy can help to ensure the consistency and effectiveness of the risk management process, and to comply with the relevant laws and regulations. However, this is not the first course of action, as it follows the identification and assessment of the business objectives and the risks. Reviewing existing risk scenarios with stakeholders is a part of the risk monitoring and review process, which involves evaluating and improving the performance and outcomes of the risk management process for the new product areas. Reviewing existing risk scenarios with stakeholders can help to identify and address any changes or issues in the risk levels or the risk responses, and to provide feedback and learning for the risk management process. However, this is not the first course of action, as it requires the identification and analysis of the business objectives and the risks. References = Risk Scenarios Toolkit - ISACA, How to Write Strong Risk Scenarios and Statements - ISACA, The Role of Executive Management in ERM - Corporate Compliance Insights
Question # 527
Which of the following BEST facilitates the identification of emerging risk?
A.
Performing scenario-based assessments
B.
Reviewing audit reports annually
C.
Conducting root cause analyses
D.
Engaging a risk-focused audit team
Full Access
Answer:
A
Explanation:
Performing scenario-based assessments is a proactive approach that allows organizations to anticipate potential future events and assess their impact. This method helps in identifying emerging risks by exploring hypothetical situations and their possible outcomes. It enables organizations to prepare for unforeseen events by understanding how different scenarios could affect their operations and objectives.​
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 2: IT Risk Assessment, Section: Risk Identification Techniques.​, , , , , , , , , ]
Question # 528
Which of the following provides the BEST evidence of the effectiveness of an organization ' s account provisioning process?
A.
User provisioning
B.
Role-based access controls
C.
Security log monitoring
D.
Entitlement reviews
Full Access
Answer:
D
Explanation:
An organization’s account provisioning process is the process of creating, modifying, or deleting user accounts and access rights for the organization’s information systems and resources. It involves defining the access requirements, policies, and standards, and implementing and enforcing them across the organization.
The best evidence of the effectiveness of an organization’s account provisioning process is entitlement reviews, which are the periodic or regular reviews and validations of the user accounts and access rights that are granted or assigned to the users or entities that interact with the organization’s information systems and resources. Entitlement reviews can provide assurance and verification that the account provisioning process is accurate, consistent, and compliant, and that it meets the organization’s security and business objectives and requirements.
Entitlement reviews can be performed using various techniques, such as automated tools, reports, audits, surveys, etc. Entitlement reviews can also be integrated with the organization’s governance, risk management, and compliance functions, and aligned with the organization’s policies and standards.
The other options are not the best evidence of the effectiveness of an organization’s account provisioning process, because they do not provide the same level of assurance and verification that the account provisioning process is accurate, consistent, and compliant, and that it meets the organization’s security and business objectives and requirements.
User provisioning is the process of creating, modifying, or deleting user accounts and access rights for a specific user or entity, based on their identity, role, or function in the organization. User provisioning is an important part of the account provisioning process, but it is not the best evidence of the effectiveness of the account provisioning process, because it does not indicate whether the user accounts and access rights are appropriate and authorized, and whether they comply with the organization’s policies and standards.
Role-based access controls are the controls that grant or restrict user accounts and access rights based on the predefined roles or functions that the users or entities perform or assume in the organization. Role-based access controls are an important part of the account provisioningprocess, but they are not the best evidence of the effectiveness of the account provisioning process, because they do not indicate whether the roles or functions are defined and assigned correctly and consistently, and whether they comply with the organization’s policies and standards.
Security log monitoring is the process of collecting, analyzing, and reporting on the security events or activities that are recorded or logged by the organization’s information systems and resources. Security log monitoring is an important part of the account provisioning process, but it is not the best evidence of the effectiveness of the account provisioning process, because it does not indicate whether the security events or activities are legitimate or authorized, and whether they comply with the organization’s policies and standards. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 173
CRISC Practice Quiz and Exam Prep
Question # 529
Which of the following is the BEST control for a large organization to implement to effectively mitigate risk related to fraudulent transactions?
A.
Segregation of duties
B.
Monetary approval limits
C.
Clear roles and responsibilities
D.
Password policies
Full Access
Answer:
A
Explanation:
Segregation of duties is a key control for preventing and detecting fraudulent transactions, especially in a large organization where there are many employees and transactions involved. Segregation of duties means that no single person has the authority or ability to initiate, approve, execute, and record a transaction without the involvement or oversight of another person. This reduces the opportunity and incentive for fraud, as well as the risk of errors or omissions. Segregation of duties also facilitates the detection of fraud by creating an audit trail and increasing the likelihood of whistleblowing.
The other options are not as effective as segregation of duties for mitigating risk related to fraudulent transactions. Monetary approval limits (B) are useful for controlling the amount and frequency of transactions, but they do not prevent unauthorized or fraudulent transactions from occurring. Clear roles and responsibilities © are important for defining the expectations and accountabilities of employees, but they do not ensure that employees comply with them or that their actions are monitored and verified. Password policies (D) are essential for securing access to systems and data, but they do not prevent fraudsters from exploiting weak or compromised passwords or from using legitimate passwords for fraudulent purposes.
Question # 530
Which of the following is the GREATEST concern associated with the use of artificial intelligence (AI) language models?
A.
The model could be hacked or exploited.
B.
The model could be used to generate inaccurate content.
C.
Staff could become overly reliant on the model.
D.
It could lead to biased recommendations.
Full Access
Answer:
D
Explanation:
Biased recommendations from AI models can perpetuate or exacerbate organizational risks, especially in decision-making processes, regulatory compliance, and ethical standards. Addressing such concerns is vital under theEmerging Technology Risksdomain in risk management.
Question # 531
The MAIN purpose of having a documented risk profile is to:
A.
comply with external and internal requirements.
B.
enable well-informed decision making.
C.
prioritize investment projects.
D.
keep the risk register up-to-date.
Full Access
Answer:
B
Explanation:
According to the Risk Management Essentials, a risk profile is established to enhance senior management’s analysis and decision making related to priority setting and resource allocation. A risk profile is a description of a set of risks that an organization faces, and it helps to make the risks visible and understandable. By having a documented risk profile, an organization can identify the nature and level of the threats, assess the likelihood and impact of the risks, evaluate the effectiveness of the controls, and determine the risk appetite and tolerance. This information can help the organization to make well-informed decisions on how to manage the risks and achieve its objectives. References = Risk Management Essentials, Risk Profile: Definition, Importance for Individuals & Companies
Question # 532
Which of the following controls would BEST reduce the risk of account compromise?
A.
Enforce password changes.
B.
Enforce multi-factor authentication (MFA).
C.
Enforce role-based authentication.
D.
Enforce password encryption.
Full Access
Answer:
B
Explanation:
Multi-factor authentication (MFA)significantly reduces the risk of account compromise by requiring multiple forms of verification, such as a password and a one-time code, enhancing security beyond single-factor authentication methods.
Question # 533
An effective control environment is BEST indicated by controls that:
A.
minimize senior management ' s risk tolerance.
B.
manage risk within the organization ' s risk appetite.
C.
reduce the thresholds of key risk indicators (KRIs).
D.
are cost-effective to implement
Full Access
Answer:
B
Explanation:
 According to the CRISC Review Manual (Digital Version), an effective control environment is best indicated by controls that manage risk within the organization’s risk appetite, as this reflects the alignment of thecontrol objectives and activities with the organization’s strategic goals and risk preferences. The risk appetite is the amount and type of risk that the organization is willing to accept in pursuit of its objectives. Managing risk within the organization’s risk appetite helps to:
Balance the potential benefits and costs of risk-taking and risk response
Optimize the use of the organization’s resources and capabilities
Enhance the value and performance of the organization
Foster a risk-aware culture that supports the organization’s vision and mission
References = CRISC Review Manual (Digital Version), Chapter 2: IT Risk Assessment, Section 2.3: IT Risk Assessment Process, pp. 93-941
Question # 534
Which of the following should be the risk practitioner s PRIMARY focus when determining whether controls are adequate to mitigate risk?
A.
Sensitivity analysis
B.
Level of residual risk
C.
Cost-benefit analysis
D.
Risk appetite
Full Access
Answer:
B
Explanation:
The risk practitioner’s primary focus when determining whether controls are adequate to mitigate risk should be the level of residual risk, because this indicates the amount and type of risk that remains after applying the controls, and whether it is acceptable or not. Residual risk is the risk that is left over after the risk responseactions have been taken, such as implementing or improving controls. Controls are the measures or actions that are designed and performed to reduce the likelihood and/or impact of a risk event, or to exploit the opportunities that a risk event may create. The adequacy of controls to mitigate risk depends on how well they address the root causes or sources of the risk, and how effectively and efficiently they reduce the risk exposure and value. The level of residual risk reflects the adequacy of controls to mitigate risk, as it shows the gap between the inherent risk and the actual risk, and whether it is within the organization’s risk appetite and tolerance. The risk practitioner should focus on the level of residual risk when determining whether controls are adequate to mitigate risk, as it helps to evaluate and compare the benefits and costs of the controls, and to decide on the best risk response strategy, such as accepting, avoiding, transferring, or further reducing the risk. The other options are less important or relevant to focus on when determining whether controls are adequate to mitigate risk. Sensitivity analysis is a technique that measures how the risk value changes when one or more input variables are changed, such as the probability, impact, or control effectiveness. Sensitivity analysis can help to identify and prioritize the most influential or critical variables that affect the risk value, and to test the robustness or reliability of the risk assessment. However, sensitivity analysis does not directly indicate the adequacy of controls to mitigate risk, as it does not measure the level of residual risk or the risk acceptance criteria. Cost-benefit analysis is a technique that compares the expected benefits and costs of a control or a risk response action, and determines whether it is worthwhile or not. Cost-benefit analysis can help to justify and optimize the investment or resource allocation for the control or the risk response action, and to ensure that it is aligned with the organization’s objectives and value. However, cost-benefit analysis does not directly indicate the adequacy of controls to mitigate risk, as it does not measure the level of residual risk or the risk acceptance criteria. Risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite can help to define and communicate the organization’s risk preferences and boundaries, and to guide the risk decision-making and behavior. However, risk appetite does not directly indicate the adequacy of controls to mitigate risk, as it does not measure the level of residual risk or the actual risk performance. References = Risk IT Framework, ISACA, 2022, p. 131
Question # 535
The BEST metric to monitor the risk associated with changes deployed to production is the percentage of:
A.
changes due to emergencies.
B.
changes that cause incidents.
C.
changes not requiring user acceptance testing.
D.
personnel that have rights to make changes in production.
Full Access
Answer:
B
Explanation:
Changes deployed to production are those that affect the functionality, performance, or security of the system in a way that is visible or accessible to the end users1. These changes can introduce new risks or vulnerabilities, such as errors, bugs, compatibility issues, or unauthorized access2. Therefore, it is important to monitor the risk associated with these changes and measure how often they cause incidents in production.
One metric that can be used to monitor this risk is the percentage of changes that cause incidents in production. This metric indicates how effective the change management process is and how well the organization can prevent or mitigate potential problems caused by changes3. A high percentage of incidents indicates a high level of risk and a need for improvement in the change management process.
References = IT Change Management for SOC: Process and Best Practices, Determining and Managing Risk when Deploying Code, 6 Deployment Risks and How To Mitigate Them
Question # 536
Which of the following would cause the GREATEST concern for a risk practitioner reviewing the IT risk scenarios recorded in an organization’s IT risk register?
A.
Some IT risk scenarios have multi-year risk action plans.
B.
Several IT risk scenarios are missing assigned owners.
C.
Numerous IT risk scenarios have been granted risk acceptances.
D.
Many IT risk scenarios are categorized as avoided.
Full Access
Answer:
B
Explanation:
Assigning ownership to each risk scenario is fundamental in risk management. Without designated owners, there is a lack of accountability, which can lead to risks not being adequately managed or mitigated. The absence of assigned owners means that no one is responsible for monitoring, reporting, or addressing the risk, increasing the likelihood of adverse outcomes.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 2: IT Risk Assessment, Section: Risk Ownership., , , , , , , ]
Question # 537
Which of the following events is MOST likely to trigger the need to conduct a risk assessment?
A.
An incident resulting in data loss
B.
Changes in executive management
C.
Updates to the information security policy
D.
Introduction of a new product line
Full Access
Answer:
D
Explanation:
Conducting a risk assessment is a critical process that helps organizations identify, evaluate, and prioritize risks that could impact their objectives. The introduction of a new product line is most likely to trigger the need for a risk assessment due to the following reasons:
Introduction of a New Product Line (Answer D):
Significance: Launching a new product involves significant changes to business processes, technologies, and possibly market dynamics. It introduces new elements that could affect the organization ' s risk profile.
Complexity and Uncertainty: New products often come with unknown risks and uncertainties. Understanding these risks is crucial to ensure they are managed effectively.
Impact on Operations: A new product can impact various facets of the organization, including production, supply chain, IT infrastructure, and customer support. Assessing risks helps in planning and mitigating potential disruptions.
Compliance and Regulatory Considerations: New products might have to comply with new regulations or standards, necessitating a review of associated risks.
Comparison with Other Options:
A. An incident resulting in data loss:
Purpose: While incidents like data loss are serious and require immediate response and investigation, they typically trigger incident management and post-incident reviews rather than a full risk assessment.
B. Changes in executive management:
Purpose: Changes in leadership can influence the strategic direction and priorities of the organization, but they do not inherently introduce new operational risks that necessitate an immediate risk assessment.
C. Updates to the information security policy:
Purpose: Policy updates are often based on previously identified risks and aim to mitigate them. They are more about adjusting controls rather than reassessing the risk landscape completely.
[References:, ISACA CRISC Review Manual, Chapter 2, "IT Risk Assessment," which highlights the importance of conducting risk assessments in response to significant organizational changes, such as the introduction of new products, which can significantly alter the risk profile of the organization. This aligns with the need to reassess risks to ensure appropriate controls and mitigation strategies are in place for new initiatives​​., , , , , , , , , , , ]
Question # 538
Which of the following is MOST important to include in a Software as a Service (SaaS) vendor agreement?
A.
An annual contract review
B.
A service level agreement (SLA)
C.
A requirement to adopt an established risk management framework
D.
A requirement to provide an independent audit report
Full Access
Answer:
B
Explanation:
A service level agreement (SLA) is a contract between a SaaS vendor and a customer that defines the quality and availability of the SaaS service, as well as the responsibilities and obligations of both parties. An SLA is most important to include in a SaaS vendor agreement because it sets the expectations and standards for the SaaS service, provides a mechanism for measuring and monitoring the serviceperformance, and establishes the remedies and penalties for service failures or breaches. An SLA can also help to mitigate the risks and liabilities associated with SaaS delivery, such as data security, privacy, compliance, and disaster recovery. The other options are not the most important to include in a SaaS vendor agreement, although they may be beneficial or desirable depending on the context and nature of the SaaS service. An annual contract review is a process of evaluating and revising the SaaS vendor agreement to reflect the changing needs and circumstances of the customer and the vendor, but it is not a mandatory or essential element of the agreement. A requirement to adopt an established risk managementframework is a way of ensuring that the SaaS vendor follows the best practices and standards for identifying, assessing, and mitigating the risks related to the SaaS service, but it is not a specific or measurable term of the agreement. A requirement to provide an independent audit report is a way of verifying and validating the SaaS vendor’s compliance with the SLA and other contractual obligations, but it is not a direct or primary component of the agreement. References = SaaS Agreements: Key Contractual Provisions, SaaS Agreement: Everything You Need to Know, Essential checklist for SaaS agreement negotiations, KeyClauses To Understand and Evaluate in SaaS Contracts, SaaS Reseller Agreement: Everything You Need to Know
Question # 539
Which of the following should be the MAIN consideration when validating an organization ' s risk appetite?
A.
Comparison against regulations
B.
Maturity of the risk culture
C.
Capacity to withstand loss
D.
Cost of risk mitigation options
Full Access
Answer:
C
Explanation:
According to the Gaining the competitive edge – measuring and assessing an organization’s risk culture article, risk appetite is the amount and type of risk that an organization is willing to accept in pursuit of its objectives. Risk appetite should be aligned with the organization’s strategy, goals, and values, and should reflect the organization’s risk culture and capabilities. One of the main considerations when validating an organization’s risk appetite is the capacity to withstand loss, which is the ability of the organization to absorb the impact of adverse events without jeopardizing its viability or reputation. The capacity to withstand loss depends on various factors, such as the financial strength, the operational resilience, the governance structure, and the stakeholder expectations of the organization. By assessing the capacity to withstand loss, the organization can determine if its risk appetite is realistic and appropriate, or if it needs to be adjusted to match its risk profile and environment. References = Gaining the competitive edge – measuring and assessing an organization’s risk culture
Question # 540
Which of the following is the BEST course of action to reduce risk impact?
A.
Create an IT security policy.
B.
Implement corrective measures.
C.
Implement detective controls.
D.
Leverage existing technology
Full Access
Answer:
B
Explanation:
To reduce risk impact, the best course of action is to implement corrective measures, which are actions taken to eliminate or minimize the negative effects of a risk event after it has occurred12.
Corrective measures can include restoring normal operations, repairing or replacing damaged assets, recovering lost data, compensating affected stakeholders, and implementing lessons learned12.
Corrective measures can reduce risk impact by minimizing the duration, severity, and scope of the consequences of a risk event, as well as preventing recurrence or escalation of similar risks in the future12.
The other options are not the best course of action to reduce risk impact, but rather different types of risk responses that may have different objectives and effects. For example:
Creating an IT security policy is an example of a preventive measure, which is an action taken to avoid or reduce the likelihood of a risk event before it occurs12. A preventive measure can reduce risk exposure, but not risk impact.
Implementing detective controls is an example of a monitoring measure, which is an action taken to identify and measure the occurrence or status of a risk event during or after it occurs12. A monitoring measure can provide timely information and feedback, but not reduce risk impact.
Leveraging existing technology is an example of a mitigation measure, which is an action taken to reduce the likelihood or impact of a risk event before it occurs12. A mitigation measure can reduce risk exposure, but not necessarily risk impact. References =
1: Risk Management Guide for Information Technology Systems, NIST Special Publication 800-30, July 2002
2: Project Risk Management Handbook, California Department of Transportation, June 2011
Question # 541
Which of the following should be the FIRST consideration when establishing a new risk governance program?
A.
Developing an ongoing awareness and training program
B.
Creating policies and standards that are easy to comprehend
C.
Embedding risk management into the organization
D.
Completing annual risk assessments on critical resources
Full Access
Answer:
C
Explanation:
The first consideration when establishing a new risk governance program is embedding risk management into the organization. Embedding risk management means integrating risk management principles and practices into the organization’s culture, values, processes, and decision-making. Embedding risk management helps to ensure that risk management is not seen as a separate or isolated activity, but as a part of the organization’s normal operations and strategic objectives. Embedding risk management also helps to create a risk-aware and risk-responsive organization, where risk management is shared and supported by all stakeholders. The other options are not the first consideration, although they may be important steps or components of the risk governance program. Developing an ongoing awareness and training program, creating policies and standards that are easy to comprehend, and completing annual risk assessments on critical resources are all activities that can help to embed risk management into the organization, but they are not the initial or primary consideration. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.2.1, page 1-8.
Question # 542
Which of the following is the BEST way to incorporate continuous monitoring in IT risk policies?
A.
Implement a governance, risk, and compliance (GRC) tool
B.
Establish a cross-functional risk steering committee to oversee risk initiatives.
C.
Define how risk thresholds are aligned with organizational objectives.
D.
Standardize IT risk mitigation for better monitoring of IT risk.
Full Access
Answer:
C
Explanation:
The correct answer is C because the best way to incorporatecontinuous monitoringin IT risk policies is todefine how risk thresholds are aligned with organizational objectives. Continuous monitoring is effective only when it is tied to measurable thresholds that indicate when risk is moving outside acceptable limits. Those thresholds must be aligned with business objectives, risk appetite, and tolerance to make monitoring meaningful.
The other options are less appropriate as the best policy-level approach:
A. Implement a governance, risk, and compliance (GRC) toolmay support monitoring, but a tool is not the policy foundation.
B. Establish a cross-functional risk steering committeeimproves governance, but it does not define how continuous monitoring should operate.
D. Standardize IT risk mitigationhelps consistency, but continuous monitoring depends on thresholds and escalation criteria.
Exact Extracts supporting the answer:
“The main purpose of continuous monitoring is detecting changes to the enterprise’s risk environment.â€
“The main purpose of risk monitoring is to provide timely information on the actual status of the enterprise with regard to risk with the risk profile offering an overall risk status.â€
“Including thresholds that identify when controls no longer provide the intended value is essential when developing metrics to monitor the control life cycle.â€
“The most important consideration when implementing key risk indicators is linking the metric to a specific risk.â€
“The best approach for creating key risk indicators for quarterly reporting to senior leadership is identifying the enterprise risk appetite and metrics and measures of current risk.â€
These extracts show that continuous monitoring must be based on defined thresholds linked to enterprise objectives and risk levels. Therefore, the best answer isdefine how risk thresholds are aligned with organizational objectives.
===========
Question # 543
An organization is subject to a new regulation that requires nearly real-time recovery of its services following a disruption. Which of the following is the BEST way to manage the risk in this situation?
A.
Move redundant IT infrastructure to a closer location.
B.
Obtain insurance and ensure sufficient funds are available for disaster recovery.
C.
Review the business continuity plan (BCP) and align it with the new business needs.
D.
Outsource disaster recovery services to a third-party IT service provider.
Full Access
Answer:
C
Explanation:
Updating the BCP to align with real-time recovery requirements ensures the organization’s resilience to disruptions while meeting regulatory standards. This action reflectsBusiness Continuity and Disaster Recovery Planningbest practices.
Question # 544
A segregation of duties control was found to be ineffective because it did not account for all applicable functions when evaluating access. Who is responsible for ensuring the control is designed to effectively address risk?
A.
Risk manager
B.
Control owner
C.
Control tester
D.
Risk owner
Full Access
Answer:
B
Explanation:
The control owner is the person who is responsible for ensuring that the control is designed to effectively address risk. The control owner is also responsible for implementing, operating, monitoring, and maintaining the control. The control owner should ensure that the control is aligned with the risk owner’s risk appetite and tolerance, and that the control is periodically reviewed and updated to reflect changes in the risk environment. The risk manager, the control tester, and the risk owner are not directly responsible for the design of the control, although they may provide input, feedback, or approval. References = Risk and Information Systems Control Study Manual, Chapter 1, Section 1.3.2, page 1-15.
Question # 545
Which of the following is the GREATEST benefit of a three lines of defense structure?
A.
An effective risk culture that empowers employees to report risk
B.
Effective segregation of duties to prevent internal fraud
C.
Clear accountability for risk management processes
D.
Improved effectiveness and efficiency of business operations
Full Access
Answer:
C
Explanation:
A three lines of defense structure is a model that defines the roles and responsibilities of different functions and levels within an organization for risk management and control. The first line of defense is the operational management, which is responsible for owning and managing the risks. The second line of defense is the risk management and compliance functions, which are responsible for overseeing and supporting the risk management processes. The third line of defense is the internal audit function, which is responsible for providing independent assurance on the effectiveness of the risk management and control systems. The greatest benefit of a three lines of defense structure is that it provides clear accountability for risk management processes, as it clarifies who is responsible for what, and how they interact and communicate with each other. This can help to avoid duplication, confusion, or gaps in the risk management activities, and ensure that the risks are properly identified, assessed, treated, monitored, and reported. References = CRISC Review Manual, 7th Edition, page 107.
Question # 546
A risk assessment has identified that departments have installed their own WiFi access points on the enterprise network. Which of the following would be MOST important to include in a report to senior management?
A.
The network security policy
B.
Potential business impact
C.
The WiFi access point configuration
D.
Planned remediation actions
Full Access
Answer:
B
Explanation:
A risk assessment is a process of identifying, analyzing, and evaluating the risks that may affect the enterprise’s objectives and operations. It involves determining the likelihood and impact of various risk scenarios, and prioritizing them based on their significance and urgency.
A WiFi access point is a device that allows wireless devices to connect to a wired network using radio signals. It can provide convenience and flexibility for users, but it can also introduce security risks, such as unauthorized access, data leakage, malware infection, or denial of service attacks.
If departments have installed their own WiFi access points on the enterprise network, without proper authorization, configuration, or monitoring, it means that they have bypassed the network security policy and controls, and created potential vulnerabilities and exposures for the enterprise.
The most important information to include in a report to senior management is the potential business impact of this risk, which is the estimated loss or damage that the enterprise may suffer if the risk materializes. The potential business impact can be expressed in terms of financial, operational, reputational, or legal consequences, and it can help senior management to understand the severity and urgency of the risk, and to decide on the appropriate risk response and allocation of resources.
The other options are not the most important information to include in a report to senior management, because they do not convey the magnitude and significance of the risk, and they may not be relevant or actionable for senior management.
The network security policy is the set of rules and guidelines that define the security objectives, requirements, and responsibilities for the enterprise network. It is important to have a clear and comprehensive network security policy, and to ensure that it is communicated, enforced, and monitored across the enterprise, but it is not the most important information to include in a report to senior management, because it does not indicate the actual or potential impact of the risk, and it may not reflect the current or desired state of the network security.
The WiFi access point configuration is the set of parameters and settings that define the functionality, performance, and security of the WiFi access point. It is important to have a secure and consistent WiFi access point configuration, and to follow the best practices and standards for wireless network security, but it is not the most important information to include in a report to senior management, because it does not indicate the actual or potential impact of the risk, and it may not be relevant or understandable for senior management.
The planned remediation actions are the steps and measures that are intended to mitigate, transfer, avoid, or accept the risk, and to restore the normal operation and security of the enterprise network. It is important to have a feasible and effective plan for remediation actions, and to implement and monitor them in a timely and efficient manner, but it is not the most important information to include in a report to senior management, because it does not indicate the actual or potential impact of the risk, and it may not be feasible or appropriate without senior management’s approval or support. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 146
Question # 547
Which of the following factors will have the GREATEST impact on the implementation of a risk mitigation strategy for an organization?
A.
Cost-benefit analysis
B.
Risk tolerance
C.
Known vulnerabilities
D.
Cyber insurance
Full Access
Answer:
B
Explanation:
Risk tolerance defines the boundaries for acceptable risk levels and directly impacts decision-making for mitigation strategies. A well-defined tolerance helps prioritize actions and allocate resources effectively, emphasizing its central role in theRisk Responsedomain.
Question # 548
Which of the following resources is MOST helpful when creating a manageable set of IT risk scenarios?
A.
Results of current and past risk assessments
B.
Organizational strategy and objectives
C.
Lessons learned from materialized risk scenarios
D.
Internal and external audit findings
Full Access
Answer:
C
Explanation:
 According to the CRISC Review Manual1, lessons learned from materialized risk scenarios are the insights and knowledge gained from analyzing the causes, impacts, and responses of actual risk events that occurred in the past. Lessons learned from materialized risk scenarios are the most helpful resource when creating a manageable set of IT risk scenarios, as they help to identify and prioritize the most relevant and realistic risks that could affect the organization’s objectives, processes, and resources. Lessons learned from materialized risk scenarios also helpto improve the risk management practices and capabilities, and to avoid repeating the same mistakes or gaps in the future. References = CRISC Review Manual1, page 206.
Question # 549
What should be the PRIMARY objective of updating a risk awareness program in response to a steady rise in cybersecurity threats across the industry?
A.
To increase familiarity and understanding of potential security incidents
B.
To ensure compliance with risk management policies and procedures
C.
To reduce the risk of insider threats that could compromise security practices
D.
To lower the organization ' s risk appetite and tolerance levels
Full Access
Answer:
A
Explanation:
The main goal of updating a risk awareness program in response to rising threats is to ensure employees understand new risks and how to respond to them, thereby enhancing overall security posture.
[Reference:CRISC Manual – Domain 1: Governance, Slide 517-520, , , , ]
Question # 550
Who is MOST appropriate to be assigned ownership of a control
A.
The individual responsible for control operation
B.
The individual informed of the control effectiveness
C.
The individual responsible for resting the control
D.
The individual accountable for monitoring control effectiveness
Full Access
Answer:
D
Explanation:
 A control is a measure or action that is implemented to reduce the likelihood or impact of a risk event, or to enhance the benefits or opportunities of a risk event. A control owner is a person who is assigned the responsibility and authority for the design, implementation, operation, and maintenance of a control. The most appropriate person to be assigned ownership of a control is the individual accountable for monitoring control effectiveness, which is the process of measuring and evaluating the performance and compliance of the control. By assigning the control ownership to the individual accountable for monitoring control effectiveness, the organization can ensure that the control is aligned with the risk objectives, operates as intended, and delivers the expected results. References = 4
Question # 551
Following a review of a third-party vendor, it is MOST important for an organization to ensure:
A.
results of the review are accurately reported to management.
B.
identified findings are reviewed by the organization.
C.
results of the review are validated by internal audit.
D.
identified findings are approved by the vendor.
Full Access
Answer:
A
Explanation:
 A review of a third-party vendor is a process that involves examining and evaluating the performance, quality, and compliance of the vendor that provides a product or service to the organization1. A review of a third-party vendor can help to identify and address the risks and issues that may arise from the vendorrelationship, such as data breaches, service disruptions, contract violations, or reputation damage2. Following a review of a third-party vendor, it is most important for an organization to ensure that the results of the review are accurately reported to management, as this will enable the management to make informed and timely decisions and actions based on the findings and recommendations of the review. Accurate reporting of the results of the review will also help to establish and maintain the trust and transparency between the organization and the vendor, and to demonstrate the accountability and responsibility of the organization for its vendor risk management3. Identified findings are reviewed by the organization, results of the review are validated by internal audit, and identified findings are approved by the vendor are not the most important things to ensure following a review of a third-party vendor, as they do not provide the same level of impact and value as accurate reporting of the results of the review. Identified findings are reviewed by the organization is a process that involves analyzing and interpreting the outcomes and implications of the review of a third-party vendor, and determining the appropriate risk responses and actions to address the findings4. Thisis an important step in the vendor risk management process, but it is not the most important thing to ensure following a review of a third-party vendor, as it does not communicate or inform the management or the vendor of the results of the review. Results of the review are validated by internal audit is a process that involves verifying and confirming the accuracy and reliability of the review of a third-party vendor, and providing assurance and advice on the adequacy and effectiveness of the vendor risk management. This is an important step in the vendor risk management process, but it is not the most important thing to ensure following a review of a third-party vendor, as it does not report or share the results of the review with the management or the vendor. Identified findings are approved by the vendor is a process that involves obtaining the consent and agreement of the vendor on the outcomes and recommendations of the review of a third-party vendor, and ensuring their cooperation and compliance with the risk responses and actions. This is an important step in the vendor risk management process, but it is not the most important thing to ensure following a review of a third-party vendor, as it does not report or inform the management of the results of the review. References = 1: The guide to third-party vendor reviews - TerraTrue HQ | TerraTrue2: 4 Tips For Organizations To Evaluate Third-Party Vendors – Forbes Advisor3: Vendor Risk Management: Best Practices for 2023 - Venminder4: [Risk and Information Systems Control Study Manual, Chapter 3: Risk Response, Section 3.1: Risk Response Options, pp. 113-115.] : [IT Risk Resources | ISACA] : Who Is Considered a Third Party or Vendor? - Venminder : [Risk and Information Systems Control Study Manual, Chapter 2: IT Risk Assessment, Section 2.1: Risk Identification, pp. 57-59.] : [Risk and Information SystemsControl Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.1:Control Design, pp. 233-235.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.2: Control Implementation, pp. 243-245.] : [Risk and Information Systems Control Study Manual, Chapter 5: Information Systems Control Design and Implementation, Section 5.3: Control Monitoring and Maintenance, pp. 251-253.]
Question # 552
A risk practitioner is performing a risk assessment of recent external advancements in quantum computing. Which of the following would pose the GREATEST concern for the risk practitioner?
A.
The organization has incorporated blockchain technology in its operations.
B.
The organization has not reviewed its encryption standards.
C.
The organization has implemented heuristics on its network firewall.
D.
The organization has not adopted Infrastructure as a Service (laaS) for its operations.
Full Access
Answer:
B
Question # 553
Which of the following BEST balances the costs and benefits of managing IT risk*?
A.
Prioritizing and addressing risk in line with risk appetite. Eliminating risk through preventive and detective controls
B.
Considering risk that can be shared with a third party
C.
Evaluating the probability and impact of risk scenarios
Full Access
Answer:
A
Explanation:
Risk appetite is the broad-based amount of risk that an organization is willing to accept in its activities. Risk appetite reflects the level of risk that the organization is prepared to take to achieve its strategic goals, and provides guidance and boundaries for the risk management activities and decisions. The best way to balance the costs and benefits of managing IT risk is to prioritize and address risk in line with risk appetite, which means that the organization should identify, assess, treat, monitor, and communicate the risks that are within or exceed the risk appetite, and allocate the resources and efforts accordingly. By doing so, the organization can optimize its risk-return trade-off, align its risk exposure with its strategic objectives, and enhance its risk culture and performance. References = 5
Question # 554
Which of the following is the BEST recommendation of a risk practitioner for an organization that recently changed its organizational structure?
A.
Communicate the new risk profile.
B.
Implement a new risk assessment process.
C.
Revalidate the corporate risk appetite.
D.
Review and adjust key risk indicators (KRIs).
Full Access
Answer:
A
Explanation:
Communicating the new risk profile is the best recommendation for a risk practitioner for an organization that recently changed its organizational structure, because it helps to inform and align the stakeholders on the current state of risks and their implications for the organization’s objectives and strategy. A risk profile is a summary of the key risks that an organization faces, along with their likelihood, impact, and response strategies. An organizational structure is the way that an organization arranges its people, roles, and responsibilities to achieve its goals and deliver its value proposition. A change in the organizational structure may affect the risk profile, as it may introduce new sources or types of risk, or alter the existing risk levels orresponses. Therefore, communicating the new risk profile is the best recommendation, as it helps to ensure that the stakeholders are aware of and prepared for the changes and challenges that the new organizational structure may bring. Implementing a new risk assessment process, revalidating the corporate risk appetite, and reviewing and adjusting key risk indicators (KRIs) are all important tasks to perform after communicating the new risk profile, but they are not the best recommendation, as they depend on the communication and understanding of the new risk profile. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.2.3, page 91
Question # 555
An organization wants to launch a campaign to advertise a new product Using data analytics, the campaign can be targeted to reach potential customers. Which of the following should be of GREATEST concern to the risk practitioner?
A.
Data minimization
B.
Accountability
C.
Accuracy
D.
Purpose limitation
Full Access
Answer:
D
Explanation:
 The greatest concern for the risk practitioner when an organization wants to launch a campaign to advertise a new product using data analytics is the purpose limitation. Purpose limitation is a principle that states that personal data should be collected for specified, explicit, and legitimate purposes, and not further processed in a manner that is incompatible with those purposes. By using data analytics to target potential customers, the organization may violate the purpose limitation principle if the data was collected for a different purpose and the customers did not consent to the new use of their data. Data minimization, accountability, and accuracy are other principles that should be followed, but they are not as concerning as the purposelimitation. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 8; CRISC Review Manual, 6th Edition, page 97.
Question # 556
A public online information security training course is available to an organization ' s staff. The online course contains free-form discussion fields. Which of the following should be of MOST concern to the organization ' s risk practitioner?
A.
The form may be susceptible to SQL injection attacks.
B.
Data is not encrypted in transit to the site.
C.
Proprietary corporate information may be disclosed.
D.
Staff nondisclosure agreements (NDAs) are not in place.
Full Access
Answer:
C
Explanation:
Free-form fields in public forums increase the risk of accidental or intentional disclosure of sensitive or proprietary information. This creates legal and reputational exposure. Monitoring or disabling such features is essential to mitigating data leakage risks.
[Reference:CRISC Manual – Domain 2, Slide 124-127, 203, , , , ]
Question # 557
Which of the following should be a risk practitioner’s MOST important consideration when developing IT risk scenarios?
A.
The impact of controls on the efficiency of the business in delivering services
B.
Linkage of identified risk scenarios with enterprise risk management
C.
Potential threats and vulnerabilities that may have an impact on the business
D.
Results of network vulnerability scanning and penetration testing
Full Access
Answer:
C
Explanation:
The MOST important consideration when developing IT risk scenarios is the potential threats and vulnerabilities that may have an impact on the business, because they are the key elements of a risk scenario that describe the sources and causes of the risk, and the potential consequences and impacts of the risk on the business objectives and processes. The other options are not as important as the potential threats and vulnerabilities, because:
Option A: The impact of controls on the efficiency of the business in delivering services is a secondary consideration that may affect the cost-benefit analysis of the risk response, but it does not directly affect the identification and assessment of the risk scenario.
Option B: Linkage of identified risk scenarios with enterprise risk management is a good practice that ensures the alignment and integration of the IT risk management with the overall enterprise risk management, but it does not directly affect the identification and assessment of the risk scenario.
Option D: Results of network vulnerability scanning and penetration testing are useful sources of information that may reveal some of the threats and vulnerabilities in the IT environment, but they are not the only or the most important consideration when developing IT risk scenarios, as they may not cover all the aspects and dimensions of the risk. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 104.
Question # 558
Which of the following is the BEST course of action to help reduce the probability of an incident recurring?
A.
Perform a risk assessment.
B.
Perform root cause analysis.
C.
Initiate disciplinary action.
D.
Update the incident response plan.
Full Access
Answer:
B
Explanation:
An incident is an unplanned event that disrupts or degrades the normal operation or performance of an IT service, system, or network1. An incident can cause various negative impacts, such as service outages, data losses, security breaches, or customer dissatisfaction2. An incident can recur if the underlying cause or problem of the incident is not properly identified and resolved3.
The best course of action to help reduce the probability of an incident recurring is to perform root cause analysis. Root cause analysis is a systematic process of finding and eliminating the fundamental cause or problem that led to the incident4. Root cause analysis can help to:
Prevent or minimize the recurrence of the incident by addressing the source of the problem, not just the symptoms or effects
Identify and implement corrective or preventive actions that can effectively resolve or mitigate the problem
Learn from the incident and improve the IT service, system, or network quality and reliability
Enhance the incident management and problem management processes and capabilities5
References = What is an Incident?, Incident Management - Wikipedia, Problem Management - Wikipedia, Root Cause Analysis - Wikipedia, Root Cause Analysis: A Guide for Business Leaders
Question # 559
Which of the following is the GREATEST concern when an organization uses a managed security service provider as a firewall administrator?
A.
Exposure of log data
B.
Lack of governance
C.
Increased number of firewall rules
D.
Lack of agreed-upon standards
Full Access
Answer:
A
Explanation:
A managed security service provider (MSSP) is a third-party entity that offers network security services to an organization, such as firewall operation, administration, monitoring, and maintenance1. A firewall is a device or software that controls the incoming and outgoing network traffic based on predefined rules2. A firewall administrator is a person or entity that manages and maintains the firewall configuration, rules, and policies3. When an organizationuses an MSSP as a firewall administrator, the greatest concern is the exposure of log data, because log data contains sensitive and valuable information about the organization’s network activity, such as source and destination IP addresses, ports, protocols, timestamps, and user identities4. If the log data is not protected properly by the MSSP, it could be accessed, modified, or stolen by unauthorized parties, such as hackers, competitors, or regulators, which could result in data breaches, compliance violations, reputational damage, or legal liabilities for the organization5. The other options are not as concerning as the exposure of log data, because they do not pose a direct and immediate threat to the organization’s data security and privacy, but rather affect the quality and efficiency of the firewall management, as explained below:
B. Lack of governance is a concern when an organization uses an MSSP as a firewall administrator, because it could lead to misalignment or inconsistency between the organization’s and the MSSP’s objectives, policies, and standards for firewall management. However, this concern can be mitigated by establishing a clear and comprehensive service level agreement (SLA) with the MSSP,which defines the roles, responsibilities, expectations, and performance indicators for the firewall management service6.
C. Increased number of firewall rules is a concern when an organization uses an MSSP as a firewall administrator, because it could create complexity, confusion, or duplication in the firewall configuration, which could affect the firewall performance and security. However, this concern can be mitigated by conducting regular firewall audits and reviews with the MSSP, which can help to rationalize, optimize, and update the firewall rules, and to ensure that they are relevant, effective, and efficient for the organization’s network environment.
D. Lack of agreed-upon standards is a concern when an organization uses an MSSP as a firewall administrator, because it could result in gaps or weaknesses in the firewall design and implementation, which could compromise the firewall functionality and security. However, this concern can be mitigated by adopting and following industry best practices, norms, and expectations for firewall management, such as the National Institute of Standards and Technology (NIST) guidelines, the Center for Internet Security (CIS) benchmarks, or the Payment Card Industry Data Security Standard (PCI DSS) requirements . References = Risk and Information Systems Control Study Manual, Chapter 4, Section 4.2.1, page 115. What Is A Managed Security Service Provider (MSSP)? - Fortinet, What is a Firewall? - Definition from Techopedia, Firewall Administrator Job Description - Betterteam, What is a Firewall Log? - Definition from Techopedia, Firewall Log Management: Why It’s Important and How to Do It Right, How to Write a Service Level Agreement (SLA) for an MSSP, [Firewall Auditing: BestPractices for Security and Compliance], [Guidelines on Firewalls and Firewall Policy | CSRC] , [CIS Firewall Benchmark - CIS], [PCI DSS and Firewalls - PCI Security Standards Council]
Question # 560
While reviewing a contract of a cloud services vendor, it was discovered that the vendor refuses to accept liability for a sensitive data breach. Which of the following controls will BES reduce the risk associated with such a data breach?
A.
Ensuring the vendor does not know the encryption key
B.
Engaging a third party to validate operational controls
C.
Using the same cloud vendor as a competitor
D.
Using field-level encryption with a vendor supplied key
Full Access
Answer:
A
Explanation:
Encryption is a technique that transforms data into an unreadable format using a secret key, so that only authorized parties can access and decrypt the data. Encryption can help to protectsensitive data from unauthorized access or disclosure, especially when the data is stored or transmitted in the cloud1.
Ensuring the vendor does not know the encryption key is a control that will best reduce the risk associated with a data breach, because it can help to:
Prevent the vendor from accessing or disclosing the sensitive data, intentionally or unintentionally
Limit the exposure or impact of the data breach, even if the vendor’s systems or networks are compromised by hackers or malicious insiders
Maintain the confidentiality and integrity of the sensitive data, regardless of the vendor’s liability or responsibility
Enhance the trust and confidence of the customers and stakeholders, who may be concerned about the vendor’s refusal to accept liability for a data breach23
The other options are not as effective as ensuring the vendor does not know the encryption key for reducing the risk associated with a data breach. Engaging a third party to validate operational controls is a control that can help to verify and improve the vendor’s security practices and processes, but it does not guarantee that the vendor will prevent or respond to a data breach adequately or timely. Using the same cloud vendor as a competitor is not a control, but rather a business decision that may increase the risk associated with a data breach, as the vendor may have access to or disclose the sensitive data of both parties, or may favor one party over the other. Using field-level encryption with a vendor supplied key is a control that can help to encrypt specific fields or columns of data, such as names, addresses, or credit card numbers, but it does not prevent the vendor from accessing or disclosing the data, as the vendor has the encryption key4. References =
Encryption - ISACA
Cloud Encryption: Using Data Encryption in The Cloud
Cloud Encryption: Why You Need It and How to Do It Right
Field-Level Encryption - ISACA
[CRISC Review Manual, 7th Edition]
Question # 561
Which of the following is the BEST approach for determining whether a risk action plan is effective?
A.
Comparing the remediation cost against budget
B.
Assessing changes in residual risk
C.
Assessing the inherent risk
D.
Monitoring changes of key performance indicators(KPIs)
Full Access
Answer:
B
Explanation:
According to the CRISC Review Manual (Digital Version), assessing changes in residual risk is the best approach for determining whether a risk action plan is effective, as it measures the impact and value of the risk response actions and controls on the risk level. Residual risk is the risk that remains after the risk response actions and controls have been implemented. Assessing changes in residual risk helps to:
Evaluate the extent to which the risk response actions and controls have reduced the likelihood and/or impact of the risk to an acceptable level
Identify and report any deviations, errors, or weaknesses in the risk response actions and controls and their performance
Recommend and implement corrective actions or improvement measures to address any issues or deficiencies in the risk response actions and controls
Monitor and measure the effectiveness and efficiency of the risk response actions and controls and their alignment with the organization’s risk appetite and risk tolerance
Update the risk register and the risk treatment plan to reflect the current risk status and the residual risk levels
References = CRISC Review Manual (Digital Version), Chapter 3: IT Risk Response, Section 3.2: Risk Response Process, pp. 161-1621
Question # 562
An organization is planning to move its application infrastructure from on-premises to the cloud. Which of the following is the BEST course of the actin to address the risk associated with data transfer if the relationship is terminated with the vendor?
A.
Meet with the business leaders to ensure the classification of their transferred data is in place
B.
Ensure the language in the contract explicitly states who is accountable for each step of the data transfer process
C.
Collect requirements for the environment to ensure the infrastructure as a service (IaaS) is configured appropriately.
D.
Work closely with the information security officer to ensure the company has the proper security controls in place.
Full Access
Answer:
B
Explanation:
The best course of action to address the risk associated with data transfer if the relationship is terminated with the vendor is to ensure the language in the contract explicitly states who is accountable for each step of the data transfer process. This can help to avoid ambiguity, confusion, or disputes over the ownership, responsibility, and liability of the data and the data transfer process. Meeting with the business leaders, collecting requirements, and working with the information security officer are important activities, but they are not as effective as ensuring the contractual agreement is clear and enforceable. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 4; CRISC Review Manual, 6th Edition, page 153.
Question # 563
Which of the following is the PRIMARY purpose of a risk register?
A.
To assign control ownership of risk
B.
To provide a centralized view of risk
C.
To identify opportunities to transfer risk
D.
To mitigate organizational risk
Full Access
Answer:
B
Explanation:
According to ISACA, a risk register is a tool to record and track the identified risks, their ratings, responses, and status. The primary purpose of a risk register is to provide a centralized view of risk for the organization, as it enables the consolidation, communication, and reporting of risk information across different levels, units, and functions. A risk register can also support the risk management process, such as risk identification, assessment, treatment, monitoring, and review.
[References:, •ISACA, Risk IT Framework, 2nd Edition, 2019, p. 761, •ISACA, Capability Maturity Model and Risk Register Integration: The Right Approach to Enterprise Governance2, , , , , , , , , , ]
Question # 564
Where should a risk practitioner document the current state and desired future state of organizational risk?
A.
Risk register
B.
Risk action plan
C.
Risk management strategy
D.
Business continuity plan (BCP)
Full Access
Answer:
C
Question # 565
Which of the following would be the GREATEST risk associated with a new implementation of single sign-on?
A.
Inability to access key information
B.
Complex security administration
C.
User resistance to single sign-on
D.
Single point of failure
Full Access
Answer:
D
Explanation:
Single sign-on (SSO)simplifies authentication but introduces asingle point of failure. If the SSO mechanism is compromised or goes down, it can result in the loss of access across multiple systems, leading to widespread business disruption or security breaches.
[Reference:CRISC Manual – Domain 2, Slide 124, , , , ]
Question # 566
Which of the following is the BEST indication of a potential threat?
A.
Increase in identified system vulnerabilities
B.
Ineffective risk treatment plans
C.
Excessive policy and standard exceptions
D.
Excessive activity in system logs
Full Access
Answer:
A
Explanation:
An increase in system vulnerabilities directly correlates with an elevated exposure to potential threats. Identifying more vulnerabilities signals a need to re-evaluate the risk environment.
[Reference:CRISC Manual – Domain 2: Risk Assessment, Slide 169, , , , ]
Question # 567
Which of the following would BEST mitigate an identified risk scenario?
A.
Conducting awareness training
B.
Executing a risk response plan
C.
Establishing an organization ' s risk tolerance
D.
Performing periodic audits
Full Access
Answer:
B
Explanation:
The best way to mitigate an identified risk scenario is to execute a risk response plan. A risk response plan is a document that describes the actions and resources that are needed to address the risk scenario. A risk response plan can include one or more of the following strategies: avoid, transfer, mitigate, accept, or exploit. By executing a risk response plan, the organization can reduce the likelihood and/or impact of the risk scenario, or take advantage of the opportunities that the risk scenario may present. The other options are not as effective as executing a riskresponse plan, as they are related to the awareness, assessment, or monitoring of the risk scenario, not the actual treatment of the risk scenario. References = Risk and Information Systems Control Study Manual, Chapter 3: IT Risk Response, Section 3.2: IT Risk Response Options, page 133.
Question # 568
Which of the following is the MOST useful indicator to measure the efficiency of an identity and access management process?
A.
Number of tickets for provisioning new accounts
B.
Average time to provision user accounts
C.
Password reset volume per month
D.
Average account lockout time
Full Access
Answer:
B
Explanation:
The average time to provision user accounts is the most useful indicator to measure the efficiency of an identity and access management (IAM) process, because it reflects how quickly and smoothly the process can grant access to the appropriate users. The average time to provision user accounts can be calculated by dividing the total time spent on provisioning user accounts by the number of user accounts provisioned in a given period. A lower average time indicates a more efficient IAM process, as it means that users can access the resources they need without unnecessary delays or errors. A higher average time may indicate problems or bottlenecks in the IAM process, such as manual steps, complex workflows, lack of automation, or insufficient resources. The average time to provision user accounts can also be compared across different applications, systems, or business units to identify areas for improvement or best practices. The other options are less useful indicators to measure the efficiency of an IAM process. The number of tickets for provisioning new accounts shows the demand for the IAM process, but not how well the process meets the demand. The password reset volume per month shows the frequency of password-related issues, but not how effectively the IAM process handles them. The average account lockout time shows the impact of account lockouts on user productivity, but not howefficiently the IAM process prevents or resolves them. References = Top Identity and Access Management MetricsÂ
Question # 569
Which of the following would provide the MOST comprehensive information for updating an organization ' s risk register?
A.
Results of the latest risk assessment
B.
Results of a risk forecasting analysis
C.
A review of compliance regulations
D.
Findings of the most recent audit
Full Access
Answer:
A
Explanation:
A risk register is a document that is used as a risk management tool to identify and track risks that may affect a project or an organization1. A risk register should be updated regularly to reflect the current status and changes of the risks, as well as the actions taken to mitigate or resolve them2. The most comprehensive information for updating a risk register would come from the results of the latest risk assessment, which is a process that involves identifying, analyzing, and evaluating the risks and their potential impacts3. A risk assessment provides a detailed and systematic overview of the risks, theirsources, causes, likelihood, severity, and consequences, as well as the existing and planned controls andresponses4. A risk assessment also helps to prioritize the risks based on their level of exposure and urgency, and to align them with the organization’s risk appetite and tolerance5. Therefore, the results of the latest risk assessment would provide the most relevant and complete information for updating a risk register and ensuring that it reflects the current risk profile and situation of the project or the organization. Results of a risk forecasting analysis are not the most comprehensive information for updating a risk register, as they do not provide a complete picture of the risks and their impacts. A risk forecasting analysis is a technique that uses historical data, trends, and scenarios to estimate the potential outcomes and impacts of future events that may affect the organization’s objectives and performance6. A risk forecasting analysis can help to anticipate and prepare for the risks, but it does not provide specific information on the sources, causes, likelihood, severity, and consequences of the risks, nor the existing and planned controls and responses. A review ofcompliance regulations is not the most comprehensive information for updating a risk register, as it does not cover all the aspects and dimensions of risk management. A review of compliance regulations is a process that involves checking and verifying that the organization’s activities, processes, and systems are in accordance with the applicable laws, rules, and standards7. A review of compliance regulations can help to identify and mitigate the risks related to legal or regulatory violations, but it does not provide specific information on the other types and sources of risks, such as operational, strategic, financial, or reputational risks, nor the existing and planned controls and responses. Findings of the most recent audit are not the most comprehensive information for updating a risk register, as they do not provide a current and holistic view of the risks and their impacts. An audit is an independent examination and evaluation of the organization’s activities, processes, and systems, to provide assurance and advice on their adequacy and effectiveness. An audit can help to identify and report the issues or gaps in the organization’s risk management, but it does not provide specific information on the current status and changes of the risks, nor the existing and planned controls and responses. References = Risk and Information Systems Control Study Manual, Chapter 4: Risk and Control Monitoring and Reporting, Section 4.2: Risk Monitoring, pp. 189-191.
Question # 570
When collecting information to identify IT-related risk, a risk practitioner should FIRST focus on IT:
A.
risk appetite.
B.
security policies
C.
process maps.
D.
risk tolerance level
Full Access
Answer:
A
Explanation:
When collecting information to identify IT-related risk, a risk practitioner should first focus on IT risk appetite, which is the amount of risk that the organization is willing to accept in pursuit of its IT objectives, before action is deemed necessary to reduce the risk1. IT risk appetite reflects the organization’s IT risk attitude and its willingness to accept risk in specific scenarios, with a governance model in place for IT risk oversight. IT risk appetite helps to guide the organization’s approach to IT risk and IT risk management, and to align its IT risk decisions with its business objectives and context. The other options are not the best answers, as they are either derived from or dependent on the IT risk appetite. IT security policies are the rules and guidelines that define the organization’s IT security objectives, requirements, and responsibilities, and they are based on the IT risk appetite. IT process maps are the graphical representations of the IT processes, activities, and tasks that support the organization’s IT objectives, and they are influenced by the IT risk appetite. IT risk tolerance level is the acceptable variation between the IT risk thresholds and the IT objectives, and it is determined by the IT risk appetite. References = IT Risk Resources | ISACA; RiskAppetite vs. Risk Tolerance: What is the Difference?; IT Risk Management - an overview | ScienceDirect Topics; IT Risk Management Framework - an overview | ScienceDirect Topics
Question # 571
When of the following is the BEST key control indicator (KCI) to determine the effectiveness of en intrusion prevention system (IPS)?
A.
Percentage of system uptime
B.
Percentage of relevant threats mitigated
C.
Total number of threats identified
D.
Reaction time of the system to threats
Full Access
Answer:
B
Explanation:
 The percentage of relevant threats mitigated is the best key control indicator (KCI) to determine the effectiveness of an intrusion prevention system (IPS), because it measures how well the IPS is performing its intended function of preventing unauthorized access or attacks. The percentageof system uptime is not a good KCI, because it does not reflect the quality or accuracy of the IPS. The total number of threats identified is not a good KCI, because it does not indicate how many of those threats were actually prevented by the IPS. The reaction time of the system to threats is not a good KCI, because it does not measure the impact or severity of the threats that were prevented or not prevented by the IPS. References = CRISC: Certified in Risk & Information Systems Control Sample Questions2
Question # 572
Which of the following is the MOST important consideration when establishing a recovery point objective (RPO)?
A.
Latency of the alternate site
B.
Amount of acceptable data loss
C.
Time and resources for offsite backups
D.
Cost of testing the business continuity plan (BCP)
Full Access
Answer:
B
Explanation:
RPOdefines themaximum tolerable data lossin case of a disruption — i.e., how much data the enterprise can afford to lose between the last backup and an incident.
ISACA’s business continuity and CRISC guidance:
“The recovery point objective (RPO) is based on the amount of acceptable data loss determined by business requirements.â€
A, C, Dare logistical concerns; onlyBdefines the RPO itself.
CRISC Reference:Domain 3 – Risk Response and Mitigation, Topic: Business Continuity Objectives (RTO/RPO).
Question # 573
Which of the following BEST enables an organization to address risk associated with technical complexity?
A.
Documenting system hardening requirements
B.
Minimizing dependency on technology
C.
Aligning with a security architecture
D.
Establishing configuration guidelines
Full Access
Answer:
C
Explanation:
Addressing Technical Complexity:
Security Architecture Alignment: Aligning with a security architecture helps manage the complexity by providing a structured framework for implementing and managing security controls.
Comprehensive Framework: A security architecture ensures that all security controls are integrated and aligned with the organization’s overall security strategy, reducing the risk associated with technical complexity.
Steps Involved:
Develop or Adopt a Security Architecture: Use established frameworks such as SABSA, TOGAF, or Zachman.
Implementation: Apply the security architecture across all systems and processes to ensure consistency and integration.
Monitoring and Maintenance: Continuously monitor the security architecture and update it as necessary to address new threats and technologies.
Comparison with Other Options:
Documenting System Hardening Requirements: Important but does not address the overall complexity.
Minimizing Dependency on Technology: Not always feasible and does not fully address the inherent complexity.
Establishing Configuration Guidelines: Helpful but should be part of the broader security architecture.
Best Practices:
Continuous Improvement: Regularly update and improve the security architecture to adapt to evolving threats and technologies.
Training and Awareness: Ensure that all relevant personnel understand the security architecture and their role in maintaining it.
[References:, CRISC Review Manual: Discusses the importance of aligning with a security architecture to manage technical complexity and ensure comprehensive security controls​​., ISACA Standards: Emphasize the role of security architecture in providing a structured approach to managing security across the organization​​., , , , , , , , , , , ]
Question # 574
Which of the following would be- MOST helpful to understand the impact of a new technology system on an organization ' s current risk profile?
A.
Hire consultants specializing m the new technology.
B.
Review existing risk mitigation controls.
C.
Conduct a gap analysis.
D.
Perform a risk assessment.
Full Access
Answer:
D
Explanation:
A risk assessment is a process of measuring and comparing the likelihood and impact of various risk scenarios, and prioritizing them based on their significance and urgency. A risk assessmentcan help the organization to understand and document the risks that may affect its objectives and operations, and to support the decision making and planning for the risk management.
Performing a risk assessment would be the most helpful to understand the impact of a new technology system on an organization’s current risk profile, because it can help the organization to address the following questions:
What are the potential benefits and challenges of implementing the new technology system, and how do they align with the organization’s objectives and needs?
What are the existing or emerging risks that may affect the new technology system, and how do they relate to the organization’s current risk profile?
How likely and severe are the risks that may affect the new technology system, and what are the possible consequences or impacts for the organization and its stakeholders?
How can the risks that may affect the new technology system be mitigated or prevented, and what are the available or feasible options or solutions?
Performing a risk assessment can help the organization to understand the impact of the new technology system on its current risk profile by providing the following benefits:
It can enable the comparison and evaluation of the current and desired state and performance of the organization’s risk management function, and to identify and quantify the gaps or opportunities for improvement.
It can provide useful references and benchmarks for the alignment and integration of the new technology system with the organization’s risk management function, and for the compliance with the organization’s risk policies and standards.
It can support the implementation and monitoring of the new technology system, and for the allocation and optimization of the resources, time, and budget for the new technology system.
The other options are not the most helpful to understand the impact of a new technology system on an organization’s current risk profile, because they do not provide the same level of detail and insight that performing a risk assessment provides, and they may not be specific or applicable to the organization’s objectives and needs.
Hiring consultants specializing in the new technology means engaging or contracting external experts or professionals that have the skills and knowledge on the new technology system, and that can provide advice or guidance on the implementation and management of the new technology system. Hiring consultants specializing in the new technology can help the organization to enhance its competence and performance on the new technology system, but it is not the most helpful, because it does not measure and compare the likelihood and impact of the risks that may affect the new technology system, and it may not be relevant or appropriate for the organization’s current risk profile.
Reviewing existing risk mitigation controls means examining and evaluating the adequacy and effectiveness of the controls or countermeasures that are intended to reduce or eliminate the risksthat may affect the organization’s objectives and operations. Reviewing existing risk mitigation controls can help the organization to improve and optimize its risk management function, but it is not the most helpful, because it does not identify and prioritize the risks that may affect the newtechnology system, and it may not cover all the relevant or significant risks that may affect the new technology system.
Conducting a gap analysis means comparing and contrasting the current and desired state and performance of the organization’s objectives and operations, and identifying and quantifying the gaps or differences that need to be addressed or corrected. Conducting a gap analysis can help the organization to identify and document its improvement needs and opportunities, but it is not the most helpful, because it does not measure and compare the likelihood and impact of the risks that may affect the new technology system, and it may not be aligned or integrated with the organization’s current risk profile. References =
ISACA, CRISC Review Manual, 7th Edition, 2022, pp. 19-20, 23-24, 27-28, 31-32, 40-41, 47-48, 54-55, 58-59, 62-63
ISACA, CRISC Review Questions, Answers & Explanations Database, 2022, QID 208
CRISC Practice Quiz and Exam Prep
Question # 575
Which of the following is the PRIMARY reason to use administrative controls in conjunction with technical controls?
A.
To gain stakeholder support for the implementation of controls
B.
To comply with industry best practices by balancing multiple types of controls
C.
To improve the effectiveness of controls that mitigate risk
D.
To address multiple risk scenarios mitigated by technical controls
Full Access
Answer:
C
Explanation:
Administrative controls, such as policies, procedures, and training, complement technical controls by addressing the human and organizational aspects of risk management. Using bothtypes of controls together enhances the overall effectiveness of the risk mitigation strategy, ensuring that technical measures are supported by appropriate governance and user behavior.
[Reference:ISACA CRISC Review Manual, 7th Edition, Chapter 4: Information Technology and Security, Section: Control Types and Implementation., , , , , , , ]
Question # 576
Which of the following is the BEST indicator of executive management ' s support for IT risk mitigation efforts?
A.
The number of stakeholders involved in IT risk identification workshops
B.
The percentage of corporate budget allocated to IT risk activities
C.
The percentage of incidents presented to the board
D.
The number of executives attending IT security awareness training
Full Access
Answer:
D
Explanation:
The best indicator of executive management’s support for IT risk mitigation efforts is the number of executives attending IT security awareness training. This shows that the executives are committed to enhancing their knowledge and skills on IT security issues, and that they are setting a positive example for the rest of the organization. The number of stakeholders involved in IT risk identification workshops, the percentage of corporate budget allocated to IT risk activities, and the percentage of incidents presented to the board are other possible indicators, but they are not as strong as the number of executives attending IT security awareness training. References = ISACA Certified in Risk and Information Systems Control (CRISC) Certification Exam Question and Answers, question 7; CRISC Review Manual, 6th Edition, page 202.
Question # 577
When developing a risk awareness training program, which of the following is the BEST way to promote a risk-aware culture?
A.
Emphasize individual responsibility for managing risk.
B.
Communicate incident escalation procedures.
C.
Illustrate methods to identify threats and vulnerabilities.
D.
Challenge the effectiveness of business processes.
Full Access
Answer:
A
Explanation:
Emphasizing individual responsibility ensures that every employee understands their role in managing risk, which is fundamental to cultivating a risk-aware culture.
[Reference:CRISC Manual – Domain 1, Slide 522-523, , , , ]
Question # 578
Which of the following is the BEST way for a risk practitioner to consolidate the results of risk assessments across multiple operating units?
A.
Implement a governance, risk, and compliance (GRC) system.
B.
Update departmental risk registers with items from the central risk register.
C.
Aggregate operating unit risk registers to a central risk register.
D.
Perform additional risk assessments and create an enterprise risk matrix.
Full Access
Answer:
C
Explanation:
The BEST answer is C because consolidation should roll up operating-unit risk assessment results into a central enterprise view. Operating units own and identify their local risks, but the enterprise needs an aggregated risk profile for decision-making. The uploaded CRISC notes state that the risk register is the best tool for identifying changes in the enterprise risk profile and that aggregated risk to the enterprise is the most important aspect of a risk profile. They also state that a centrally published risk register with workflow features is the best way to maintain accuracy over time.
ISACA explains that a risk register is a collection of identified risk scenarios incorporated into the enterprisewide risk profile, and that risk registers document risk areas and rank them by likelihood and impact. ISACA’s CRISC outline also includes maintaining or establishing the information system risk register and incorporating it into the enterprisewide risk profile.
A is incorrect because a GRC system is only a tool; it does not define the consolidation approach. B is reversed because enterprise consolidation should aggregate from departmental/unit registers into the central view, not push central items down first. D is unnecessary if operating-unit assessments already exist; creating an enterprise matrix may help reporting, but the best consolidation method is a central risk register.
Question # 579
In addition to the risk register, what should a risk practitioner review to develop an understanding of the organization ' s risk profile?
A.
The control catalog
B.
The asset profile
C.
Business objectives
D.
Key risk indicators (KRls)
Full Access
Answer:
C
Explanation:
In addition to the risk register, which is a tool to document and monitor the risks that affect the organization, a risk practitioner should review the business objectives of the organization to develop an understanding of its risk profile. The risk profile is a description of the set of risks that the organization faces in relation to its goals and strategies. By reviewing the business objectives, the risk practitioner can identify the sources, drivers, and consequences of the risks, as well as the alignment, prioritization, and tolerance of the risks. The business objectives also provide the context and criteria for evaluating and managing the risks. The other options are not the best choices to review for developing an understandingof the organization’s risk profile, as they do not capture the full scope and nature of the risks. The control catalog is a list of the existing controls that are implemented to mitigate the risks, but it does not reflect the effectiveness, efficiency, or sufficiency of the controls. The asset profile is a description of the resources and capabilities that the organization possesses or relies on, but it does not indicate the value, vulnerability, or interdependency of the assets. The key risk indicators (KRIs) are metrics that measure the level and trend of the risks, but they do not explain the causes, impacts, orresponses to the risks. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.2, Page 49.
Question # 580
Which of the following is MOST important when discussing risk within an organization?
A.
Adopting a common risk taxonomy
B.
Using key performance indicators (KPIs)
C.
Creating a risk communication policy
D.
Using key risk indicators (KRIs)
Full Access
Answer:
A
Explanation:
 A common risk taxonomy is a framework that defines and categorizes the sources, types, and impacts of risks within an organization1. It helps to establish a consistent and shared understanding of risk across the organization, and to facilitate effective risk identification, assessment, reporting, and communication2. A common risk taxonomy also enables comparison and aggregation of risks at different levels and domains, and supports alignment of risk management with business objectives and strategies3. Using key performance indicators (KPIs) and key risk indicators (KRIs) are important for measuring and monitoring risk and performance, but they are not the most important factor when discussing risk within an organization. KPIs and KRIs should be derived from the common risk taxonomy and aligned with theorganization’s riskappetite and tolerance4. Creating a risk communication policy is also important for ensuring that risk information is communicated to the right stakeholders at the right time and in the right format, but it is not the most important factor either. A risk communication policy should be based on the common risk taxonomy and the risk roles and responsibilities within the organization5. References = Risk and Information Systems Control Study Manual, Chapter 1: IT Risk Identification, Section 1.2: Risk Taxonomy, pp. 25-29.
Question # 581
An application runs a scheduled job that compiles financial data from multiple business systems and updates the financial reporting system. If this job runs too long, it can delay financial reporting. Which of the following is the risk practitioner ' s BEST recommendation?
A.
Implement database activity and capacity monitoring.
B.
Ensure the business is aware of the risk.
C.
Ensure the enterprise has a process to detect such situations.
D.
Consider providing additional system resources to this job.
Full Access
Answer:
D
Explanation:
 The risk practitioner’s best recommendation is to consider providing additional system resources to this job, as this would help to reduce the likelihood and impact of the risk of delaying financial reporting. Providing additional system resources, such as memory, CPU, disk space, or bandwidth, can improve the performance and efficiency of the application and the scheduled job. This can also help to avoid potential errors, failures, or interruptions that could affect the quality and timeliness of the financial data and reporting.
The other options are not the best recommendations for this situation. Implementing database activity and capacity monitoring is a good practice to identify and analyze the root causes of performance issues, but it does not directly address the risk of delaying financial reporting. Ensuring the business is aware of the risk is an important step to communicate and escalate the risk, but it does not provide a solution or mitigation strategy. Ensuring the enterprise has a process to detect such situations is a preventive measure to avoid or minimize the occurrence ofthe risk, but it does not eliminate or reduce the risk. References = Practical Recommendations for Better Enterprise Risk Management - ISACA, HR Risk Management: A Practitioner’s Guide - AIHR, Isaca CRISC today updated questions - Verified by Isaca Experts
Question # 582
An organization learns of a new ransomware attack affecting organizations worldwide. Which of the following should be done FIRST to reduce the likelihood of infection from the attack?
A.
Identify systems that are vulnerable to being exploited by the attack.
B.
Confirm with the antivirus solution vendor whether the next update will detect the attack.
C.
Verify the data backup process and confirm which backups are the most recent ones available.
D.
Obtain approval for funding to purchase a cyber insurance plan.
Full Access
Answer:
A
Explanation:
The first step to reduce the likelihood of infection from the attack is to identify systems that are vulnerable to being exploited by the attack. This would help the organization to assess the scope and severity of the risk, and to prioritize the systems that need immediate protection. Identifying systems that are vulnerable to being exploited by the attack would also help the organization to apply the appropriate patches, updates, or configurations to prevent or mitigate the attack, and to isolate or disconnect the systems that are already infected or compromised. References = Risk and Information Systems Control Study Manual, 7th Edition, Chapter 2, Section 2.1.2, page 60123
Question # 583
Which of the following is the MOST important consideration when performing a risk assessment of a fire suppression system within a data center?
A.
Insurance coverage
B.
Onsite replacement availability
C.
Maintenance procedures
D.
Installation manuals
Full Access
Answer:
C
Explanation:
 The MOST important consideration when performing a risk assessment of a fire suppression system within a data center is the maintenance procedures, because they ensure that the fire suppression system is functioning properly and reliably, and that it can prevent or minimize the damage caused by fire incidents. The maintenance procedures should include regular testing, inspection, and servicing of the fire suppression system components, such as sprinklers, detectors, alarms, and extinguishers. The other options are not as important as the maintenance procedures, because:
Option A: Insurance coverage is a financial measure that can compensate for the loss or damage caused by fire incidents, but it does not prevent or reduce the likelihood or impact of the fire incidents. Insurance coverage is also dependent on the terms and conditions of the insurance policy, which may not cover all the scenarios or costs of the fire incidents.
Option B: Onsite replacement availability is a contingency measure that can facilitate the recovery or restoration of the fire suppression system after a fire incident, but it does not prevent or reduce the likelihood or impact of the fire incidents. Onsite replacement availability is alsodependent on the availability and compatibility of the replacement parts, which may not match the original fire suppression system specifications or requirem ents.
Option D: Installation manuals are a reference source that can provide guidance on how to install or configure the fire suppression system, but they do not ensure that the fire suppression system is functioning properly and reliably. Installation manuals are also static documents that may not reflect the current or updated fire suppression system standards or practices. References = Risk and Information Systems Control Study Manual, 7th Edition, ISACA, 2020, p. 211.
Question # 584
Which of the following is the GREATEST concern when using a generic set of IT risk scenarios for risk analysis?
A.
Quantitative analysis might not be possible.
B.
Risk factors might not be relevant to the organization
C.
Implementation costs might increase.
D.
Inherent risk might not be considered.
Full Access
Answer:
B
Explanation:
 According to the CRISC 351-400 topic3 Flashcards, the greatest concern when using a generic set of IT risk scenarios for risk analysis is that the risk factors might not be relevant to the organization. This is because generic risk scenarios are not tailored to the specific context, objectives, and environment of the organization, and they may not capture the unique threats, vulnerabilities, and impacts that the organization faces. Therefore, using generic risk scenarios may result in inaccurate or incomplete risk assessment and analysis, and may lead to ineffective or inappropriate risk responses. To avoid this, the organization should customize the risk scenarios to reflect its own situation and needs, and involve the relevant stakeholders and experts in the process. References = CRISC 351-400 topic3 Flashcards, Generic IT Risk Scenarios for Risk Analysis: The Greatest Concern
Question # 585
A risk practitioner has received an updated enterprise risk management (ERM) report showing that residual risk is now within the organization ' s defined appetite and tolerance levels. Which of the following is the risk practitioner ' s BEST course of action?
A.
Identify new risk entries to include in ERM.
B.
Remove the risk entries from the ERM register.
C.
Re-perform the risk assessment to confirm results.
D.
Verify the adequacy of risk monitoring plans.
Full Access
Answer:
D
Explanation:
The risk practitioner’s best course of action when the residual risk is now within the organization’s defined appetite and tolerance levels is to verify the adequacy of risk monitoring plans. Risk monitoring is the process of tracking and reviewing the risk status and performance, and ensuring that the risk responses are effective and efficient1. Risk monitoring plans are the documents that specify the objectives, scope, methods, roles, and responsibilities for the riskmonitoring activities2. By verifying the adequacy of risk monitoring plans, the risk practitioner can:
Ensure that the risk monitoring plans are aligned with the organization’s risk strategy, objectives, and policies, and that they comply with the relevant standards and regulations3.
Evaluate whether the risk monitoring plans are comprehensive and consistent, and that they cover all the key aspects and indicators of the risks and the risk responses4.
Identify and address any gaps, issues, or challenges that may affect the implementation or outcome of the risk monitoring plans, and recommend and implement appropriate improvement actions5.
The other options are not the best course of action, because:
Identifying new risk entries to include in ERM is not a relevant or necessary course of action, as it is not directly related to the residual risk or the risk responses. ERM is the process of identifying, analyzing, evaluating, and managing the risks that may affect the organization’s strategic, operational, financial, or reputational objectives6. Identifying new risk entries is a part of the risk identification process, which is the first step in ERM. It should be performedperiodically or when there are significant changes in the internal or external environment, not when the residual risk is within the appetite and tolerance levels7.
Removing the risk entries from the ERM register is not a valid or advisable course of action, as it may create a false sense of security or complacency. The ERM register is a tool that records and summarizes the key information and data about the identified risks and the risk responses. Removing the risk entries from the ERM register may imply that the risks no longer exist or matter, which is not true. The risks may still occur or change, and the risk responses may still fail or become obsolete. Therefore, the risk entries should be kept and updated in the ERM register, unless the risks are completely eliminated or transferred.
Re-performing the risk assessment to confirm results is not an efficient or effective course of action, as it may be redundant or unnecessary. Risk assessment is the process of estimating the probability and impact of the risks, and prioritizing the risks based on their significance and urgency. Re-performing the risk assessment may not provide any new or useful information or insights, and may waste time and resources. Instead, the risk practitioner should verify and validate the risk assessment results, and ensure that they are accurate and reliable.
References =
Risk Monitoring - CIO Wiki
Risk Monitoring Plan - CIO Wiki
Risk Monitoring and Reporting - ISACA
Risk Monitoring and Control - Project Management Institute
Risk Monitoring and Review - The National Academies Press
Enterprise Risk Management - CIO Wiki
Risk Identification - CIO Wiki
[Risk Register - CIO Wiki]
[Risk Register: How to Use It in Project Management - ProjectManager.com]
[Risk Assessment - CIO Wiki]
[Risk Assessment Process - ISACA]
Question # 586
Which of the following deficiencies identified during a review of an organization ' s cybersecurity policy should be of MOST concern?
A.
The policy lacks specifics on how to secure the organization ' s systems from cyberattacks.
B.
The policy has gaps against relevant cybersecurity standards and frameworks.
C.
The policy has not been reviewed by the cybersecurity team in over a year.
D.
The policy has not been approved by the organization ' s board.
Full Access
Answer:
D
Explanation:
The policy has not been approved by the organization’s board should be of most concern, as it indicates a lack of governance and oversight for the organization’s cybersecurity posture. The board is ultimately responsible for setting the strategic direction, objectives, and risk appetite of the organization, and for ensuring that the cybersecurity policy aligns with them. Without the board’s approval, the policy may not reflect the organization’s vision, mission, values, and culture, and may not be communicated, implemented, or enforced effectively. The board’s approval also demonstrates the commitment and support of the senior management for the cybersecurity program, and enhances the accountability and responsibility of the stakeholders involved.
[References:, •ISACA, Essential Functions of a Cybersecurity Program1, •ISACA, Cybersecurity: Based on the NIST Cybersecurity Framework2, , , , , , , , , , ]
Question # 587
Which of the following is the BEST way to determine the potential organizational impact of emerging privacy regulations?
A.
Evaluate the security architecture maturity.
B.
Map the new requirements to the existing control framework.
C.
Charter a privacy steering committee.
D.
Conduct a privacy impact assessment (PIA).
Full Access
Answer:
D
Explanation:
The best way to determine the potential organizational impact of emerging privacy regulations is to conduct a privacy impact assessment (PIA). A PIA is a systematic process of identifying, analyzing, and evaluating the privacy risks and impacts of a new or existing system, process, program, or initiative that involves the collection, use, storage, or disclosure of personal information. A PIA can help to ensure that the enterprise complies with the emerging privacyregulations, and that the privacy rights and expectations of the individuals are respected and protected. A PIA can also help to identify the gaps, weaknesses, and opportunities for improvement in the enterprise’s privacy policies, procedures, and controls. Evaluating the security architecture maturity, mapping the new requirements to the existing control framework, and chartering a privacy steering committee are not as comprehensive and effective as conducting a PIA, as they do not address the specific privacy risks and impacts of the enterprise’s activities. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 192.
Question # 588
Which of the following would BEST indicate to senior management that IT processes are improving?
A.
Changes in the number of intrusions detected
B.
Changes in the number of security exceptions
C.
Changes in the position in the maturity model
D.
Changes to the structure of the risk register
Full Access
Answer:
C
Explanation:
The best indicator to senior management that IT processes are improving is the changes in the position in the maturity model. A maturity model is a framework that defines the levels of capability and performance of a process, such as IT processes, based on the criteria such as governance, management, control, measurement, and improvement. A maturity model can help to assess the current state and the desired state of the IT processes, and to identify the gaps, strengths, and opportunities for improvement. A maturity model can also help to communicate the progress and the value of the IT processes to the senior management, and to support the strategic alignment and integration of the IT processes with the business objectives. Changes in the position in the maturity model indicate that the IT processes are improving, as they show that the IT processes are moving from a lower level to a higher level of maturity, and that they are achieving higher standards of quality, efficiency, and effectiveness. Changes in the number of intrusions detected, changes in the number of security exceptions, and changes to the structure of the risk register are not as good as changes in the position in the maturity model, as they do not provide a comprehensive and consistent measure of the IT processes improvement, and they may not reflect the actual impact and performance of the IT processes. References = CRISC Review Manual, 6th Edition, ISACA, 2015, page 36.
Question # 589
Which of the following is the BEST key performance indicator (KPI) to measure how effectively risk management practices are embedded in the project management office (PMO)?
A.
Percentage of projects with key risk accepted by the project steering committee
B.
Reduction in risk policy noncompliance findings
C.
Percentage of projects with developed controls on scope creep
D.
Reduction in audits involving external risk consultants
Full Access
Answer:
C
Explanation:
The percentage of projects with developed controls on scope creep is the best key performance indicator (KPI) to measure how effectively risk management practices are embedded in the project management office (PMO), as it reflects the ability of the PMO to identify, assess, and respond to the risk of project scope changes that may affect the project objectives, budget, and schedule. The other options are not the best KPIs, as they do not directly measure the effectiveness of risk management practices in the PMO, but rather the outcomes or consequences of risk management decisions. References = CRISC Review Manual, 7th Edition, page 110.
Question # 590
The MOST important reason to aggregate results from multiple risk assessments on interdependent information systems is to:
A.
establish overall impact to the organization
B.
efficiently manage the scope of the assignment
C.
identify critical information systems
D.
facilitate communication to senior management
Full Access
Answer:
A
Explanation:
 The interdependency of information systems means that the failure or disruption of one system can affect the performance or availability of other systems. Therefore, it is important to aggregate the results from multiple risk assessments on interdependent information systems to understand the overall impact to the organization. By aggregating the results, the risk manager can identify the potential cascading effects, the cumulative consequences, and the worst-casescenarios of interdependent risks. This can help theorganization to prioritize the risks, allocate the resources, and implement the risk response strategies accordingly. The other options are not as important as the overall impact to the organization, because they do not capture the full extent of the interdependency of information systems. References = Risk and Information Systems Control Study Manual, Chapter 3, Section 3.4.3, page 99.
Question # 591
An organization has engaged a third party to provide an Internet gateway encryption service that protects sensitive data uploaded to a cloud service. This is an example of risk:
A.
mitigation.
B.
avoidance.
C.
transfer.
D.
acceptance.
Full Access
Answer:
C
Explanation:
Risk transfer is a risk response strategy that involves shifting the responsibility or burden of a risk to another party, such as a third party, an insurance company, or a joint venture. Risk transfer does not eliminate the risk, but it reduces the exposure or impact of the risk to the enterprise. An example of risk transfer is engaging a third party to provide an Internet gateway encryption service that protects sensitive data uploaded to a cloud service. By doing so, the organization transfers the risk of data breach or loss to the third party, who is responsible for ensuring the security and availability of the data. The other options are not examples of risk transfer, as they involve different risk response strategies:
Risk mitigation is a risk response strategy that involves reducing the likelihood or impact of a risk to an acceptable level, such as by implementing controls, policies, or procedures.
Risk avoidance is a risk response strategy that involves eliminating the risk by not performing the activity that generates the risk, such as by discontinuing a product or service, or not entering a market.
Risk acceptance is a risk response strategy that involves acknowledging the risk and taking no action to address it, such as by tolerating the risk, exploiting the risk, or sharing the risk. References =Risk and Information Systems Control Study Manual, 7th Edition, Chapter 3, Section 3.3.1.1, pp. 107-108.
Question # 592
A risk assessment has revealed that the probability of a successful cybersecurity attack is increasing. The potential loss could exceed the organization ' s risk appetite. Which of the following ould be the MOST effective course of action?
A.
Re-evaluate the organization ' s risk appetite.
B.
Outsource the cybersecurity function.
C.
Purchase cybersecurity insurance.
D.
Review cybersecurity incident response procedures.
Full Access
Answer:
D
Explanation:
Cybersecurity incident response procedures are the plans and actions that an organization takes to respond to and recover from a cybersecurity attack. They include identifying the source and scope of the attack, containing and eradicating the threat, restoring normal operations, and analyzing the root cause and lessons learned. Reviewing cybersecurity incident response procedures is the most effective course of action when the probability of a successful cybersecurity attack is increasing and the potential loss could exceed the organization’s risk appetite, as it helps to prepare the organization for minimizing the impact and duration of the attack, as well as improving the resilience and security posture of the organization.