

Question # 4
Which Snowflake capabilities are typically used for rollback scenarios?
Choose two
A.
SELECT SYSTEM$CANCEL_QUERY(‘problematic_query_id’);
B.
CREATE TABLE prd_table_bkp CLONE prd_table BEFORE (STATEMENT = > ‘problematic_query_id’);
C.
CREATE TABLE prd_table_bkp as SELECT * from table(result_scan(‘problematic_query_id’()));
D.
ALTER TABLE prd_table SWAP WITH prd_table_bkp;
E.
Contact Snowflake Support to retrieve Fail-safe data.
Full Access
Answer:
B, D
Explanation:
Snowflake Time Travel and zero-copy cloning provide an efficient mechanism for recovering from accidental data modifications without requiring a conventional full-table backup.
Option B uses Time Travel cloning with the BEFORE clause to create a table representing the historical state immediately preceding a specified statement. The STATEMENT parameter identifies the relevant query ID, and Snowflake reconstructs the qualifying historical version from retained data.
Option D uses ALTER TABLE ... SWAP WITH to exchange the original and restored table objects atomically. This enables the recovered data to become available under the production table name while retaining the displaced table as another object.
Option A cancels an executing query but does not reverse changes that have already committed.
Option C queries a previous statement's result set rather than reconstructing the table's historical state. RESULT_SCAN is not a substitute for Time Travel recovery.
Option E involves Snowflake Fail-safe, which is a last-resort disaster-recovery capability, not the normal administrative mechanism for reversing an erroneous statement.
Technical qualification: The source's problematic_query_id is a placeholder, and the SQL would require an actual qualifying statement ID. Successful recovery also requires the historical version to remain within the configured Time Travel retention period. The administrator must review dependencies, object privileges, and downstream effects before swapping production tables.
Official Snowflake references: Understanding & Using Time Travel; AT | BEFORE; ALTER TABLE; Cloning Considerations.
Question # 5
What are the advantages of using Snowflake organizations?
Choose two
A.
Administrators can change Snowflake account editions on-demand based on need.
B.
Administrators can monitor and understand usage across all accounts in the organization.
C.
Administrators can simplify data movement across all accounts within the organization.
D.
User administration is simplified across all accounts within the organization.
E.
Administrators have the ability to create accounts in any available cloud provider or region.
Full Access
Answer:
B, C
Explanation:
Answer: B and C
Explanation
B. Administrators can monitor and understand usage across all accounts in the organization (Correct): Snowflake Organizations introduces the ORGANIZATION_USAGE schema and Snowsight Admin views. This allows users with the ORGADMIN role to centrally track credit consumption, storage usage, and billing across all accounts within the business entity.
C. Administrators can simplify data movement across all accounts within the organization (Correct): Organizations streamline cross-account and cross-region operations by enabling native database replication, failover/failback groups, and secure data sharing without requiring custom pipeline infrastructure.
Why the Other Options Are Incorrect
A is incorrect: Account editions (Standard, Enterprise, Business Critical) cannot be switched dynamically or on-demand by an administrator; changing an existing account’s edition typically requires contacting Snowflake Support.
D is incorrect: User administration and access control remain account-scoped. Snowflake Organizations does not provide centralized, cross-account user identity management or unified SCIM provisioning.
E is incorrect: Although administrators can self-provision accounts across major supported cloud providers (AWS, Azure, GCP), this capability is bounded by organization contract agreements, account limits, and region availability (certain isolated or government cloud regions cannot be freely created on-demand).
Official Snowflake references: Introduction to Organizations; Working with Account Editions; Organization Users; January and May 2026 general-availability announcements.
Question # 6
MY_TABLE is a table that has not been updated or changed for several days. On 01 January 2021 at 07:01, a user ran a query that updated this table. The query ID is '8e5d0ca9-005e-44e6-b858-a8f5b37c5726'. It is now 07:30 on the same day.
Which queries allow the user to view the historical data that was in the table before this query ran?
Choose three
A.
SELECT * FROM my_table WITH TIME_TRAVEL(OFFSET = > -60*30);
B.
SELECT * FROM my_table AT(TIMESTAMP = > '2021-01-01 07:00:00'::timestamp);
C.
SELECT * FROM TIME_TRAVEL('MY_TABLE', 2021-01-01 07:00:00);
D.
SELECT * FROM my_table PRIOR TO STATEMENT '8e5d0ca9-005e-44e6-b858-a8f5b37c5726';
E.
SELECT * FROM my_table AT(OFFSET = > -60*30);
F.
SELECT * FROM my_table BEFORE(STATEMENT = > '8e5d0ca9-005e-44e6-b858-a8f5b37c5726');
Full Access
Answer:
B, E, F
Explanation:
Snowflake Time Travel enables administrators to query historical table versions within the configured data-retention period. The AT and BEFORE clauses support recovery based on timestamps, relative time offsets, and statement identifiers.
Option B is correct because AT(TIMESTAMP = > ...) retrieves the table's historical state at the specified timestamp. Since the update occurred at 07:01, querying the table at 07:00 retrieves its preceding state.
Option E is correct because OFFSET specifies a relative number of seconds. At the hypothetical current time of 07:30, -60*30 refers to 07:00, before the update.
Option F is correct because BEFORE with a STATEMENT parameter retrieves the table state immediately before the specified statement completed.
Options A, C, and D use unsupported Time Travel syntax.
Snowflake requires historical data to remain within the table's retention period. Additionally, the STATEMENT parameter must identify a qualifying query executed within the previous 14 days.
Current-version qualification: The scenario is explicitly set on January 1, 2021. These statements are valid in that historical context; they cannot be used today to recover January 2021 data unless an applicable historical recovery mechanism still retains it. Timestamp interpretation also depends on Snowflake's timestamp type and session time zone.
Official Snowflake references: AT | BEFORE; Understanding & Using Time Travel.
Question # 7
Which of the following are characteristics of Dynamic Data Masking?
Choose two
A.
A masking policy that is currently set on a table can be dropped.
B.
A single masking policy can be applied to columns in different tables.
C.
A masking policy can be applied to the VALUE column of an external table.
D.
The role that creates the masking policy will always see unmasked data in query results.
E.
A single masking policy can be applied to columns with different data types.
Full Access
Answer:
B, C
Explanation:
Snowflake Dynamic Data Masking enforces column-level protection at query execution time. Masking policies determine whether the querying context receives the original value or a transformed representation.
Option B is correct because the same masking policy can be assigned to multiple compatible columns across different tables or views. This supports centralized governance and consistent protection of sensitive fields throughout an environment.
Option C is also correct. Snowflake supports assigning a masking policy to an external table's automatically generated VALUE column. The policy must accept and return the VARIANT data type, and the assignment must be performed using an ALTER TABLE statement rather than during initial external-table creation.
Option A is incorrect because a masking policy cannot normally be dropped while it remains associated with a column or tag. The administrator must first remove the applicable assignment.
Option D is incorrect because creating a policy does not automatically authorize viewing unmasked data. Visibility depends on the policy expression and execution context.
Option E is incorrect because a masking policy's argument and return signatures impose data-type compatibility requirements. One policy cannot be freely attached to columns of unrelated types.
This distinction is important when implementing reusable policies and managing external data.
Official Snowflake references: Understanding Column-level Security; DROP MASKING POLICY; Tag-based Masking Policies.
Question # 8
A Snowflake organization, MYORG, contains two Snowflake accounts:
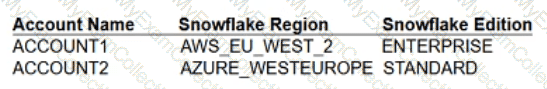
ACCOUNT1 has a database named PROD_DB and has the ORGADMIN role enabled. Management wants PROD_DB replicated to ACCOUNT2.
A.
re any configuration steps required in ACCOUNT1 before database replication can be configured and started in ACCOUNT2?
B.
USE ROLE ORGADMIN;
SELECT SYSTEM$GLOBAL_ACCOUNT_SET_PARAMETER(
'MYORG.ACCOUNT1',
'ENABLE_ACCOUNT_DATABASE_REPLICATION',
'TRUE'
);
SELECT SYSTEM$GLOBAL_ACCOUNT_SET_PARAMETER(
'MYORG.ACCOUNT2',
'ENABLE_ACCOUNT_DATABASE_REPLICATION',
'TRUE'
);
USE ROLE ACCOUNTADMIN;
ALTER DATABASE PROD_DB
ENABLE REPLICATION TO ACCOUNTS MYORG.ACCOUNT2;
C.
USE ROLE ORGADMIN;
SELECT SYSTEM$GLOBAL_ACCOUNT_SET_PARAMETER(
'MYORG.ACCOUNT1',
'ENABLE_ACCOUNT_DATABASE_REPLICATION',
'TRUE'
);
USE ROLE ACCOUNTADMIN;
ALTER DATABASE PROD_DB
ENABLE REPLICATION TO ACCOUNTS MYORG.ACCOUNT2
IGNORE EDITION CHECK;
D.
No configuration steps are necessary in ACCOUNT1. Replicating databases across accounts within the same Snowflake organization is enabled by default.
E.
It is not possible to replicate a database from an Enterprise edition Snowflake account to a Standard edition Snowflake account.
Full Access
Answer:
A
Explanation:
Snowflake supports replication of databases between accounts belonging to the same organization, including accounts in different cloud providers and regions.
Option A correctly performs two prerequisites. First, an organization administrator enables replication for both the source and destination accounts by calling SYSTEM$GLOBAL_ACCOUNT_SET_PARAMETER with ENABLE_ACCOUNT_DATABASE_REPLICATION set to TRUE.
Second, an appropriately authorized account administrator enables replication on PROD_DB and explicitly identifies ACCOUNT2 as an approved destination.
Option B is incorrect because it does not enable replication for ACCOUNT2. Additionally, IGNORE EDITION CHECK is not necessary when the primary account uses Enterprise Edition and the destination uses Standard Edition.
Snowflake reserves that override for specified circumstances involving Business Critical or higher editions and lower-edition destination accounts or related compliance differences.
Option C is incorrect because the required replication features must be enabled for participating accounts.
Option D is incorrect because Snowflake supports database replication from Enterprise Edition to Standard Edition.
Current-version qualification: These commands represent the legacy database-replication workflow. Snowflake now supports replication groups and recommends group-based replication for broader business-continuity configurations. The ORGADMIN role is also being phased out in favor of GLOBALORGADMIN in a dedicated organization account.
Official Snowflake references: SYSTEM$GLOBAL_ACCOUNT_SET_PARAMETER; ALTER DATABASE; Introduction to Replication and Failover Across Multiple Accounts.
Question # 9
Which session parameter can be used to test the integrity of secure views based on the account that accesses the view?
A.
MIMIC_CONSUMER_ACCOUNT
B.
TEST_ACCOUNT_ID
C.
PRODUCER_TEST_ACCT
D.
SIMULATED_DATA_SHARING_CONSUMER
Full Access
Answer:
D
Explanation:
Snowflake provides the SIMULATED_DATA_SHARING_CONSUMER session parameter to allow data providers to validate how shared secure views behave when accessed from a specified consumer account.
This is important when secure views apply account-dependent filtering, such as restricting individual consumers to their permitted subsets of shared data.
An administrator can configure a test session using:
ALTER SESSION
SET SIMULATED_DATA_SHARING_CONSUMER =
'ORGNAME.ACCOUNTNAME';
The administrator can then query the secure view and inspect the rows that would be returned to the specified consumer account.
Option D is correct because it identifies the documented session parameter.
Options A, B, and C reference unsupported parameter names.
Snowflake requires the role executing the simulation to own the secure view. A session using a different role cannot perform the simulation merely because that role has SELECT access.
The parameter is intended specifically for testing shared secure views and secure materialized views, not for changing the actual consumer identity or granting access.
Administrative qualification: Snowflake explicitly advises against setting this parameter at the account level. Although the parameter's definition supports multiple configuration scopes, its effects should be limited to controlled testing sessions.
Simulation also does not replace end-to-end validation of consumer privileges, authentication, and share configuration.
Official Snowflake references: Parameters — SIMULATED_DATA_SHARING_CONSUMER; Create and Configure Shares; Use Secure Objects to Control Data Access.
Question # 10
Which role or roles should be used to correctly create the object needed to configure an OAuth 2.0 integration?
A.
Any role with GRANT USAGE on SECURITY INTEGRATION
B.
ACCOUNTADMIN and SYSADMIN
C.
ACCOUNTADMIN and SECURITYADMIN
D.
ACCOUNTADMIN only
Full Access
Answer:
D
Explanation:
Snowflake configures OAuth 2.0 authentication through a security integration created using the CREATE SECURITY INTEGRATION statement. The integration defines the relevant OAuth authentication and authorization settings, depending on whether Snowflake OAuth or External OAuth is implemented.
Creating an OAuth security integration requires the global CREATE INTEGRATION privilege on the Snowflake account.
The ACCOUNTADMIN system role possesses this privilege by default. Therefore, ACCOUNTADMIN is the appropriate selection when evaluating the standard system-role configuration without additional privilege delegation.
Option A is incorrect because USAGE on an existing security integration does not provide authority to create a new integration.
Options B and C are incorrect because neither SYSADMIN nor SECURITYADMIN is inherently required to participate in creation. These roles also do not receive the required CREATE INTEGRATION privilege merely through their default administrative responsibilities.
The following statement illustrates the intended administrative context:
USE ROLE ACCOUNTADMIN;
CREATE SECURITY INTEGRATION oauth_integration
TYPE = OAUTH
ENABLED = TRUE
OAUTH_CLIENT = CUSTOM;
```
Additional integration parameters may be required depending on the OAuth implementation.
Verification qualification: The phrase "ACCOUNTADMIN only" is technically too restrictive. Snowflake explicitly permits the CREATE INTEGRATION privilege to be granted to other roles. Thus, D is the intended answer for default system-role privileges, but not an absolute authorization rule.
Official Snowflake references: CREATE SECURITY INTEGRATION (Snowflake OAuth); CREATE SECURITY INTEGRATION (External OAuth); Configure Snowflake OAuth for Partner Applications.
Question # 11
Which are characteristics of data replication in Snowflake?
Choose three
A.
The ALTER DATABASE ... ENABLE REPLICATION TO ACCOUNTS command must be issued from the primary account.
B.
Users must be granted REPLICATIONADMIN privileges in order to enable replication.
C.
To start replication run the ALTER DATABASE ... REFRESH command on the account where the secondary database resides.
D.
Replication can only occur within the same cloud provider.
E.
Databases created from shares can be replicated.
F.
Users can have unlimited primary databases and they can be replicated to an unlimited number of accounts if all accounts are within the same organization.
Full Access
Answer:
A, C, F
Explanation:
Snowflake supports database replication between accounts in the same organization, including accounts deployed in different regions and cloud platforms.
Option A is correct because the administrator enables replication on the source database from the account containing that primary database. The ALTER DATABASE ... ENABLE REPLICATION TO ACCOUNTS statement identifies the destination accounts authorized to create replicas.
Option C is correct because replication refreshes are initiated from the account containing the secondary database, using ALTER DATABASE < secondary_database > REFRESH.
Option F is supported by Snowflake's database-replication documentation, which permits any number of primary databases in an account and allows a primary database to be replicated to any number of accounts within the organization. Practical resource limits and applicable account restrictions must still be considered.
Option B is incorrect because REPLICATIONADMIN is not a required predefined system role for the legacy database-replication workflow. ACCOUNTADMIN performs the relevant operations.
Option D is incorrect because cross-cloud replication is supported.
Option E is incorrect because databases created from incoming shares cannot be replicated using this database-replication mechanism.
Current-version warning: This question describes legacy database replication. Snowflake now strongly recommends replication and failover groups under its account-replication architecture. The selected answers remain valid for the specific commands named in the question.
Official Snowflake references: Introduction to Database Replication Across Multiple Accounts; ALTER DATABASE; Database Replication Considerations.
Question # 12
Which command can temporarily disable multi-factor authentication (MFA) for the Snowflake username user1 for 24 hours?
A.
alter user user1 set MINS_TO_BYPASS_MFA=1440;
B.
alter user user1 set DISABLE_MFA=1440;
C.
alter user user1 set TEMPORARY_MFA_BYPASS=1440;
D.
alter user user1 set HOURS_TO_BYPASS_MFA=24;
Full Access
Answer:
A
Explanation:
Snowflake provides the MINS_TO_BYPASS_MFA user property to support temporary authentication recovery when an enrolled user cannot complete multi-factor authentication.
This property specifies the number of minutes during which the affected user may authenticate without providing the normally required second authentication factor.
The requested duration is 24 hours, equivalent to 1,440 minutes:
ALTER USER user1
SET MINS_TO_BYPASS_MFA = 1440;
An authorized administrator can execute this command to establish a temporary MFA bypass for user1. The bypass expires after the configured duration, allowing normal MFA enforcement to resume without permanently removing the user's enrollment.
Option B is incorrect because DISABLE_MFA is a Boolean user property, not a numeric duration setting. Assigning 1440 does not express the intended temporary bypass. Options C and D reference properties that are not supported by Snowflake's ALTER USER syntax.
The administrator should use the minimum bypass duration necessary to restore access because authentication without a second factor increases exposure to compromised credentials.
Snowflake also supports ALTER USER ... ENROLL MFA to help locked-out users register a replacement authentication method. That approach may be preferable when the original device has been lost.
Official Snowflake references: ALTER USER; CREATE USER; Multi-factor Authentication: Recovering a User Who Is Locked Out.
Question # 13
Which type of Snowflake Marketplace listing can be added and queried right away?
A.
Monetized listing
B.
Standard listing
C.
Regional listing
D.
Personalized listing
Full Access
Answer:
B
Explanation:
Snowflake Marketplace enables providers to publish data products that consumers can discover and access through secure data-sharing mechanisms.
Option B is the intended answer because a standard, freely accessible listing allows authorized consumers to obtain the available dataset without a personalized approval process.
After adding the listing to their account, consumers can query the imported database using appropriate privileges and a virtual warehouse.
Option A refers to a monetized listing, where access to the complete data product can depend on purchase authorization, an accepted offer, or a trial arrangement.
Option C does not identify a corresponding access model that inherently guarantees immediate availability. Regional availability affects whether the data product has already been fulfilled to the consumer's region.
Option D refers to a personalized listing, which normally involves requesting access from the provider before the complete data product becomes available.
Current-version qualification: Snowflake's contemporary listing documentation generally describes this capability as a public free listing rather than a standard listing.
Also, immediate access is conditional on the product being available in the consumer's region and the consumer having the required privileges. Cross-region fulfillment may introduce a delay.
Thus, B remains the intended examination answer, but its terminology should be modernized.
Official Snowflake references: Create and Publish a Listing; Access and Install Listings as a Consumer; About Data Exchange.
Question # 14
A sales team at an organization runs the following Snowflake query several times each day:

What can the Snowflake Administrator do to optimize use of persisted query results whenever possible?
A.
Wrap the query in a User-Defined Function (UDF) to match syntax execution.
B.
Assign everyone on the sales team to the same virtual warehouse.
C.
Assign everyone on the sales team to the same security role.
D.
Leverage the CURRENT_DATE function for date calculations.
Full Access
Answer:
D
Explanation:
Snowflake persisted query results enable the query engine to reuse previously computed results when eligible identical queries are executed again.
Option D is the intended optimization because CURRENT_DATE expresses the business requirement using date-level precision rather than calculating an execution-time timestamp and subsequently converting it to a date.
This is more appropriate for reports whose date boundaries change daily rather than with every query execution.
Option A is incorrect because wrapping SQL inside a UDF does not automatically make queries eligible for persisted-result reuse.
Option B is incorrect because persisted query results are not tied to the local data cache of a particular virtual warehouse.
Option C is unnecessary because Snowflake can reuse eligible persisted SELECT results across roles when the executing roles have the required access privileges.
Snowflake also requires compatible query text, unchanged underlying data, an available cached result, and appropriate configuration settings. Persisted results generally expire after 24 hours, although successful reuse can extend their availability.
Critical source-query warning: The exhibit reverses its BETWEEN boundaries: the current date appears before the date seven days earlier. This must be corrected before deployment. Furthermore, CURRENT_DATE is session-time-zone-dependent, and Snowflake does not guarantee cache reuse merely because CURRENT_TIMESTAMP is replaced. The answer is the best of the available choices, not a guaranteed cache optimization.
Official Snowflake references: Using Persisted Query Results; CURRENT_DATE; Context Functions.
Question # 15
A user has enrolled in multi-factor authentication (MFA) to connect to Snowflake. The user tells the Snowflake Administrator that they lost their mobile phone the prior evening.
Which action should the Administrator take to enable the user to sign in to the system without revoking the user’s MFA enrollment?
A.
Alter the user and set MINS_TO_BYPASS_MFA to a value that will disable MFA long enough for the user to log in.
B.
Alter the user and set DISABLE_MFA to true, which will suspend the MFA requirement for 24 hours.
C.
Instruct the user to connect to Snowflake using SnowSQL, which does not support MFA authentication.
D.
Instruct the user to append the normal URL with /?mode=mfa_bypass & code= to log on.
Full Access
Answer:
A
Explanation:
Snowflake provides temporary MFA bypass functionality to recover user access when an enrolled authentication device becomes unavailable. The appropriate administrative action is to configure the MINS_TO_BYPASS_MFA property on the affected user.
For example:
ALTER USER user1
SET MINS_TO_BYPASS_MFA = 30;
This command permits the user to authenticate temporarily without completing MFA for the configured 30-minute period. Importantly, the operation does not revoke the user's existing MFA enrollment or permanently disable the authentication requirement.
Option B is unsuitable because DISABLE_MFA is a Boolean setting and does not automatically provide a 24-hour expiration period. It is not equivalent to a controlled, time-limited bypass.
Option C is incorrect because Snowflake supports MFA authentication through SnowSQL and other supported clients. Changing the connection client does not inherently eliminate MFA enforcement.
Option D proposes an unsupported URL-based authentication bypass.
From a security-administration perspective, the administrator should first validate the user's identity through an approved recovery procedure, establish the shortest practical bypass interval, and guide the user through registration of a replacement MFA method.
Current Snowflake documentation also describes ALTER USER ... ENROLL MFA as a recovery mechanism for users who must register a new authenticator.
Official Snowflake references: Multi-factor Authentication; Recovering a User Who Is Locked Out; ALTER USER.
Question # 16
C. reating a stream on a standard table requires the CREATE STREAM privilege on the target schema and SELECT on the source table. The role also needs USAGE on the parent database and schema to access objects in that location.
An Administrator loads data into a staging table each day. After it is loaded, users from several different departments transform the data and load it into different production tables.
How should the staging table be created and used to MINIMIZE storage costs and MAXIMIZE performance?
A.
Create it as an external table, which will not incur Time Travel costs.
B.
Create it as a transient table with a retention time of 0 days.
C.
Create it as a temporary table with a retention time of 0 days.
D.
Create it as a permanent table with a retention time of 0 days.
Full Access
Answer:
B
Explanation:
Snowflake transient tables are designed for intermediate or reproducible data that must persist beyond an individual session but does not require the complete recovery protections of permanent tables.
In this scenario, multiple departments access the same staging dataset through separate user sessions. A transient table provides persistent, shared access while avoiding the additional storage overhead associated with Fail-safe.
Configuring DATA_RETENTION_TIME_IN_DAYS to zero eliminates the normal Time Travel retention period, minimizing historical storage consumption.
An appropriate implementation is:
CREATE TRANSIENT TABLE STAGING_DATA
(
RECORD_ID NUMBER,
SOURCE_VALUE VARCHAR
)
DATA_RETENTION_TIME_IN_DAYS = 0;
Option A is unsuitable because external tables reference files in external storage and may introduce additional query overhead during repeated transformations.
Option C is incorrect because temporary tables are session-scoped and are not suitable for shared departmental processing across independent sessions.
Option D retains the seven-day Fail-safe protection associated with permanent tables, even when Time Travel retention is configured as zero.
Option B therefore provides the most appropriate balance of shared accessibility and reduced storage charges.
Technical qualification: Transient tables use native Snowflake storage, but they are not inherently faster than equivalent permanent tables. Their principal advantage here is lower recovery-related storage overhead. The staging dataset must be reproducible because it cannot be recovered after its applicable retention period expires.
Official Snowflake references: Working with Temporary and Transient Tables; Understanding Storage Costs.
Question # 17
Which responsibility belongs to the SECURITYADMIN role but is not granted to the USERADMIN role?
A.
Reset a Snowflake user's password
B.
Manage system grants
C.
Create new users
D.
Create new roles
Full Access
Answer:
B
Explanation:
Snowflake implements a hierarchical system of predefined administrative roles to separate identity administration, security governance, and object management responsibilities.
USERADMIN is primarily responsible for creating and administering users and roles. It has the CREATE USER and CREATE ROLE global privileges by default.
SECURITYADMIN occupies a higher position in the standard role hierarchy and inherits USERADMIN's capabilities.
In addition, SECURITYADMIN possesses the global MANAGE GRANTS privilege, which authorizes administrators to grant and revoke privileges across the Snowflake account.
Option B is therefore correct because managing account-wide privilege grants is a capability assigned to SECURITYADMIN but not automatically granted to USERADMIN.
Option A is incorrect because USERADMIN can manage credentials for users it owns or otherwise has authorization to modify.
Options C and D are incorrect because user and role creation are foundational USERADMIN responsibilities.
An important security distinction is that MANAGE GRANTS enables privilege administration but does not automatically grant direct access to all protected data or confer object-creation privileges.
For example, SECURITYADMIN may grant SELECT on a table to a role without necessarily having the SELECT privilege itself.
Organizations should delegate these responsibilities through appropriate custom roles rather than granting SECURITYADMIN broadly to users performing routine identity-management tasks.
Official Snowflake references: Overview of Access Control: System-defined Roles; Access Control Best Practices.
Question # 18
What is the default data-retention period for transient databases, schemas, and tables in Snowflake Enterprise Edition and higher?
A.
1 day
B.
14 days
C.
30 days
D.
90 days
Full Access
Answer:
A
Explanation:
Snowflake Time Travel preserves historical data versions to support recovery operations such as querying previously modified data, cloning historical objects, and restoring dropped objects.
The default Time Travel retention period for transient databases, schemas, and tables is one day, regardless of whether the account uses Enterprise Edition or a higher edition.
Option A is therefore correct.
Unlike permanent tables, transient tables do not benefit from Snowflake's seven-day Fail-safe retention period. Their Time Travel retention can be configured to zero or one day, and historical data is not recoverable through normal Time Travel operations after the applicable period expires.
Option D is a plausible distractor because Enterprise Edition and higher support Time Travel retention periods of up to 90 days for permanent databases, schemas, and tables. However, this extended retention capability does not apply to transient tables.
Options B and C describe durations that are unavailable for transient tables.
Administrators should carefully distinguish between a database's default retention setting and the maximum retention supported by its contained table types. Creating a transient database does not provide extended historical recovery merely because the account uses Enterprise Edition.
Transient objects are primarily appropriate for intermediate, reproducible, or noncritical datasets where reduced storage overhead is more important than extended recovery protection.
Official Snowflake references: Working with Temporary and Transient Tables: Comparison of Table Types; Understanding & Using Time Travel.

